
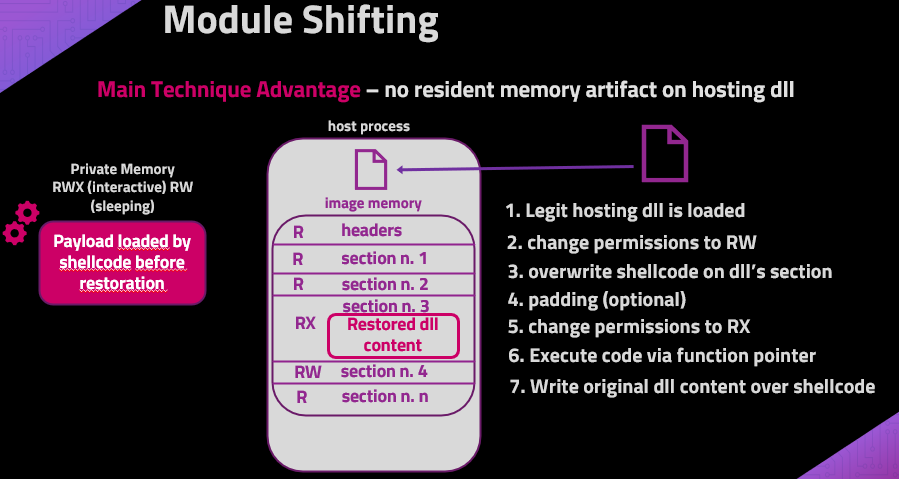
ModuleShifting
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
memory-forensicsred-teamingpayload-development+1
135
naksyn/moduleshiftingStealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
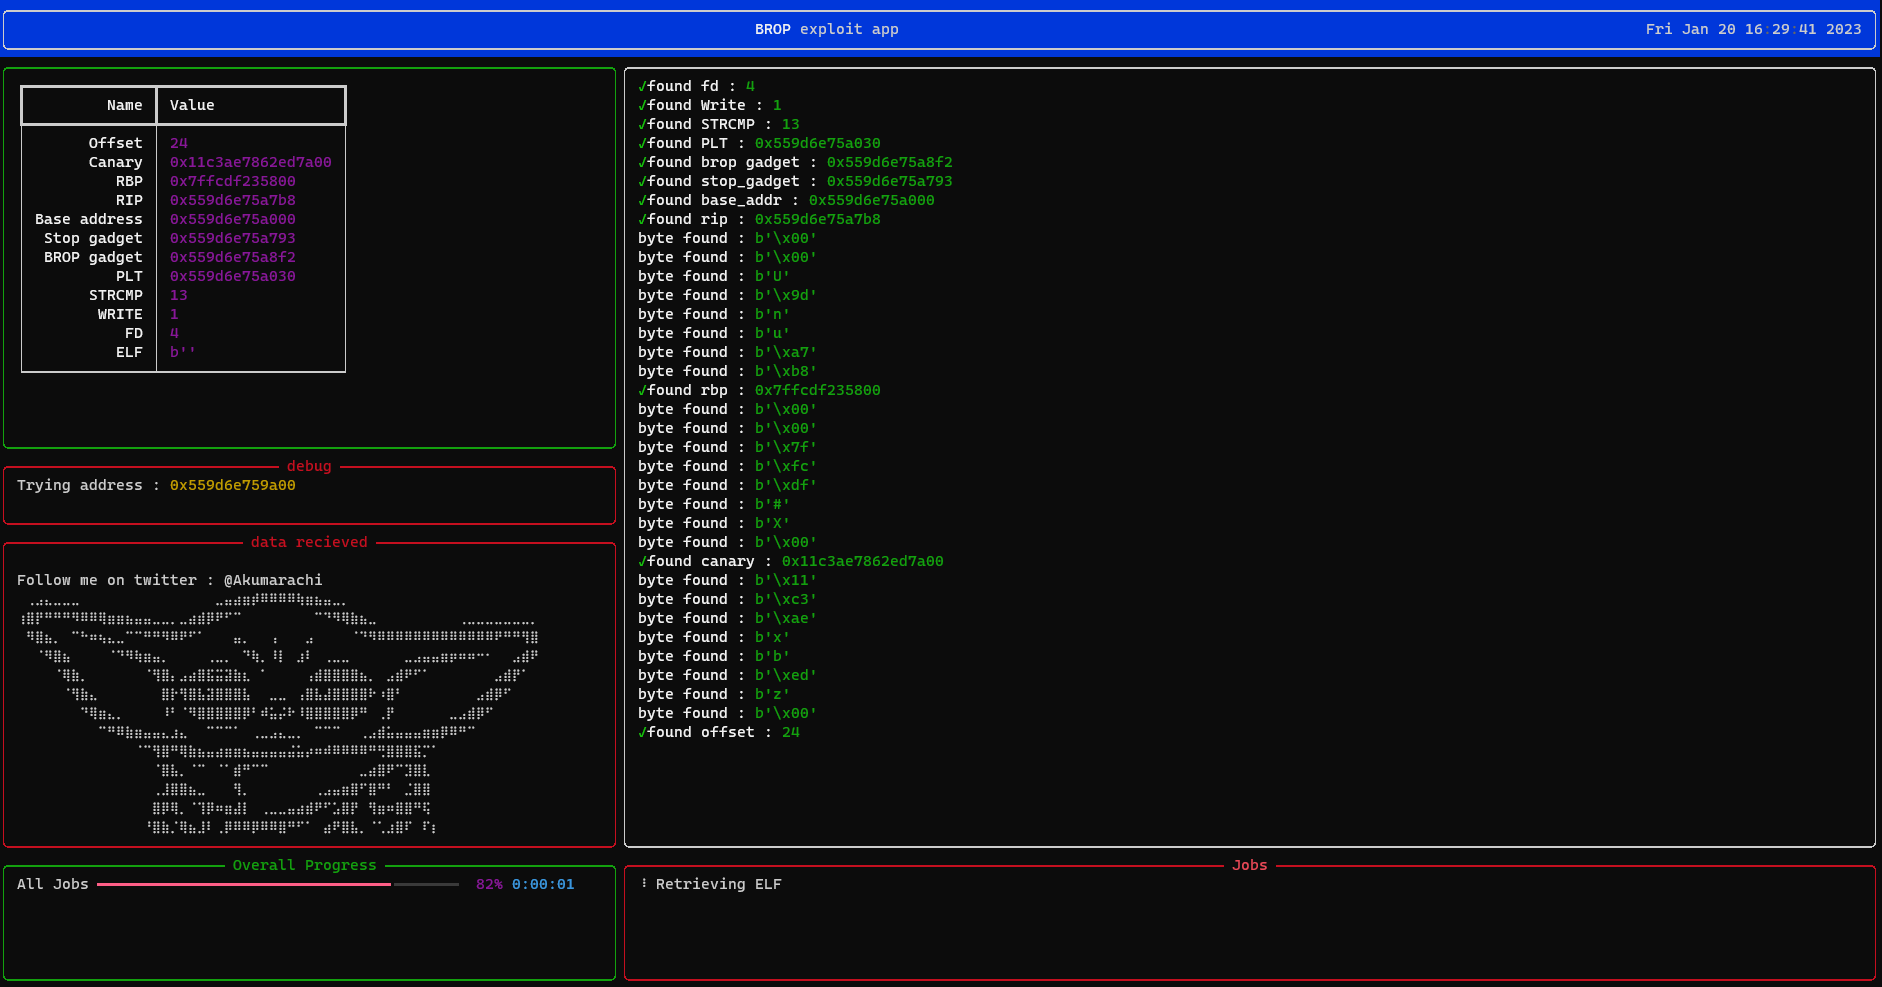 hakumarachi/bropper
An automatic Blind ROP exploitation tool
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 monoxgas/koppeling
Adaptive DLL hijacking / dynamic export forwarding
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
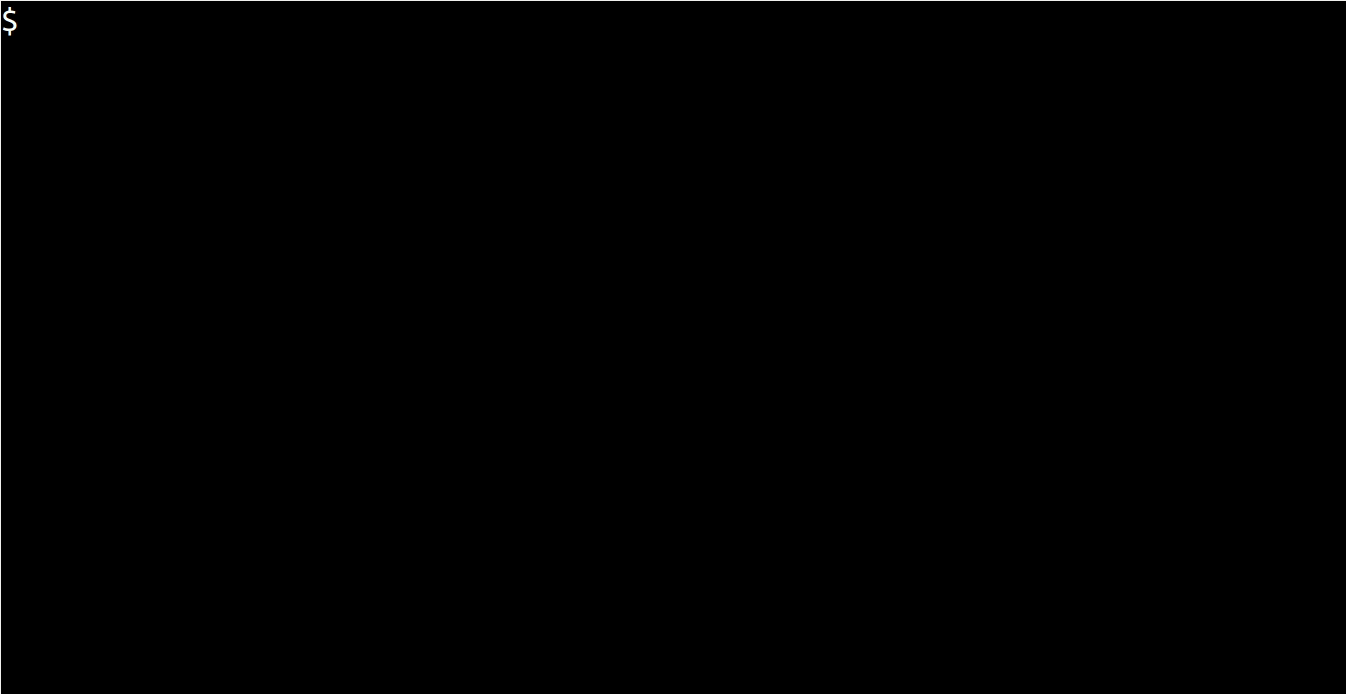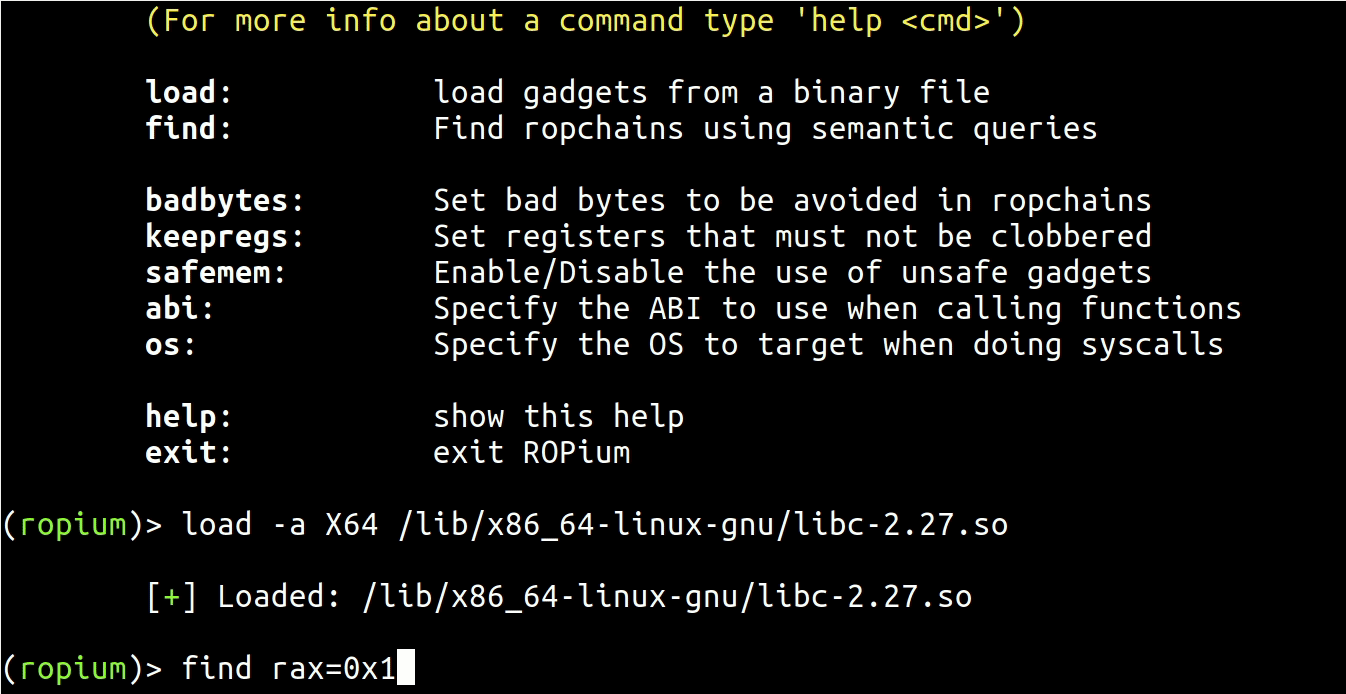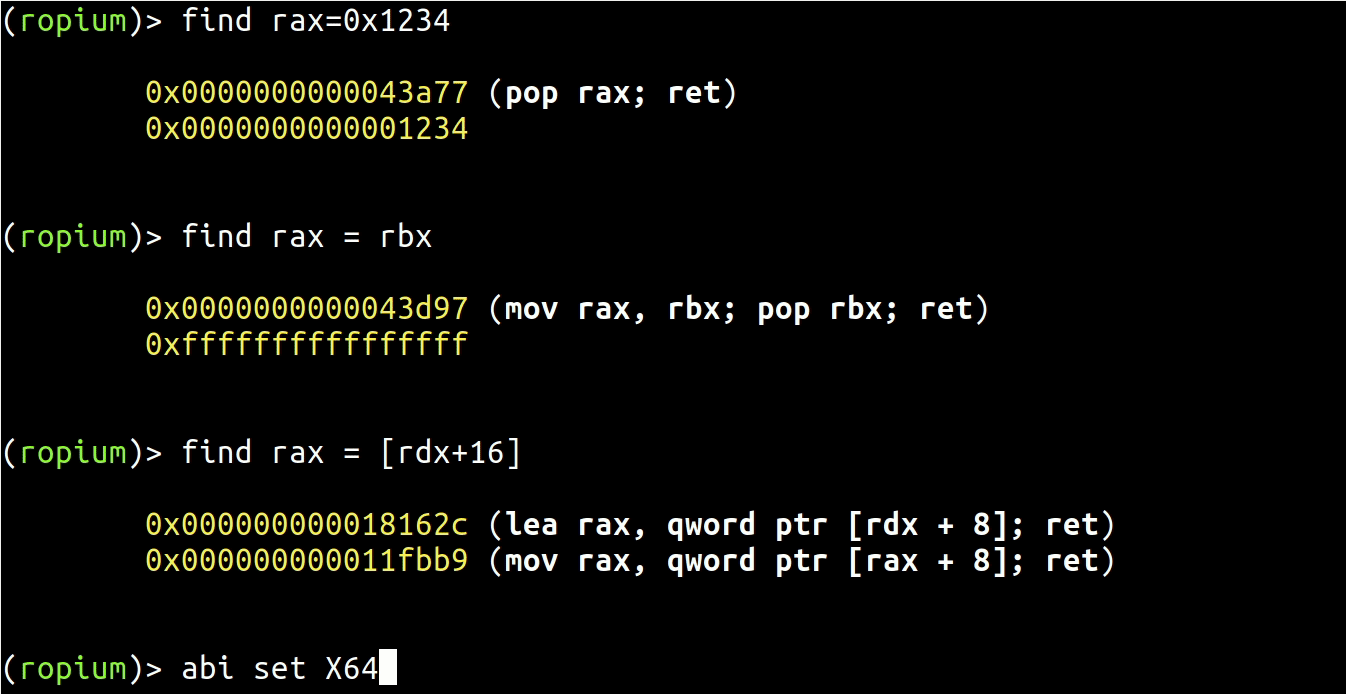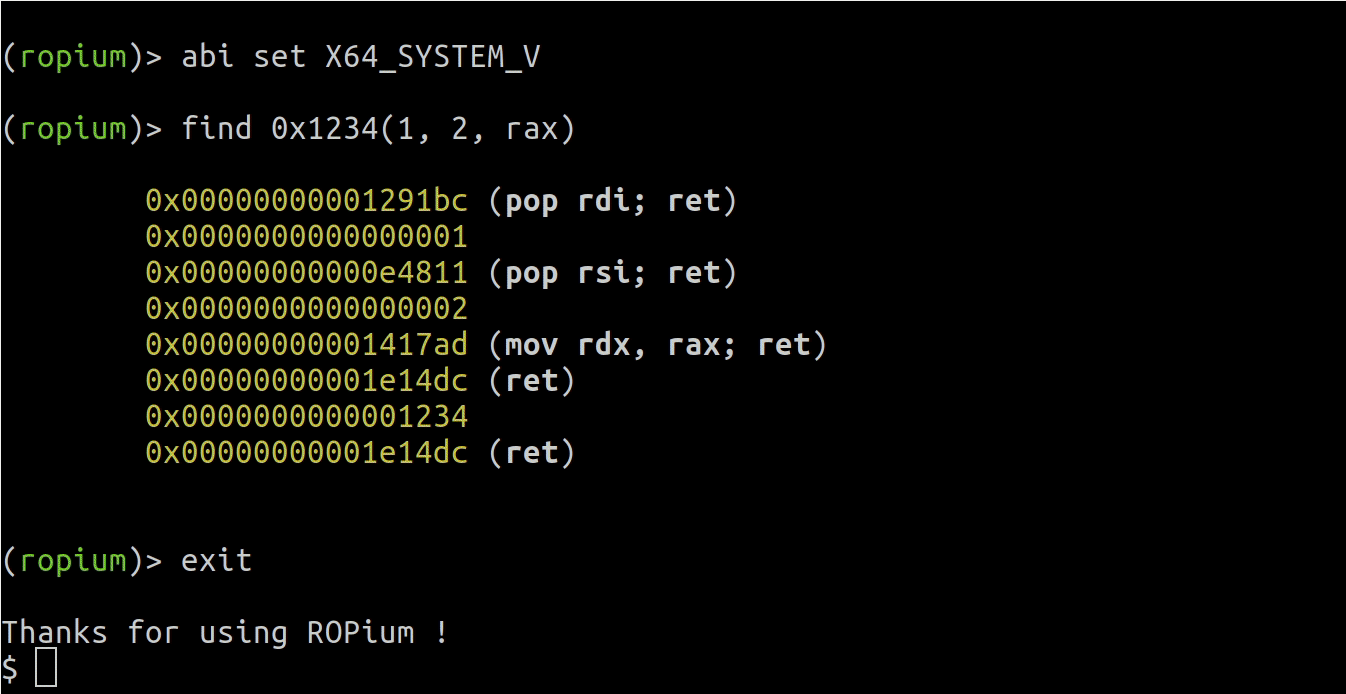 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 diego-altf4/pwnctftool
Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
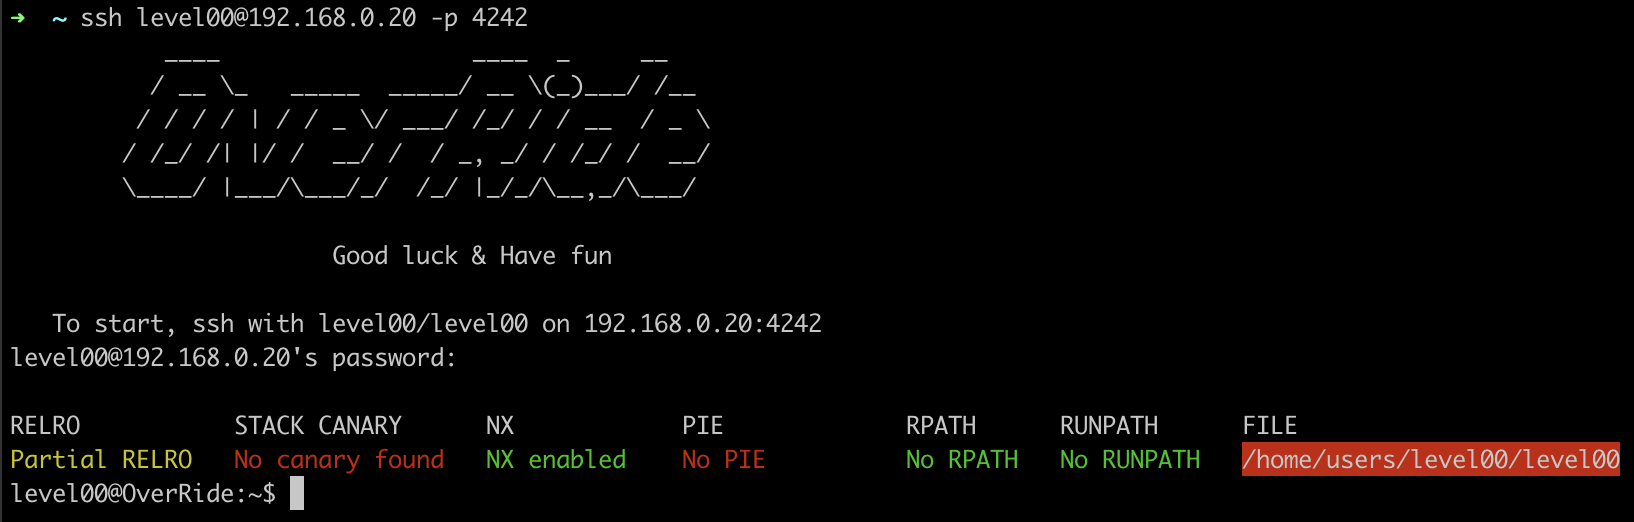 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 heathen42/ctf
Curated collection of CTF challenge solutions covering binary exploitation, reverse engineering, and system security with detailed write-ups.

 xteardx/diaphora-mcp
MCP server for automated binary diffing.