

 google/safetext
Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 ameetsaahu/kernel-exploitation
Linux kernel exploit development notes and scripts for CTF challenges, covering initramfs extraction, msg_msg/ldt_struct abuse, and practical…
 mr-xn/blackhat_usa2022
BLACKHAT USA2022 PDF Public
 hackerhouse-opensource/mssettingsdelegateexecute
Bypass UAC on Windows 10/11 x64 using ms-settings DelegateExecute registry key.
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.
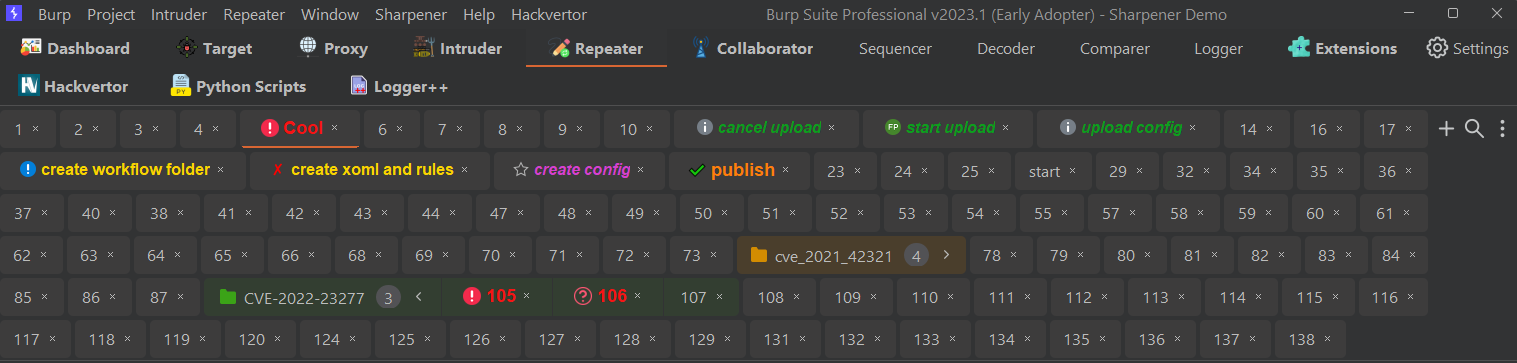 mdsecresearch/burpsuitesharpener
Enhances Burp Suite with tab management, customizable themes, keyboard shortcuts, title renaming, window position memory, and UI utilities for faster…
 codextf2/cobaltstrike-sleepmask-yara
Just a git repo for the sleepmask detection rule i found in https://codex-7.gitbook.io/codexs-terminal-window/blue-team/detecting-cobalt-strike/sleep-…
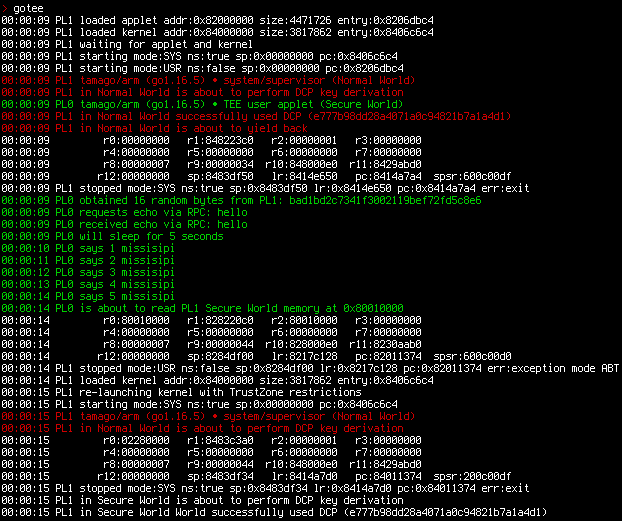 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 irsl/microsoft-diagcab-rce-poc
Proof of concept about a path traversal vulnerability in Microsoft's Diagcab technology that could lead to remote code execution
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
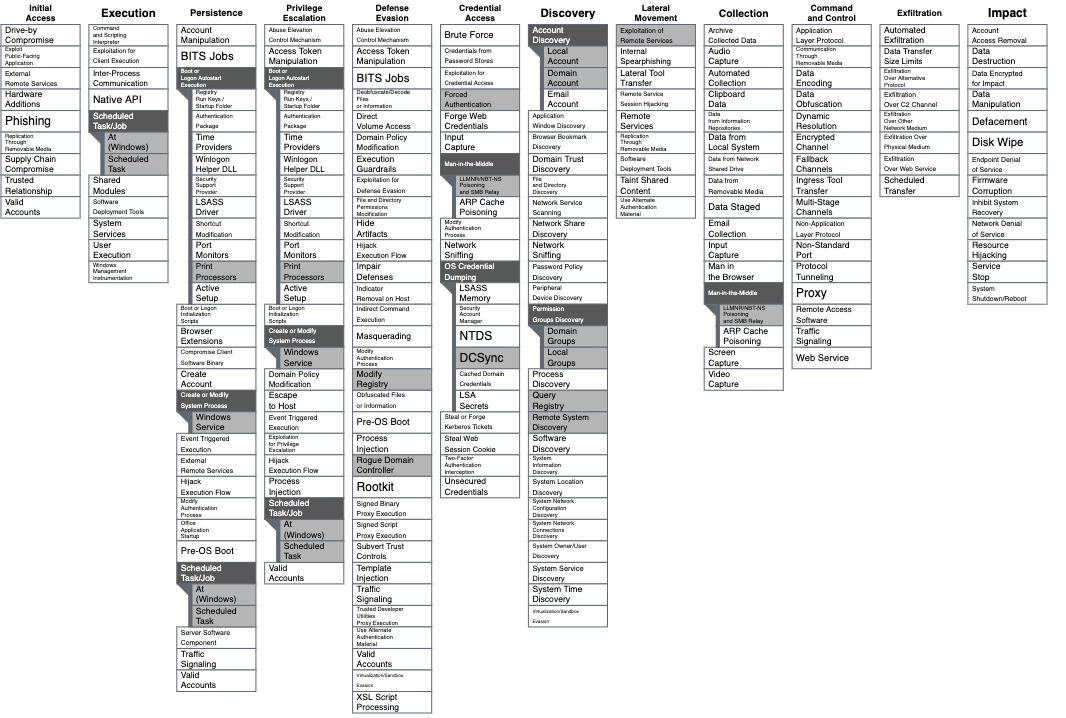 jonny-jhnson/msrpc-to-attack
A repository that maps commonly used attacks using MSRPC protocols to ATT&CK
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…