
Sentora
 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
vulnerability-scannersthreat-intelligenceintrusion-detection+3
12
d3vhex/sentoraAn open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 htrxuan/hdwebmobile-photo-video-reviews
WooCommerce plugin: photo & video product reviews, closing CVE-2026-12684's unauthenticated-upload vulnerability class by construction
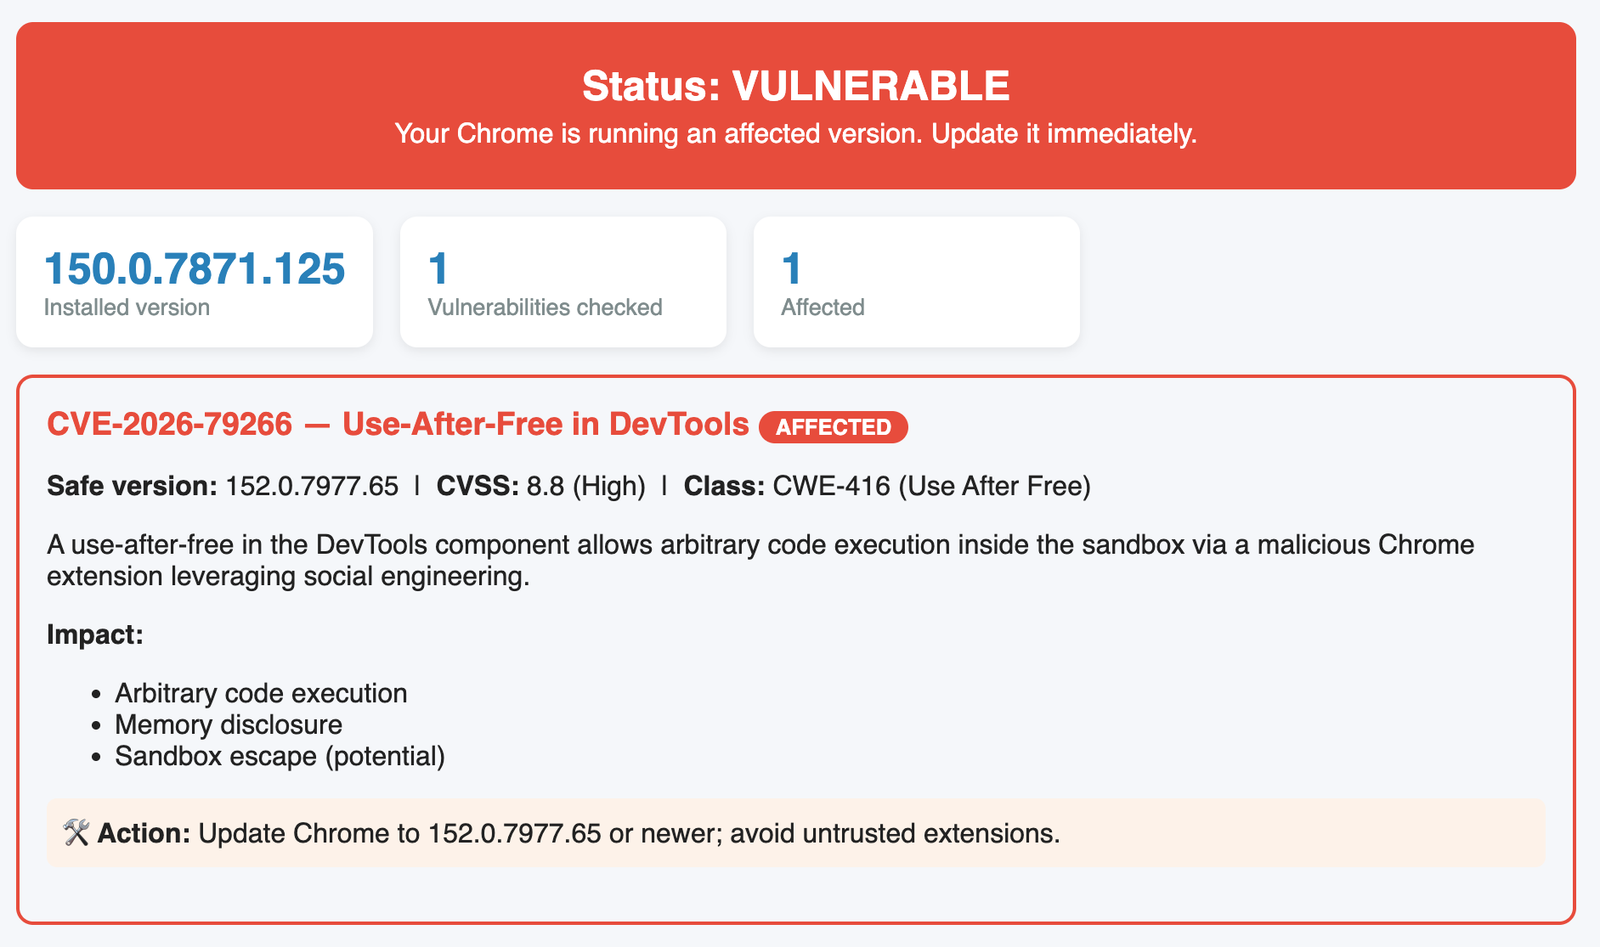 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
 shizuku198411/cve-2026-0300
Non-destructive exposure survey tool for assessing PAN-OS User-ID Authentication Portal surfaces related to CVE-2026-0300, performing safe HTTP(S)…
 sebinxavi/cve-checker-2026
Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)
 scriptzteam/paranoid-dirty-frag-cve-2026-43284
Paranoid disable Linux IPsec ESP support (esp4/esp6) and RxRPC support.
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…
 professional-slacker/alg_check
Audits and hardens Linux systems against AF_ALG local privilege escalation (CVE-2026-31431) by checking kernel crypto API exposure, restricting…
 parmstro/cfdr
Ansible playbook for detecting and remediating CVE-2026-31431 (Copy Fail) - Linux kernel local privilege escalation vulnerability
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 mr-r3b00t/cve-2026-0300
Deceptive honeypot designed to simulate and monitor exploitation attempts targeting CVE-2026-0300, capturing attacker behavior for analysis and…
 mlazzarotto/copy-fail-cve-2026-31431-mitigation-ansible-playbook
An Ansible Playbook to mitigate the vulnerability CVE-2026-31431 on RHEL-based and Debian-based OSes.
 mahradbt/copyfail-mitigation
Ansible playbooks to audit and mitigate CVE-2026-31431 ("Copy Fail"), a local privilege escalation vulnerability in the Linux kernel's `algif_aead`…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 linko-iheb/cve-2026-41940-scanner
Passive, read-only vulnerability scanner for detecting CVE-2026-41940 in cPanel & WHM. Performs version-based fingerprinting, generates…
 kwilck/copyfail
Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…
 joltcan/ansible-role-cve-2026-31431
Ansible role that applies and verifies the modprobe.d mitigation for CVE-2026-31431 by disabling the algif_aead kernel module, with safety checks for…
 isagoakira/ghes-cve-scanner
Scans GitHub Enterprise Server instances for CVE-2026-3854 and CVE-2026-4821, providing version-based detection with batch scanning and multiple…