
mobsfscan
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
android-securitystatic-analysisios-security+3
779
mobsf/mobsfscanmobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 ashishb/android-security-awesome
A collection of android security related resources
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 crowdstrike/xwf-yara-scanner
Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
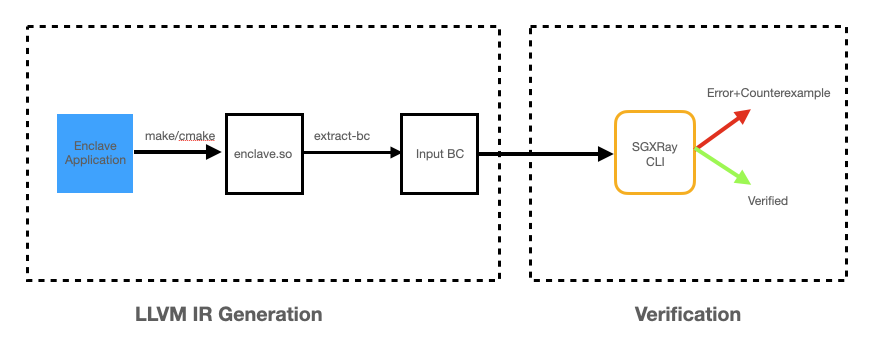 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…
 dissectmalware/xlmmacrodeobfuscator
Extract and Deobfuscate XLM macros (a.k.a Excel 4.0 Macros)
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
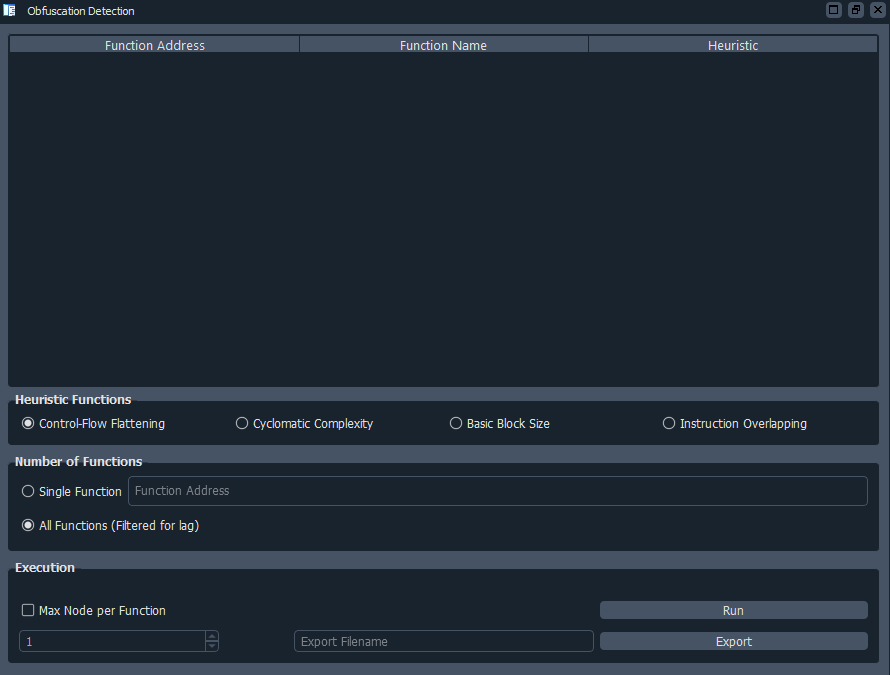 mcdulltii/obfdetect
IDA plugin for automated detection of obfuscated code and control-flow flattening in binaries using heuristic analysis and dominator tree…
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
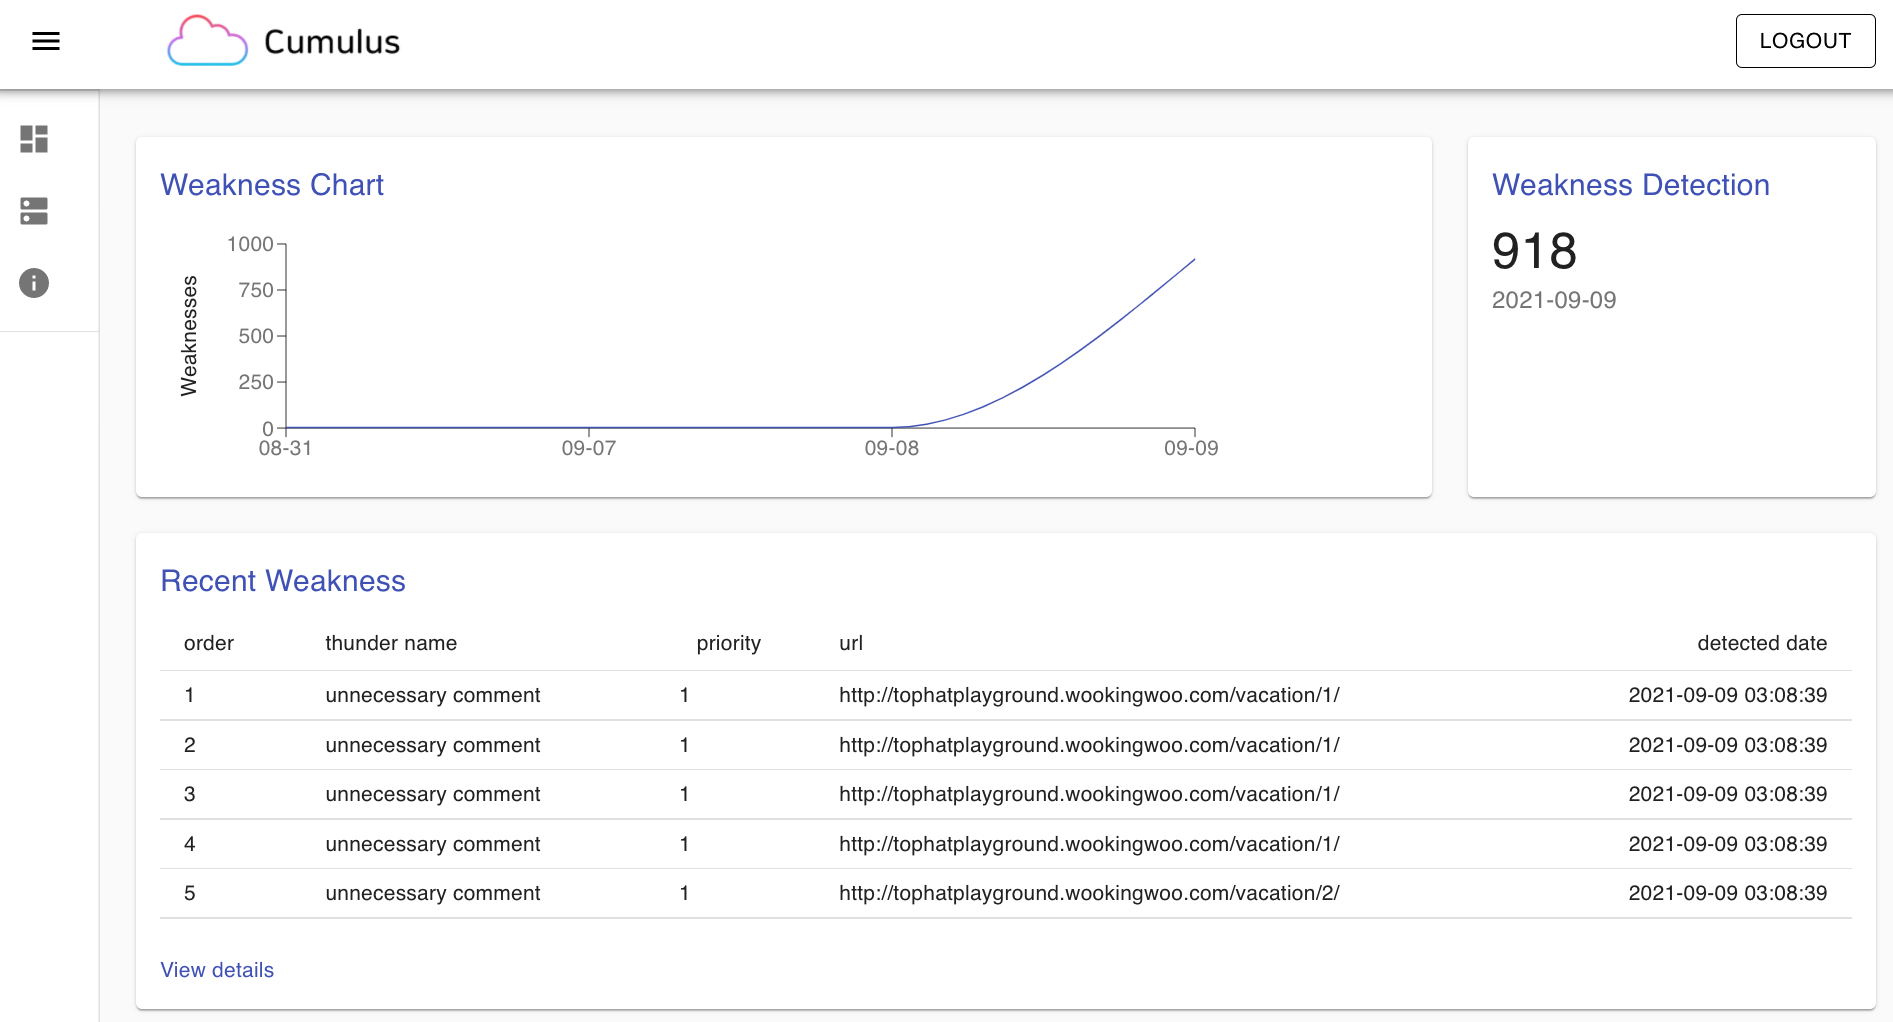 tophat-cloud/cumulus
Real-time web application weakness monitoring SDK and scanner. Detects XSS, SQL injection, sensitive payloads, and code vulnerabilities via dynamic…
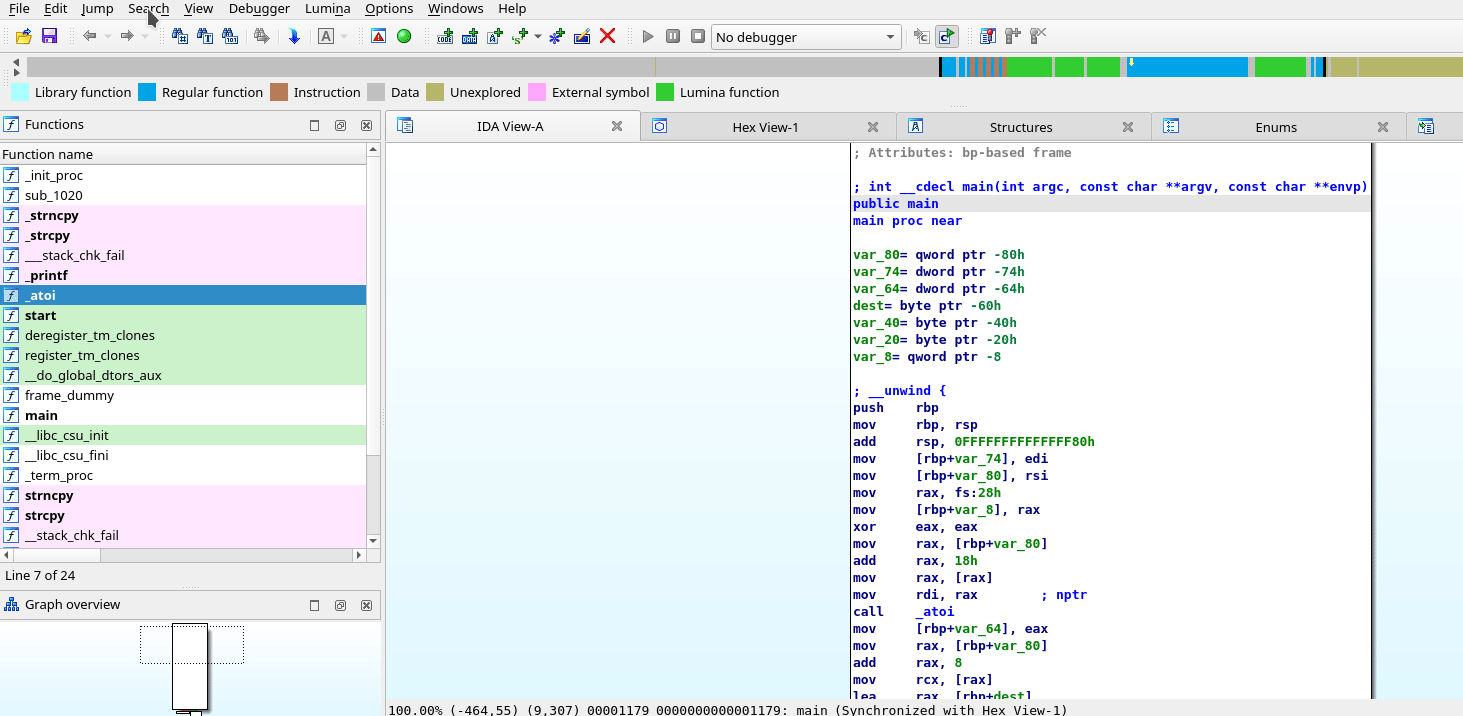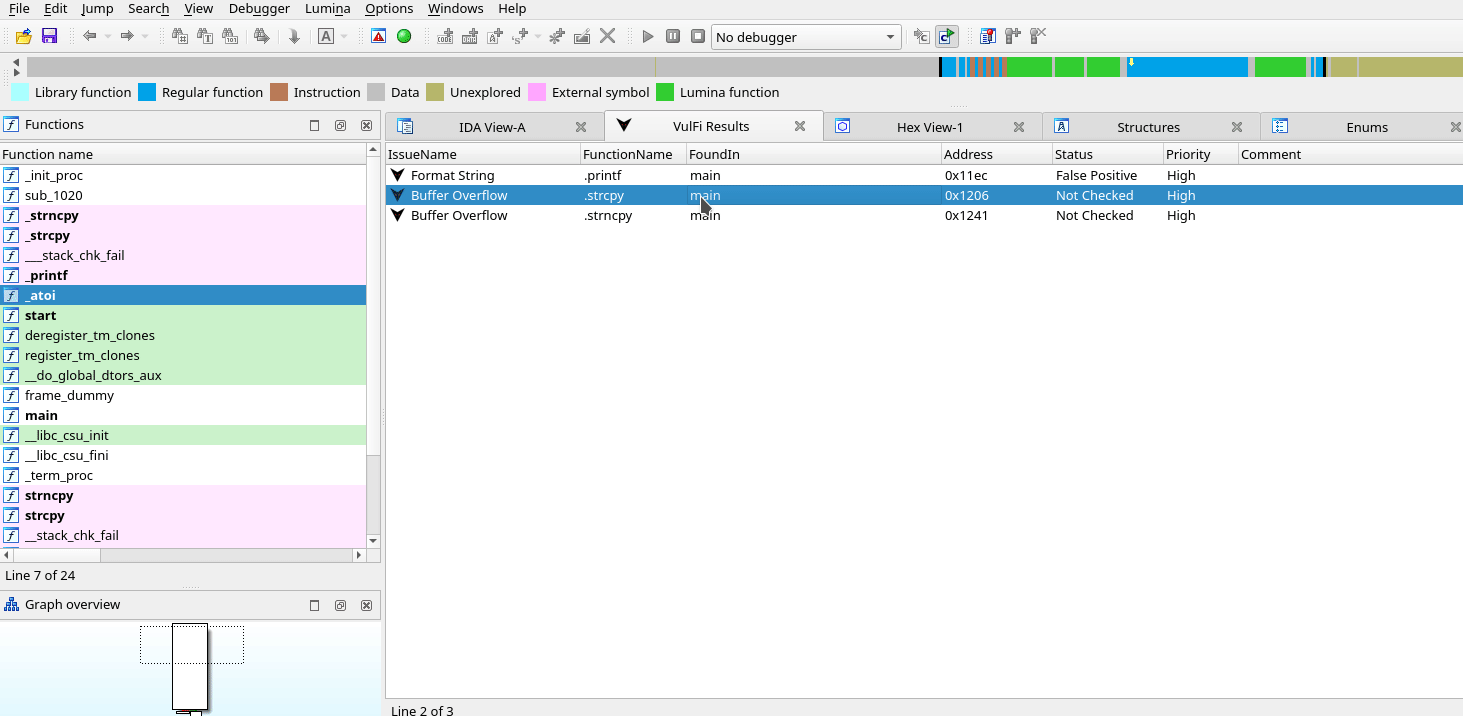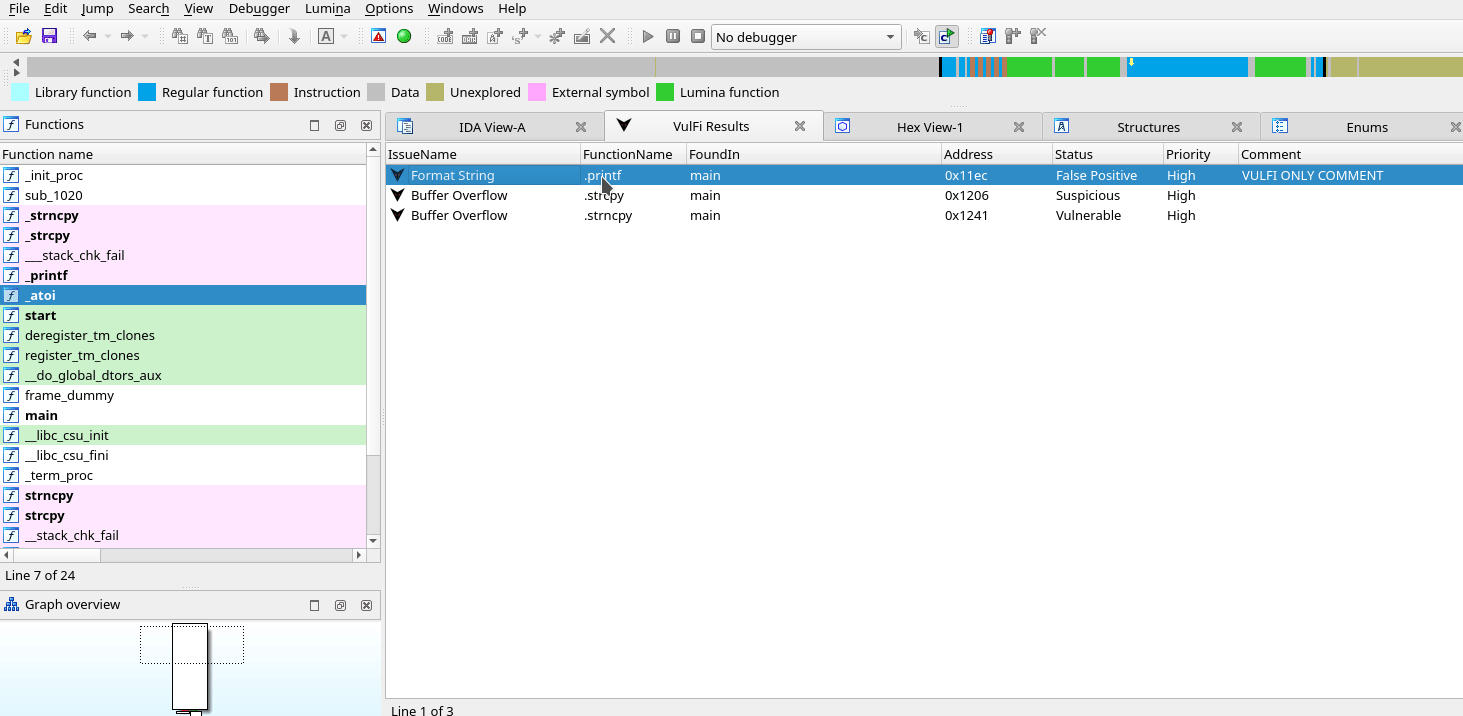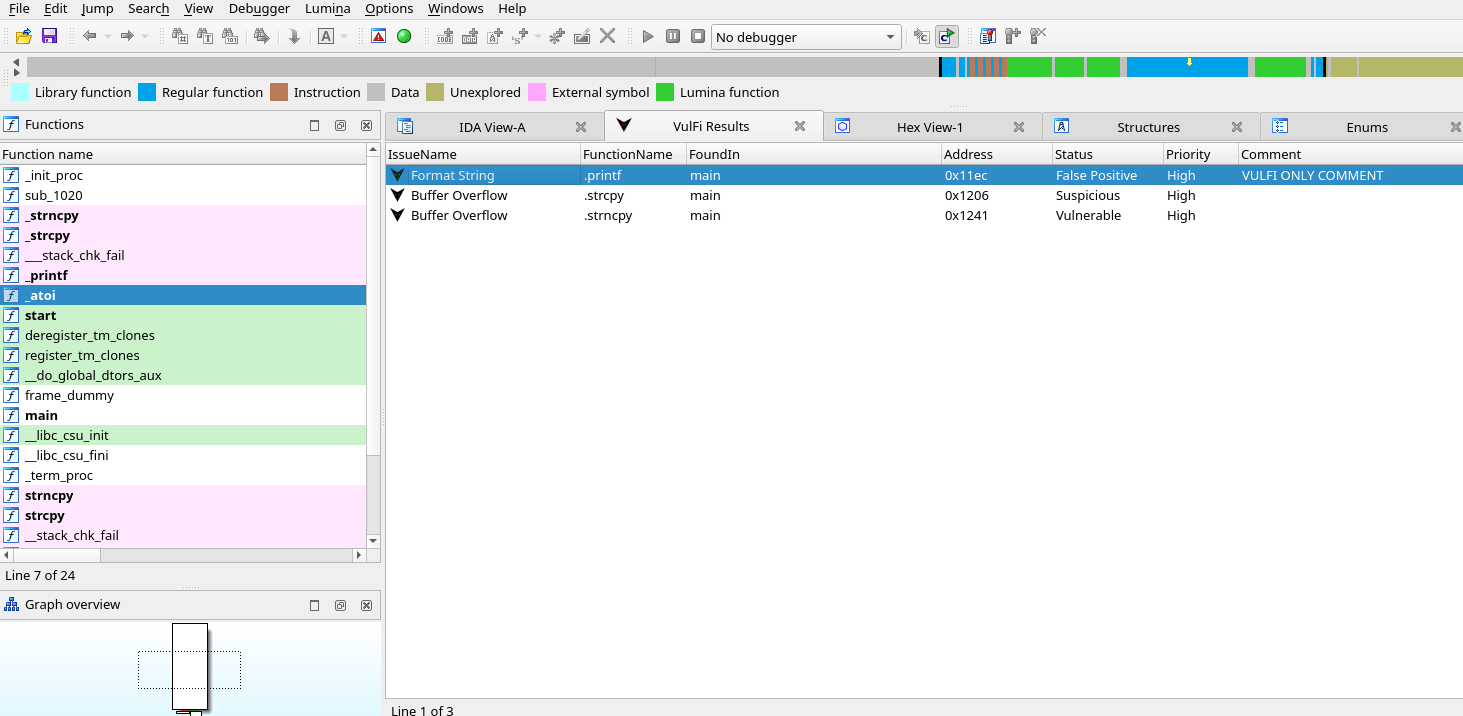 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
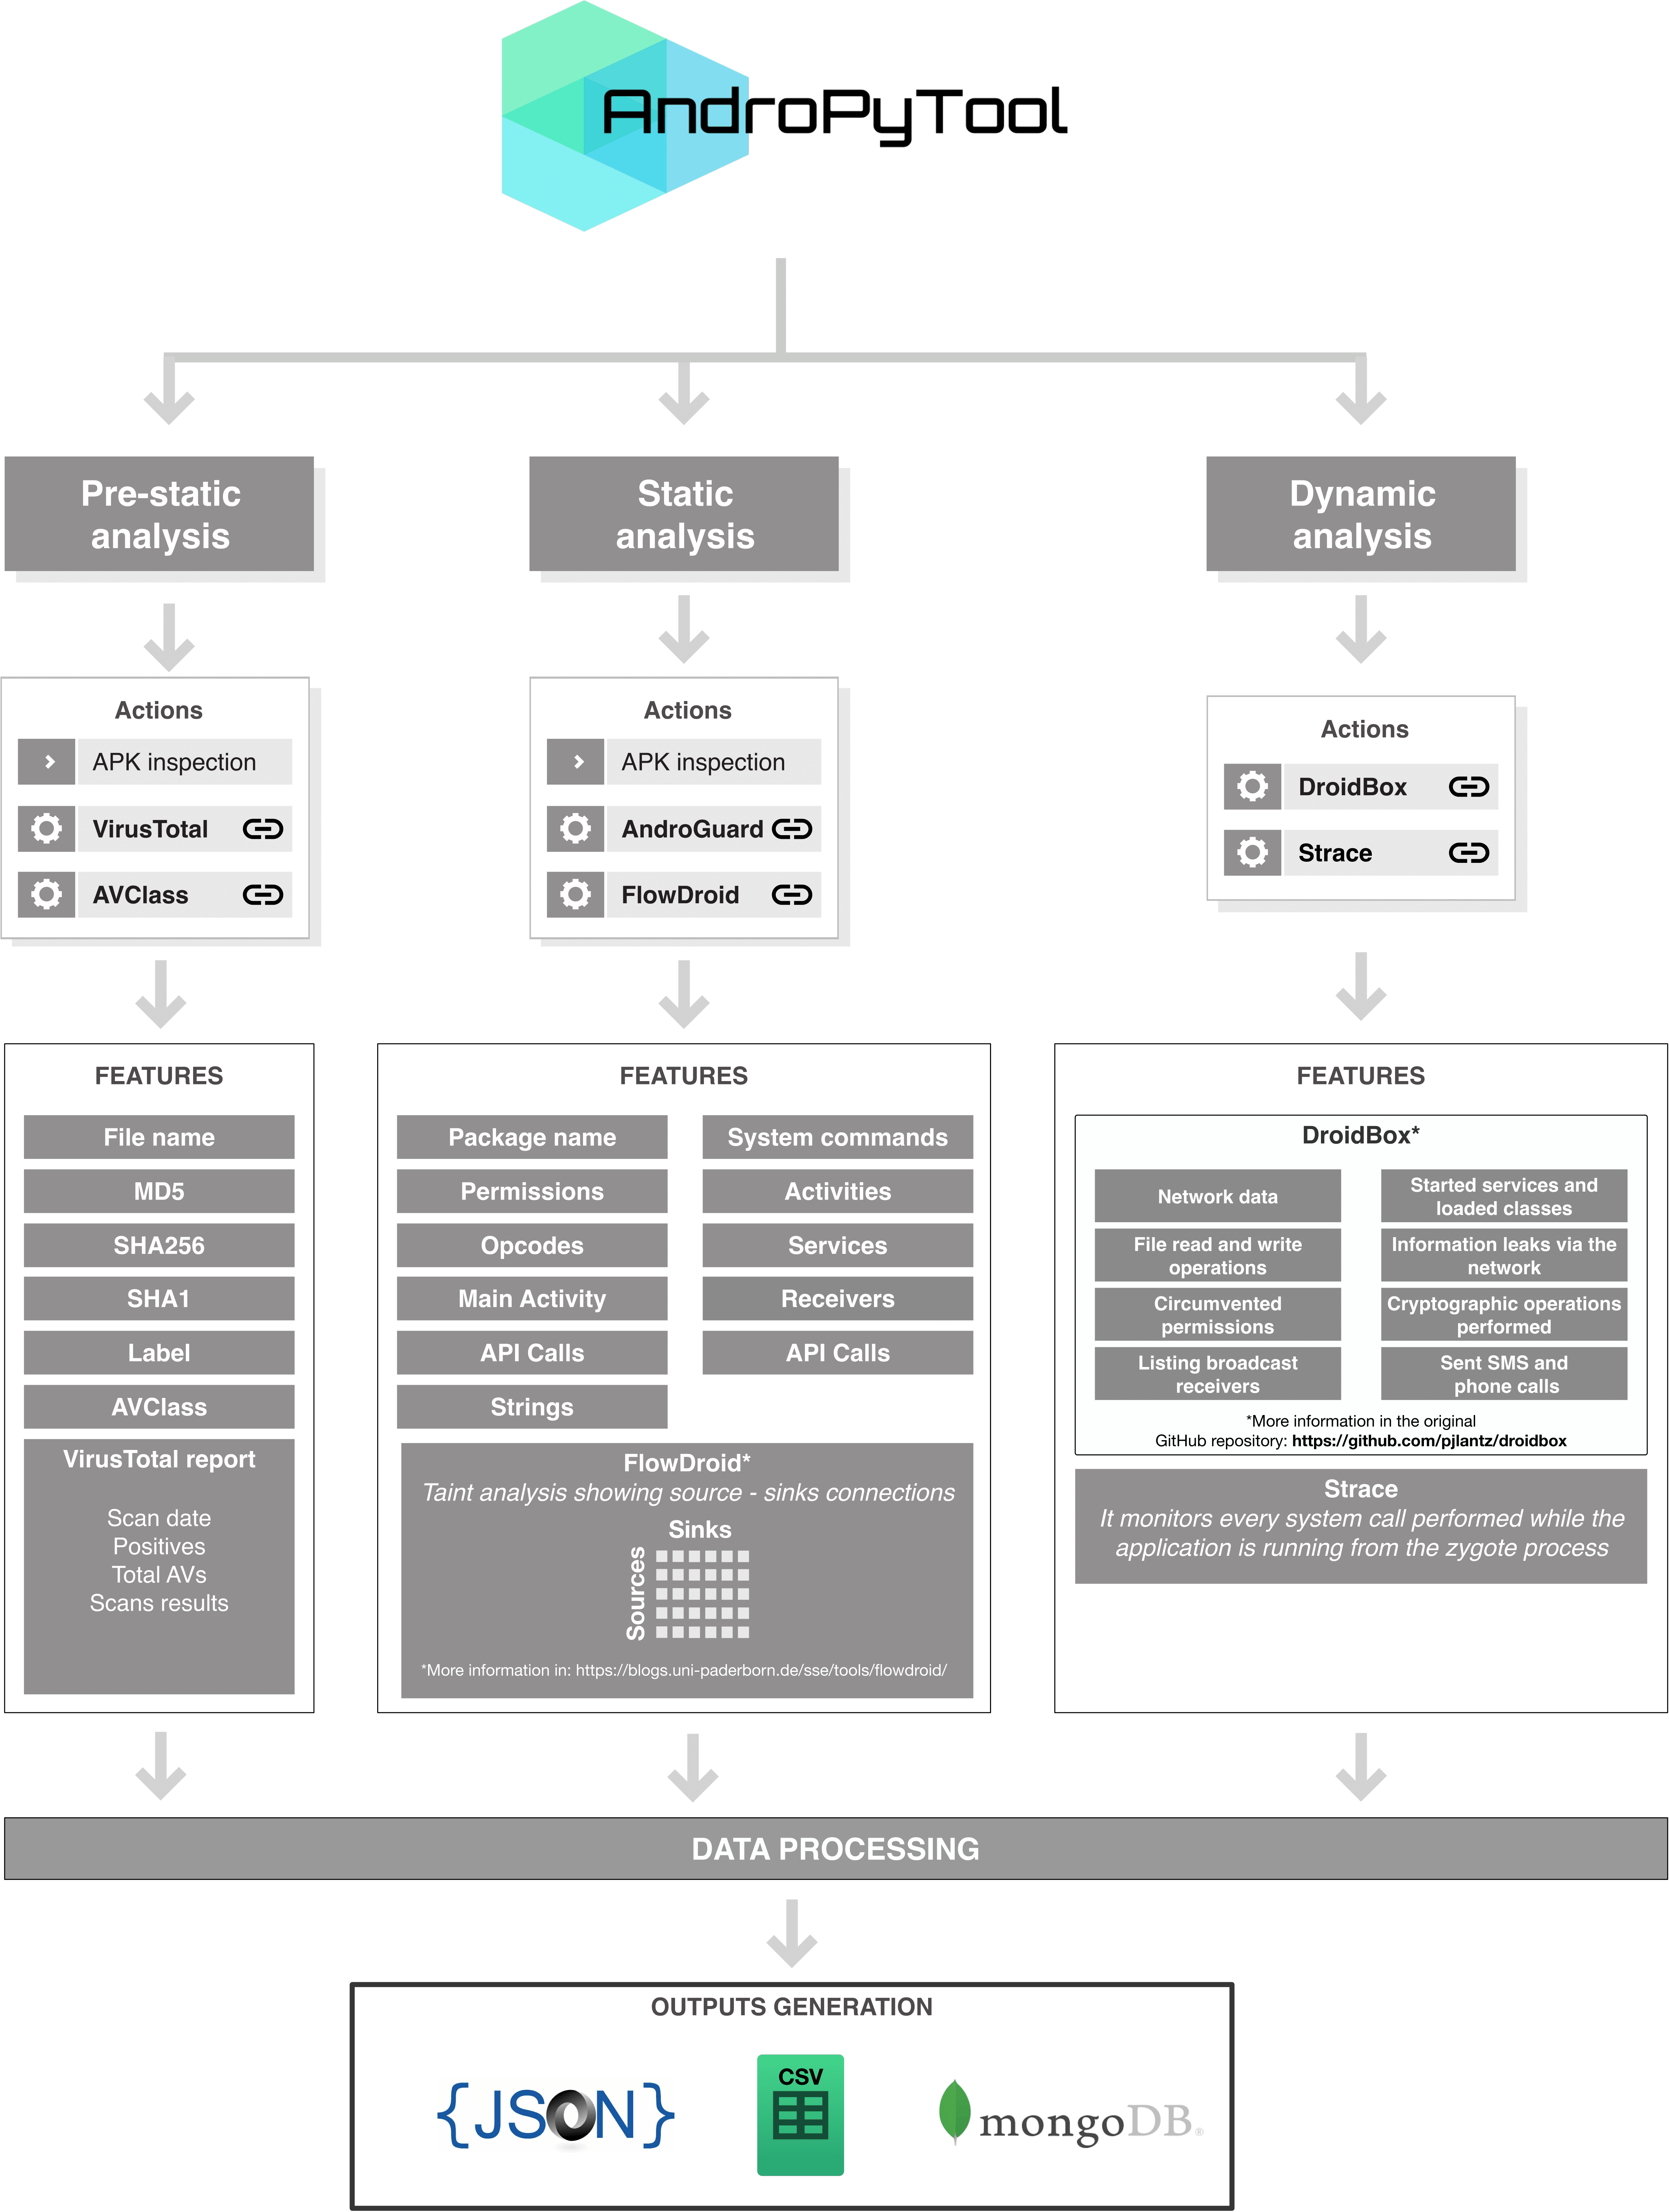 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
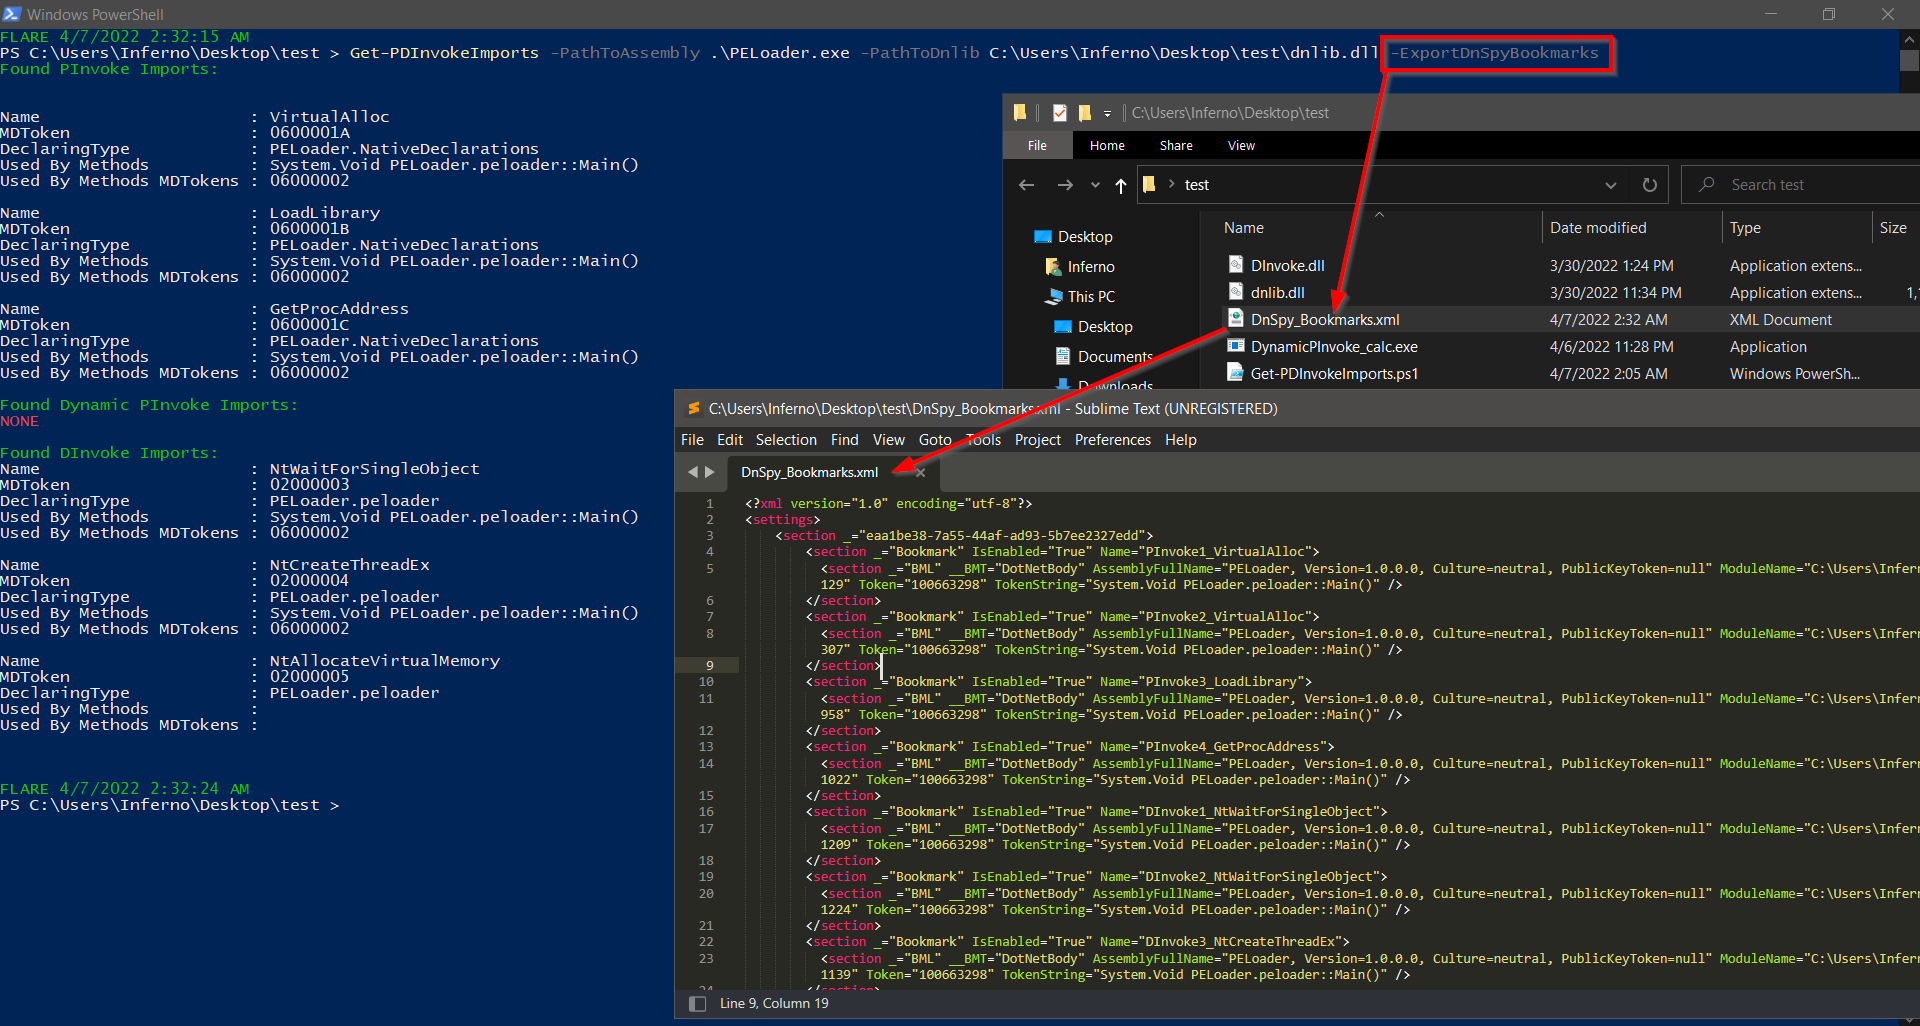 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…