

RecycledInjector
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
privilege-escalationshellcodeshellcode-generation
florylsk/recycledinjectorNative syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
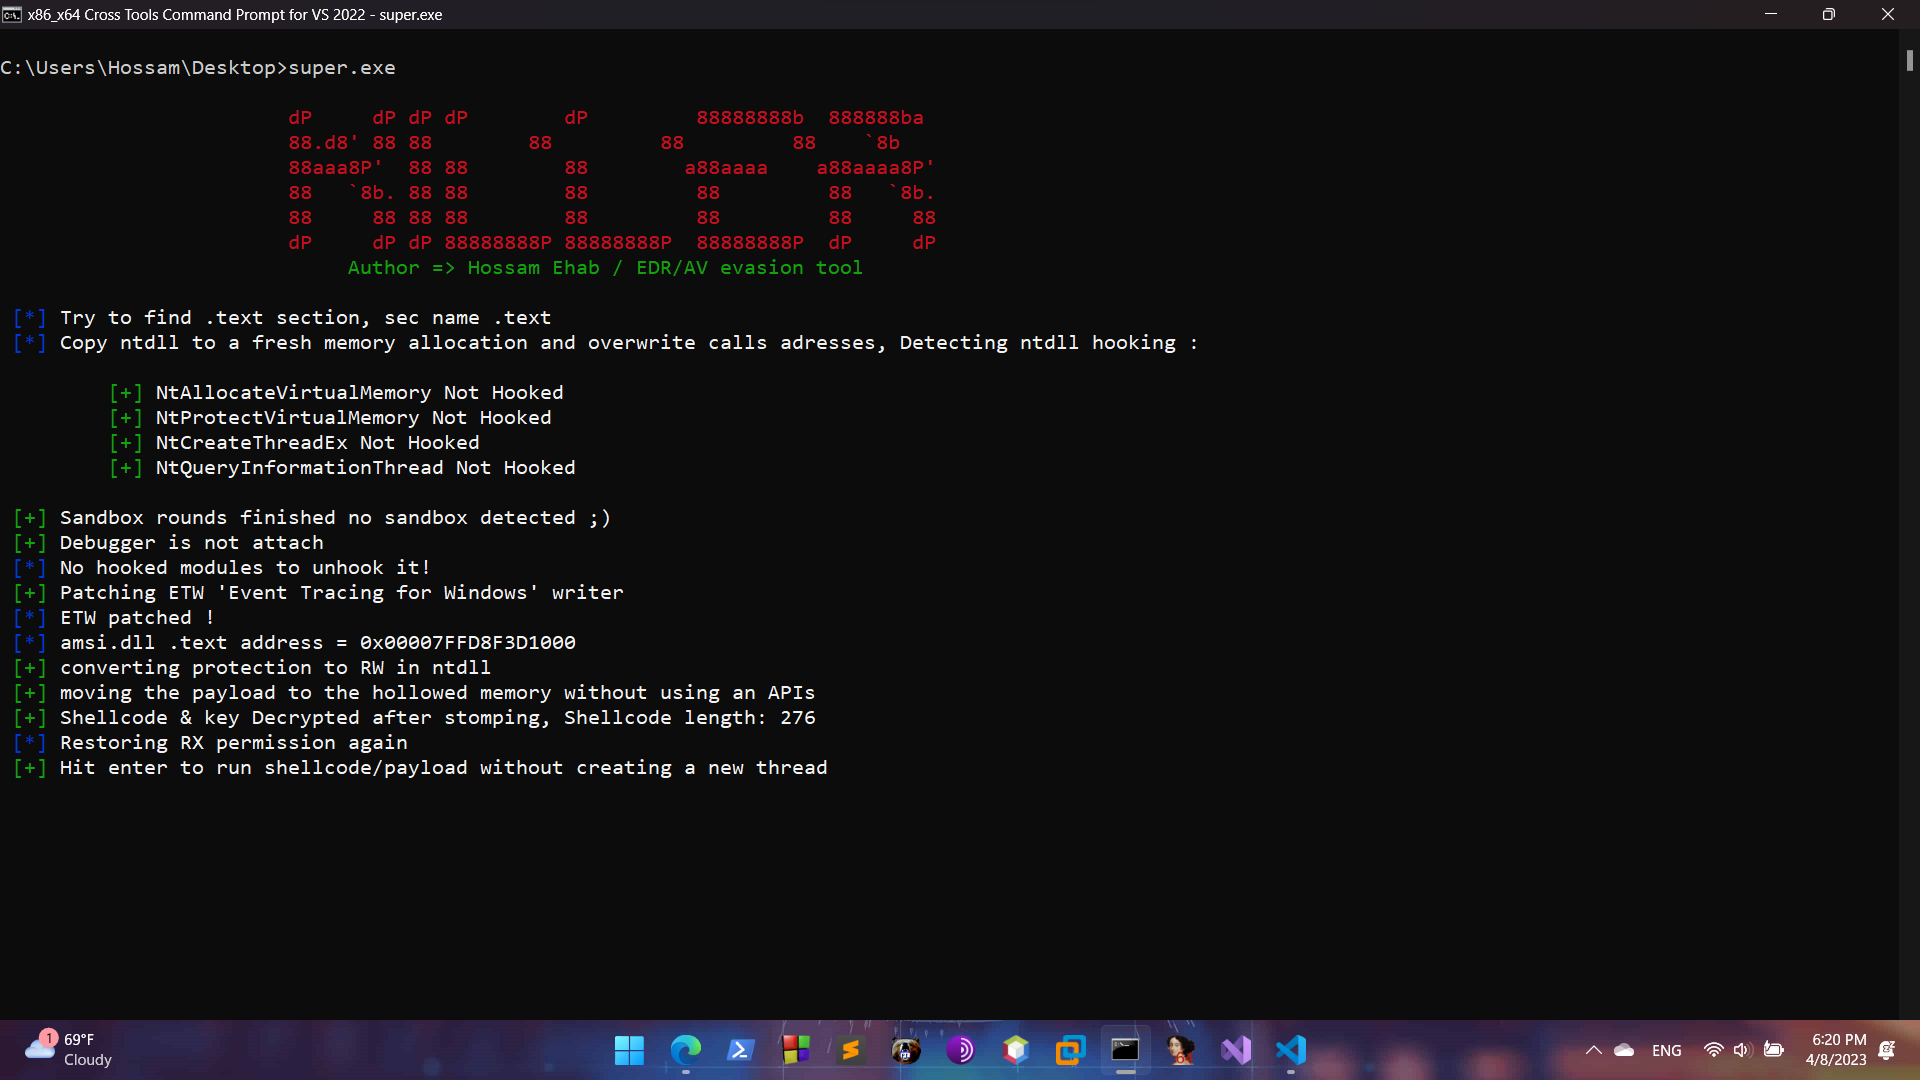 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 icyguider/nimcrypt
PE Crypter written in Nim
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…