

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
hades — Go shellcode loader that combines multiple evasion techniques | Kitploit

Tools/GitHubGitHub/f1zm0/hades
IDS/IPS EvasionShellcodeShellcode Generation
GitHubf1zm0/hades

hades

Go shellcode loader that combines multiple evasion techniques
View Repository
39146593 years agoReviewed by Kitploit
Share

Made with Go Go Reference project license project status Twitter Follow

About

Hades is a proof of concept loader that combines several evasion technques with the aim of bypassing the defensive mechanisms commonly used by modern AV/EDRs.

Usage

The easiest way, is probably building the project on Linux using make.

git clone https://github.com/f1zm0/hades && cd hades
make

Then you can bring the executable to a x64 Windows host and run it with .\hades.exe [options].

PS > .\hades.exe -h

  '||'  '||'     |     '||''|.   '||''''|   .|'''.|
   ||    ||     |||     ||   ||   ||  .     ||..  '
   ||''''||    |  ||    ||    ||  ||''|      ''|||.
   ||    ||   .''''|.   ||    ||  ||       .     '||
  .||.  .||. .|.  .||. .||...|'  .||.....| |'....|'

          version: dev [11/01/23] :: @f1zm0

Usage:
  hades -f <filepath> [-t selfthread|remotethread|queueuserapc]

Options:
  -f, --file <str>        shellcode file path (.bin)
  -t, --technique <str>   injection technique [selfthread, remotethread, queueuserapc]

Example:

Inject shellcode that spawms calc.exe with queueuserapc technique:

.\hades.exe -f calc.bin -t queueuserapc

Showcase

User-mode hooking bypass with syscall RVA sorting (NtQueueApcThread hooked with frida-trace and custom handler)
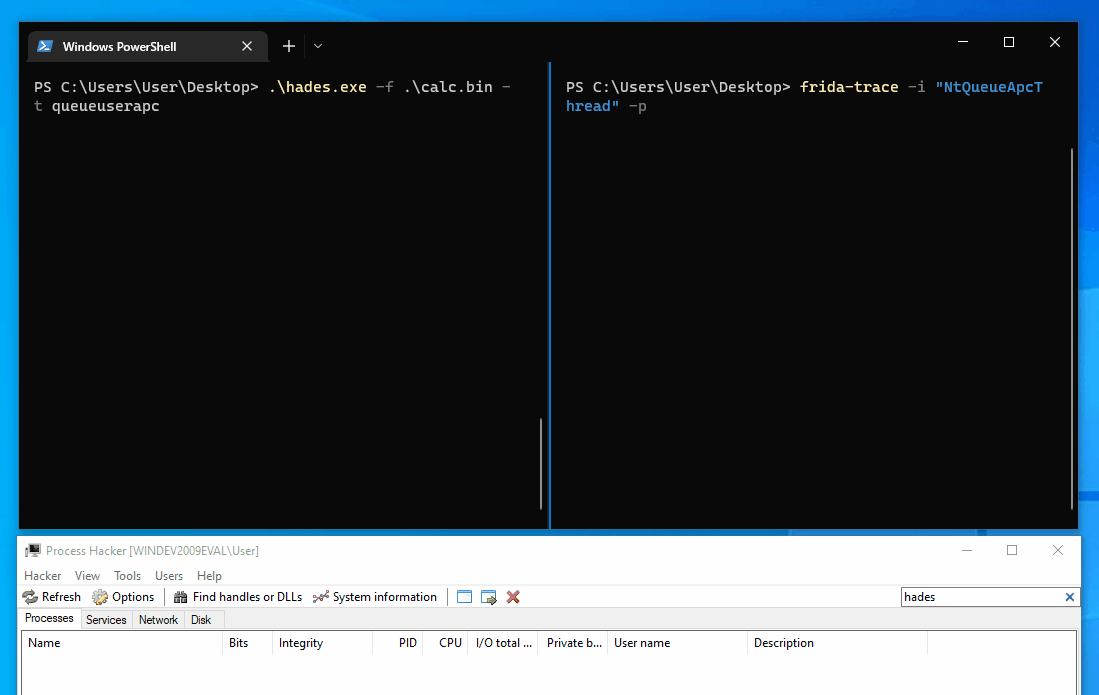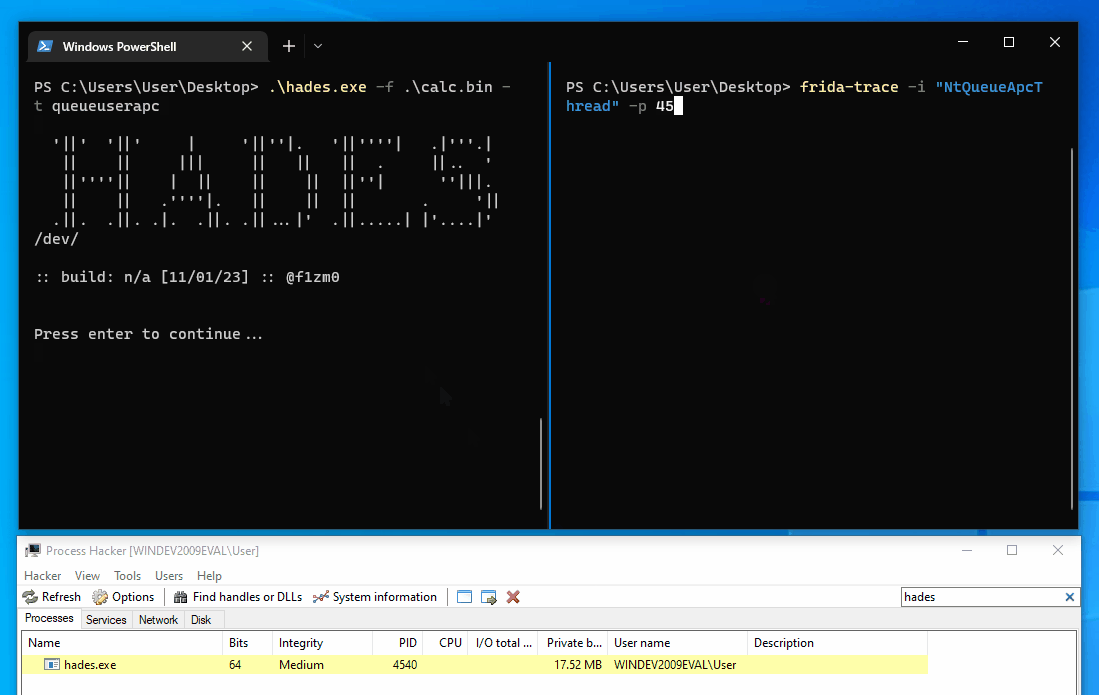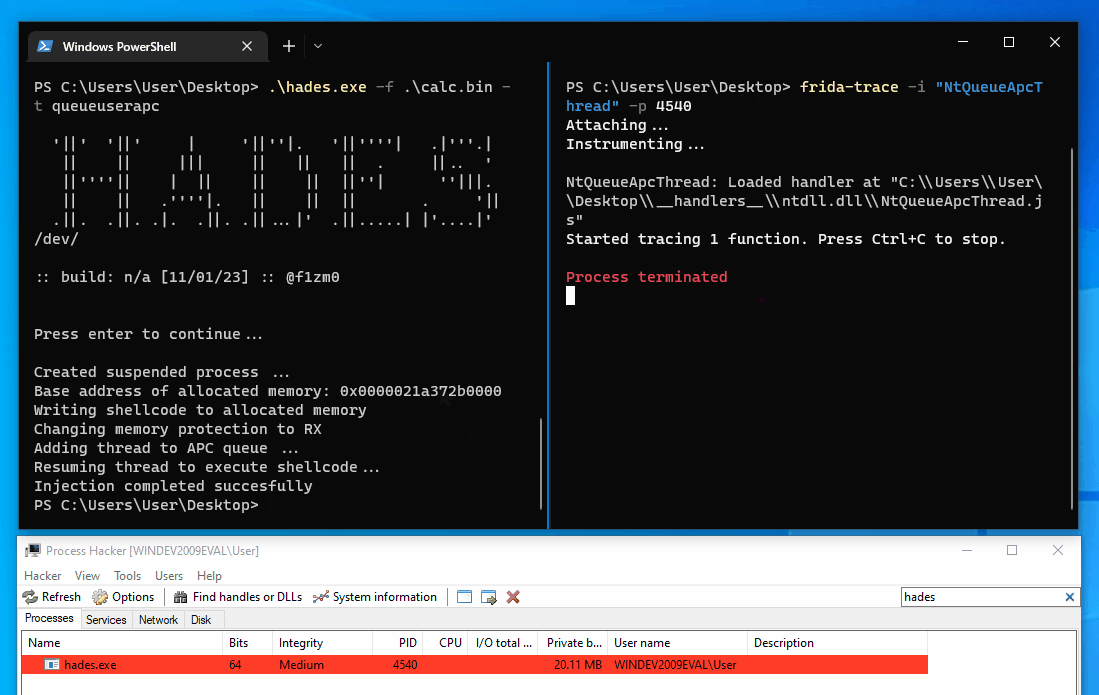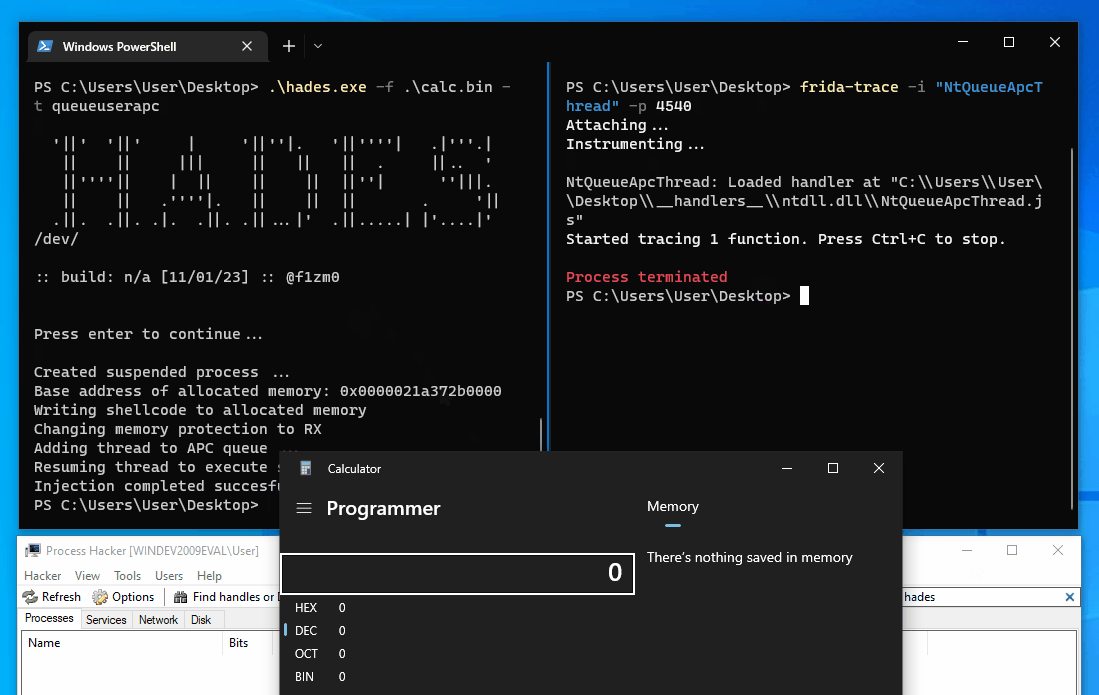
NtQueueApcThread Frida interceptor

Instrumentation callback bypass with indirect syscalls (injected DLL is from syscall-detect by jackullrich)

syscall-detect bypass

Additional Notes

Direct syscall version

In the latest release, direct syscall capabilities have been replaced by indirect syscalls provided by acheron. If for some reason you want to use the previous version of the loader that used direct syscalls, you need to explicitly pass the direct_syscalls tag to the compiler, which will figure out what files needs to be included and excluded from the build.

GOOS=windows GOARCH=amd64 go build -ldflags "-s -w" -tags='direct_syscalls' -o dist/hades_directsys.exe cmd/hades/main.go

Disclaimers

Warning
This project has been created for educational purposes only, to experiment with malware dev in Go, and learn more about the unsafe package and the weird Go Assembly syntax. Don't use it to on systems you don't own. The developer of this project is not responsible for any damage caused by the improper use of this tool.

Credits

Shoutout to the following people that shared their knowledge and code that inspired this tool:

  • @smelly__vx and @am0nsec creators of Hell's Gate
  • @modexp's excellent blog post Bypassing User-Mode Hooks and syscall invocation in C
  • @ElephantSe4l creator of FreshyCalls
  • @C_Sto creator of BananaPhone
  • @winternl for this blog post on Hooking Nirvana and instrumentation callback to detect suspicious syscalls from user-mode.

License

This project is licensed under the GPLv3 License - see the LICENSE file for details

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →





