
PayloadAutomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…

Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…

Sophos-originated indicators-of-compromise from published reports

Just my findings of malwares

Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.

This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.

Collects and organizes malware indicators of compromise (IOCs) for rapid threat detection, incident response, and actionable intelligence sharing.

Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.

Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…

Active C2 IoCs

This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

This repository contains indicators of compromise (IOCs) of our various investigations.

Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…

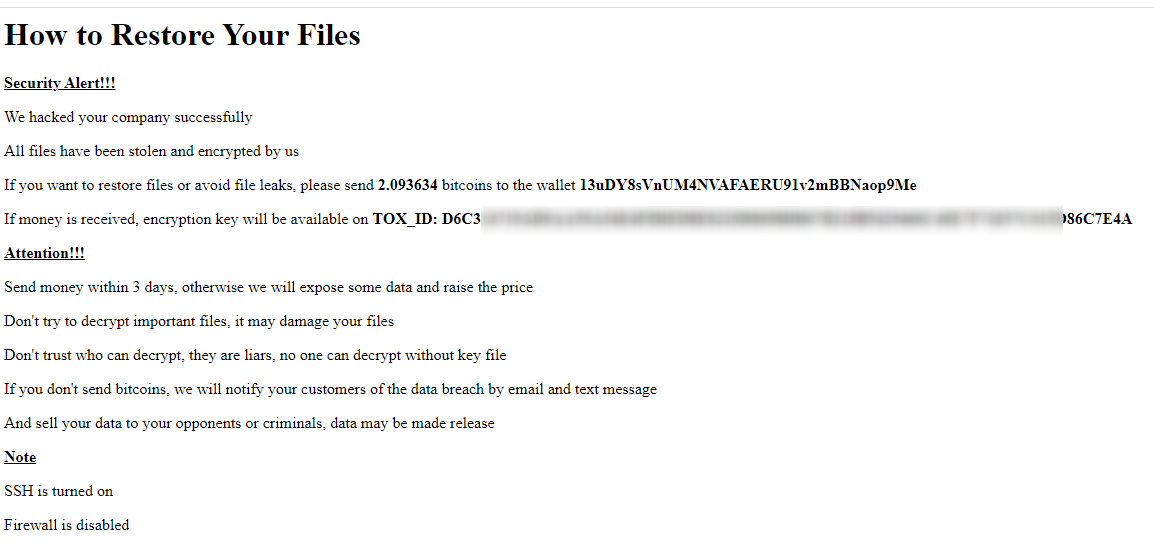
ESXi semi-automated ransomware attacks bitcoin wallets

Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.


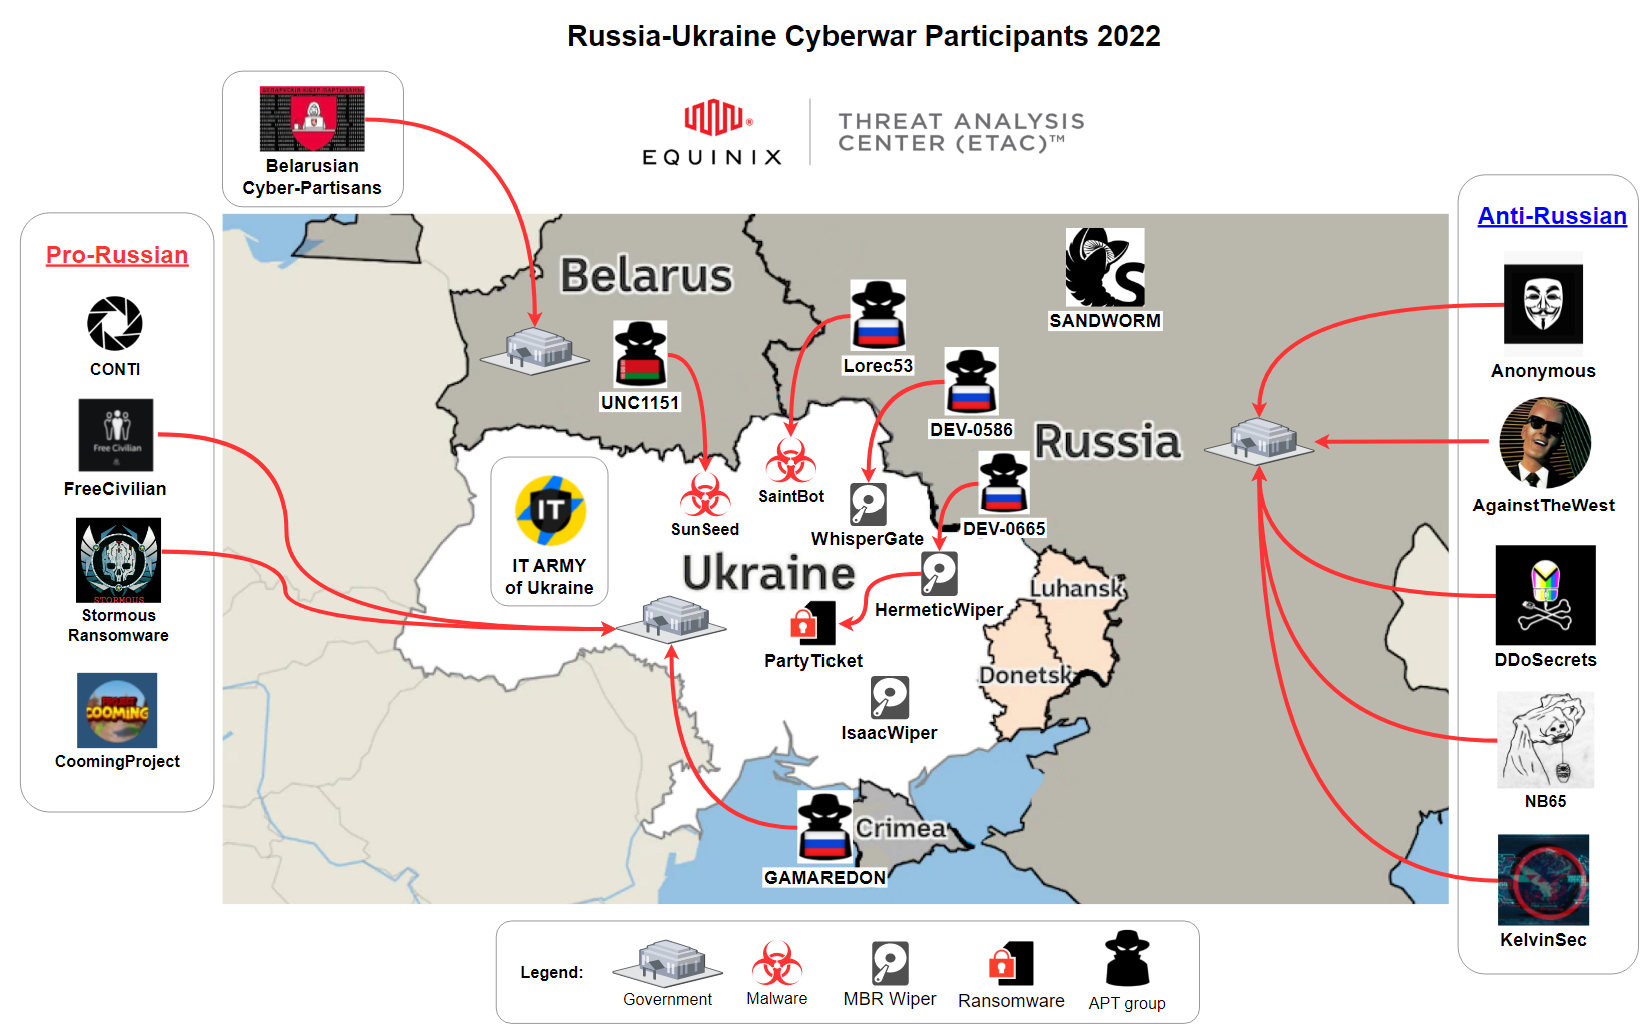
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…