Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Ukraine-Cyber-Operations — Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional free threat intelligence. Slava Ukraini. Glory to Ukraine. | Kitploit
Tools/GitHubGitHub/curated-intel/ukraine-cyber-operations
Indicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Threat Feeds & AggregatorsMalware AnalysisThreat IntelligenceCurated Resources
GitHubcurated-intel/ukraine-cyber-operations

Ukraine-Cyber-Operations

Share

Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional free threat intelligence. Slava Ukraini. Glory to Ukraine.

View RepositoryWebsite
93589433 years agoReviewed by Kitploit

logo

Ukraine Cyber Operations

Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional free threat intelligence. Slava Ukraini. Glory to Ukraine. (Blog | Twitter | LinkedIn)

Resources

  • Timeline of 2022 Threat Reports

    • January Threat Reports

    • February Threat Reports

    • March Threat Reports

    • April Threat Reports

    • May Threat Reports

    • June Threat Reports

    • July Threat Reports

    • August Threat Reports

    • September Threat Reports

    • October Threat Reports

    • November Threat Reports

    • December Threat Reports

  • Timeline of 2023 Threat Reports

    • January Threat Reports

    • February Threat Reports

    • April Threat Reports

    • May Threat Reports

    • June Threat Reports

  • Vendor Support

  • Vetted OSINT Sources

  • Miscellaneous Resources

  • Equinix Threat Analysis Center (ETAC) contributions:

    • Contextualized Indicators of Compromise (IOCs) by ETAC (Last updated 25 March 2022)
    • Contextualized CERT-UA IOCs - see here (Last updated 28 March 2022)
    • Vetted YARA rule collection by ETAC (Last updated 4 April 2022)
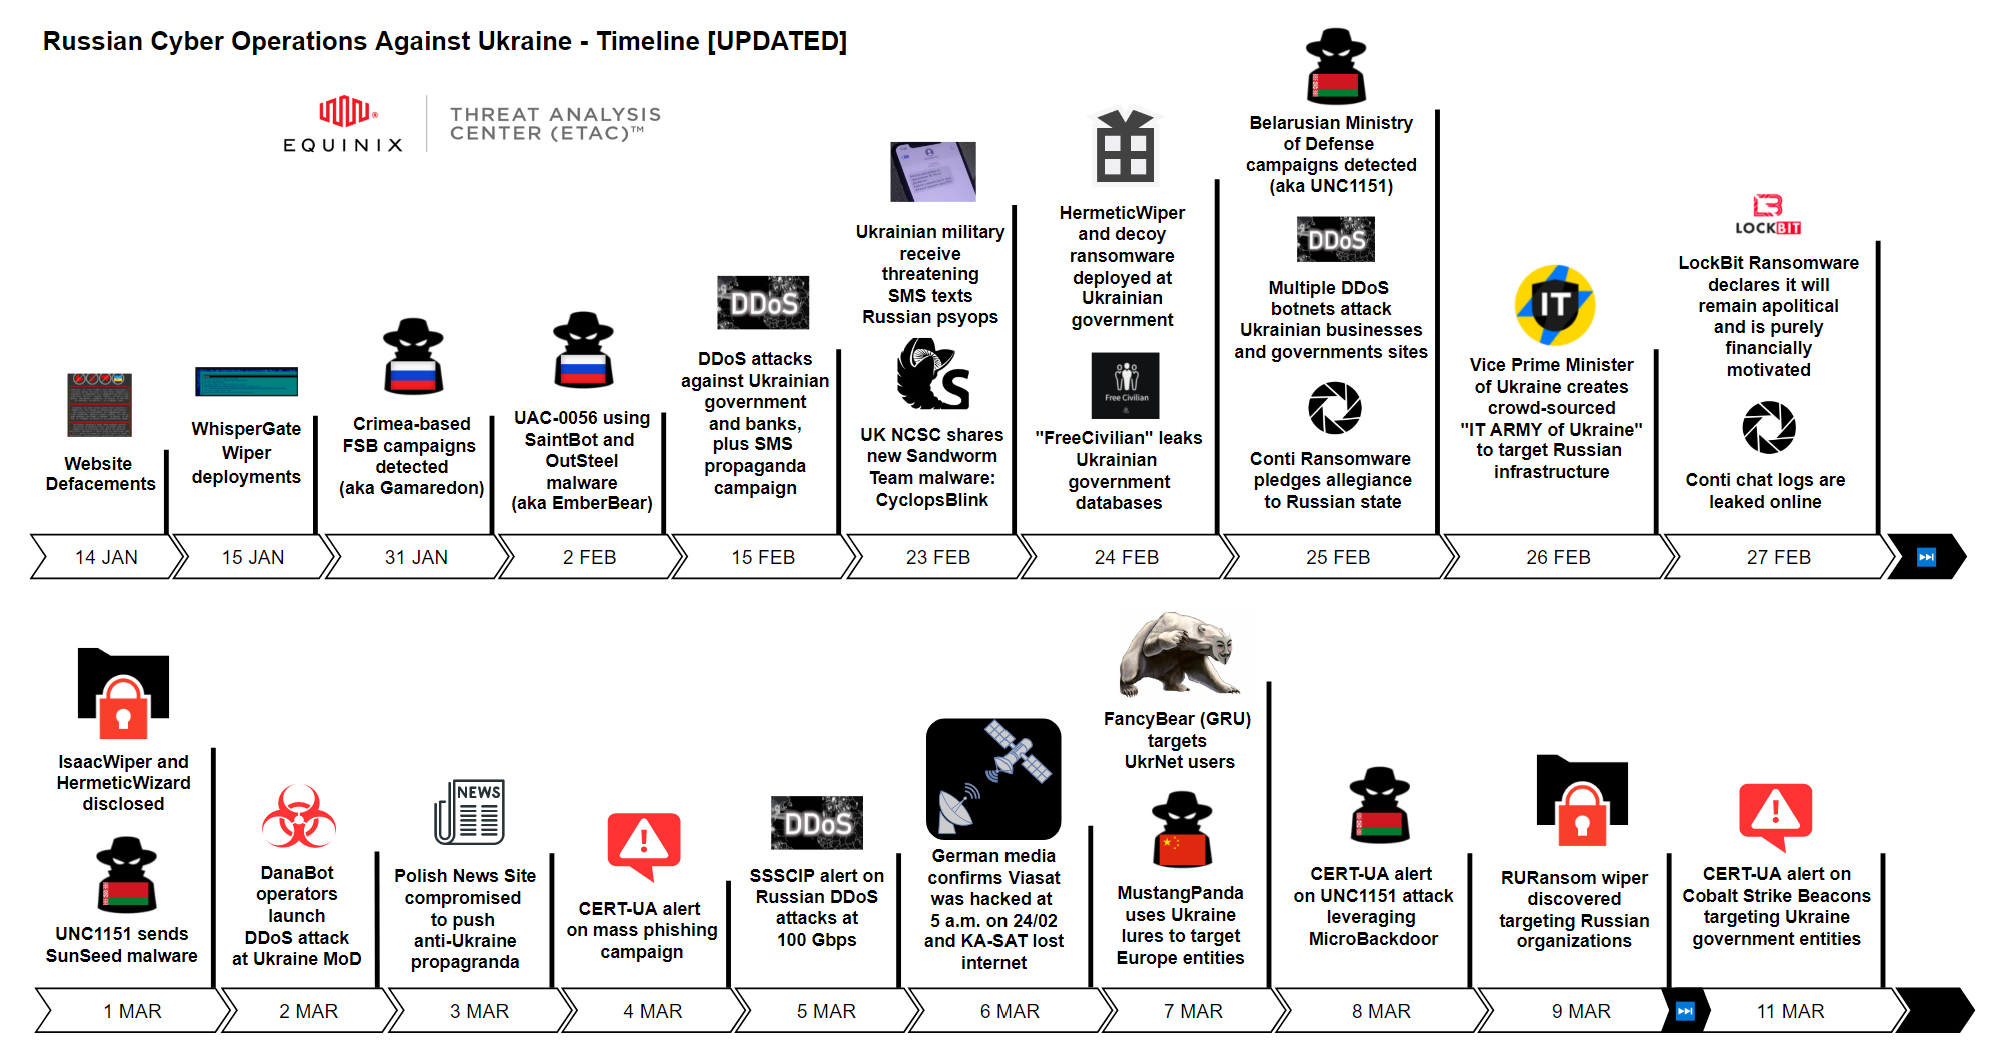
    • Graphic of a Timeline of Russia-Ukraine Cyberwar (Last updated 14 March 2022)
    • Graphic of a Map of Russia-Ukraine Cyberwar (Last updated 3 March 2022 )
  • KPMG-Egyde Contributions:

    • Added loosely-vetted IOC Threat Hunt Feeds (h/t 0xDISREL) (Last updated 7 April 2022)
    • IOCs shared by these feeds are LOW-TO-MEDIUM CONFIDENCE we strongly recommend NOT adding them to a blocklist
    • These could potentially be used for THREAT HUNTING and could be added to a WATCHLIST
    • IOCs are generated in MISP COMPATIBLE CSV format
    • Additional Threat Hunt Feed for recently registered Ukrainian domain names (h/t DomainTools)
    • Additional Threat Hunt Feed for threat groups targeting Ukraine (h/t RecordedFuture)
    • Ukrainain organizations offered by Access and Data Brokers on underground forums

Graphics by ETAC

timeline

cyberwar

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →