
openocd
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
embedded-systems-securityreverse-engineeringdebuggers+4
openocd-org/openocdOfficial OpenOCD Read-Only Mirror (no pull requests)
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
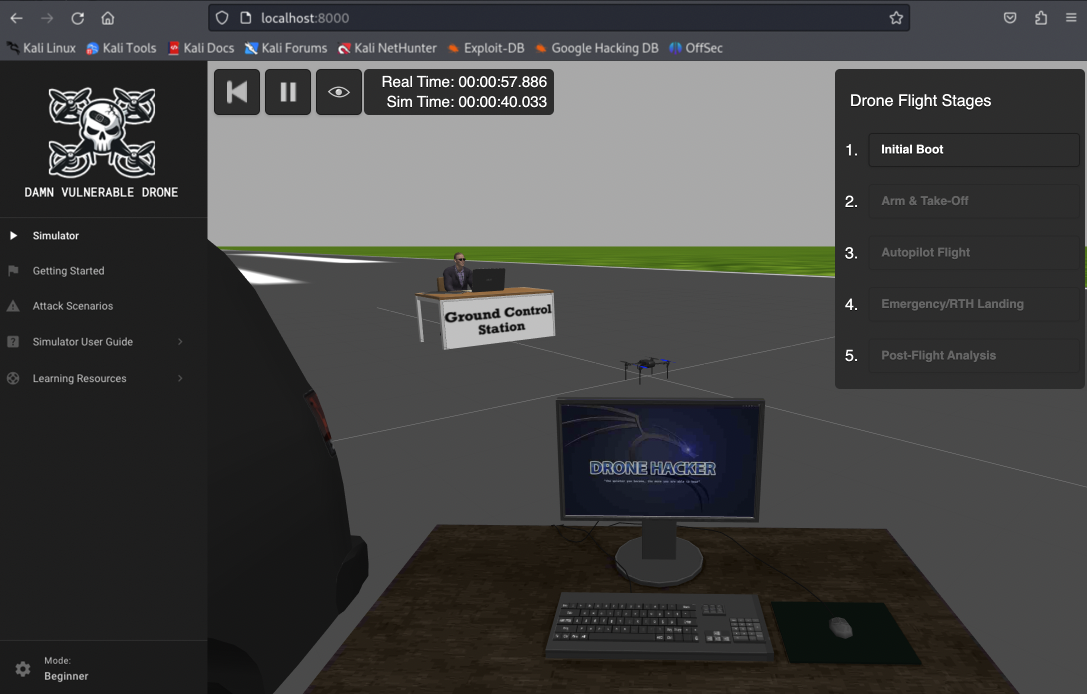 nicholasaleks/damn-vulnerable-drone
Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…
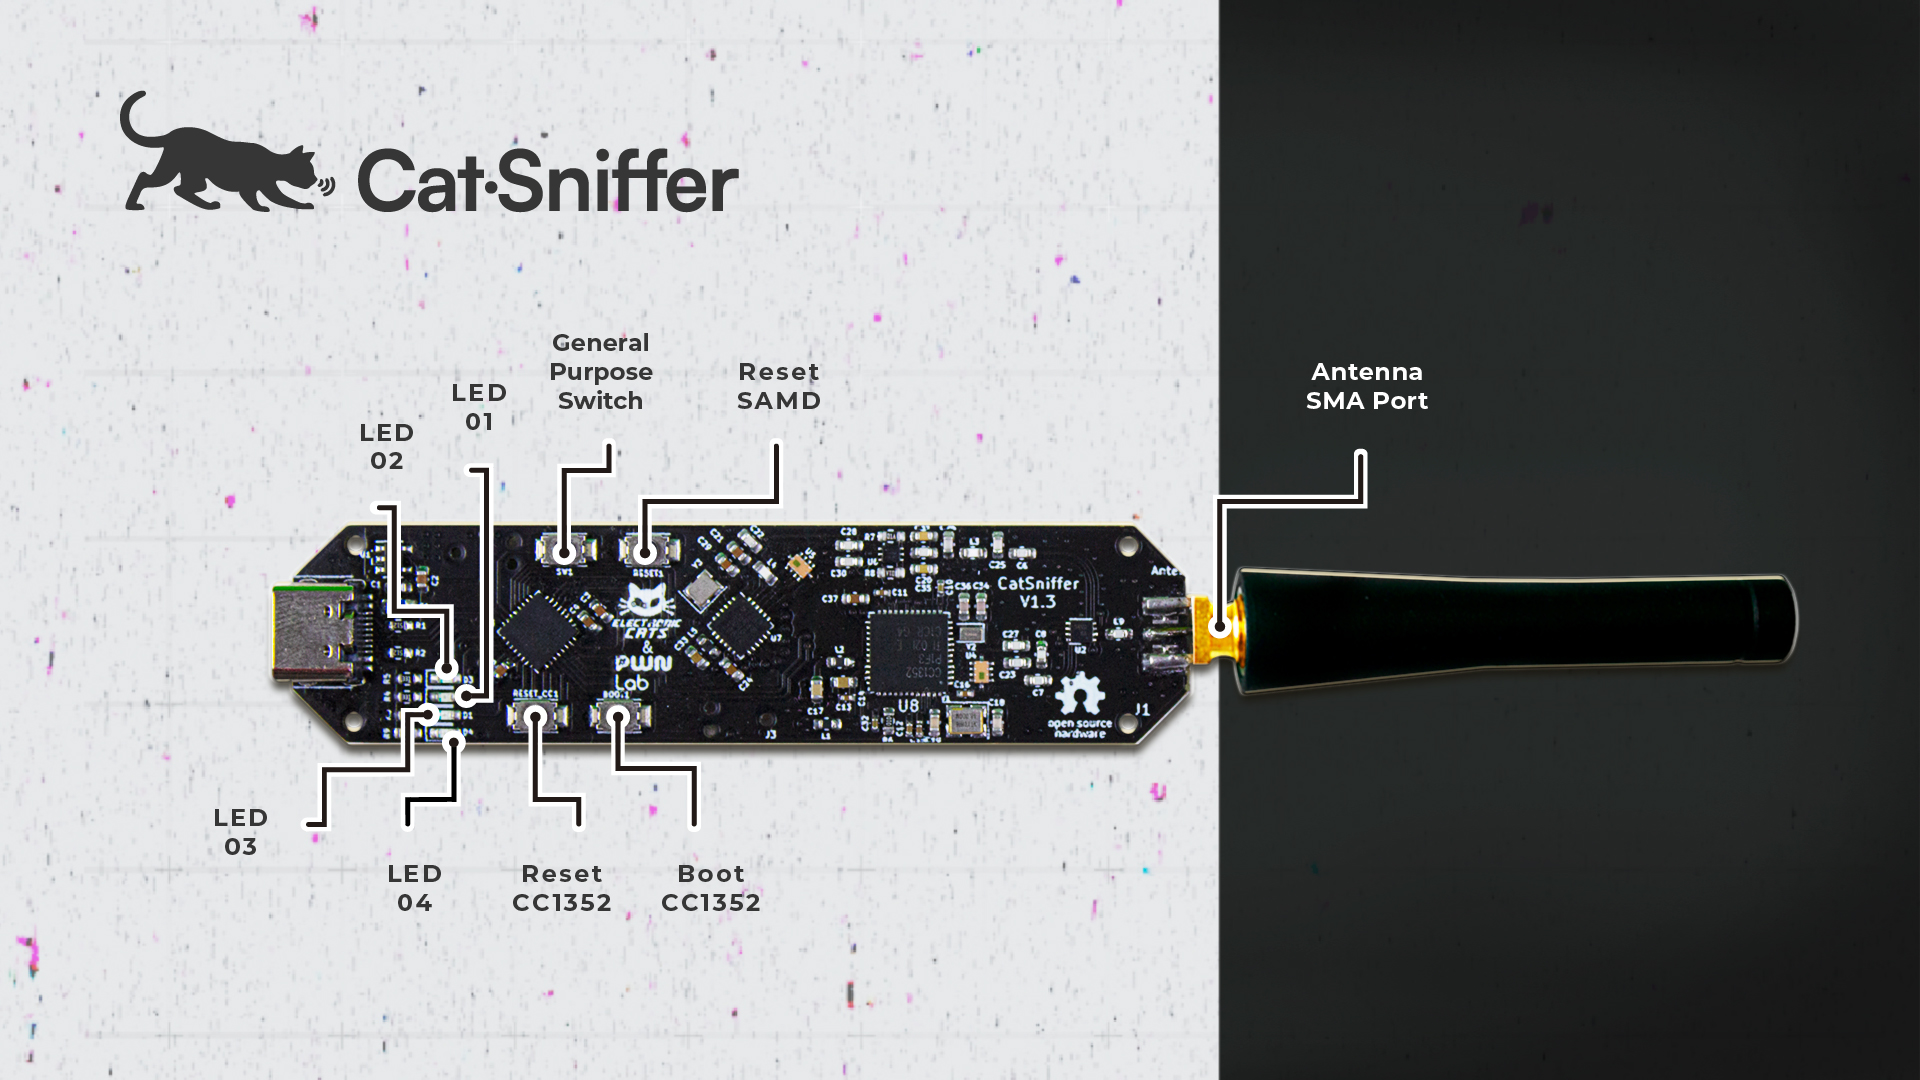 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
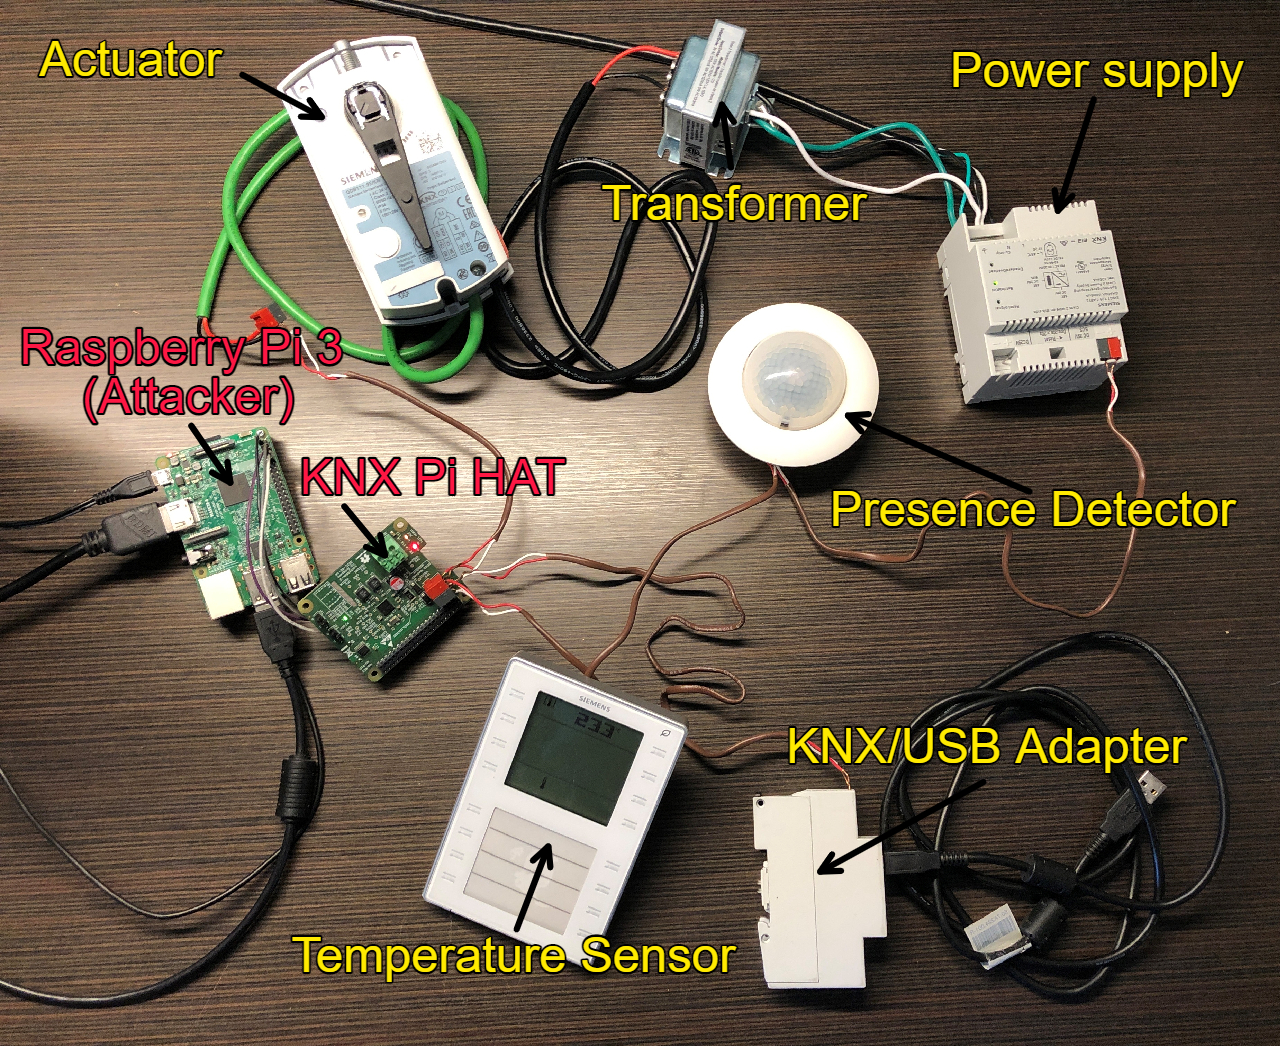 chrism09/knx-bus-dump
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 souravbaghz/carpunk
CAN bus injection toolkit for automotive security testing. Performs interface control, sniffing, and CAN injection attacks on vehicle networks,…
 e-m-b-a/emba
EMBA - The firmware security analyzer
 cr0n1c/dlink_shell_poc
Dlink 615/815 shell PoC
 snawoot/hisilicon-dvr-telnet
PoC materials for article https://habr.com/en/post/486856/
 trungnguyen1909/qemu-t8030
iPhone 11 emulated on QEMU
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 aliasrobotics/aztarna
aztarna, a footprinting tool for robots.
 osqzss/bladegps
Real-time GPS signal simulator for bladeRF
 evilsocket/bleah
This repository is DEPRECATED, please use bettercap as this tool has been ported to its BLE modules.
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 osqzss/gps-sdr-sim
Software-Defined GPS Signal Simulator