
fwknop
 mrash/fwknop
Single Packet Authorization > Port Knocking
authentication-authorizationdefensive-toolsencryption-decryption-tools+3
mrash/fwknopSingle Packet Authorization > Port Knocking
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 magic-wormhole/magic-wormhole
get things from one computer to another, safely
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 nullarray/netset
Operational Security utility and automator.
 alberties/ghostfuscator
The Python Password-Protected Obfuscator
 rejithregi-group/securityproject
Python Security Project that implements a file encryption and decryption tool
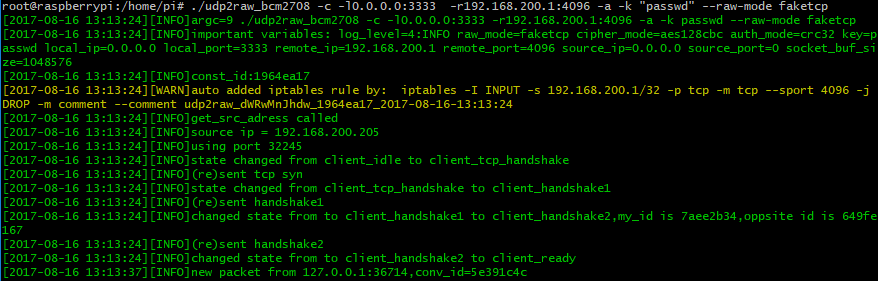 wangyu-/udp2raw
A Tunnel which Turns UDP Traffic into Encrypted UDP/FakeTCP/ICMP Traffic by using Raw Socket,helps you Bypass UDP FireWalls(or Unstable UDP…
 nodesocket/cryptr
A simple shell utility for encrypting and decrypting files using scrypt.
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 lockedbyte/cryptovenom
Cryptovenom: The Cryptography Swiss Army Knife
 devploit/xorpass
Encoder to bypass WAF filters using XOR operations.