
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Disk Forensics — Tools — Page 2 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
74 results
KapeFiles preview

KapeFiles

GitHubericzimmerman/kapefiles

This repository serves as a place for community created Targets and Modules for use with KAPE.
disk-forensicsforensicsdigital-forensics+2
864
5 days ago
hashr preview

hashr

GitHubgoogle/hashr

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
disk-forensicshash-analysisforensics+2
1308 months ago
Volumiser preview

Volumiser

GitHubccob/volumiser

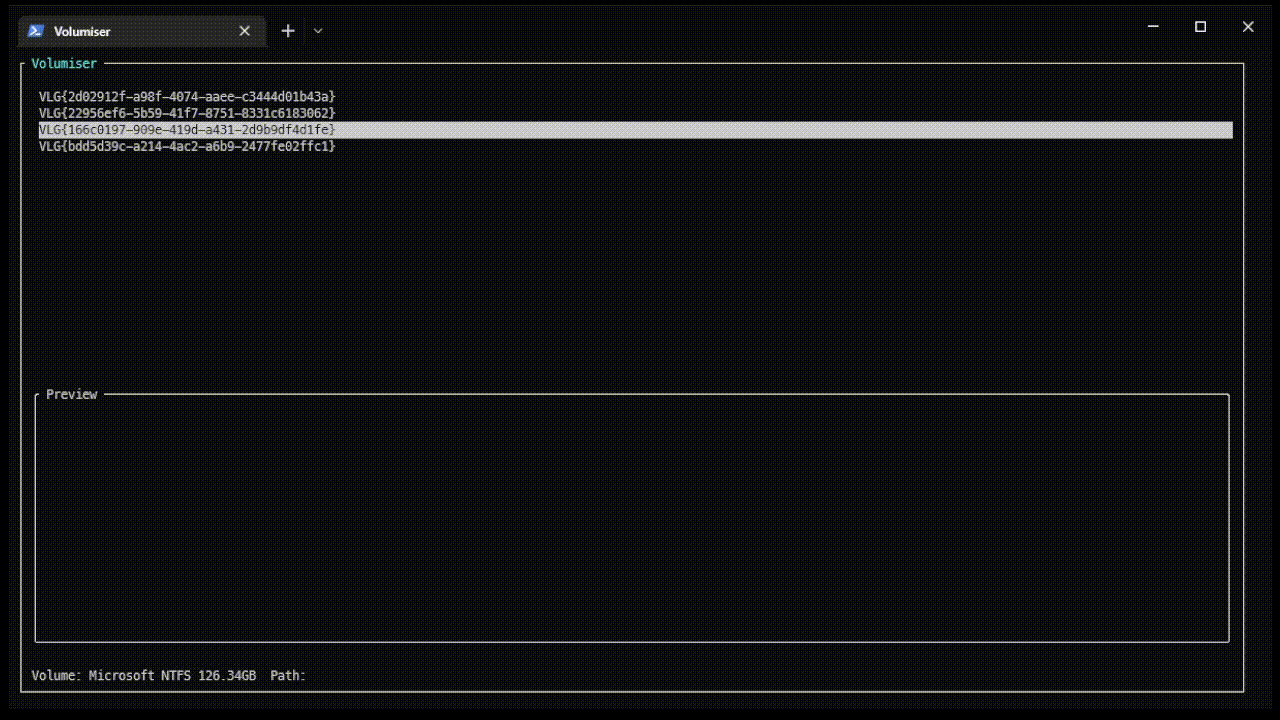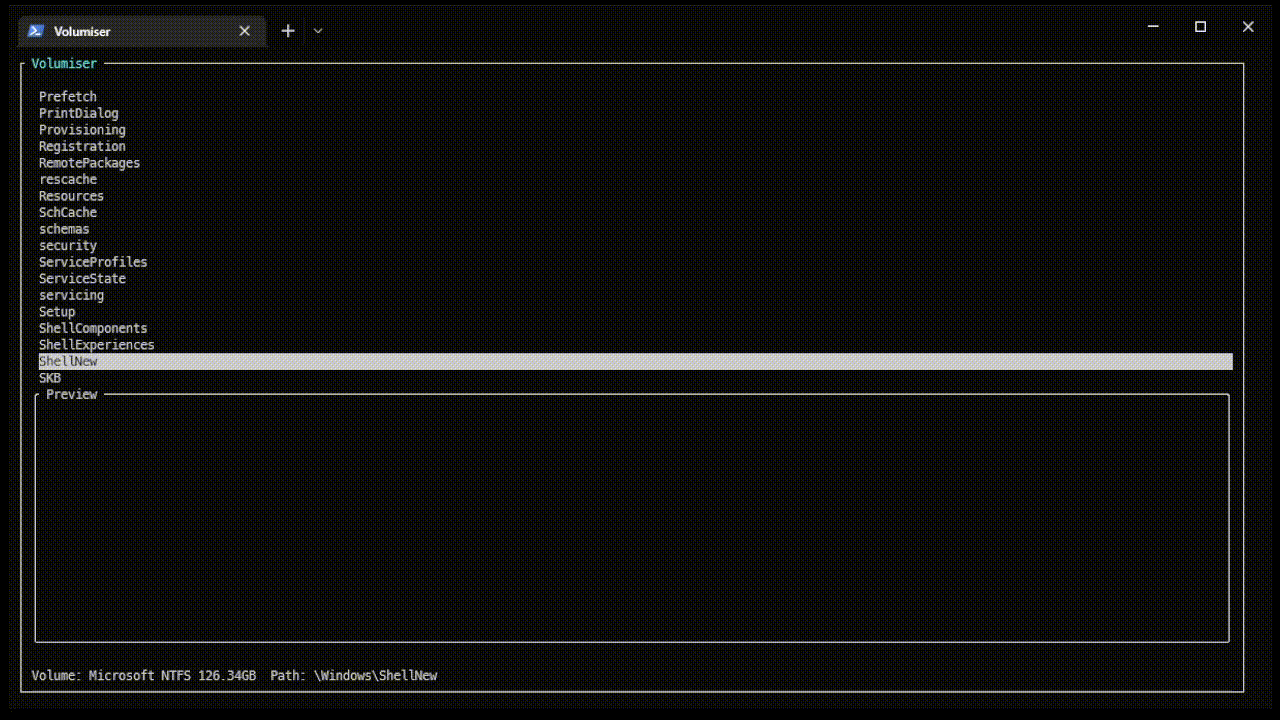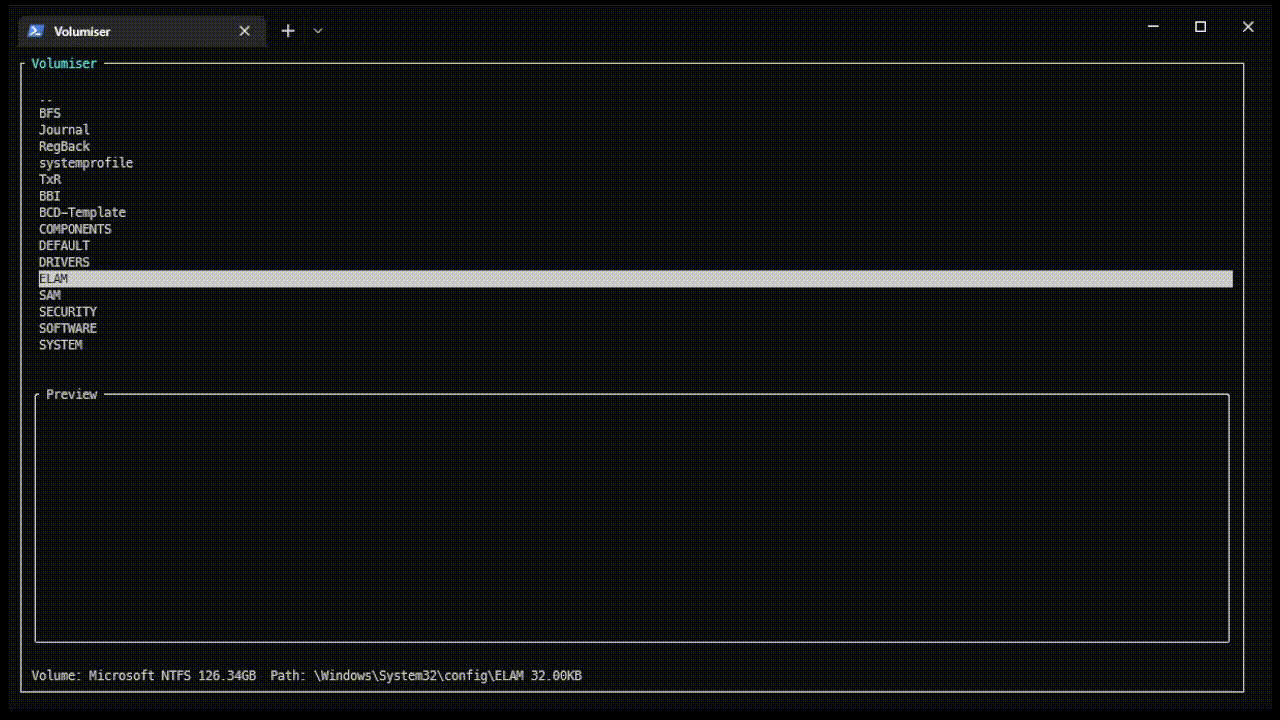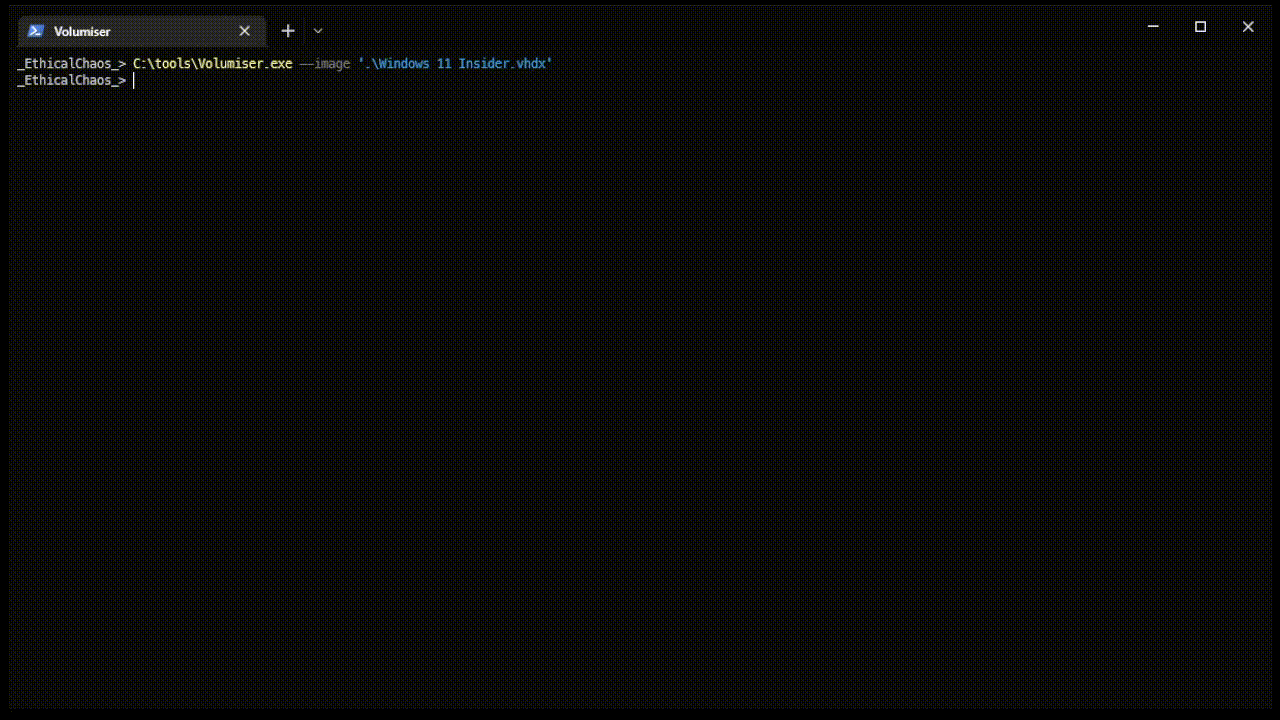
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
disk-forensicsdata-exfiltrationpost-exploitation+3
4371 year ago
cyberchef-recipes preview

cyberchef-recipes

GitHubmattnotmax/cyberchef-recipes

A list of cyber-chef recipes and curated links
disk-forensicsencryption-decryption-toolsnetwork-forensics+8
2.2k2 years ago
LogFileParser preview

LogFileParser

GitHubjschicht/logfileparser

Parser for $LogFile on NTFS
disk-forensicsforensicsdata-recovery+3
2184 months ago
autopsy preview

autopsy

GitHubsleuthkit/autopsy

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
disk-forensicsforensicsmobile-forensics+3
3.3k5 months ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
disk-forensicspost-exploitationdata-recovery+3
25811 months ago
ForensiX preview

ForensiX

GitHubtheevidencehunter/forensix

Digital Forensics Intelligence Framework
disk-forensicshash-analysisforensics+4
6 months ago
veeam-velociraptor preview

veeam-velociraptor

GitHubsynacktiv/veeam-velociraptor

Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.
disk-forensicsforensicsdigital-forensics+1
12 years ago
Disk-Arbitrator preview

Disk-Arbitrator

GitHubaburgh/disk-arbitrator

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
disk-forensicsforensicsdata-recovery+2
7141 year ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:
disk-forensicsosintmemory-forensics+9
1.4k6 days ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

defensive-toolsdisk-forensicsioc-management+14
1.2k2 days ago
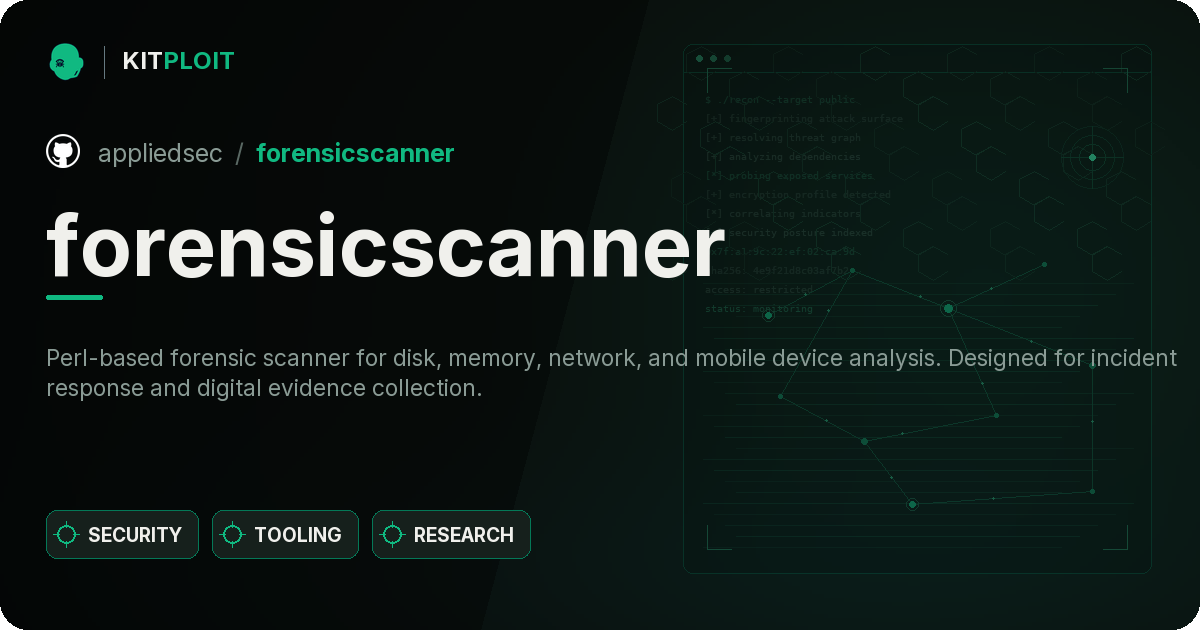
forensicscanner preview

forensicscanner

GitHubappliedsec/forensicscanner

Forensic Scanner
disk-forensicsmemory-forensicsnetwork-forensics+3
4113 years ago
analyzeMFT preview

analyzeMFT

GitHubrowingdude/analyzemft

analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
disk-forensicsforensicsdata-recovery+1
5321 year ago
LAB-DFIR-cve-2023-38831 preview

LAB-DFIR-cve-2023-38831

GitHubra3edaj/lab-dfir-cve-2023-38831

d

disk-forensicsmemory-forensicsvulnerability-analysis+6
2 years ago
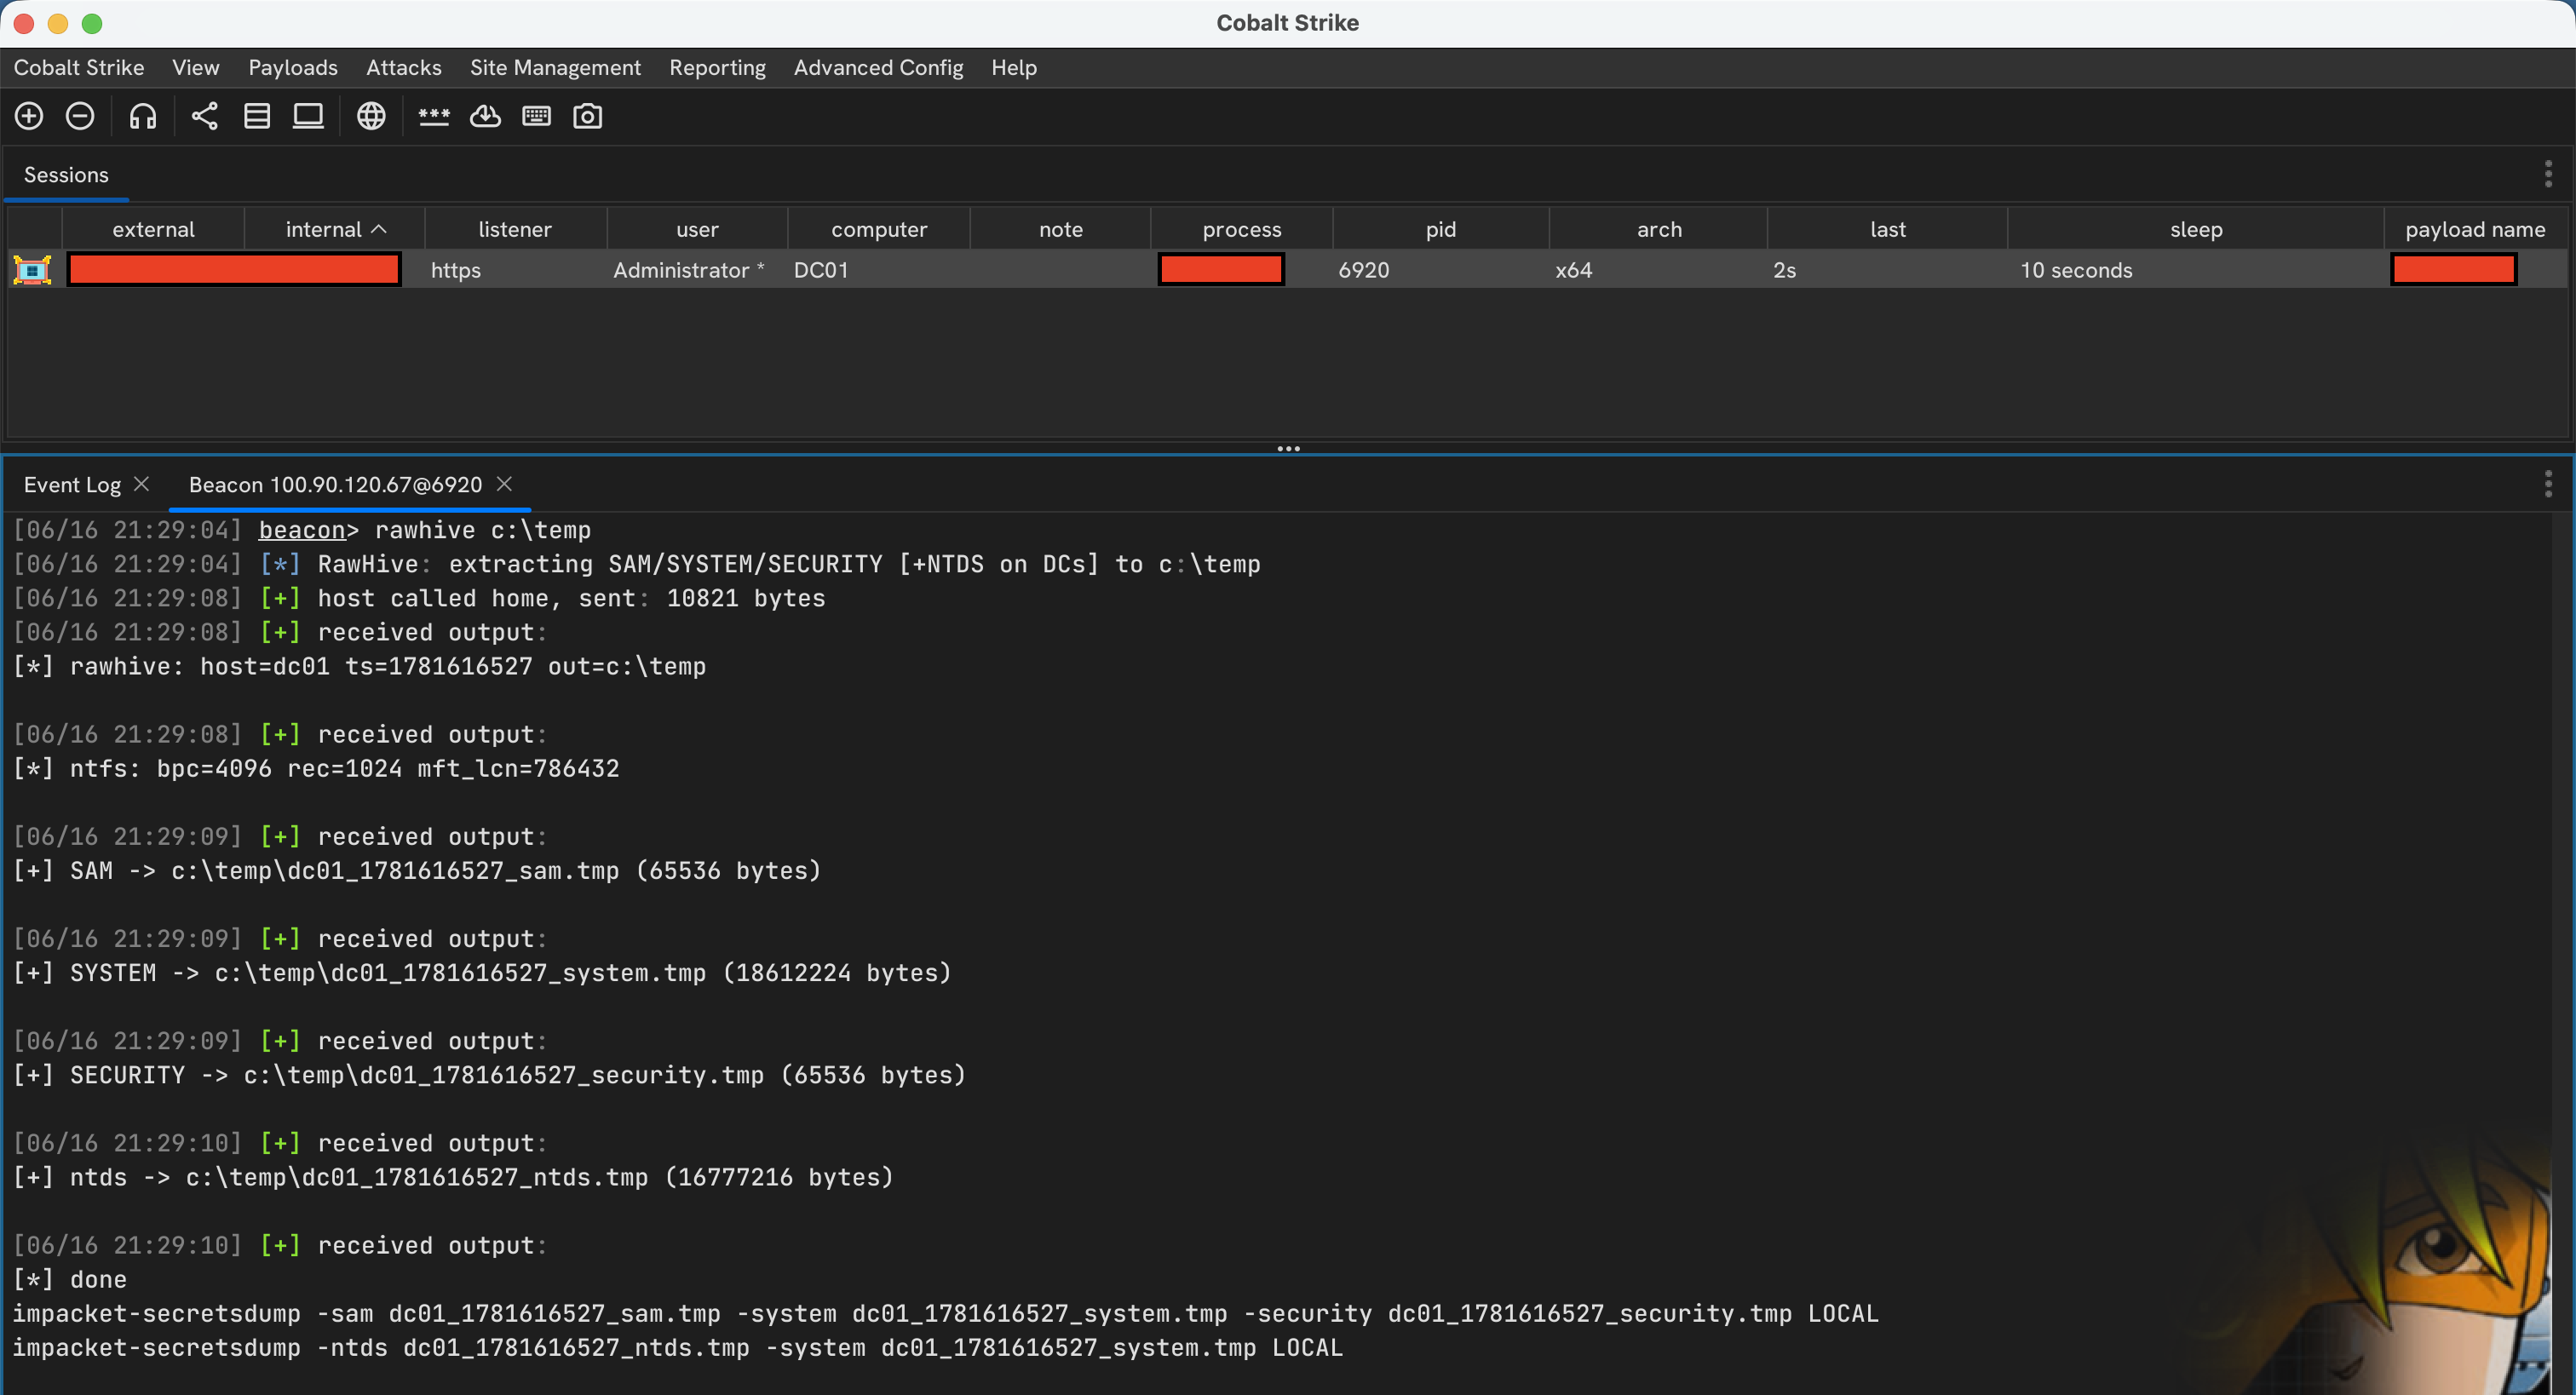
RawHive preview

RawHive

GitHubnmht3t/rawhive

Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
disk-forensicsexploitationforensics+4
937 days ago
ffs preview

ffs

GitHubdmtrkovalenko/ffs

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
disk-forensicsgeneral-purpose-utilitiesscripting-automation+3
1743 months ago
Crow-Eye preview

Crow-Eye

GitHubghassan-elsman/crow-eye

Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…

defensive-toolsdisk-forensicsforensics+3
1118 days ago
Previous12345Next