
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
digital-forensics — Tools — Page 30 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
622 results
Collect-MemoryDump preview

Collect-MemoryDump

GitHublethal-forensics/collect-memorydump

Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

memory-forensicsforensicsdigital-forensics+1
265
11 months ago
exif-gps-tracer preview

exif-gps-tracer

GitHubm0n1x90/exif-gps-tracer

A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…

osintreconnaissanceforensics+2
445 years ago
iocextract preview

iocextract

GitHubpedramamini/iocextract

Defanged Indicator of Compromise (IOC) Extractor.

ioc-managementosintthreat-feeds-aggregators+5
5842 years ago
ForensicMiner preview

ForensicMiner

GitHubsecurityjoes/forensicminer

A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.

disk-forensicsmemory-forensicsforensics+2
1641 year ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.

information-gatheringdigital-forensicscloud-security+3
8373 months ago
gitxray preview

gitxray

GitHubkulkansecurity/gitxray

A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.

osintinformation-gatheringdigital-forensics+3
1839 months ago
netlas-cookbook preview

netlas-cookbook

GitHubnetlas-io/netlas-cookbook

The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…

osintreconnaissanceiot-security+9
8881 month ago
DroneXtract preview

DroneXtract

GitHubang13t/dronextract

Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…

forensicssteganographydata-recovery+3
3633 years ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

memory-forensicsforensicsinformation-gathering+3
8567 years ago
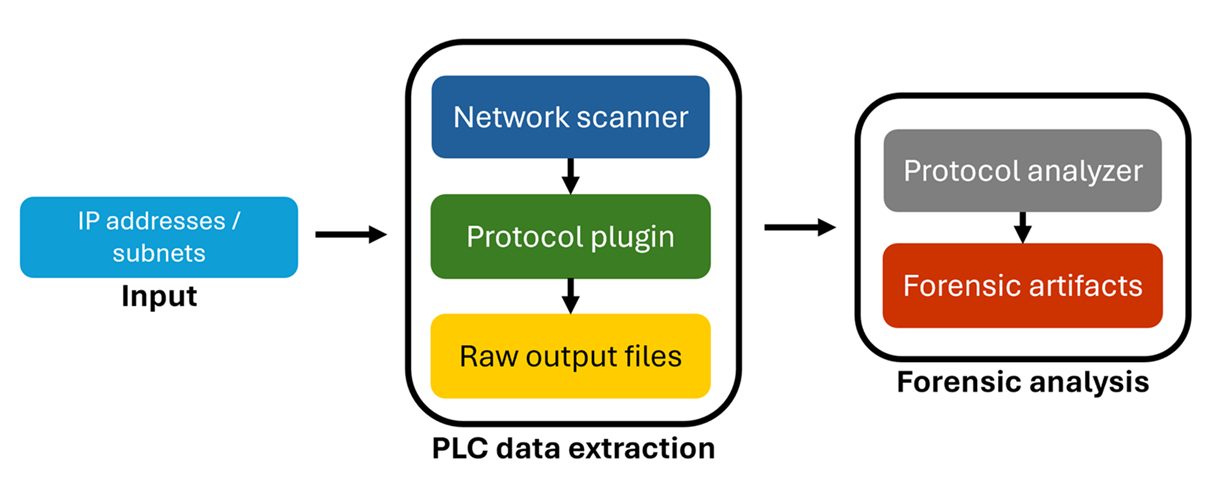
ics-forensics-tools preview

ics-forensics-tools

GitHubmicrosoft/ics-forensics-tools

Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…

vulnerability-analysisscada-ics-securityforensics+2
3711 year ago
MemTracer preview

MemTracer

GitHubmayhamad/memtracer

Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…

memory-forensicsforensicsmalware-analysis+1
644 years ago
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…

forensicsdigital-forensicscloud-security+3
1831 month ago
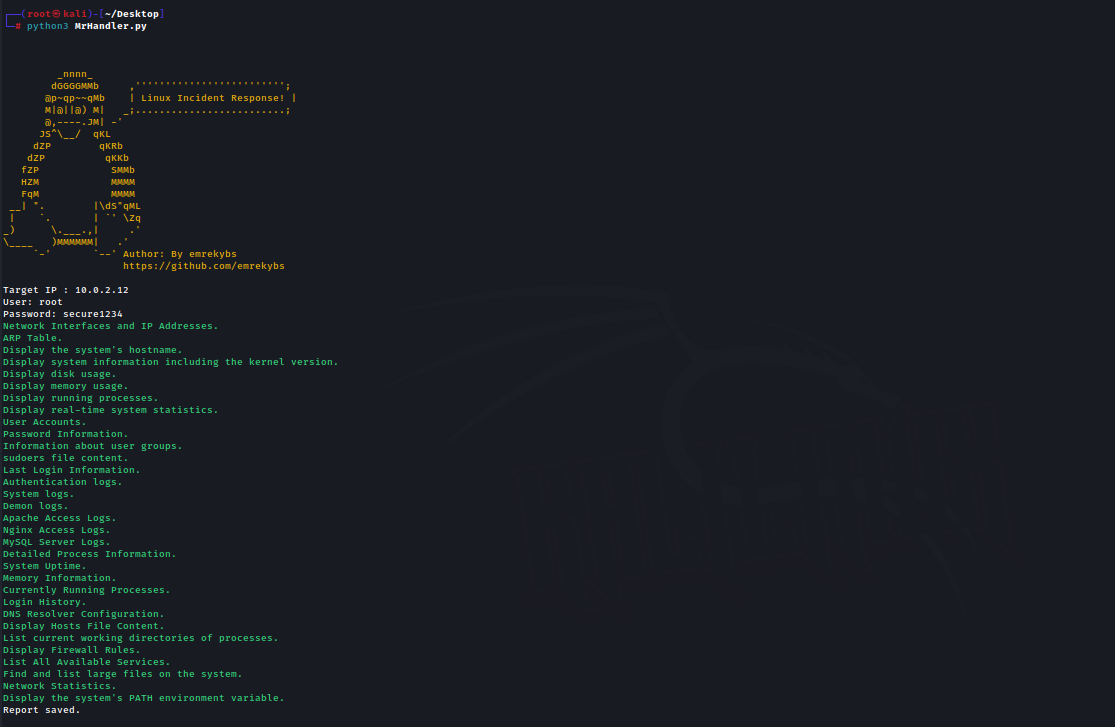
MrHandler preview

MrHandler

GitHubemrekybs/mrhandler

SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…

forensicsdigital-forensicsincident-response+1
866 months ago
TEx preview

TEx

GitHubguibacellar/tex

Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…

osintforensicsinformation-gathering+2
3752 years ago
Linpmem preview

Linpmem

GitHubvelocidex/linpmem

Linux kernel driver for physical memory acquisition, enabling read access to any physical address including reserved memory and memory holes, with…

memory-forensicsforensicsdigital-forensics+1
1051 year ago
awesome-soc-analyst preview

awesome-soc-analyst

GitHubletsdefend/awesome-soc-analyst

Useful resources for SOC Analyst and SOC Analyst candidates.

phishingmalware-analysisdigital-forensics+6
9863 years ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…

ioc-managementosintstatic-analysis+8
3202 years ago
forensictools preview

forensictools

GitHubcristianzsh/forensictools

Collection of forensic tools

disk-forensicsmemory-forensicsnetwork-forensics+7
7012 months ago
Previous1…293031…35Next