
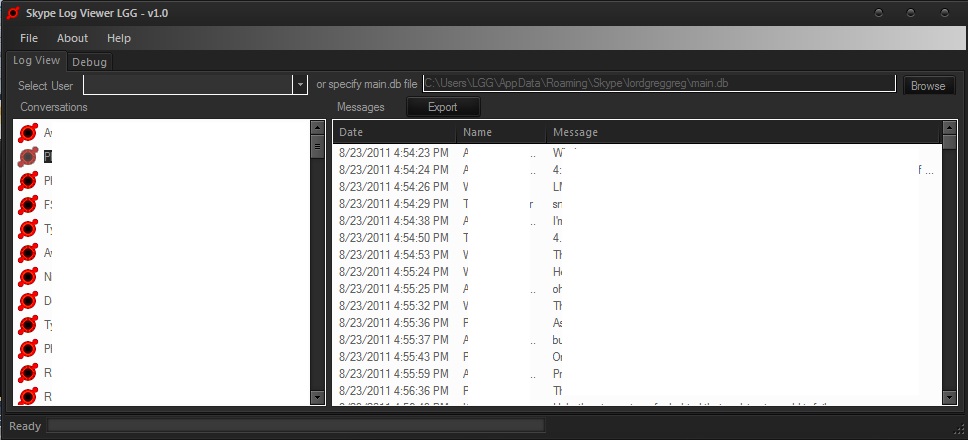
skype-log-viewer
 lgggreg/skype-log-viewer
Download and View Skype History Without Skype
osintforensicsinformation-gathering+1
lgggreg/skype-log-viewerDownload and View Skype History Without Skype
 skelsec/pypykatz
Mimikatz implementation in pure Python
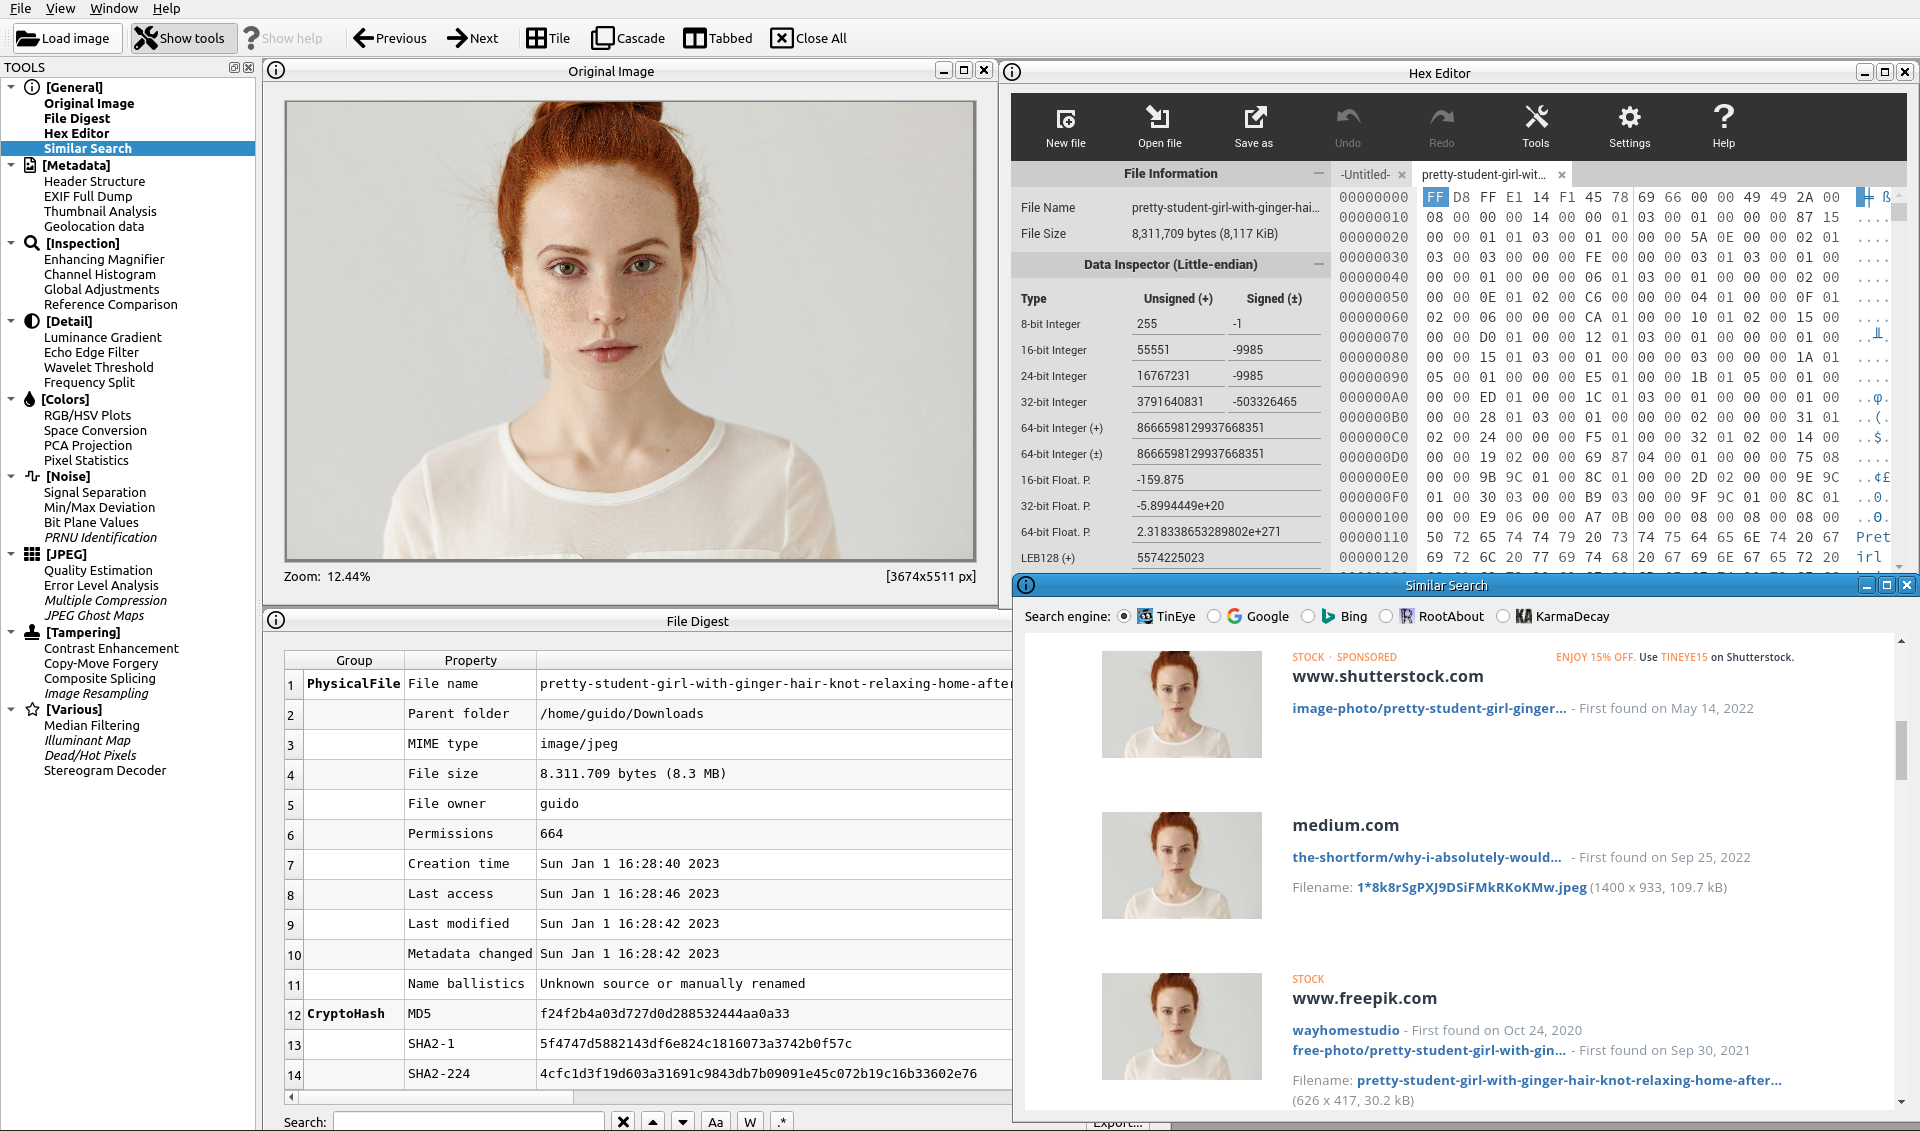 guidobartoli/sherloq
An open-source digital image forensic toolset
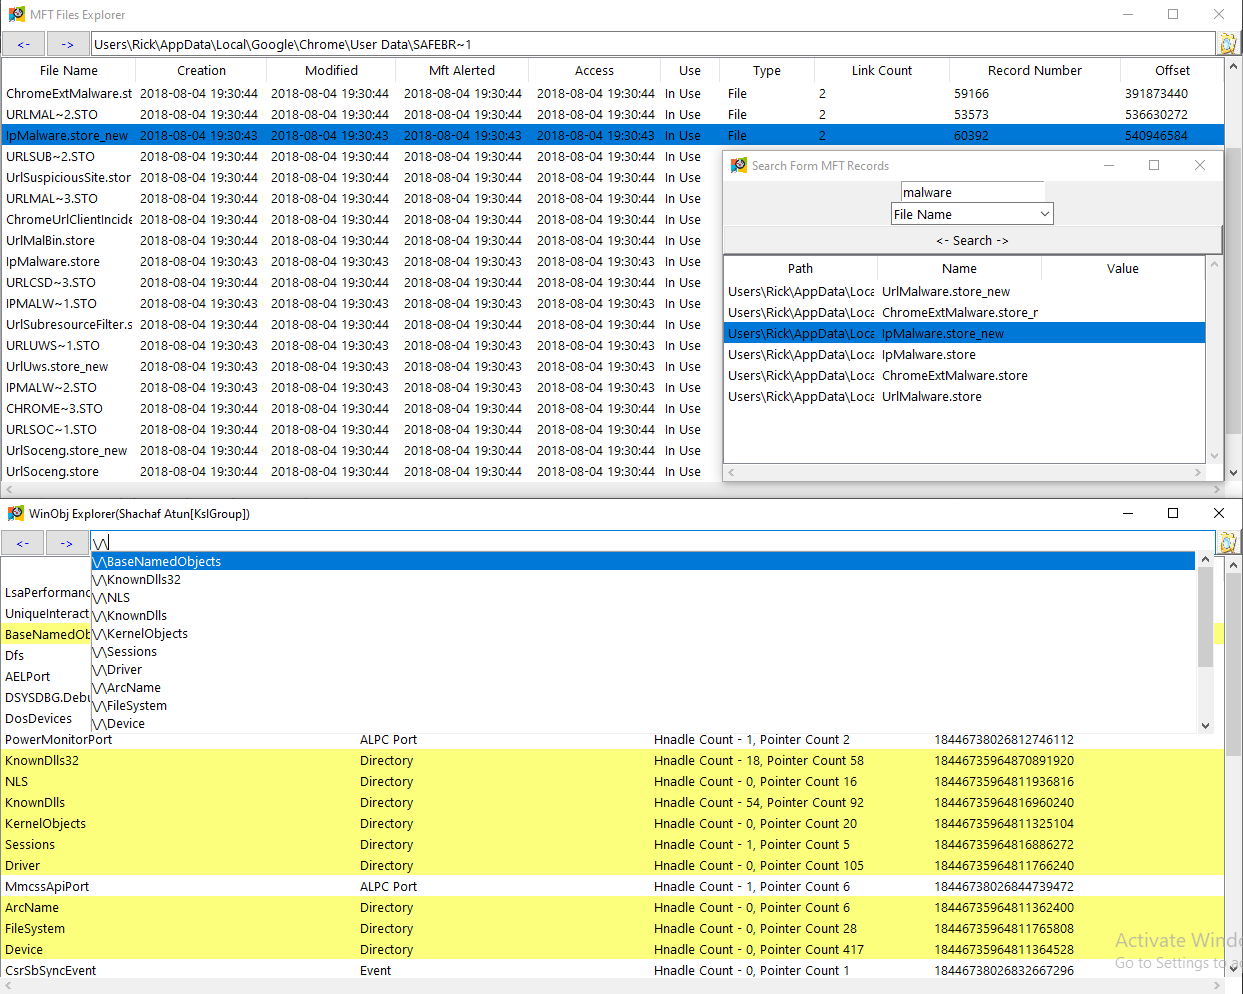 memoryforensics1/volexp
volatility explorer (volatility 2)
 bitranox/fingerprint
Monitoring Registry and File Changes in Windows
 yeti-platform/yeti
Your Everyday Threat Intelligence
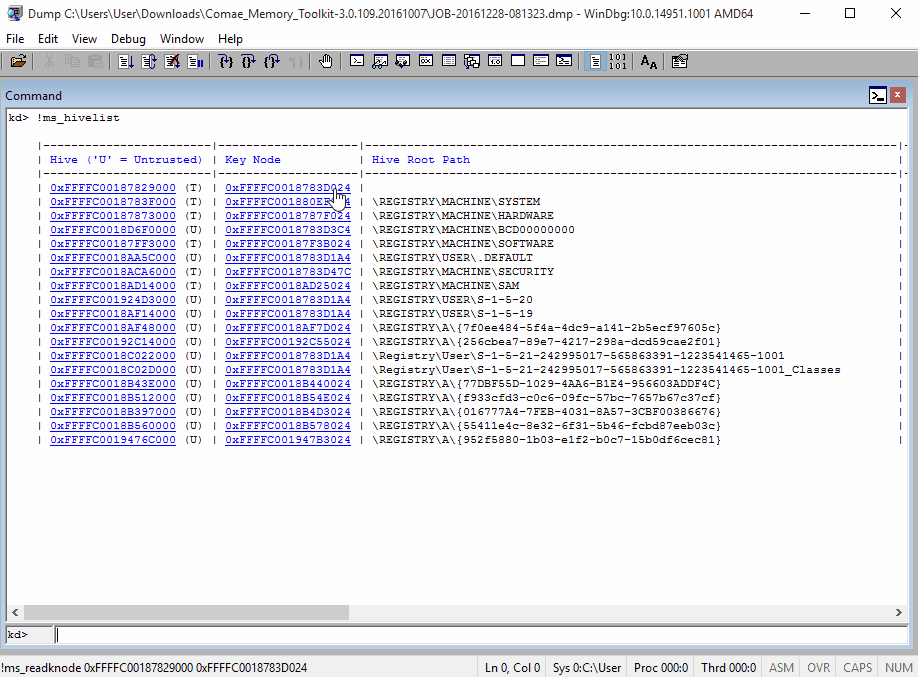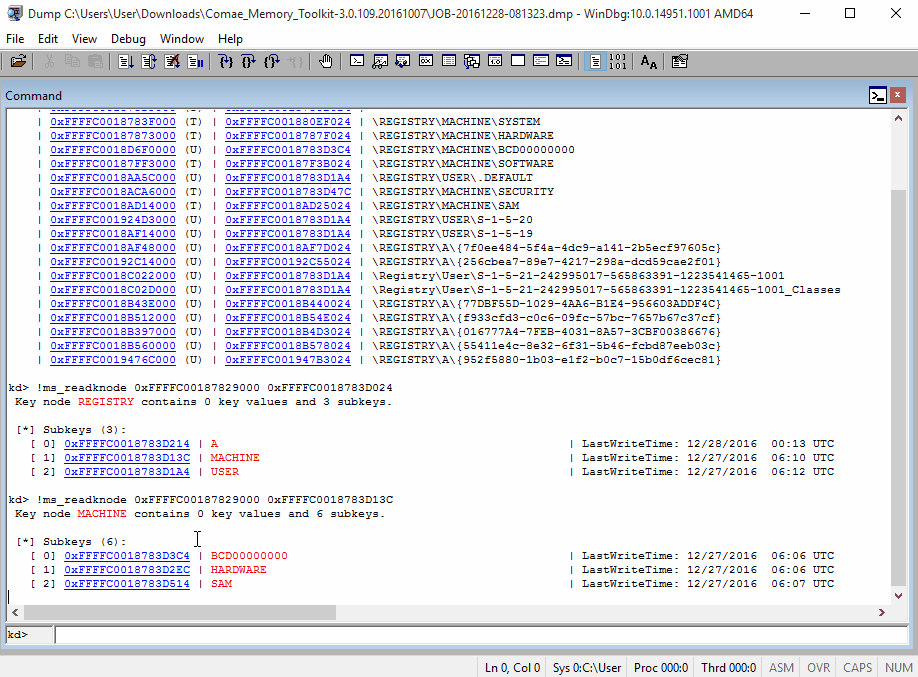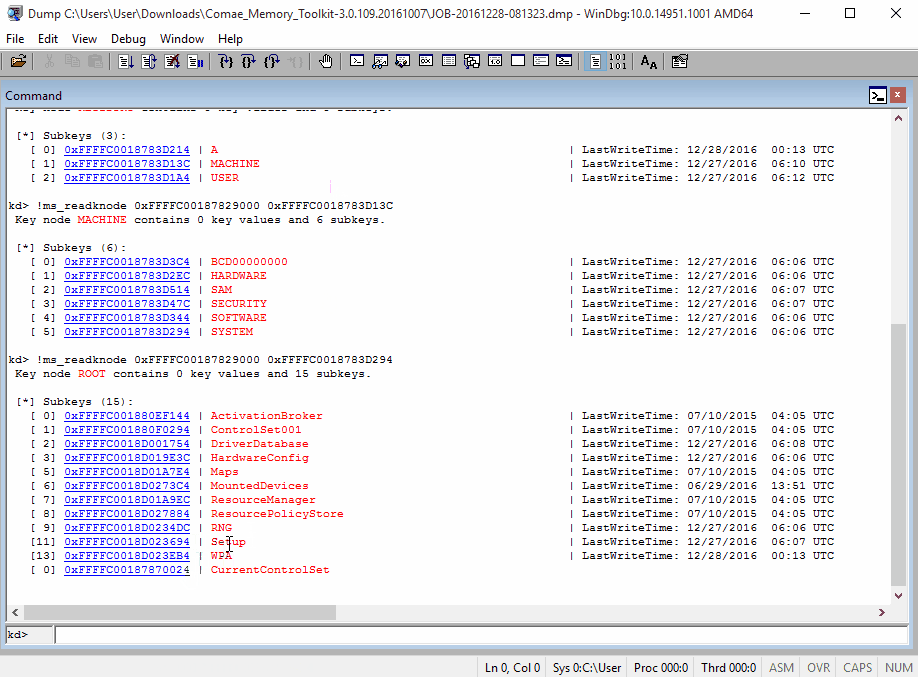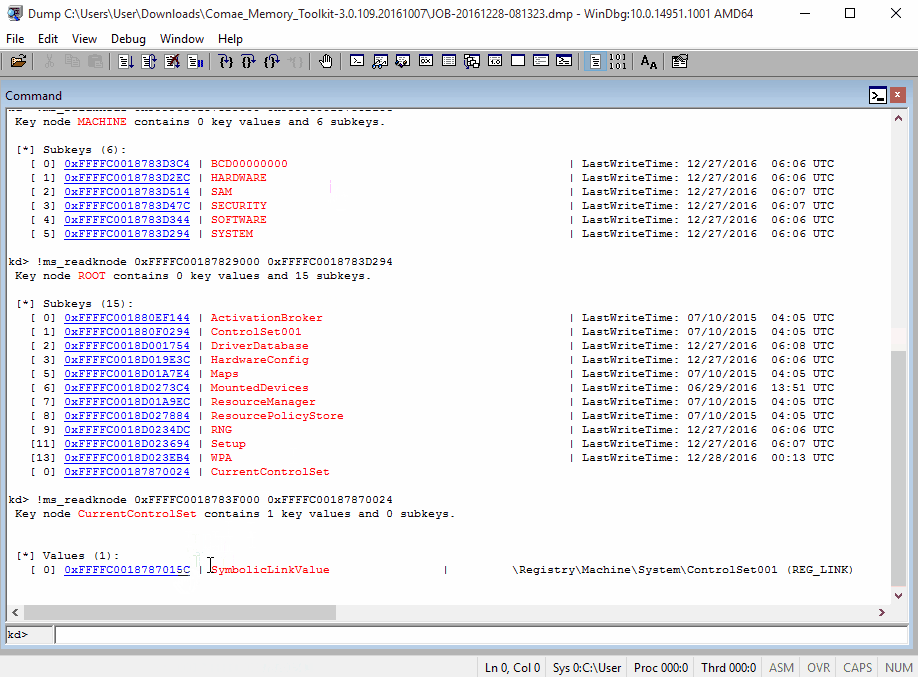 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
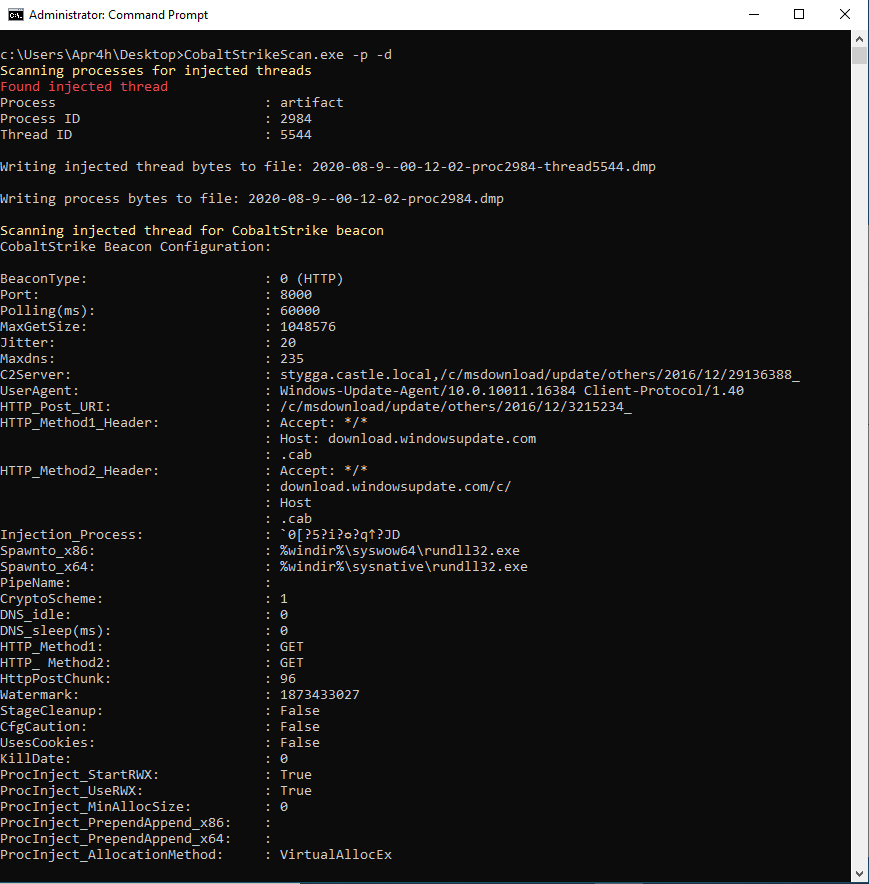 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration

 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
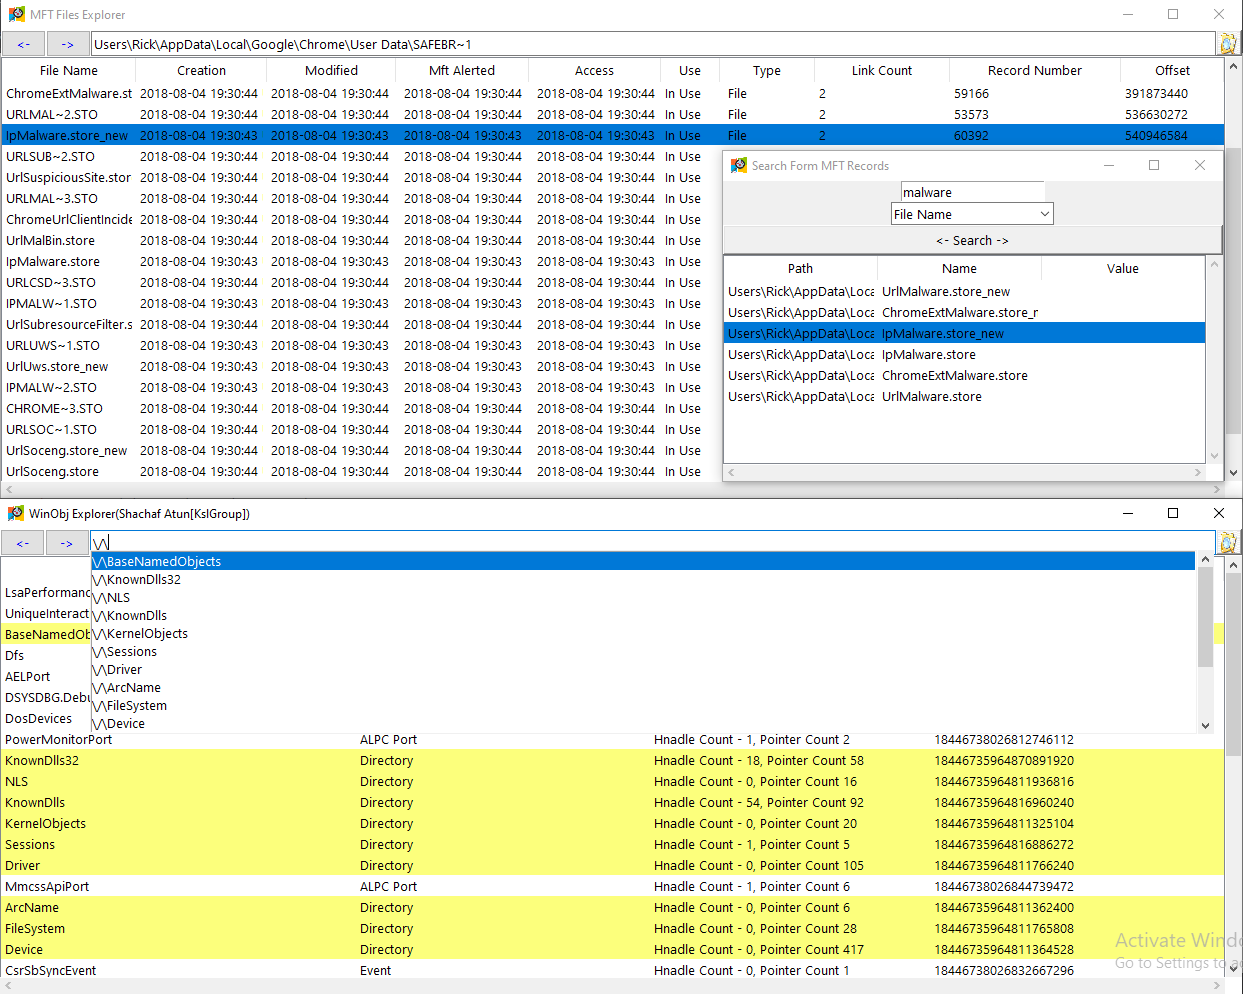 memoryforensics1/vol3xp
Volatility Explorer Suit (volatility 3)
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
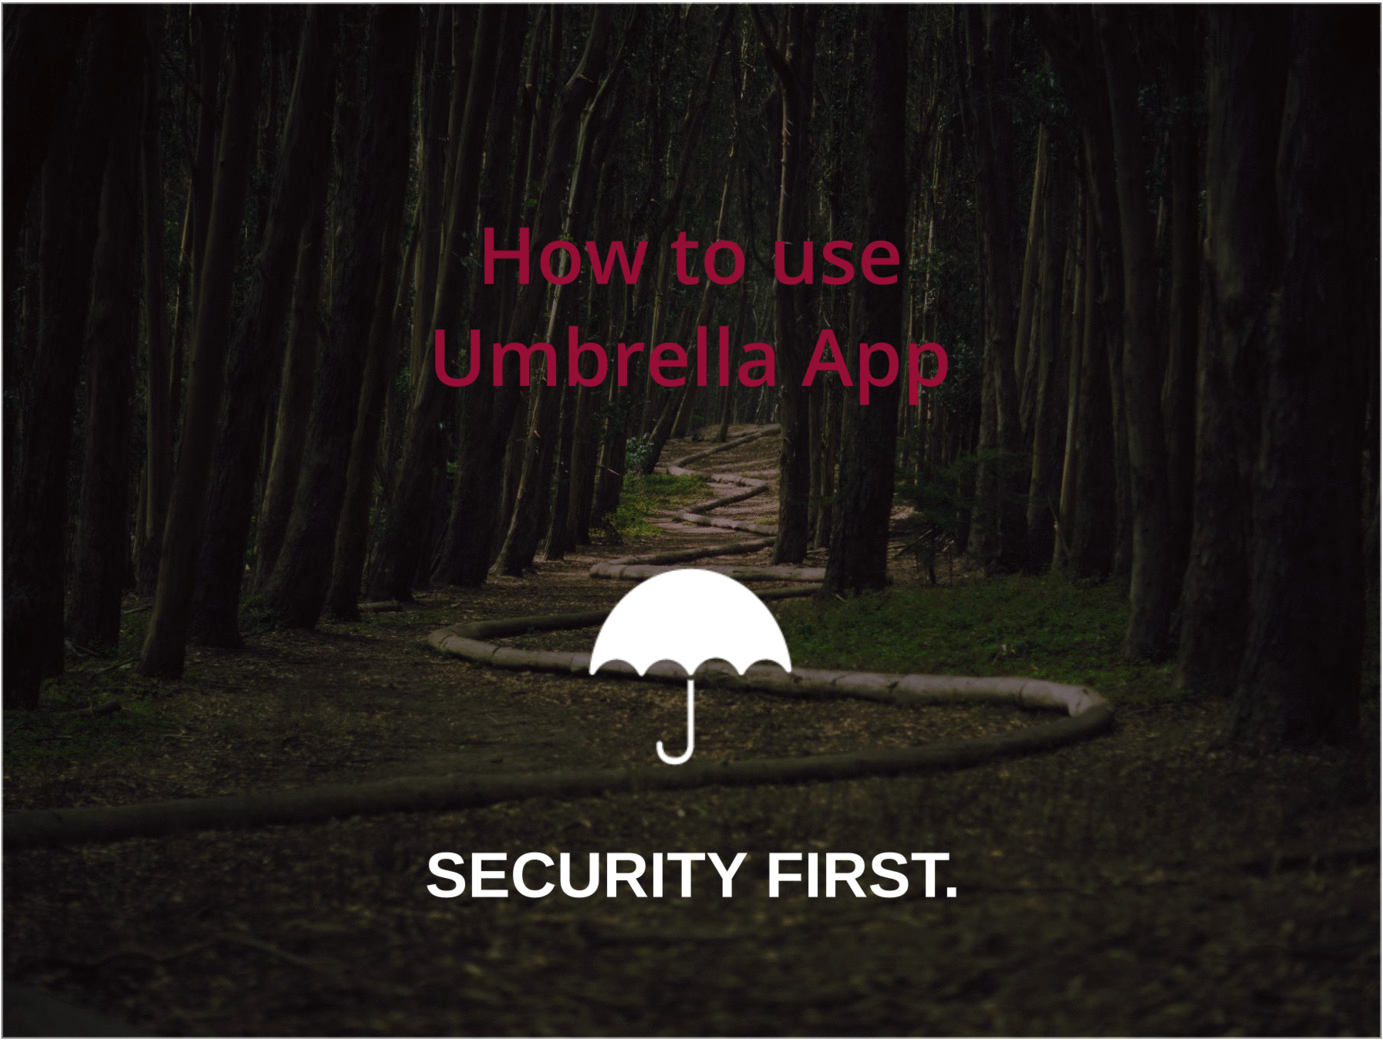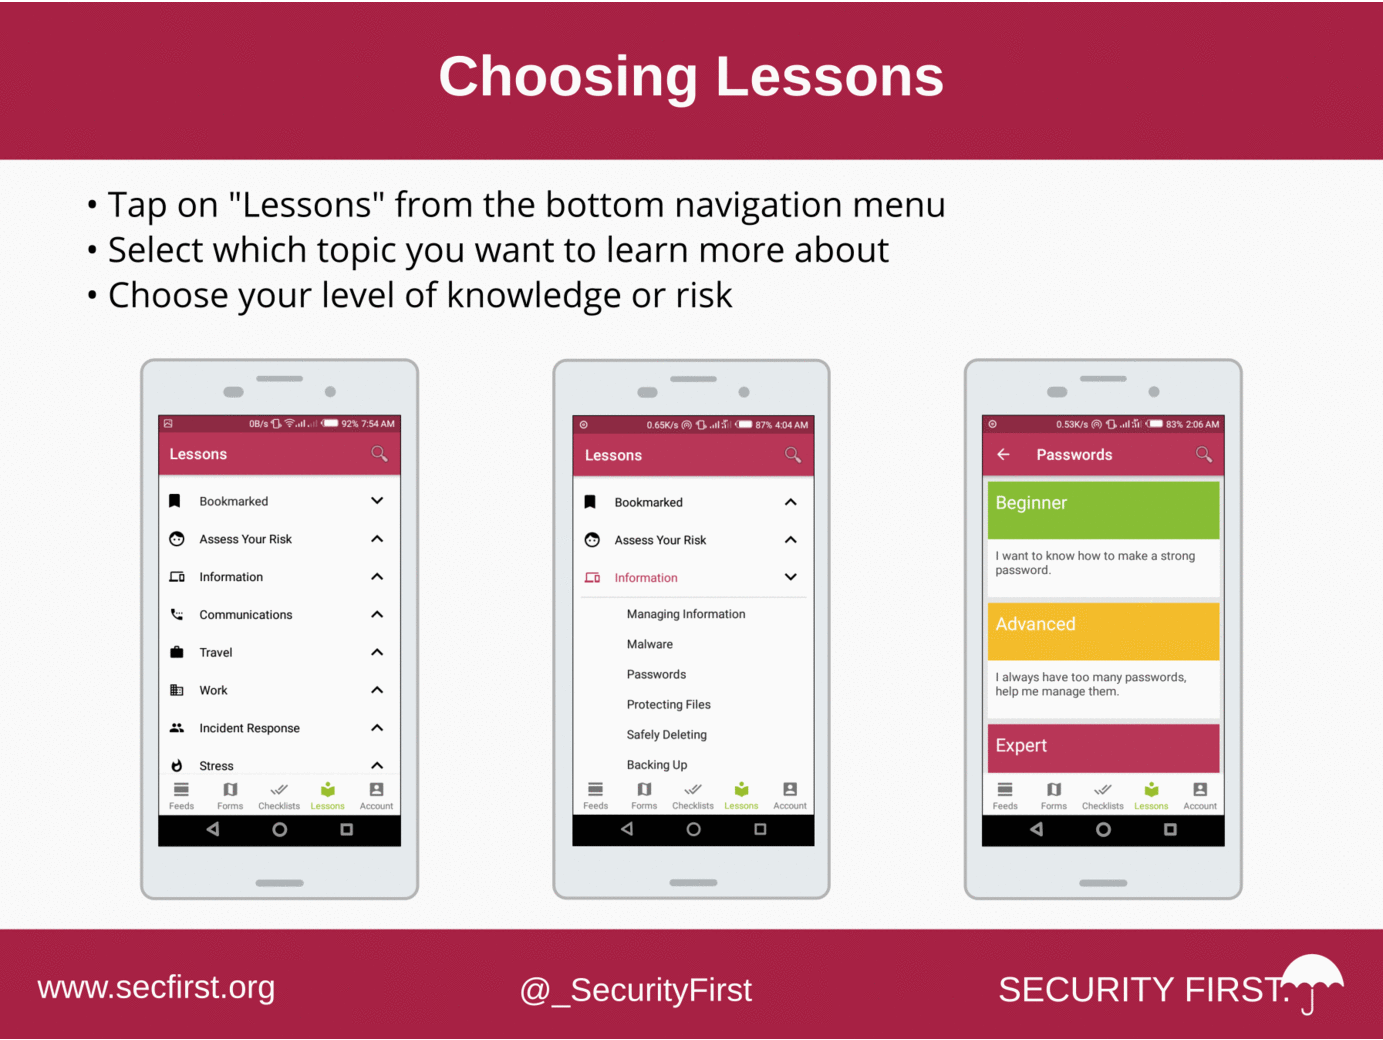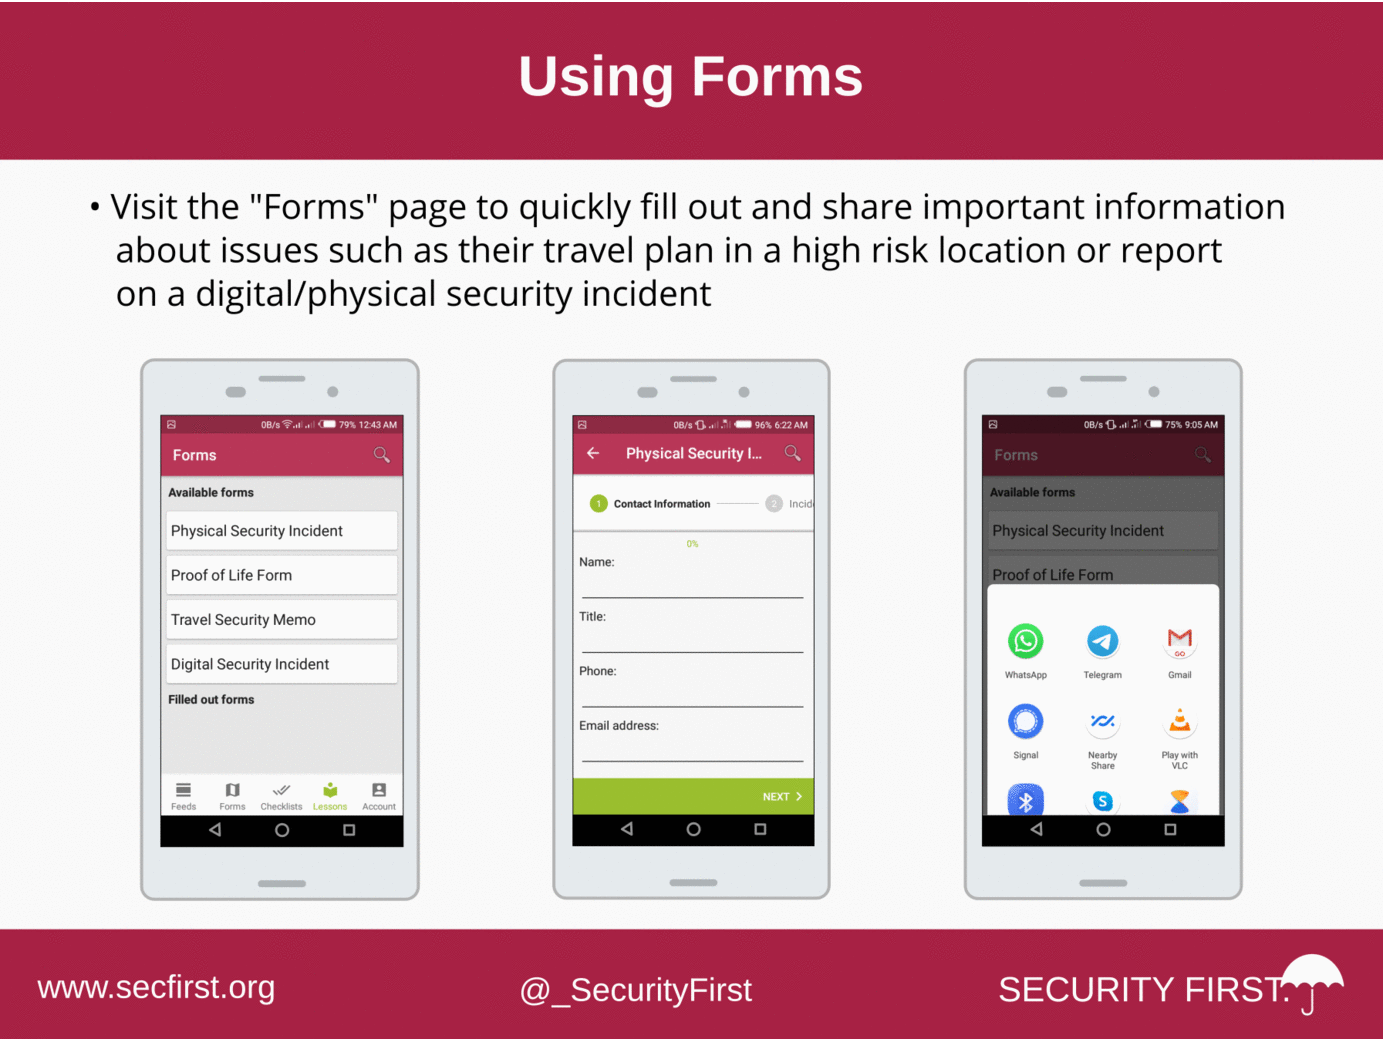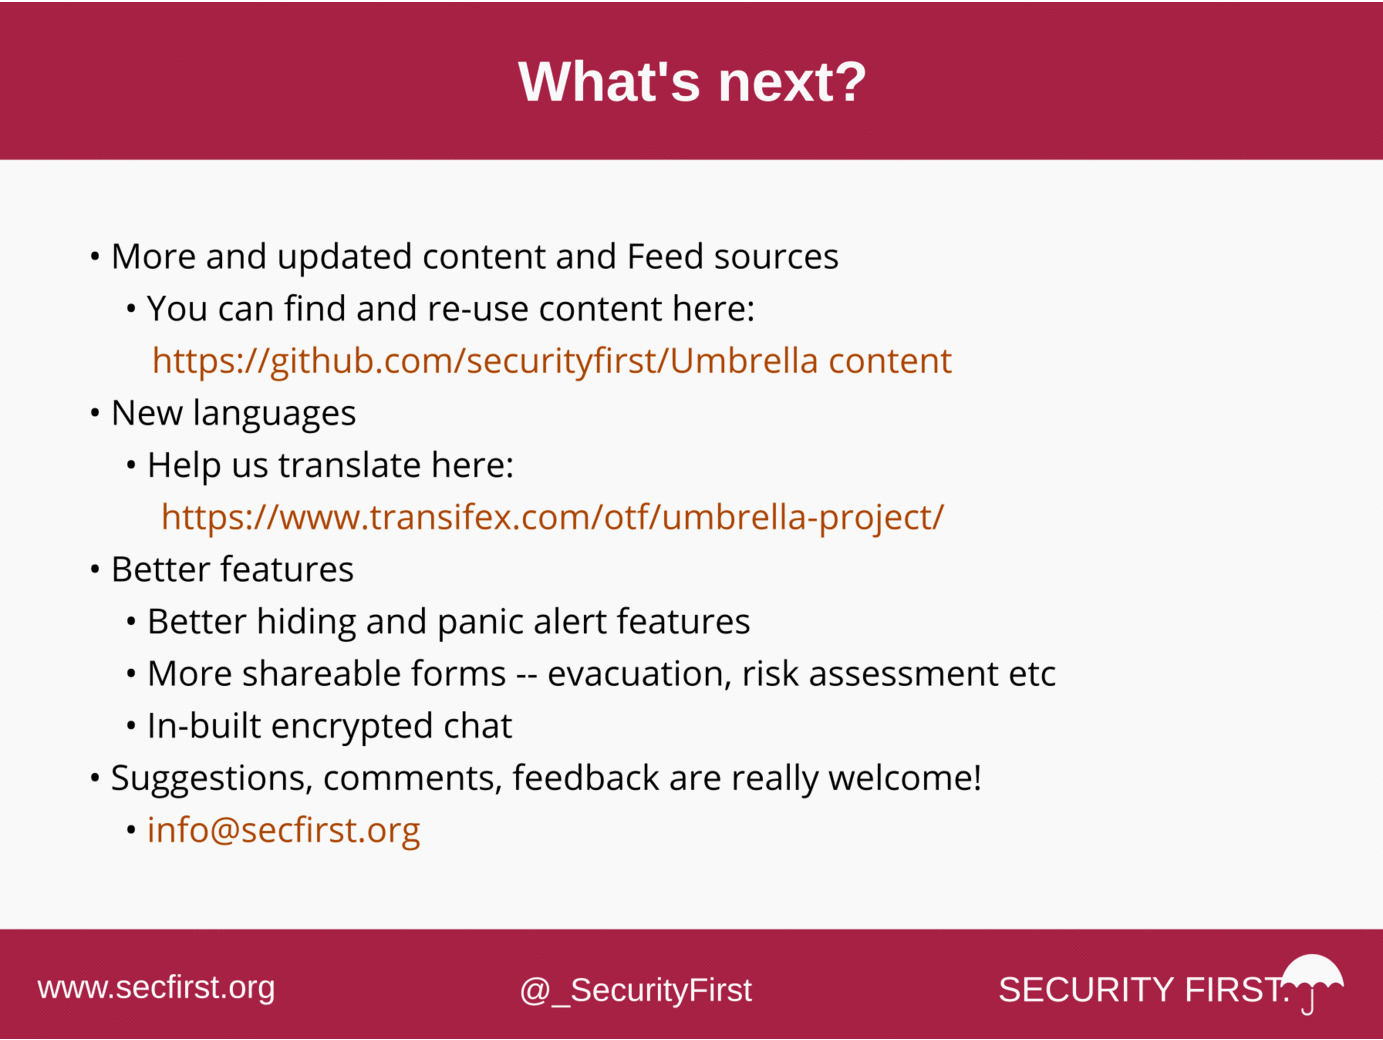 securityfirst/umbrella_android
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
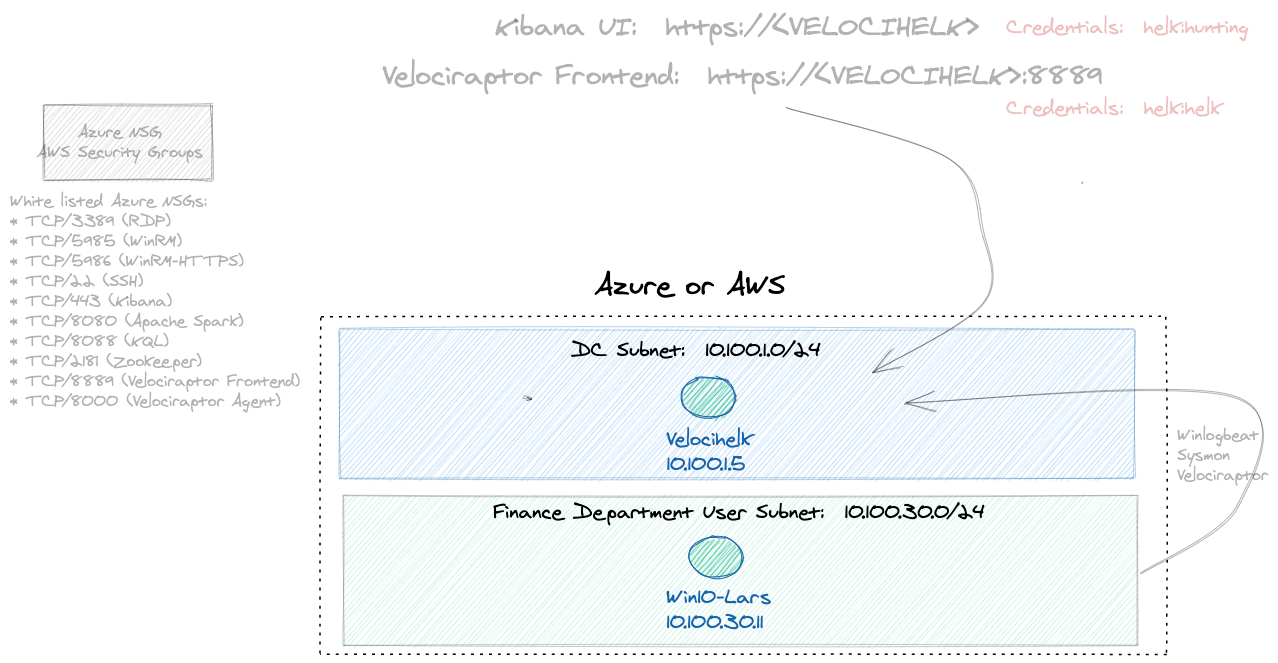 iknowjason/bluecloud
Cyber Range including Velociraptor + HELK system with a Windows VM for security testing and R&D. Azure and AWS terraform support.
 hamza-megahed/volatility-gui
GUI for Volatility forensics tool written in PyQT5