
qvm-tool
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
static-analysisdynamic-analysis-sandboxingvulnerability-analysis+5
3
neurosaki987/qvm-toolStatic analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
 werew/qsynth-artifacts
Benchmark datasets and synthesis artifacts for QSynth, containing Tigress-obfuscated C functions, x86_64 binaries, execution traces, ground truth,…
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
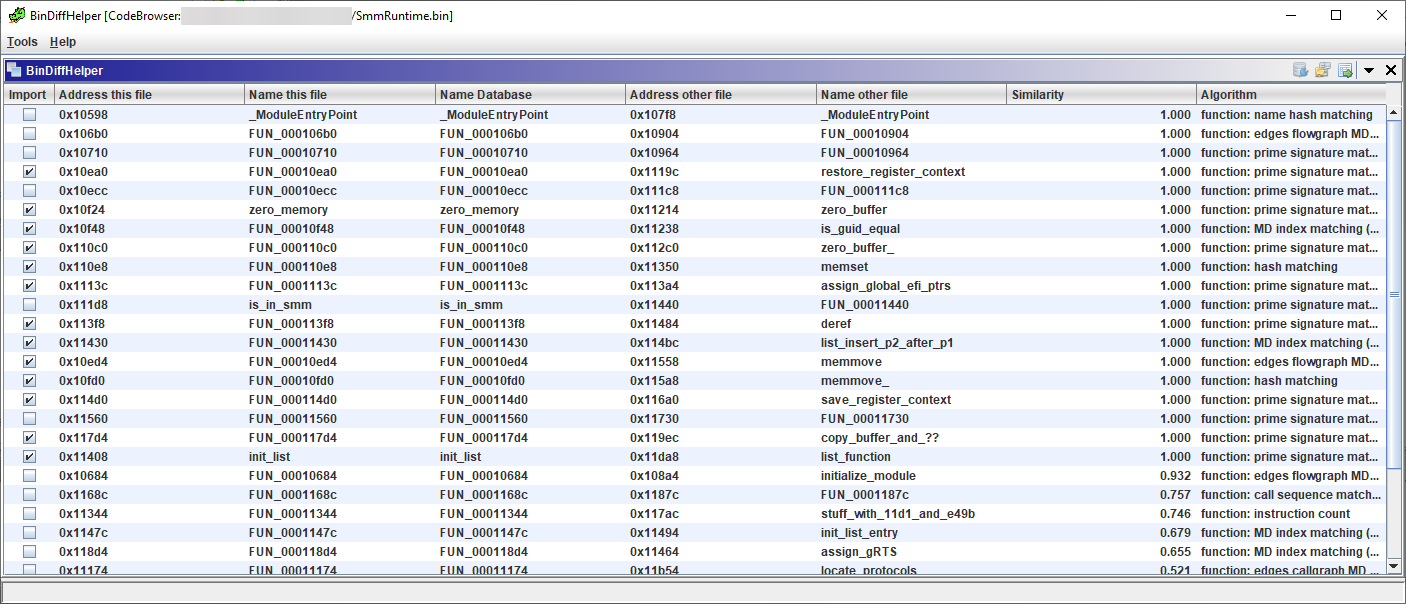 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
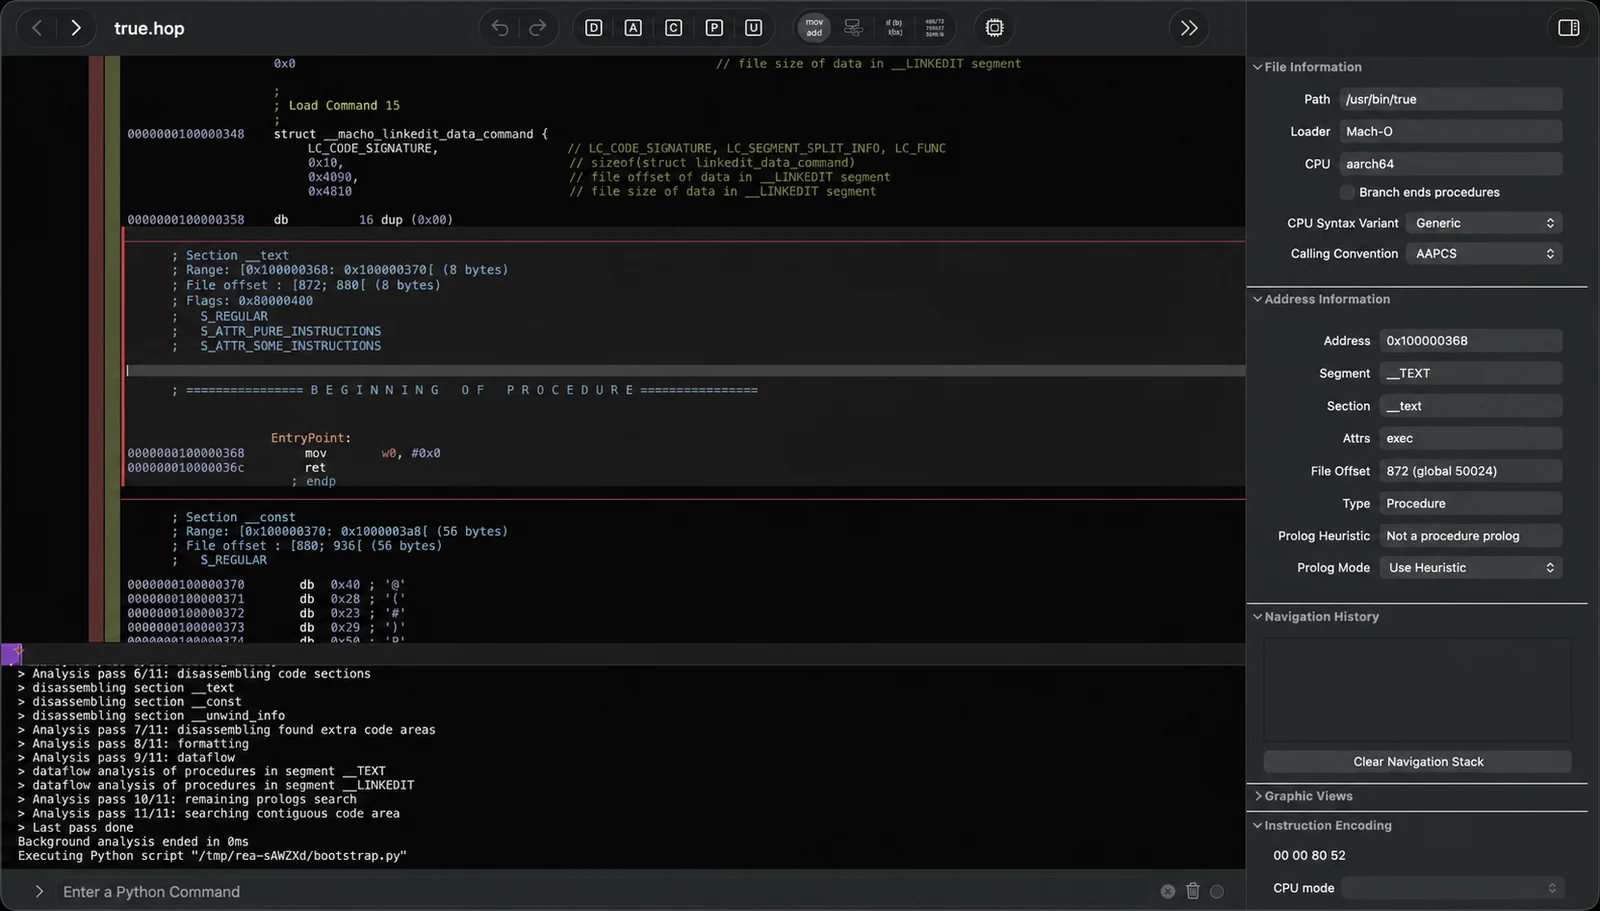 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
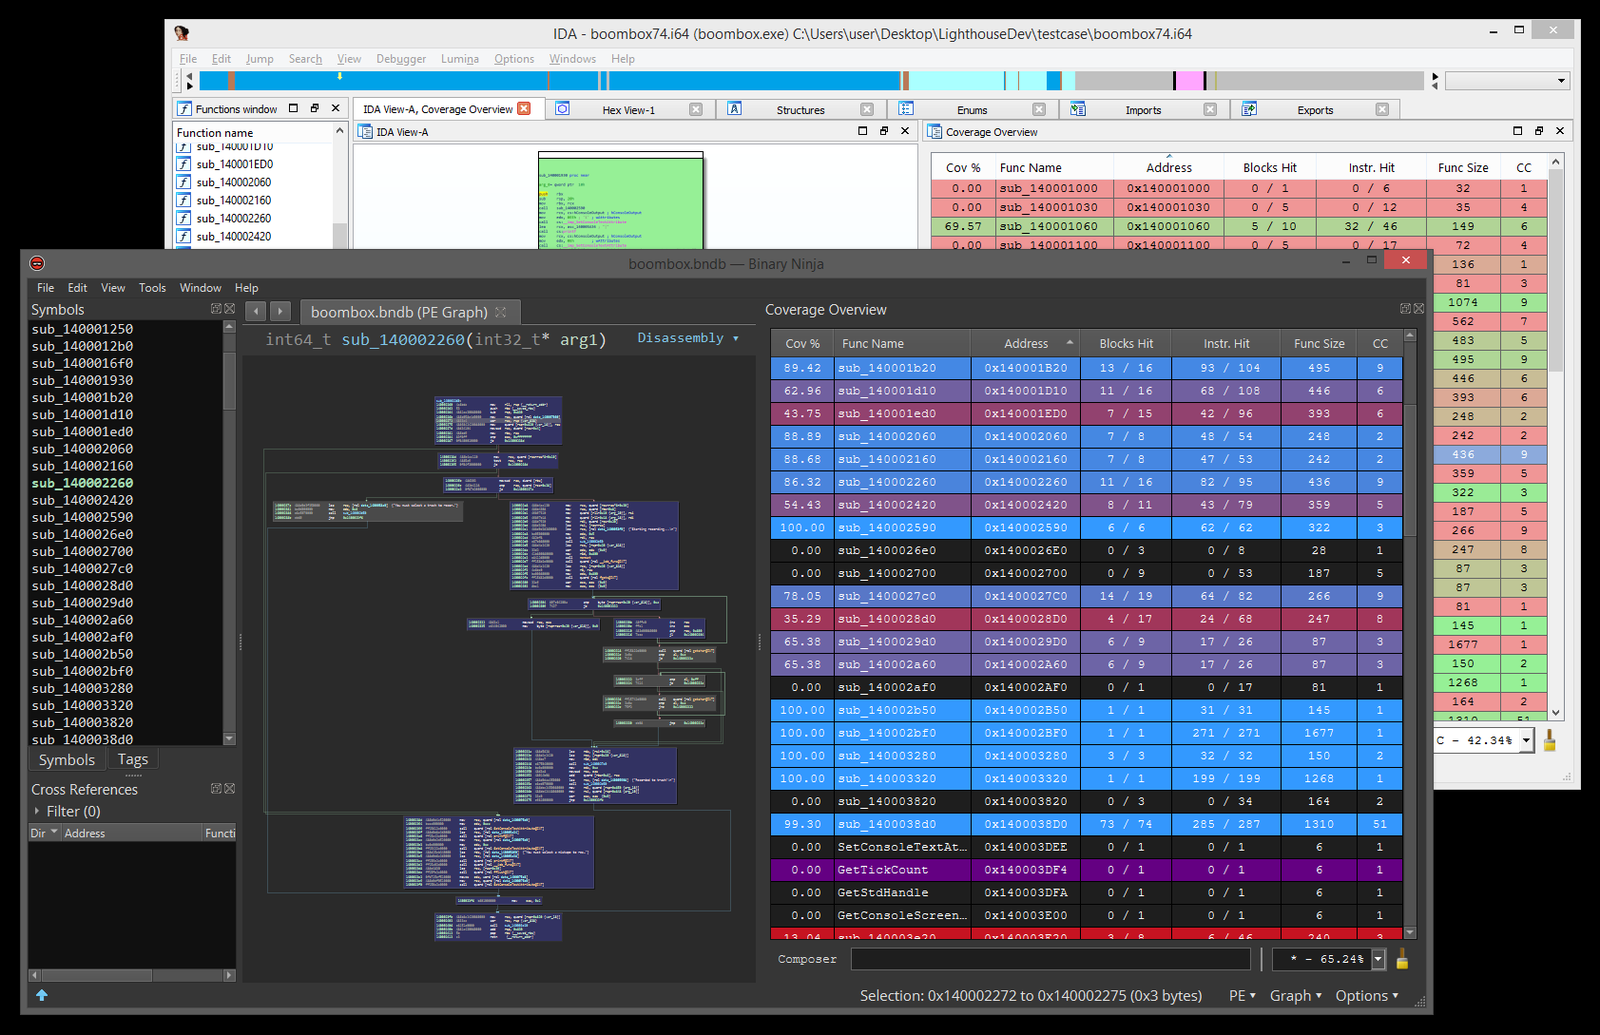 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 ezyang/htmlpurifier
Standards compliant HTML filter written in PHP
 angr/pyvex
Python bindings for Valgrind's VEX IR.
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…