
Interview_Tips
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
web-securitynetwork-securitycryptography+5
69
jigerjain/interview_tipsSummary of Cyber Security interview questions I have been through, hope this helps
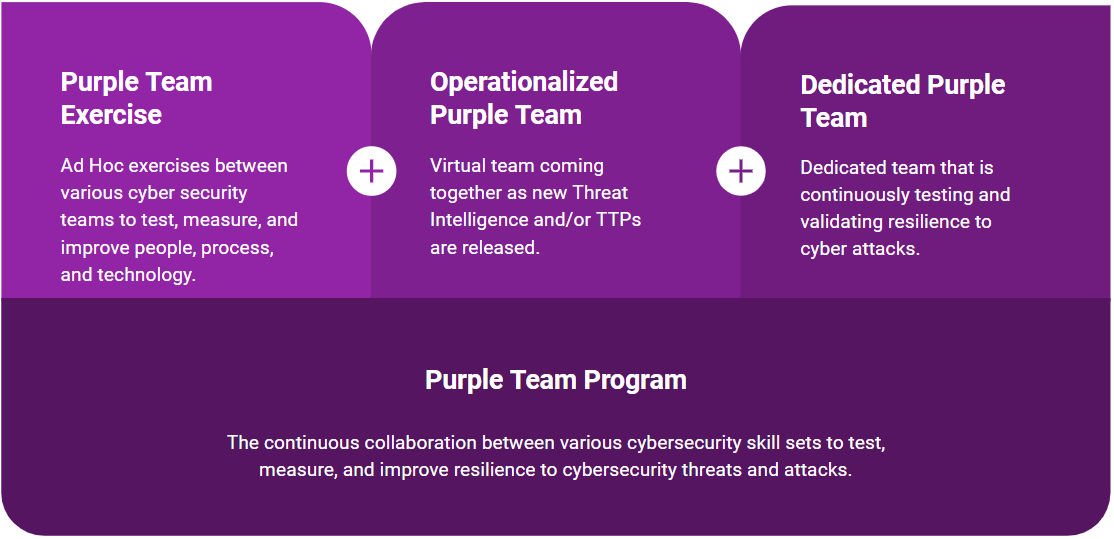 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
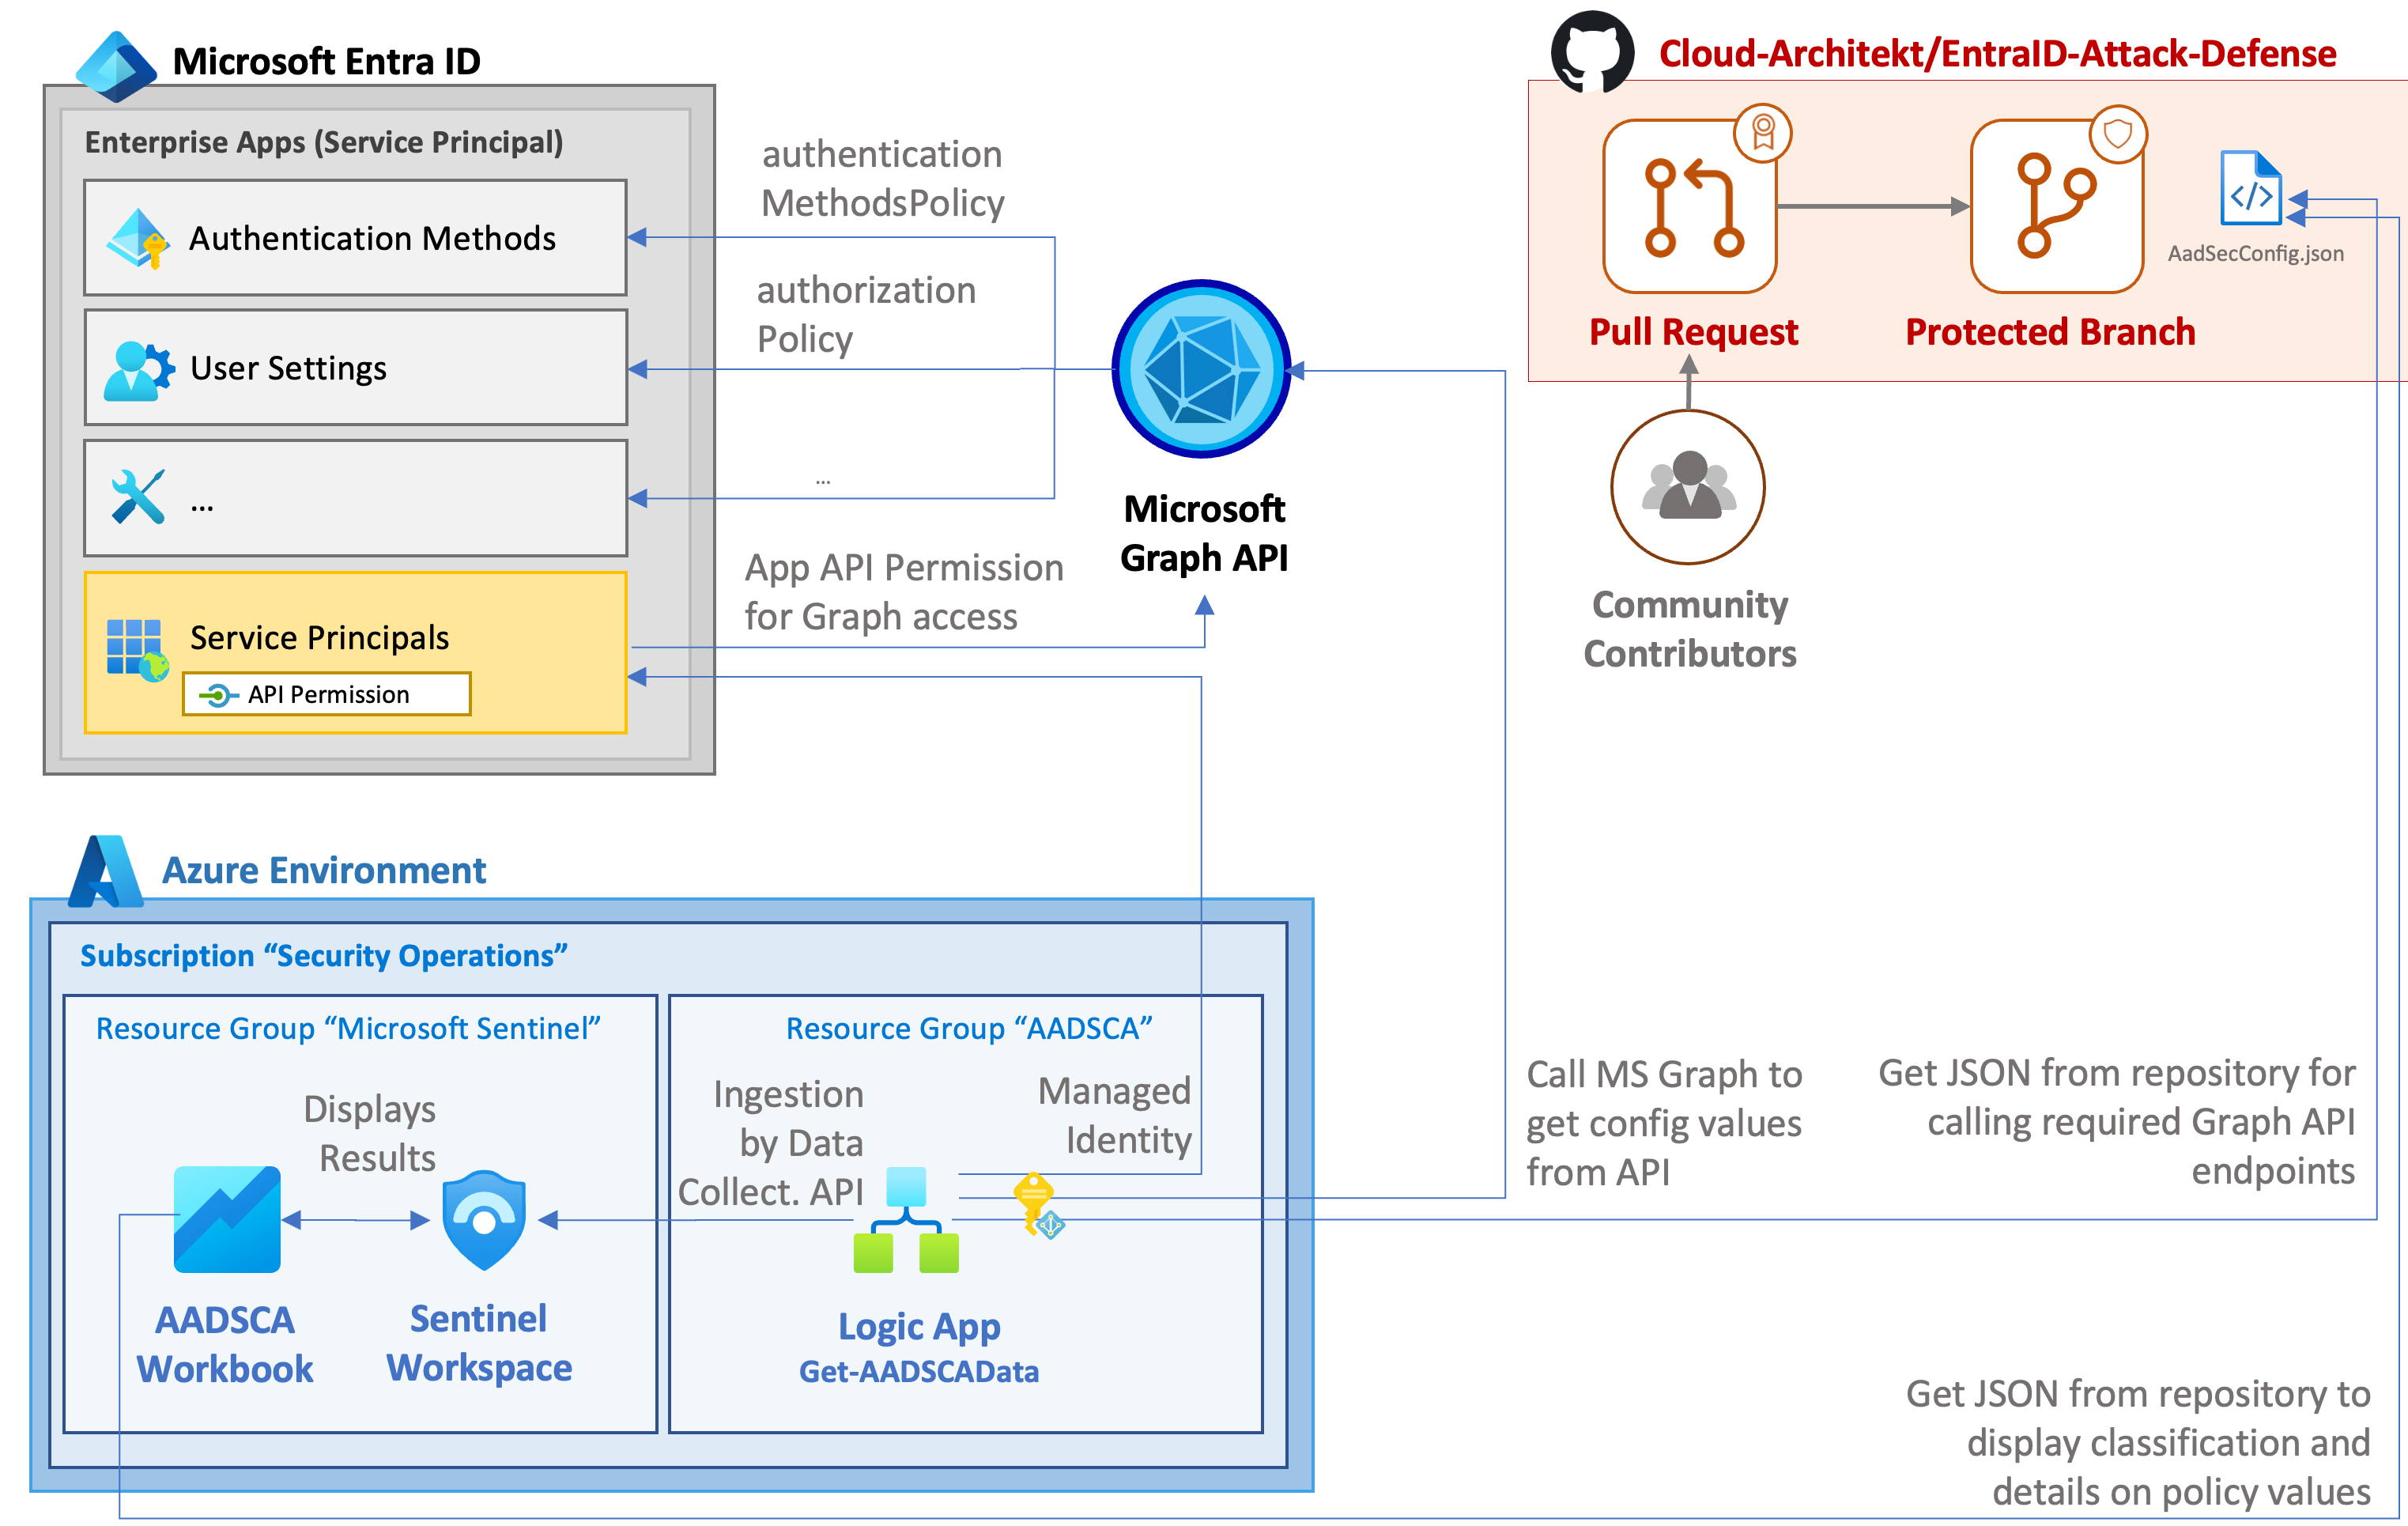 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 cujanovic/ssrf-testing
SSRF (Server Side Request Forgery) testing resources
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
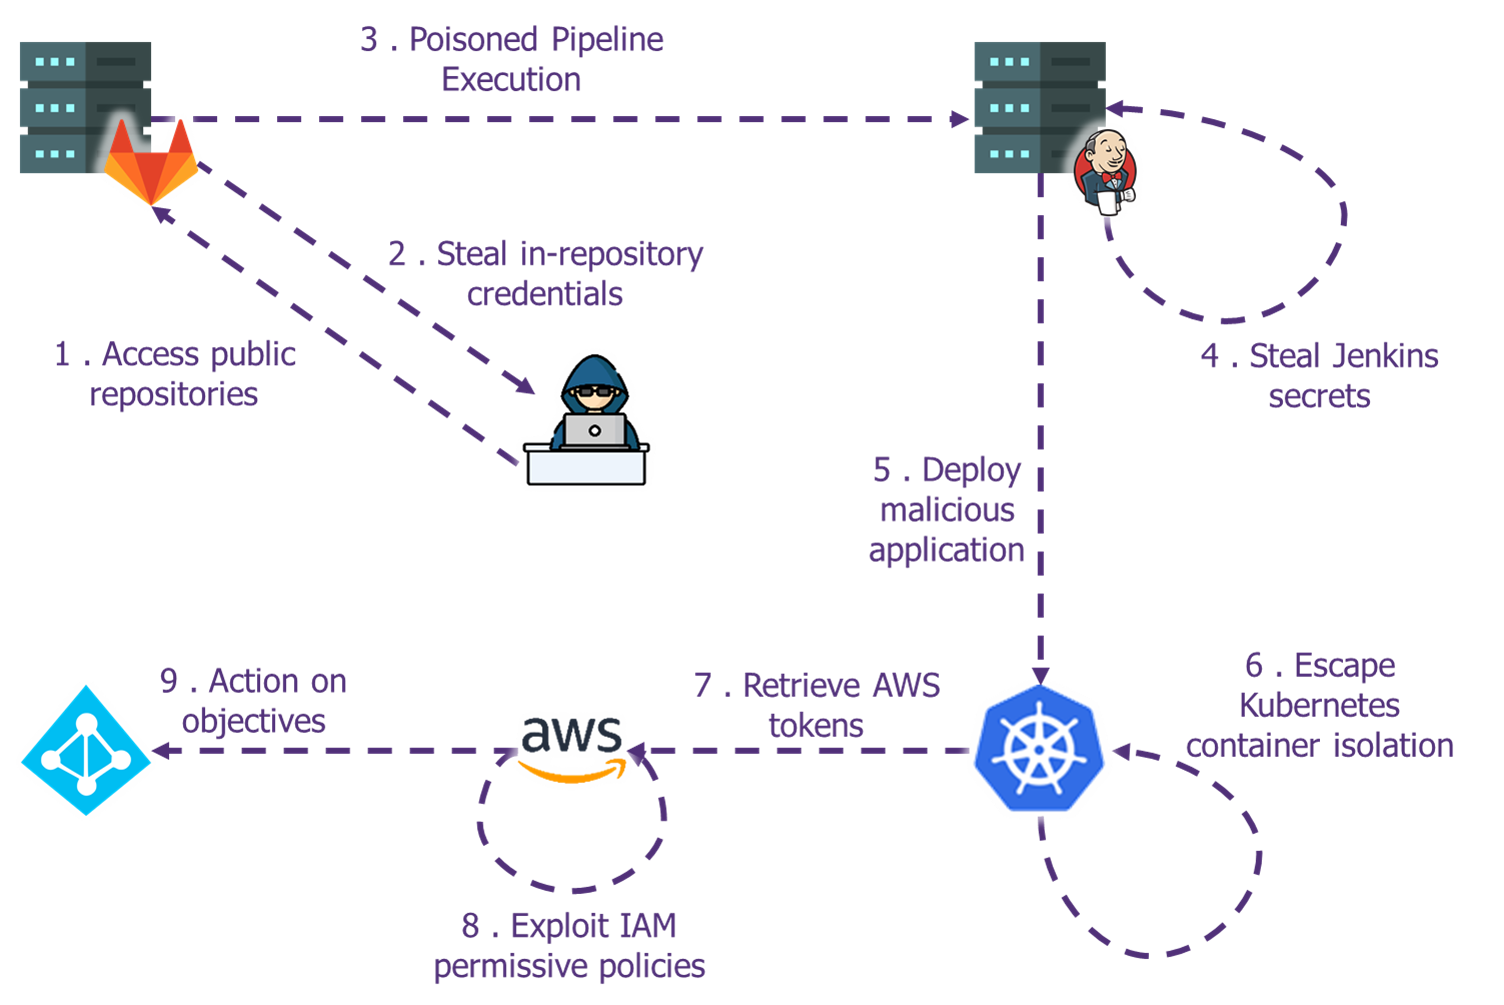 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 pop3ret/awsome-pentesting
My cheatsheet notes to pentest AWS infrastructure
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
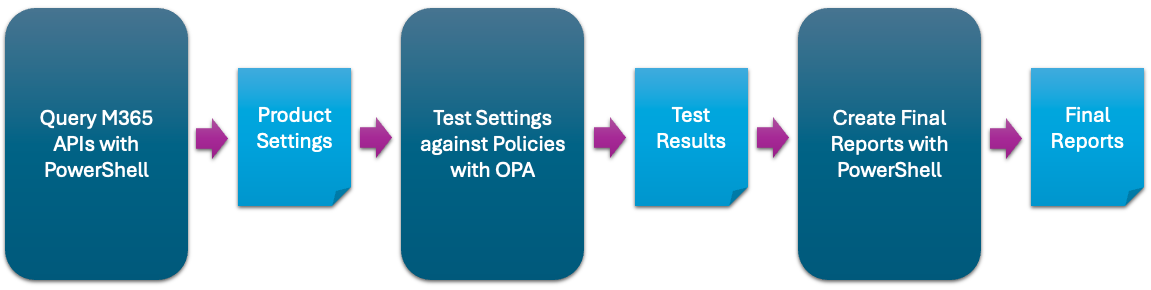 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 dafthack/cloudpentestcheatsheets
This repository contains a collection of cheatsheets I have put together for tools related to pentesting organizations that leverage cloud providers.
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 taleliyahu/threat_model_examples
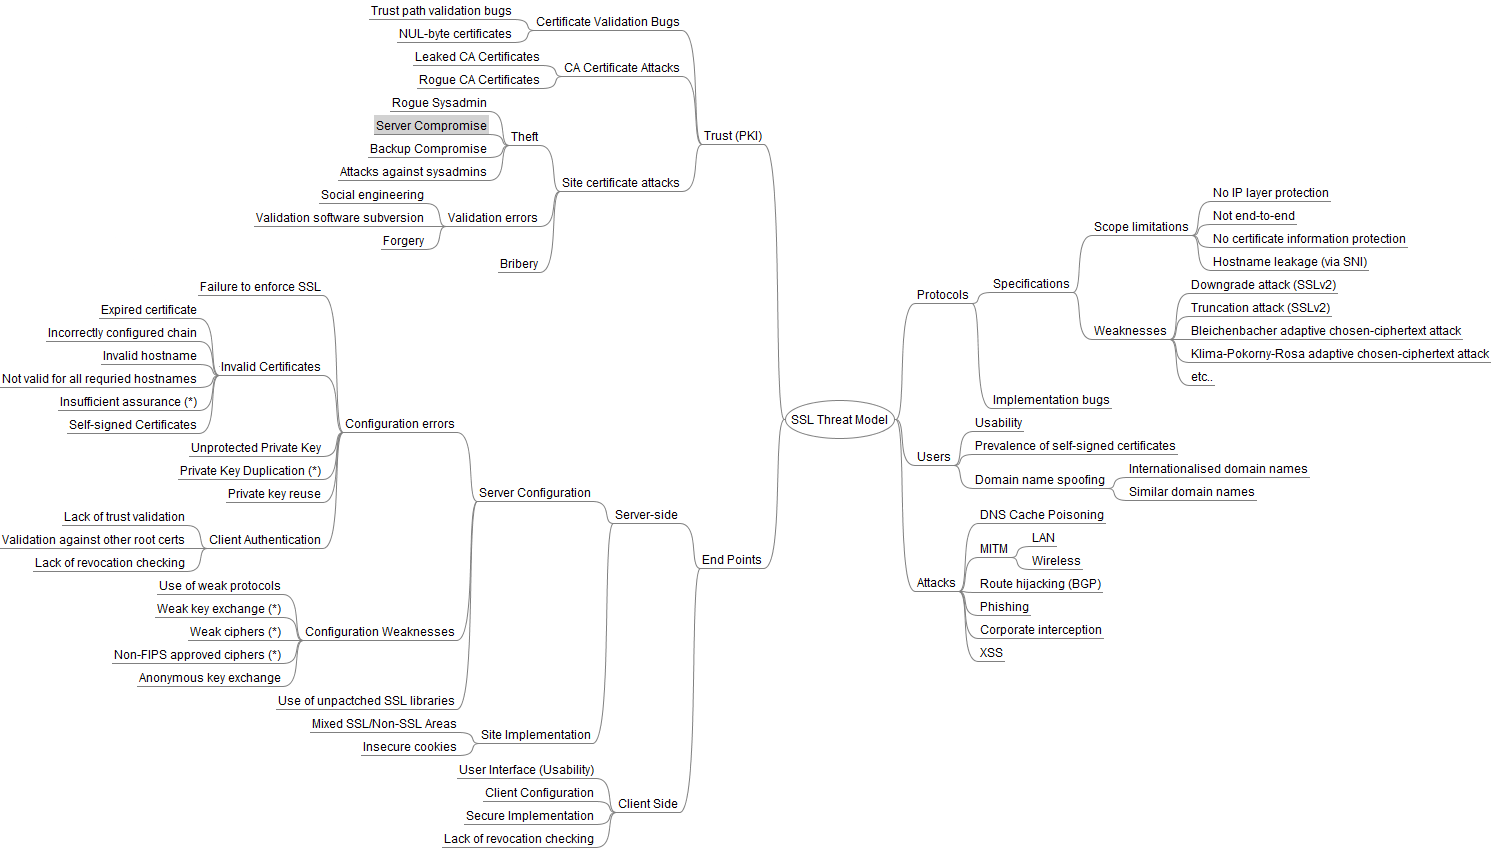
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 daddycocoaman/azbelt
AAD related enumeration in Nim