ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Rust-powered HTTP Request Smuggling Scanner.

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

Discover hidden parameters in Caido

A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library

A Burp Extension designed to identify argument injection vulnerabilities.

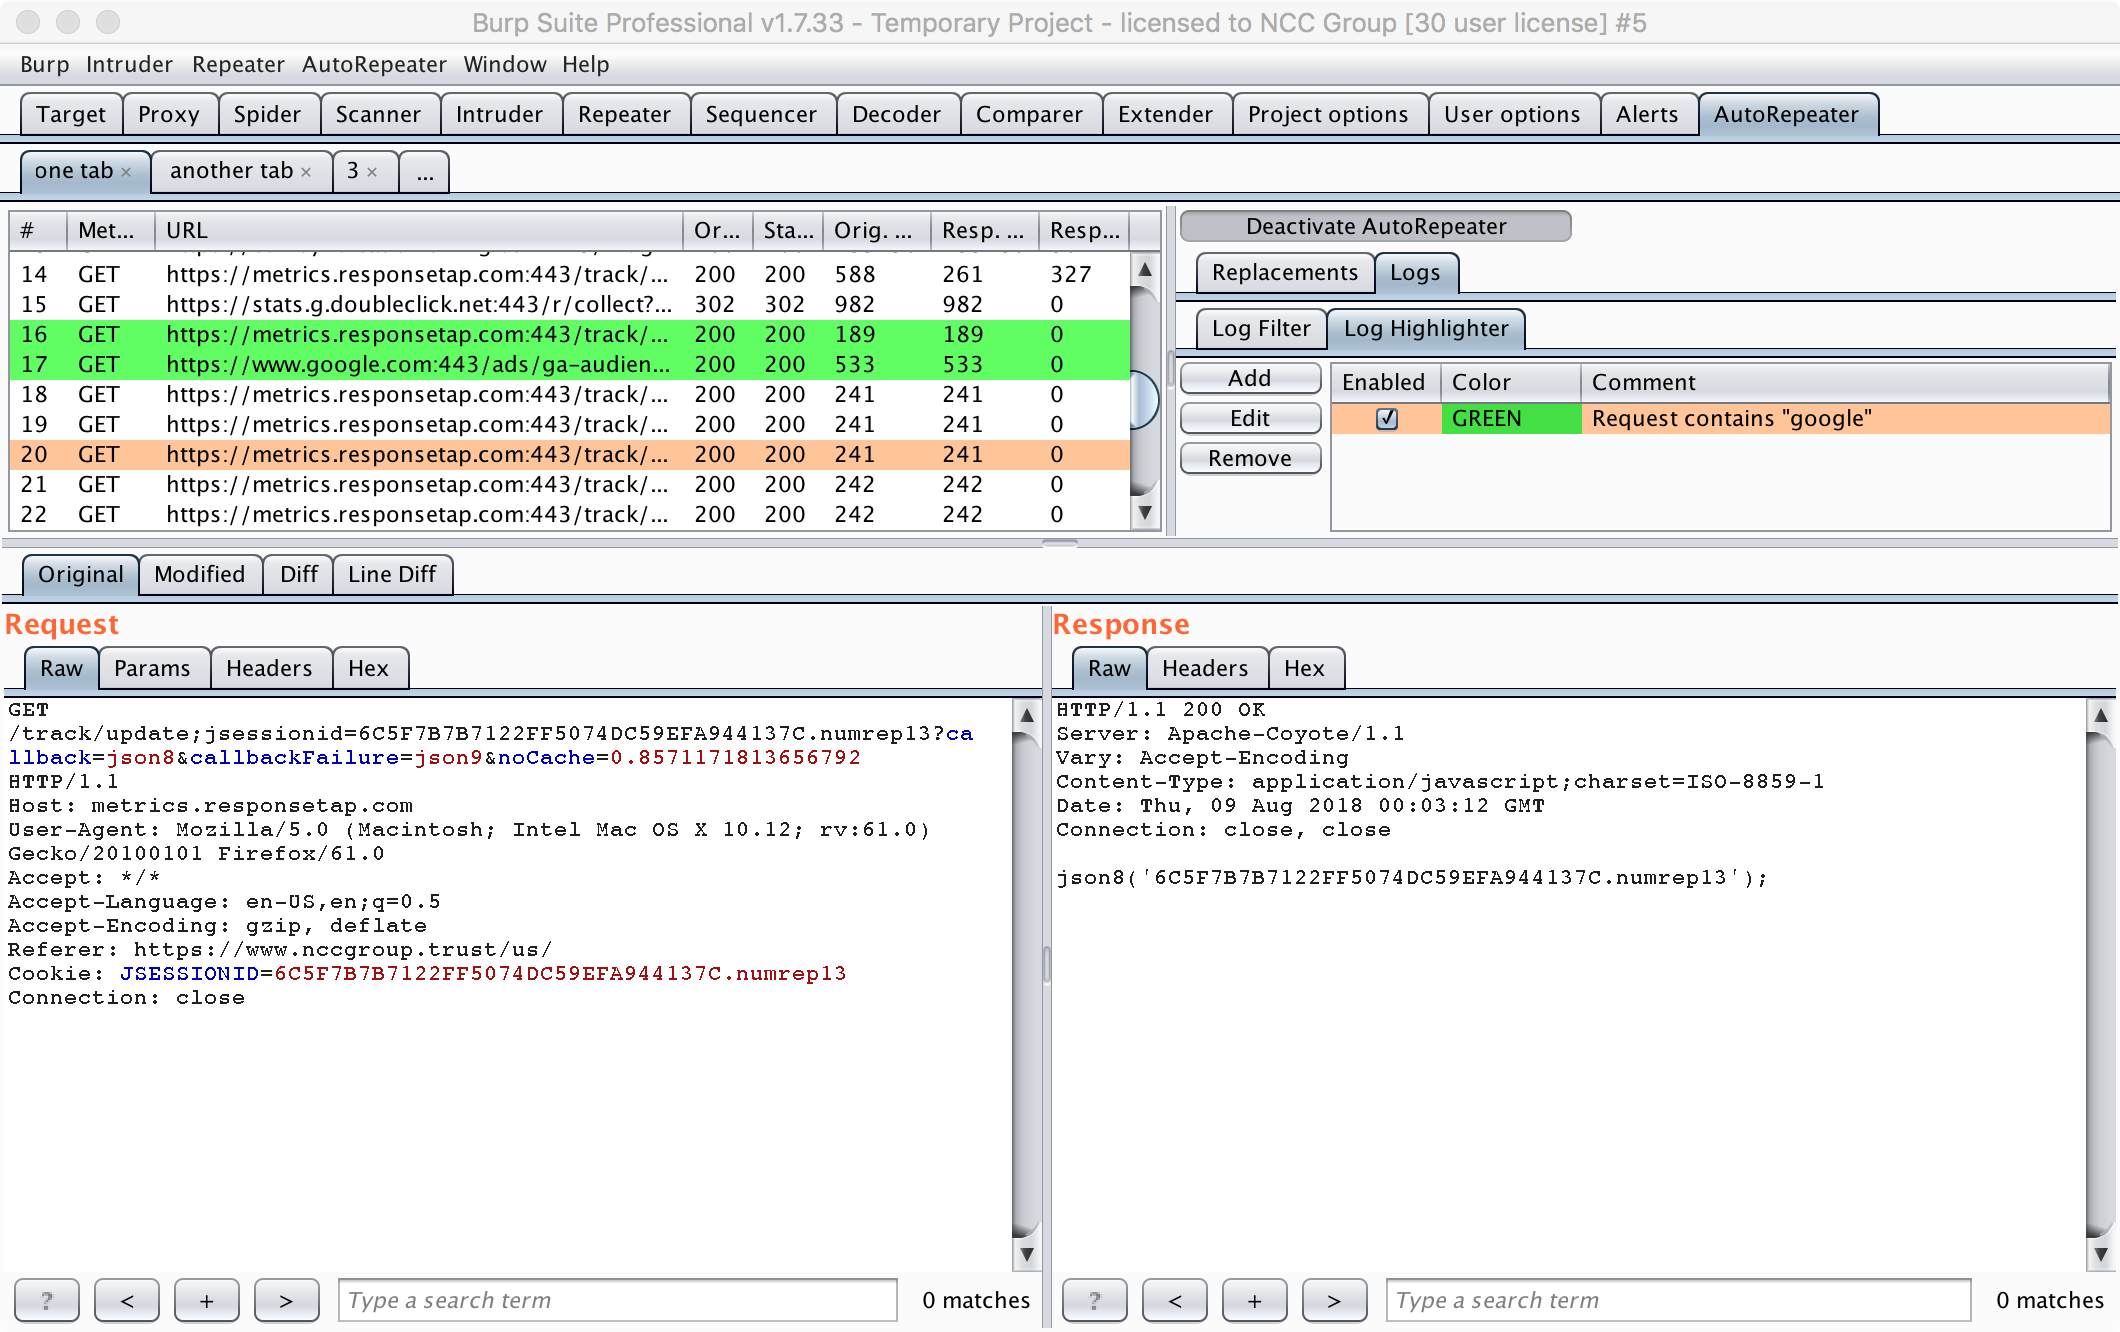
Automated HTTP Request Repeating With Burp Suite

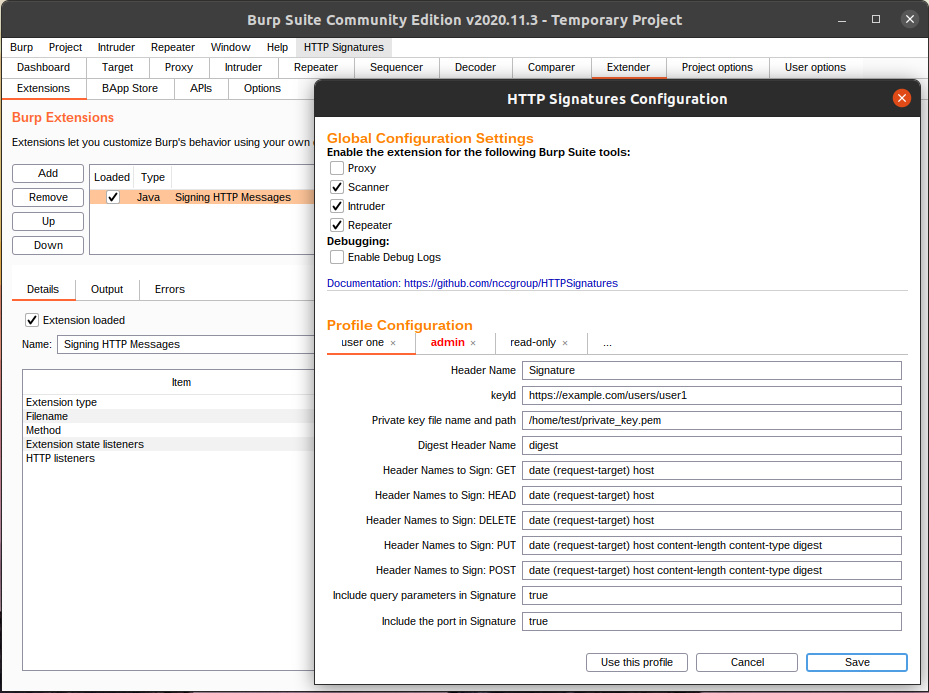
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.

A Burp Extender plugin, that will make binary soap objects readable and modifiable.

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

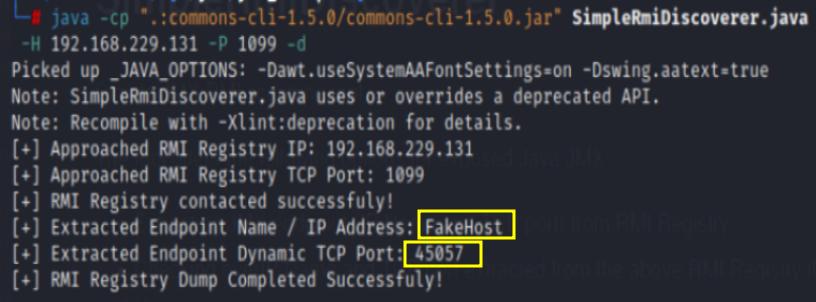
Simple JMX RMI scanning tool

HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite

Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…

find sensitive data leaking from ServiceNow instances.

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

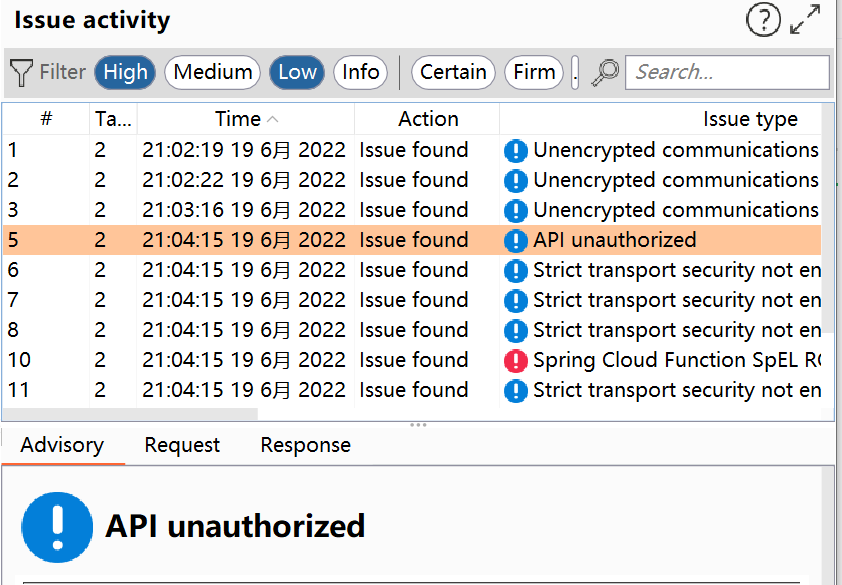
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977