

hidra
 hidra0x/hidra
Research jailbreak project for A12 iOS 18.7.2 devices, chaining the AppleJPEGDriver UAF (CVE-2026-20687) toward a kernel read/write primitive. No…
binary-exploitationexploitationios-security+6
hidra0x/hidraResearch jailbreak project for A12 iOS 18.7.2 devices, chaining the AppleJPEGDriver UAF (CVE-2026-20687) toward a kernel read/write primitive. No…
 mattifinder/rpmc_attacks
Research code and hardware for RPMC attacks: voltage glitching, SPI interposer firmware, and NV-state rollback to brute-force Windows Hello and…
 unsignedchad/cve-2026-21155-sve-2026-3546
Technical writeup and PoC for CVE-2026-21155 (SVE-2026-3546): fail-open signature checks and an unbounded boot-logo JPEG decode in Samsung Exynos…
 yuki493/s5e8835-sboot-probe
Static S-Boot/LK probe for Samsung Exynos 1380 (s5e8835): SVE-2026-3546 / CVE-2026-21155 resolver patch, four-device coverage, and safety notes.
 xen0nize/cve-2026-21096
Crash-only proof-of-concept for CVE-2026-21096, a 32-bit integer overflow leading to heap overflow in Samsung's Quram JPEG decoder, with reversing…
 ostorlab/rasp
Packs a runtime into built APK, AAB or IPA files to detect root, jailbreak, debuggers, Frida hooks, emulators, VPN/proxy interception and repackaging…
 cracked5pider/ldrlibraryex
A small x64 library to load dll's into memory.
 idoka/awesome-automotive-can-id
🚜 Collect of CAN IDs and its payloads for various car brands/models in one place. Might be useful for Cyber Security Researchers, Reverse…
 mosajjal/fortitool
Fortinet Firmware decryption and analysis tools

 droncito/aquadecomp
Orchestrates JADX, CFR, Procyon and Vineflower to decompile Android APK/AAB/XAPK/APKS files, with hidden DEX extraction, deobfuscation, signed APK…
 seifheakal/blue-harness
Make your own app expensive to reverse. A build-time audit, harden and verify harness for native binaries and mobile apps, built to counter…
 deathshotxd/sip2shell
One SIP text message to FreeSWITCH, and you are running commands. Exploit, scanner and a real vulnerable/patched Docker lab for CVE-2026-116779.
 tlsbollei/kittyloader
Evasive Windows loader in C/Assembly that decrypts an embedded payload in memory, unhooks PEB module lists, and applies anti-debug, sandbox and…
 racoten/suture-pic
A Windows implant development framework for offensive engineering and C2 research.
 mein-0/fortiless
Proof-of-concept and analysis of a type-3 kernel out-of-bounds write in FortiClient's FortiShield_74.sys minifilter, including port protocol details…
 ahmedboin/jailbreak
Domain-organized library of reverse engineering playbooks, guides, and research notes for analyzing software and recreating patches, with repeatable…
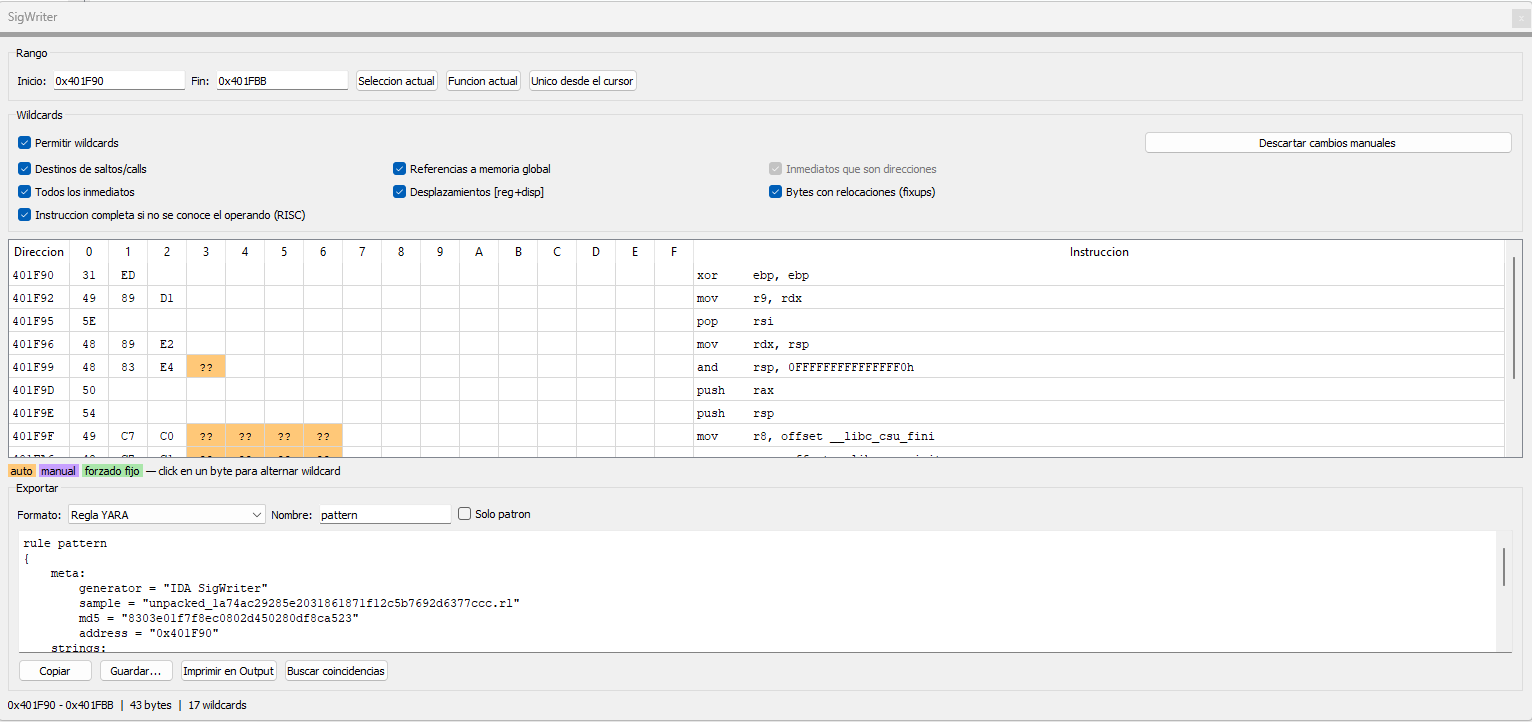 crackinglandia/idasignwriter
IDA Pro plugin that generates byte signatures from disassembly selections, with automatic and manual wildcards, match search, and export to YARA,…
 ryftenius/resx
Specialized Windows Reverse Engineering & Binary Analysis Toolkit | API Deobfuscation, Call Graphs, Kernel Driver & IOCTL Analysis