
 hidra0x/hidra
Research jailbreak project for A12 iOS 18.7.2 devices, chaining the AppleJPEGDriver UAF (CVE-2026-20687) toward a kernel read/write primitive. No public build yet.




A12 / iOS 18.7.2 — from AppleJPEGDriver UAF to kernel r/w.
Hidra is a research jailbreak project for A12 devices on iOS 18.7.2. It builds
on the kernel UAF in AppleJPEGDriver (CVE-2026-20687) and the controlled
free/reclaim work in hidgate-poc.
There is no public jailbreak build yet. Hidra is a research project, not a working jailbreak. It does not provide kernel read/write today, does not bypass PAC/PPL/SPTM yet, and does not install anything. Do not run research builds on a primary phone.
«Паника — это не конец. Это доказательство, что мы уже в ядре.» Crash → Control → Jailbreak.
The first path (IOHIDFamily, CVE-2026-28992) is crash-only on the reachable
SPU provider: the freed object is provider-side and copyEvent never delivers
an event on this target. The second path (AppleJPEGDriver,
CVE-2026-20687) is different:
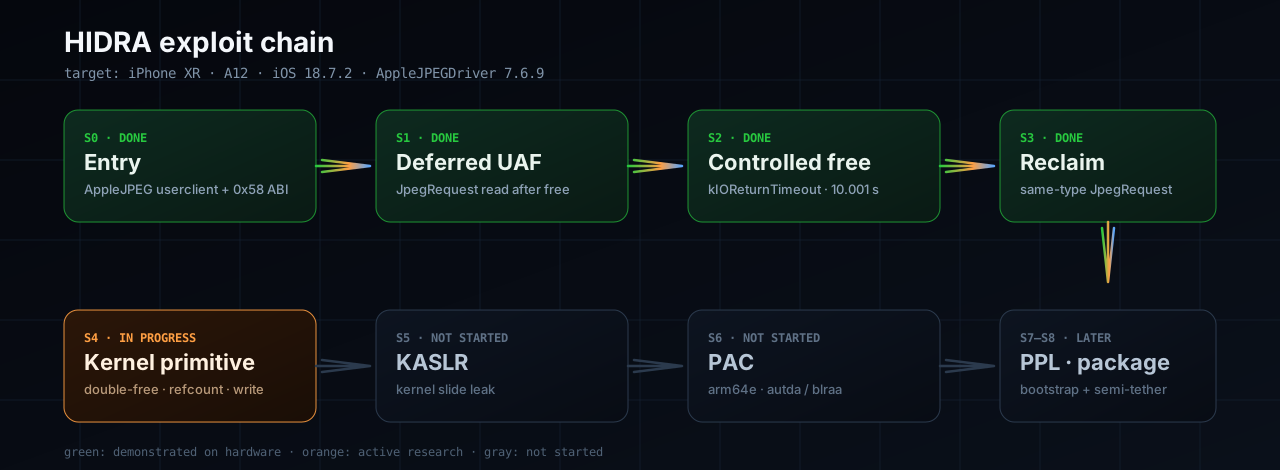
0x58 decode ABI works;kIOReturnTimeout;JpegRequest can be reclaimed with a same-type request;That is enough to start building a kernel primitive. It is not enough for a jailbreak yet.
The open-source entry PoC is MOON Probe:
hidgate-poc/PoC/applejpeg.
It demonstrates the userclient, the 0x58 ABI, and the deferred UAF.
A sideloaded app opens AppleJPEGDriver type 0, submits async decodes, and
forces a synchronous decode into the 10 s timeout. This is already working on
the test device.
The timeout frees a JpegRequest while its embedded queue node remains in the
per-codec vector. A same-type allocation replaces the freed object. The next
goal is to turn this into one of:
JpegRequest;IOSurface or IOUserClient;The public PoC's *(*(request+0)+0x28)() path is PAC-protected on A12
(autda + blraa), so a fake vtable is not the first move.
A kernel read or a side channel must reveal the kernel slide and the addresses
of the objects used by the primitive. The standard proc_pidfdinfo,
mach_port_kobject, and mach_vm_region surfaces are clean on 18.7.2.
A12 is arm64e. The kernel uses PAC for function pointers and data pointers. Hidra needs either a signing gadget/oracle, a data-only path that avoids authenticated pointers, or a leak of a valid signed pointer.
Kernel text and page tables are protected. The project needs a data-only page-table attack, a PPL bypass, or a supported kernel patch primitive before it can install a bootstrap.
The first target is a semi-tethered jailbreak: the device boots normally, the user runs the Hidra app after a reboot, and the bootstrap is reapplied. Untethered persistence is a later goal.
The package will ship as:
The PC-side harness is in loader/. It implements the
semi-tethered loop:
reboot -> normal iOS -> run hidra_loader.py -> launch the agent
      -> capture stage markers -> reapply the kernel patch
It uses pymobiledevice3 for USB device info, app launch, and syslog. The
current agent is CandProbe, which emits HIDRA_STAGE0_DONE through
HIDRA_STAGE8_DONE. HIDRA_JAILBROKEN is reserved until a real kernel
primitive lands.
python -m pip install pymobiledevice3
python loader/hidra_loader.py doctor
python loader/hidra_loader.py jailbreak --seconds 30
The loader is not a jailbreak by itself. It is the transport and test loop for the missing S4-S7 stages.
| Stage | Component | State |
|---|---|---|
| S0 | Entry app + AppleJPEG userclient | DONE |
| S1 | Deferred JpegRequest UAF | DONE |
| S2 | Controlled 10 s free | DONE |
| S3 | Same-type reclaim | DONE |
| S4 | Double-free / write primitive | IN PROGRESS |
| S5 | KASLR + PAC | NOT STARTED |
| S6 | PPL / SPTM + persistence | NOT STARTED |
| S7 | Package / bootstrap | NOT STARTED |
The detailed control ladder is in
hidgate-poc/docs/kernel-control.md.
Latest result: jpegclose (close the userclient during a sync decode)
reproduces the far=0x308 UAF without Camera. The paired reclaim still
misses the slot (x12=0), so S4 remains open.
| Device | SoC | iOS | State |
|---|---|---|---|
iPhone XR (iPhone11,8) | A12 / T8020 | 18.7.2 (22H124) | Primary test device |
| iPhone XS / XS Max | A12 | 18.7.x | Untested; same kext family likely |
| iPhone 11 / SE 2 | A13 | 18.7.x | Untested; may share the driver |
| iPhone 12 and newer | A14+ | any | Not supported initially |
| iOS 18.7.7+ / 26.4+ | — | — | Patched, not supported |
The project starts with the device we can test: iPhone XR on 18.7.2. Support for other A12/A13 devices will be added only after the kernel primitive is stable.
There is no promised release date. The date below is a research estimate and will slip if a stage fails.
| Milestone | Target window | Exit criterion | Confidence |
|---|---|---|---|
| M4 | Nov–Dec 2026 | reproducible double-free or write primitive | medium-low |
| M5 | Dec 2026–Feb 2027 | KASLR leak + PAC bypass or data-only path | low |
| M6 | Mar–May 2027 | PPL/SPTM bypass + bootstrap prototype | low |
| M7 | Q2 2027 | closed beta on iPhone XR 18.7.2 | low |
| M8 | Q3 2027 | public beta, if M4–M6 pass | low |
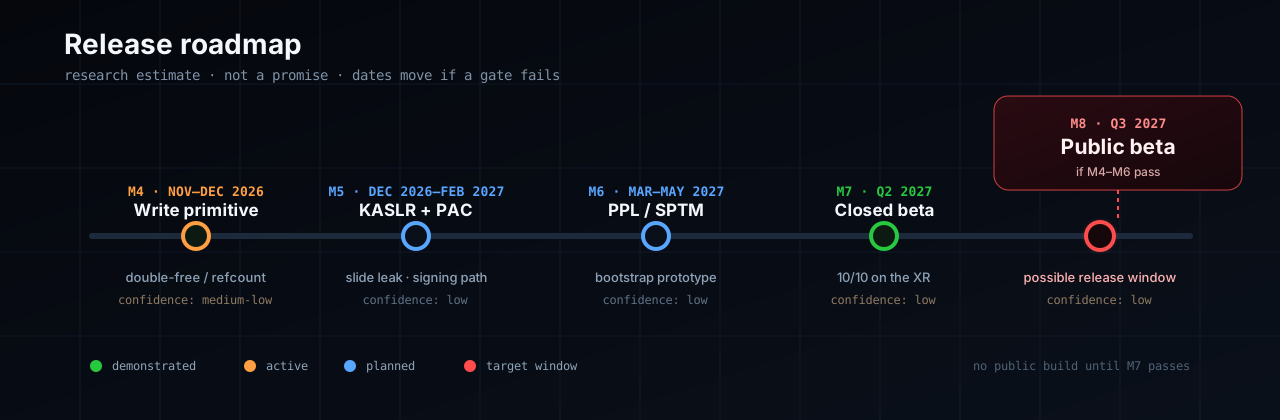
Possible public release window: Q3 2027. This is not a promise. If PAC or PPL cannot be bypassed, Hidra may ship as a kernel r/w research toolkit instead of a jailbreak.
hidra/
  README.md
  docs/
    index.html           # dark landing page (GitHub Pages)
    architecture.md      # exploit chain, stage by stage
    roadmap.md           # milestones, dates, exit criteria
    faq.md               # device/support questions
  loader/
    hidra_loader.py      # PC-side semi-tethered harness
    README.md            # usage and limitations
  assets/
    banner.svg
    logo.svg
    architecture.svg
    roadmap.svg
  SECURITY.md
  CONTRIBUTING.md
  LICENSE
The research base, PoCs, panic logs, and test matrix live in
hidgate-poc.






