
 ostorlab/rasp
Packs a runtime into built APK, AAB or IPA files to detect root, jailbreak, debuggers, Frida hooks, emulators, VPN/proxy interception and repackaging at runtime.



Runtime application self-protection (RASP) for Android and iOS apps.
rasp protects an app you have already built. It adds a small runtime to the APK, AAB or IPA, and the protected app checks the device it runs on and itself while it is in use. No change to the app's source code is needed.
https://github.com/user-attachments/assets/a43d48ed-75ec-43b1-ad76-77fc08826493
your app (APK / AAB / IPA)
        │
        ▼
  rasp pack --checks …        adds the runtime and writes the chosen checks into its config
        │
        ▼
protected app (unsigned)  ──▶  you sign it and ship it
        │
        ▼
on the device                  the runtime runs the chosen checks and hands the observations
                               to its plugins; a development build also logs them
A plugin is code compiled into the runtime (API, example). It can add its own checks, and it receives the observations of each run, for example to send them somewhere. A runtime built without plugins keeps the observations to itself, and a release build doesn't log them.
packer/, Python) adds the runtime to the app and returns it unsigned.runtime/, C++) runs inside the protected app and runs the checks.Build the runtime for your platform (details):
cd runtime
cmake --preset android
cmake --build --preset android
Put the built files where the packer looks for them: see the READMEs in
packer/src/rasp_packer/android/resources/ and
packer/src/rasp_packer/ios/resources/.
Install the packer:
cd packer
uv sync --locked
Protect an app:
uv run rasp pack app.apk --platform android --build-id my-build-1 --checks root,debugger,hooks --output app-protected.apk
Sign app-protected.apk with your release key, then ship it.
The packer is also a Python library:
import pathlib

from rasp_packer import packer
from rasp_packer import platforms

result = packer.pack(
    app=pathlib.Path("app.ipa"),
    platform=platforms.Platform.IOS,
    output=pathlib.Path("app-protected.ipa"),
    build_id="my-build-1",
    checks=["jailbreak", "debugger", "hooks"],
)
| Group | Android | iOS | Detects |
|---|---|---|---|
root | ✓ | Root files, writable system partitions, SELinux and build properties | |
jailbreak | ✓ | Jailbreak files, sandbox escape and process spawning | |
debugger | ✓ | ✓ | A debugger attached to the app |
hooks | ✓ | ✓ | Frida and other libraries injected into the app |
integrity | ✓ | The runtime's code changed in memory | |
mitm | ✓ | ✓ | VPN tunnels, and proxies on iOS |
identity | ✓ | ✓ | A repackaged copy of the app (always on) |
emulator | ✓ | ✓ | An emulator or the iOS Simulator |
virtualizer | ✓ | The app running inside another app's container |
--checks (or checks= in Python). identity is always added.--checks, only identity runs.Each check and the signals it reports are described in runtime/README.md.
| Protected Android app | Android 12 (API 31) or later. The packer raises a lower minimum SDK to 31. |
| Protected iOS app | iOS 12.0 or later |
| Packer | Python 3.14, uv |
| Runtime build | CMake 4.4, Clang from LLVM 23; the Android NDK, SDK and a JDK for Android; Xcode on a Mac for iOS |
packer/README.md: the packer, its options, build ids and checks.runtime/README.md: the runtime, each check, building and logs.TODO.md: known work that isn't done yet.Don't want to build the runtime yourself, or want to see what your protected apps find on real devices? Mobile ADR (Mobile Application Detection & Response) on the Ostorlab platform protects your apps with rasp and shows their events:
Create an account on the Ostorlab platform and open Mobile ADR.
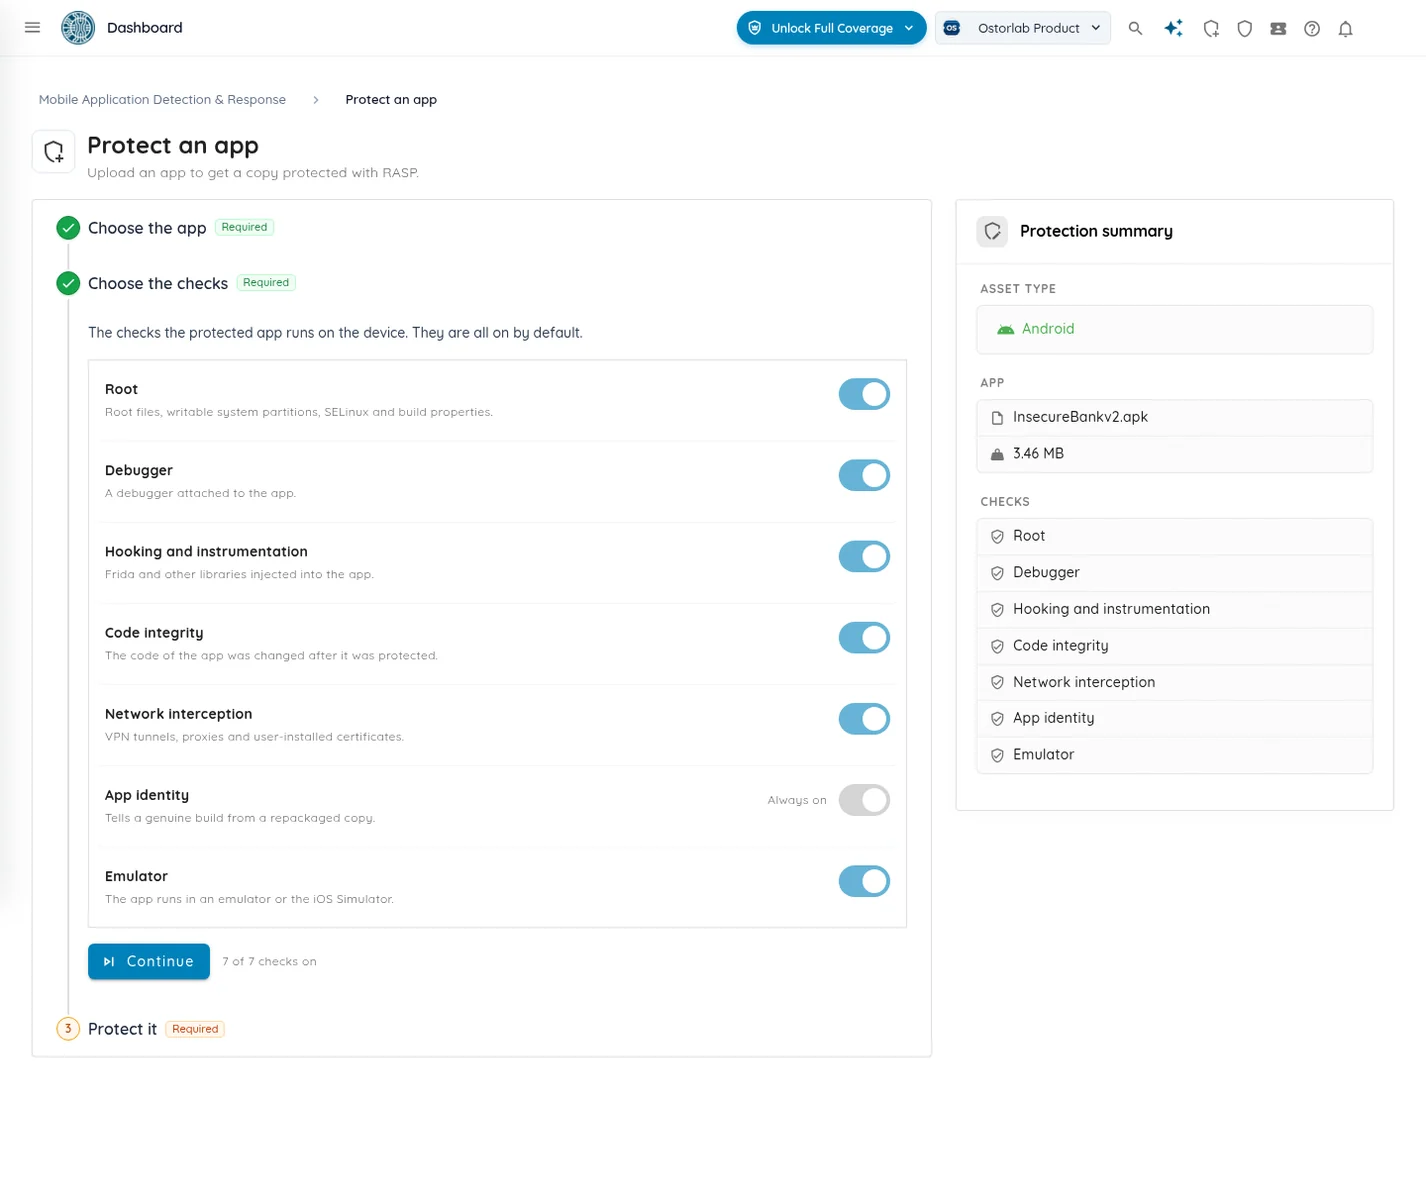
Upload your APK or IPA, choose the checks, and download the protected app (Protect an app).
Sign it and ship it as usual.
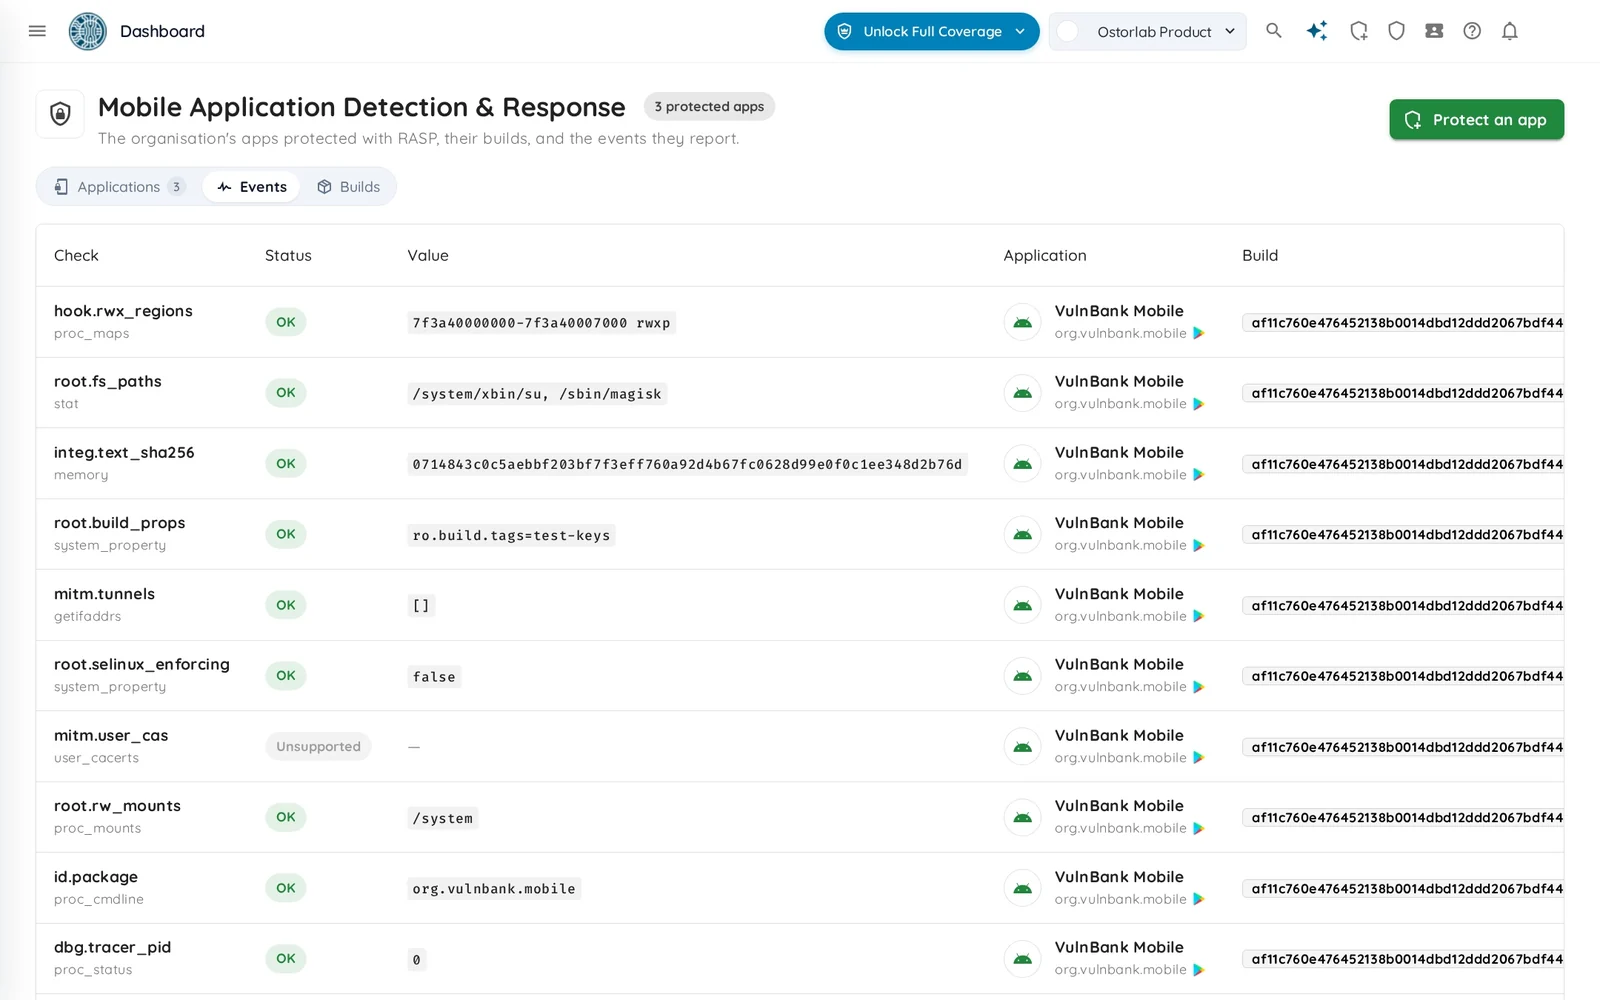
See the events in the Events tab: each check run on a device, what it found (root files, Frida, a VPN tunnel…), and whether the check could run (Events).
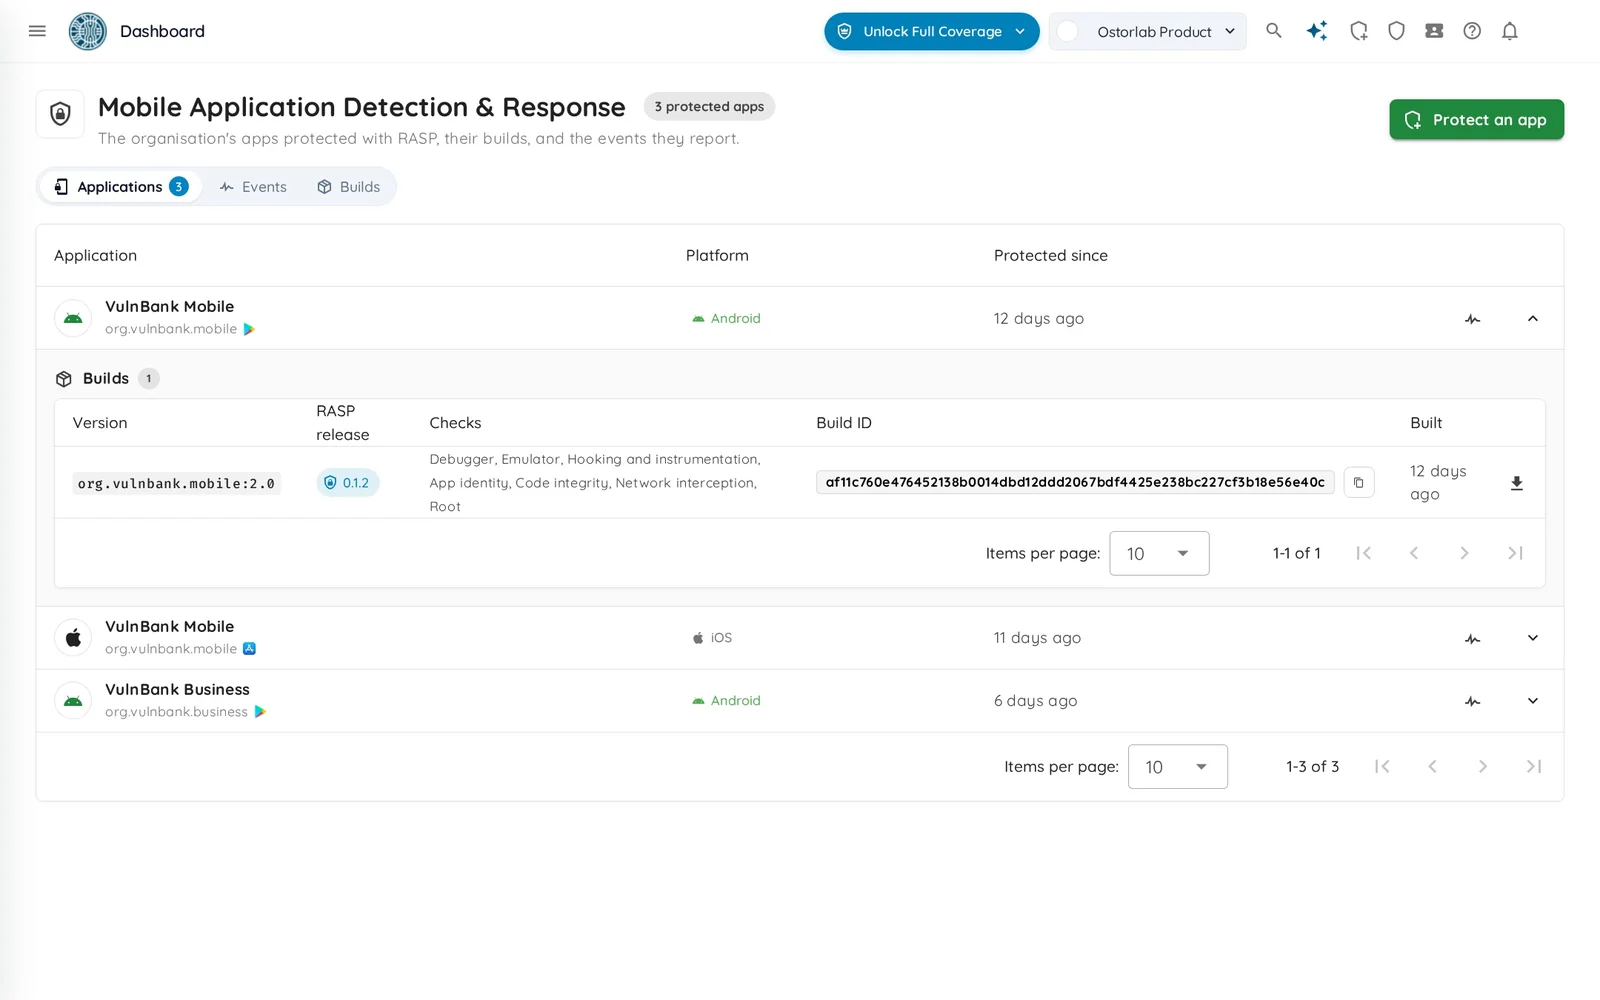
Find every protected version of your app, with its checks and RASP release (Applications and builds).
Contributions are welcome: open an issue or a pull request. Every change goes through a pull request.
packer/README.md (format, lint, types, tests).runtime/CONTRIBUTING.md first. It lists the rules the build enforces and
the ones reviewers check.Please don't report a vulnerability in a public issue. See SECURITY.md.






