

netsniff-ng
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
packet-sniffing-analysisreconnaissancenetwork-mapping+4
1.4k1 year ago
netsniff-ng/netsniff-ngA Swiss army knife for your daily Linux network plumbing.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
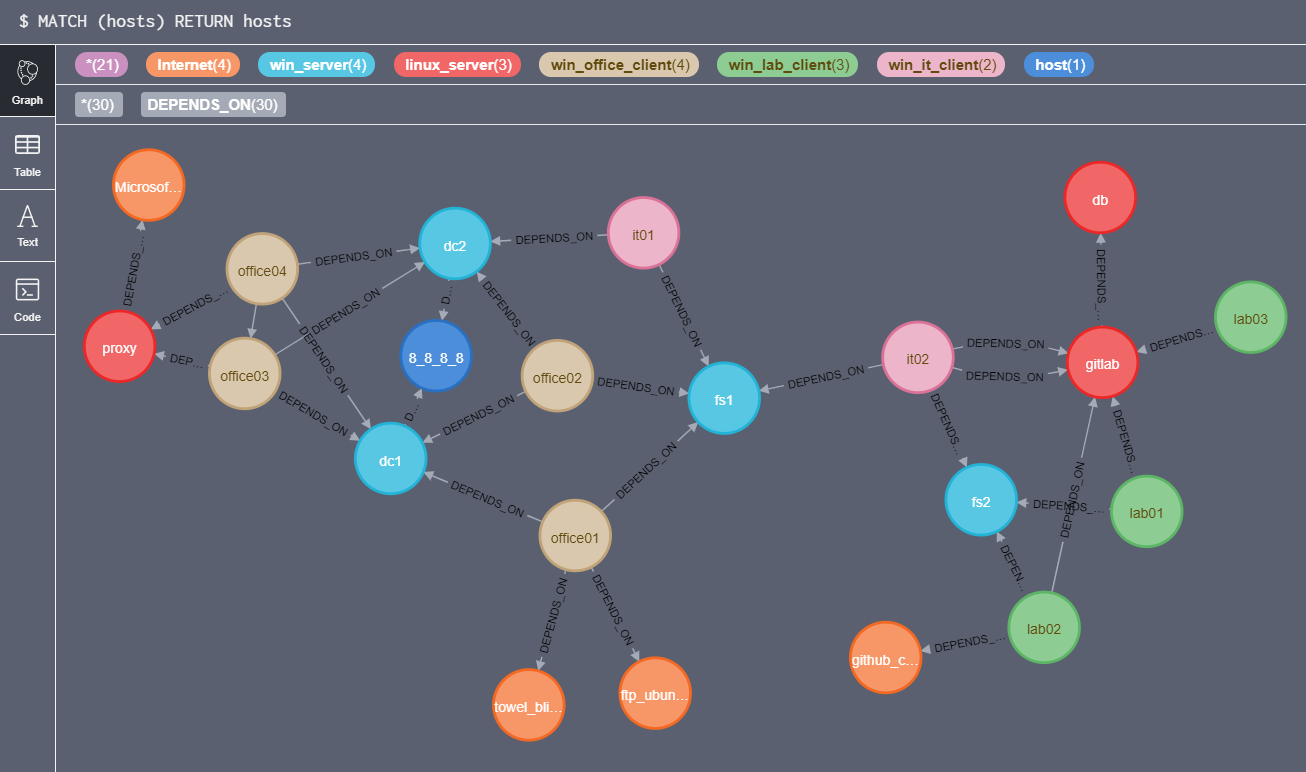 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.