

Driver-SoulExtraction
 gmh5225/driver-soulextraction
SoulExtraction is a windows driver library for extracting cert information in windows drivers
reverse-engineeringmalware-analysisbinary-analysis
gmh5225/driver-soulextractionSoulExtraction is a windows driver library for extracting cert information in windows drivers
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 gmh5225/deobf-arxan-deob-c
Simple C program to quickly deobfuscate windows executables protected with Arxan.
 kaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 tyeurada/edrevasionworkshop
Workshop materials for “Step-by-Step Malware Development: Evading EDR from Loaders to the Kernel” presented at DEF CON 34 and BSidesLV 2026. Covers…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
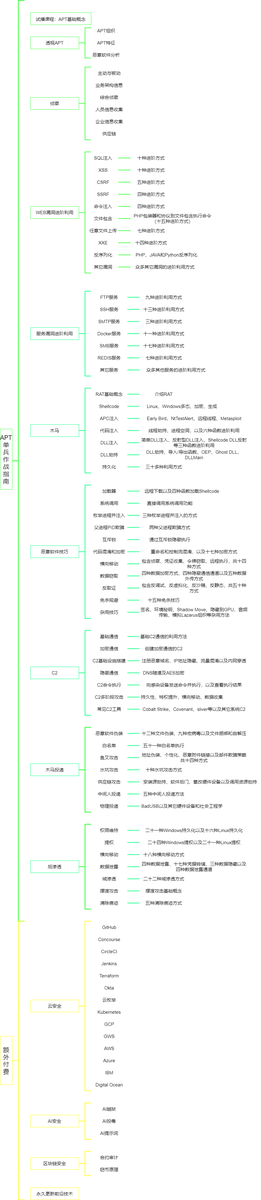 ghostwolflab/apt-individual-combat-guide
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…
 hasherezade/jsc_deobfuscator
Static deobfuscation toolkit for compiled V8 JavaScript bytecode, focusing on JSCeal payloads. Provides pattern-driven filters, control-flow…
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 gmh5225/cripple
Windows kernel driver that removes Process Protection (PP) and Process Protection Light (PPL).