Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Python script for carving Bitlocker VMK keys

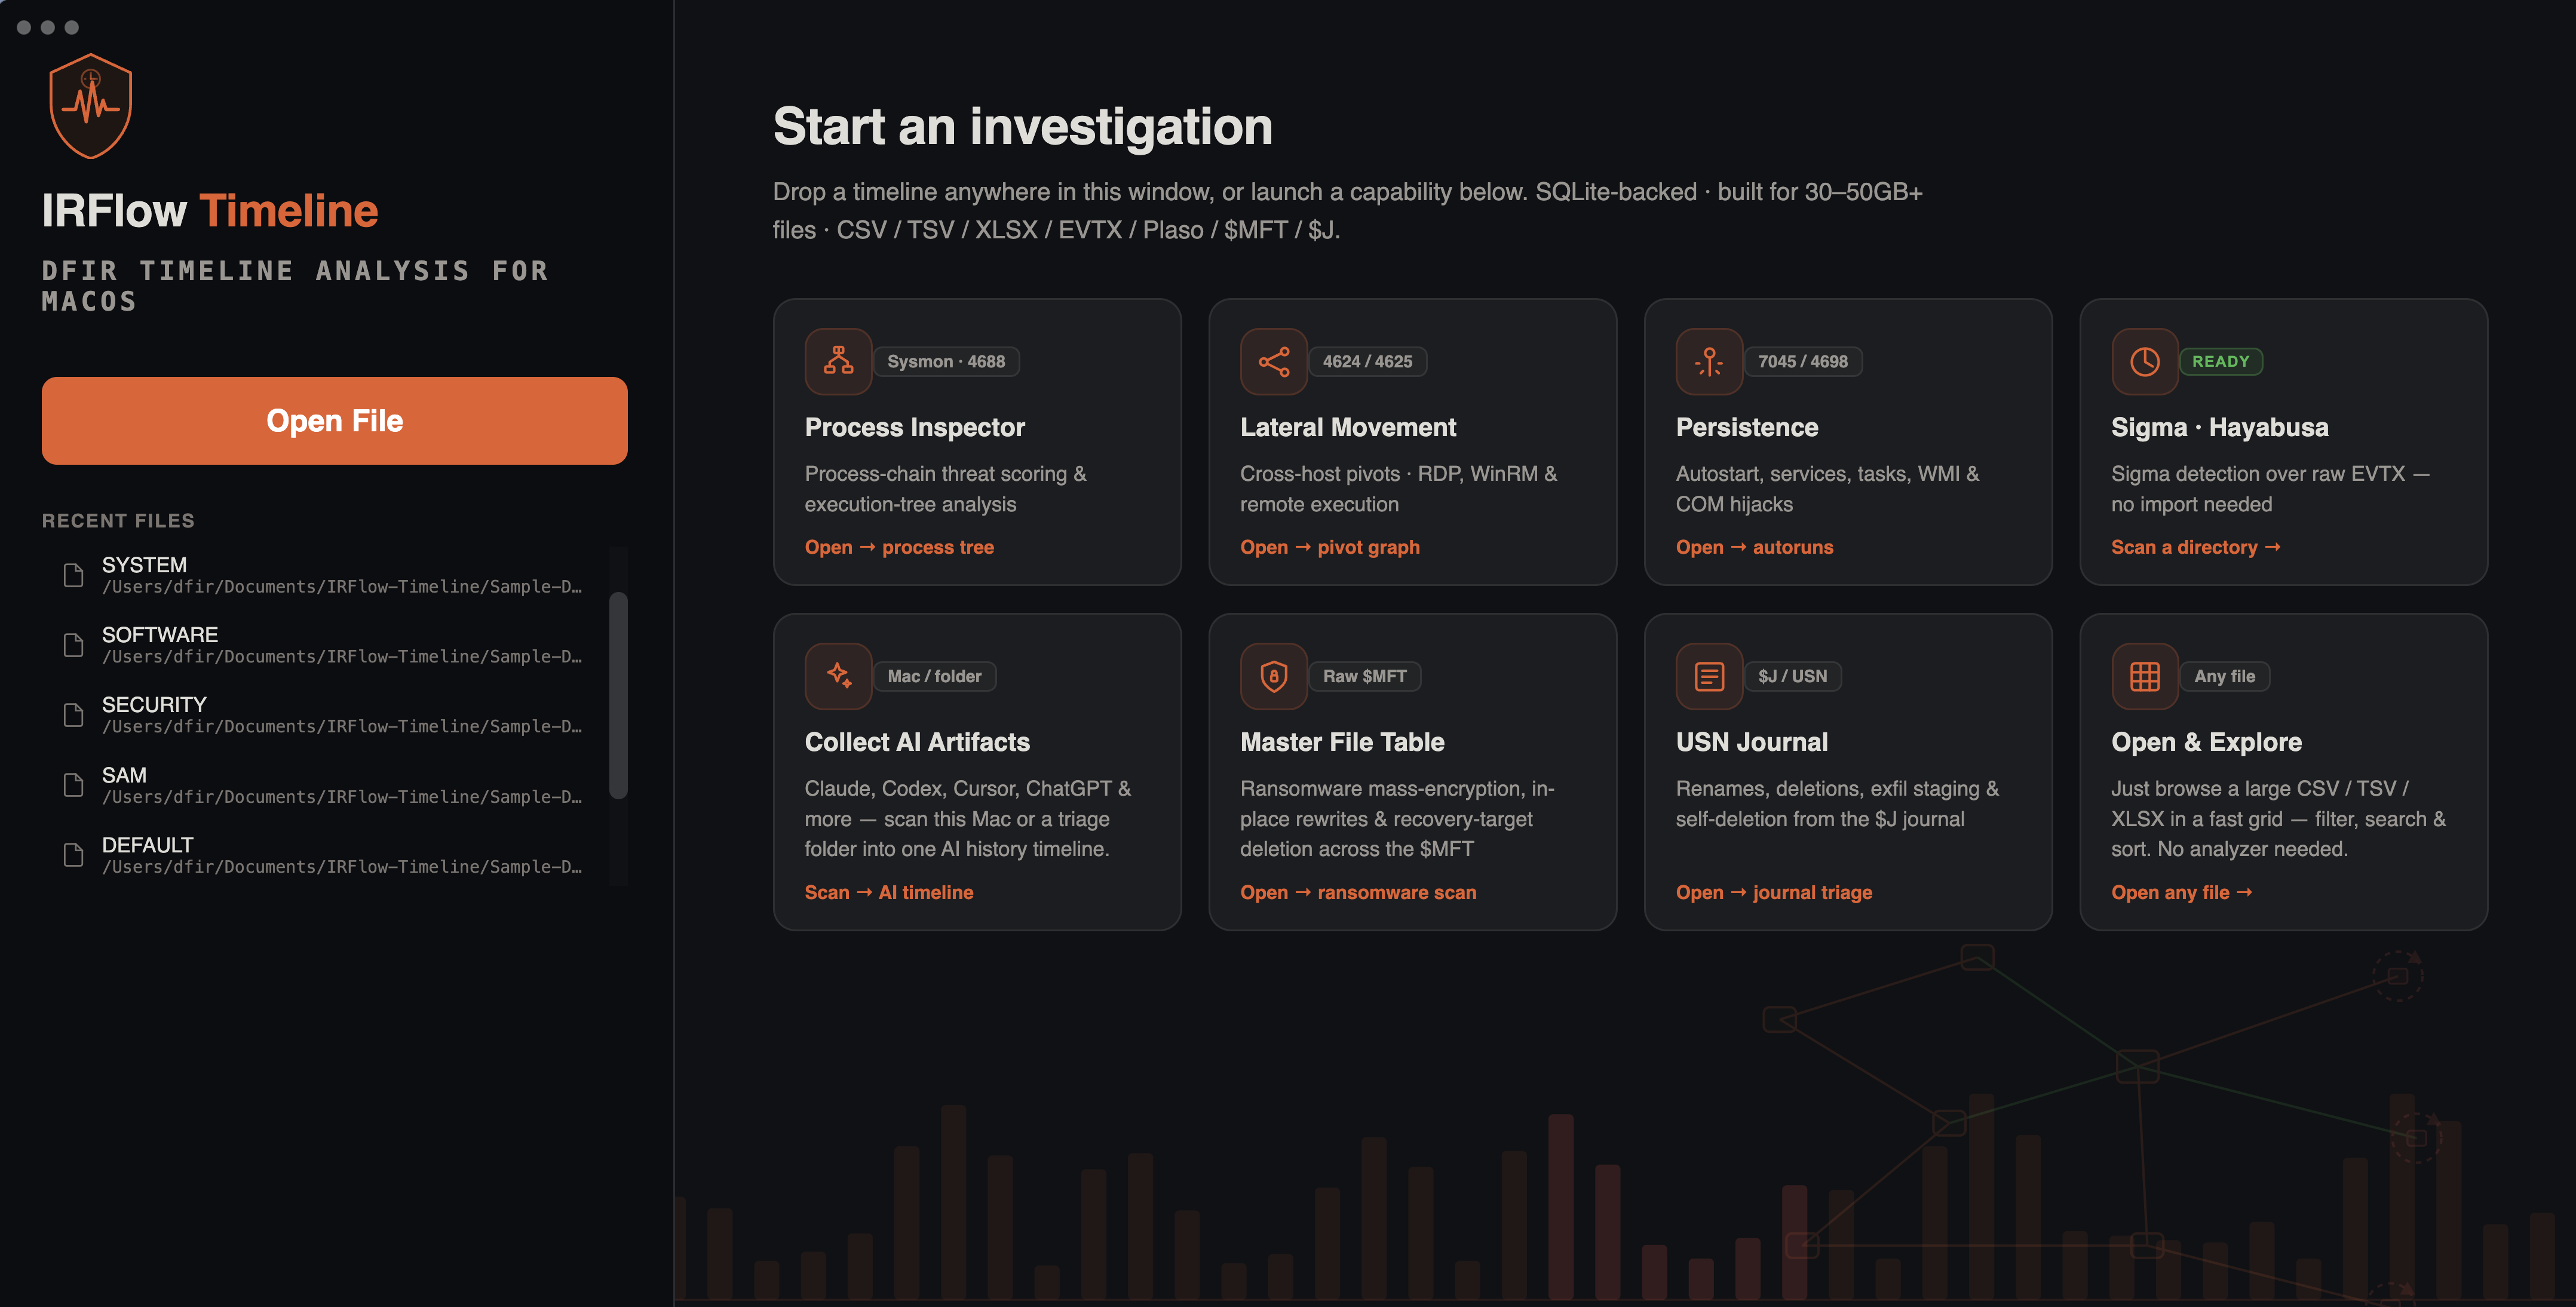
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

Incident Response Forensic Framework

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

A tool for forensic file system reconstruction.


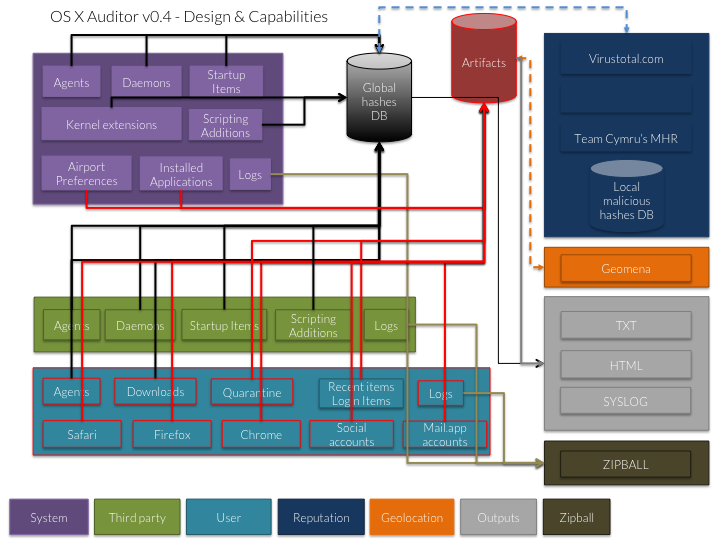
OS X Auditor is a free Mac OS X computer forensics tool

FAT filesystems explore, extract, repair, and forensic tool

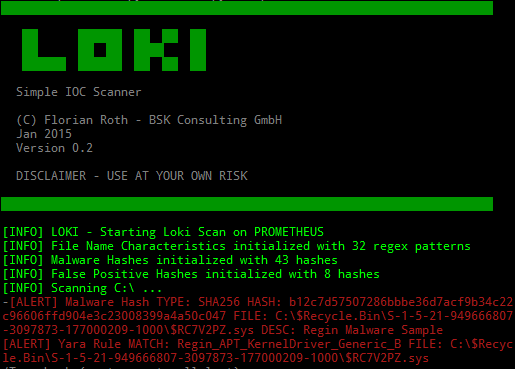
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

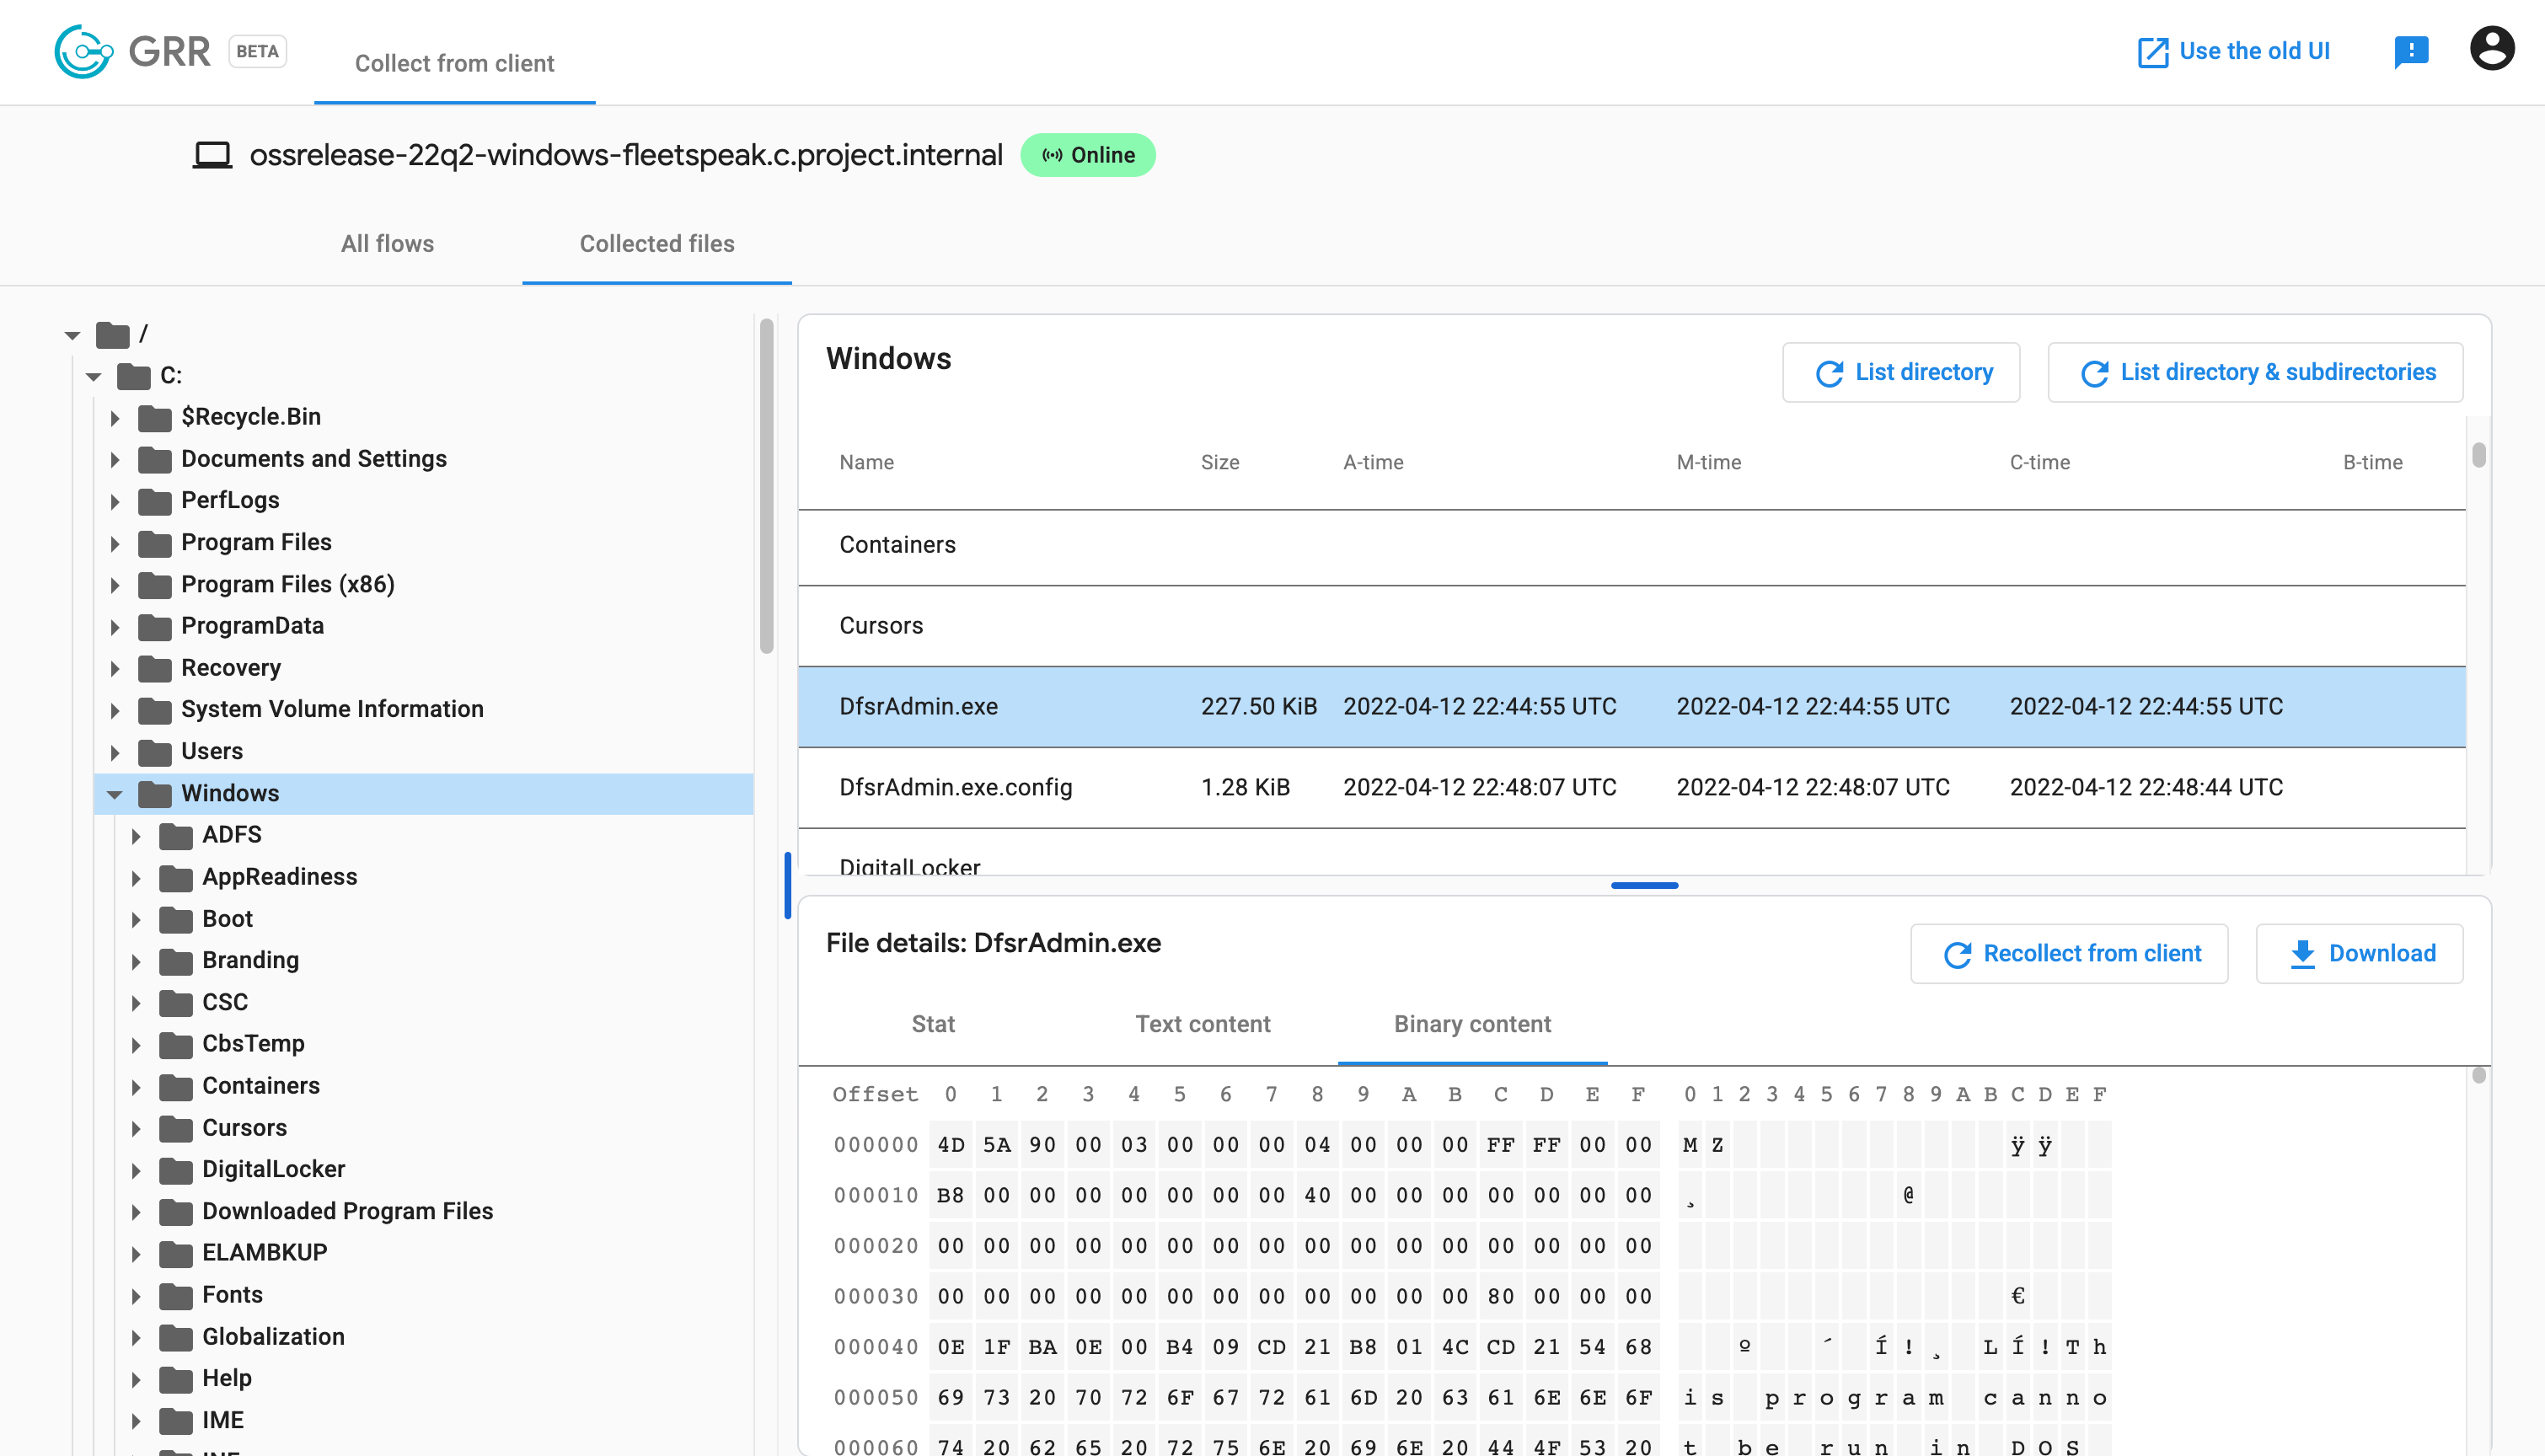
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

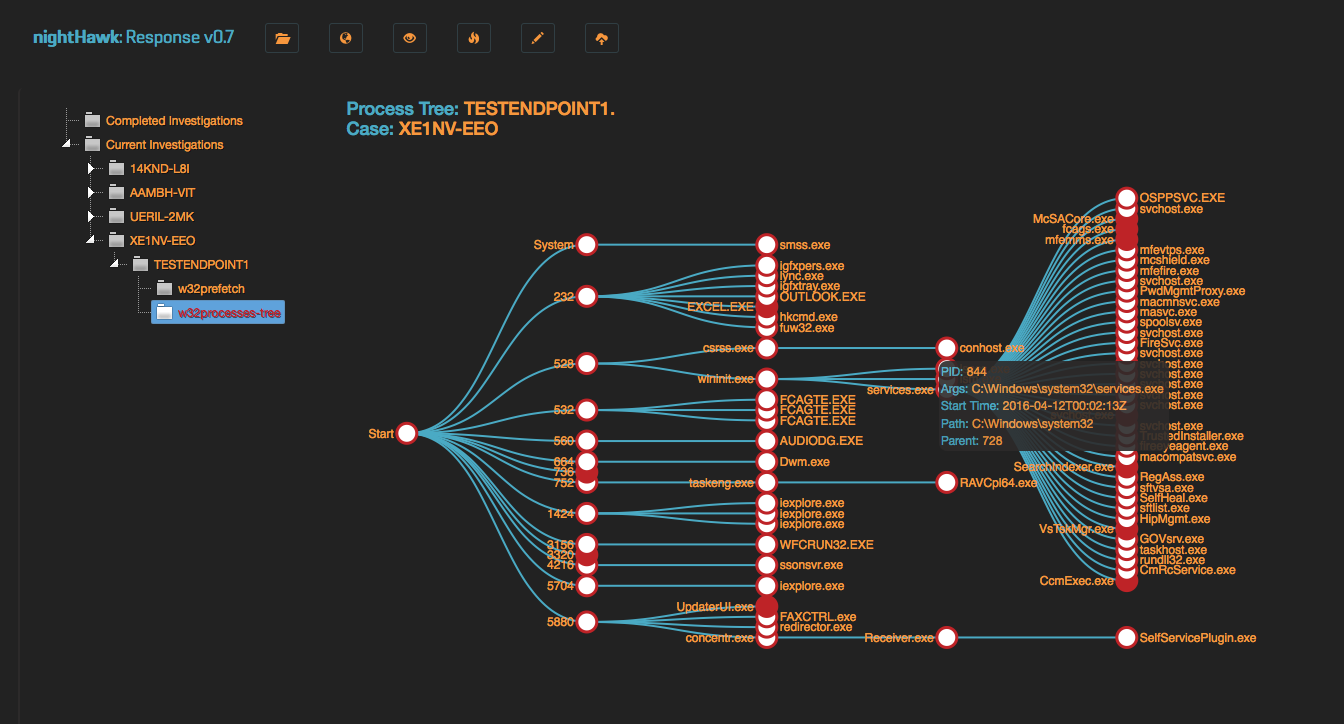
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.

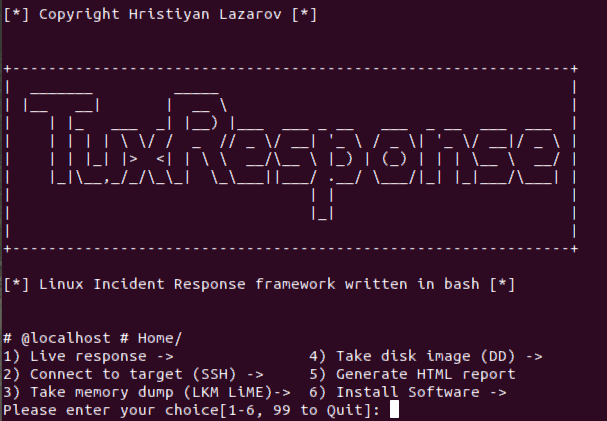
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

It's not just UsnJrnl (USN Journal Records/Change Journal Records) parser.

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…