

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Digital Forensics — Tools — Page 34 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
622 results
DAMM preview
Archived

DAMM

GitHub504ensicslabs/damm

Differential Analysis of Malware in Memory

memory-forensicsvulnerability-analysisforensics+3
215

9 years ago
android-forensics preview
Archived

android-forensics

GitHubnowsecure/android-forensics

Open source Android Forensics app and framework

android-securityforensicsmobile-forensics+2
39711 years ago
HAFNIUM-IOC preview
Archived

HAFNIUM-IOC

GitHubsoteria-security/hafnium-ioc

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865

ioc-managementvulnerability-analysisforensics+3
225 years ago
ioc-scanner-CVE-2019-19781 preview
Archived

ioc-scanner-CVE-2019-19781

GitHubmandiant/ioc-scanner-cve-2019-19781

Indicator of Compromise Scanner for CVE-2019-19781

ioc-managementvulnerability-analysisforensics+4
946 years ago
citrix-ioc-scanner-cve-2023-3519 preview
Archived

citrix-ioc-scanner-cve-2023-3519

GitHubmandiant/citrix-ioc-scanner-cve-2023-3519

Bash-based scanner detecting indicators of compromise from CVE-2023-3519 exploitation on Citrix ADC appliances, supporting live and forensic image…
ioc-managementvulnerability-analysisforensics+3
653 years ago
CVE-2025-57819-ioc-check preview
Archived

CVE-2025-57819-ioc-check

GitHubsucuri-labs/cve-2025-57819-ioc-check

This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
ioc-managementvulnerability-analysisforensics+3
1 year ago
DumpChromeSecrets preview
Archived

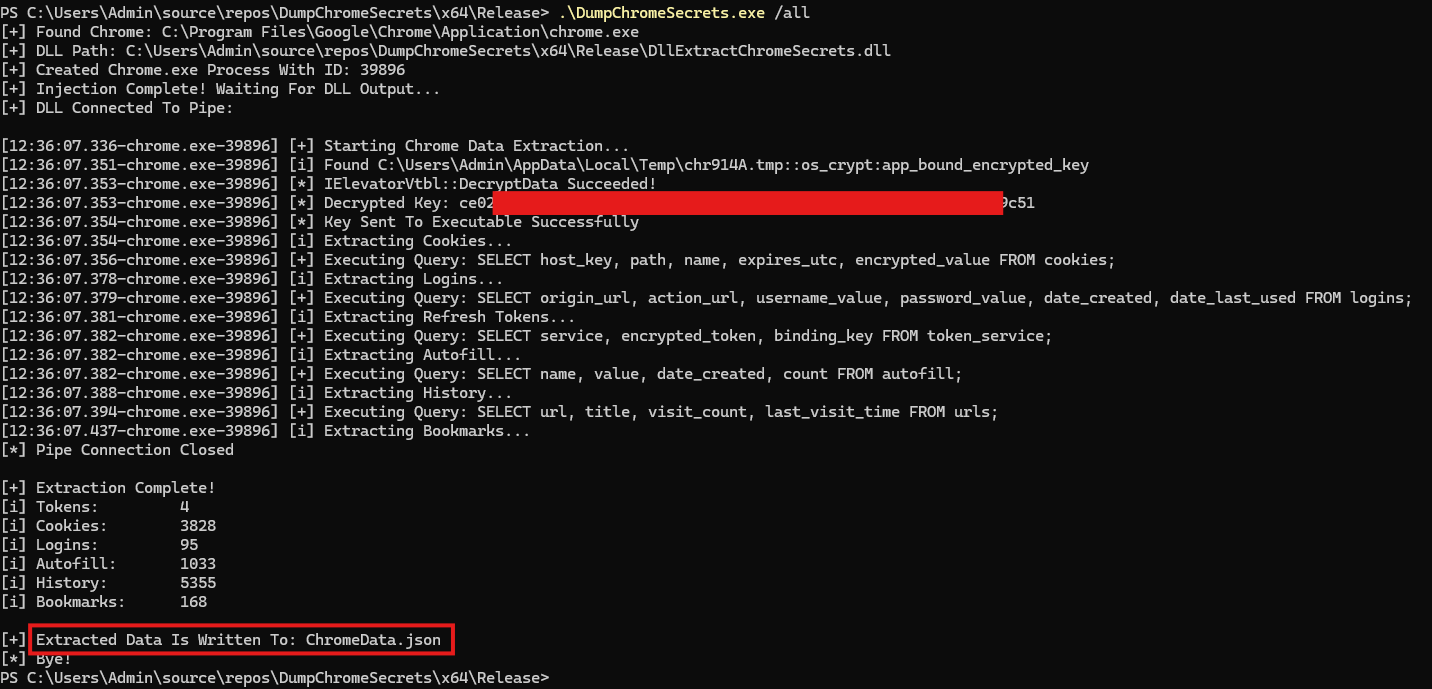
DumpChromeSecrets

GitHubmaldev-academy/dumpchromesecrets

Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
password-crackingreconnaissancedata-exfiltration+8
5589 months ago
ThreatPursuit-VM preview
Archived

ThreatPursuit-VM

GitHubmandiant/threatpursuit-vm

Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…

osintvulnerability-analysisinformation-gathering+8
1.3k3 years ago
Audix preview
Archived

Audix

GitHub0x0v1/audix

Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring

defensive-toolsconfiguration-auditingforensics+4
1181 year ago
grapl preview
Archived

grapl

GitHubgrapl-security/grapl

Graph platform for Detection and Response

reconnaissancethreat-feeds-aggregatorsforensics+8
6993 years ago
osxcollector preview
Archived

osxcollector

GitHubyelparchive/osxcollector

A forensic evidence collection & analysis toolkit for OS X

disk-forensicsosintmemory-forensics+3
1.9k7 years ago
SilkETW preview
Archived

SilkETW

GitHubmandiant/silketw

C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

defensive-toolsmemory-forensicsforensics+8
8523 years ago
varc preview
Archived

varc

GitHubcado-security/varc

Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…

container-securitymemory-forensicsforensics+3
2541 year ago
dumpscan preview
Archived

dumpscan

GitHubdaddycocoaman/dumpscan

Finding secrets in kernel and user memory

encryption-decryption-toolsmemory-forensicsforensics+4
1183 years ago
rip_raw preview
Archived

rip_raw

GitHubcado-security/rip_raw

Rip Raw is a small tool to analyse the memory of compromised Linux systems.
memory-forensicsforensicsdata-recovery+3
1334 years ago
Mandiant-Azure-AD-Investigator preview
Archived

Mandiant-Azure-AD-Investigator

GitHubmandiant/mandiant-azure-ad-investigator

Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…


digital-forensicscloud-securitythreat-intelligence+4
6503 years ago
FAMA preview
Archived

FAMA

GitHublabcif/fama

Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser

android-securityforensicsinformation-gathering+3
1532 years ago
pe_tree preview
Archived

pe_tree

GitHubblackberry/pe_tree

Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…

memory-forensicsvulnerability-analysisreverse-engineering+5
1.3k4 years ago
Previous1…333435Next