
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Digital Forensics — Tools — Page 29 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
622 results
WhatsDump preview

WhatsDump

GitHubmarcog3/whatsdump

Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
android-securityencryption-decryption-toolsforensics+2
2695 years ago
pict preview

pict

GitHubthomasareed/pict

Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
forensicsinformation-gatheringpost-exploitation+2
953 years ago
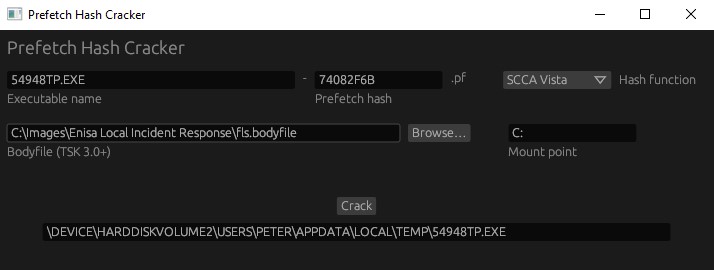
prefetch-hash-cracker preview

prefetch-hash-cracker

GitHubharelsegev/prefetch-hash-cracker

Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

password-crackingforensicsdigital-forensics+1
784 years ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
general-purpose-utilitiesmemory-forensicsnetwork-mapping+6
15.6k10h 25m ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
ioc-managementdynamic-analysis-sandboxingmemory-forensics+9
452 years ago
usbsas preview

usbsas

GitHubcea-sec/usbsas

Tool and framework for securely reading untrusted USB mass storage devices.

defensive-toolsdata-recoverydigital-forensics+1
3732 days ago
aftermath preview

aftermath

GitHubjamf/aftermath

Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
memory-forensicsforensicsdigital-forensics+3
5941 year ago
winevt_logs_analysis preview

winevt_logs_analysis

GitHubgeorgi-i/winevt_logs_analysis

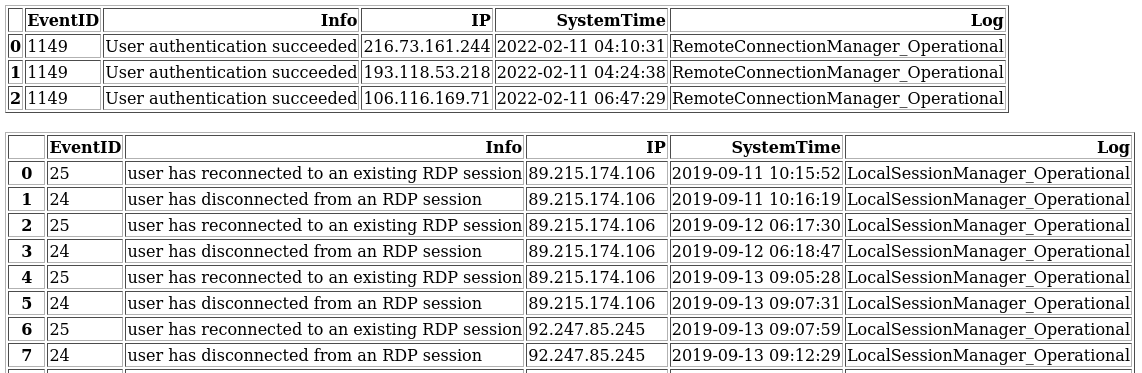
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.

forensicsdigital-forensicslog-analysis
243 years ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsthreat-intelligenceincident-response+1
1602 years ago
py_certificate_extractor preview

py_certificate_extractor

GitHubpassword123456/py_certificate_extractor

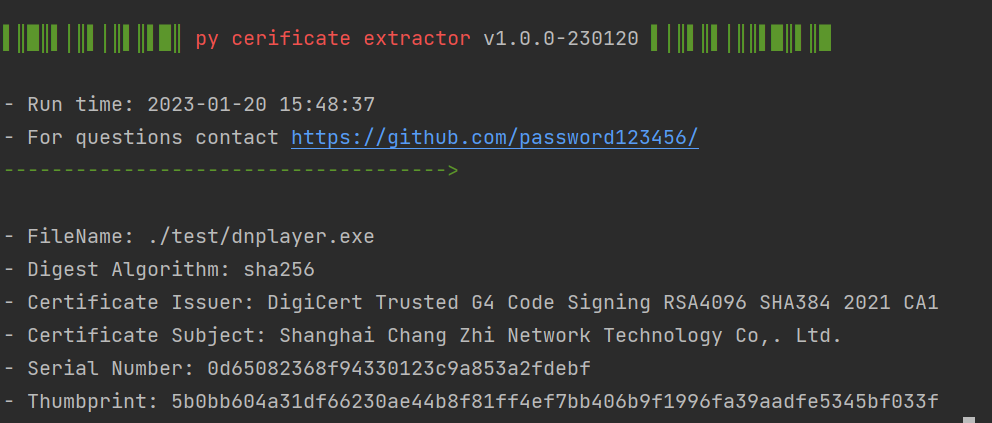
Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
static-analysiscode-analysismalware-analysis+1
3 years ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.

information-gatheringdigital-forensicsincident-response+1
391 year ago
HiddenNetworks-Python preview

HiddenNetworks-Python

GitHubtelefonica/hiddennetworks-python

USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
reconnaissancenetwork-forensicsforensics+2
386 years ago
pockint preview

pockint

GitHubedoardogerosa/pockint

A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
osintreconnaissancevulnerability-analysis+5
2853 years ago
Security-Datasets preview

Security-Datasets

GitHubotrf/security-datasets

Re-play Security Events
digital-forensicsctfthreat-intelligence+4
1.8k3 years ago
ios_triage preview

ios_triage

GitHubrealitynet/ios_triage

Bash script to extract data from a "chekcra1ned" iOS device
ios-securityforensicsmobile-forensics+1
1666 years ago
Simple-Live-Data-Collection preview

Simple-Live-Data-Collection

GitHubletsdefendio/simple-live-data-collection

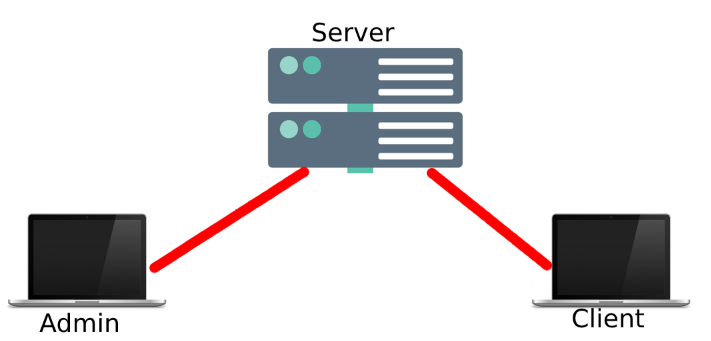
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…

forensicsinformation-gatheringdigital-forensics+1
226 years ago
CyberPipe preview

CyberPipe

GitHubdwmetz/cyberpipe

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
disk-forensicsmemory-forensicsforensics+2
34310 months ago
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts

scripting-automationforensicsdigital-forensics+2
3382 years ago
Previous1…282930…35Next