
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
digital-forensics — Tools — Page 28 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
622 results
RdpCacheStitcher preview

RdpCacheStitcher

GitHubbsi-bund/rdpcachestitcher

RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
forensicsdata-recoverydigital-forensics+1
331
5 years ago
bmc-tools preview

bmc-tools

GitHubanssi-fr/bmc-tools

RDP Bitmap Cache parser

memory-forensicsforensicsinformation-gathering+1
6955 months ago
mailMeta preview

mailMeta

GitHubgr33nm0nk2802/mailmeta

An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
osintphishing-toolsforensics+2
1755 years ago
DFIR_Resources_REvil_Kaseya preview

DFIR_Resources_REvil_Kaseya

GitHubcado-security/dfir_resources_revil_kaseya

Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack
ioc-managementforensicsmalware-analysis+3
1825 years ago
xwf-yara-scanner preview

xwf-yara-scanner

GitHubcrowdstrike/xwf-yara-scanner

Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
static-analysisforensicsmalware-analysis+1
931 year ago
MEAT preview

MEAT

GitHubjfarley248/meat

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices

ios-securityforensicsmobile-forensics+2
1686 years ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsioc-managementpacket-sniffing-analysis+5
935 years ago
BeaconEye preview

BeaconEye

GitHubccob/beaconeye

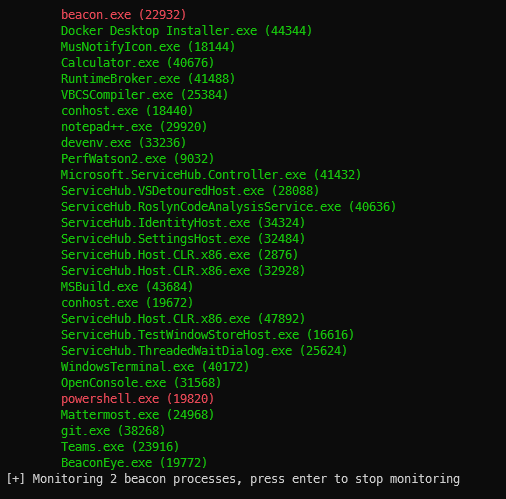
Hunts out CobaltStrike beacons and logs operator command output
memory-forensicsmalware-analysisdigital-forensics+2
9642 years ago
AzureHunter preview

AzureHunter

GitHubdarkquasar/azurehunter

A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365

information-gatheringdigital-forensicscloud-security+3
7953 years ago
misp-wireshark preview

misp-wireshark

GitHubmisp/misp-wireshark

Lua plugin to extract data from Wireshark and convert it into MISP format
packet-sniffing-analysisnetwork-forensicsforensics+2
503 years ago
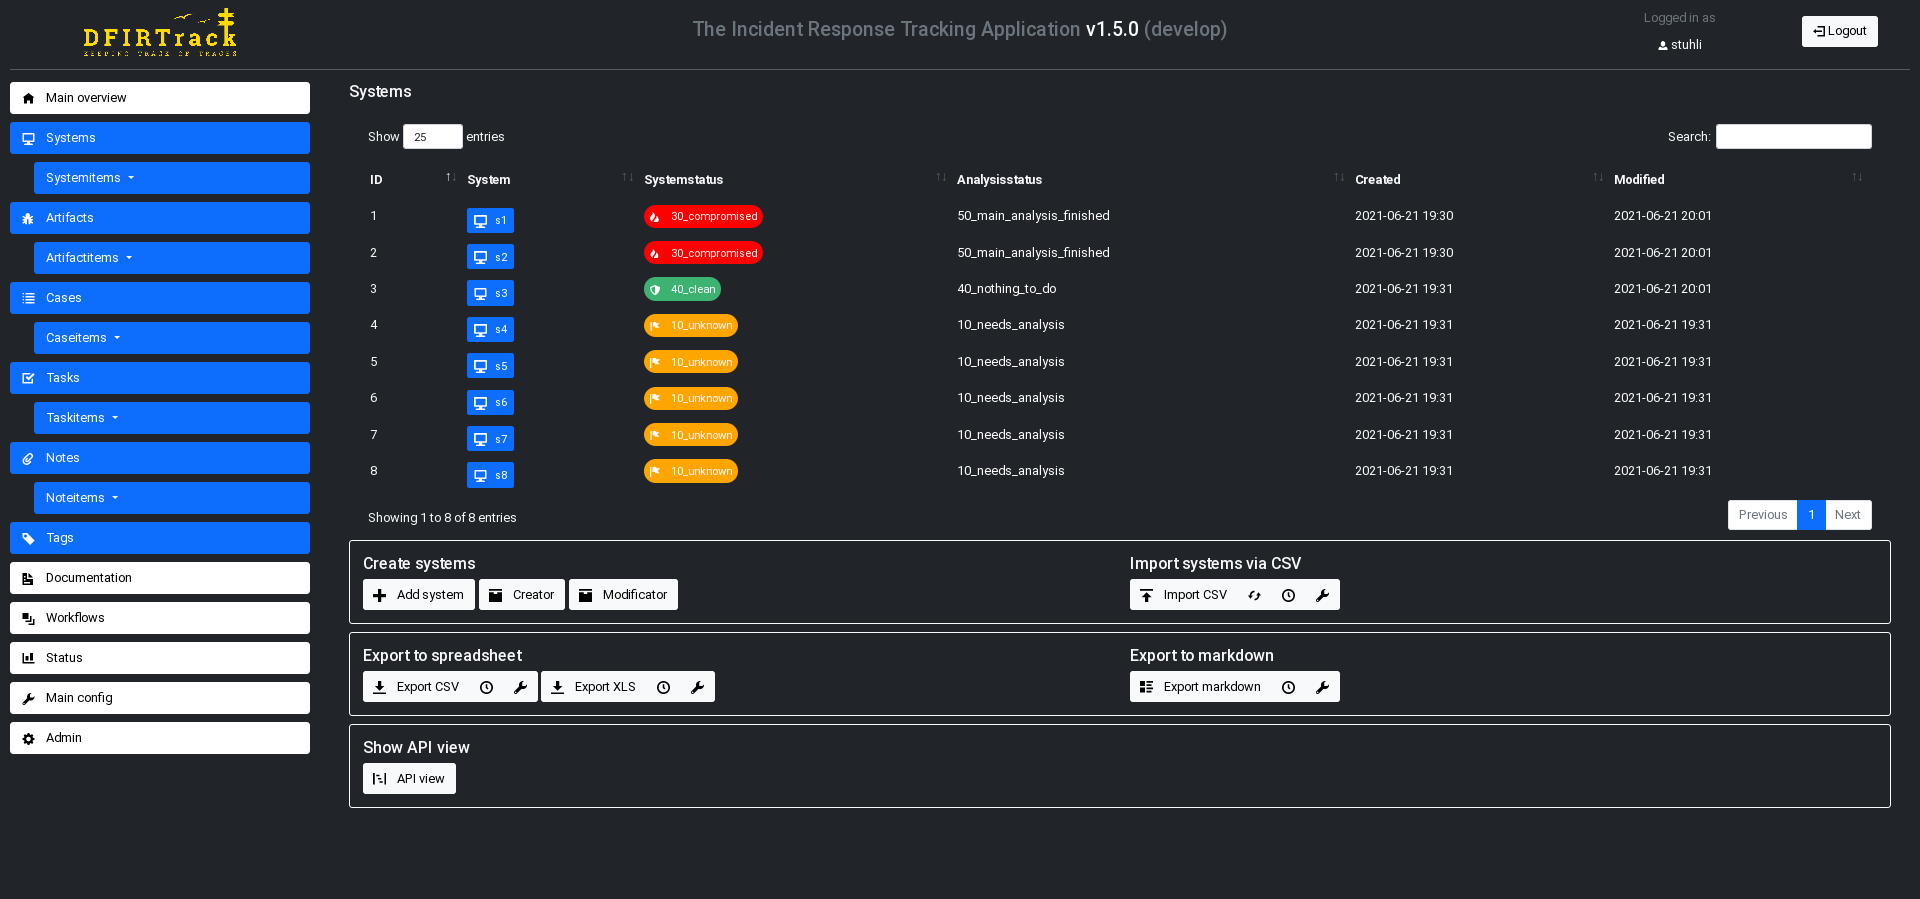
dfirtrack preview

dfirtrack

GitHubdfirtrack/dfirtrack

System-based incident response tracking application for managing large-scale DFIR cases, with import/export, task workflows, and artifact tracking…
forensicsdigital-forensicsincident-response
5389 months ago
RsWindowsThingies preview

RsWindowsThingies

GitHubforensicmatt/rswindowsthingies

Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…
digital-forensicsincident-responselog-analysis
236 years ago
Telegrip preview

Telegrip

GitHubtelegrip/telegrip

GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…

forensicsmobile-forensicsdata-recovery+1
194 years ago
ntfstool preview

ntfstool

GitHubthewhiteninja/ntfstool

Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
disk-forensicsencryption-decryption-toolsvulnerability-analysis+3
6203 months ago
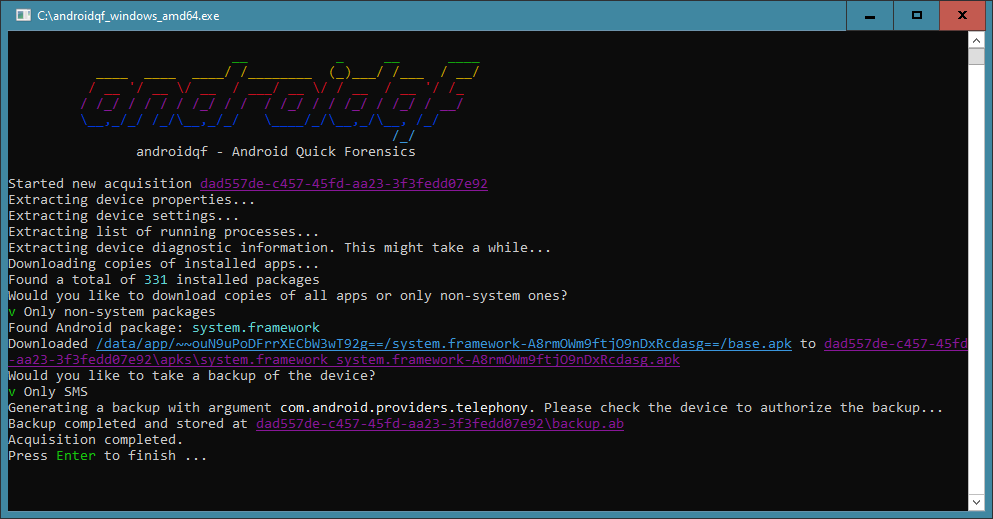
androidqf preview

androidqf

GitHubbotherder/androidqf

Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
android-securityforensicsmobile-forensics+2
3028 months ago
whatsapp-media-decrypt preview

whatsapp-media-decrypt

GitHubddz/whatsapp-media-decrypt

Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…
encryption-decryption-toolsforensicsmobile-forensics+1
1k6 years ago
hstsparser preview

hstsparser

GitHubthebeanogamer/hstsparser

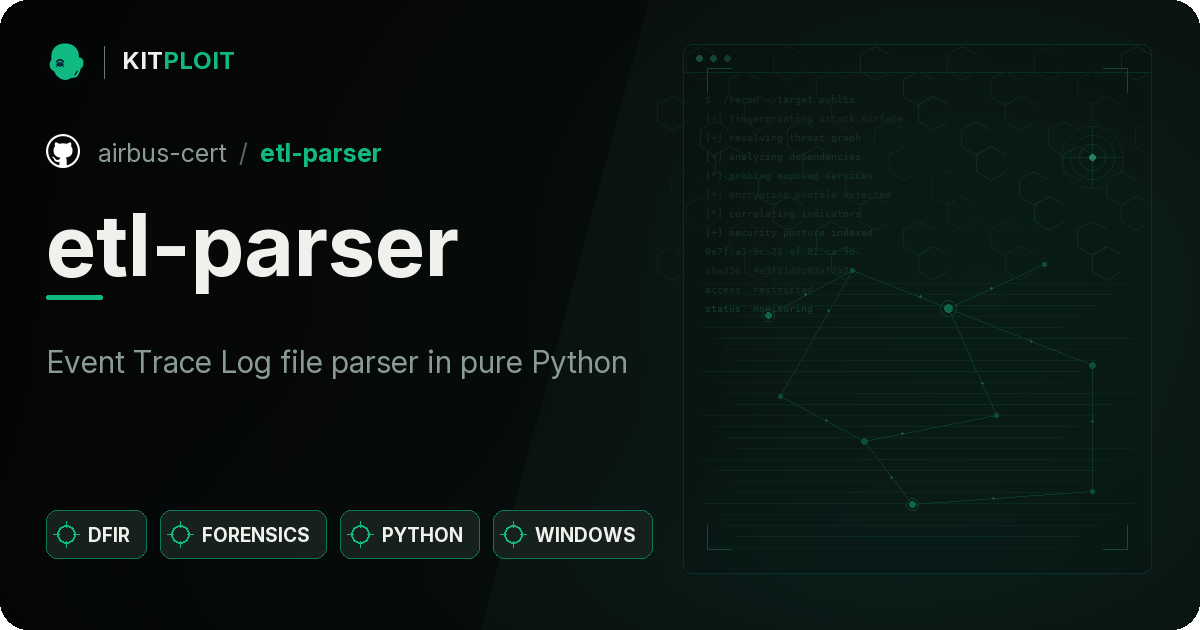
A tool to parse Firefox and Chrome HSTS databases into forensic artifacts!
forensicsdigital-forensics
261 year ago
etl-parser preview

etl-parser

GitHubairbus-cert/etl-parser

Event Trace Log file parser in pure Python

reverse-engineeringforensicsdigital-forensics+1
1565 months ago
Previous1…272829…35Next