

timesketch
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
disk-forensicsioc-managementmemory-forensics+7
3.4k
google/timesketchCollaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
 gnu-mirror-unofficial/ddrescue
Copies data from damaged or failing storage devices, handles read errors, and performs efficient rescue operations to recover as much data as…
 rockwellshah/filekey
Offline, open-source web app for passkey-based file encryption and sharing. AES-256-GCM/HPKE, no cloud, no accounts; encrypt to recipients with…
 keerthivasan-sankar/secure-vault-for-commercial
secure vault for your files
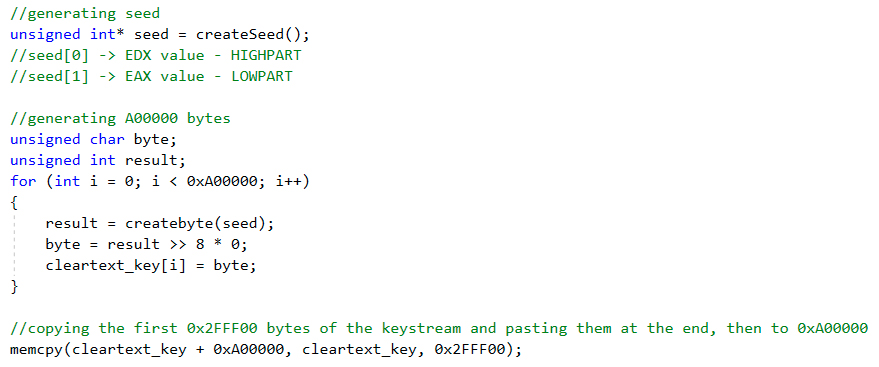 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 jschicht/logfileparser
Parser for $LogFile on NTFS
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 3gstudent/ntfsdump
Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.
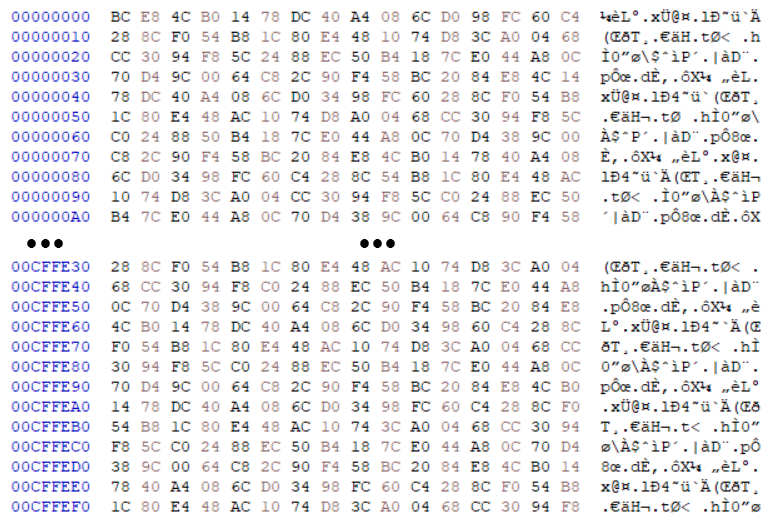 reecdeep/hivev5_file_decryptor
Hive v5 file decryption algorithm
 jas502n/010-editor-template
Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
 nccgroup/untrue
Tool for checking passwords against TrueCrypt encrypted volumes and disks, and/or decrypting the data.
 nccgroup/zipdefrag
Presented at Recon Montreal 2018