

CanoP
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
defensive-toolsstatic-analysisvulnerability-scanners+7
5
openbreach/canopStatic analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 lgranadoi/sift-hardened
Security-hardened fork of sift 17.1.3 for CVE-2026-85625. Not affiliated with crcn/sift.js.
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
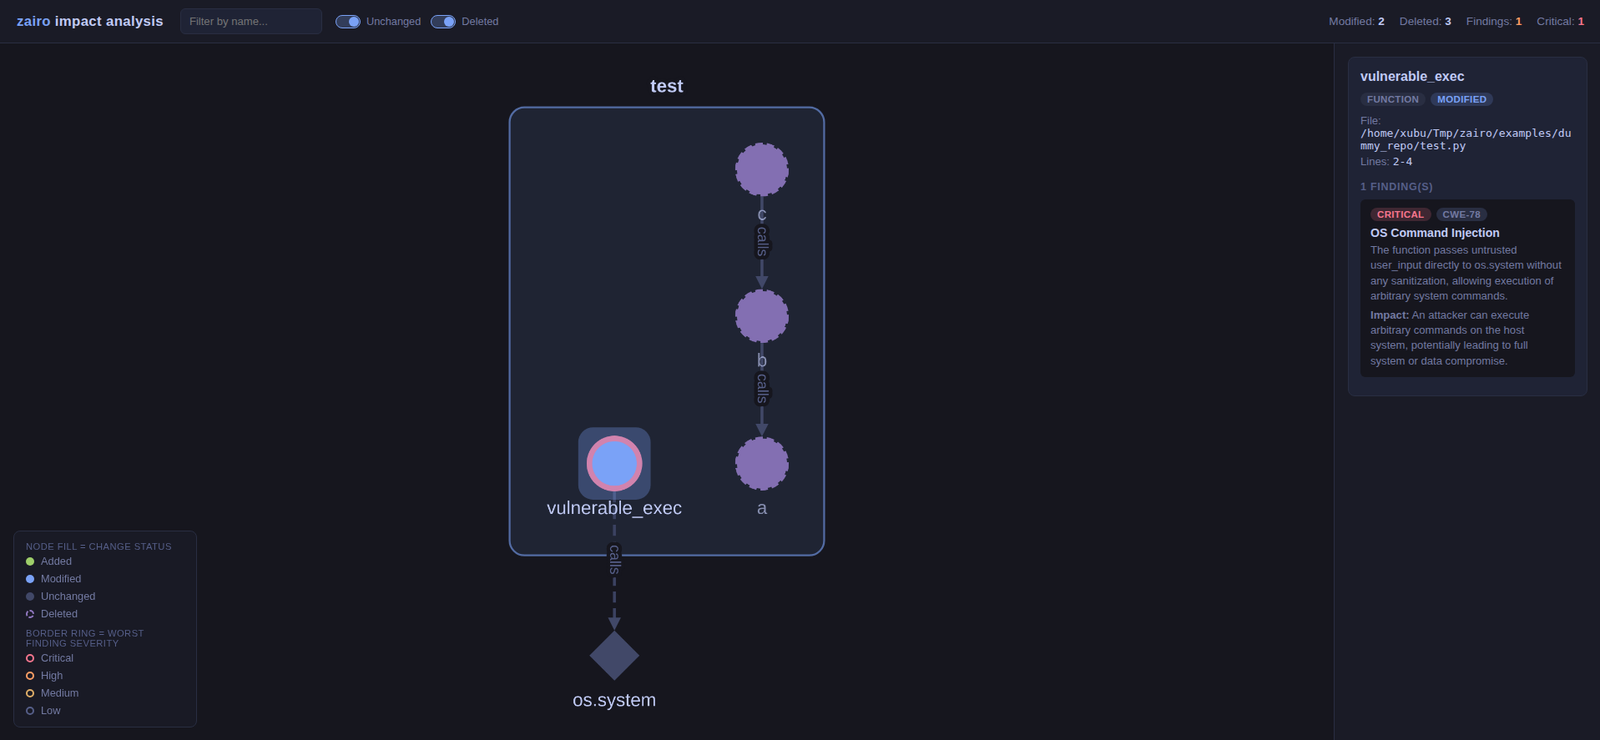 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 dannydoodlesstory/evm-audit-helpers
Collection of Solidity snippets and Foundry scripts for smart contract security audits
 nanda-rani/safe
A contextual security auditing system for research artifacts
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…