
ImpulsiveDLLHijack
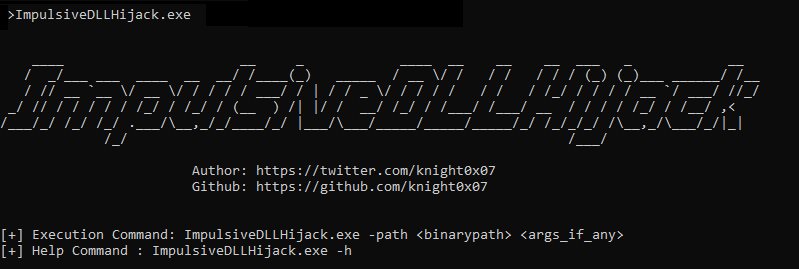
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

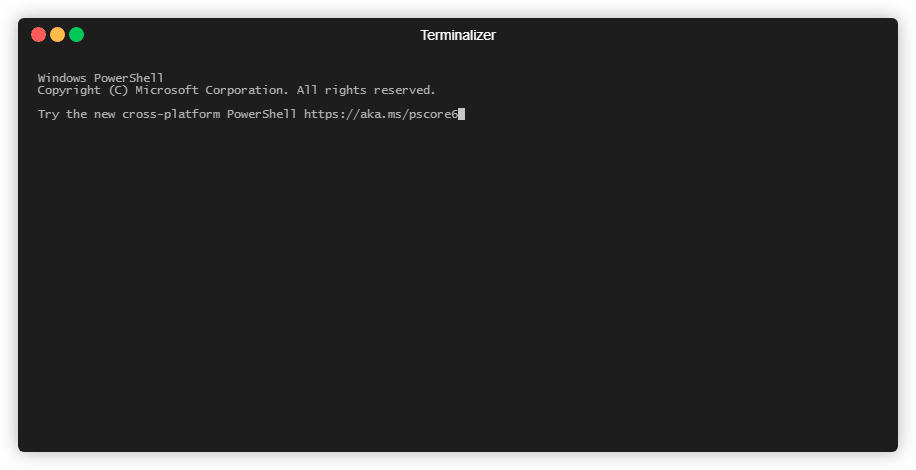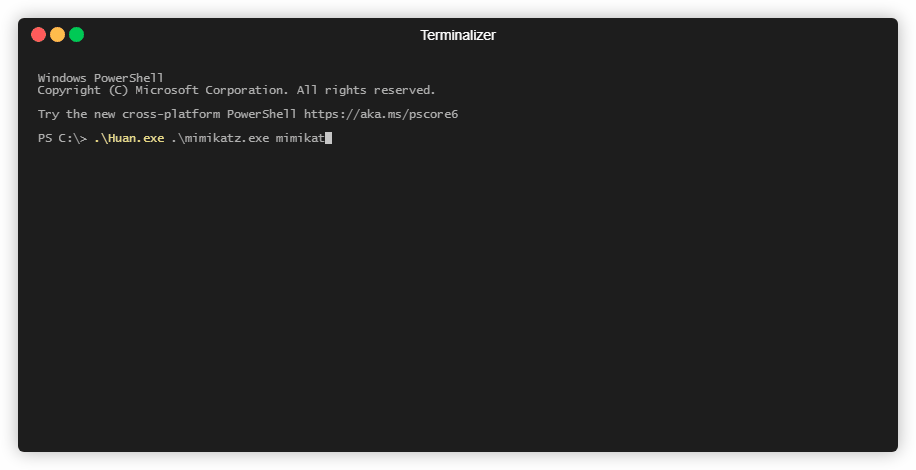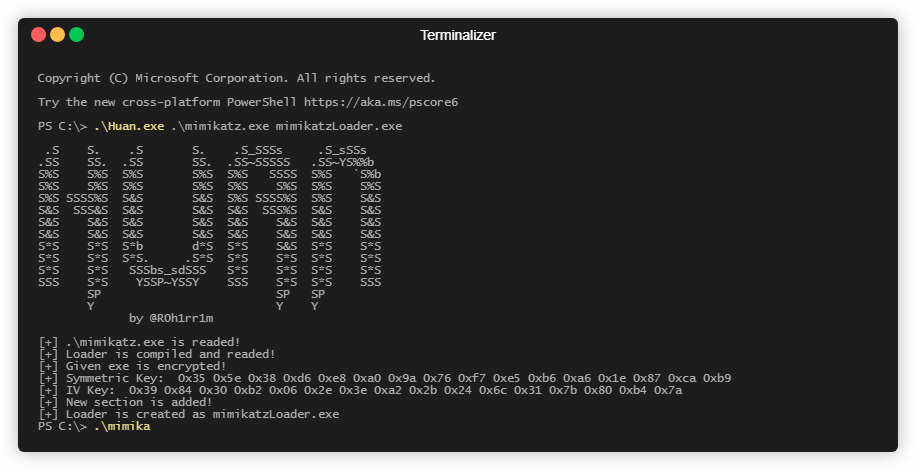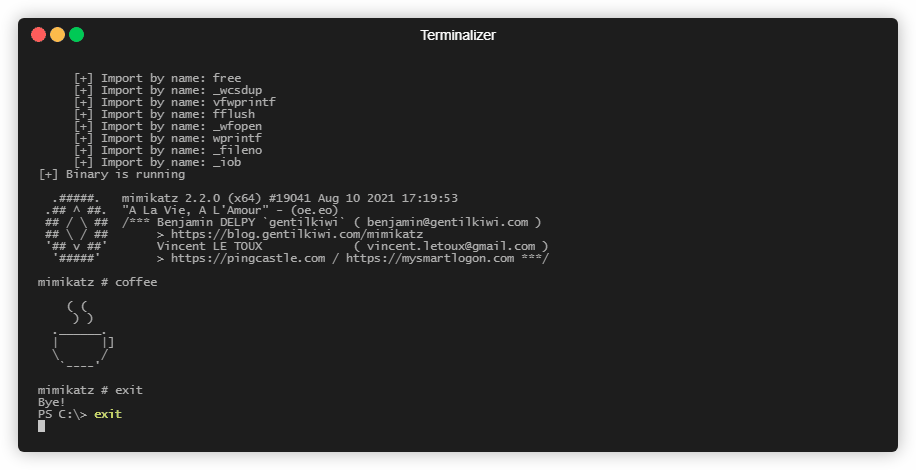
Encrypted PE Loader Generator

A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.

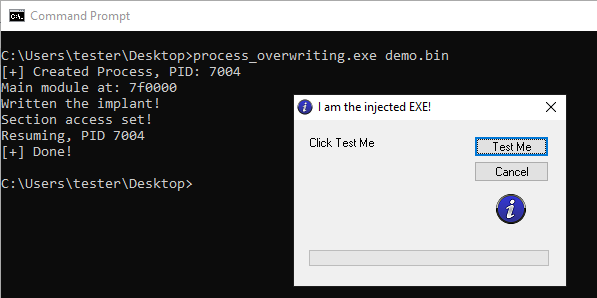
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.

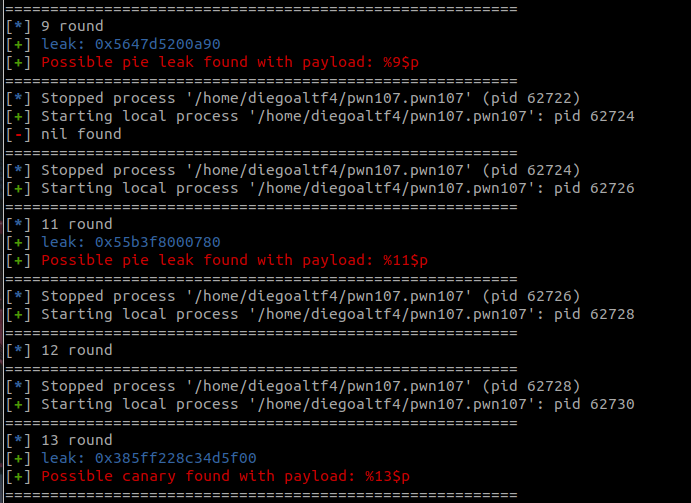
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…

A Nim implementation of reflective PE-Loading from memory

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…

MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash

Search for Unix binaries that can be exploited to bypass system security restrictions.

Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…

Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process

A modern 32/64-bit position independent implant template

A simple PoC to invoke an encrypted shellcode by using an hidden call

My experiments in weaponizing Nim (https://nim-lang.org/)

LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…

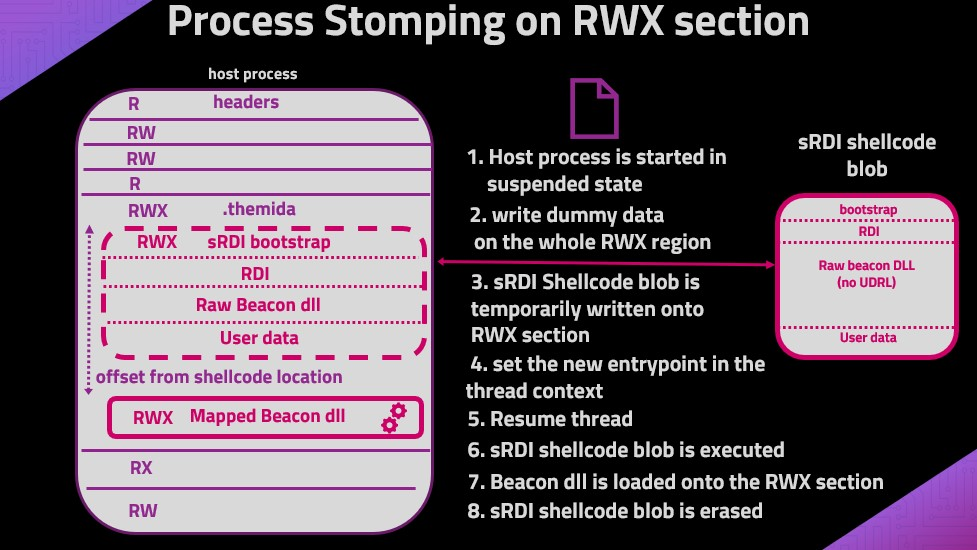
A variation of ProcessOverwriting to execute shellcode on an executable's section

ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…