
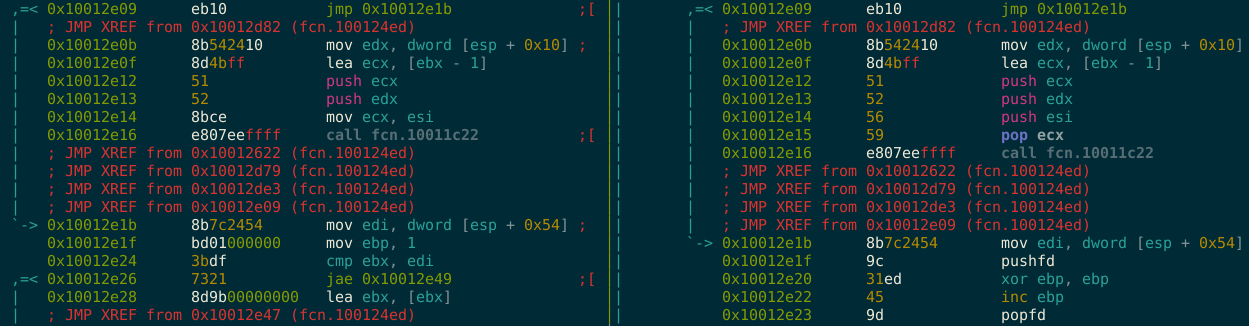
metame
 a0rtega/metame
metame is a metamorphic code engine for arbitrary executables
payload-generationreverse-engineeringmalware-analysis+2
a0rtega/metamemetame is a metamorphic code engine for arbitrary executables
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 lunixbochs/patchkit
binary patching from Python
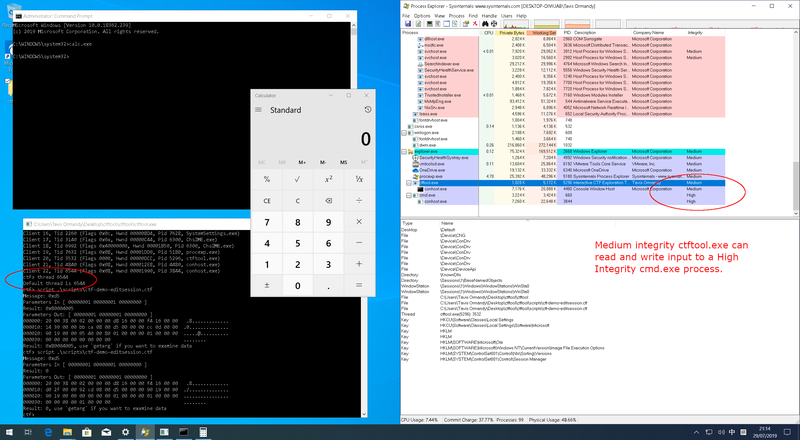
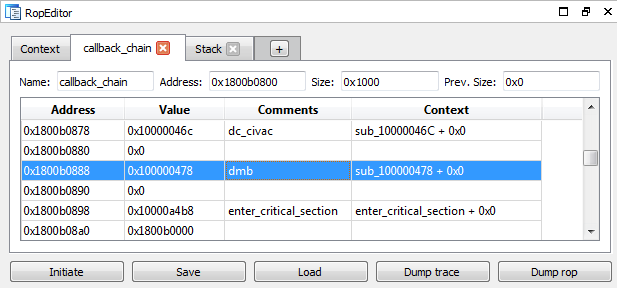 dsecurity/crauemu
crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks
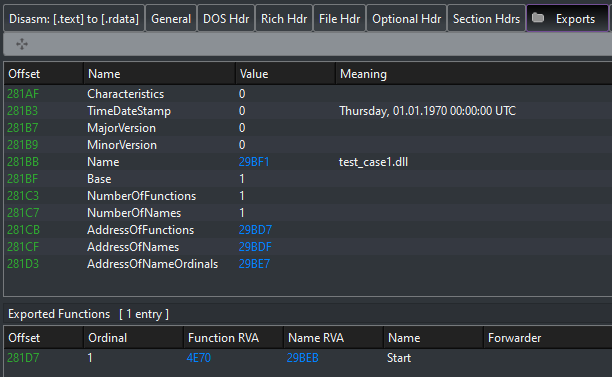 hasherezade/exe_to_dll
Converts a EXE into DLL
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 zznop/sploit
Go package that aids in binary analysis and exploitation
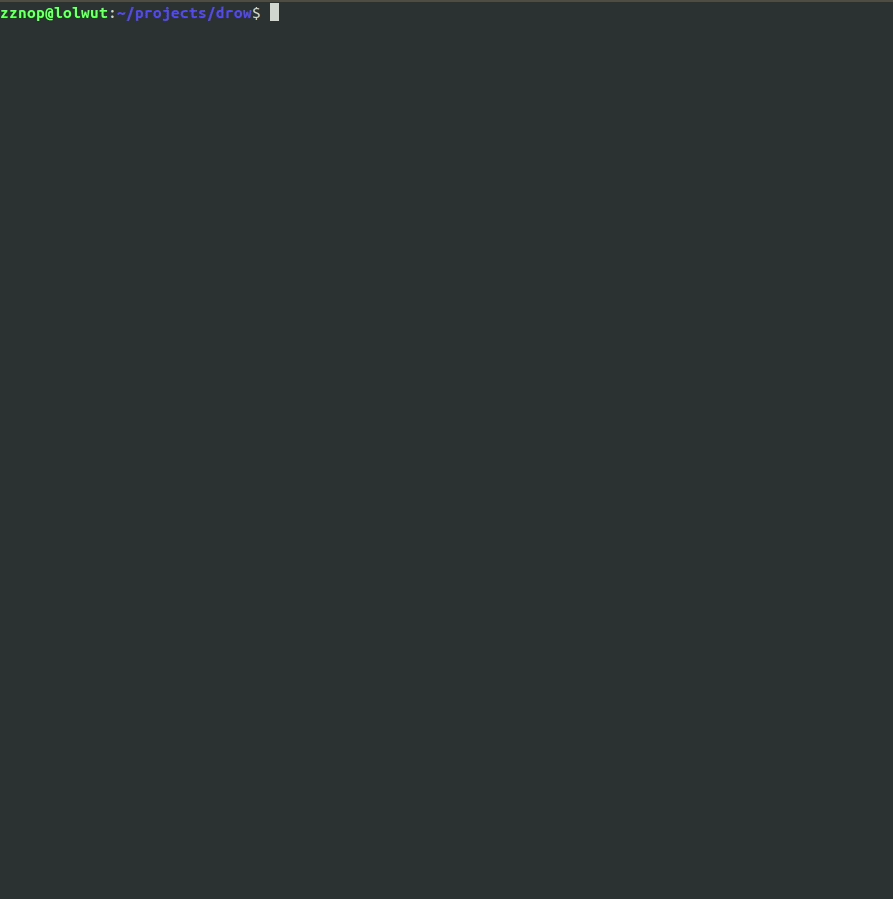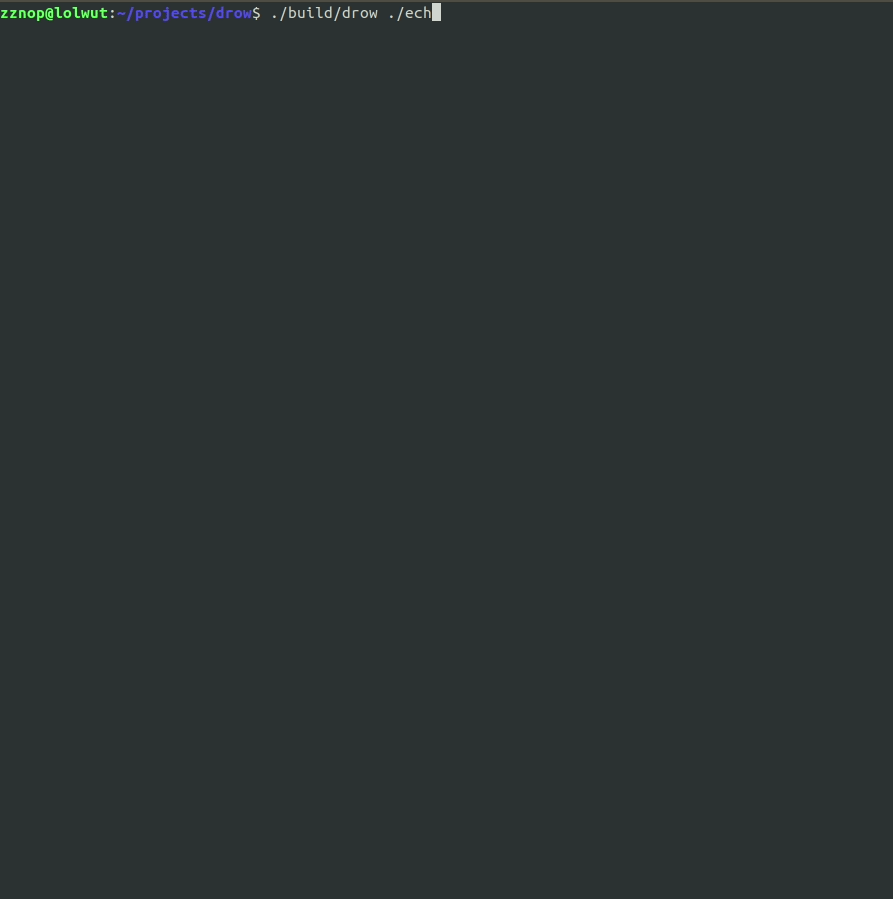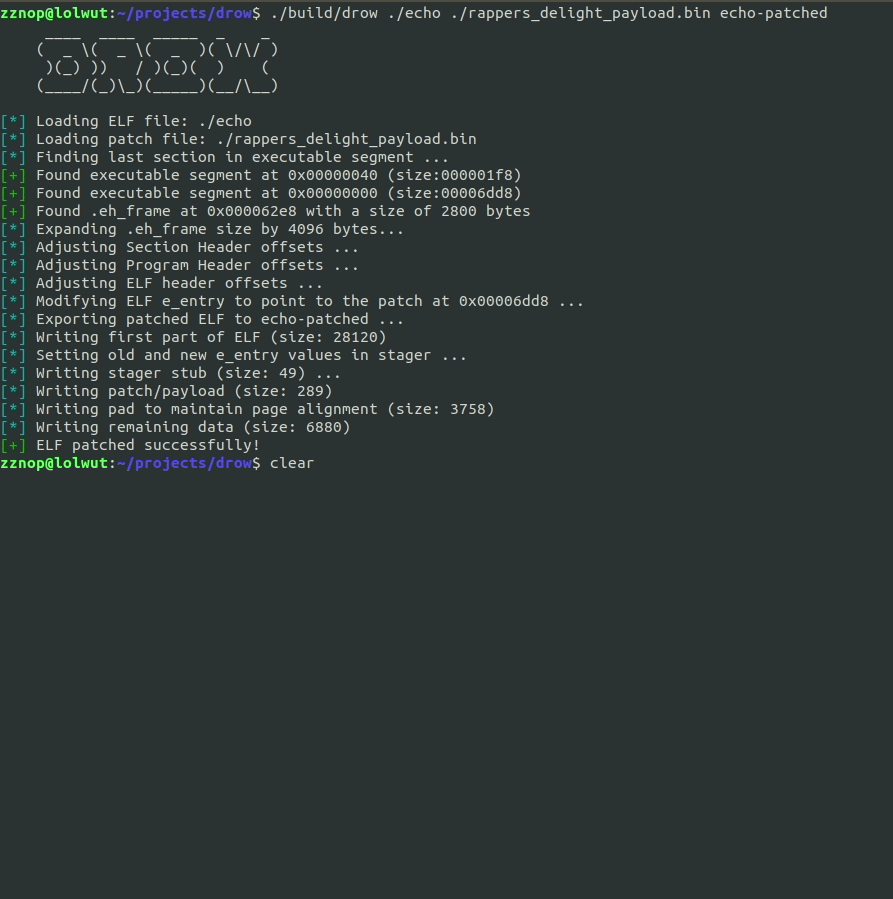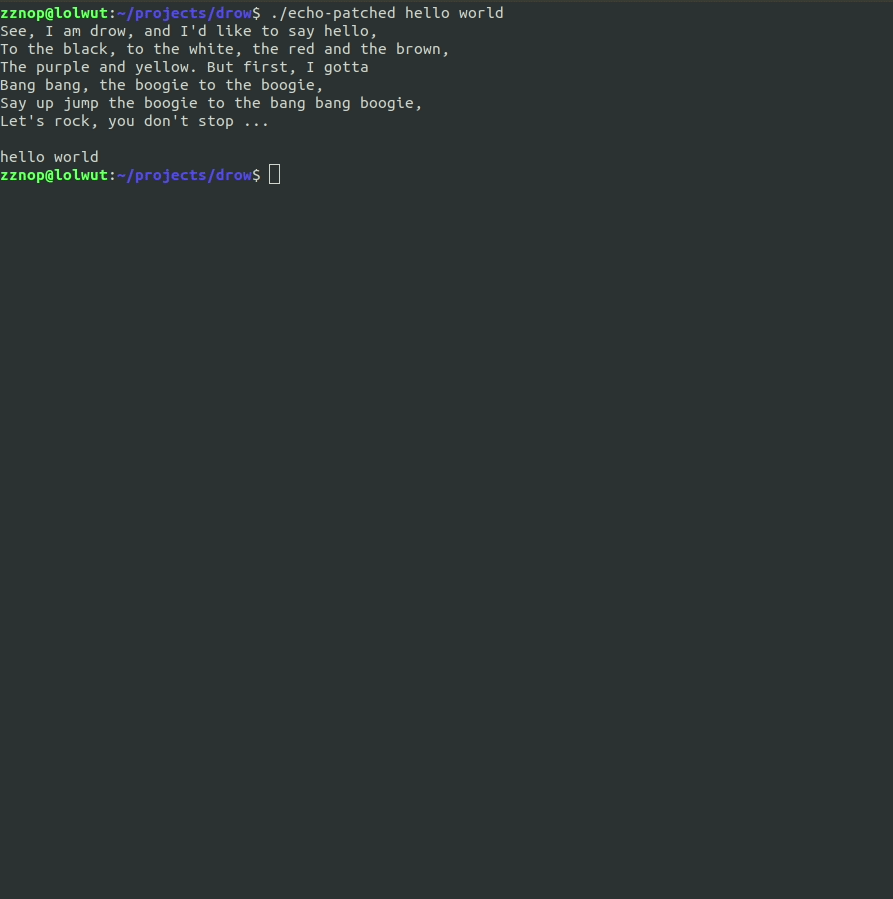 zznop/drow
Injects code into ELF executables post-build
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 gjduck/e9patch
A powerful static binary rewriting tool
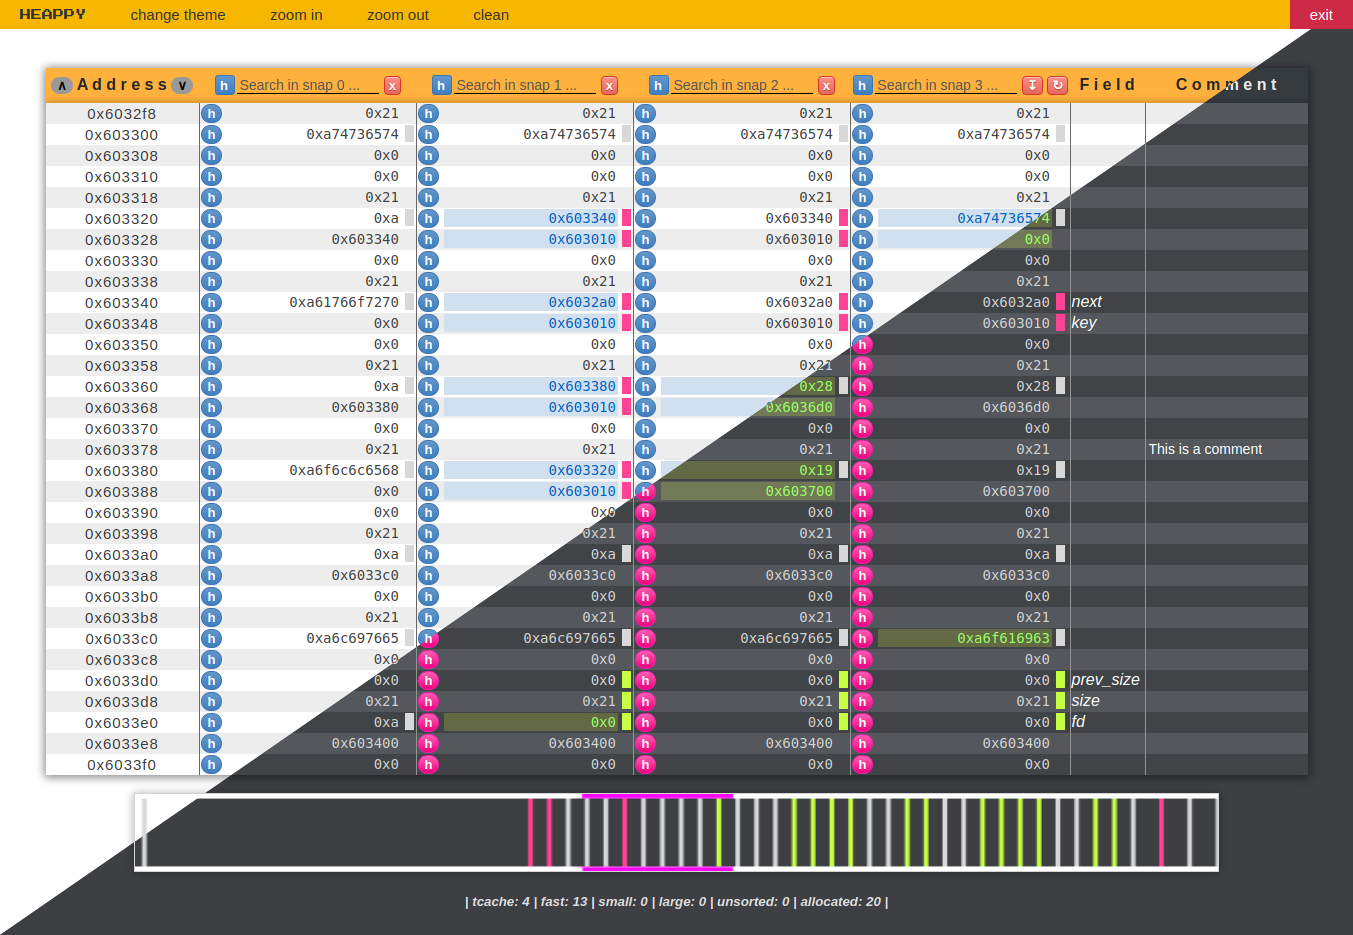 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 ashemery/exploitation-course
Offensive Software Exploitation Course
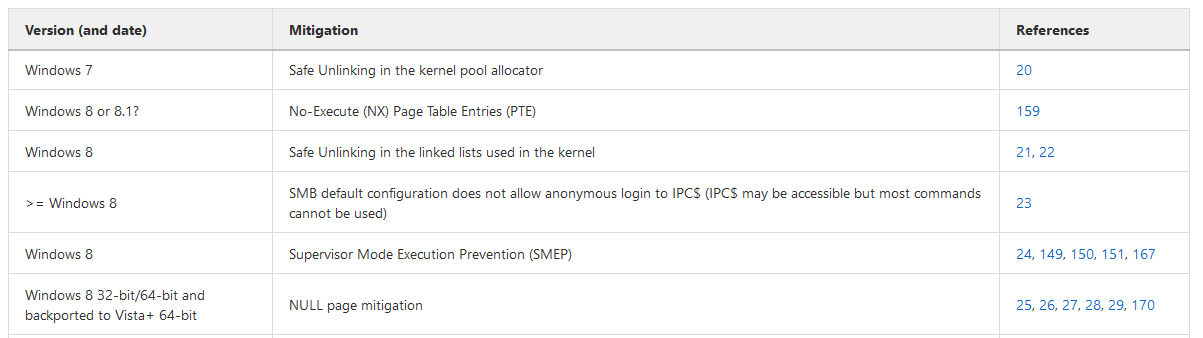 nccgroup/exploit_mitigations
Knowledge base of exploit mitigations available across numerous operating systems, architectures and applications and versions.
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
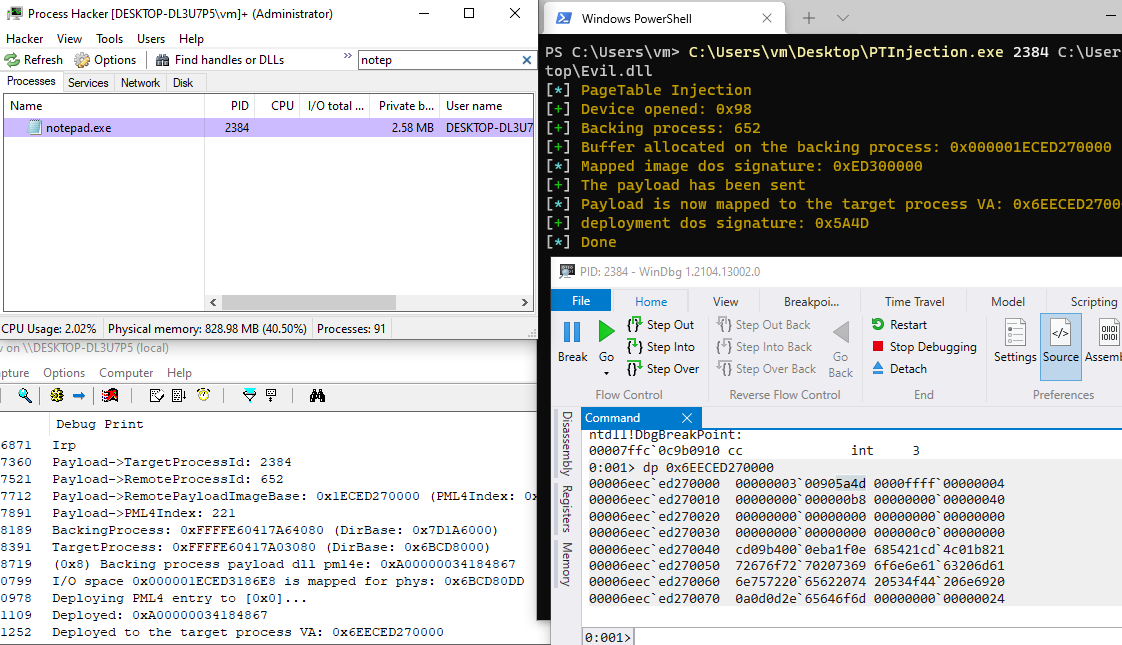 kkent030315/pagetableinjection
Code Injection, Inject malicious payload via pagetables pml4.