
ntlmscout
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
reconnaissancenetwork-mappingpassword-attacks+8
56
boydhacks/ntlmscoutUnauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
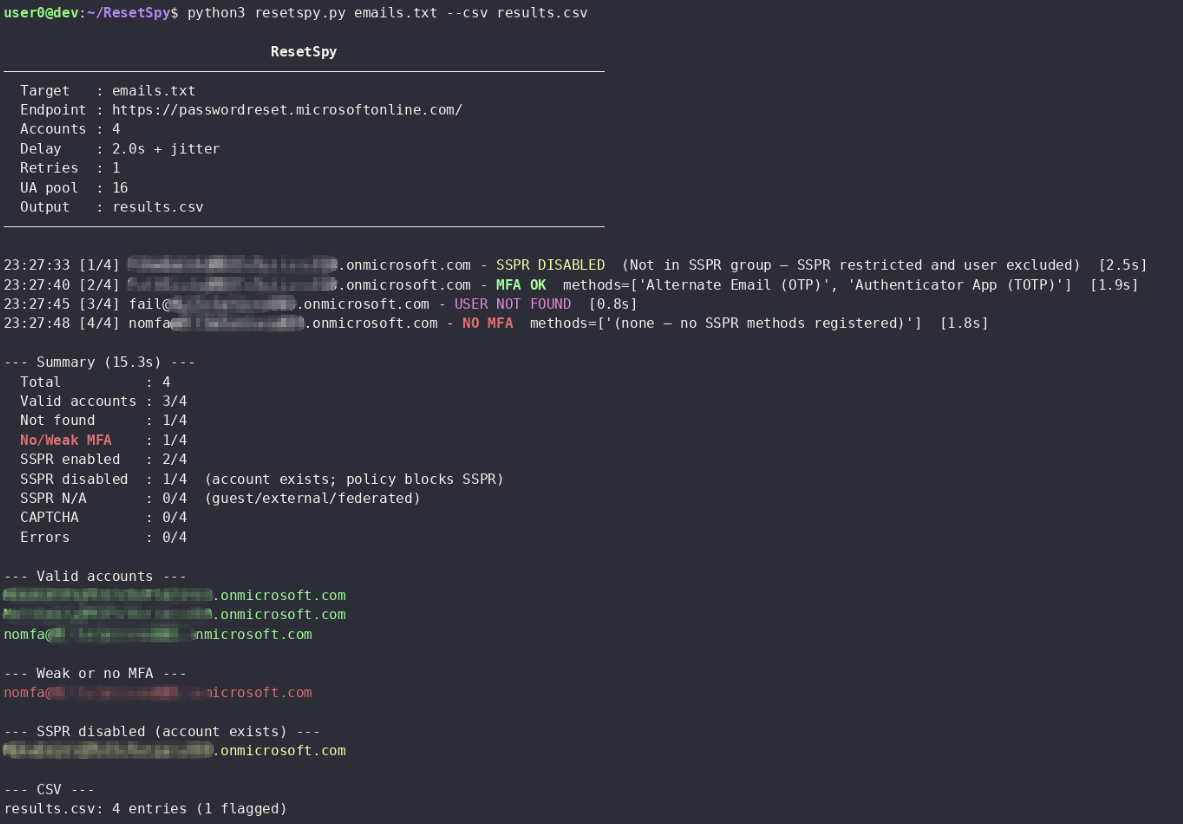 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
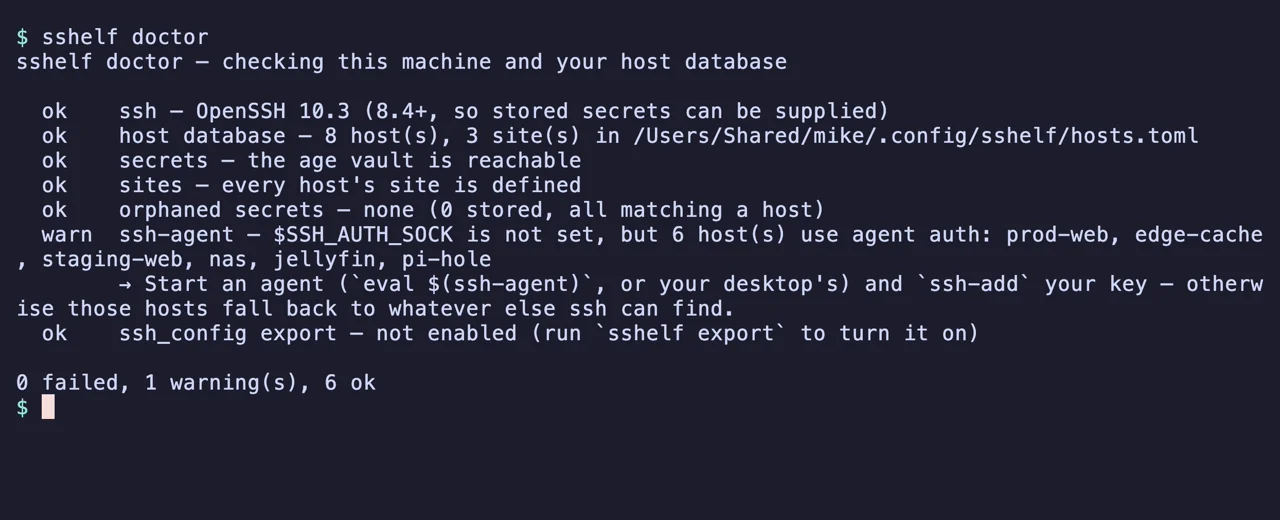 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 dev-sec/chef-os-hardening
This chef cookbook provides numerous security-related configurations, providing all-round base protection.
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 gmh5225/csrfbrute
专为红队行动设计的CSRF登录暴力破解工具,具备动态CSRF Token刷新、多线程并发和会话恢复功能,支持高并发操作和智能重试机制。
 dev-sec/chef-ssh-hardening
This chef cookbook provides secure ssh-client and ssh-server configurations.
 dev-sec/puppet-ssh-hardening
This puppet module provides secure ssh-client and ssh-server configurations.
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 oriolrius/kafka-keycloak-oauth
Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
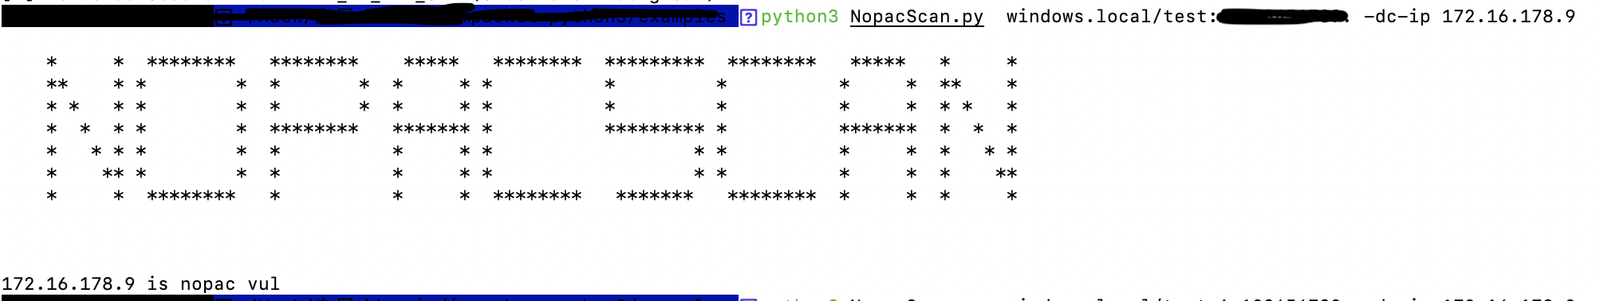 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
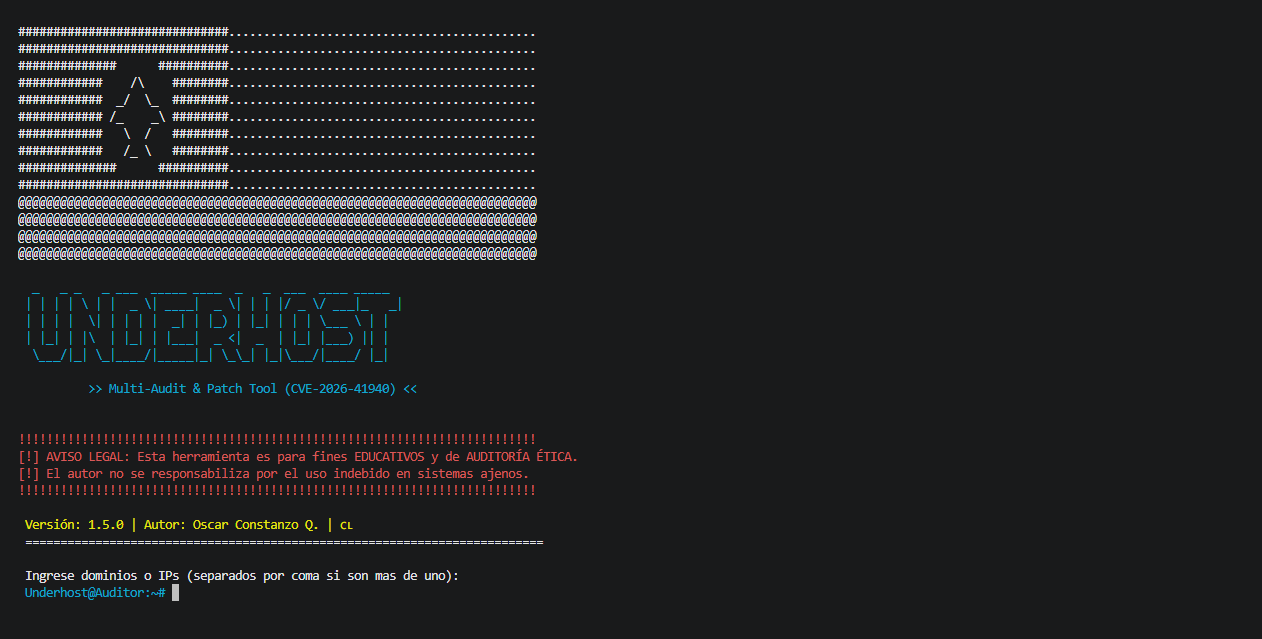 underh0st/cpanel-audit-remediation-tool
Audit and incident response tool for CVE-2026-41940 vulnerability
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database