

DevSecOpsGuideline
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
vulnerability-scannerscontainer-securitystatic-code-analysis+6
1.1k
owasp/devsecopsguidelineThe OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 openbmc/bmcweb
A do everything Redfish, KVM, GUI, and DBus webserver for OpenBMC
 opnsense/core
OPNsense GUI, API and systems backend
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 owasp/agent-skills-security-standard
Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
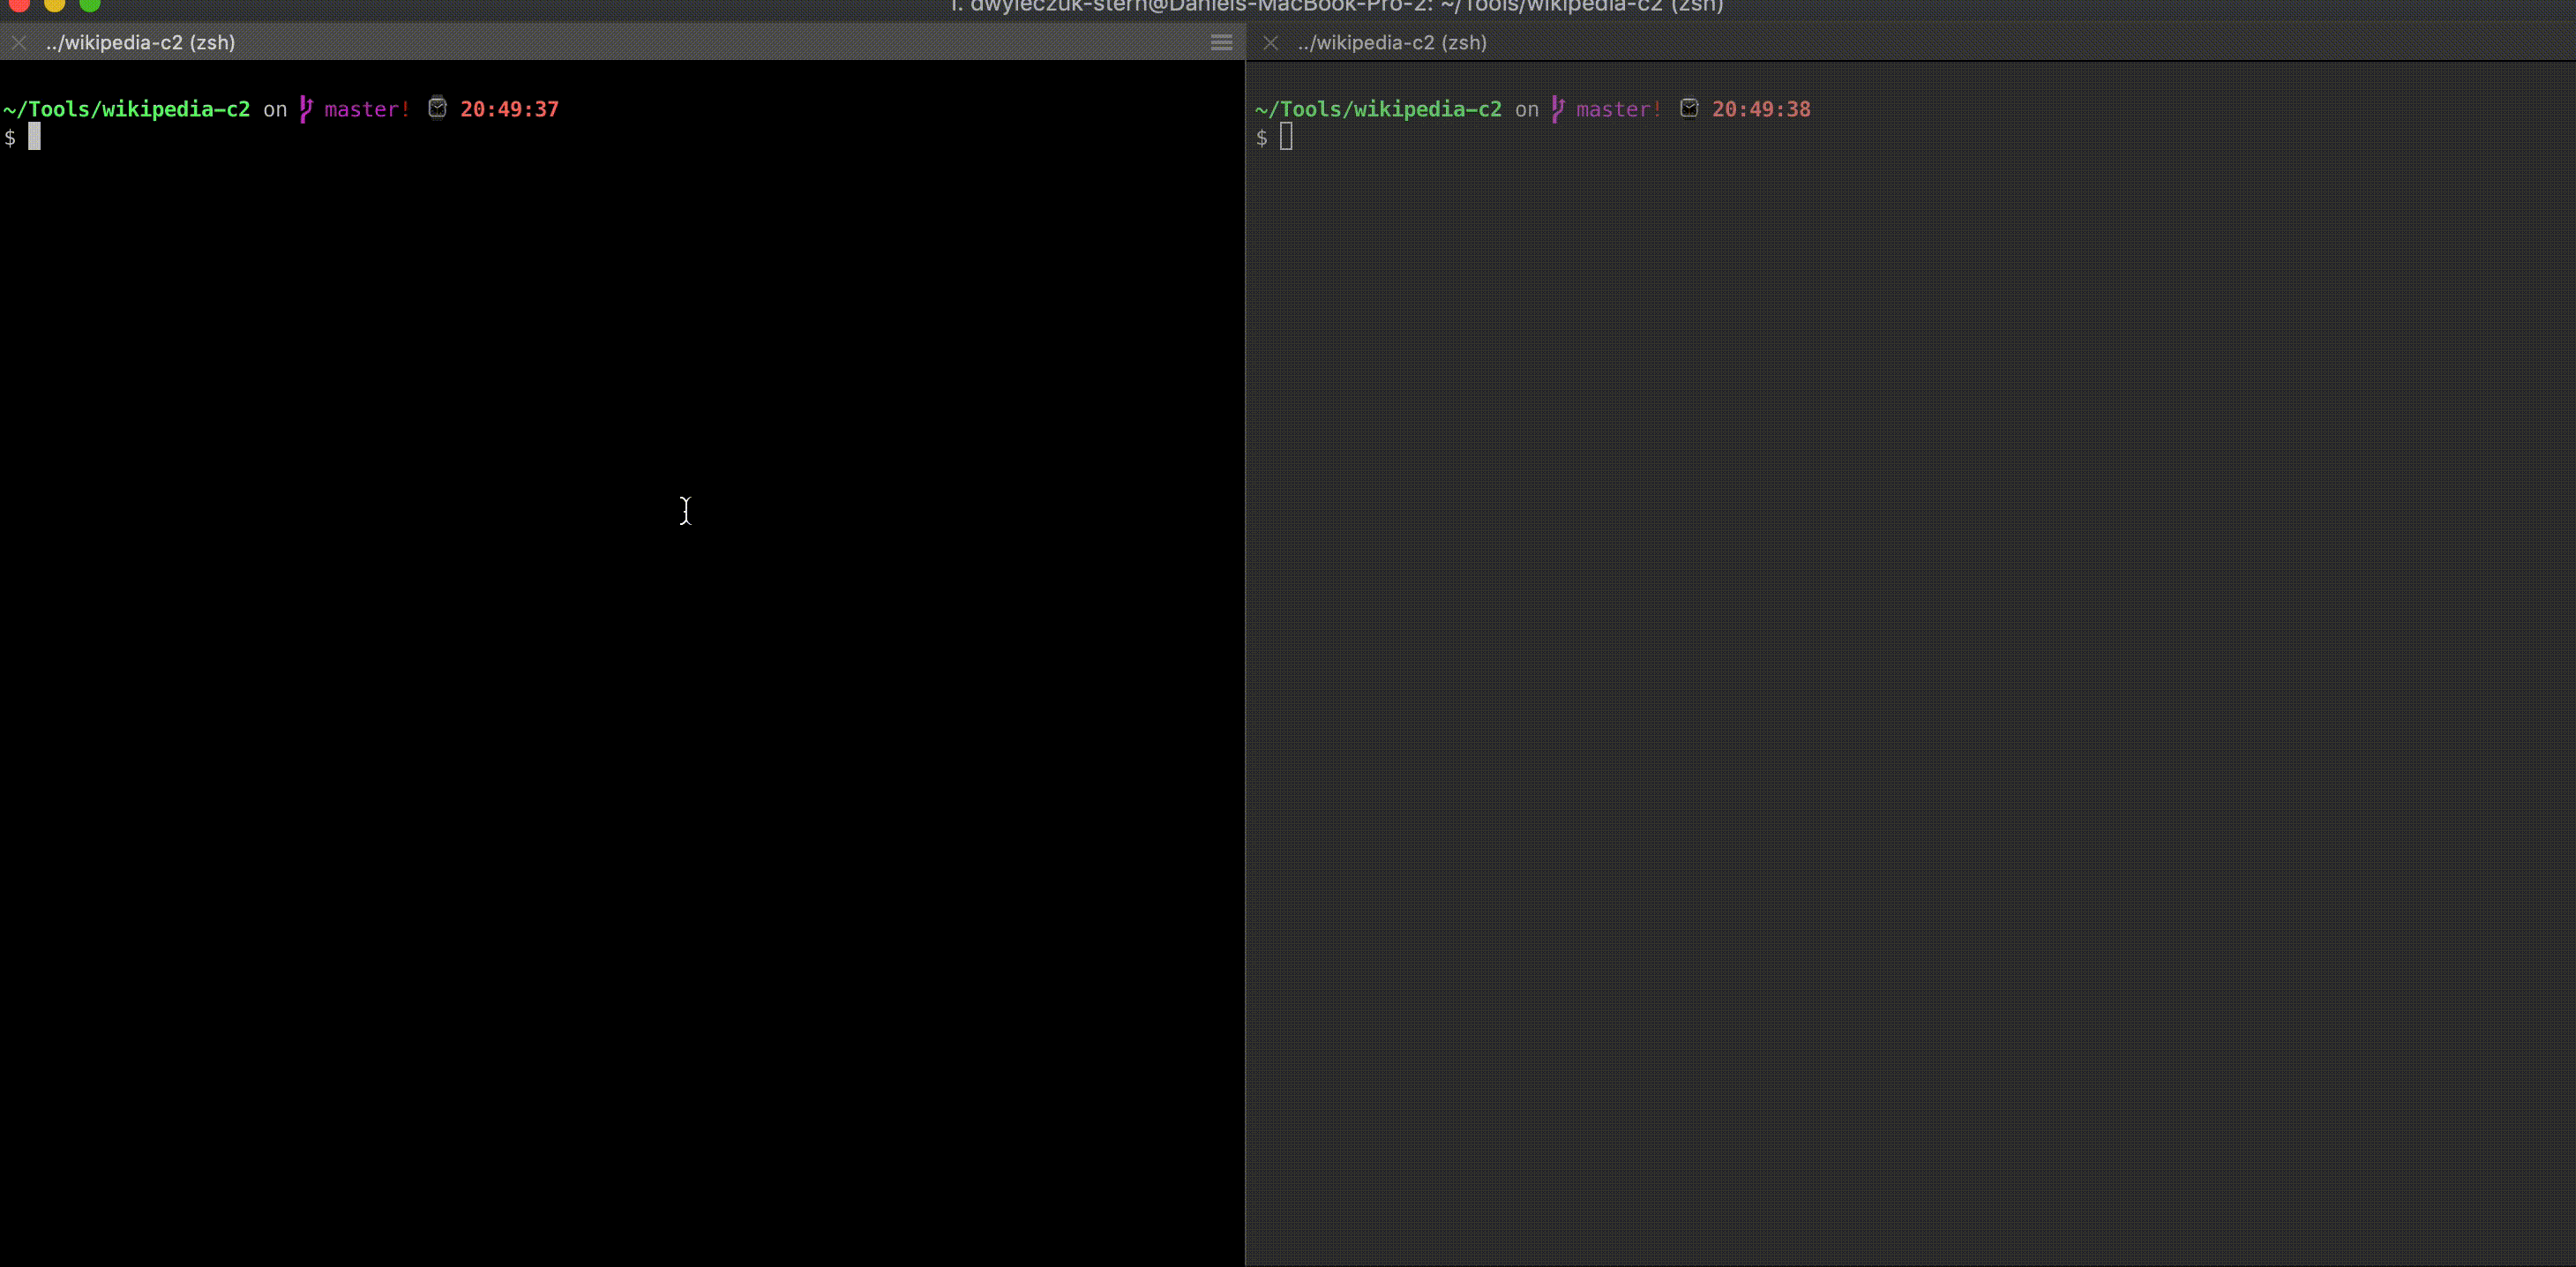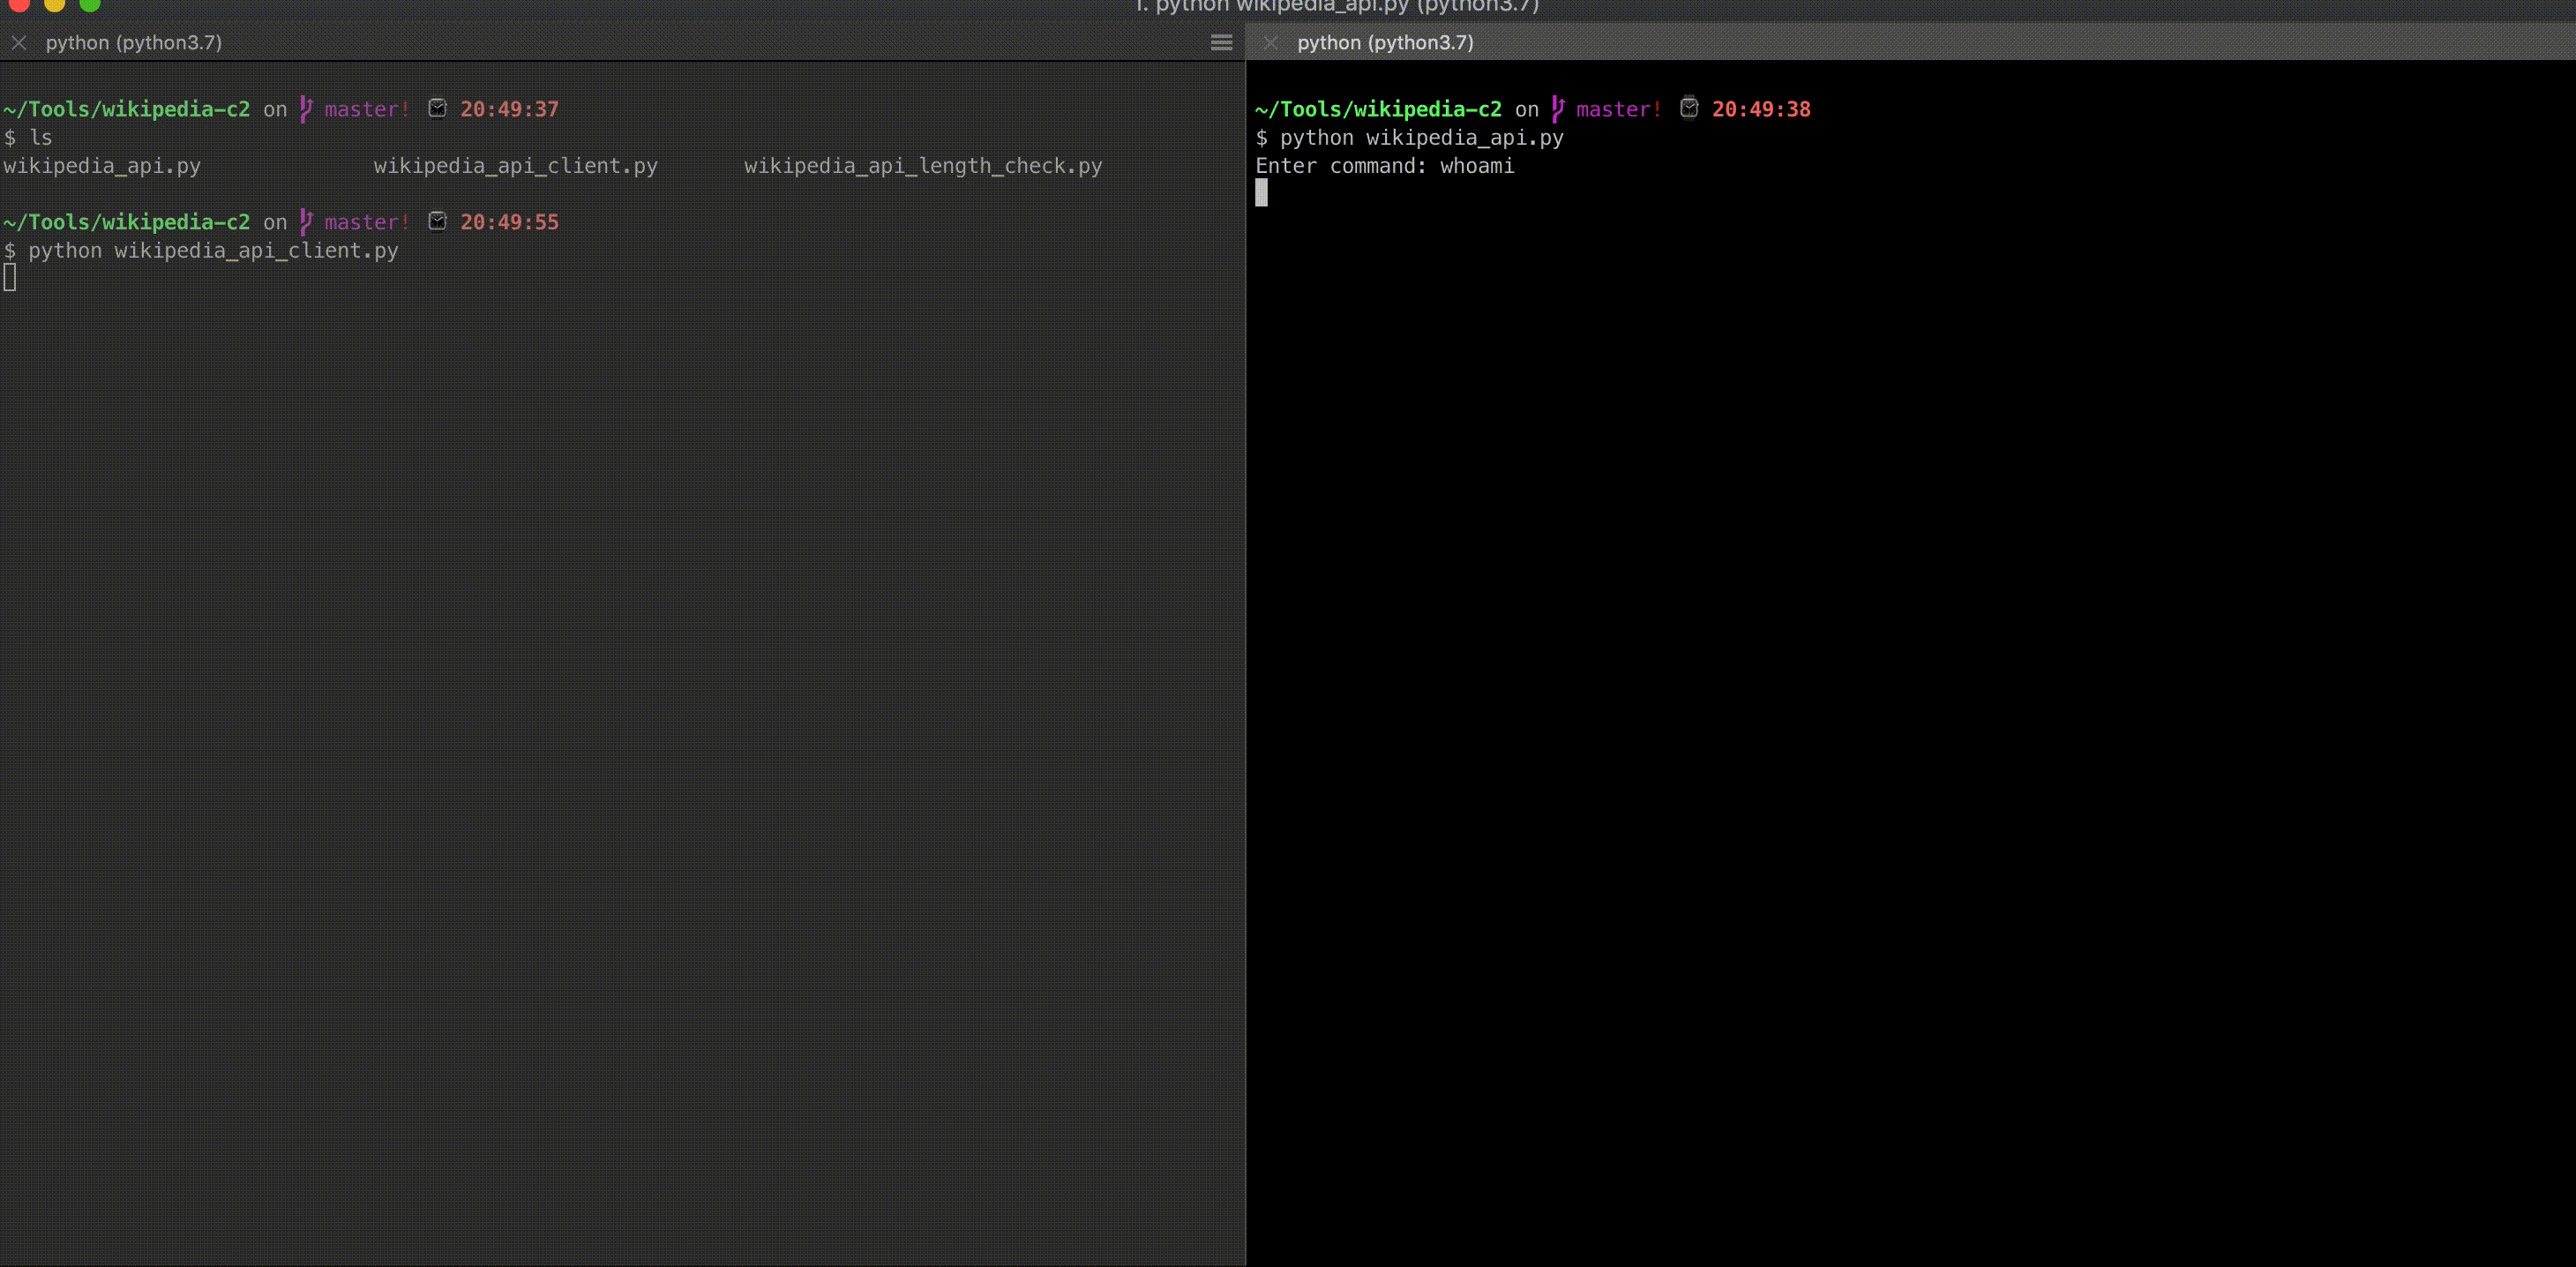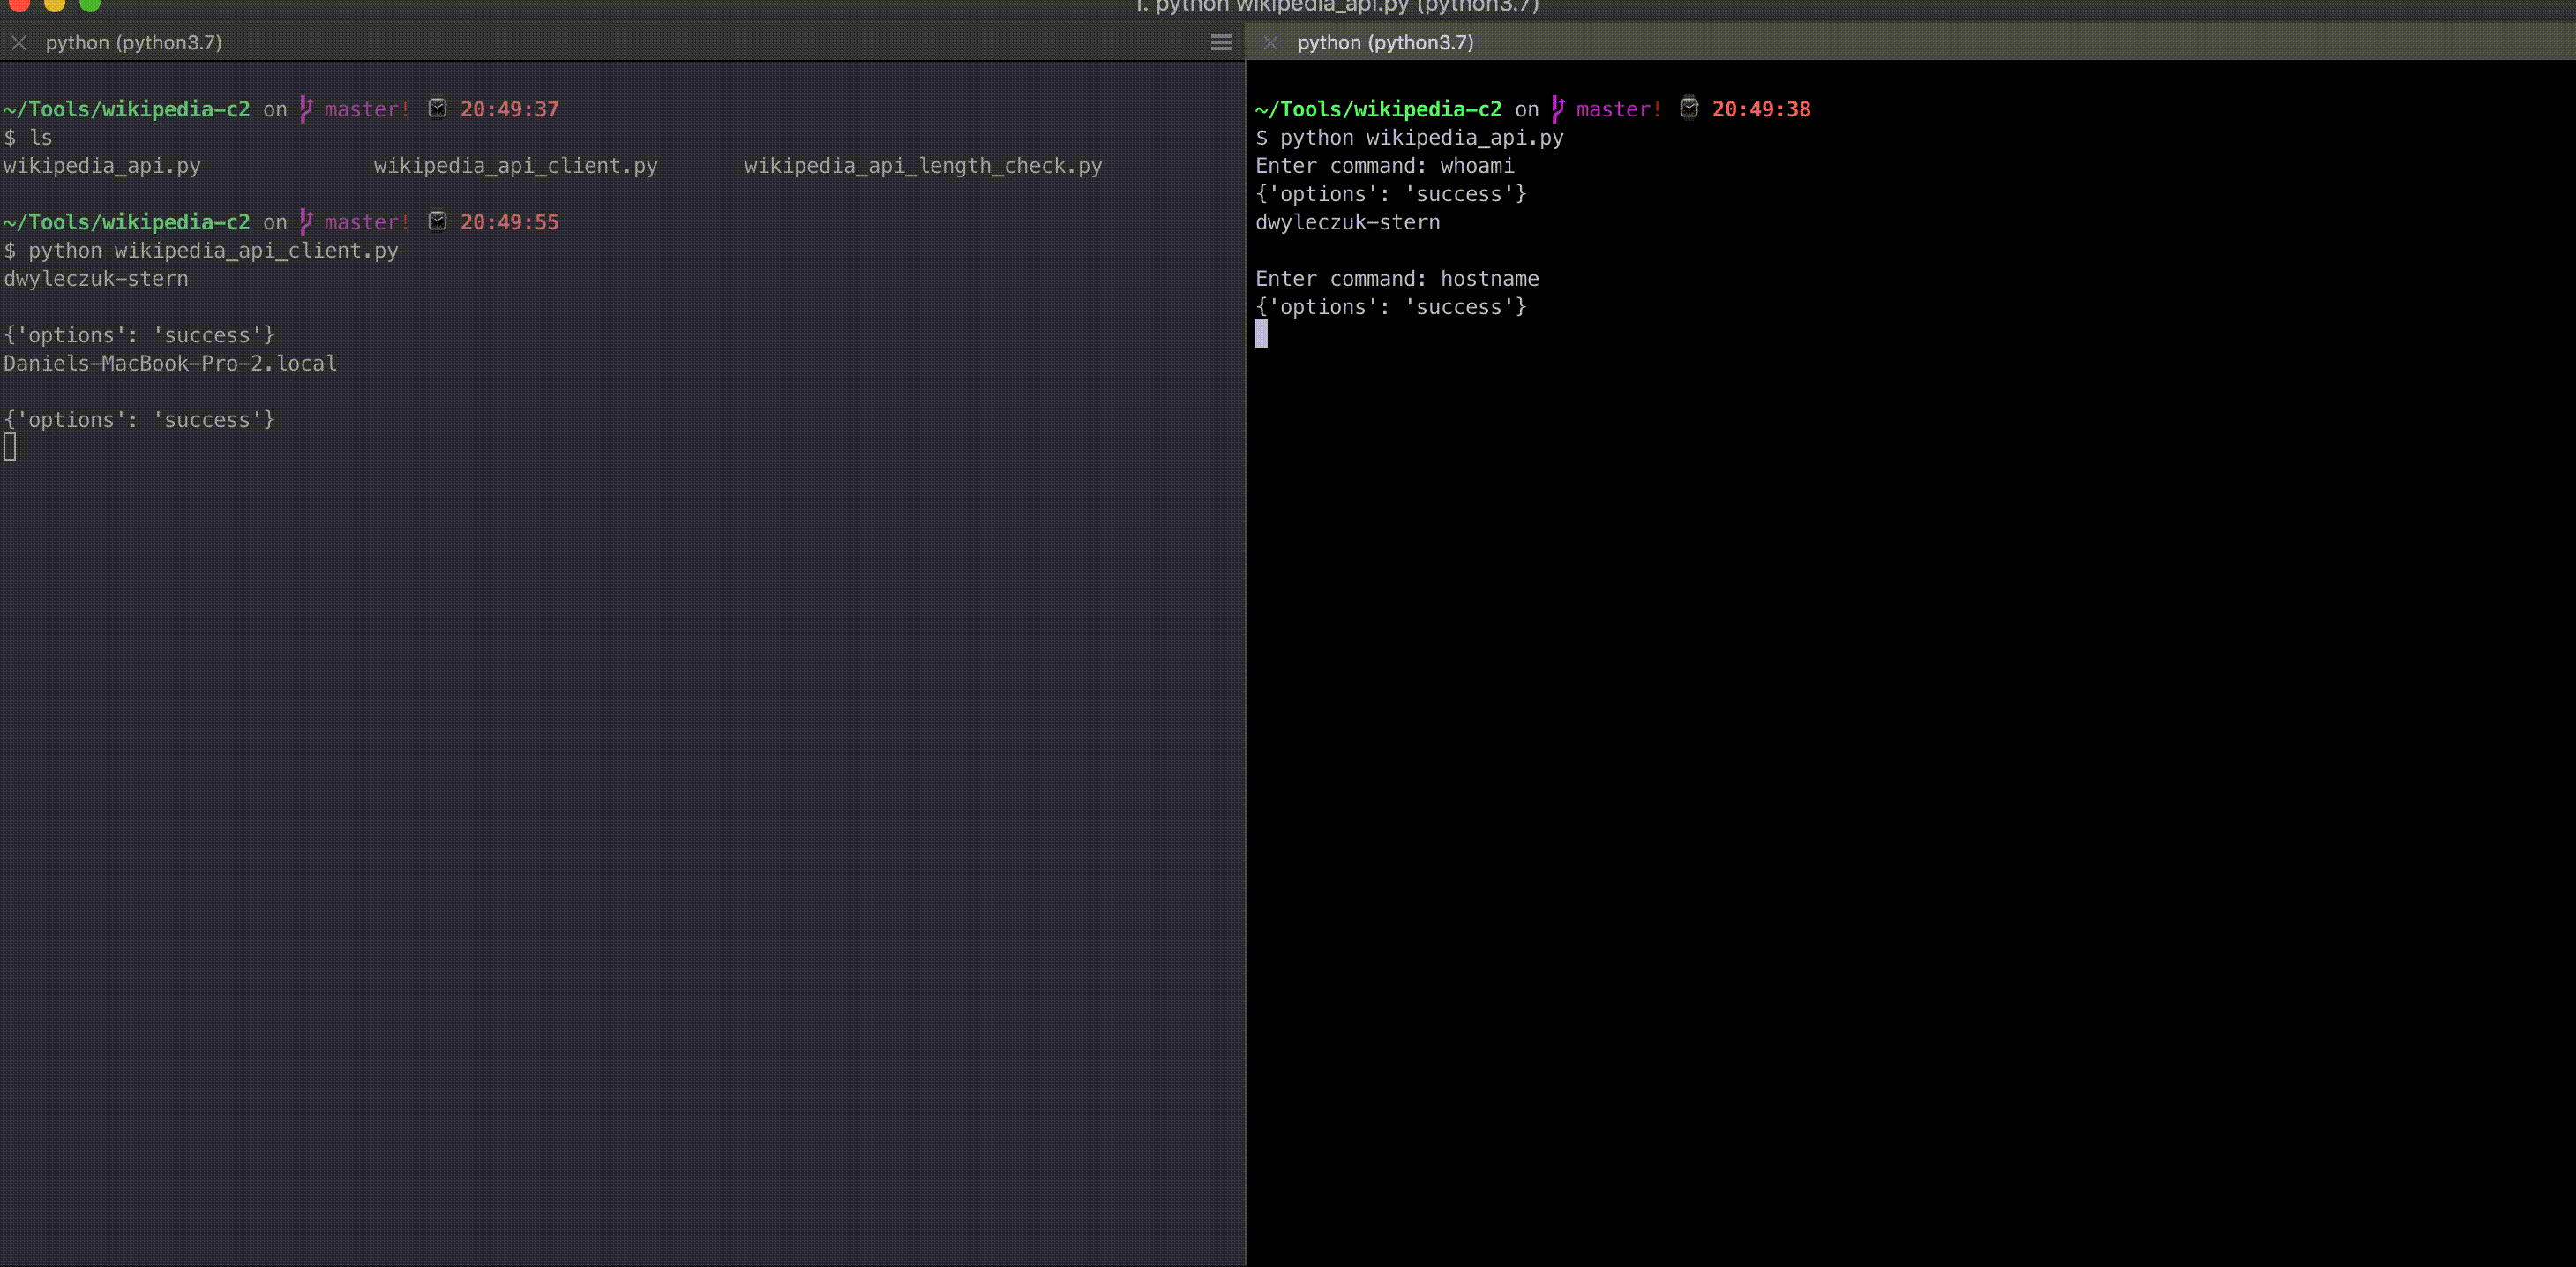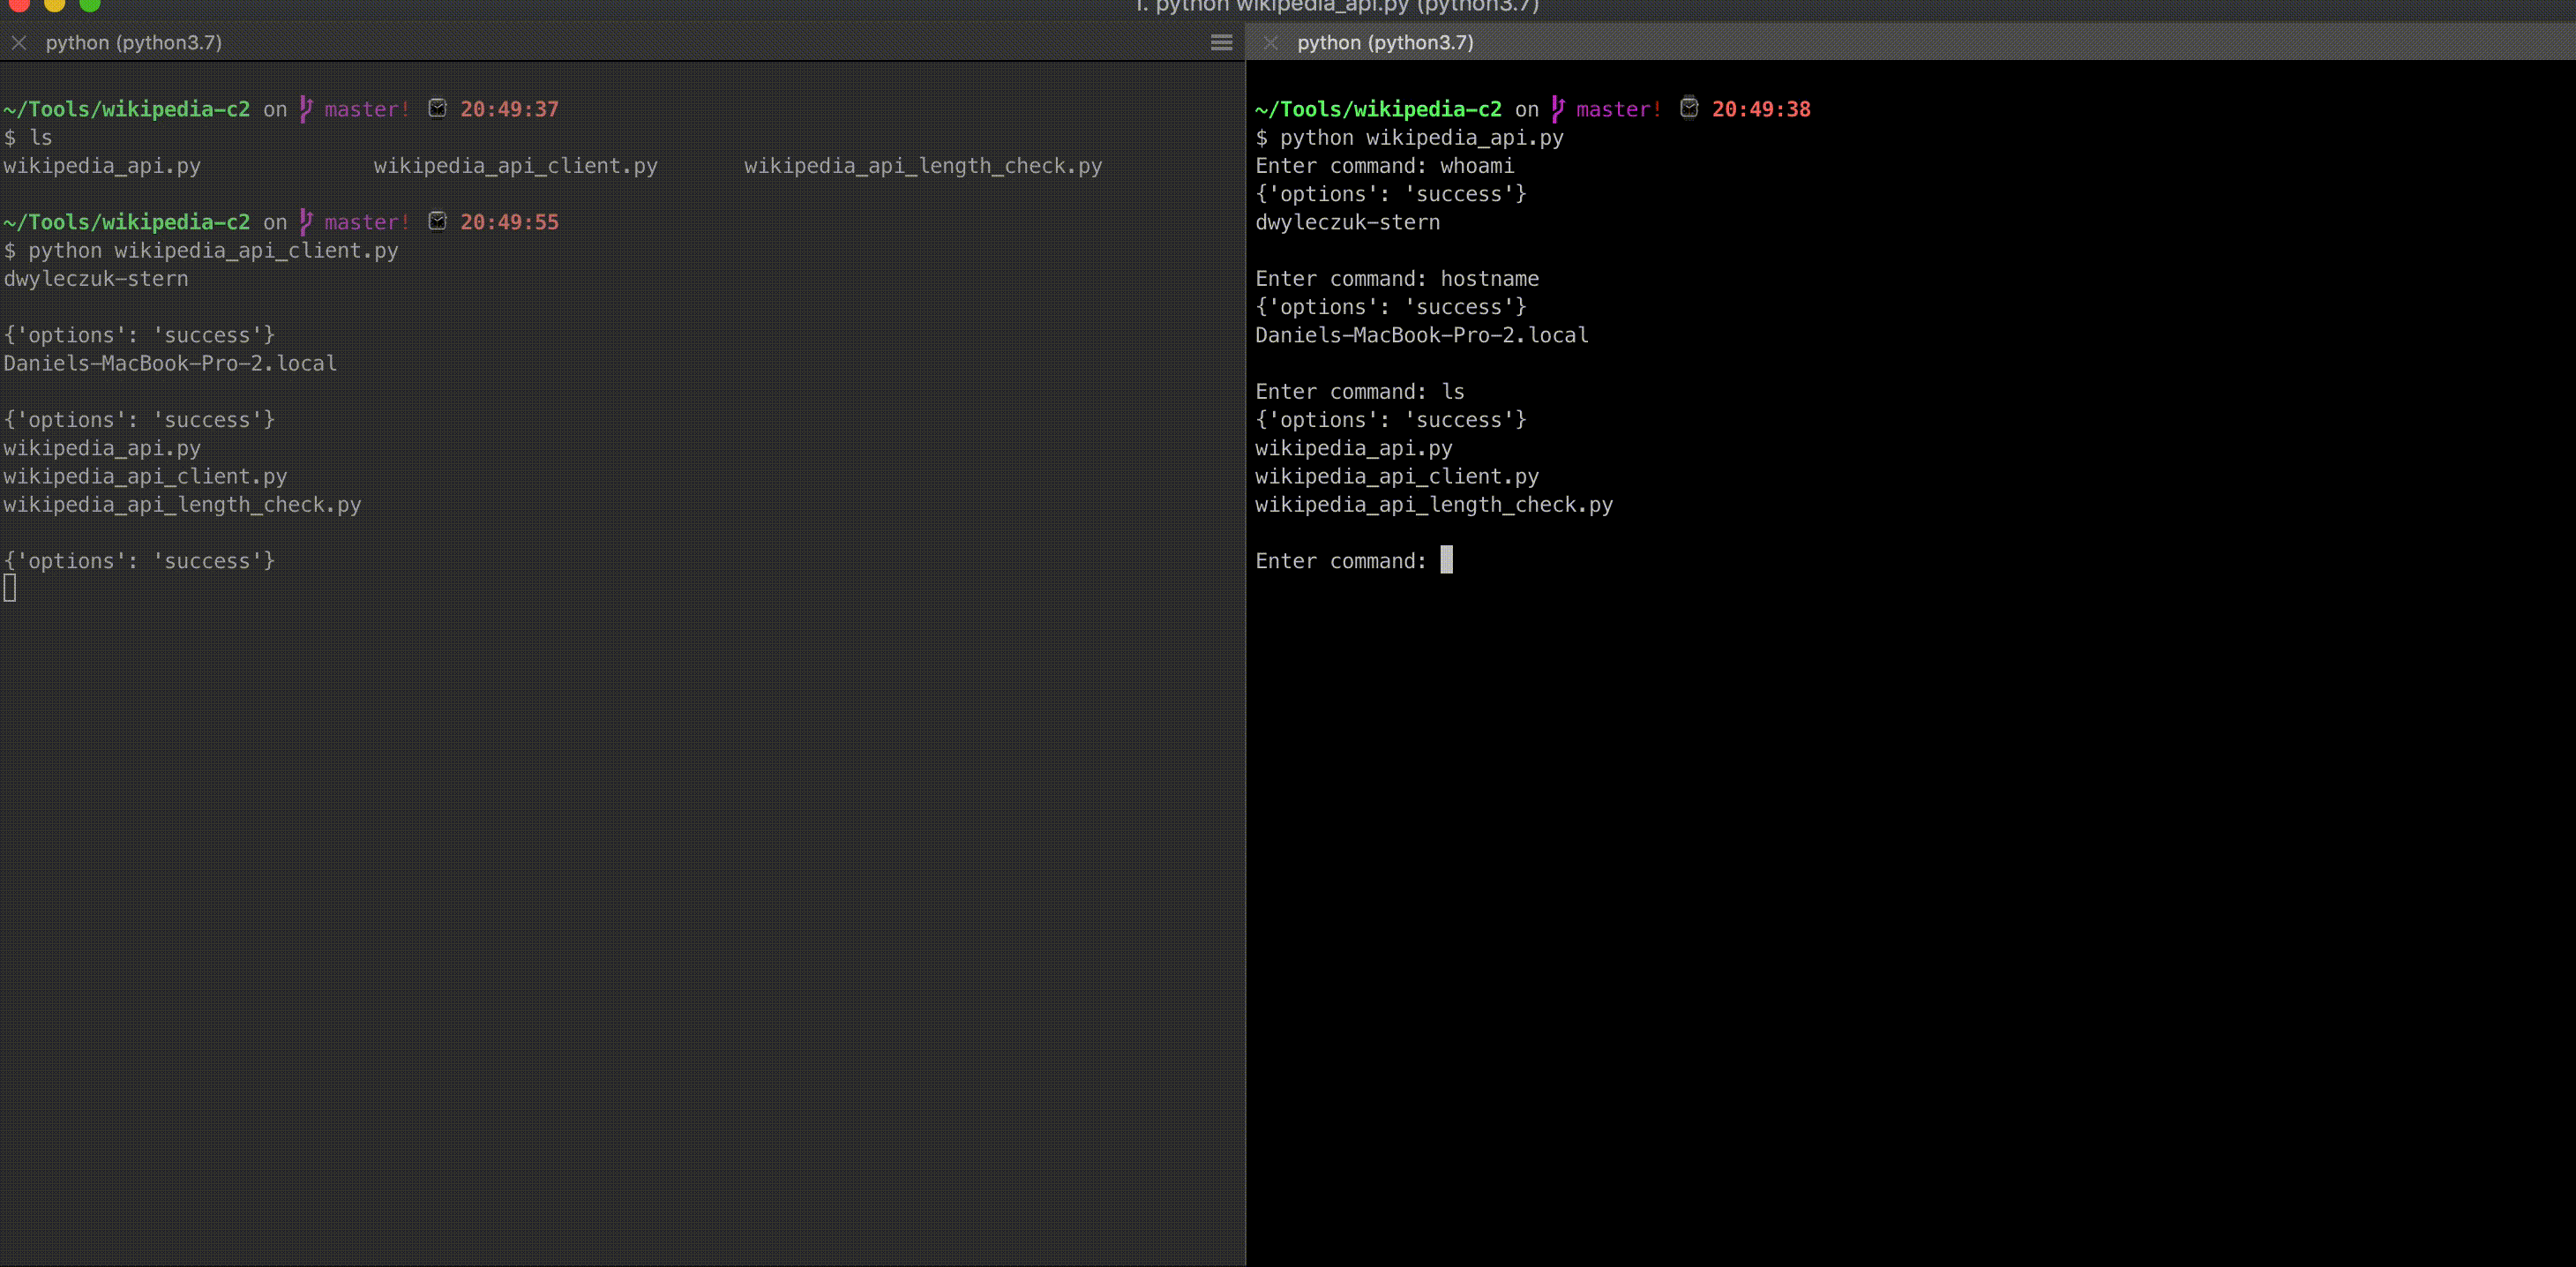 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
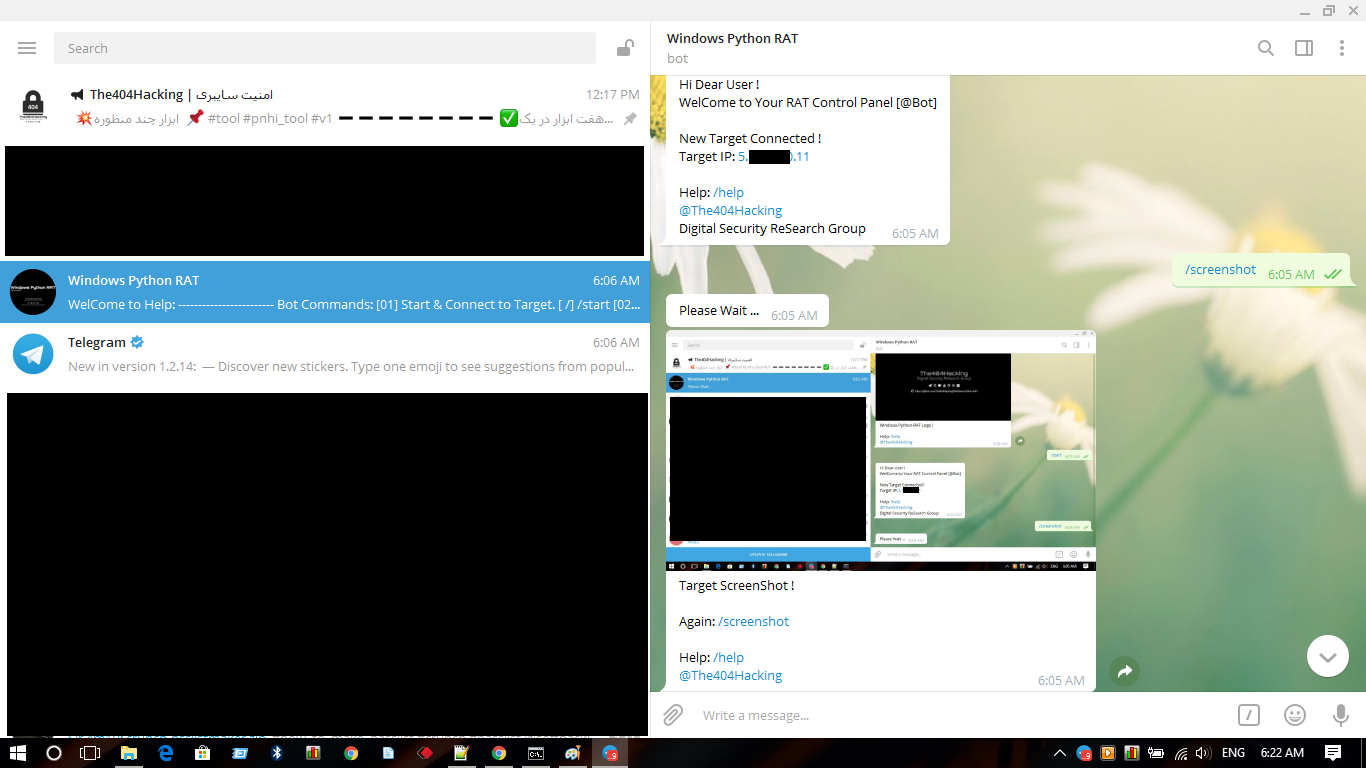 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 mx-moth/flask-saml2
Flask library for building SAML Service Providers and Identity Providers
 mrmtwoj/fix-cve-2026-60137-cve-2026-63030-in-wordpress
CVE-2026-60137Temporary Emergency Mitigation for CVE-2026-60137 & CVE-2026-63030 (wp2shell)
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.