
lm-fingerprint
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
reconnaissanceinformation-gatheringpenetration-testing+3
wattocyber/lm-fingerprintFingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
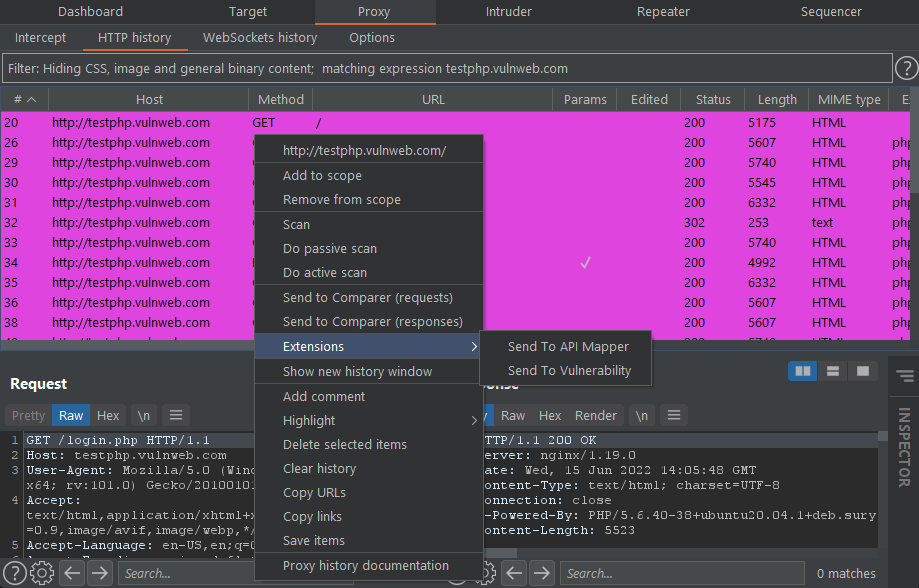 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 h33tlit/secret-regex-list
List of regex for scraping secret API keys and juicy information.
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 shieldfy/api-security-checklist
Checklist of the most important security countermeasures when designing, testing, and releasing your API
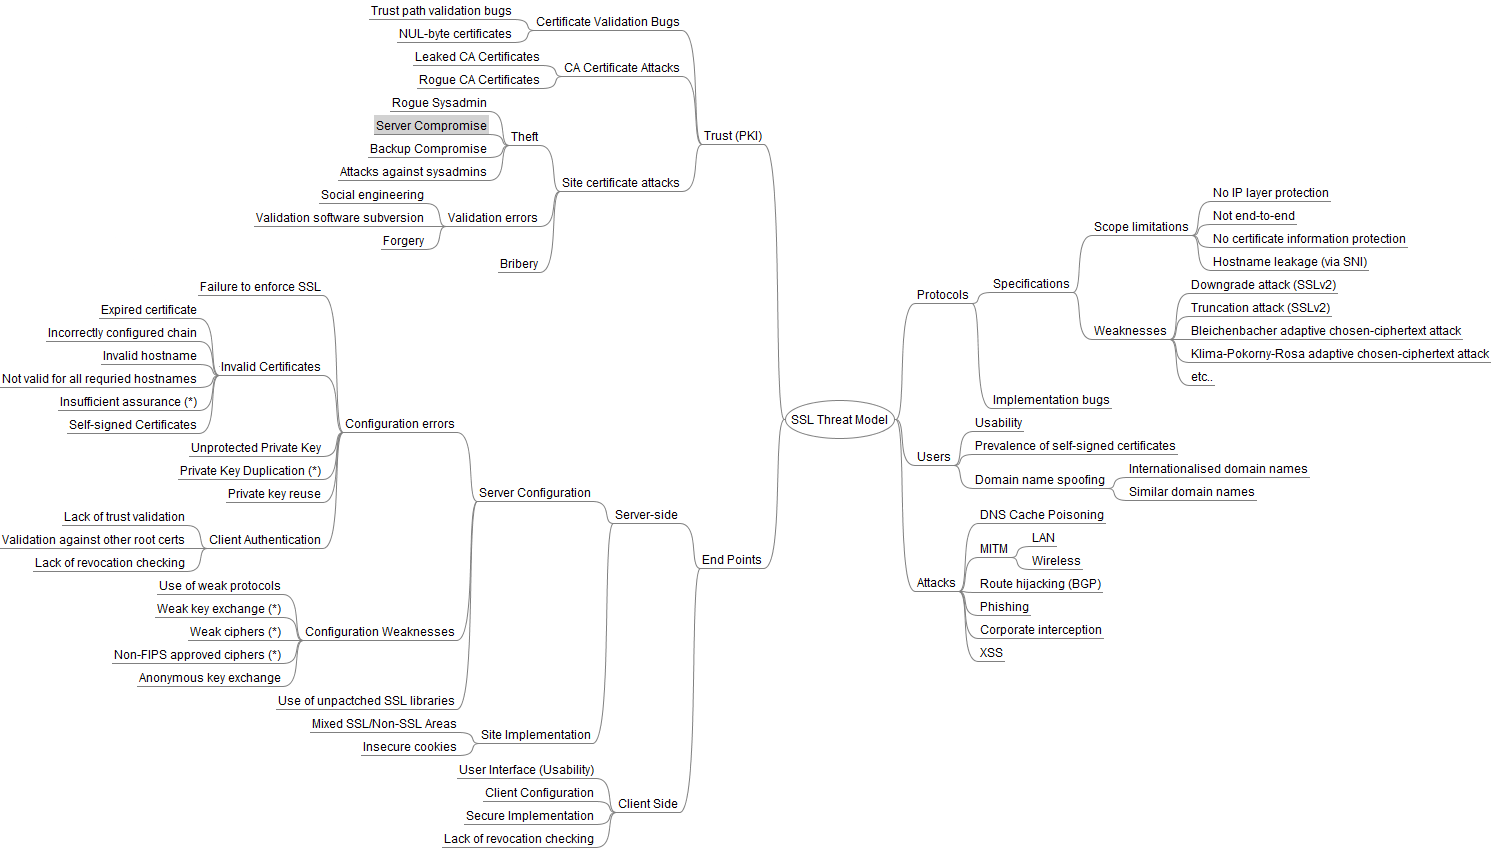 taleliyahu/threat_model_examples
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 sunandm/poc-h2-cve-2026-71554
PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)
 emadshanab/nuclei-templates-collection
Nuclei Templates Collection
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
 agentrust-io/cmcp
cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls.