
llm-agent-testbed
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
vulnerability-analysispenetration-testingeducation+4
16
pie-script/llm-agent-testbedAn empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 juanlunaia/aegis-latent-core
Self-hosted evidence gateway for AI systems: fail-closed policy, WAF, egress controls, signed durable MMR proofs, and offline verification across LLM…
 htrxuan/hdwebmobile-photo-video-reviews
WooCommerce plugin: photo & video product reviews, closing CVE-2026-12684's unauthenticated-upload vulnerability class by construction
 leekanghyun/axios-security-guide
Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 p0pr0ck5/lua-resty-waf
High-performance WAF built on the OpenResty stack
 ory/hydra
OpenID Certified OAuth 2.0 and OpenID Connect provider for token issuance, client management, JWKS, and login/consent flow orchestration via headless…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
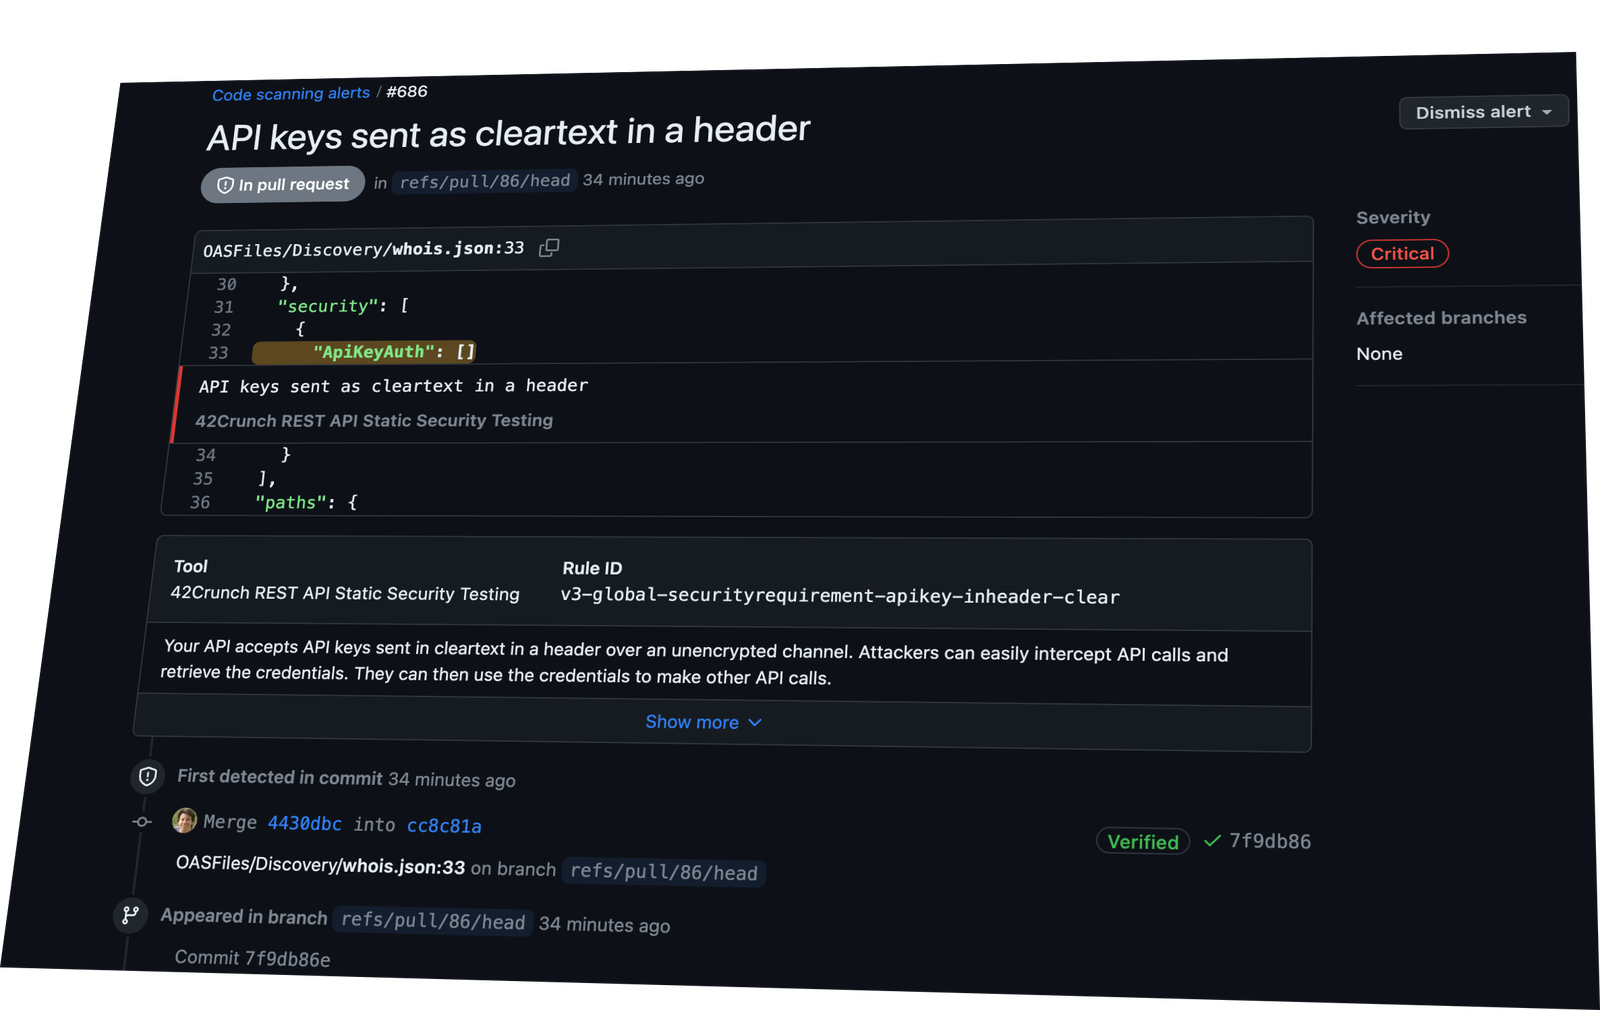 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 davidcarliez/cover
Keep private data, internal infrastructure and secrets out of cloud coding agents without breaking your workflow.
 cerbos/cerbos
Authorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…
 keycloak/keycloak
Open Source Identity and Access Management For Modern Applications and Services
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…