#1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 oalabs/hashdb
Assortment of hashing algorithms used in malware
 princessauroraj/chinese-cybercrime-research
Resources to learn more about Chinese-language cybercrime actors.
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
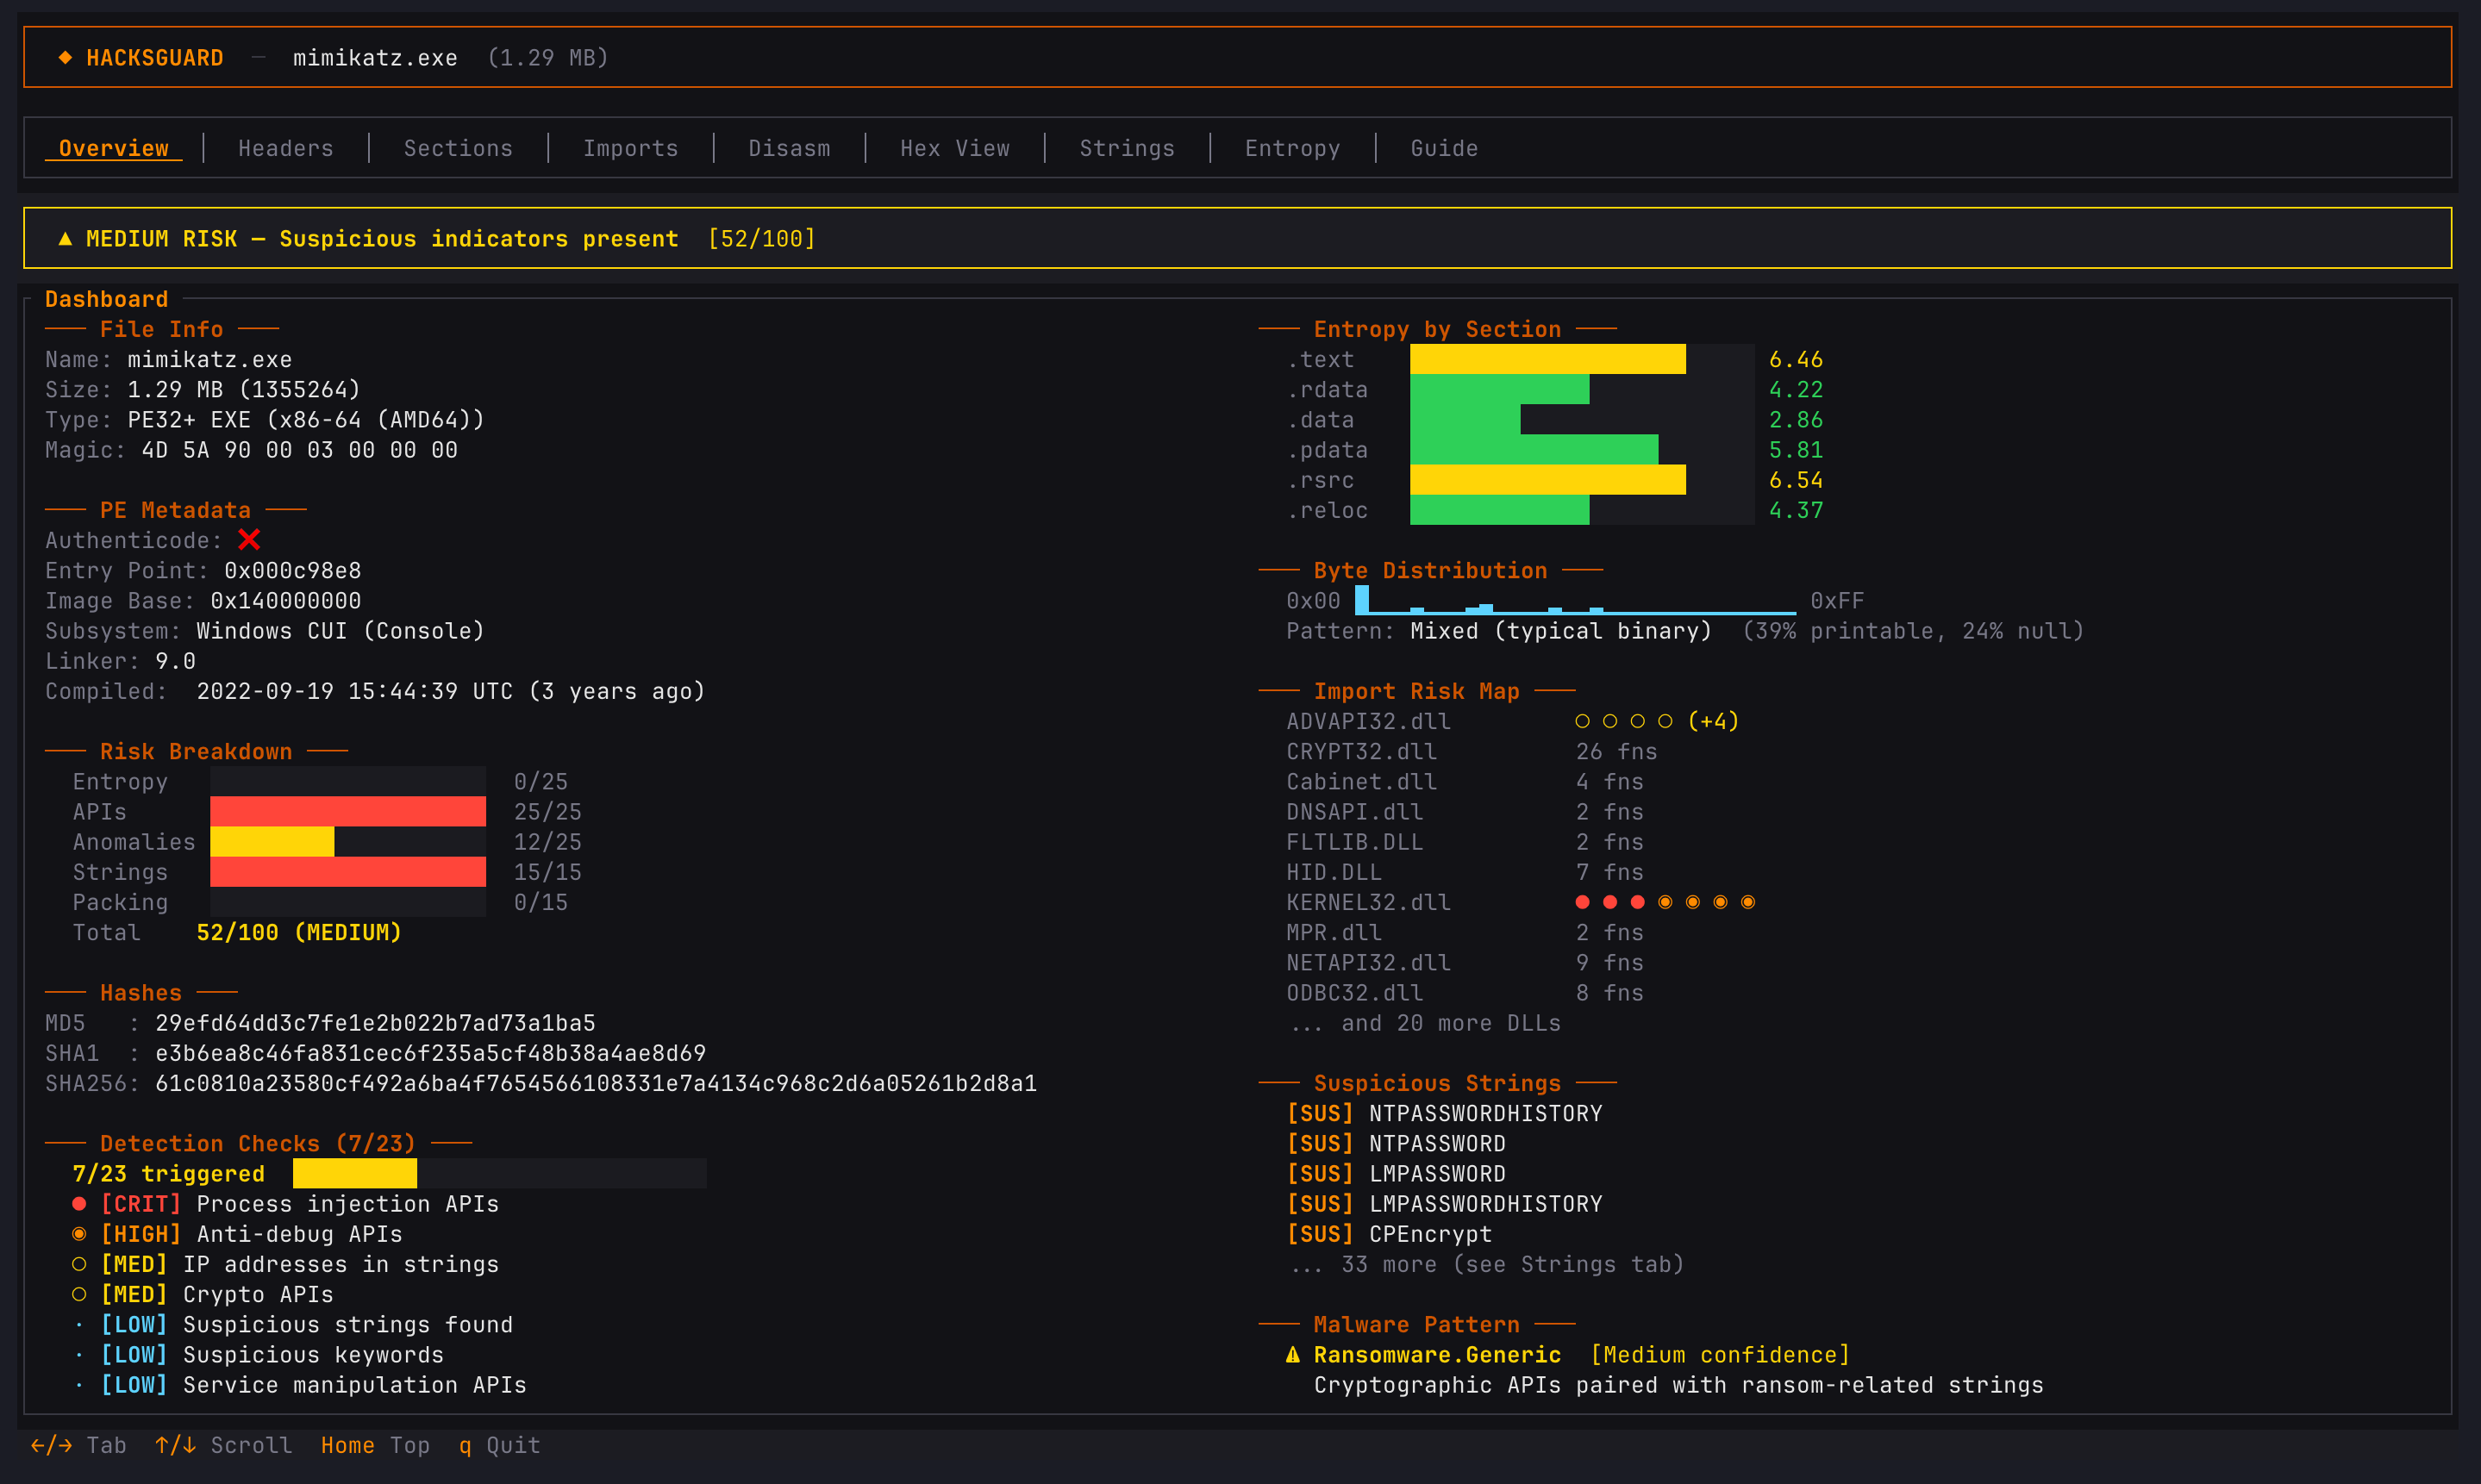 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 zardus/ctf-tools
Some setup scripts for security research tools.
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
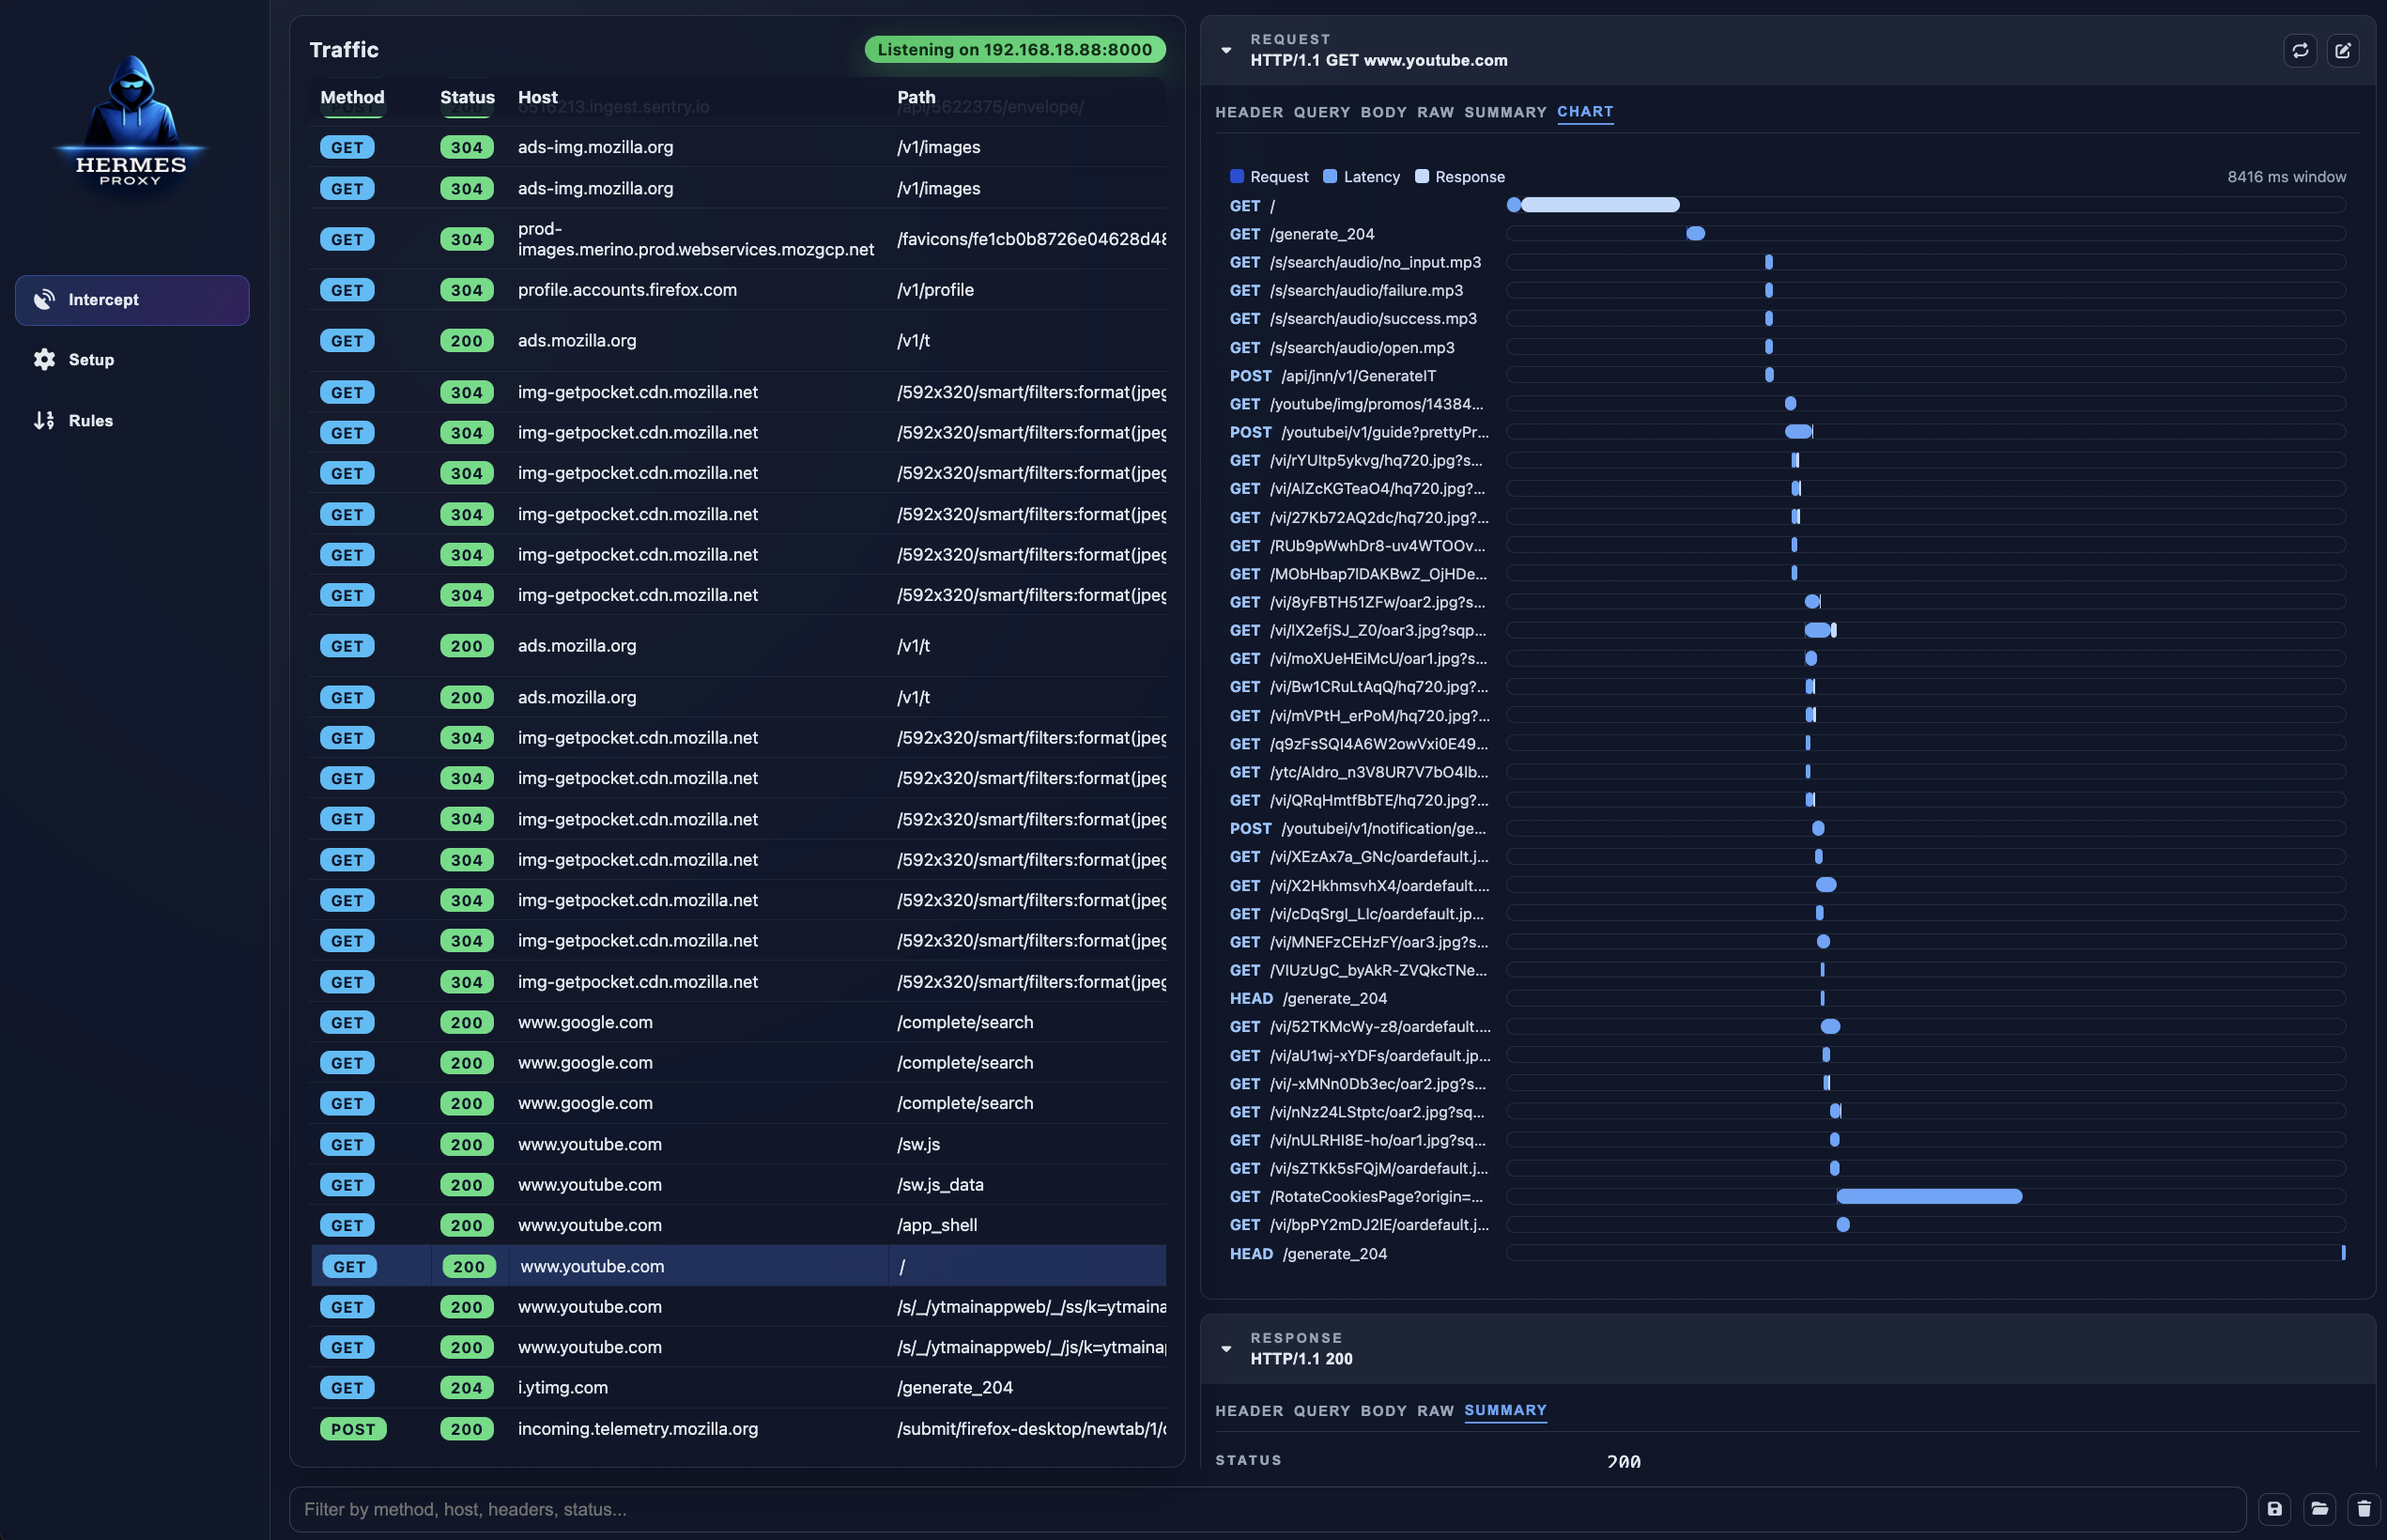 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 xiaoqimikko/pac4j-check
Offline scanner for CVE-2026-29000 (CVSS 10.0) in org.pac4j:pac4j-jwt. Inspects jars/fat-jars directly, so it works where mvn dependency:tree cannot.…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
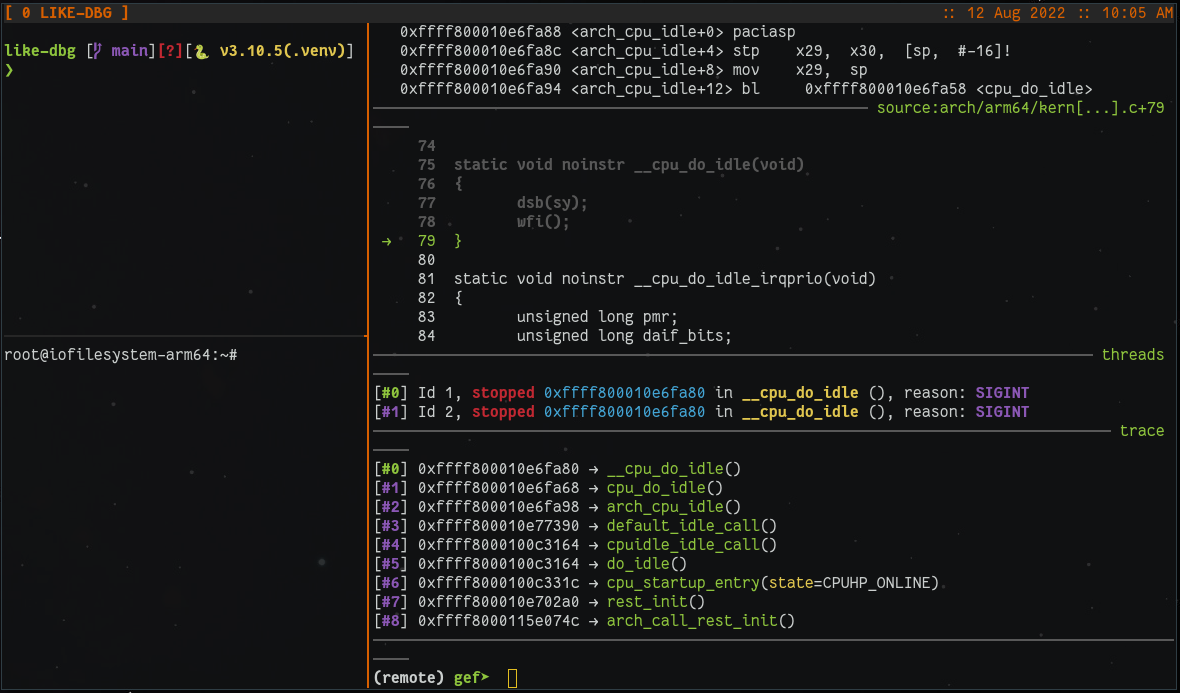 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
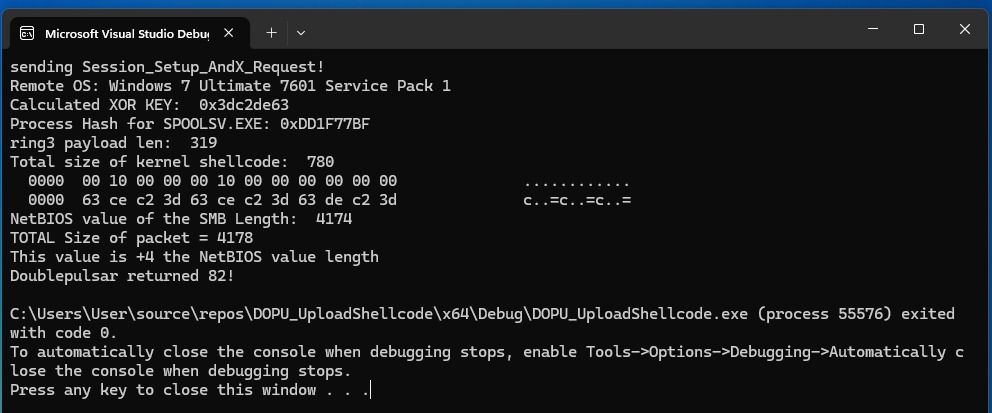 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
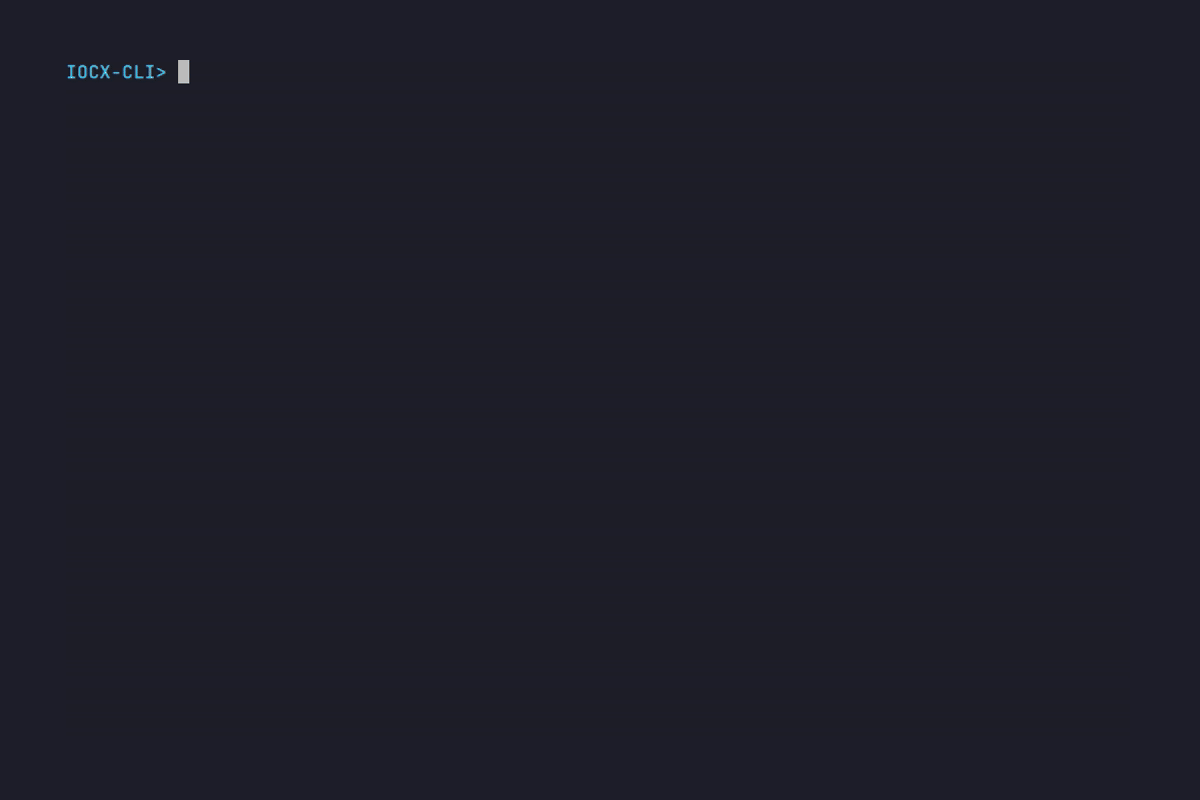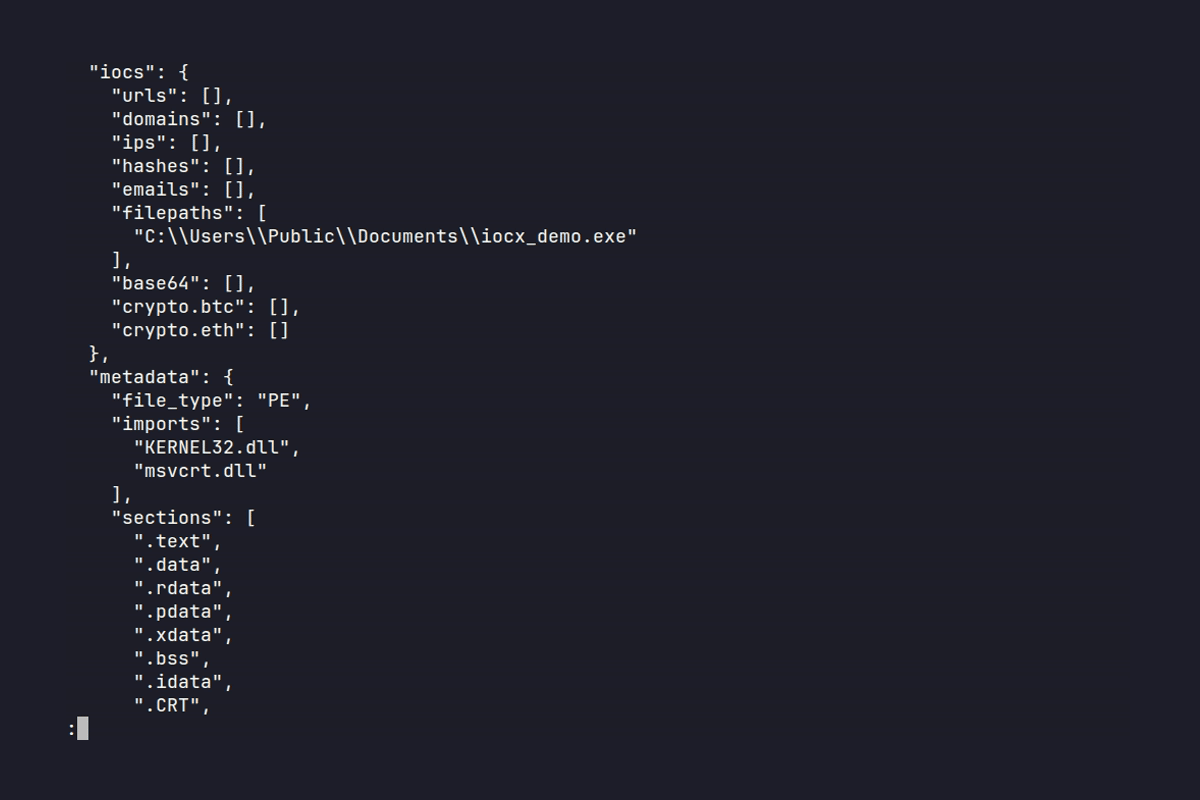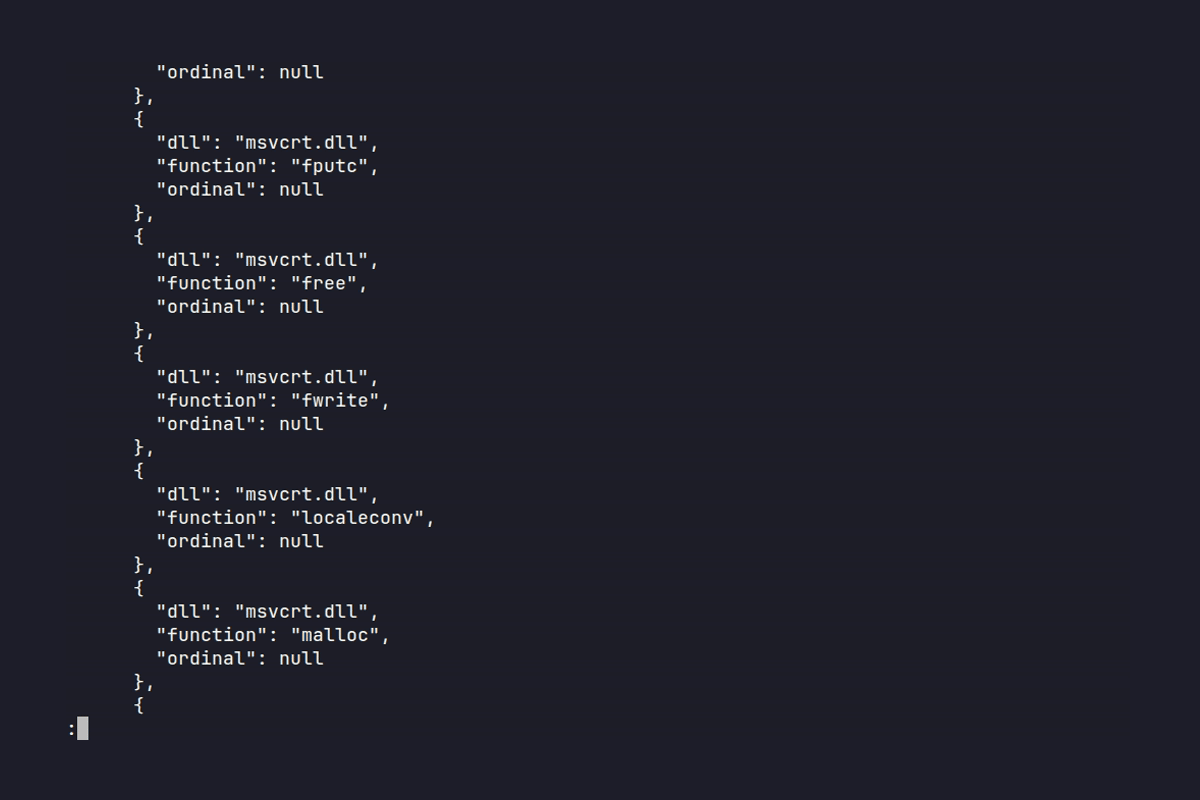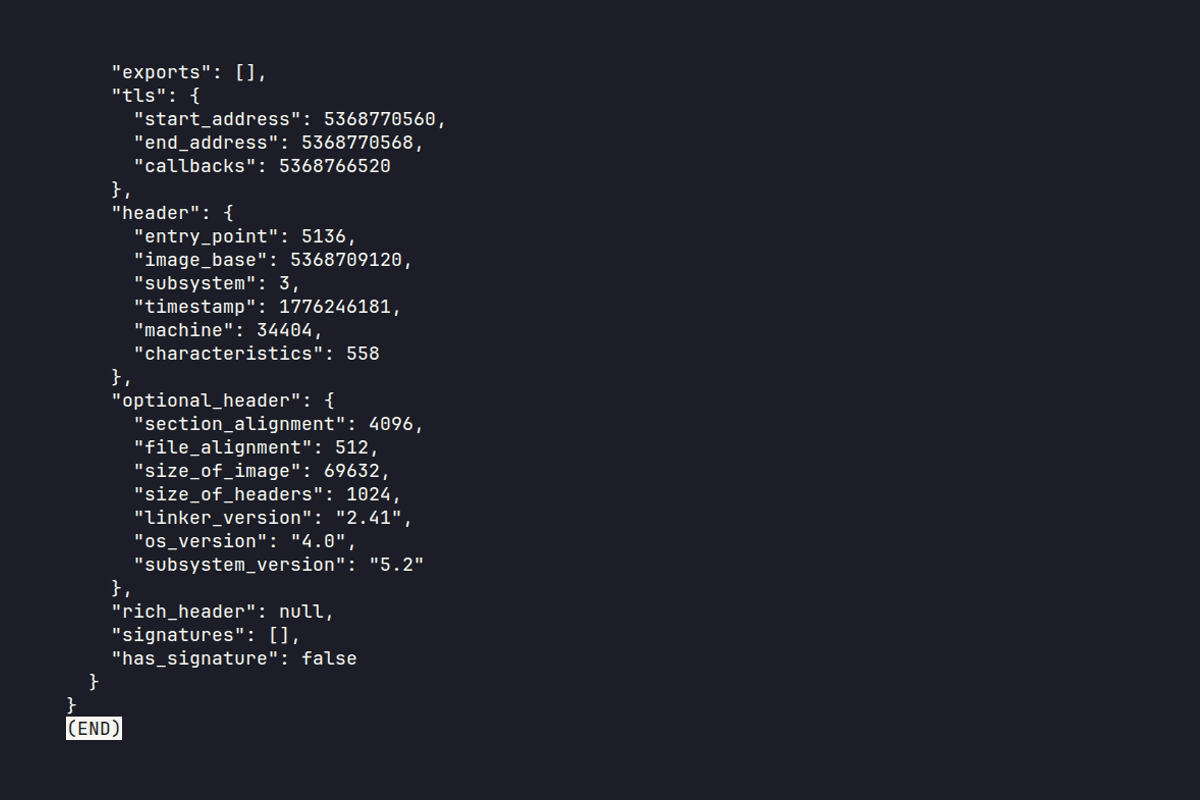 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…