#1
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 upx/upx
UPX - the Ultimate Packer for eXecutables
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 rustsec/rustsec
RustSec API & Tooling
 qybaihe/bla
Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and…
 angr/angr
A powerful and user-friendly binary analysis platform!
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
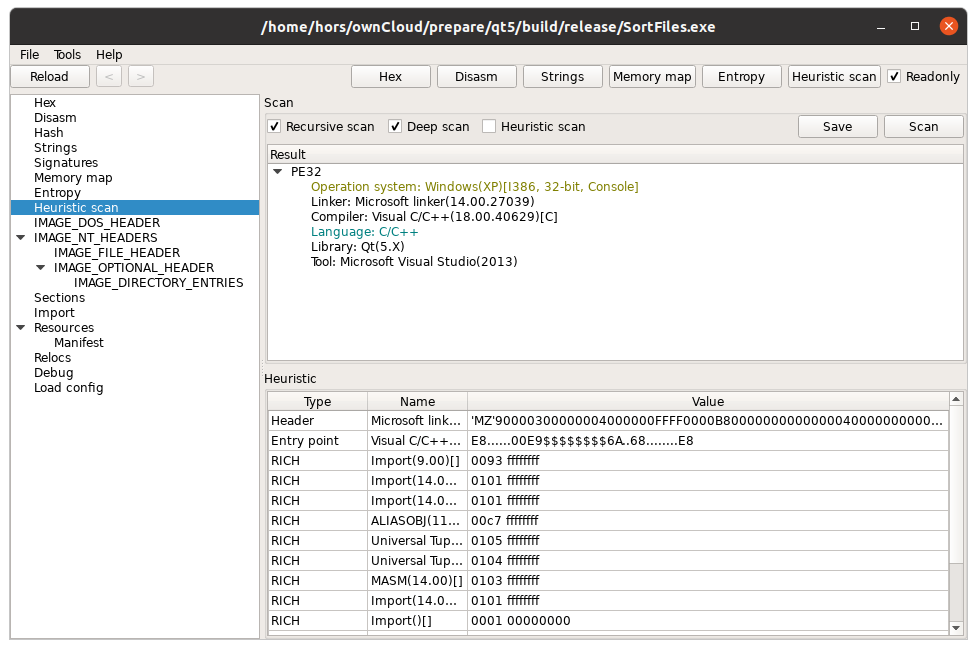 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
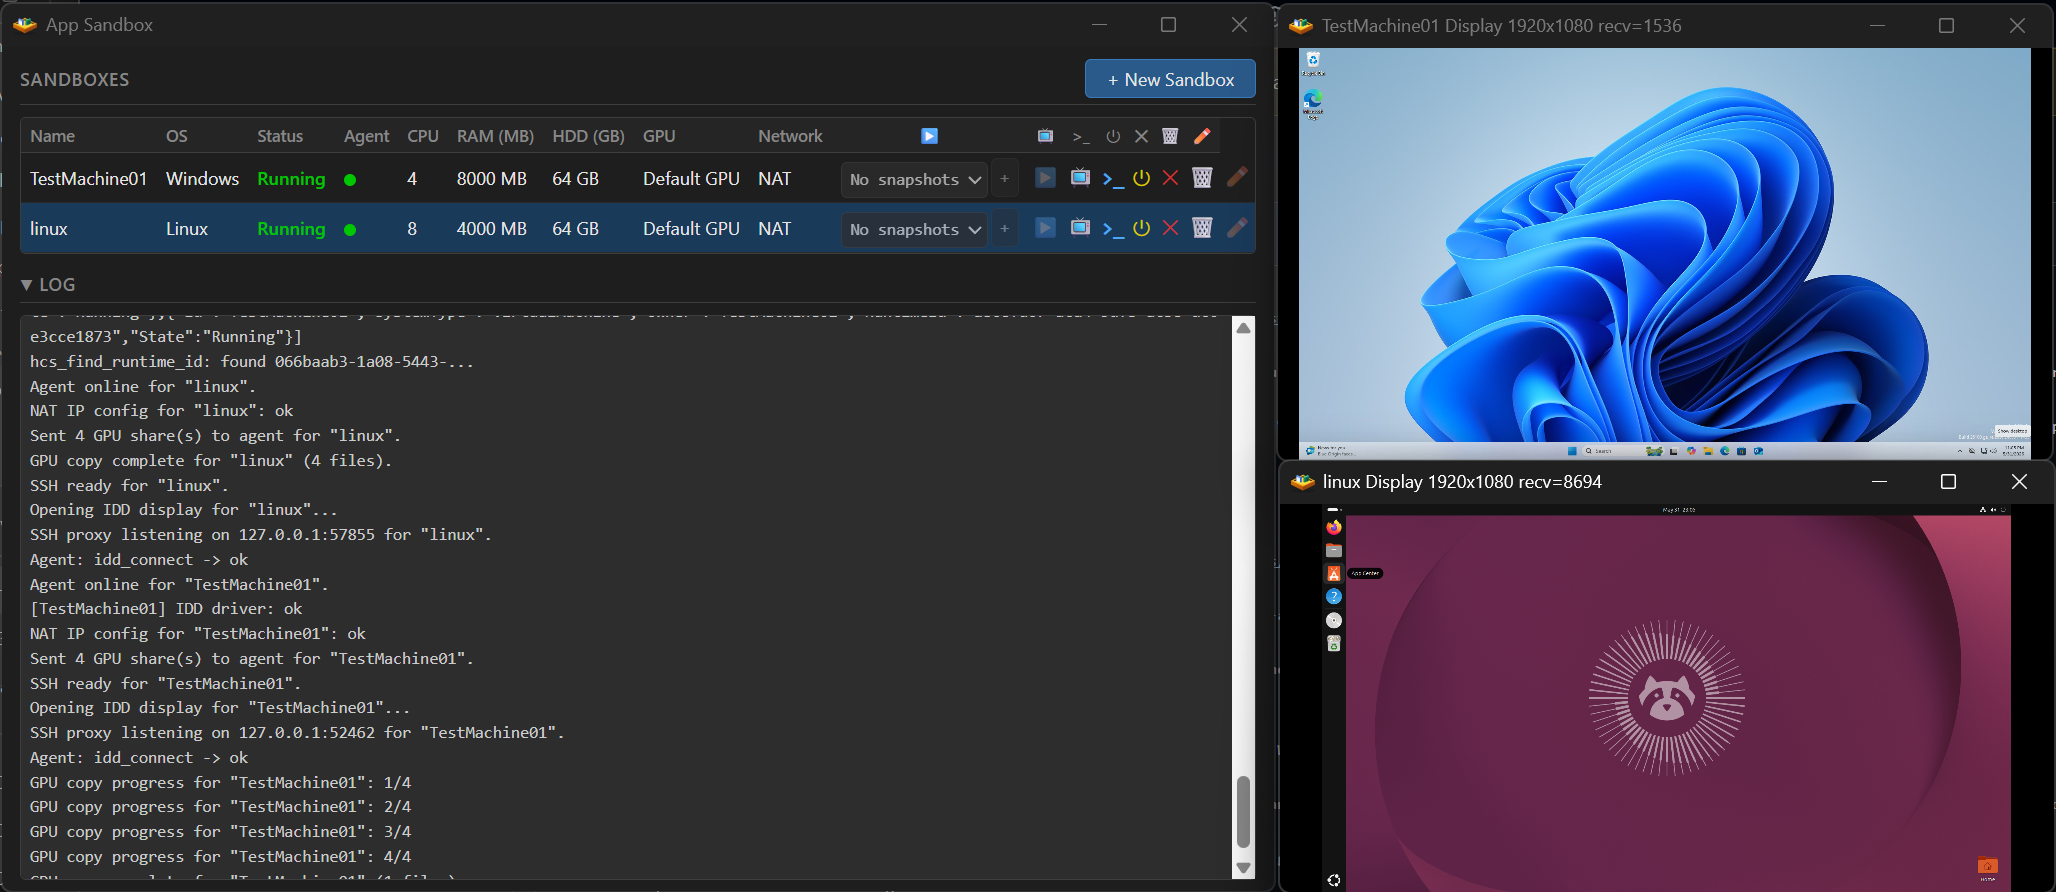 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…