

xssearch
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
crawlerinformation-gatheringpayload-generation+9
6
affolter-engineering/xssearchRust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
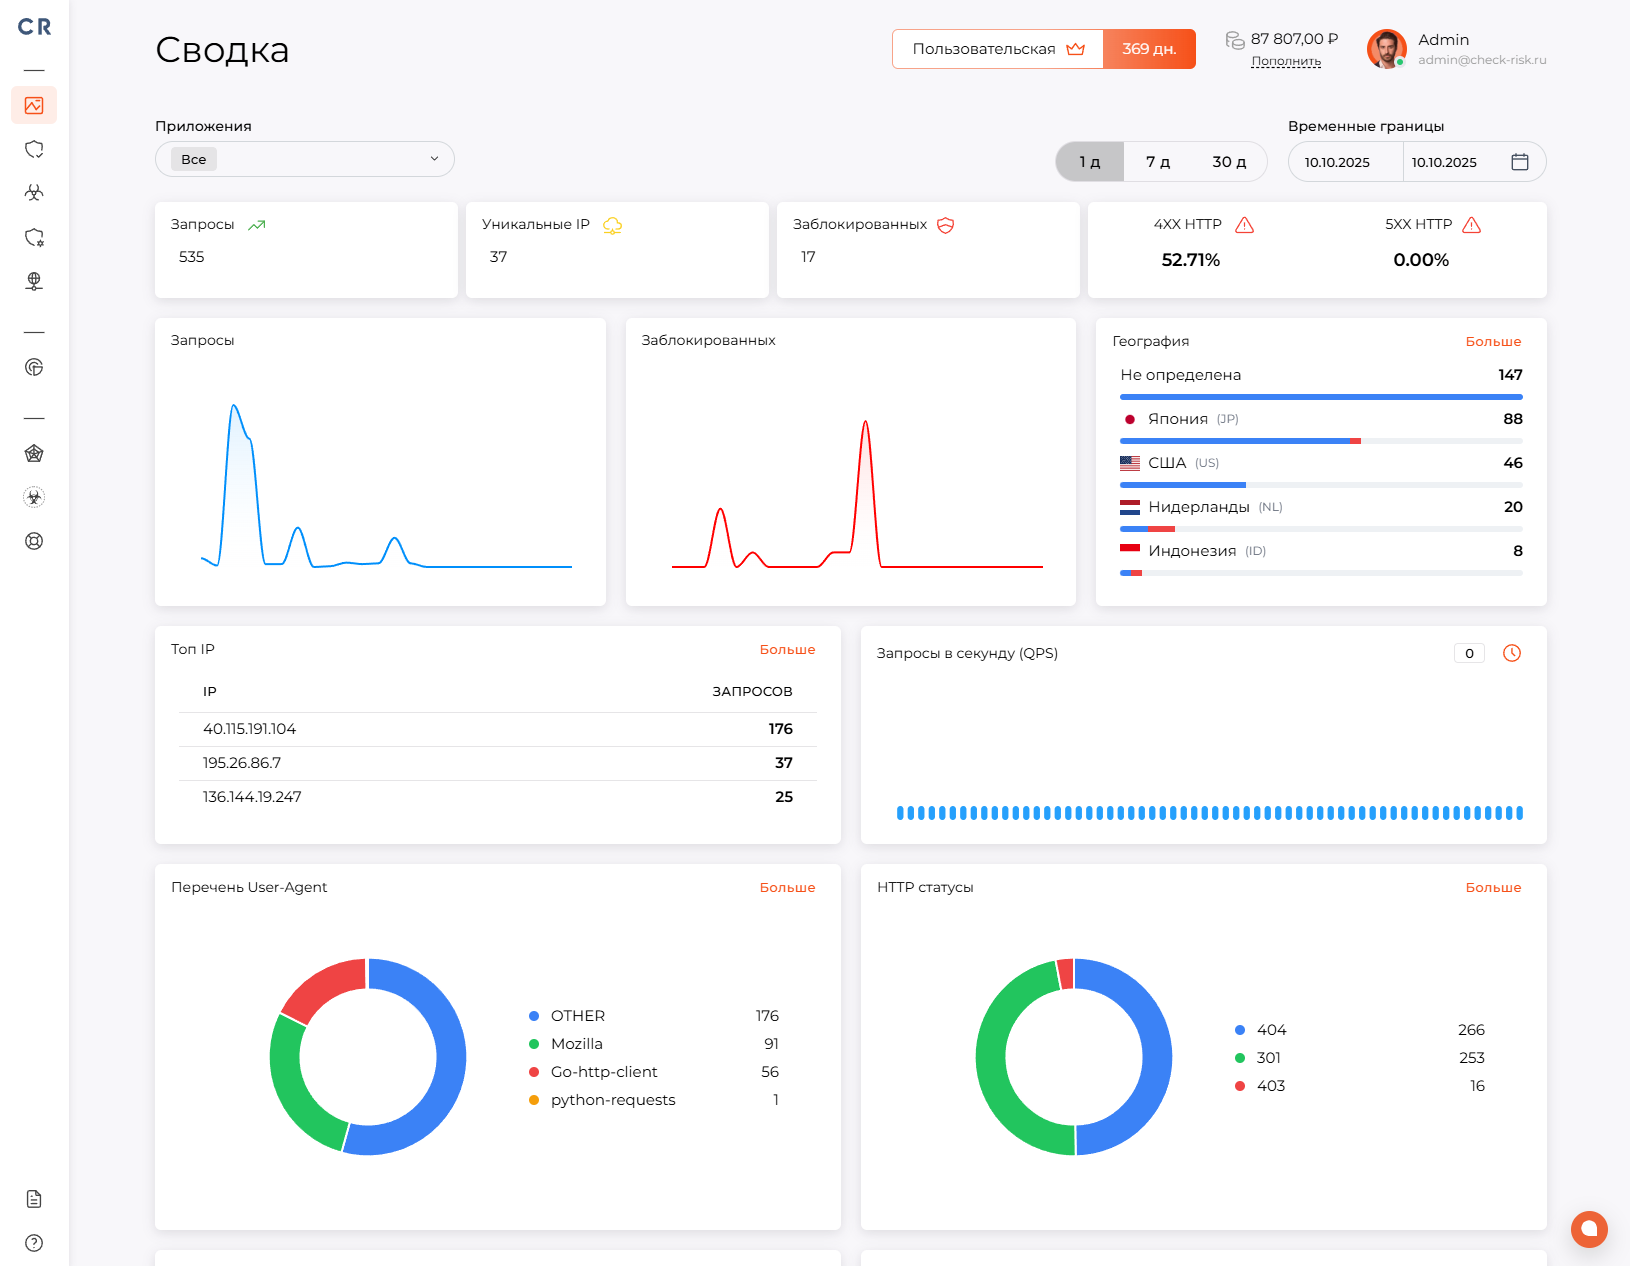
 check-risk-waf/check-risk-waf
Cloud-based Web Application Firewall (WAF) providing L3/L7 protection against SQLi, XSS, DDoS, and bot attacks. Features AI assistant, anti-bot…
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
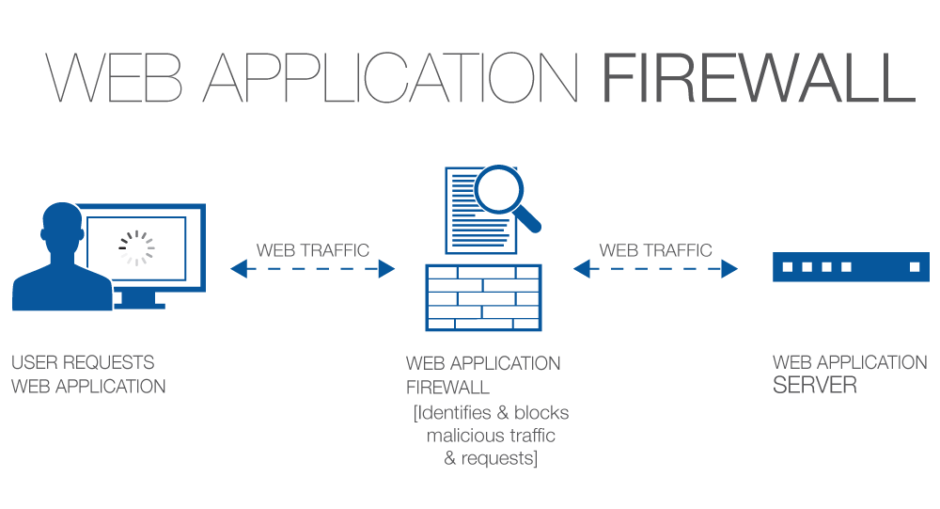 0xinfection/awesome-waf
Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
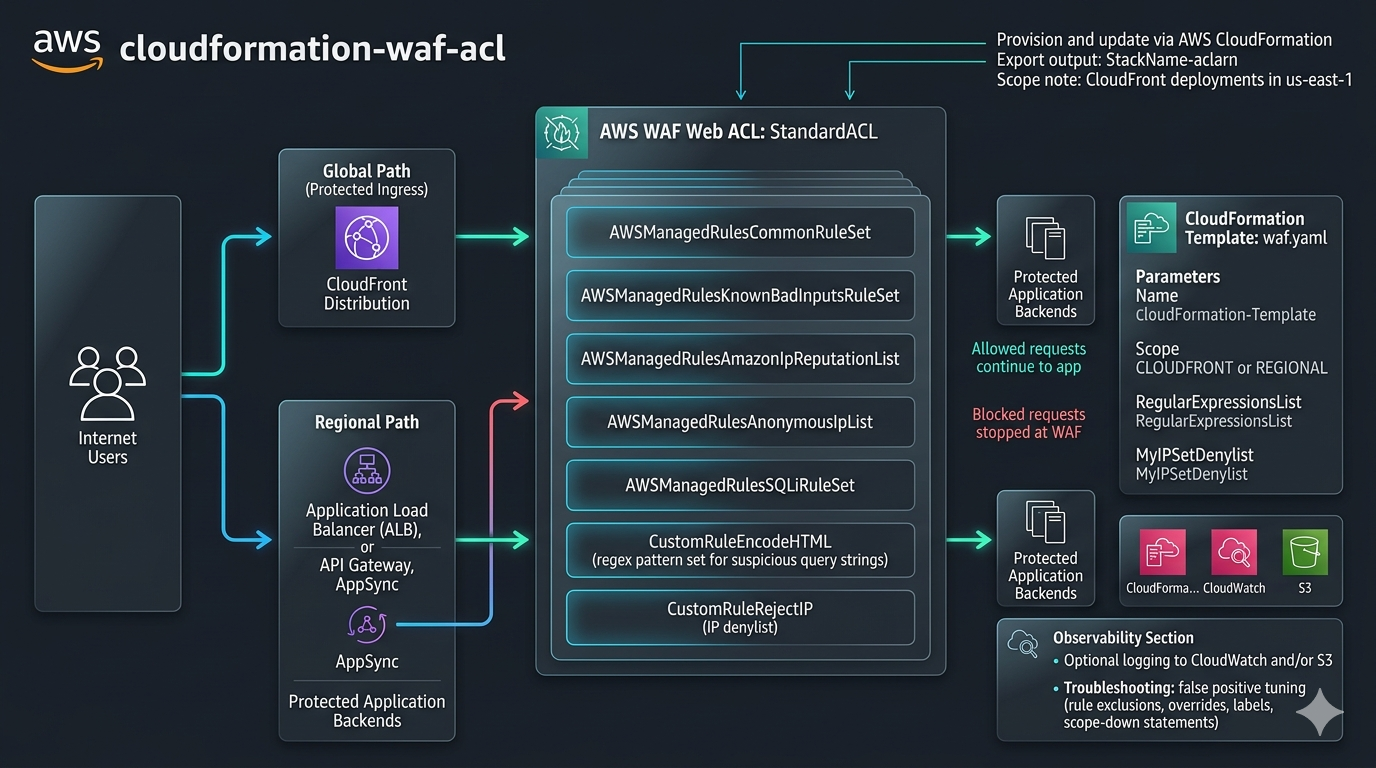 fer1035_aws/cloudformation/cloudformation-waf-acl
An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…
 papamica/waf-checker
Tests your WAF with +160 payloads
 exploreunknowed/cve-2026-24306
Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
 joelvaiju/react2shell-cve-2025-55182-poc
Python PoC for CVE-2025-55182 (React2Shell) RCE in Next.js/React Server Components with dynamic WAF bypass padding for authorized security testing.
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
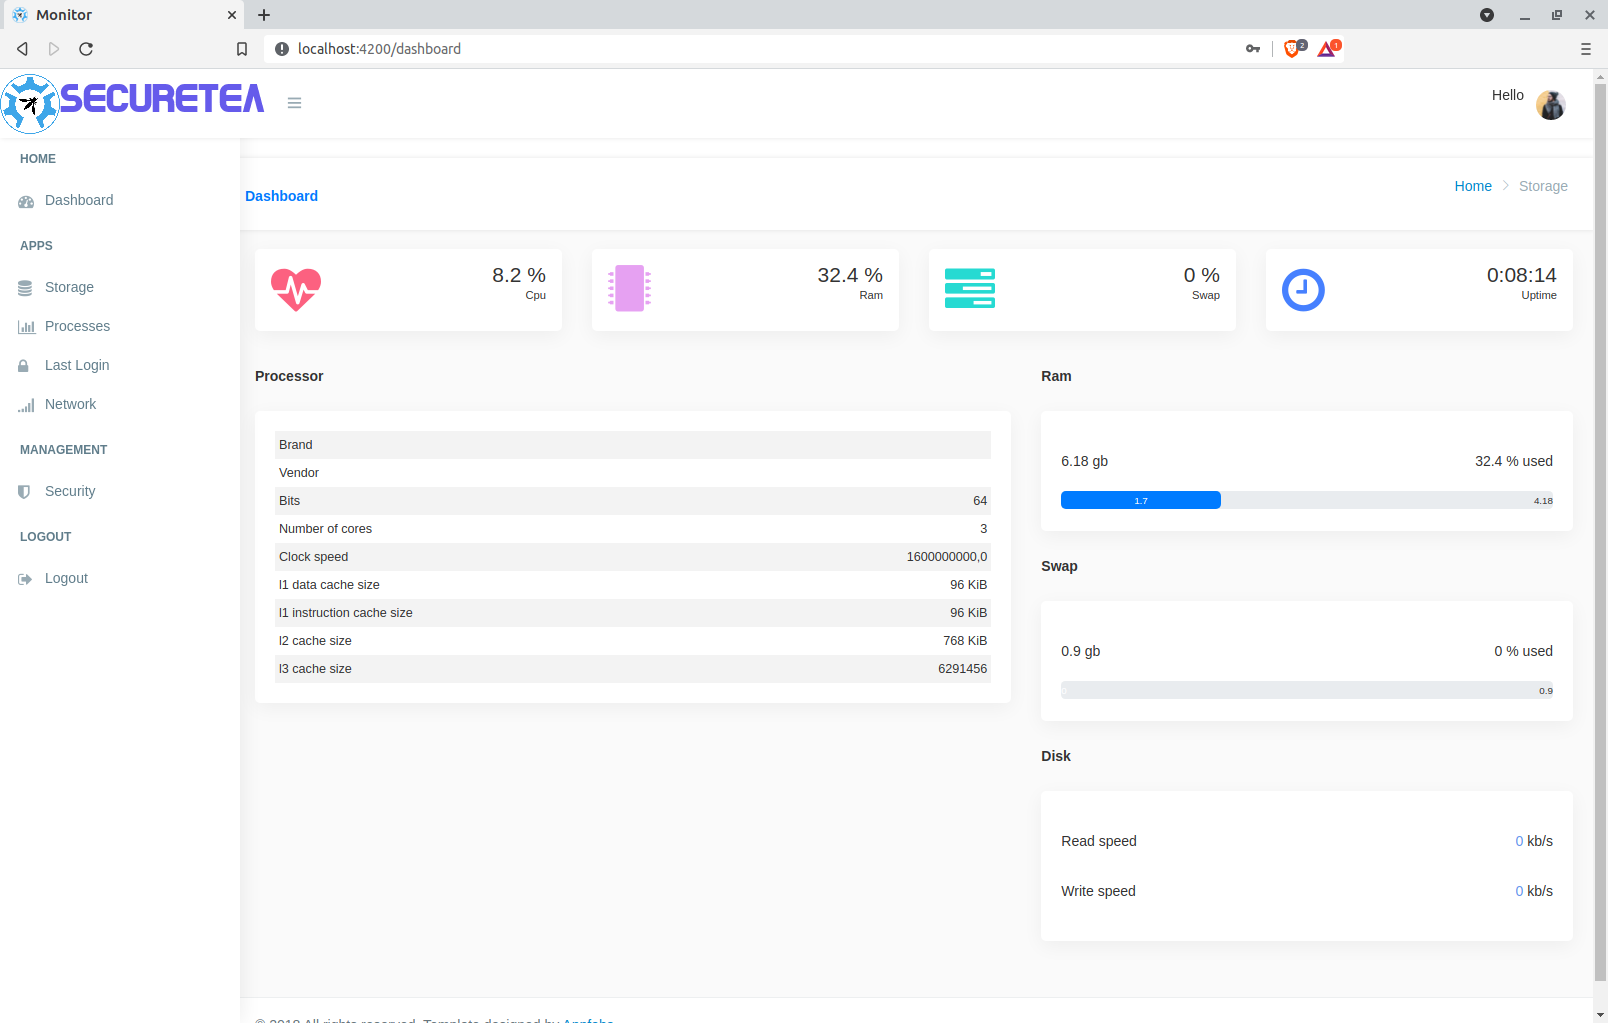 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
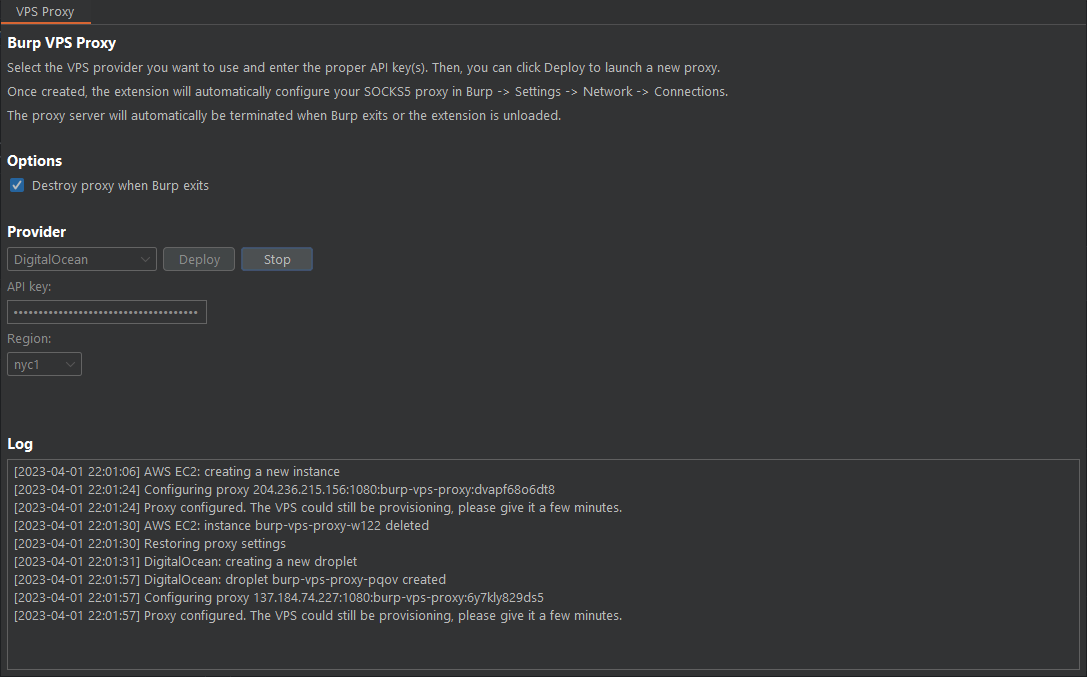 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.