Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/duggytuxy/syswarden
Defensive ToolsConfiguration AuditingNetwork SecurityCloud SecurityThreat IntelligenceIntrusion DetectionLog Analysis
GitHubduggytuxy/syswarden

syswarden

Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log analysis, and authenticated high availability.

View RepositoryWebsite
406321166h 30m agoReviewed by Kitploit
Share
Official SysWarden logo

SysWarden package workflow SysWarden security audit Plumber compliance Plumber Score OpenSSF Scorecard GitHub license Join the official SysWarden Discord

SysWarden

Linux defense. Your host. Your rules.

Host-local Linux defense with auditable, fail-closed enforcement.

Website | Documentation | Build from source | Roadmap

SysWarden is an open-source Linux security orchestrator that combines an authoritative nftables policy, host telemetry, threat-intelligence lists, out-of-band WAAP log analysis, authenticated high availability and a native terminal dashboard. It is designed for operators who want one reviewable host defense layer without placing another proxy in the application data path.

SysWarden is not an inline HTTP proxy, a traffic sanitizer or a regulatory certification product.

Current source version: v4.10.4.

The latest stable release is v4.10.4, validated under IVV (Integration, Verification and Validation).

Use the installation guide, historical recovery and removal guide and release verification record. Intermediate releases follow IVV; Upgrade generations require full IVVQ. Later source builds do not inherit a published release verdict.
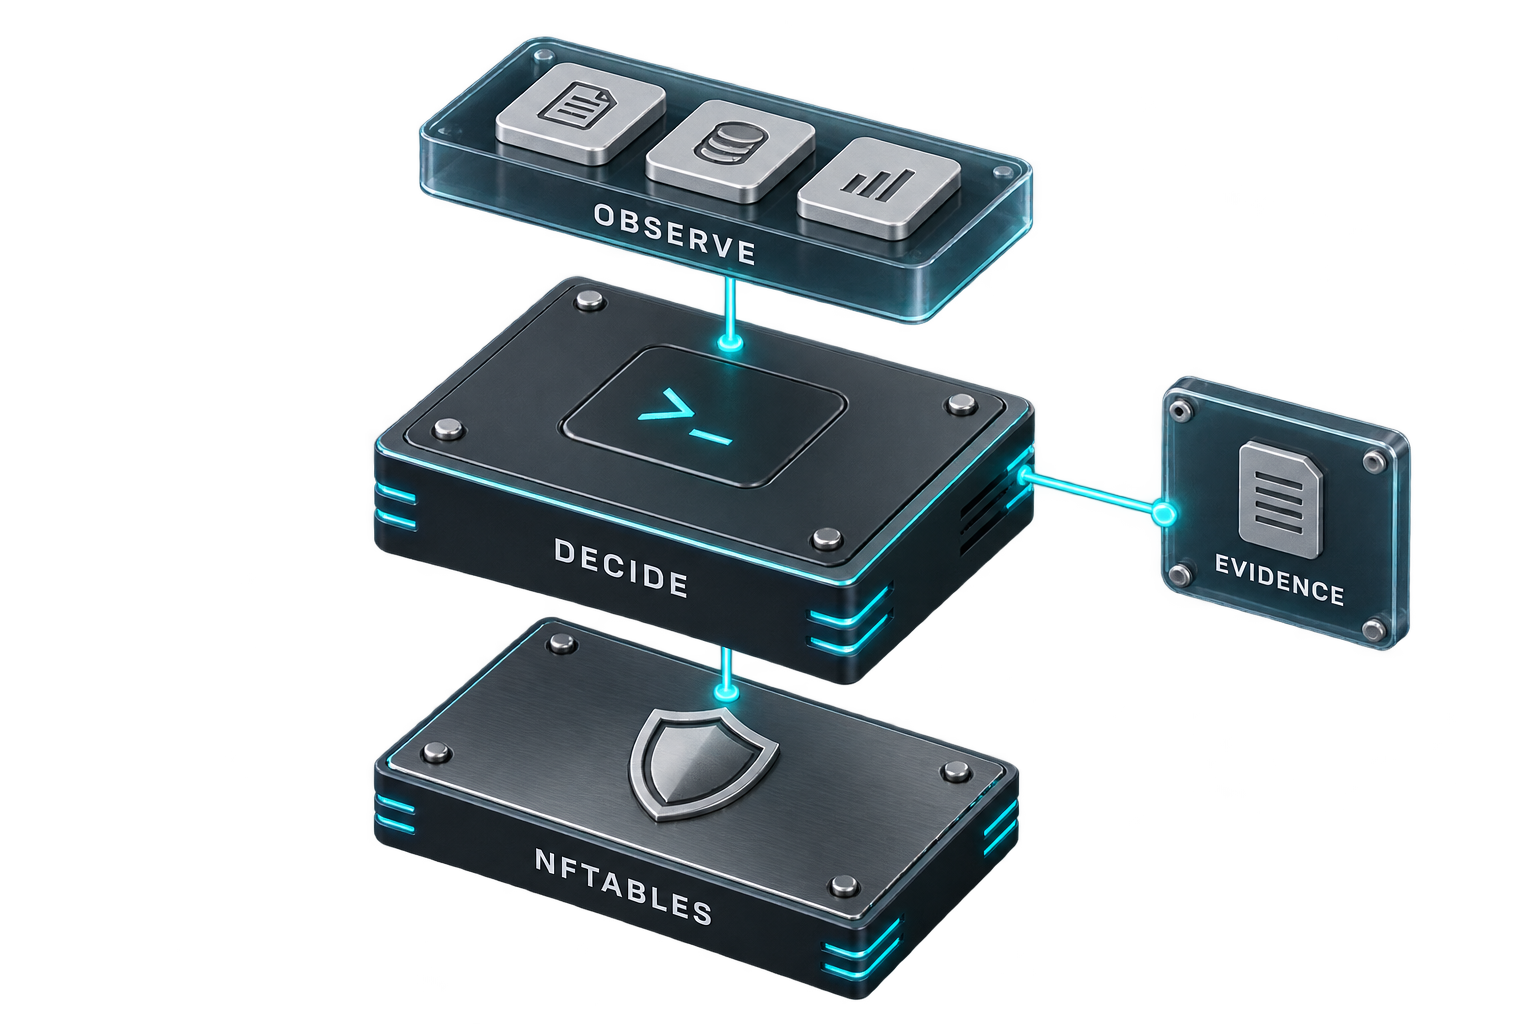
Observe, decide, enforce

Conceptual defense flow: host signals feed policy decisions, nftables enforces validated actions, and evidence records the outcome.

SysWarden observes host signals, evaluates operator policy and applies validated actions through nftables. Logs and release evidence help operators review what was observed and exercised. This illustration summarizes the defense model; individual capabilities remain subject to their documented version and scope.

Features

  • Authoritative nftables enforcement with bounded firewalld and UFW compatibility when exactly one supported frontend is already active.
  • Persistent blocklists, whitelists and SSH exceptions with canonical IP, CIDR and service-scoped entries.
  • Host telemetry and out-of-band WAAP log analysis for local detection and response workflows.
  • Bounded threat-intelligence feeds with last-known-good publication behavior.
  • Native local terminal dashboard with no browser service or listening port.
  • Authenticated HA synchronization over TLS 1.3 with explicit ownership and migration-fence controls.
  • Optional BunkerWeb integration with authenticated HA and provenance-aware cleanup.
  • Native DEB, RPM and APK packaging for supported amd64 Linux hosts.

Capabilities

AreaWhat SysWarden provides
HIDSHost-local telemetry, security-log analysis and alert visibility
HIPSValidated policy decisions enforced through authoritative nftables rules
WAAPOut-of-band analysis of logs written by a supported upstream service
Threat intelligenceCanonical local lists and bounded external feed updates
High availabilityTLS 1.3, bearer authentication and peer-scoped synchronization
OperationsLocal CLI and TUI, modular configuration, audit and lifecycle controls
Supply chainChecksummed Linux packages, signed update metadata and release evidence

BunkerWeb integration plugin

Use the optional BunkerWeb integration plugin to connect supported BunkerWeb security events to SysWarden host enforcement through the authenticated HTTPS API. The integration guide covers configuration and compatibility. Follow the version-specific prerequisites before enabling synchronization or HA v2.

Release inventory and verification

The stable v4.10.4 release publishes a machine-readable SPDX software bill of materials, syswarden-sbom.spdx.json, for dependency review. An SBOM is an inventory, not a vulnerability-free claim.

SHA256SUMS.txt checks package integrity against the downloaded inventory. Authenticate the Ed25519-signed update manifest with an independently trusted release key before installing a manually downloaded package. The operator guidance explains the existing verifier, its trust prerequisites and the distinction between package authentication and the SBOM inventory.

Intelligence Sources

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →