Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
awswaf — AWS WAF Solver, full reverse implemented in 100% Python & Golang. | Kitploit

Tools/GitHubGitHub/xkiian/awswaf
IDS/IPS EvasionWeb Application ExploitationWAF BypassWeb SecurityAnti-BotCAPTCHA Bypass
GitHubxkiian/awswaf

awswaf

AWS WAF Solver, full reverse implemented in 100% Python & Golang.

View Repository
35166971 year agoReviewed by Kitploit
Share

AWS WAF (Amazon Web Services Web Application Firewall) Solver

wakatime

Overview

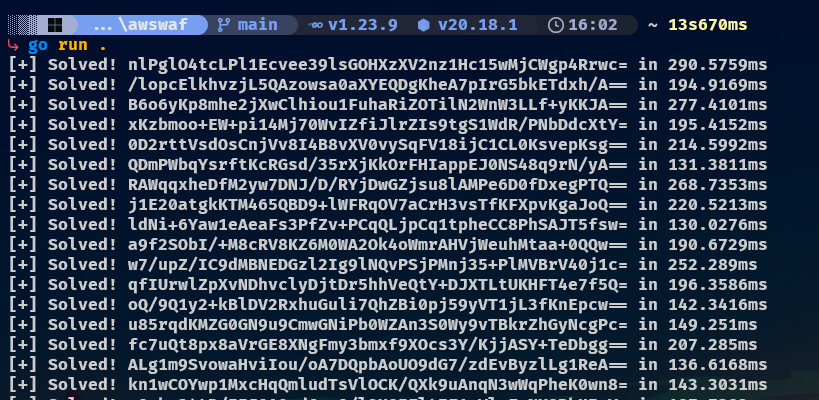
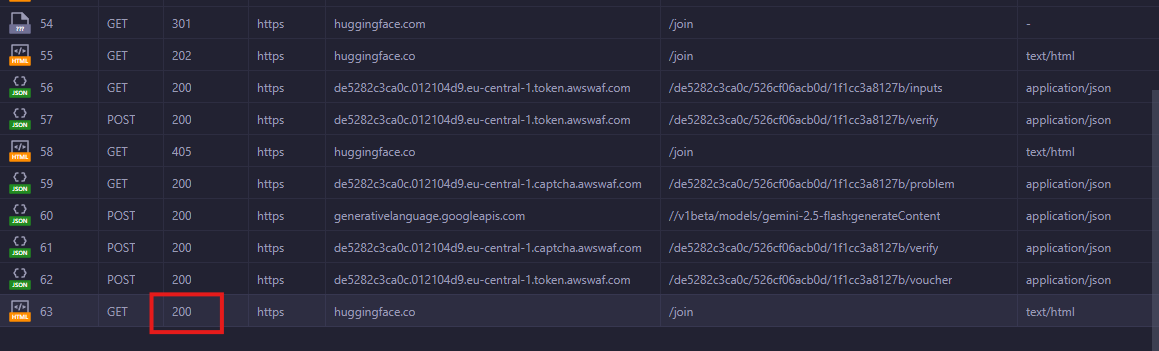
This project provides a Golang & Python-based solver for the AWS WAF challenge. It supports both the type "token" / "Invisible" and type "Captcha" using gemini


⭐️ Show Your Support

Please star the repository if you find it useful! Your support helps improve the project. ❤️


Usage

Golang

package main

import (
	"awswaf/internal/aws"
	"log"
)

func main() {
	// host & gokuProps are obtained from the initial response 
	// and can be extracted using aws.Extract(body)
	// proxy can be "" to use no proxy at all
	waf, err := aws.NewAwsWaf(
		host,
		"www.binance.com",
		"Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/137.0.0.0 Safari/537.36",
		gokuProps, proxy,
	)
	if err != nil {
		log.Println(err)
		return
	}
	
	token, err := waf.Run()
	if err != nil {
		log.Println(err)
		return
	}
	// the token is the aws-waf-token cookie
}

See main.go for a full example


Python

from awswaf.aws import AwsWaf

token = AwsWaf(goku, endpoint, "www.binance.com")()

# the token is the aws-waf-token cookie

See main.py for a full example


License

This project is licensed under the MIT License - see the LICENSE file for details.


Star History

Star History Chart

Disclaimer

This package is unofficial and not affiliated with Amazon or AWS. Use it responsibly and in accordance with AWS's terms of service.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    501
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    467
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    314
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    295

Explore all tools

Browse our collection of tools

View all tools →