

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitLabGitLab/fer1035_aws/cloudformation/cloudformation-waf-acl
Vulnerability ScannersConfiguration AuditingWeb SecurityCloud SecurityMisconfiguration
GitLabfer1035_aws/cloudformation/cloudformation-waf-acl

cloudformation-waf-acl

An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern set, and an IP set.

View Repository
314 months agoNot yet reviewed
Share

cloudformation-waf-acl

An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern set, and an IP set.
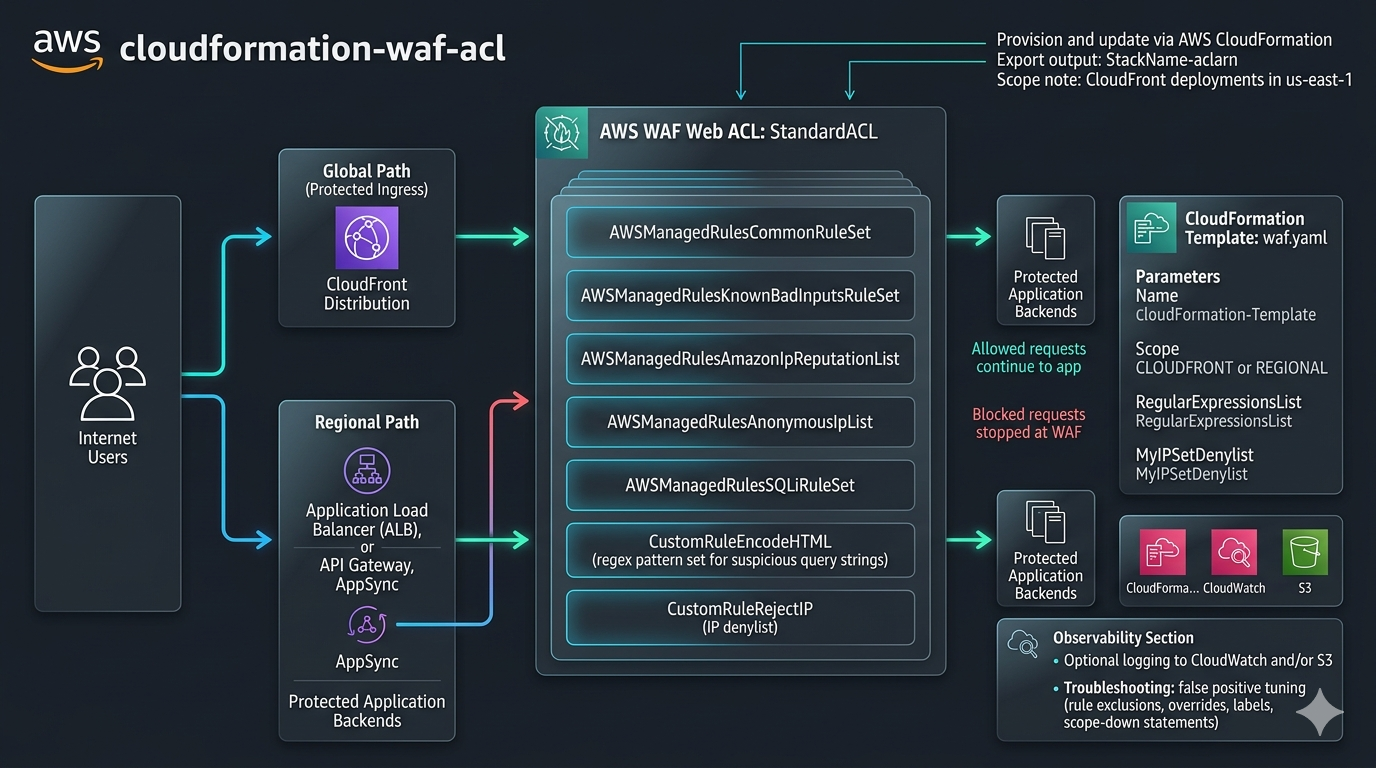
"Solution diagram"

Components

The template provisions:

  1. An AWS::WAFv2::WebACL.
  2. AWS managed protection rule groups:
    • AWSManagedRulesCommonRuleSet
    • AWSManagedRulesKnownBadInputsRuleSet
    • AWSManagedRulesAmazonIpReputationList
    • AWSManagedRulesAnonymousIpList
    • AWSManagedRulesSQLiRuleSet
  3. A custom regex pattern set (CustomRuleEncodeHTML) that can be enabled to block encoded/suspicious query string input.
  4. A custom IP set (CustomRuleRejectIP) that can be enabled to block selected source IPs.
  5. A CloudWatch log group (CloudWatchLogGroup) to store the WebACL logs.

The stack exports the Web ACL ARN as ${StackName}-aclarn.

Parameters

The template accepts the following parameters:

  1. Name
    • The name of the ACL to create.
  2. Scope
    • Allowed values: CLOUDFRONT or REGIONAL.
    • Controls where the Web ACL can be associated.
  3. RegularExpressionsList
    • Comma-delimited regex patterns (for example, ^(.*<.*)+$,^(.*>.*)+$,^(.*".*)+$,^(.*'.*)+$).
  4. MyIPSetDenylist
    • Comma-delimited list of IPv4 CIDRs (for example, 203.0.113.10/32,198.51.100.0/24).

For Scope=CLOUDFRONT, run deployments in us-east-1.

Deployment

Use CloudFormation deploy to create or update the stack.

  • Login to your AWS account and clink the quick link to deploy in CloudFormation (recommended), or

  • Download the template and deploy manually in the CloudFormation console, especially if you'd like to customize it.

Example: Regional Web ACL (for ALB, API Gateway, AppSync, etc.)

aws cloudformation deploy \
  --template-file waf.yaml \
  --stack-name waf-standard-regional \
  --capabilities CAPABILITY_NAMED_IAM \
  --parameter-overrides \
  Name=StandardACL \
  Scope=REGIONAL \
  RegularExpressionsList="^(.*<.*)+$,^(.*>.*)+$,^(.*\".*)+$,^(.*'.*)+$" \
  MyIPSetDenylist="203.0.113.10/32,198.51.100.0/24"

Example: CloudFront Web ACL

aws cloudformation deploy \
  --region us-east-1 \
  --template-file waf.yaml \
  --stack-name waf-standard-cloudfront \
  --capabilities CAPABILITY_NAMED_IAM \
  --parameter-overrides \
  Name=StandardACL \
  Scope=CLOUDFRONT \
  RegularExpressionsList="^(.*<.*)+$,^(.*>.*)+$,^(.*\".*)+$,^(.*'.*)+$" \
  MyIPSetDenylist="203.0.113.10/32,198.51.100.0/24"

Associate the Web ACL

After deployment, associate the Web ACL ARN output with your resource:

  1. CloudFront distribution (for Scope=CLOUDFRONT).
  2. Application Load Balancer, API Gateway, or other regional resources (for Scope=REGIONAL).

You can retrieve stack outputs with:

aws cloudformation describe-stacks \
  --stack-name waf-standard-regional \
  --query 'Stacks[0].Outputs'

Troubleshooting

If valid traffic is blocked by AWS Managed Rules, use one or more of the following approaches:

  1. Add higher-priority custom allow/exception rules.
  2. Override or exclude specific managed sub-rules.
  3. Pin or change managed rule group versions.
  4. Use labels and scope-down statements to narrow inspection.

Additional Protection Options for CloudFront

  1. Enable logging to CloudWatch, S3, or both for operational visibility.
  2. Add custom error responses.

These can be done manually, or using the helper script.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





