
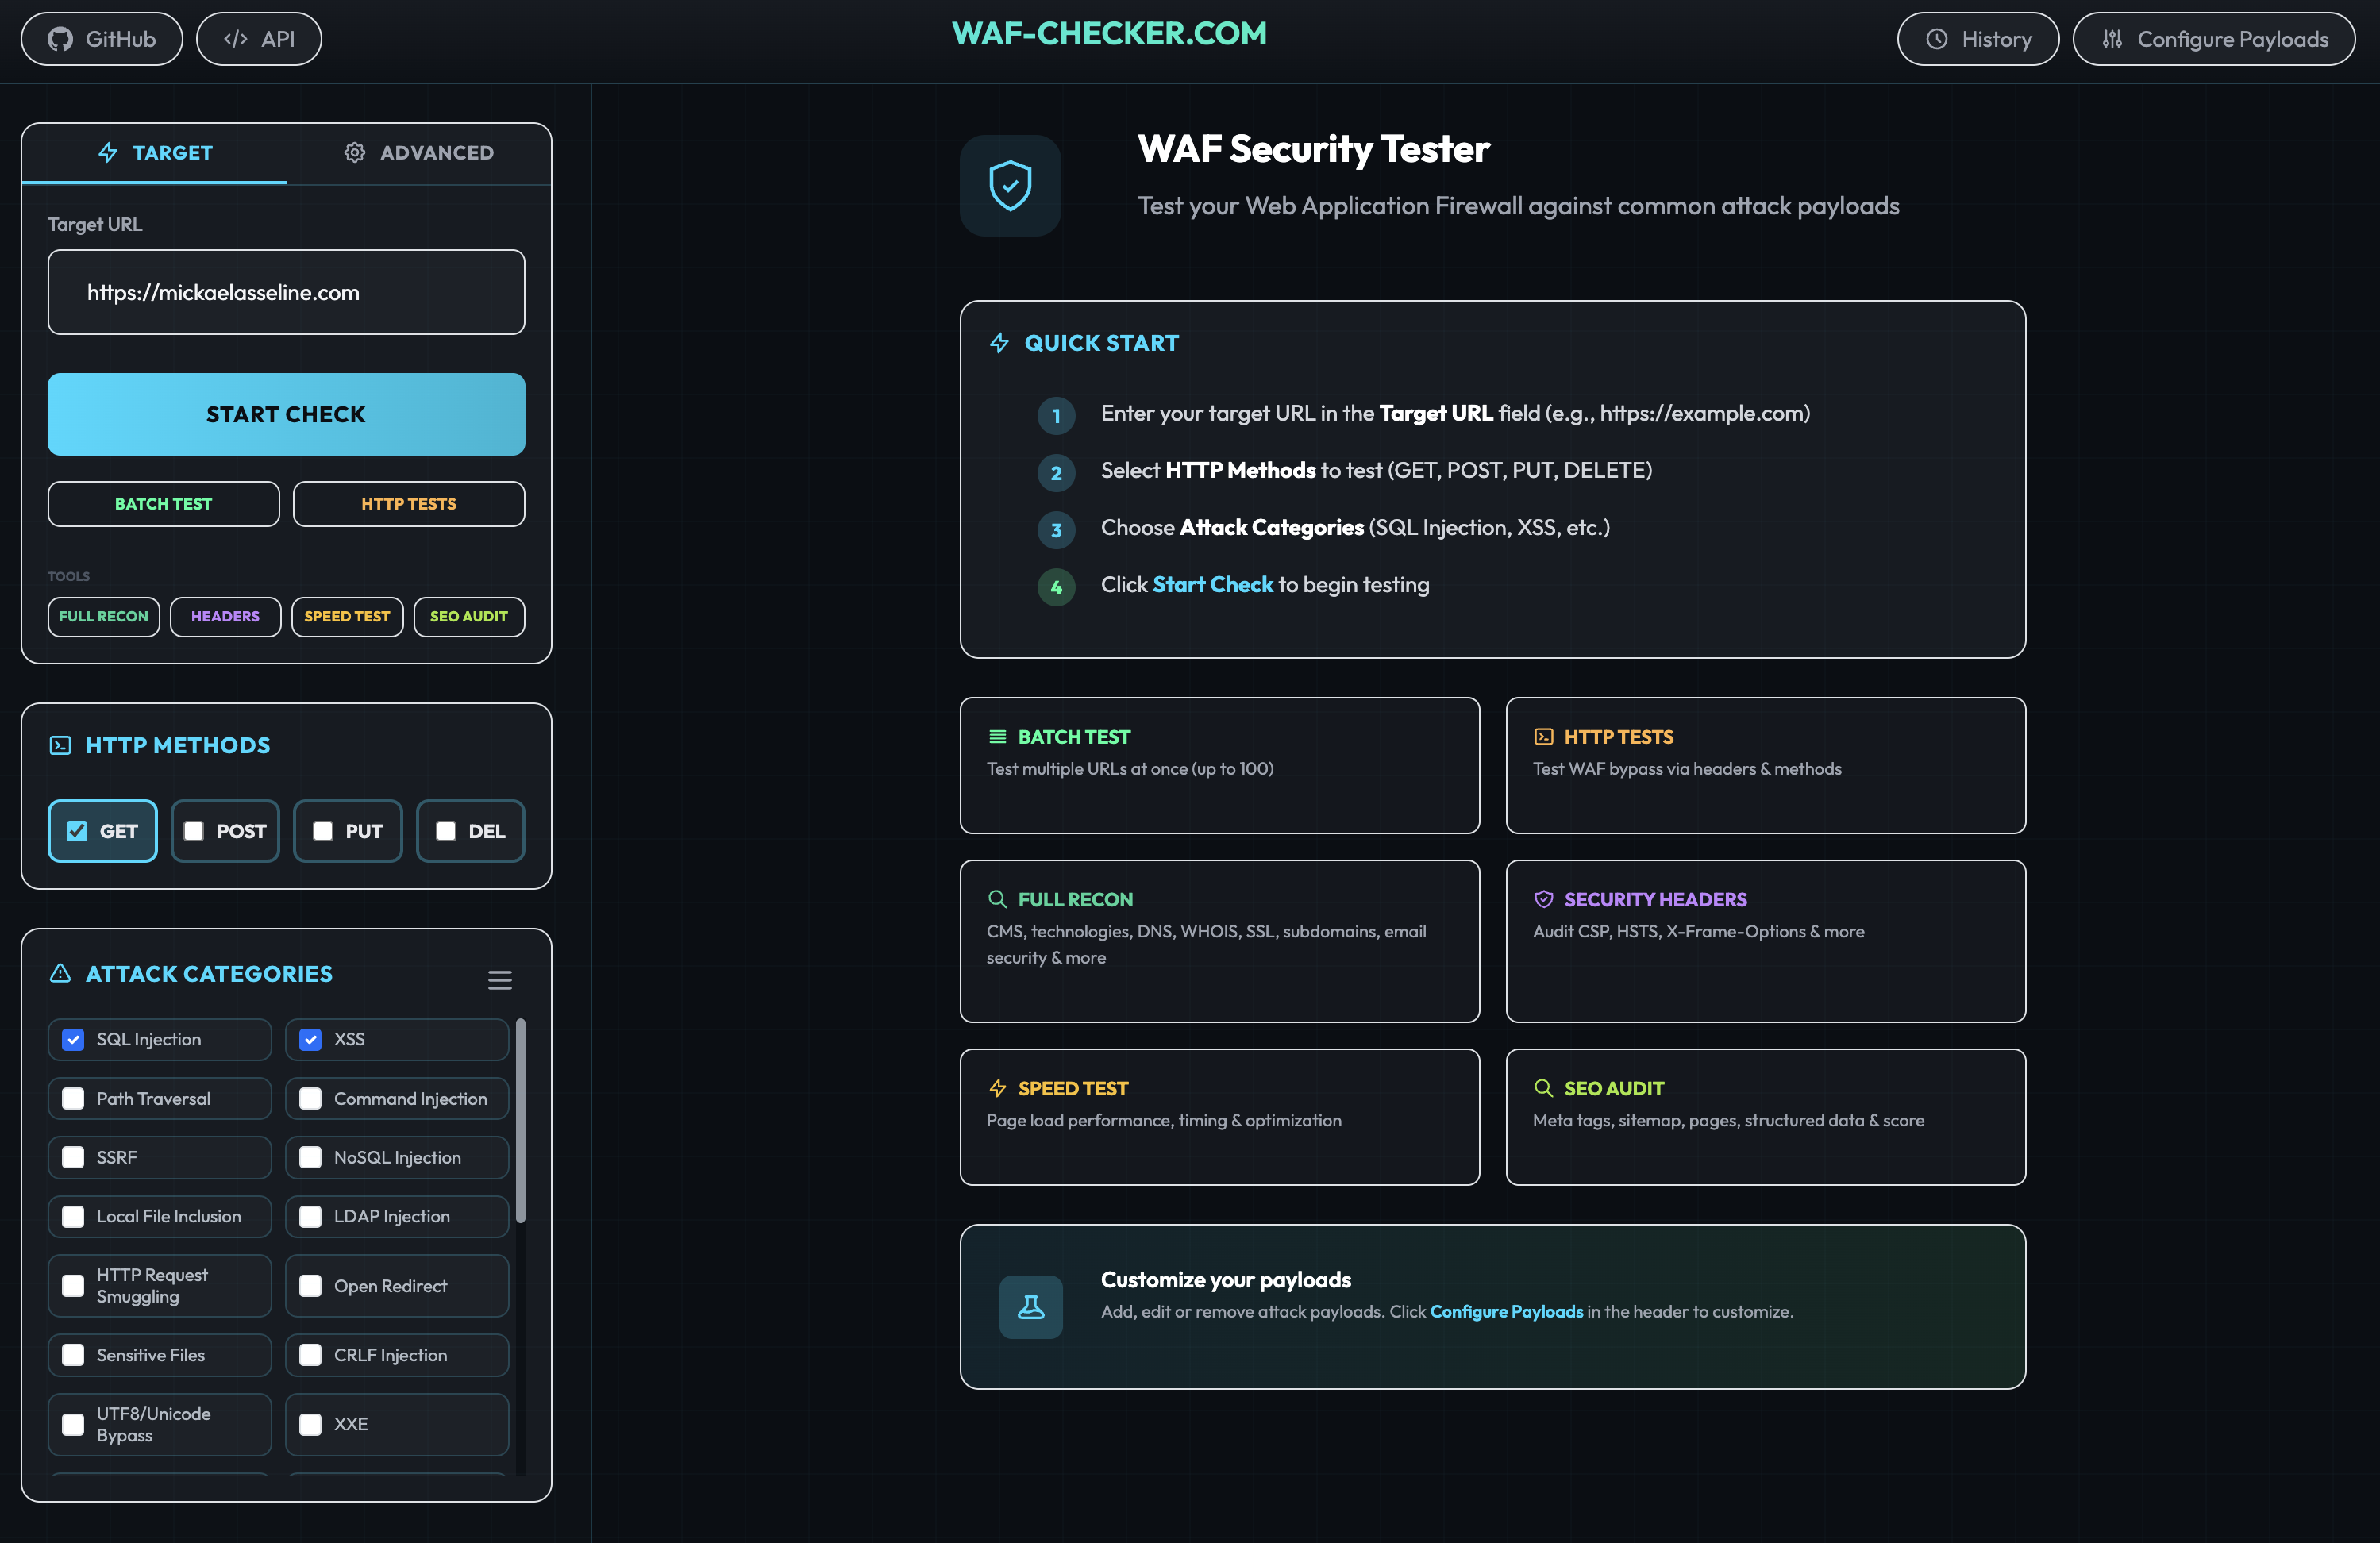
A powerful web application to test how well your Web Application Firewall (WAF) protects against common attack vectors.
→ waf-checker.com ←
Features
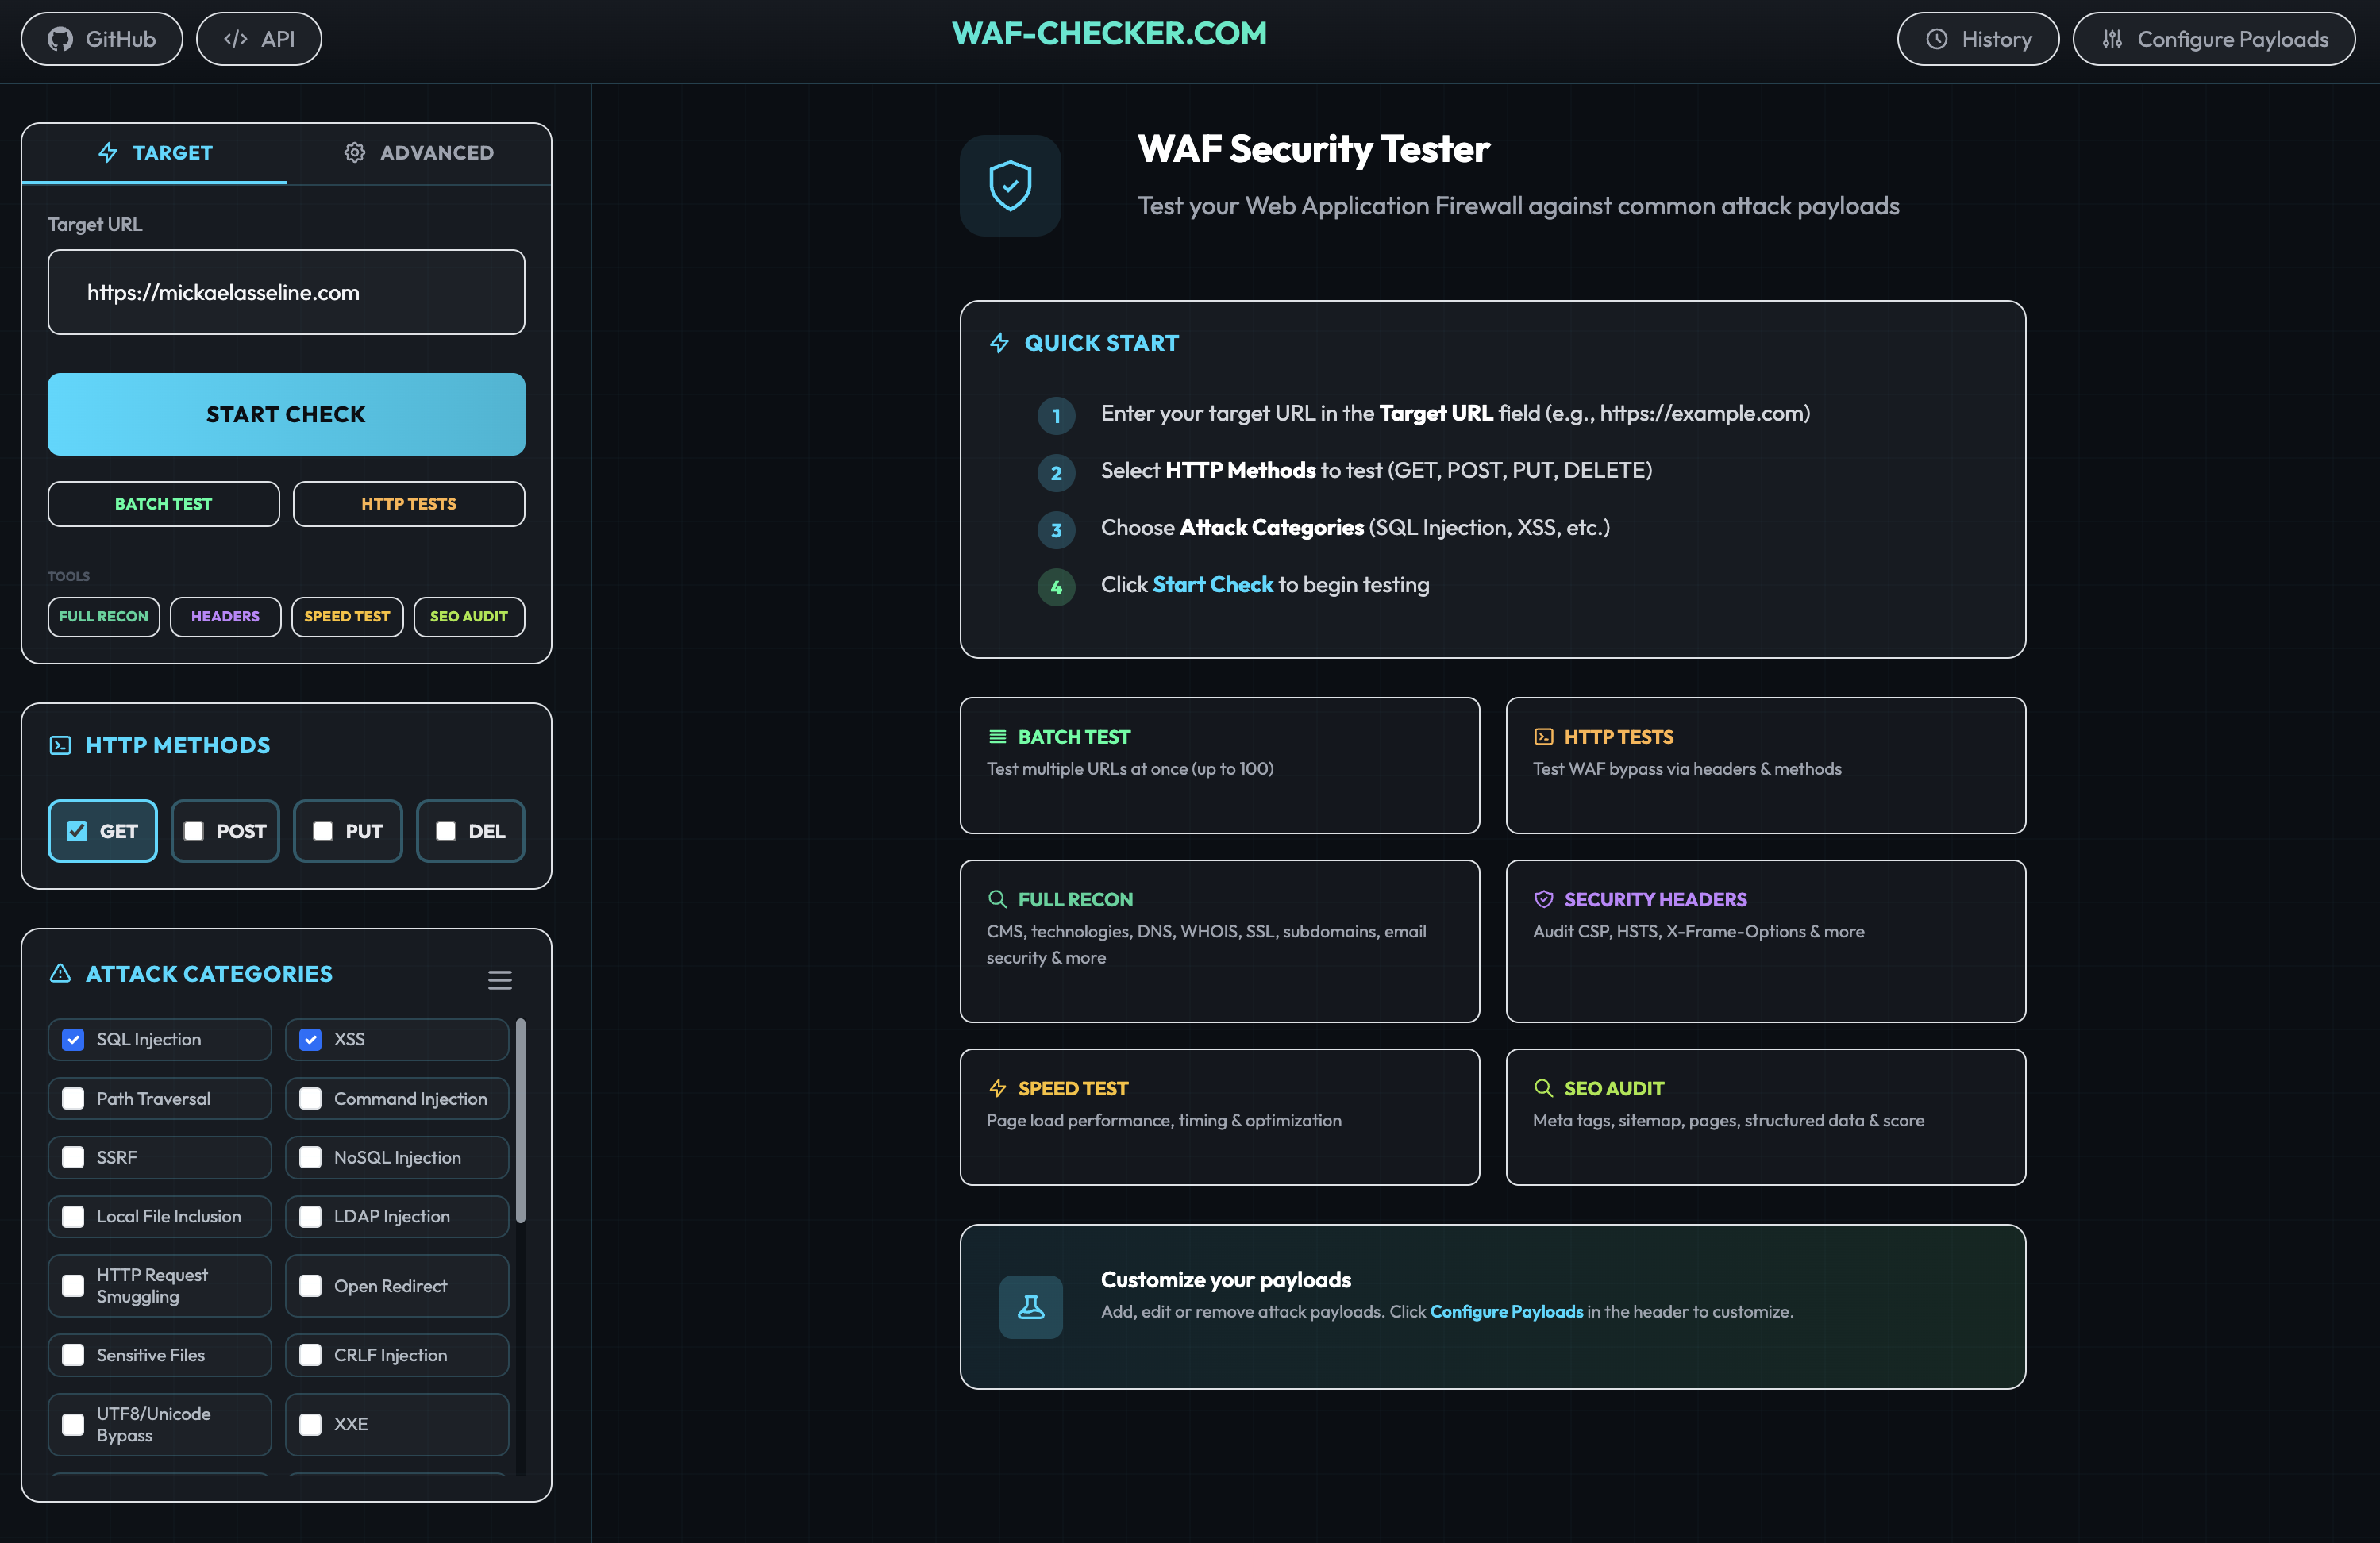
Security Testing
- 19+ attack categories out of the box: SQL Injection, XSS, Path Traversal, Command Injection, SSRF, NoSQL Injection, LFI, LDAP Injection, XXE, SSTI, CRLF, and more
- 9 advanced bypass categories with encoding variations, protocol smuggling, and framework-specific payloads
- 344+ payloads loaded dynamically from PAPAMICA/waf-payloads
- False positive testing to verify legitimate traffic isn't being blocked
- HTTP method testing across GET, POST, PUT, and DELETE
WAF Detection & Bypass
- Auto WAF detection — identifies Cloudflare, AWS WAF, Imperva, ModSecurity, Akamai, F5 BIG-IP, and 15+ other WAFs
- Advanced bypass techniques — double encoding, unicode, mixed case, comment obfuscation
- WAF-specific bypass generation — tailored strategies per detected WAF
- HTTP manipulation testing — verb tampering, parameter pollution, content-type confusion, request smuggling
Full Reconnaissance
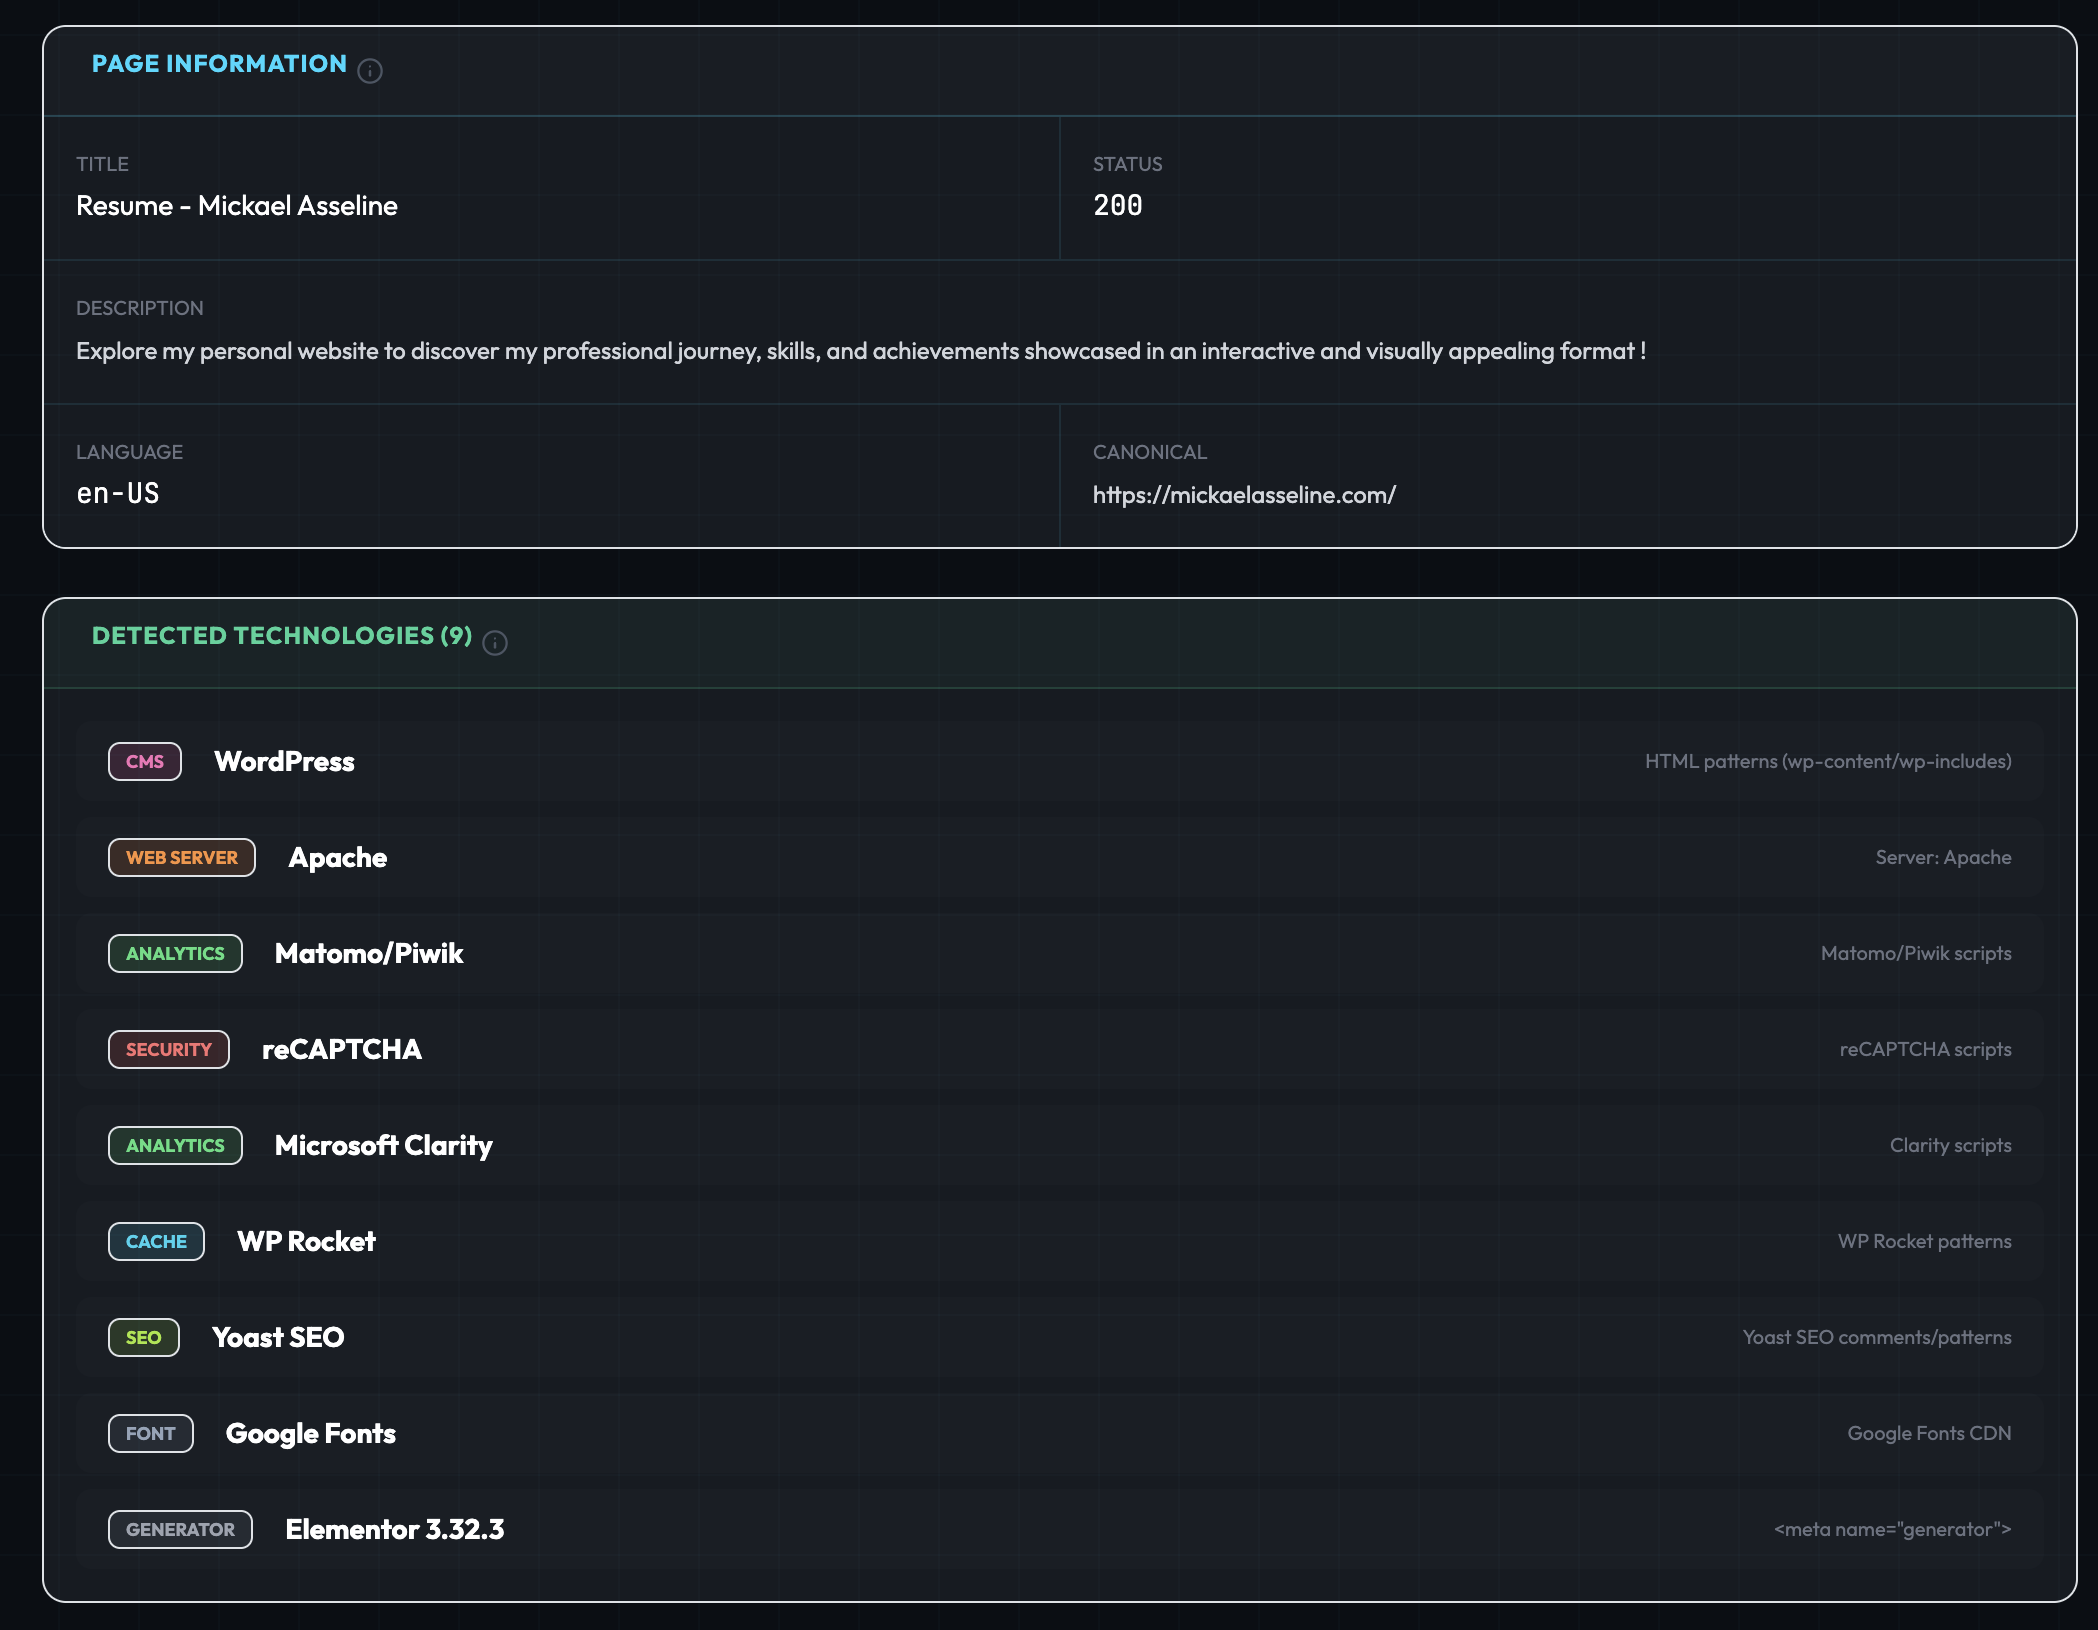
- Technology fingerprinting — CMS detection (WordPress, Drupal, Joomla, Shopify…), frameworks, web servers, CDN/WAF, analytics tools, and 25+ JavaScript libraries
- DNS analysis — A, AAAA, CNAME, MX, NS, TXT, SOA records with infrastructure detection
- WHOIS & IP geolocation — ISP, organization, ASN, location, reverse DNS (PTR)
- Subdomain discovery — via Certificate Transparency logs (crt.sh) and DNS brute-force
- Reverse IP lookup — discover all domains hosted on the same IP (shared hosting detection)
- SSL/TLS certificate details — issuer, validity, Subject Alternative Names (SANs), serial number
- CMS deep analysis — WordPress themes, plugins with versions; Drupal modules
- Path probing — robots.txt, sitemap.xml, security.txt, common admin paths
- Cookie analysis — Secure, HttpOnly, SameSite flags
- Open Graph & social metadata extraction
- RSS/Atom feeds & email address discovery
- Export results as JSON, HTML report, or screenshot (PNG)
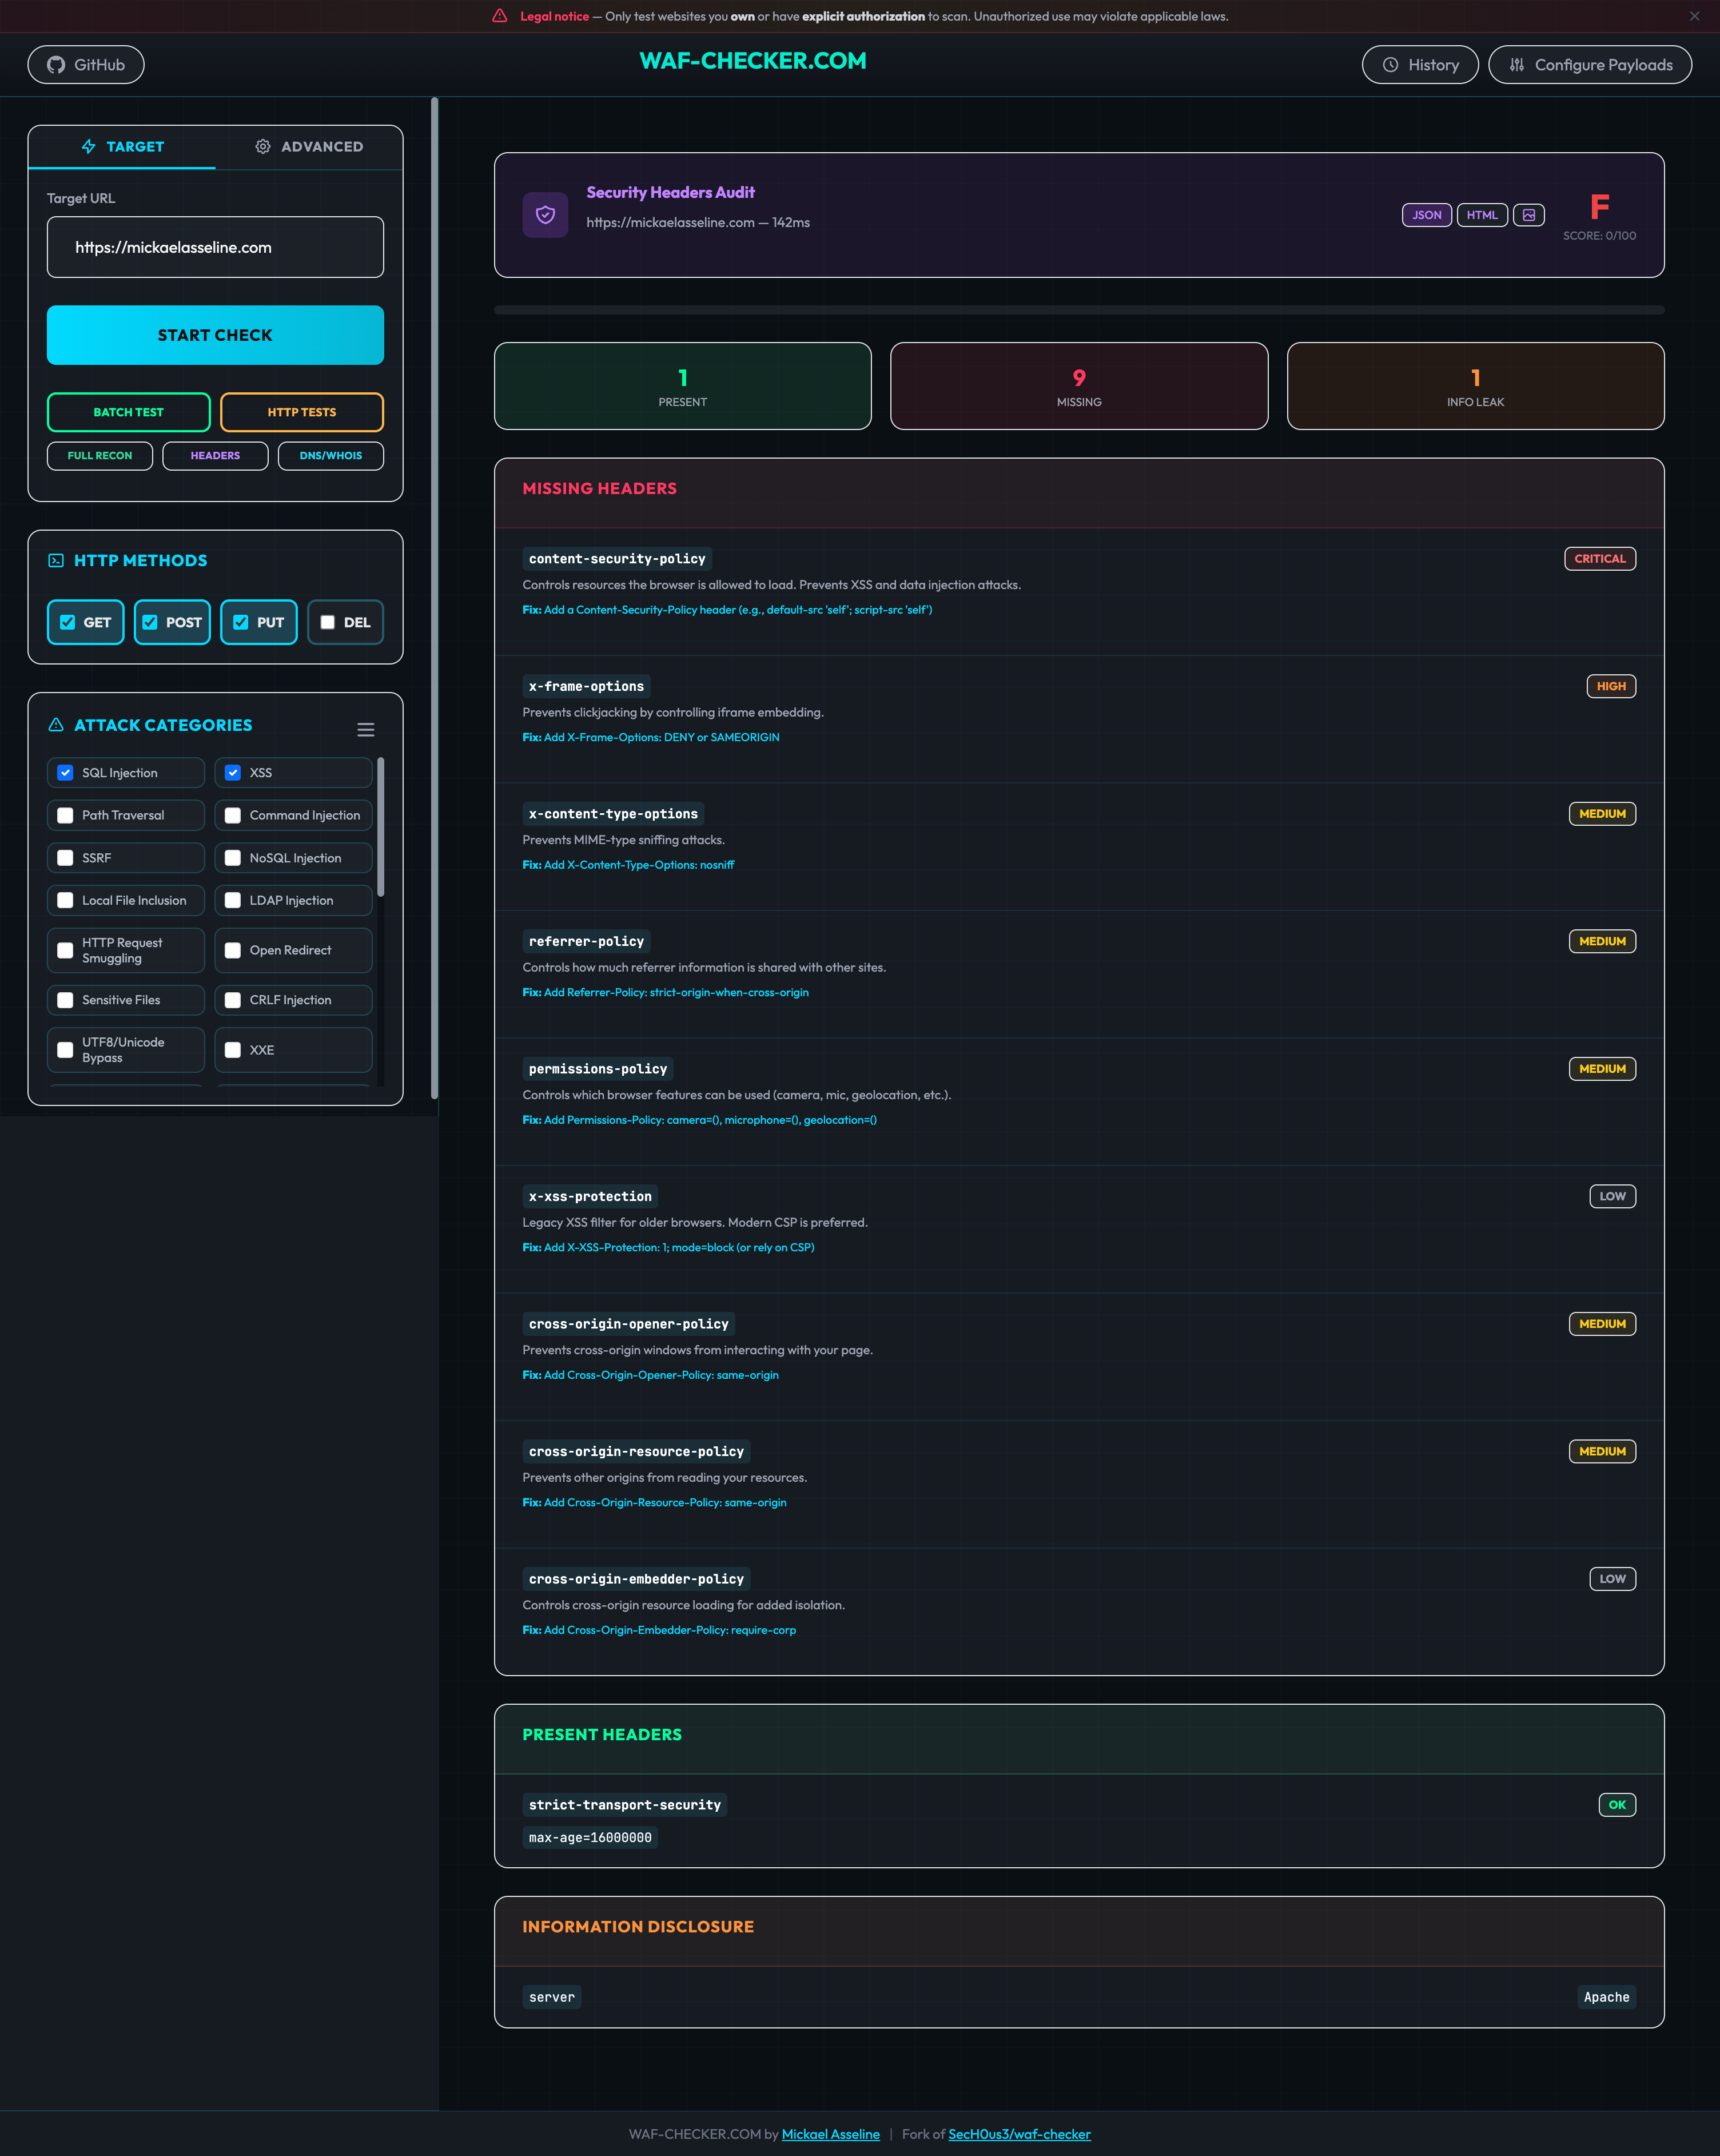
- Grade scoring (A+ to F) of HTTP security headers
- Detailed analysis of CSP, HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy
- Information disclosure detection — server version, powered-by headers, debug headers
- Actionable recommendations for each missing or misconfigured header
- Export results as JSON, HTML report, or screenshot (PNG)
Speed Test
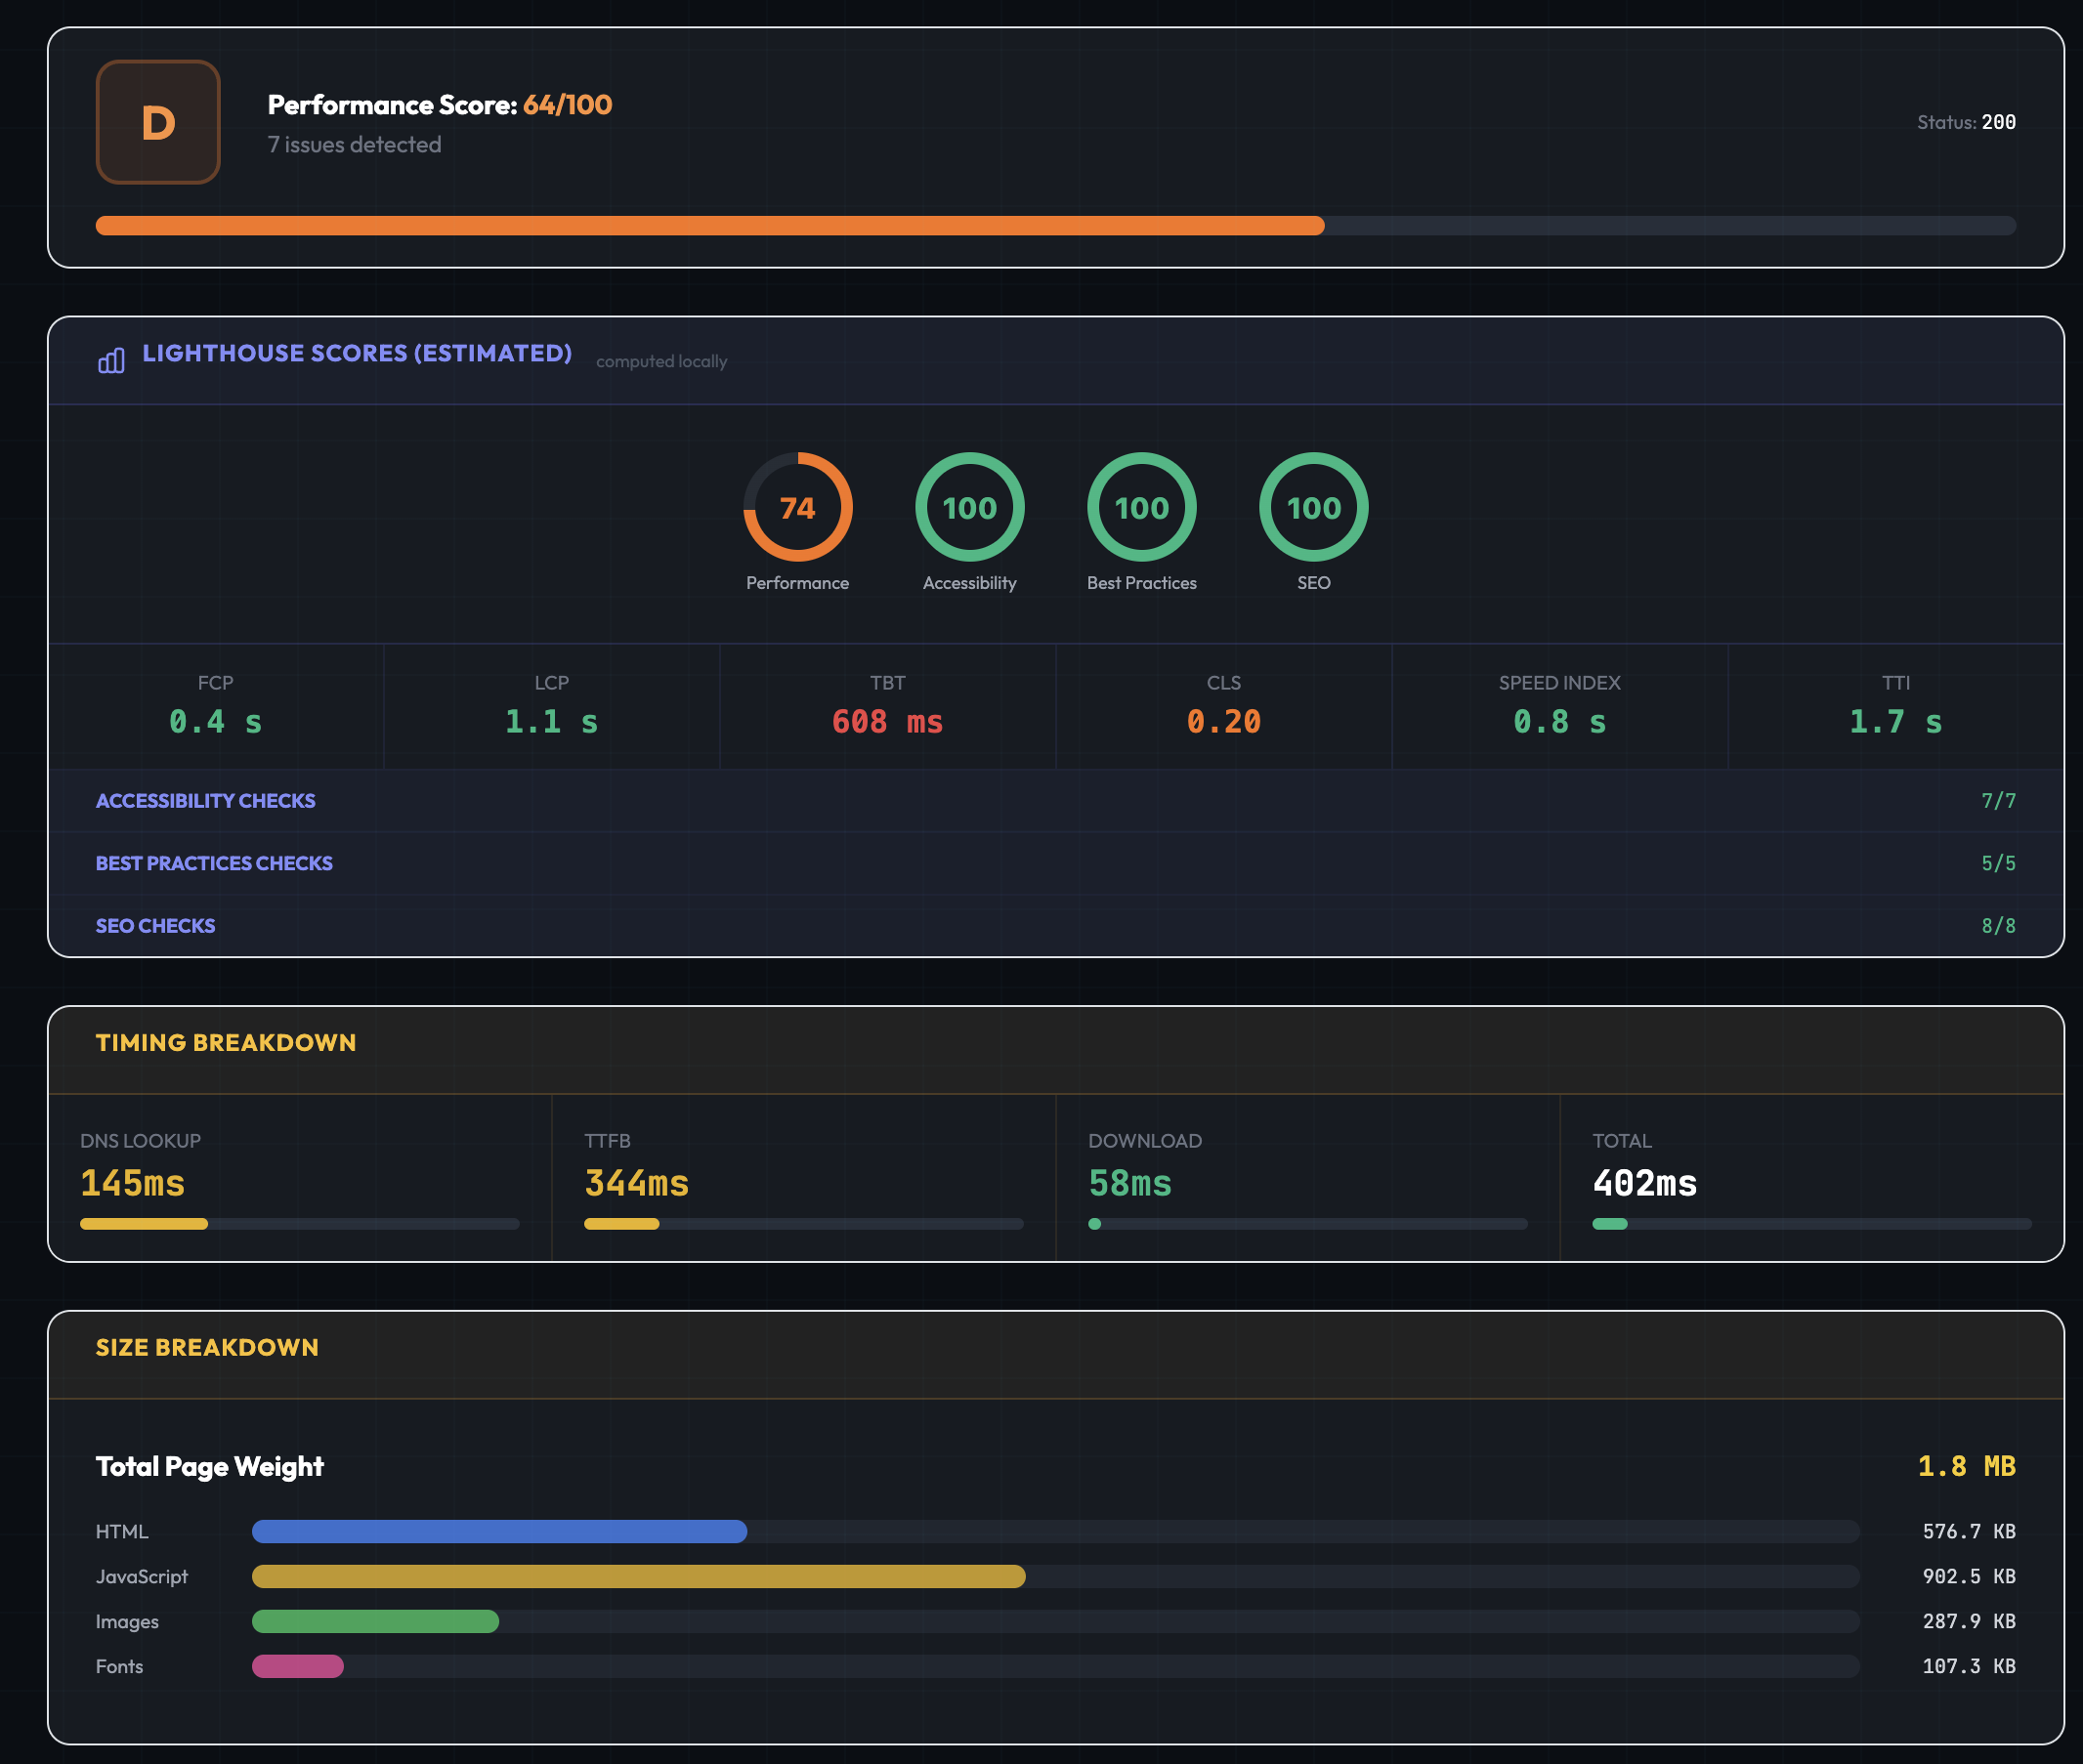
- Performance score (0–100) with issues count and status
- Lighthouse-style scores (estimated locally) — Performance, Accessibility, Best Practices, SEO
- Core Web Vitals — FCP, LCP, TBT, CLS, Speed Index, TTI with color-coded feedback
- Timing breakdown — DNS lookup, TTFB, download, total load time
- Size breakdown — total page weight and per-type (HTML, JavaScript, images, fonts)
- Optimization advice and penalty/improvement hints
- Export results as JSON, HTML report, or screenshot (PNG)
DNS / WHOIS Intelligence
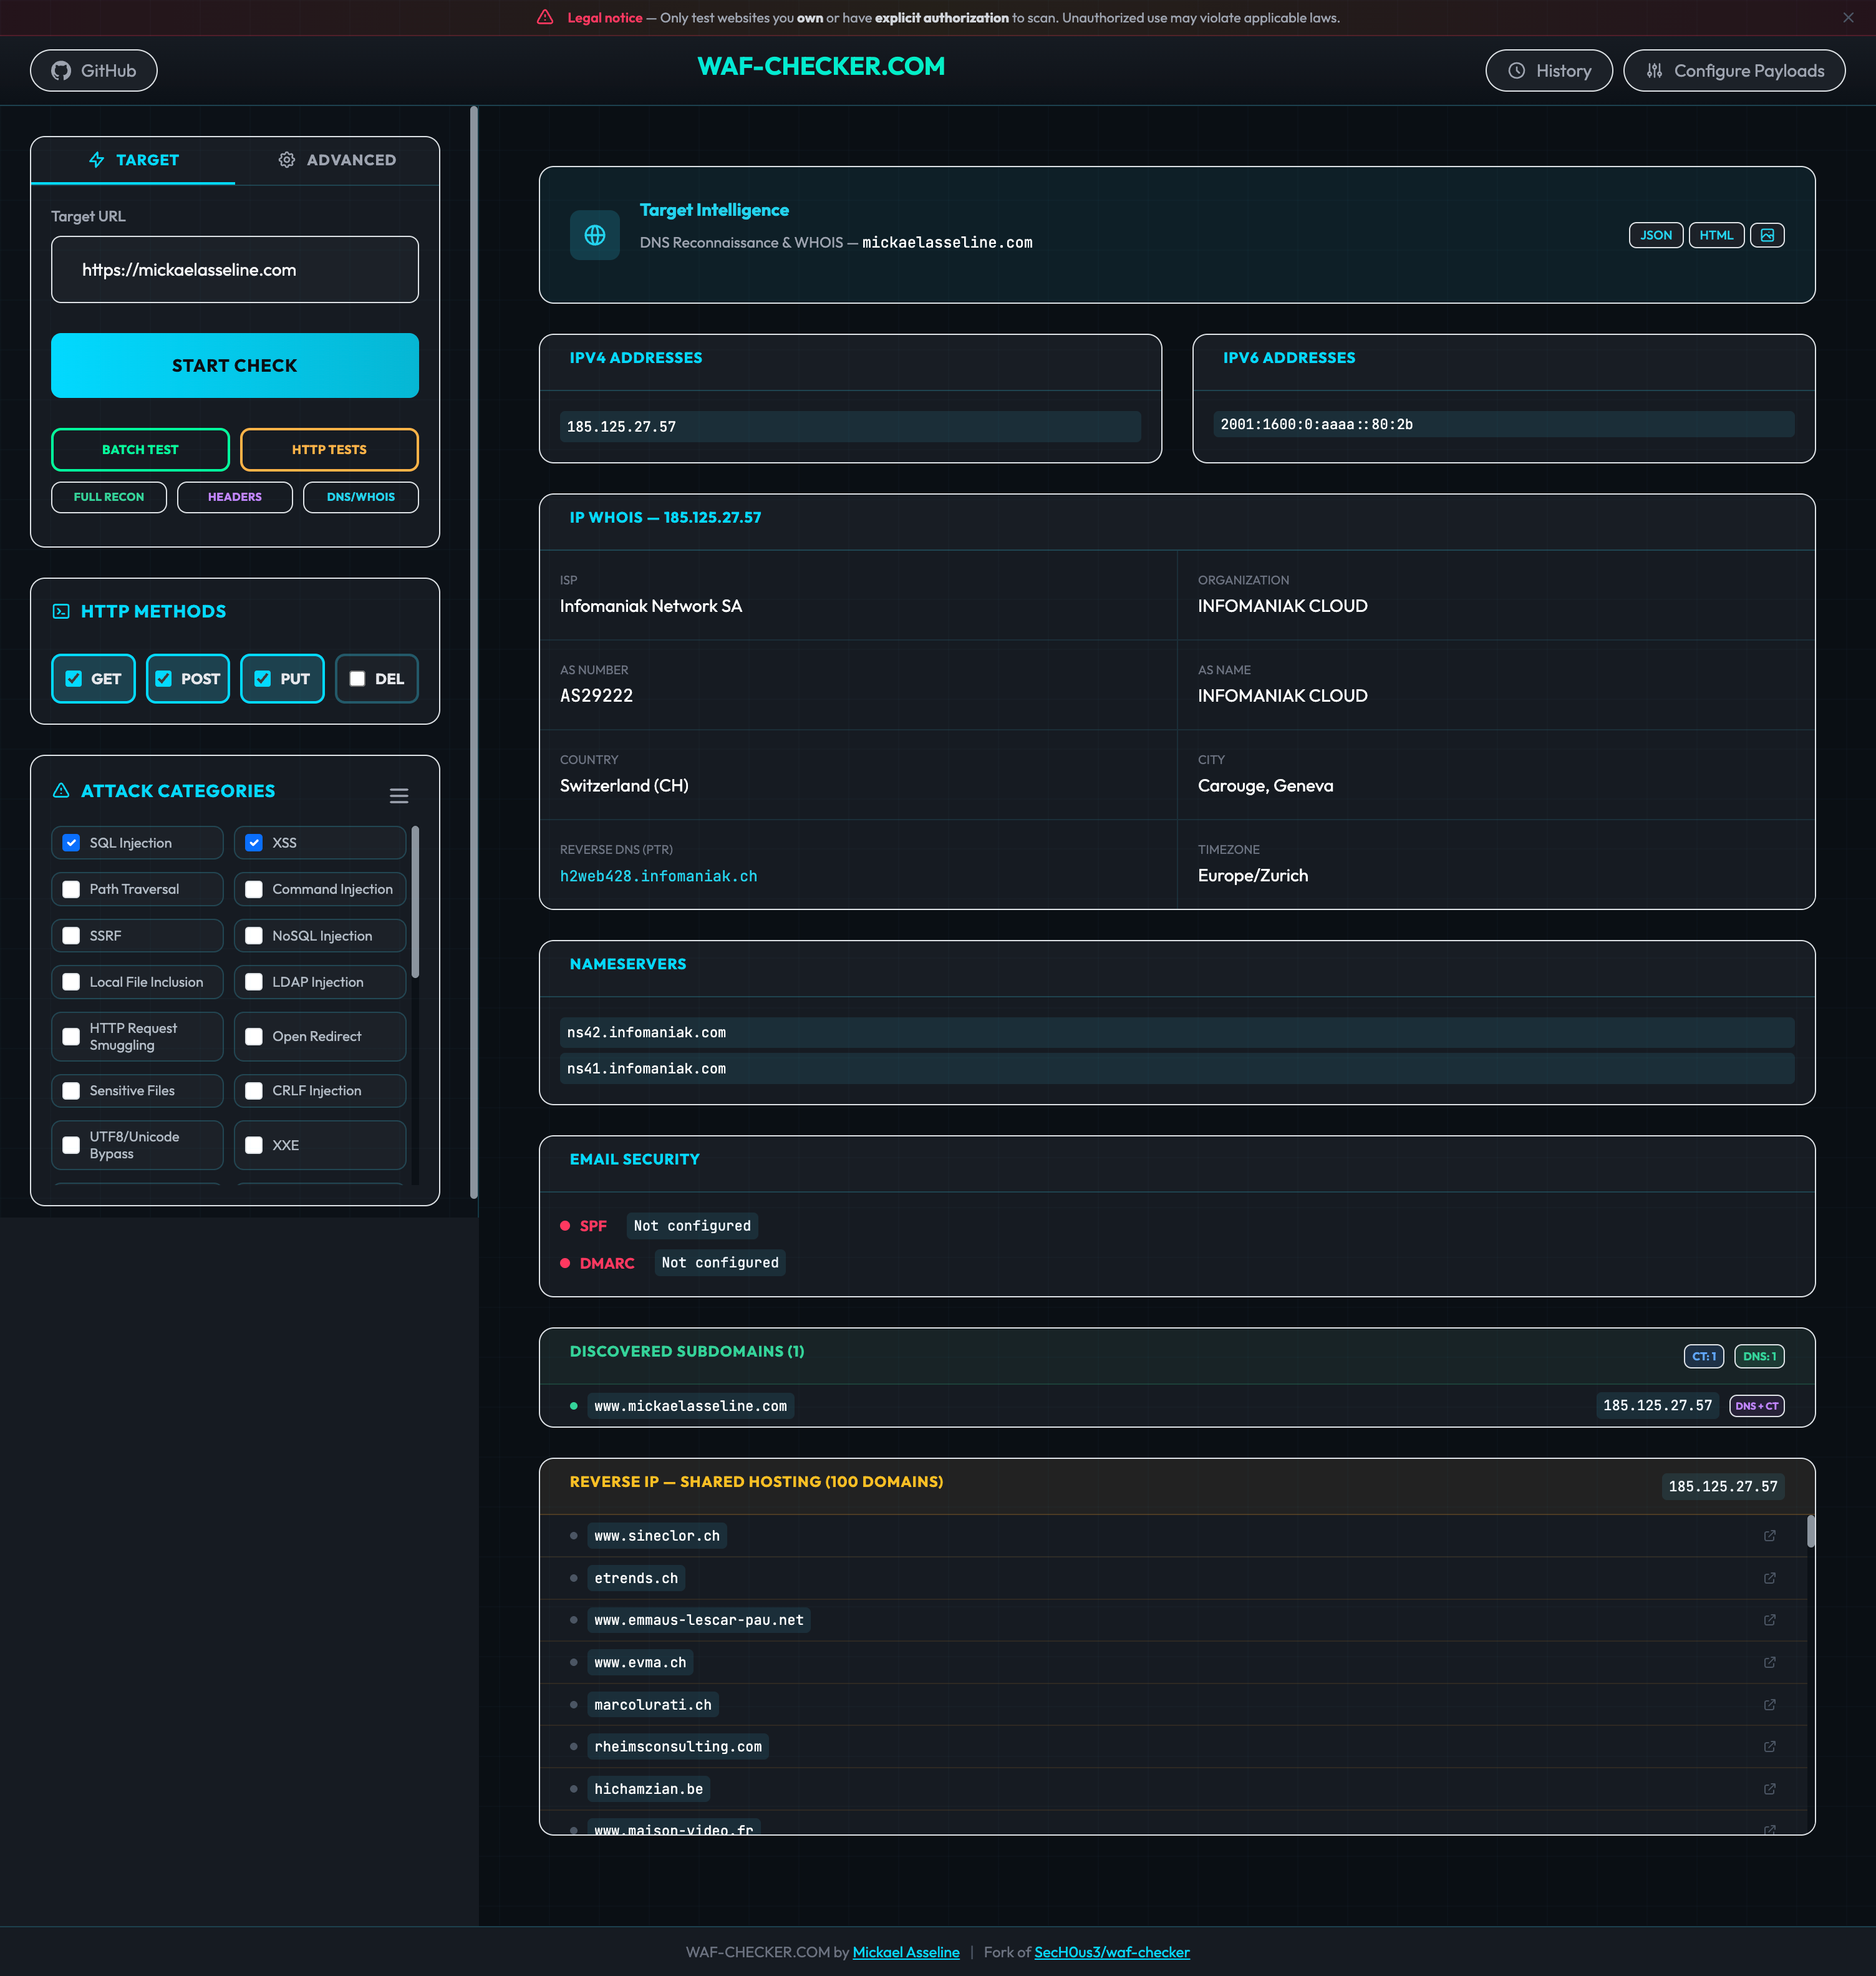
- Complete DNS resolution — A, AAAA, CNAME, MX, NS, TXT records
- WHOIS data with IP geolocation, ISP, ASN, and reverse DNS
- Email security audit — SPF & DMARC validation
- Subdomain enumeration — Certificate Transparency + DNS brute-force
- Reverse IP lookup — all domains sharing the same IP address
- Infrastructure detection — CDN, email, and DNS providers from record patterns
- Export results as JSON, HTML report, or screenshot (PNG)
SEO Audit
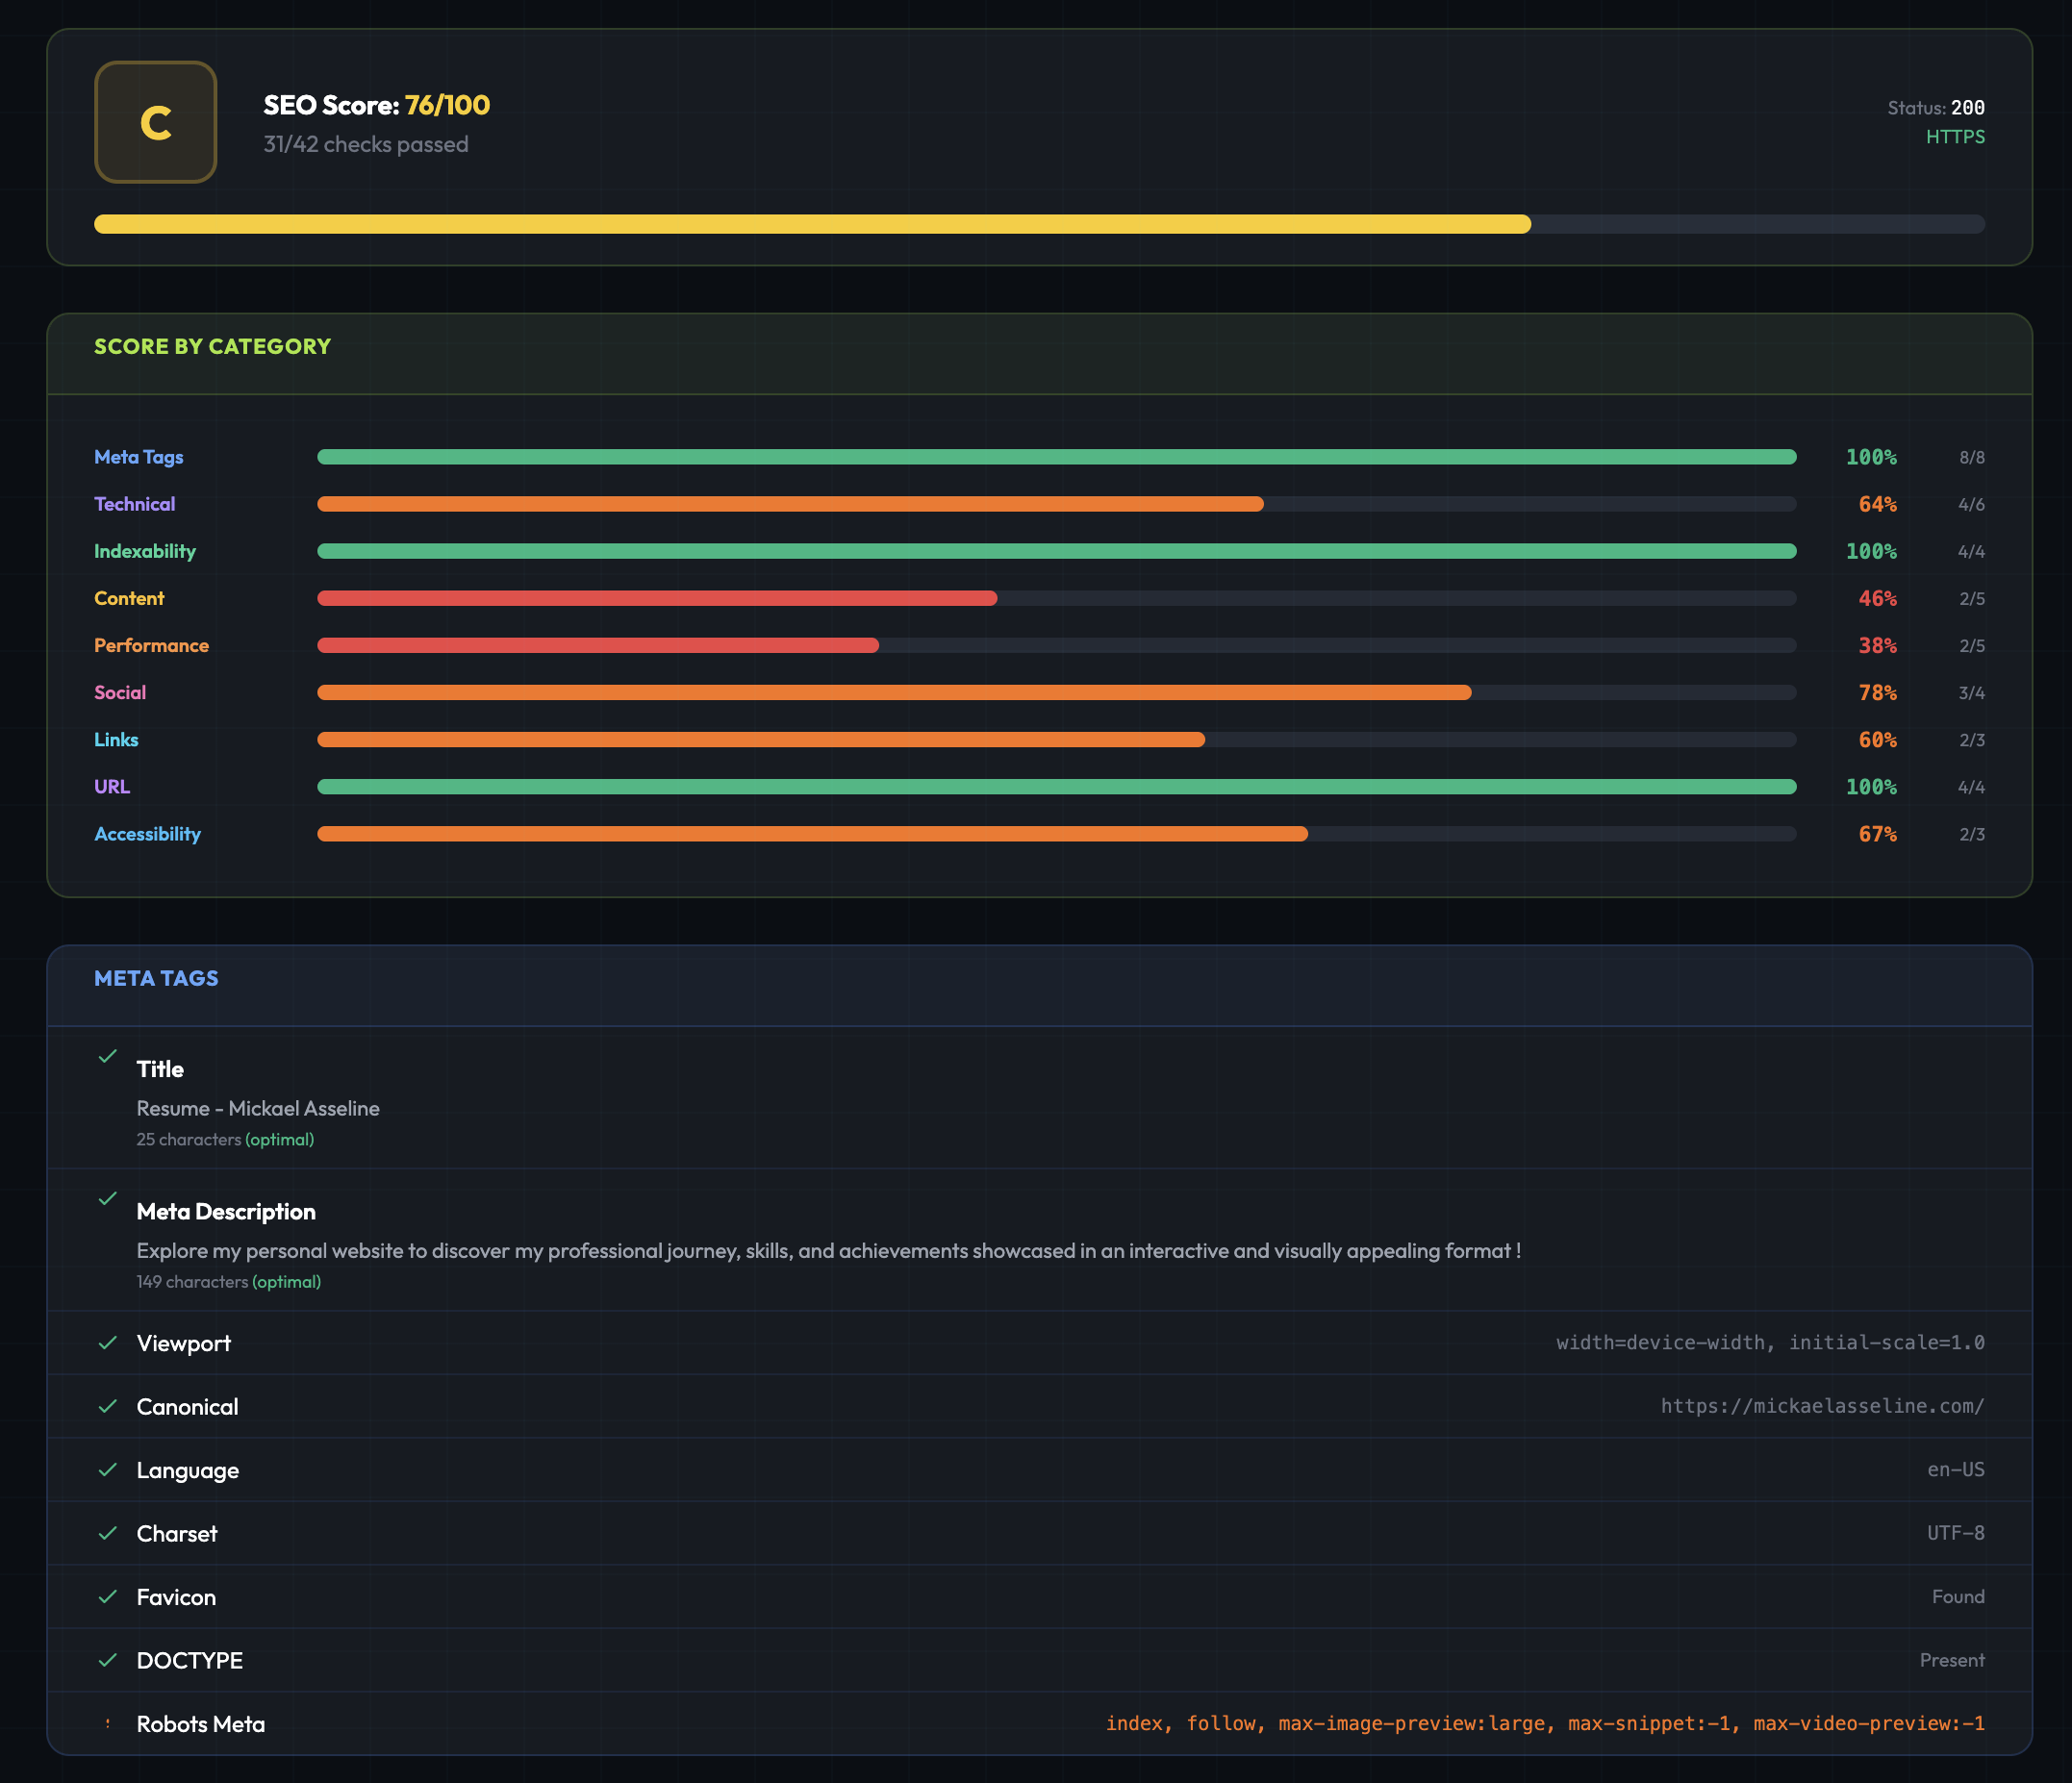
- Overall SEO score (0–100) with checks passed / total
- Score by category — Meta Tags, Technical, Indexability, Content, Performance, Social, Links, URL, Accessibility
- Meta tags verification — title, description, viewport, canonical, language, charset, favicon, DOCTYPE, robots
- Sitemap & robots.txt analysis, page discovery, structured data (JSON-LD)
- Content analysis — word count, readability, keyword density, text-to-HTML ratio
- Links audit — internal/external, nofollow, empty anchors
- Accessibility checks — lang, skip nav, ARIA landmarks, form labels
- Export results as JSON, HTML report, or screenshot (PNG)
Real-Time Results
- Streaming results via Server-Sent Events (SSE) — see results as they come in
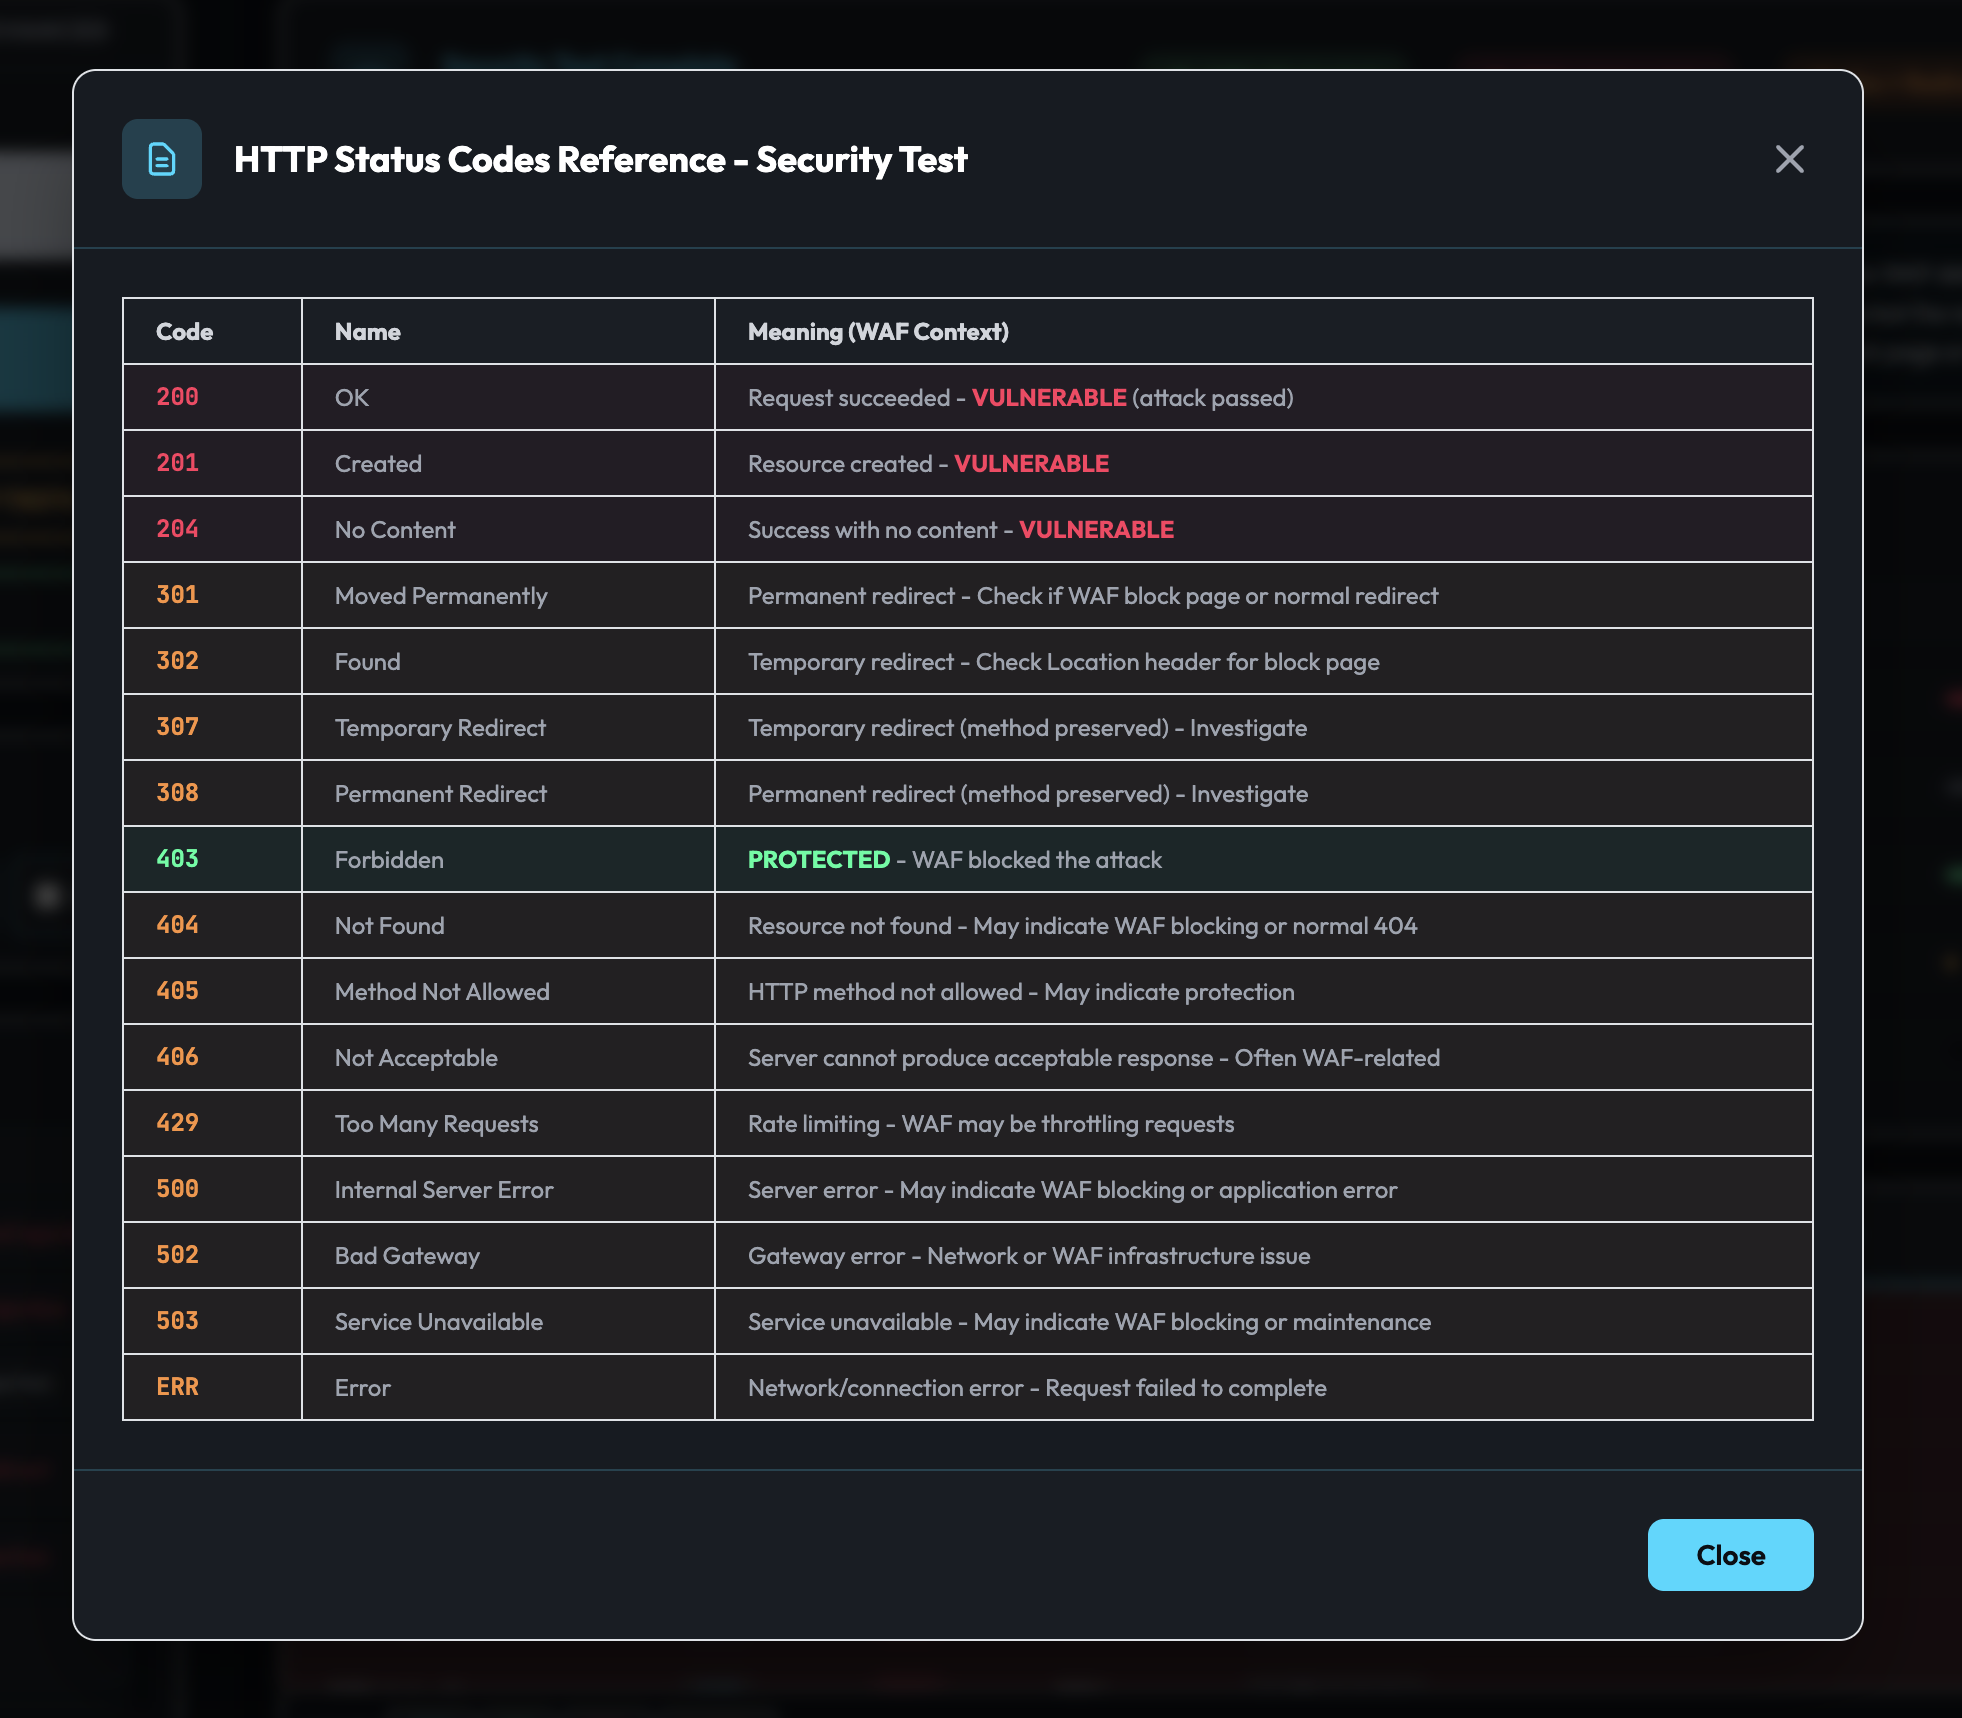
- Color-coded status codes:
403 green — WAF blocked the attack (protected)200 red — payload passed through (vulnerable)3xx orange — redirect (requires investigation)4xx yellow — other client error
- Filterable results by status code with real-time summary bars
HTTP Status Reference
Payload Configuration
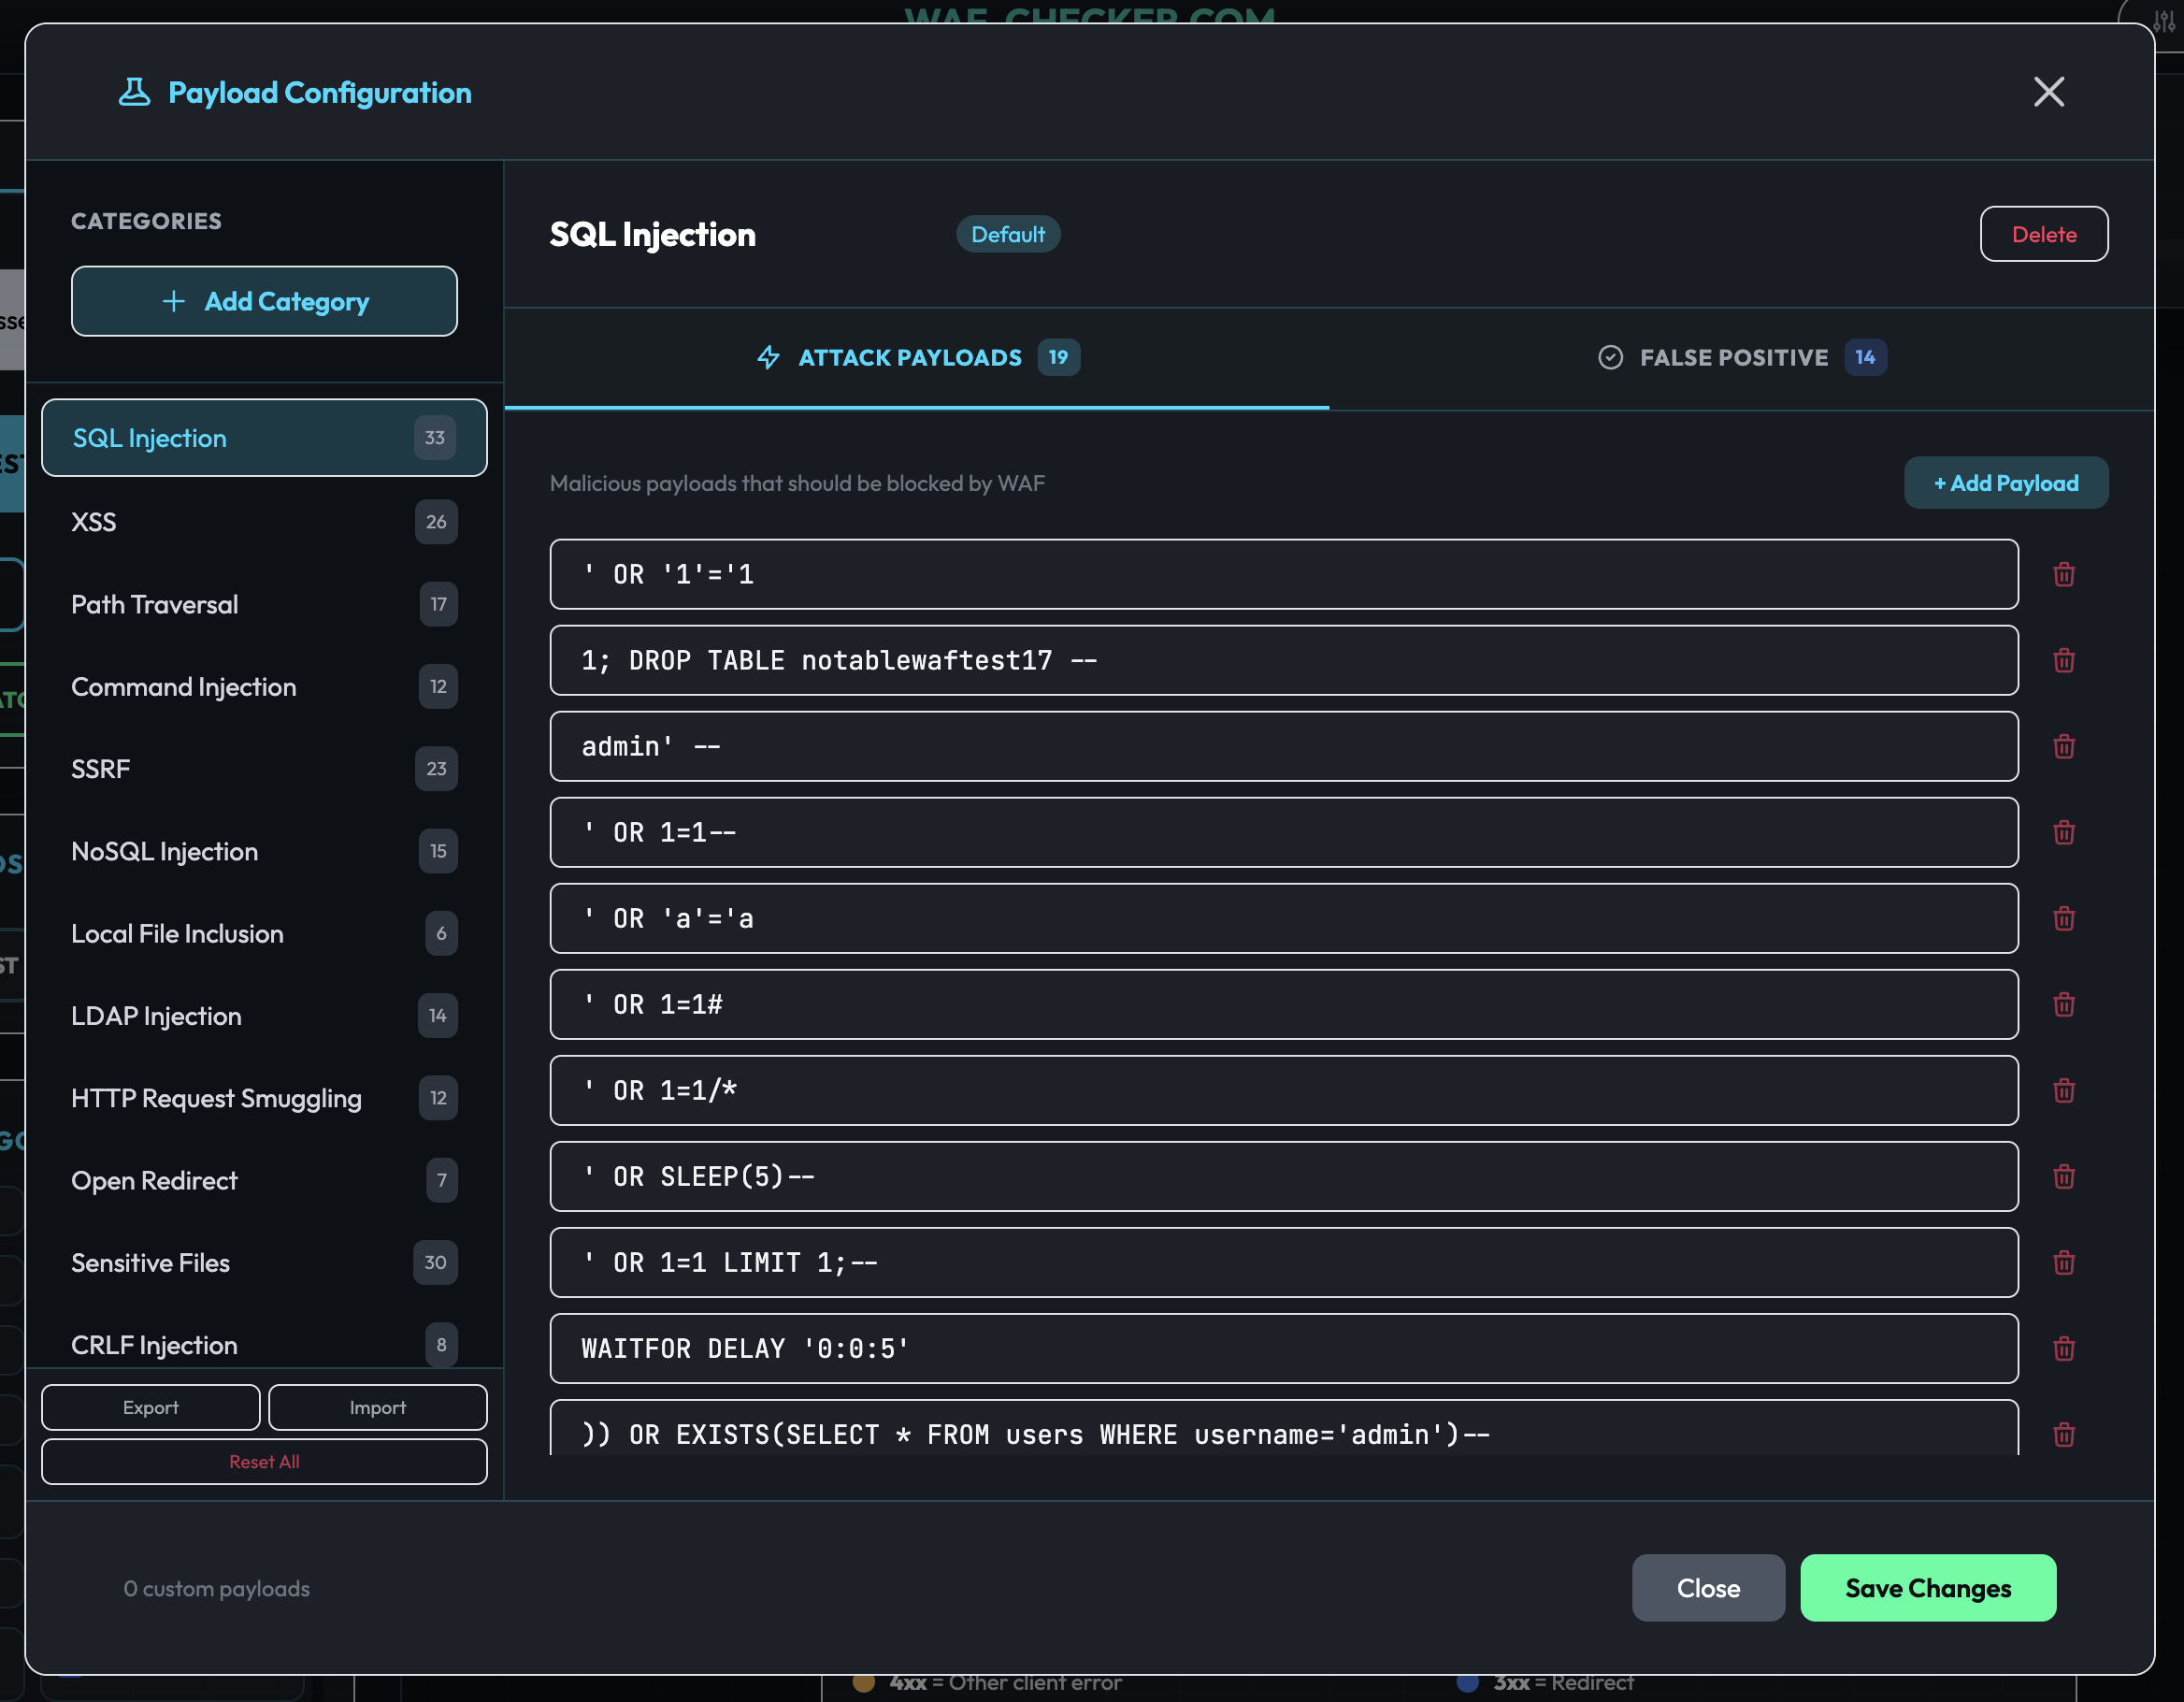
Fully customizable payload management through the built-in configuration panel:
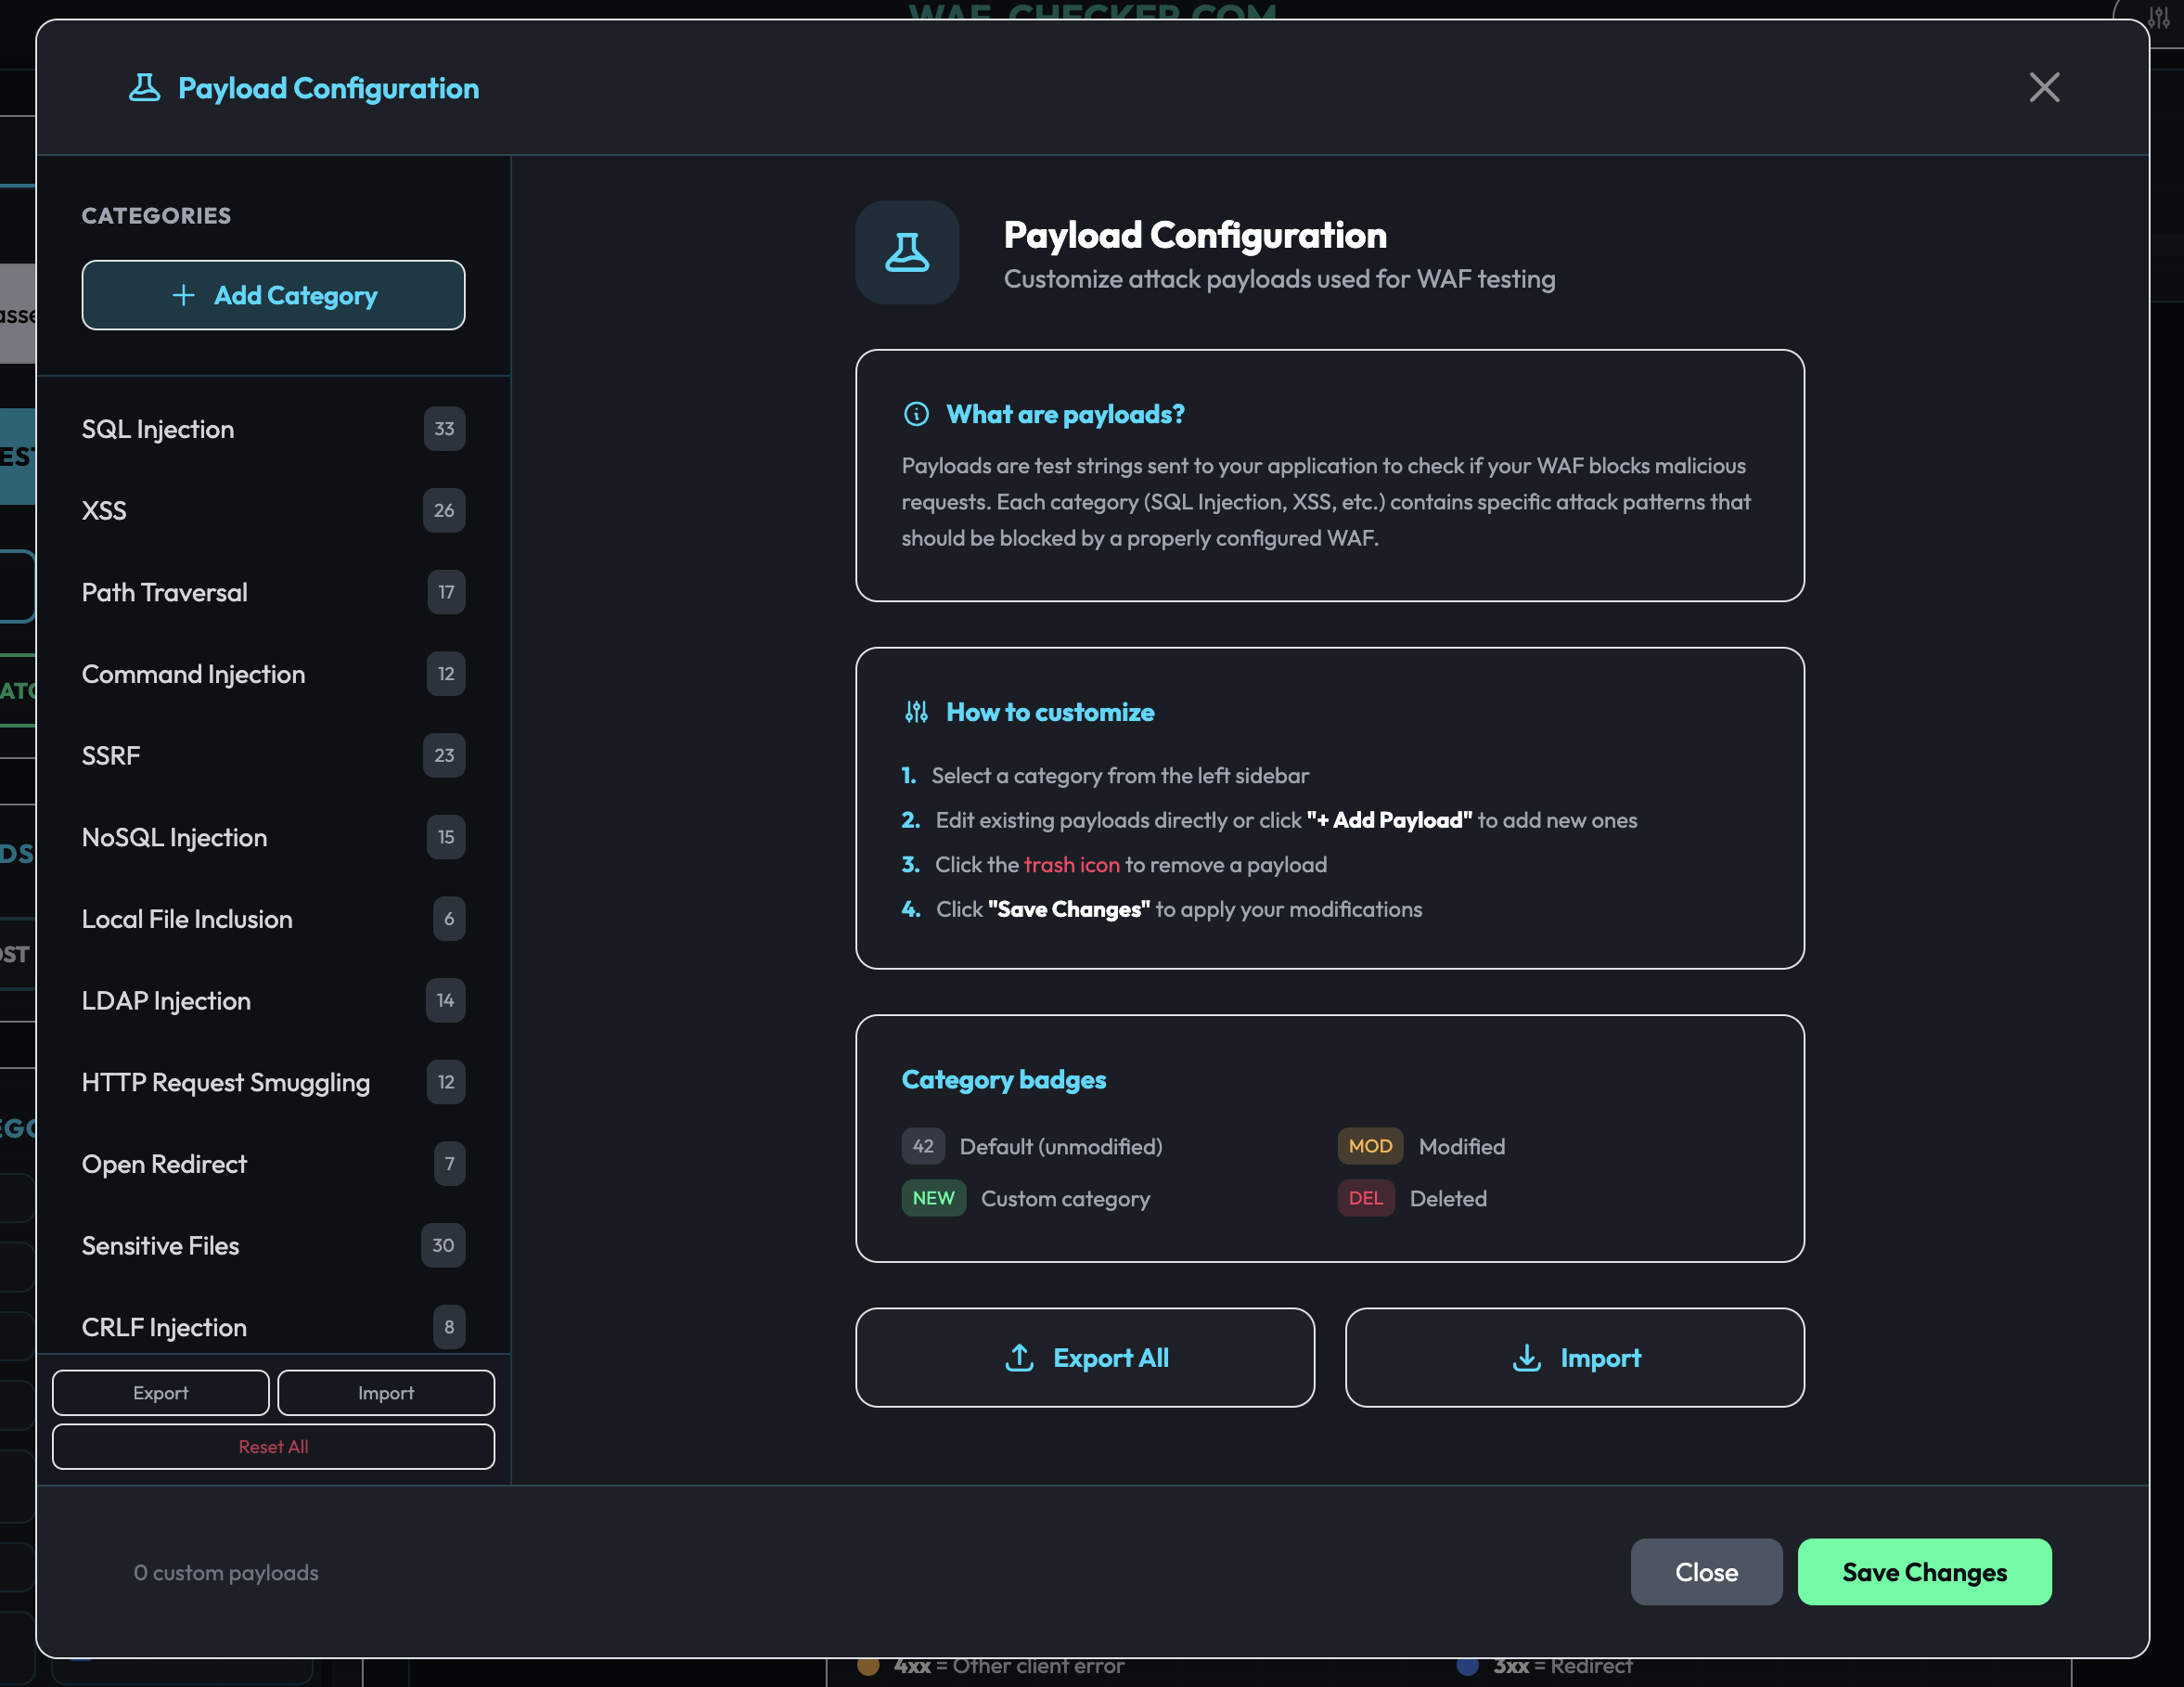
- Browse all categories with payload counts
- Add, edit, or remove individual payloads
- Create custom categories
- Separate attack payloads and false positive payloads per category
- Export/import payload configurations
- Changes persist in localStorage
Security Analytics
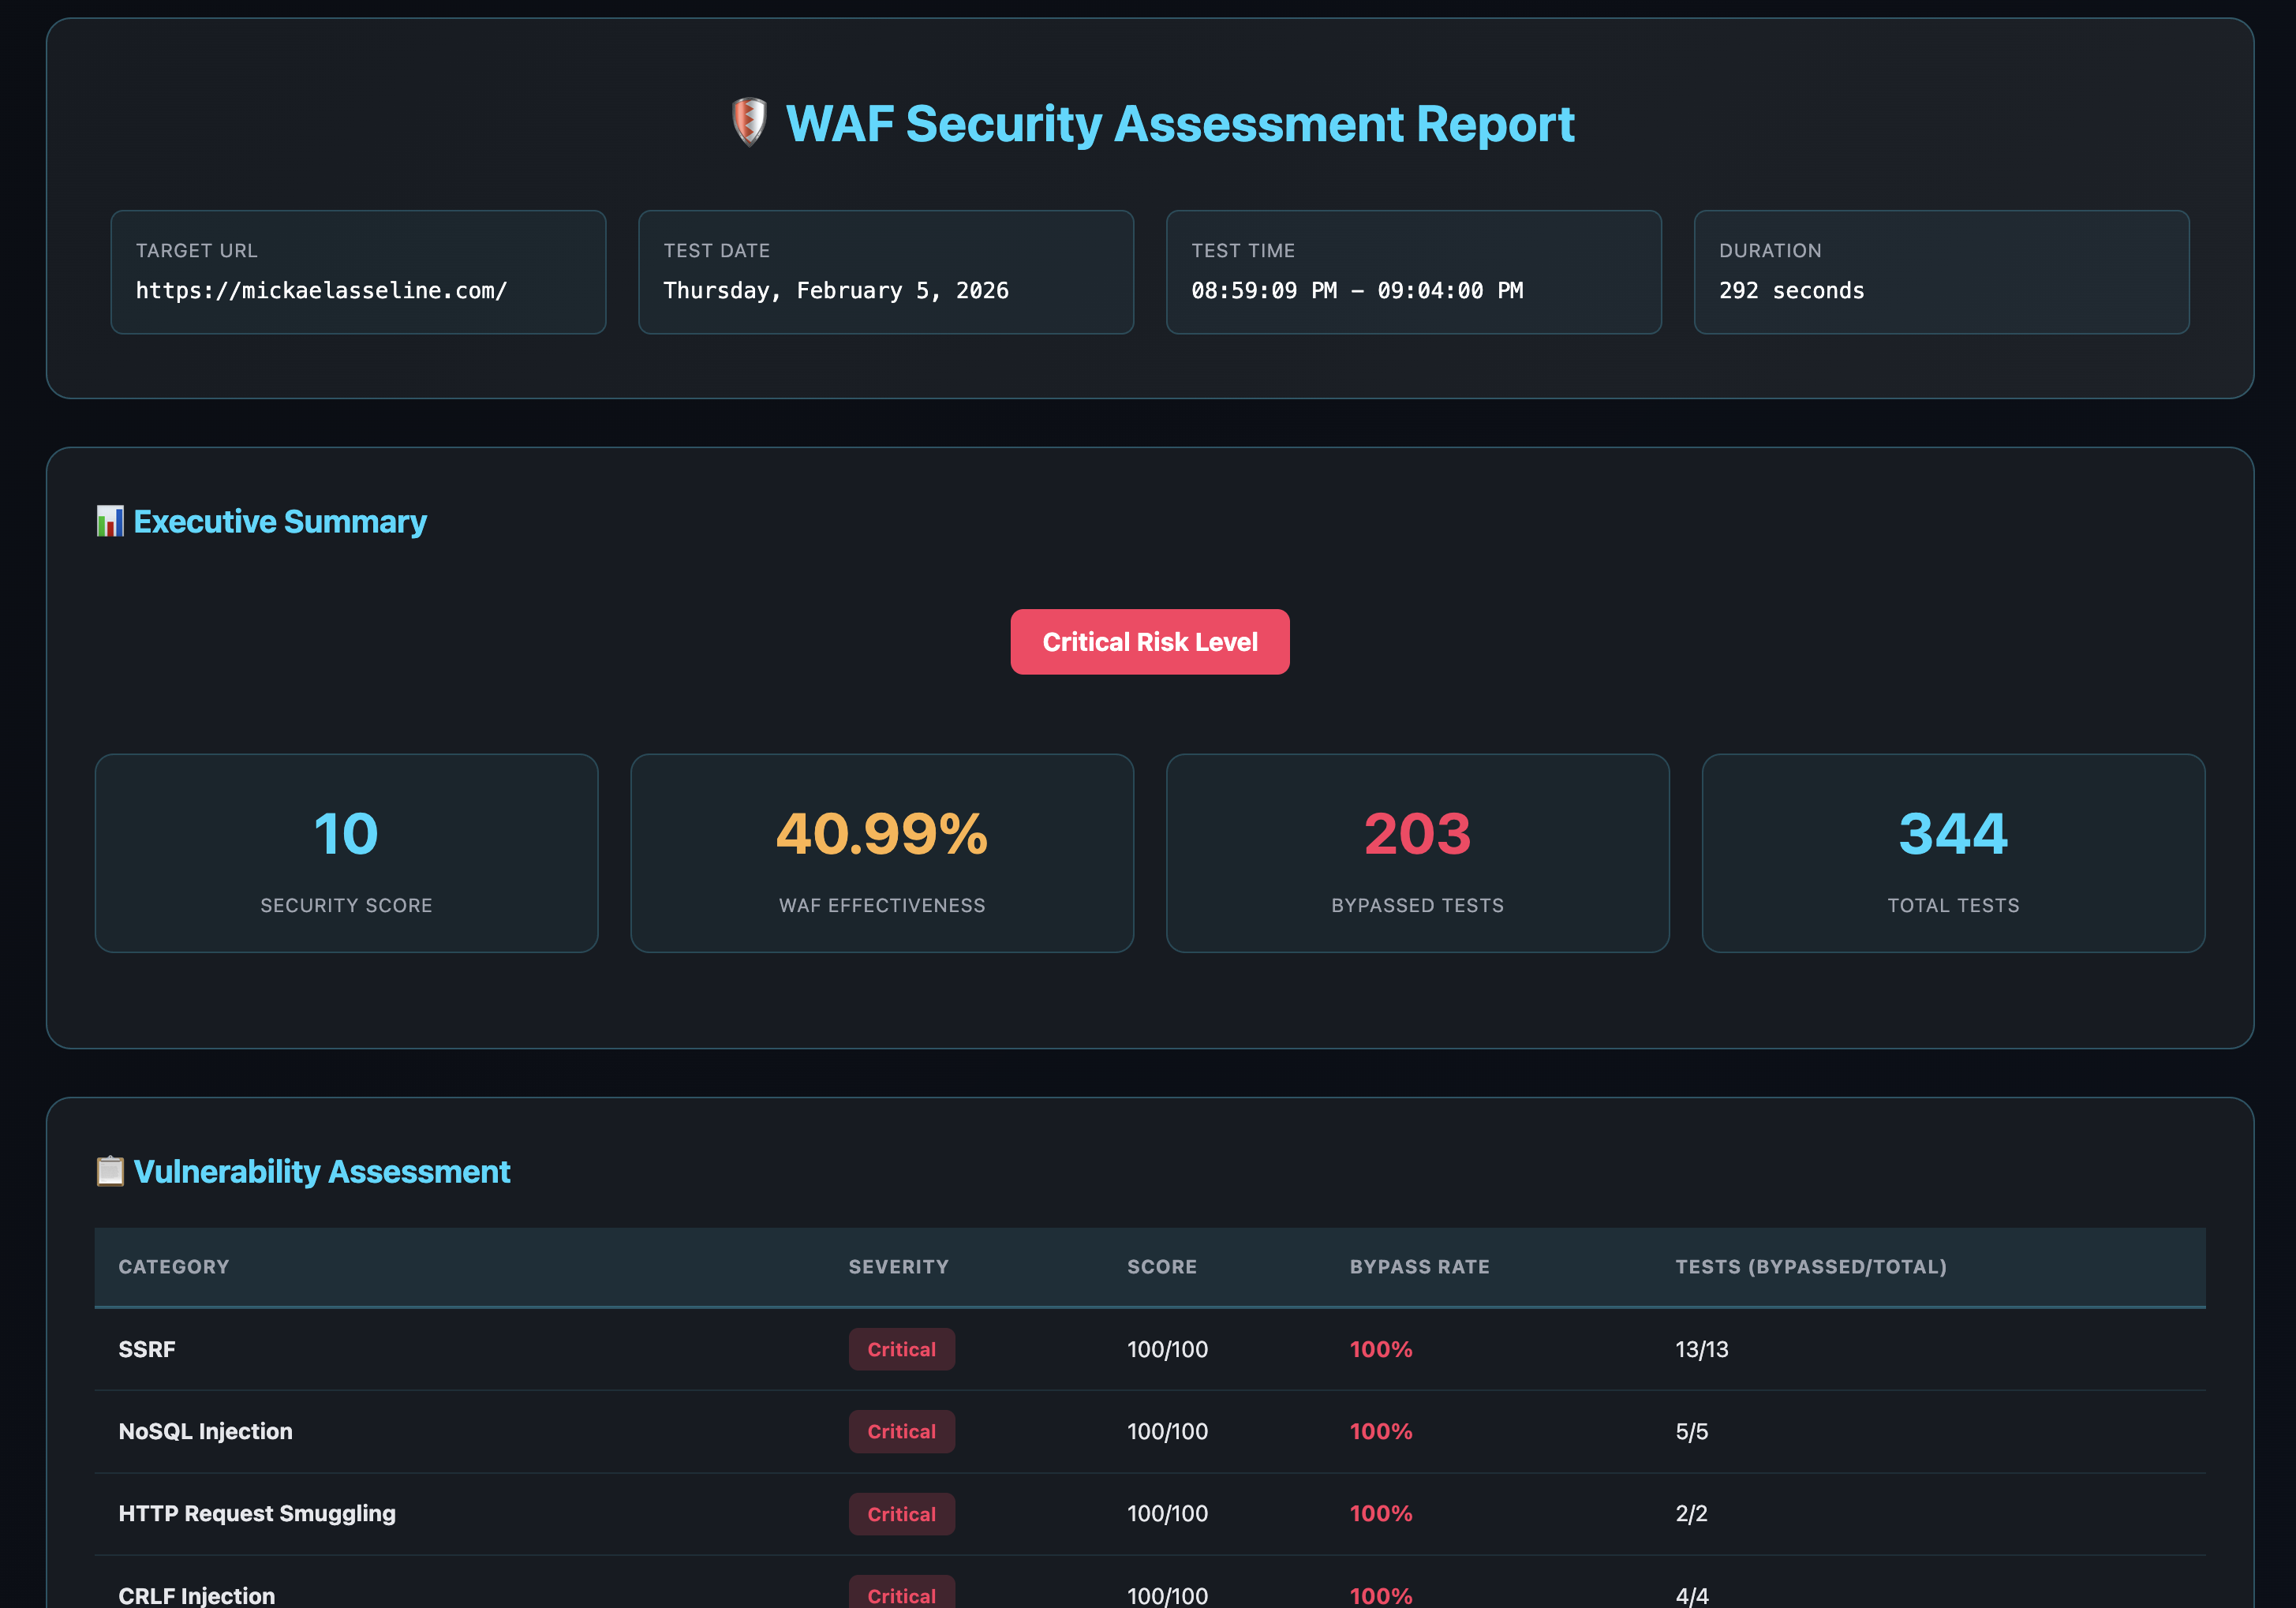
Detailed vulnerability assessment reports with scoring:
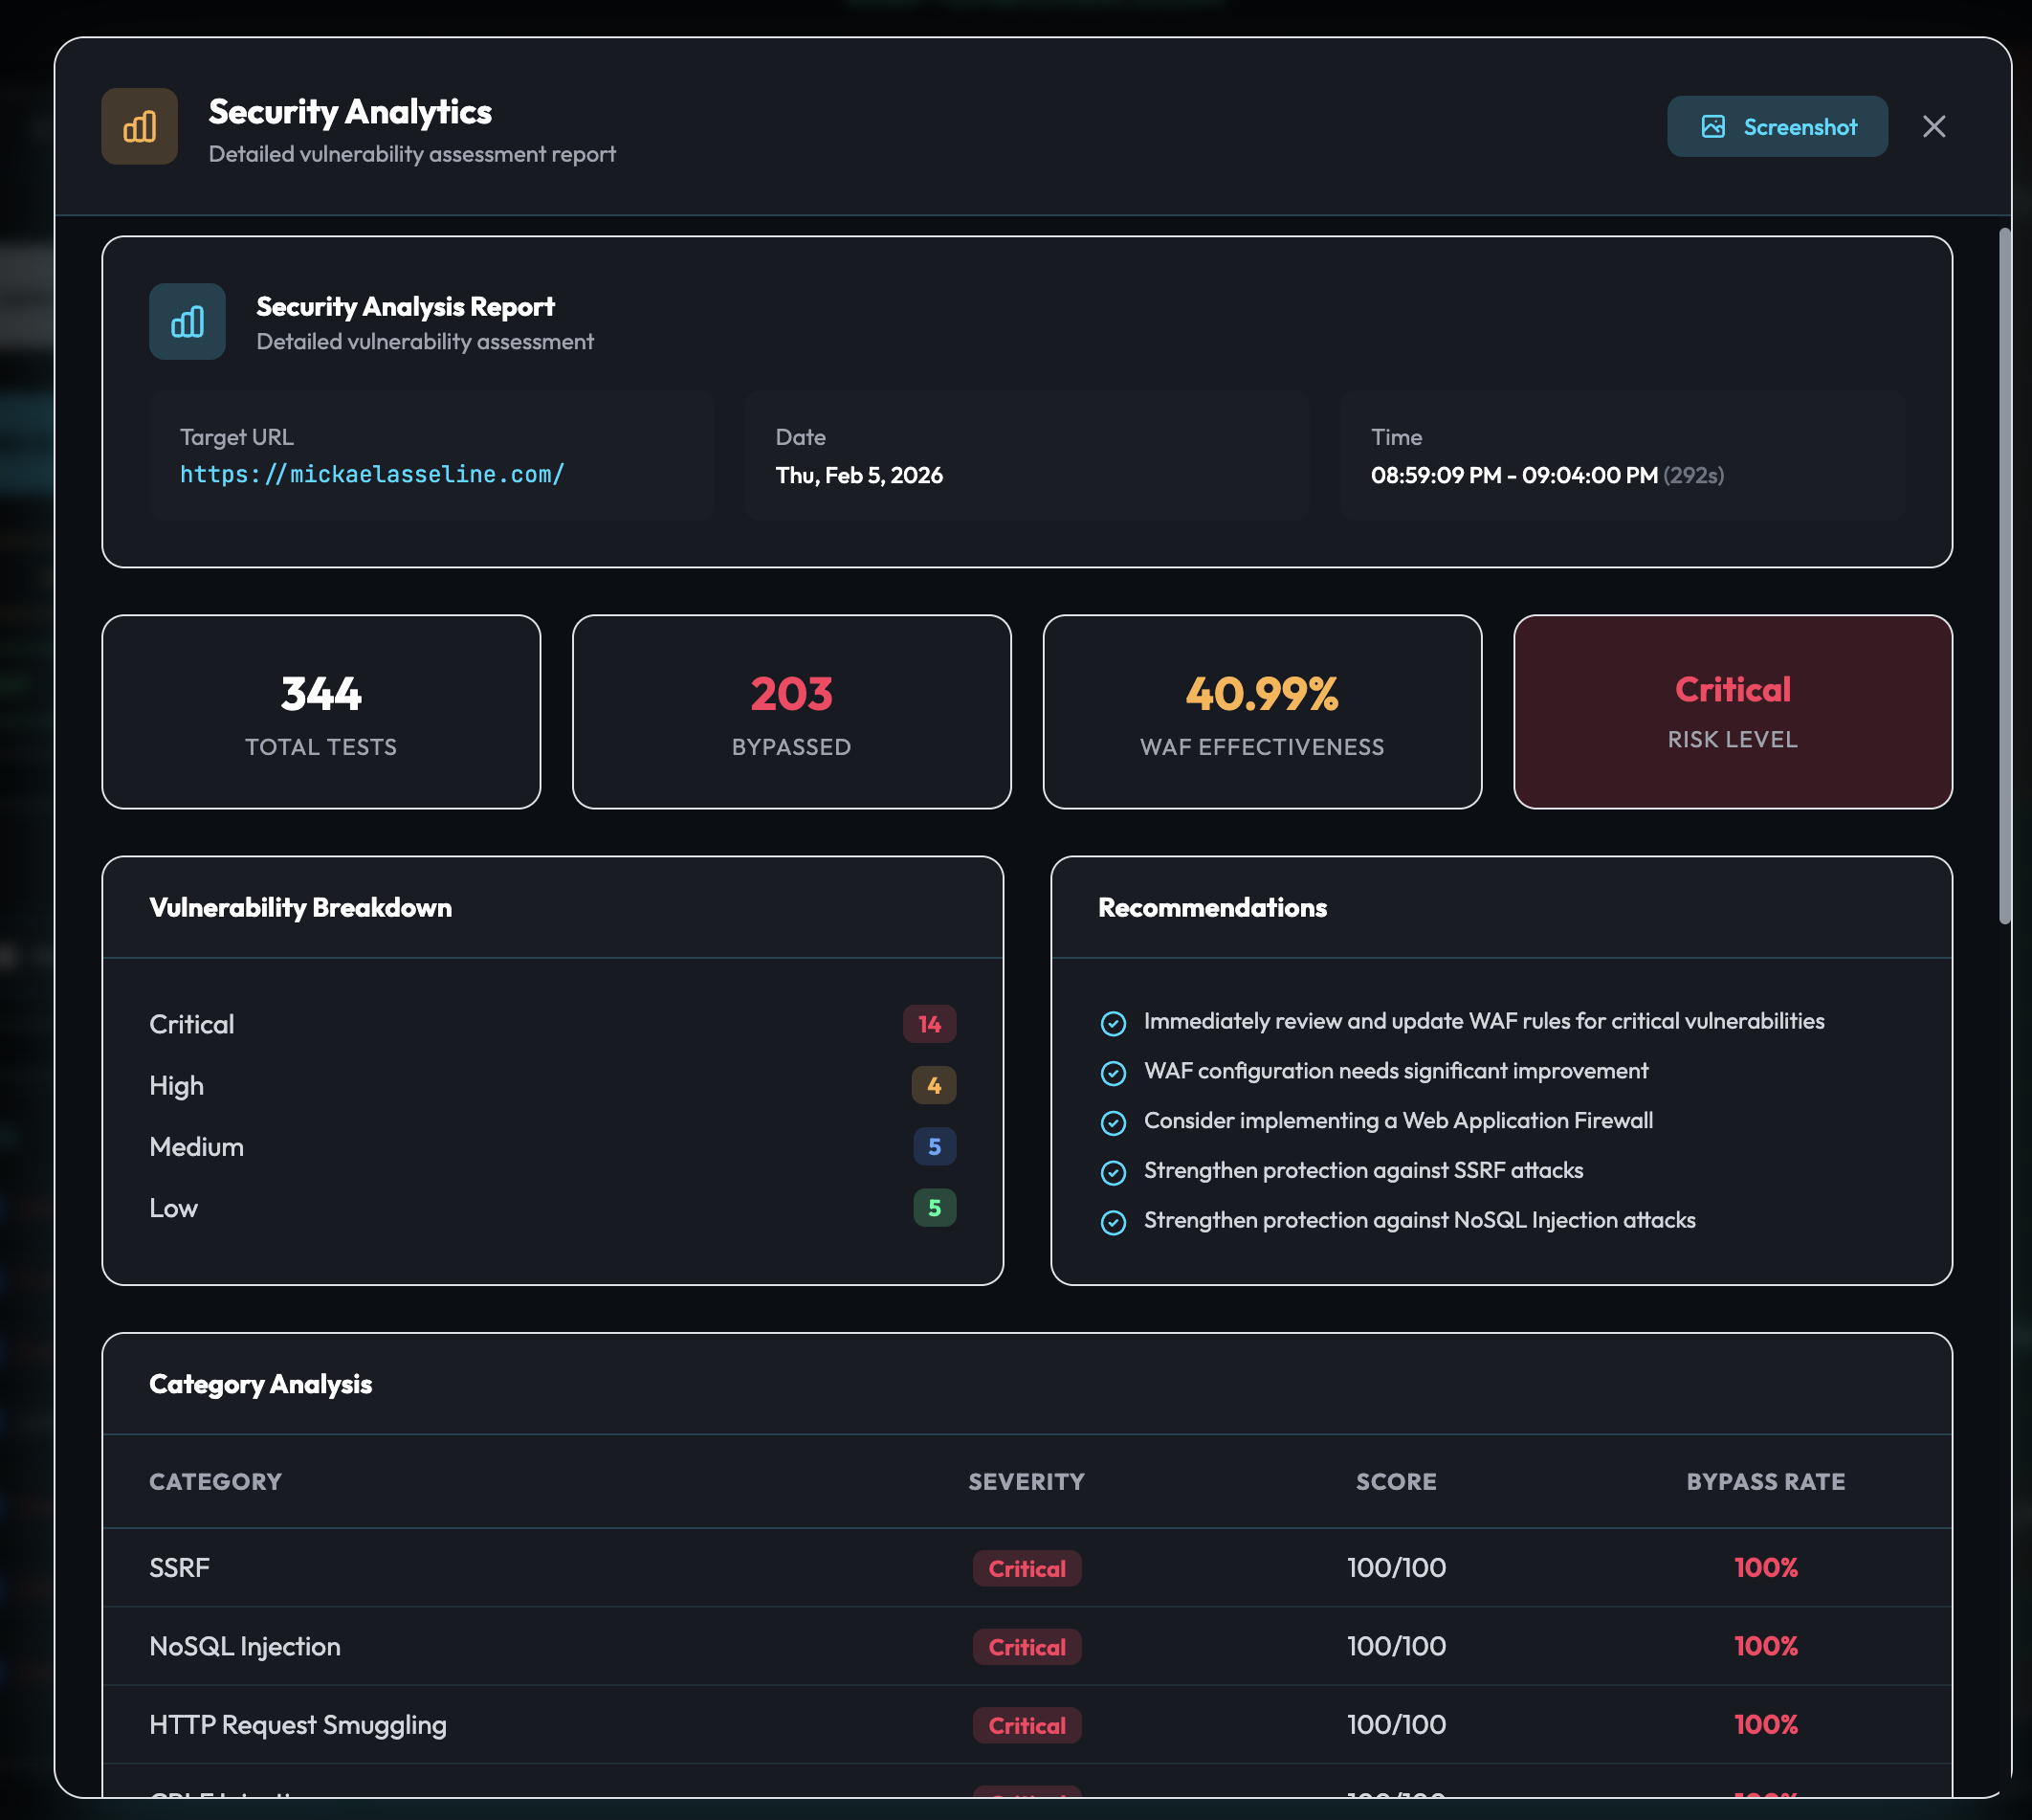
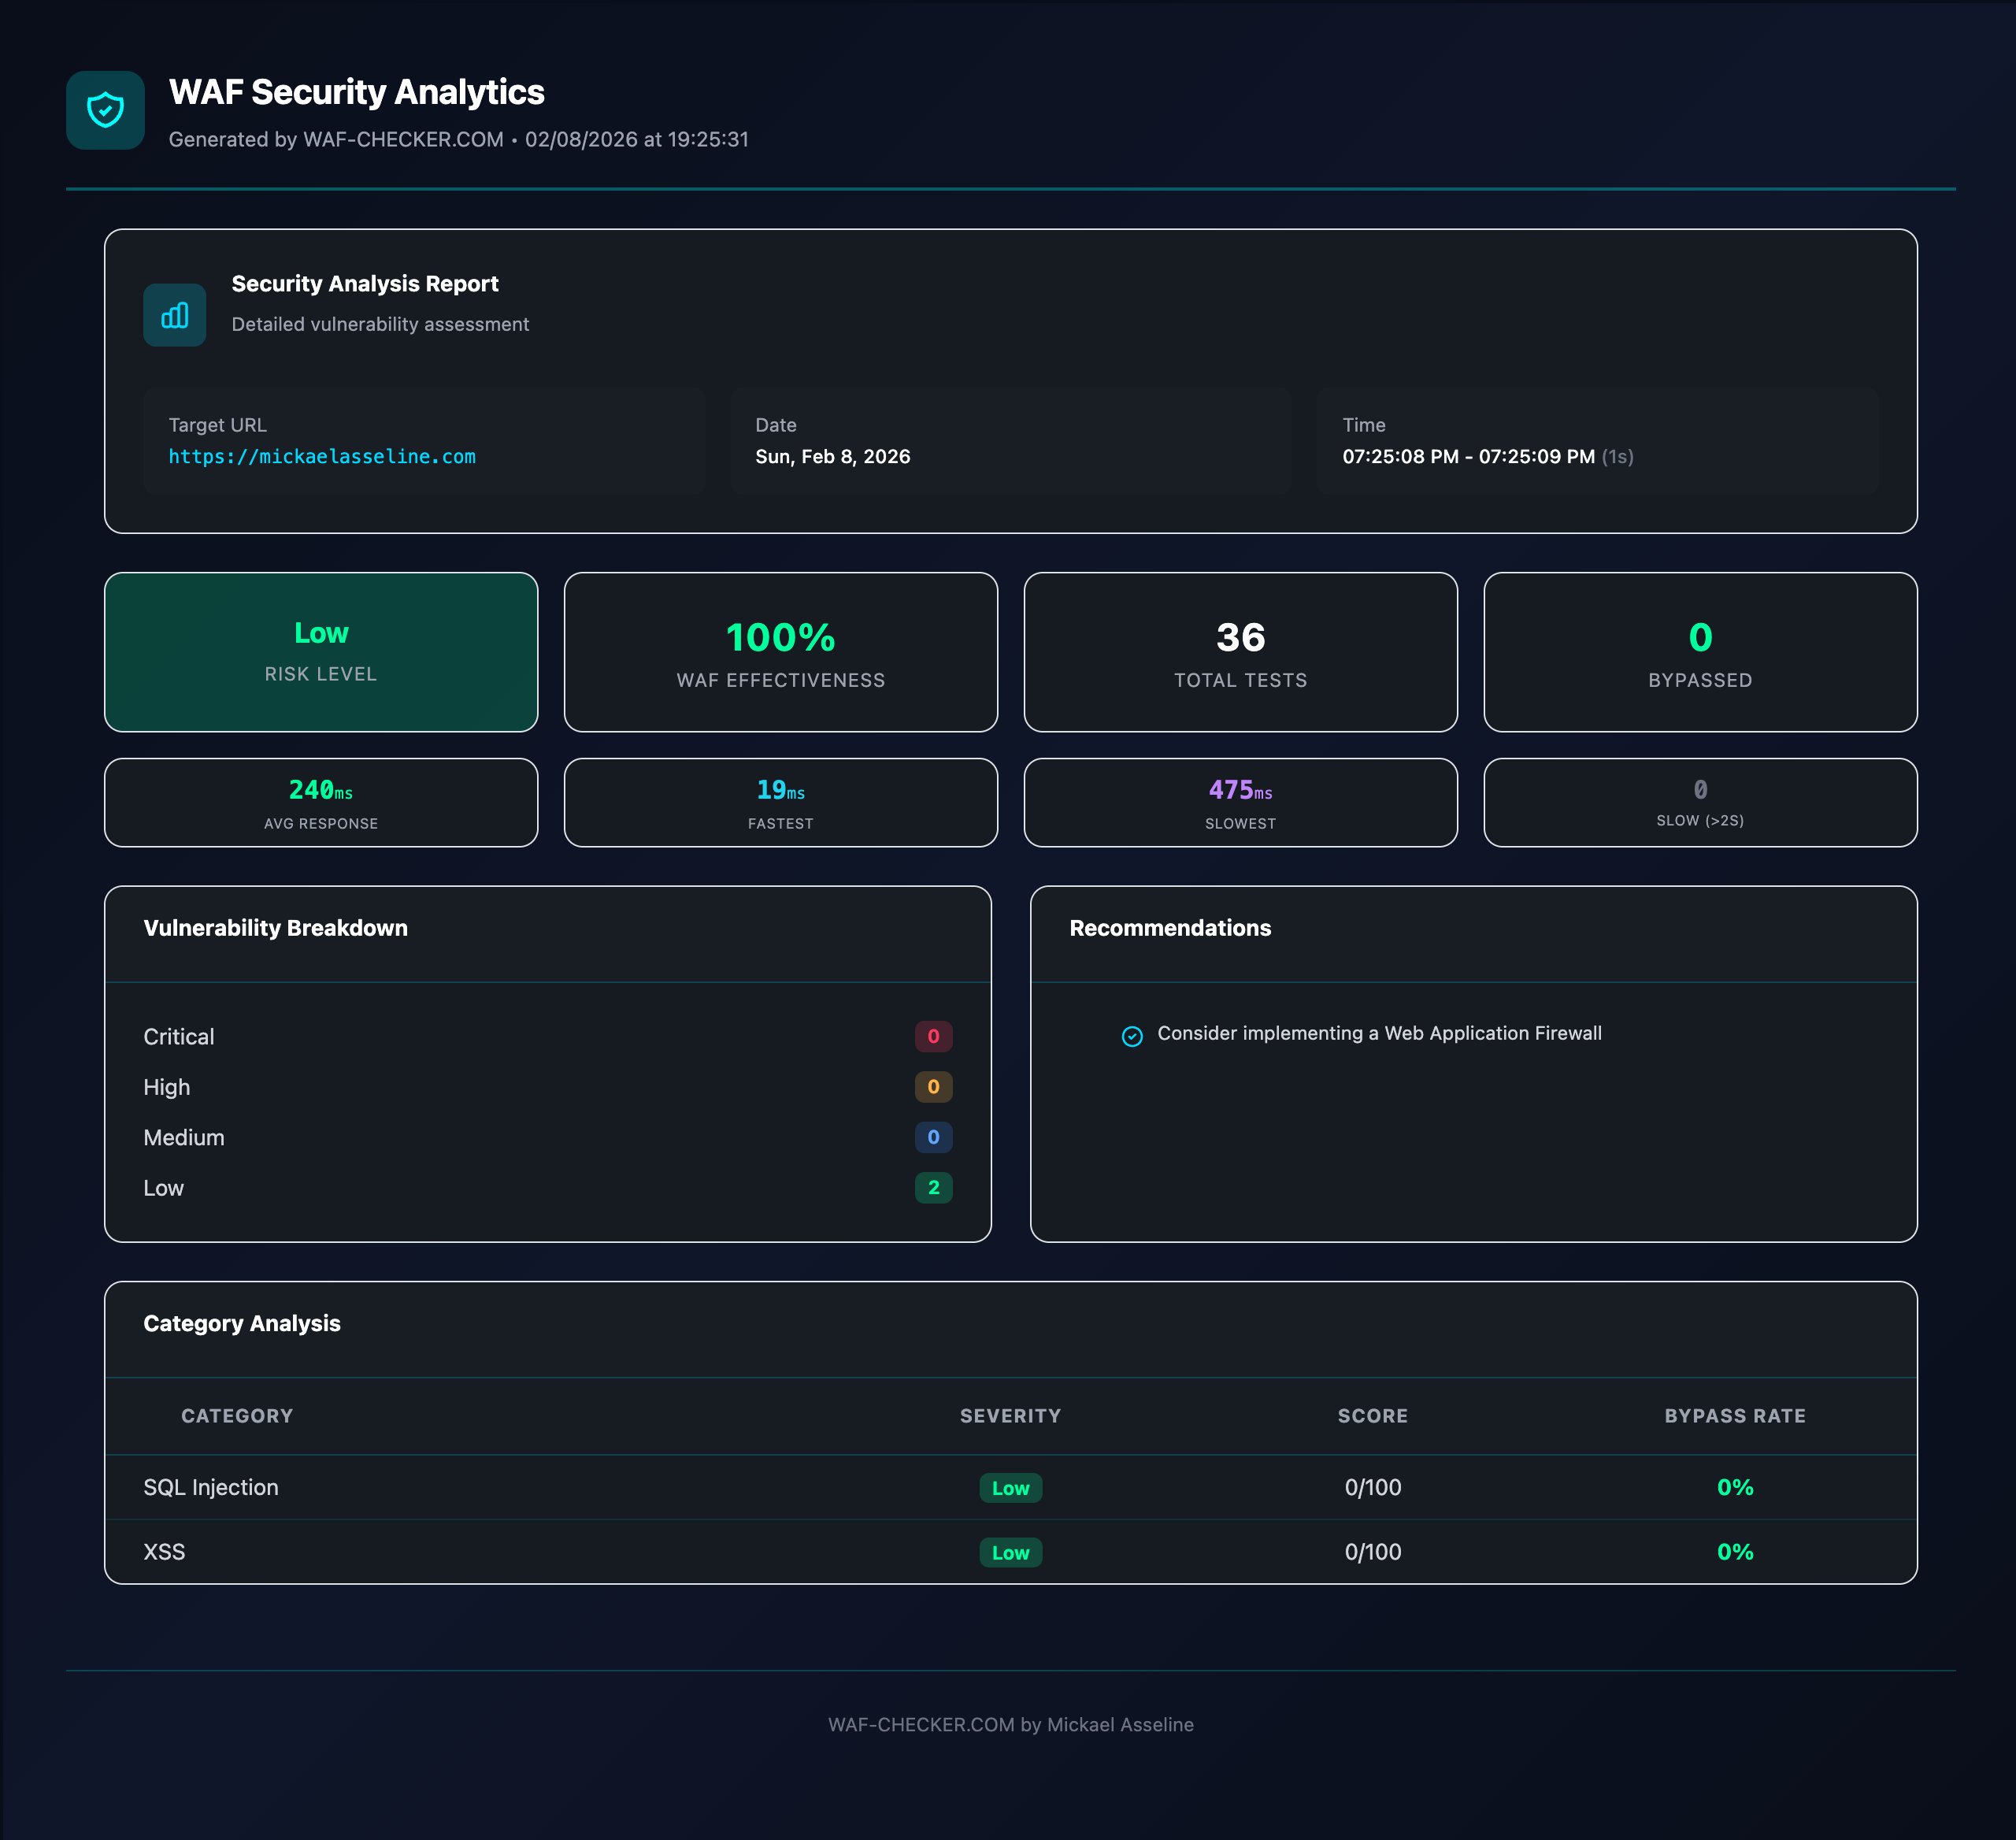
- WAF effectiveness score — percentage of attacks blocked
- Risk level assessment — Critical, High, Medium, Low
- Vulnerability breakdown by severity
- Category-level analysis with bypass rates
- Actionable recommendations
Export & Reporting

 papamica/waf-checker
