

 stuub/cve-2024-28995
CVE-2024-28955 Exploitation PoC
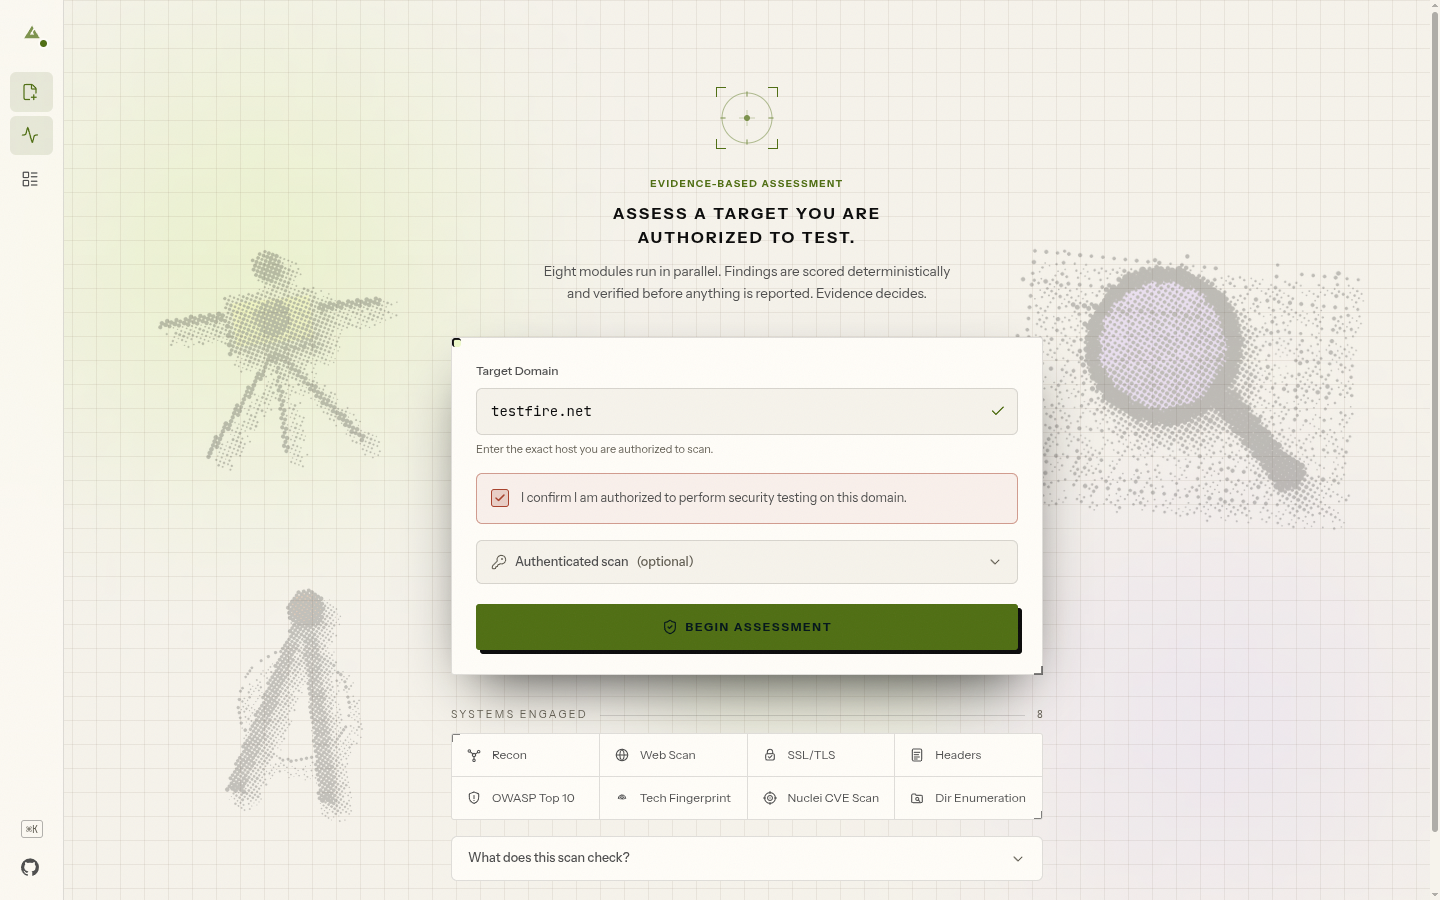 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…
 stuub/cve-2024-29895-cactirce-poc
CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
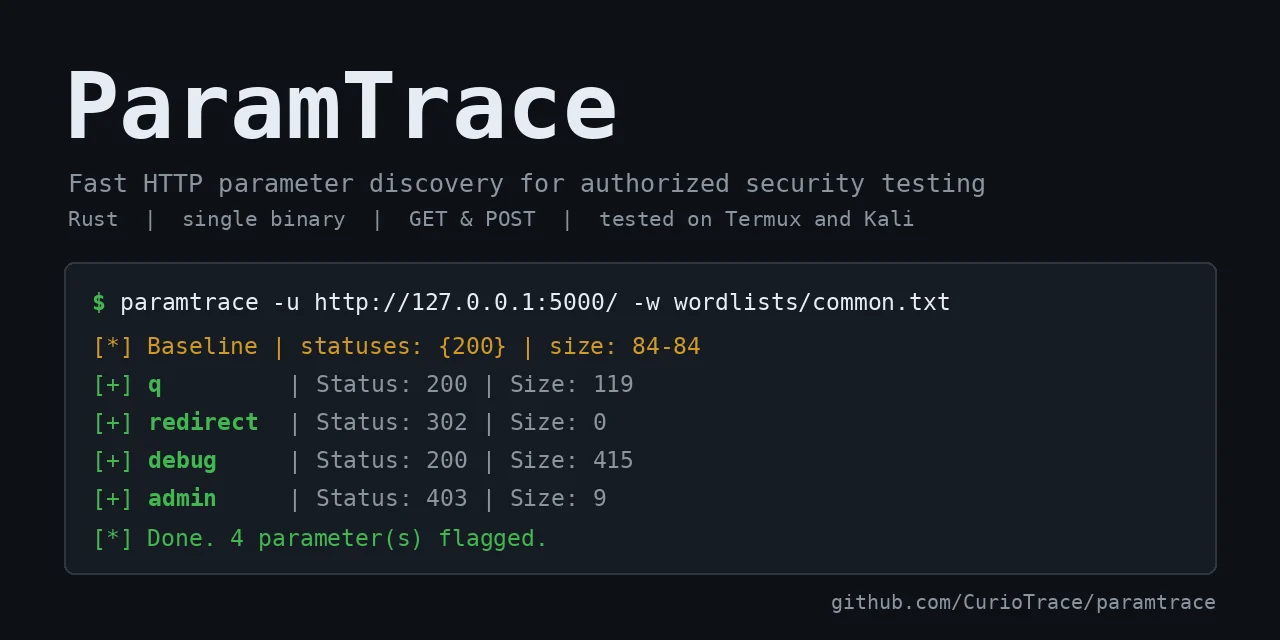 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
 ovotech/domain-protect
Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
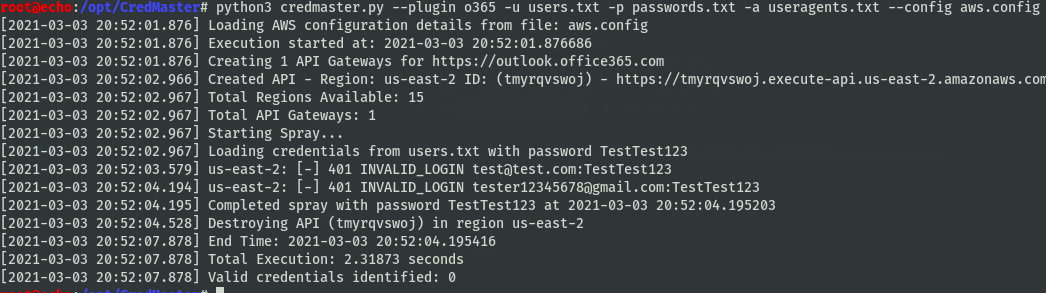 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
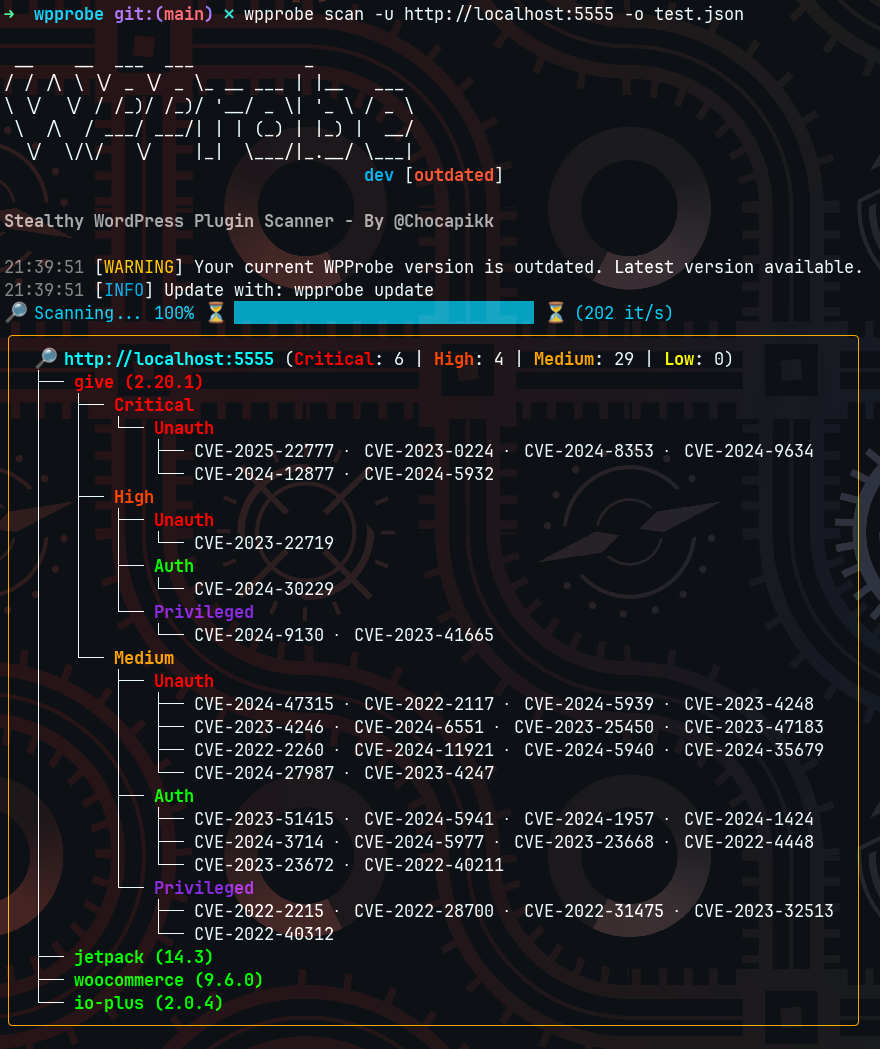 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 saffron-health/libretto
The AI toolkit for building reliable browser automations
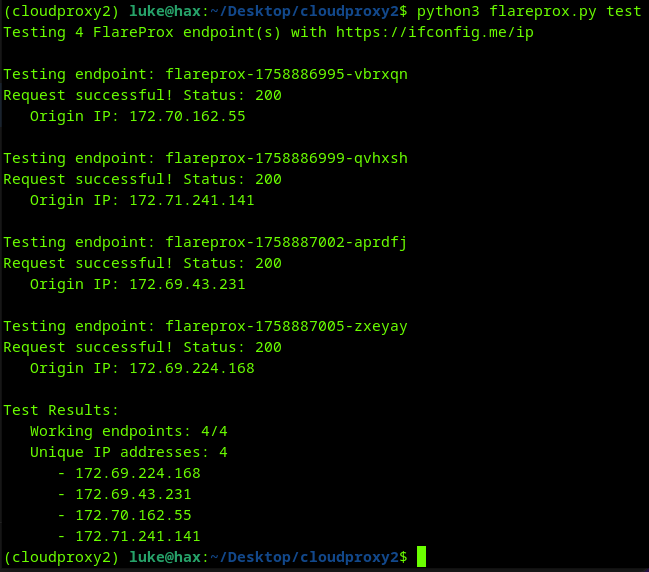 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
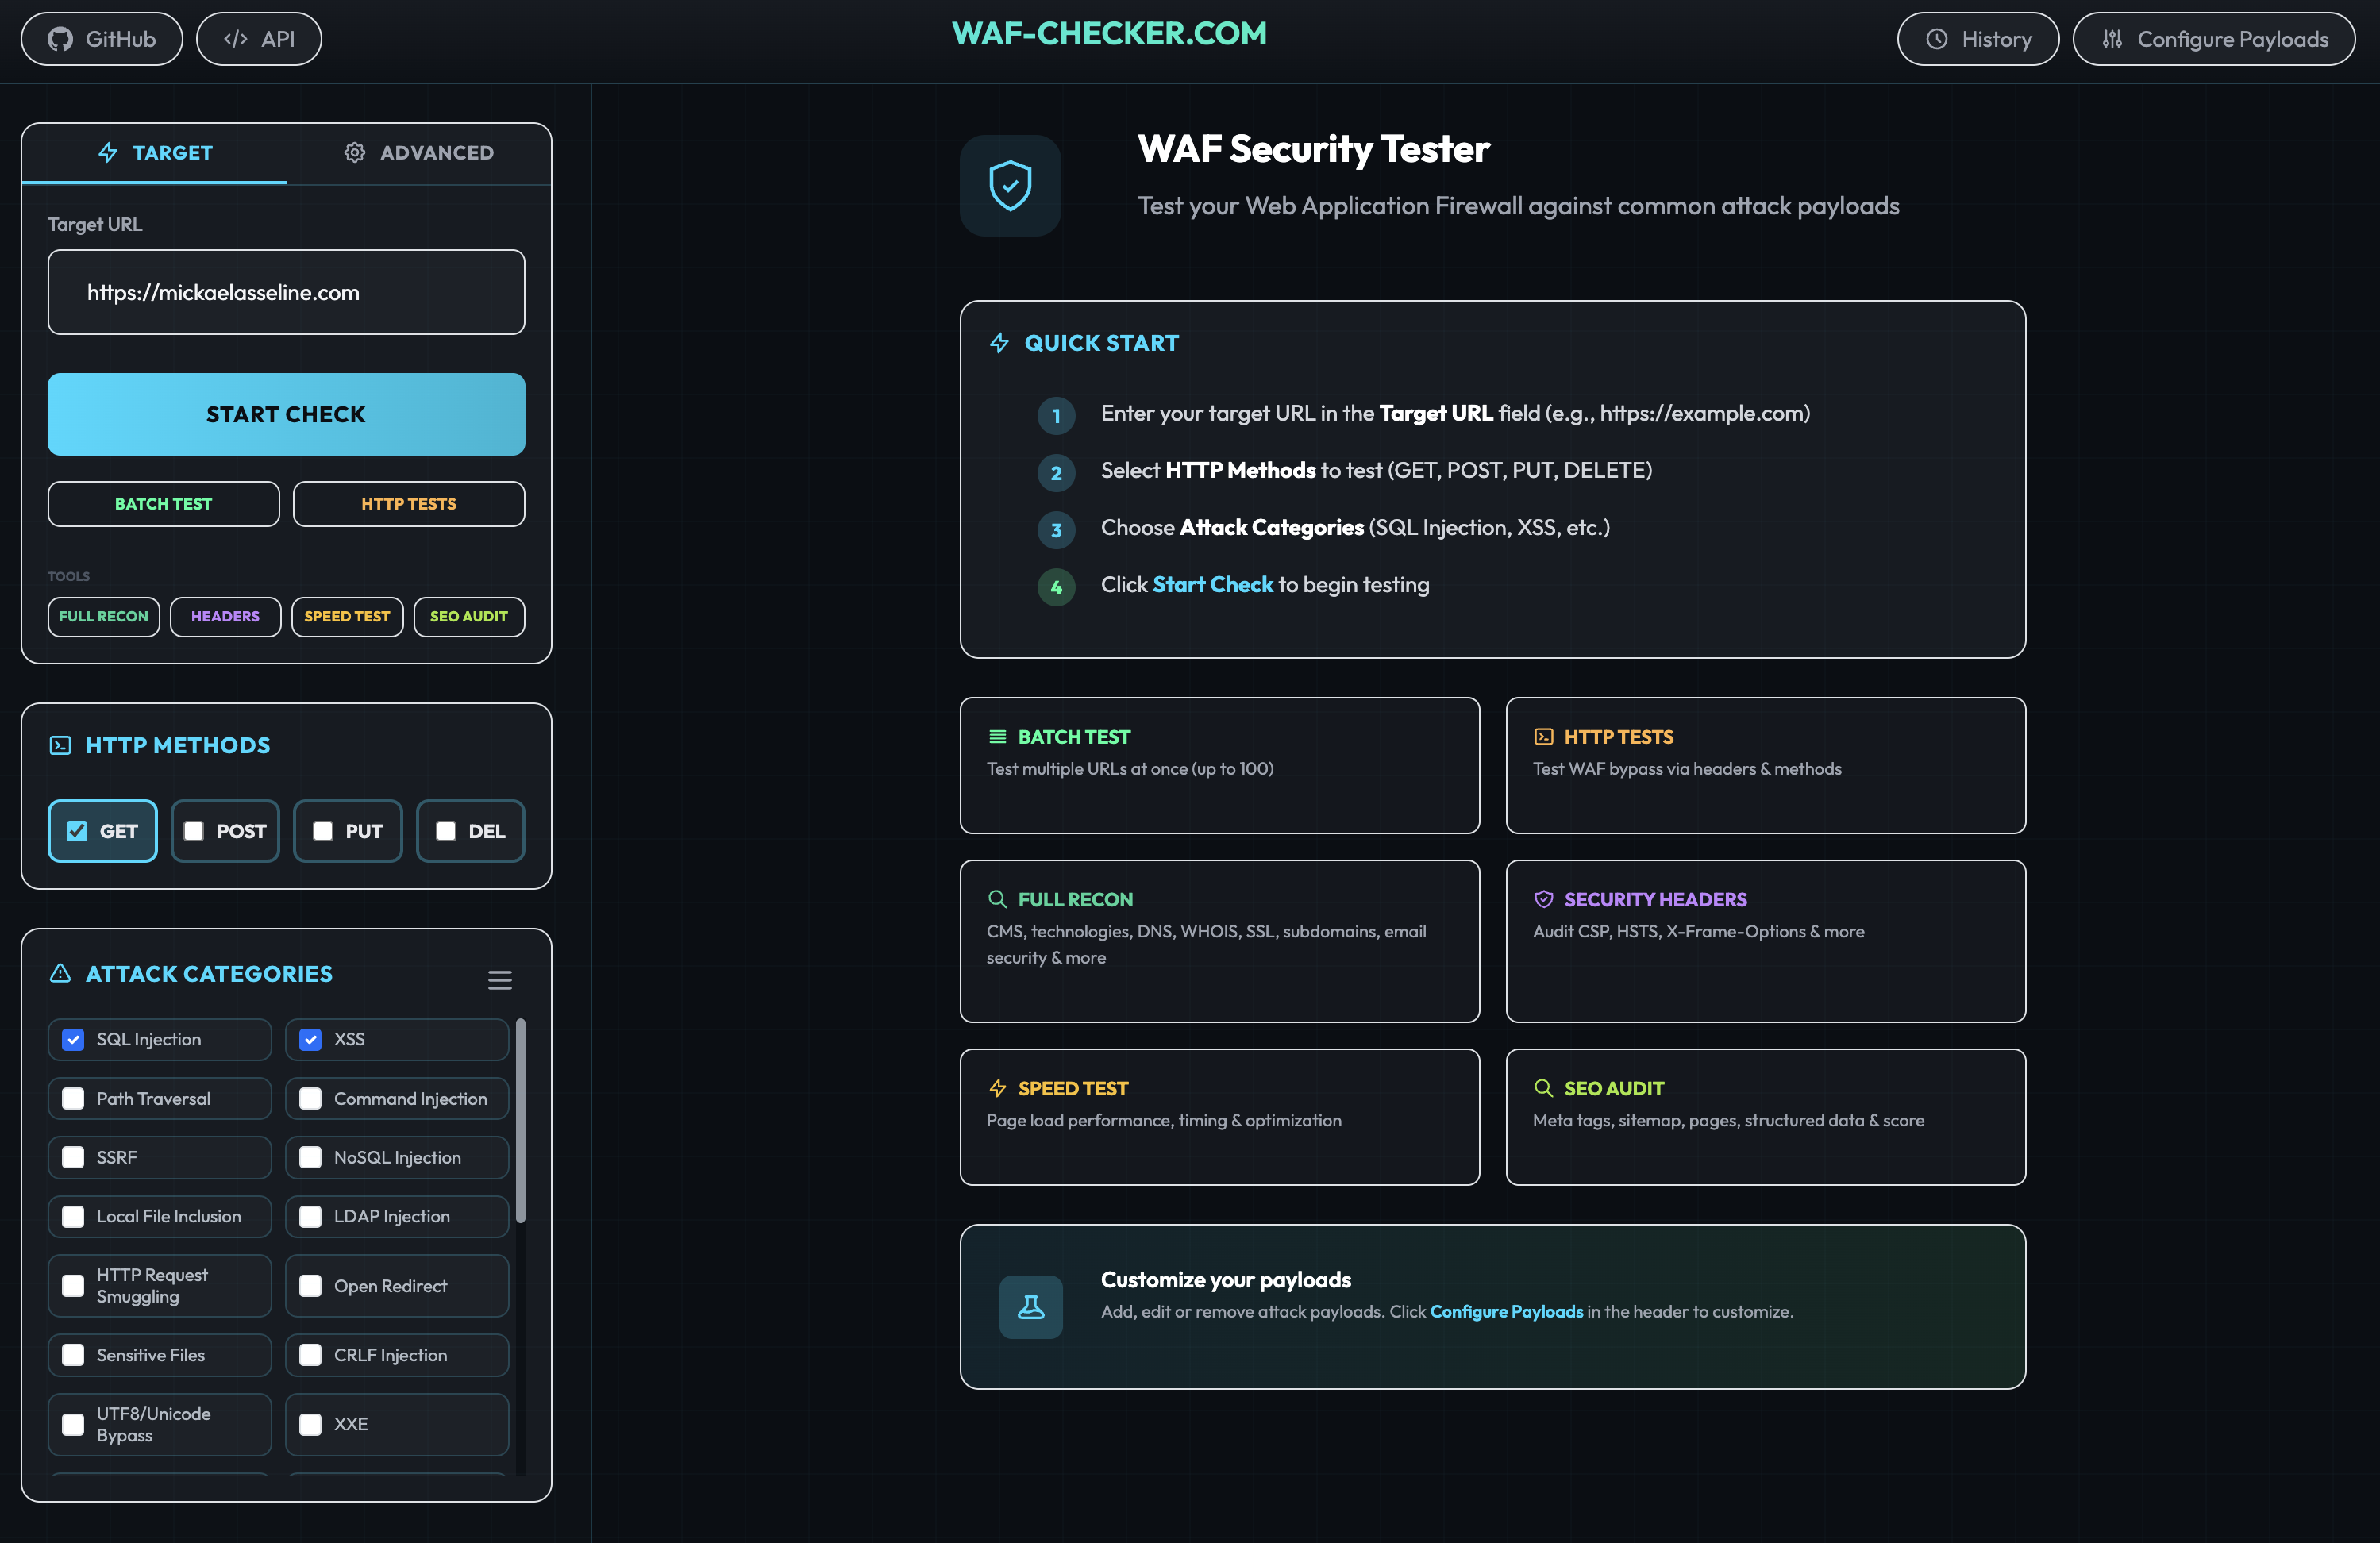 papamica/waf-checker
Tests your WAF with +160 payloads