
 #1
Tools for discovering network topology, devices, and services.
Kitploit recommended

 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 affolter-engineering/snmpen
SNMP enumeration tool that queries SNMPv1/v2c hosts to extract system information, TCP connections, and write access for penetration testing and…
 ko0ler/homelab
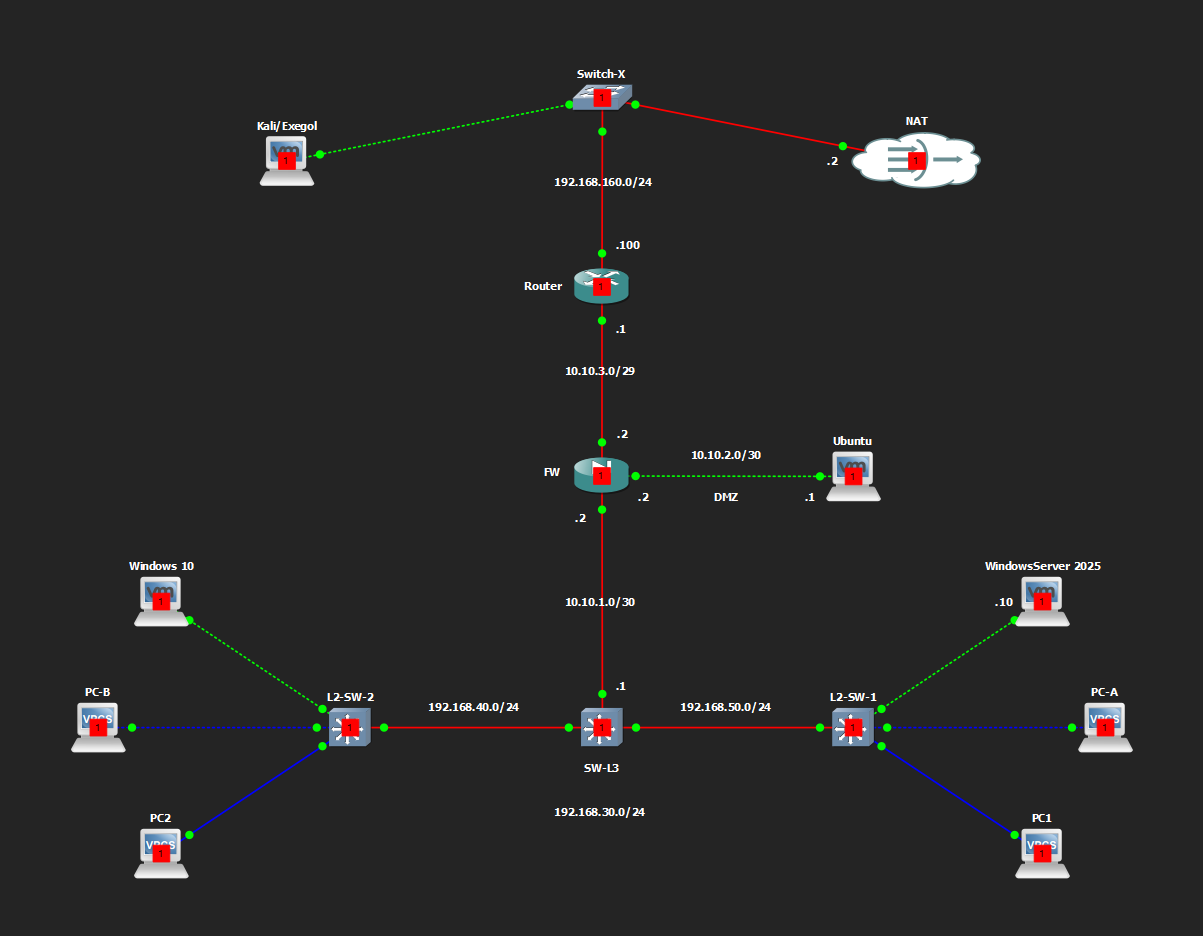
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…
 constantinefedorov/review.cve-2023-5612
Proof-of-concept and analysis for CVE-2023-5612, a GitLab CE/EE webhook SSRF. Includes curl PoC steps and custom NSE scripts to verify and…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 aixisstudio/snitch
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…








