
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
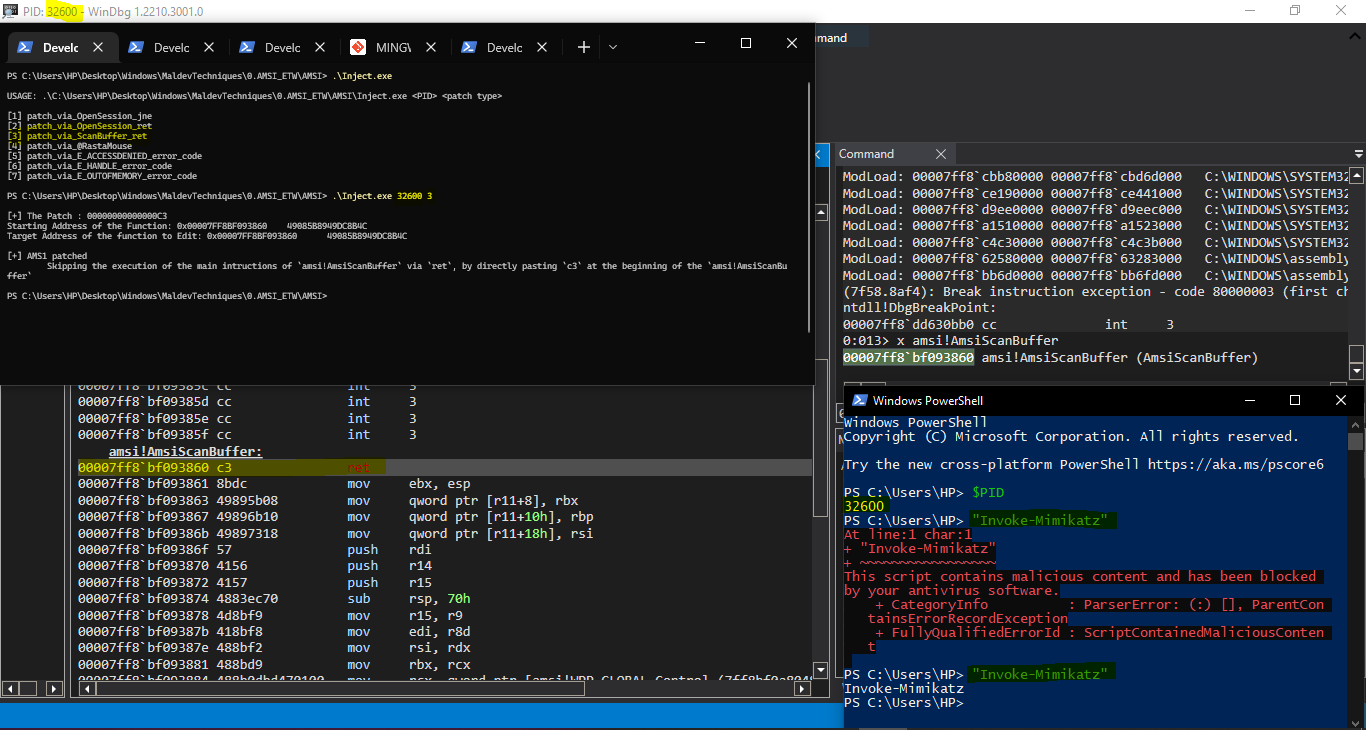
 reveng007/amsi-patches-learned-till-now
I have documented all of the AMSI patches that I learned till now
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
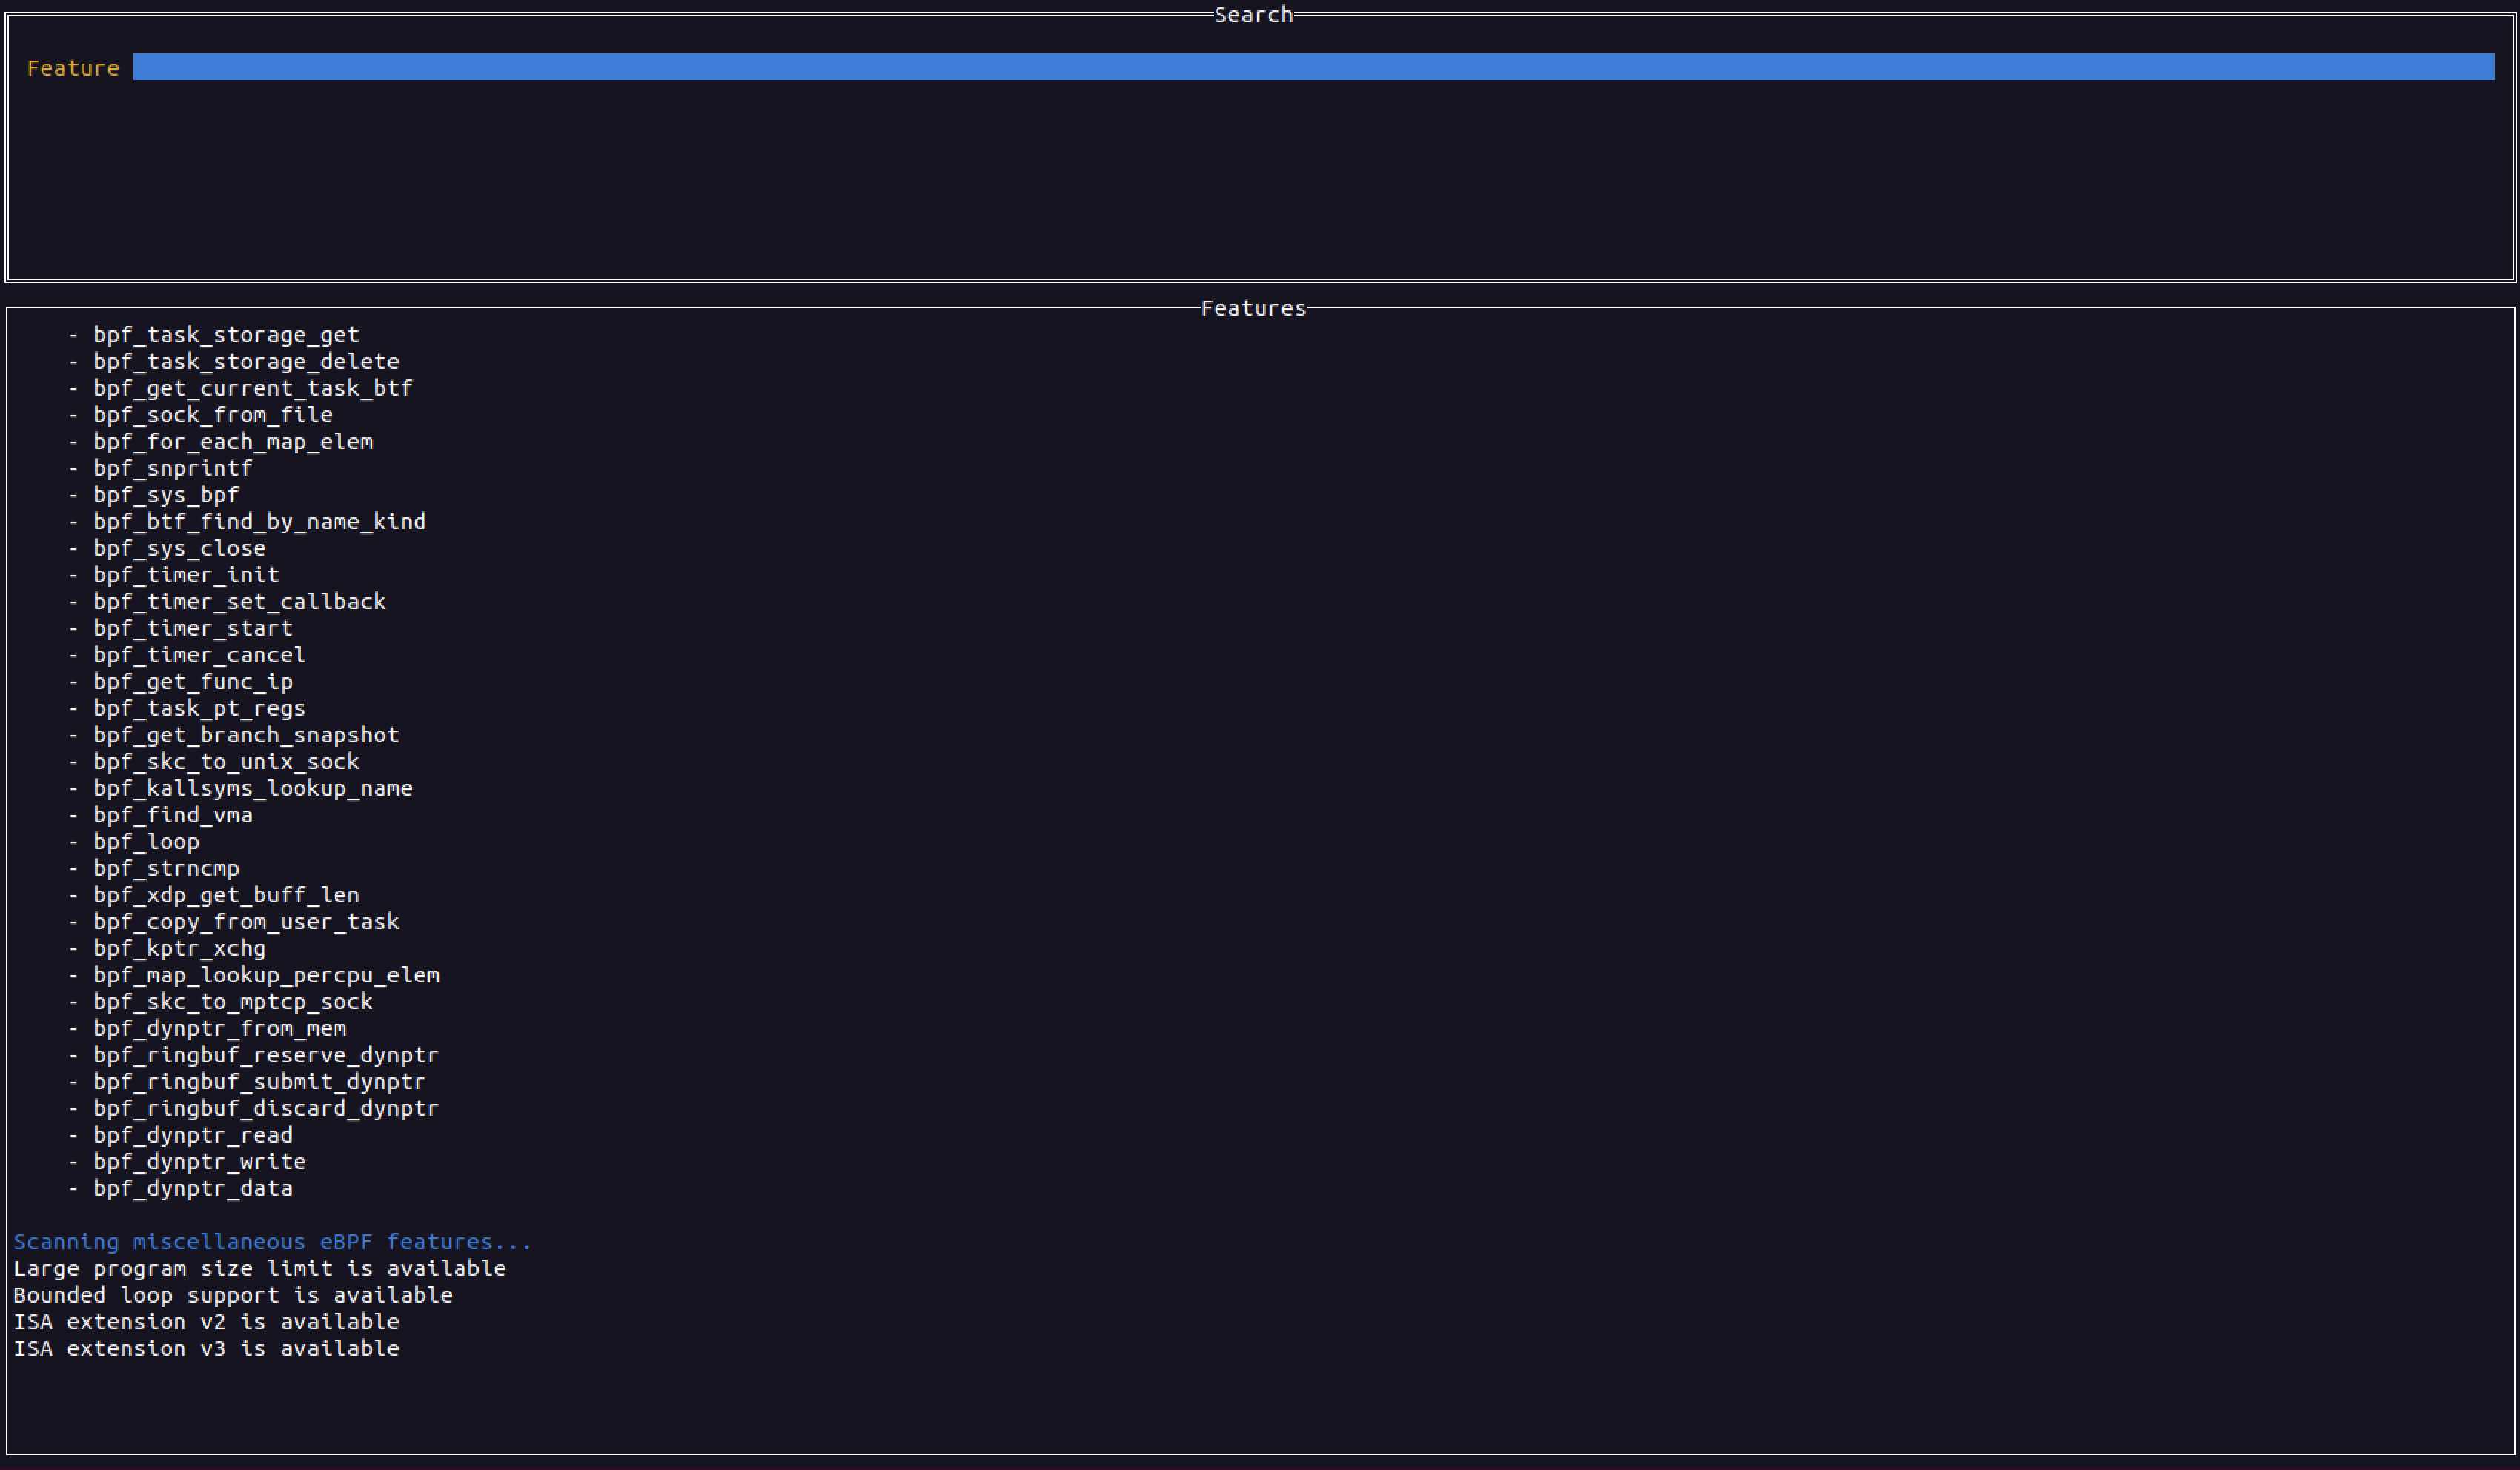 redcanaryco/ebpfmon
Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
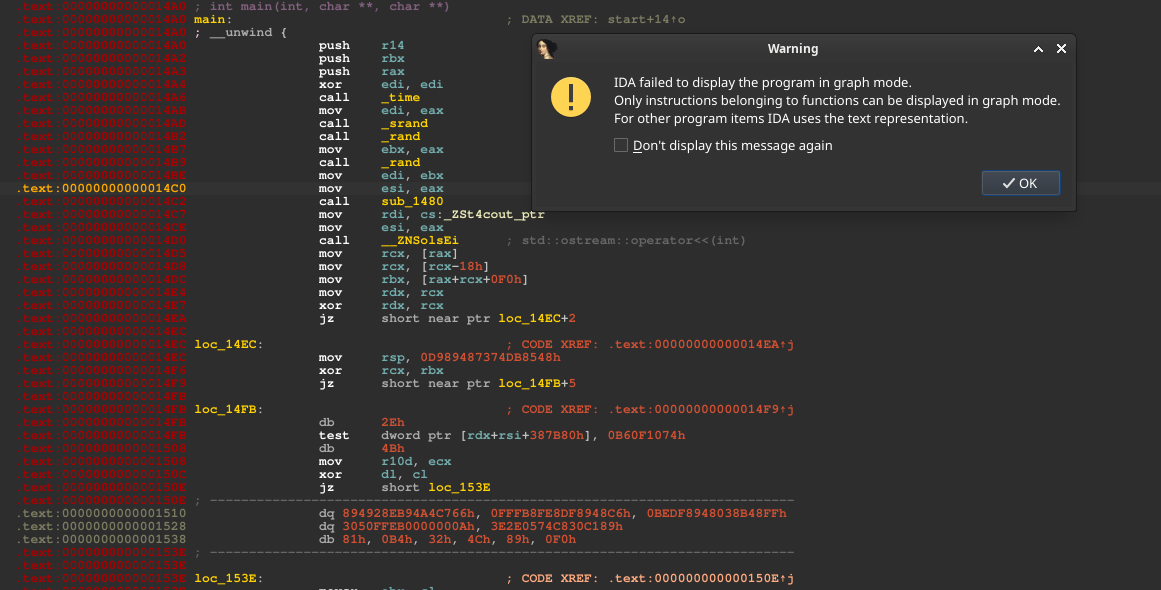 zydak/leetobfuscator
Obfuscates C/C++ through LLVM passes: string encryption, control-flow flattening, MBA rewriting, and anti-analysis to defeat reverse engineering.
 jaredcatkinson/malwaremorphology
Hands-on security workshop on malware morphology, covering structural analysis techniques, classification concepts, and practical exercises from…
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
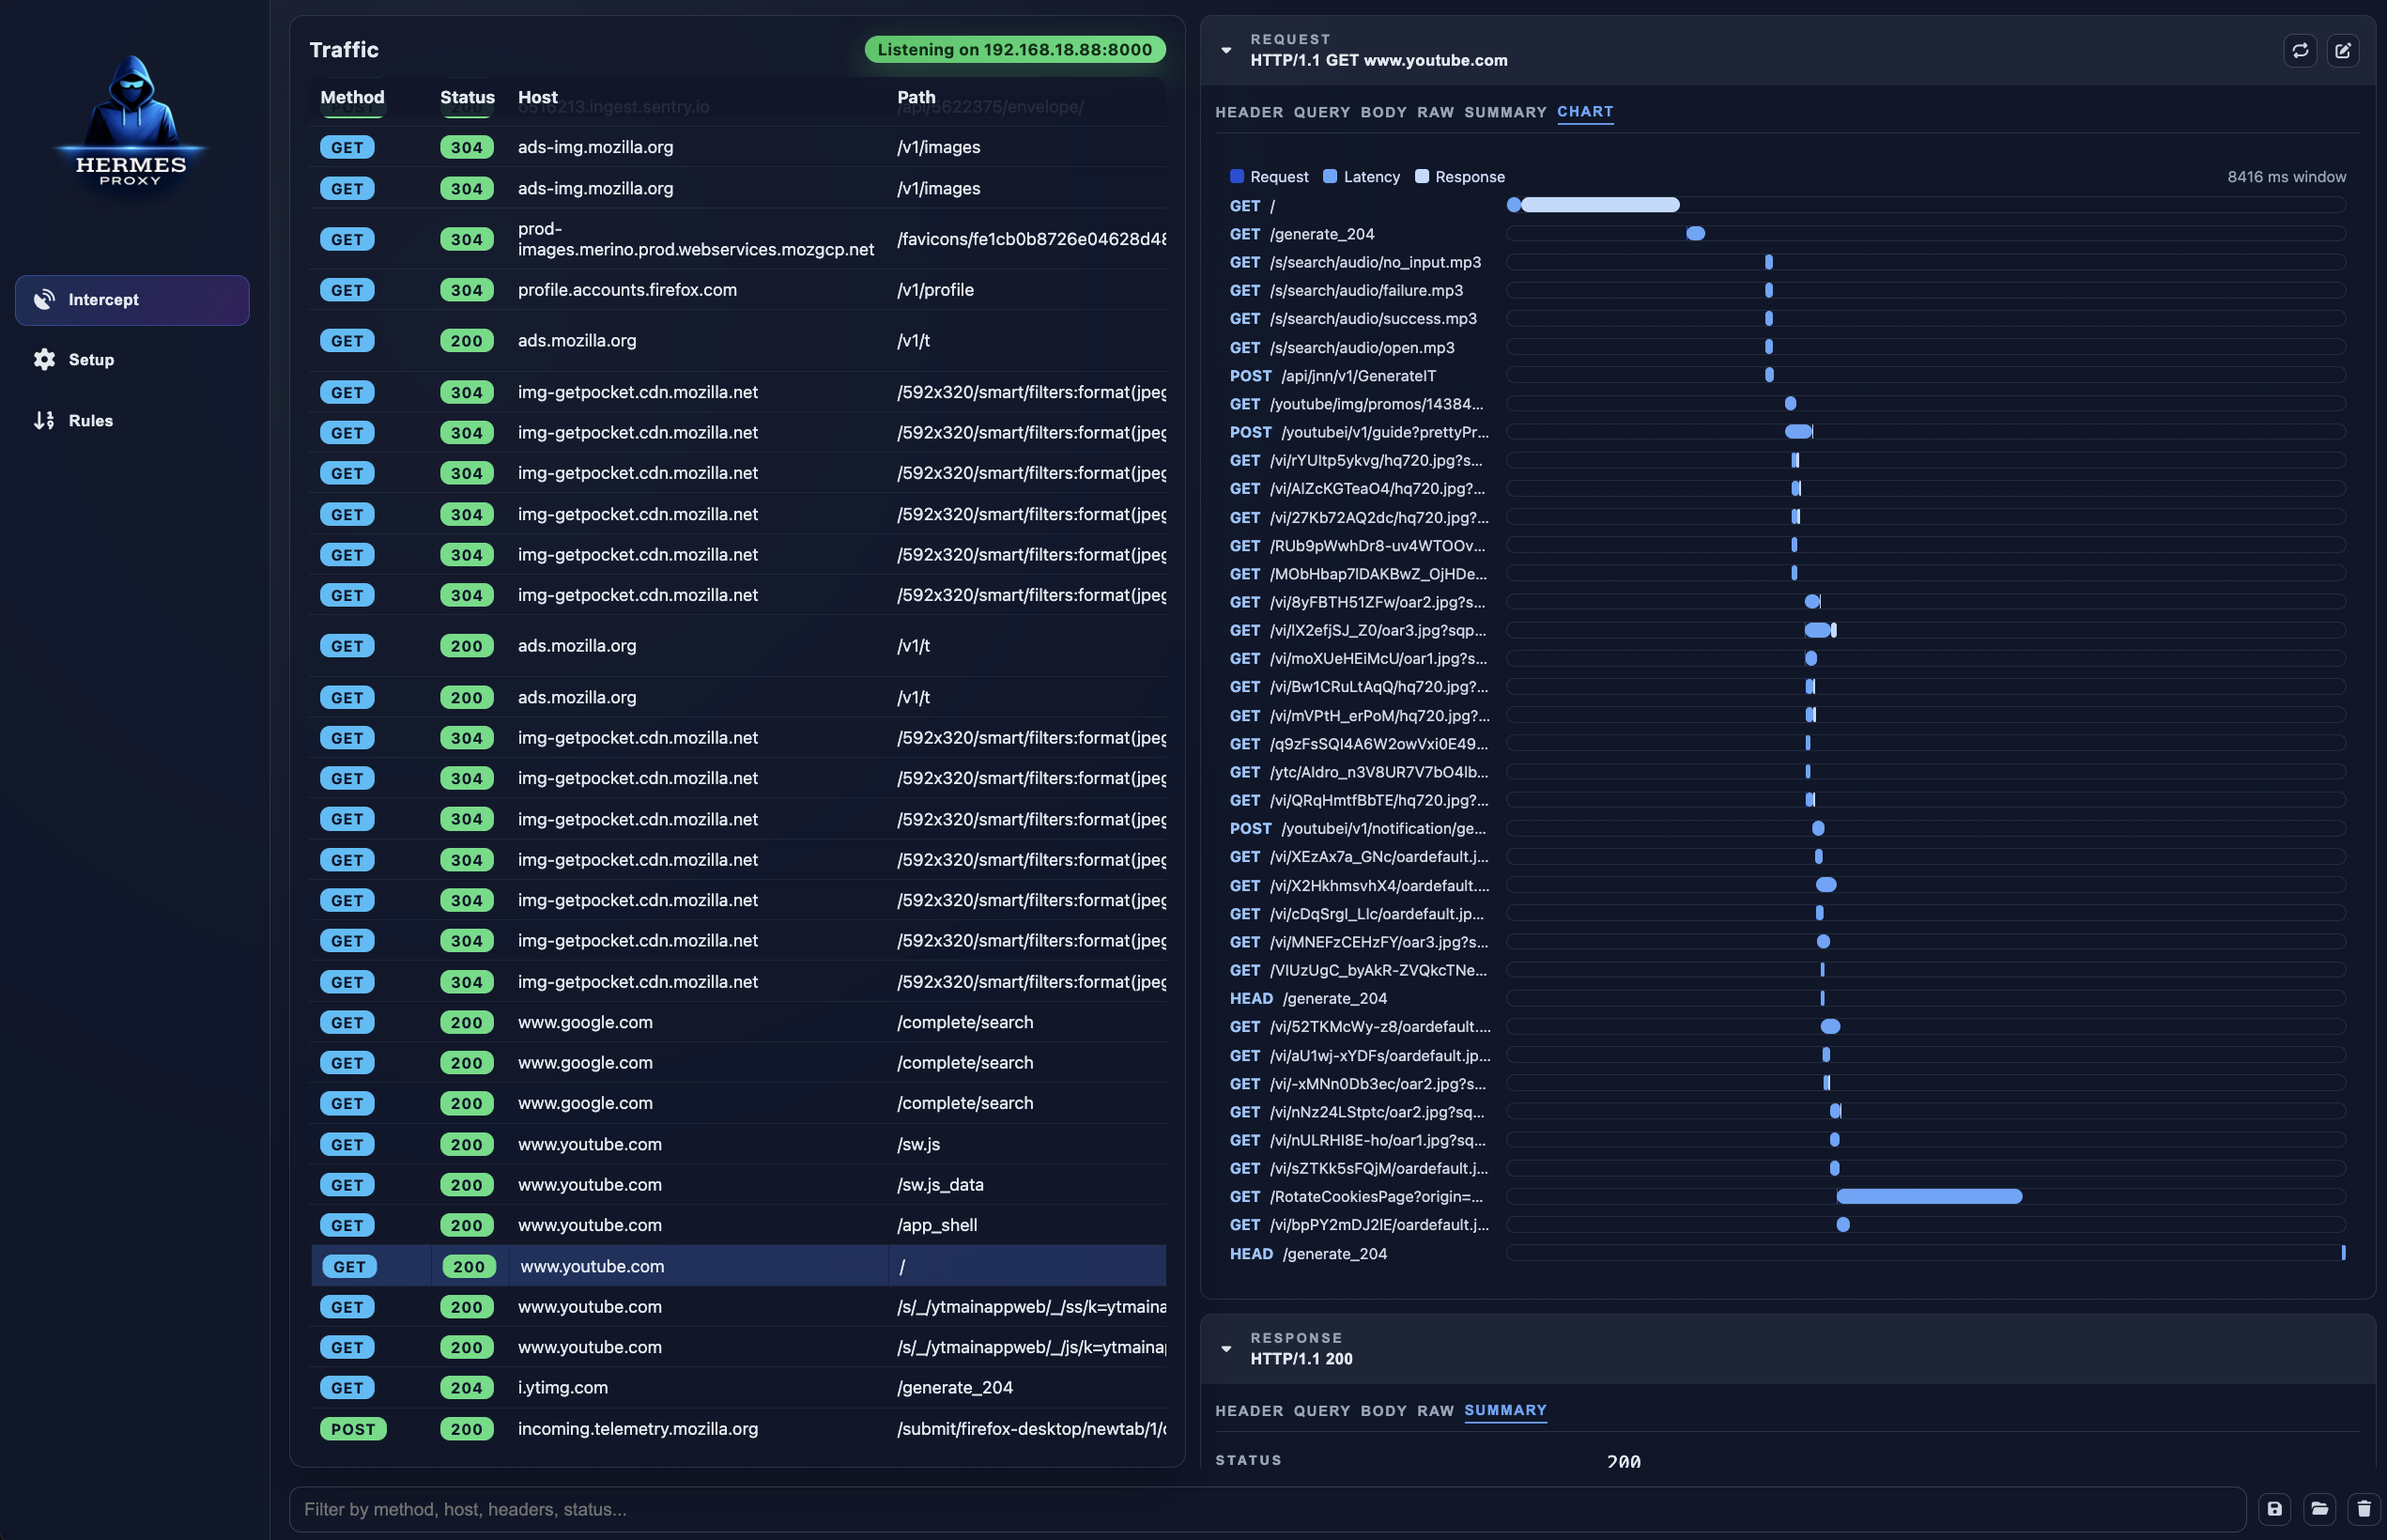 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
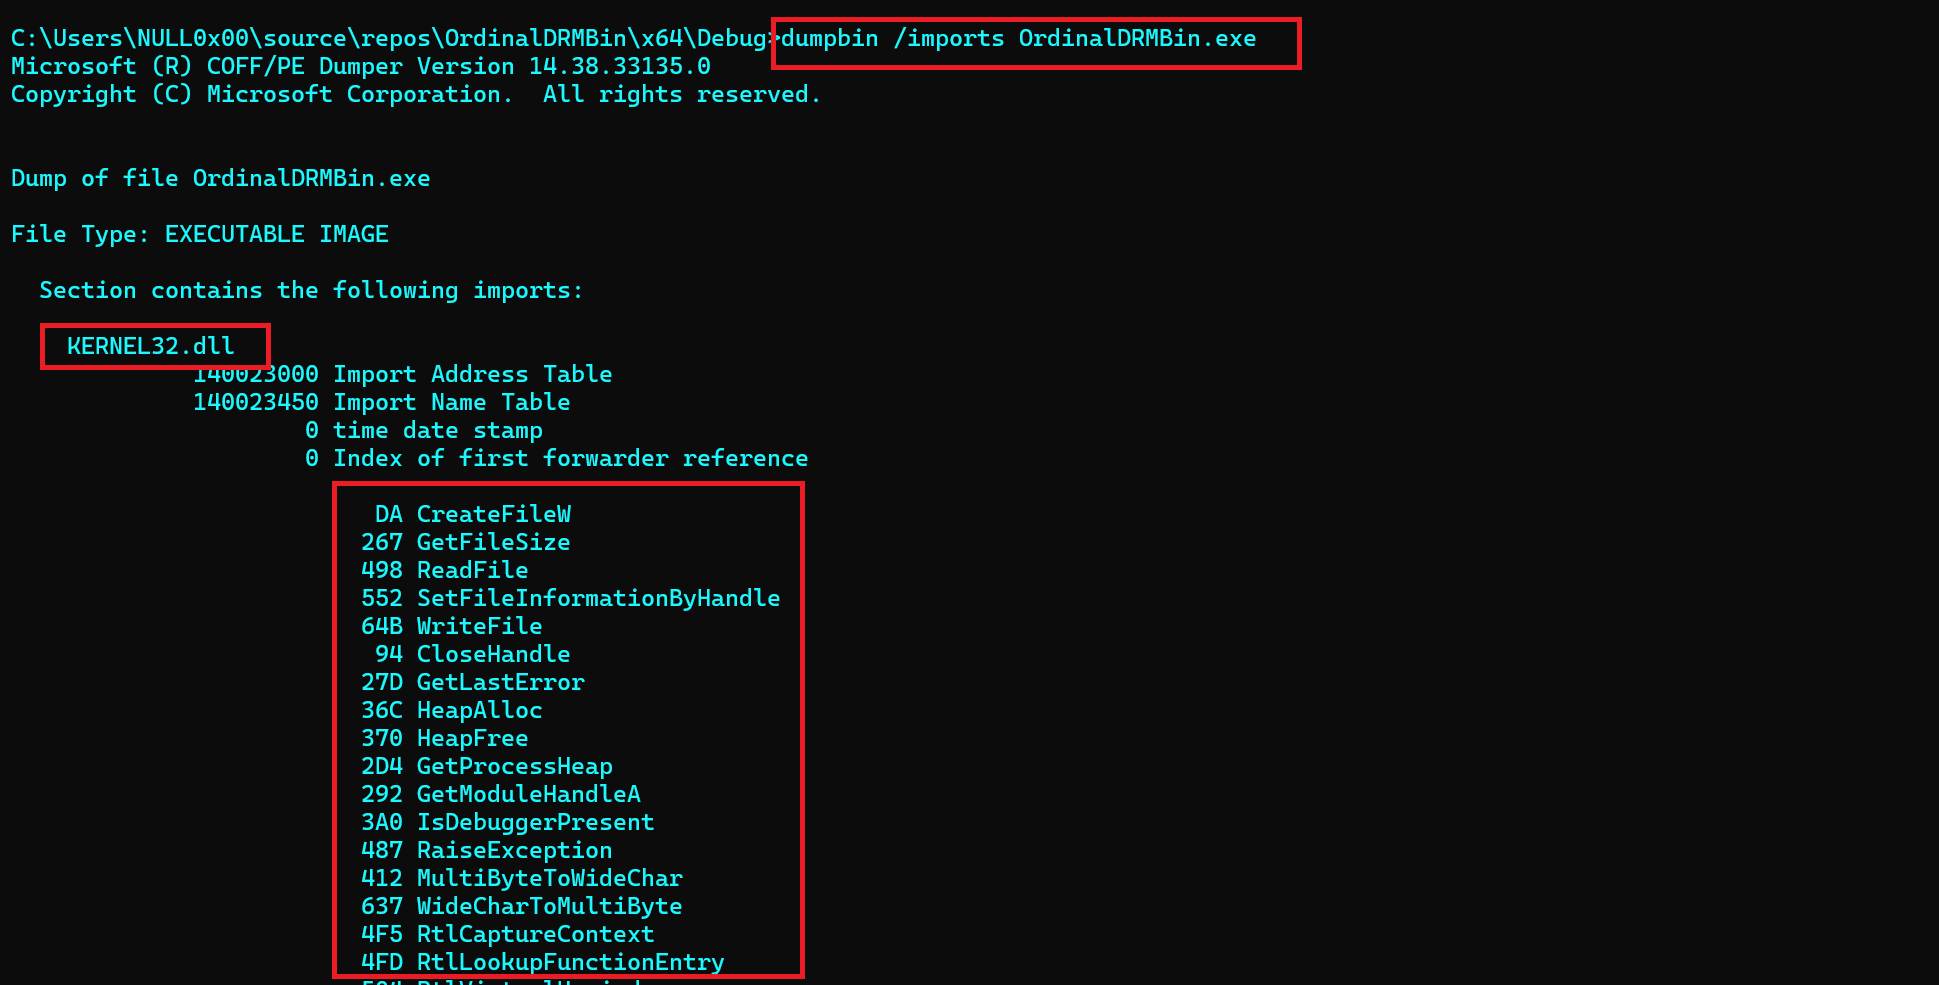 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 knight0x07/onenoteanalyzer
A C# based tool for analysing malicious OneNote documents
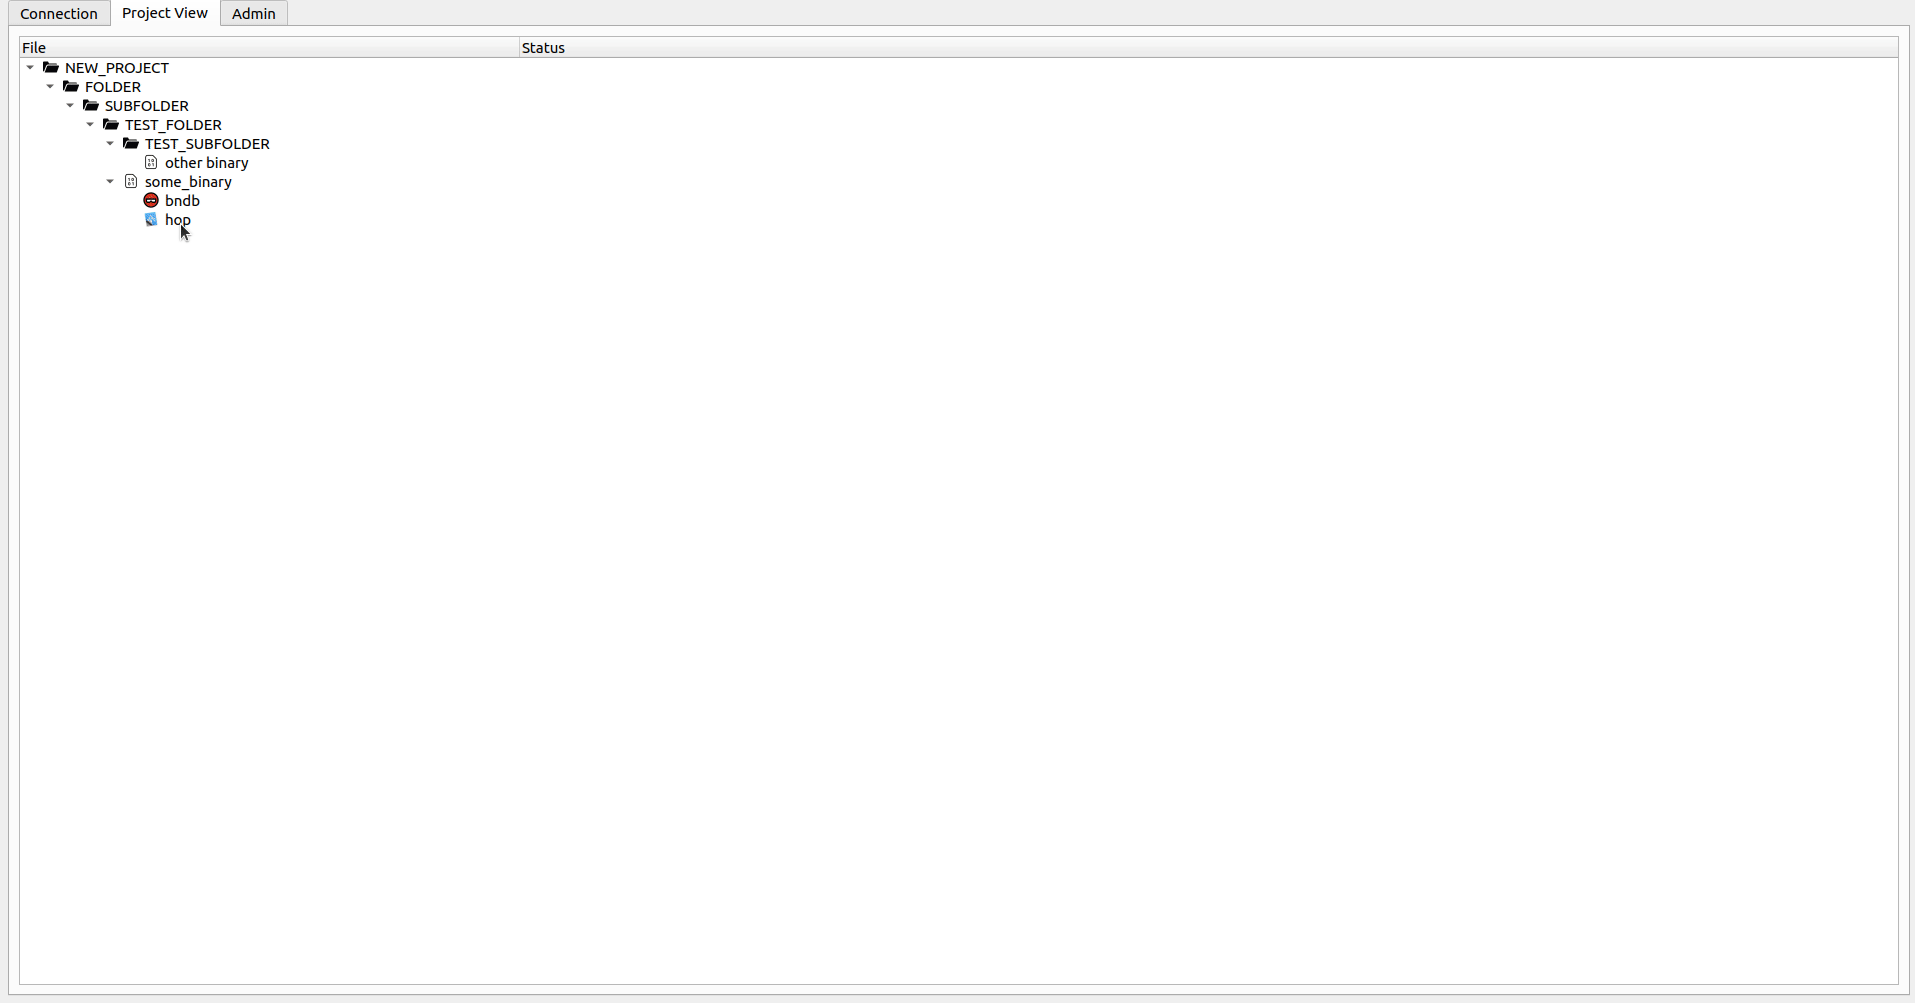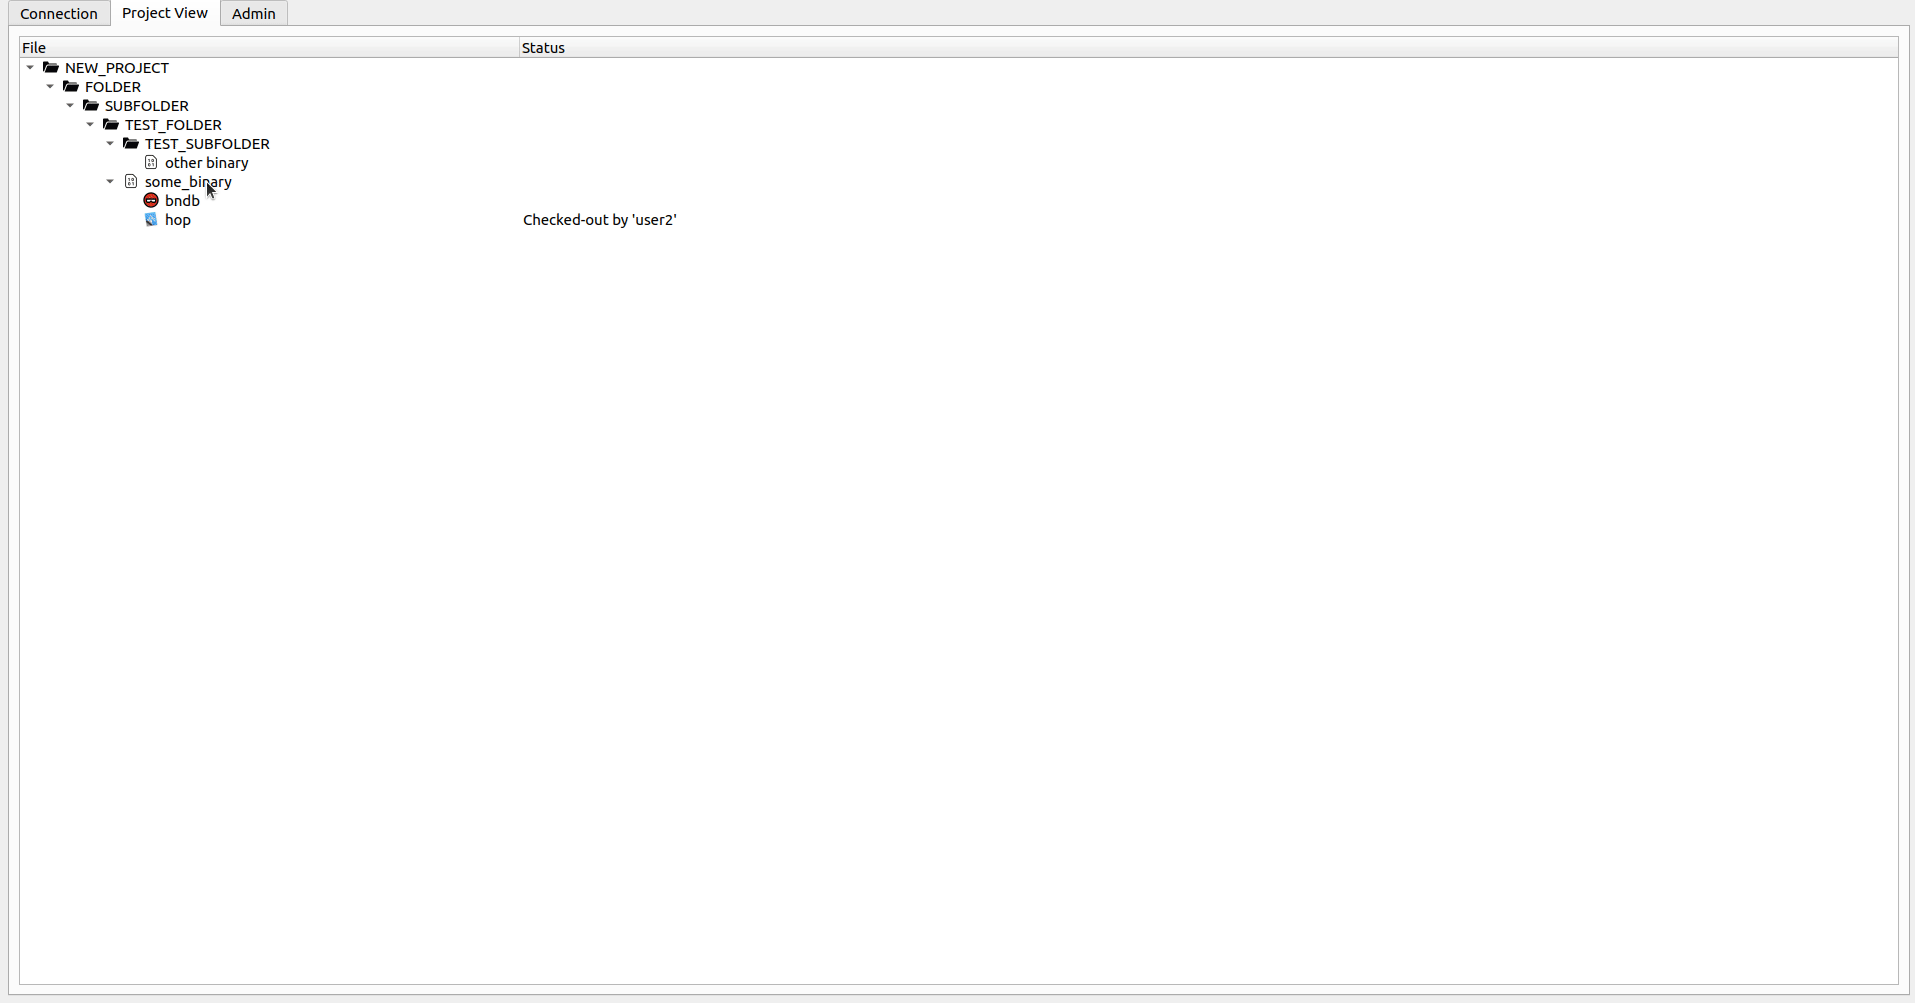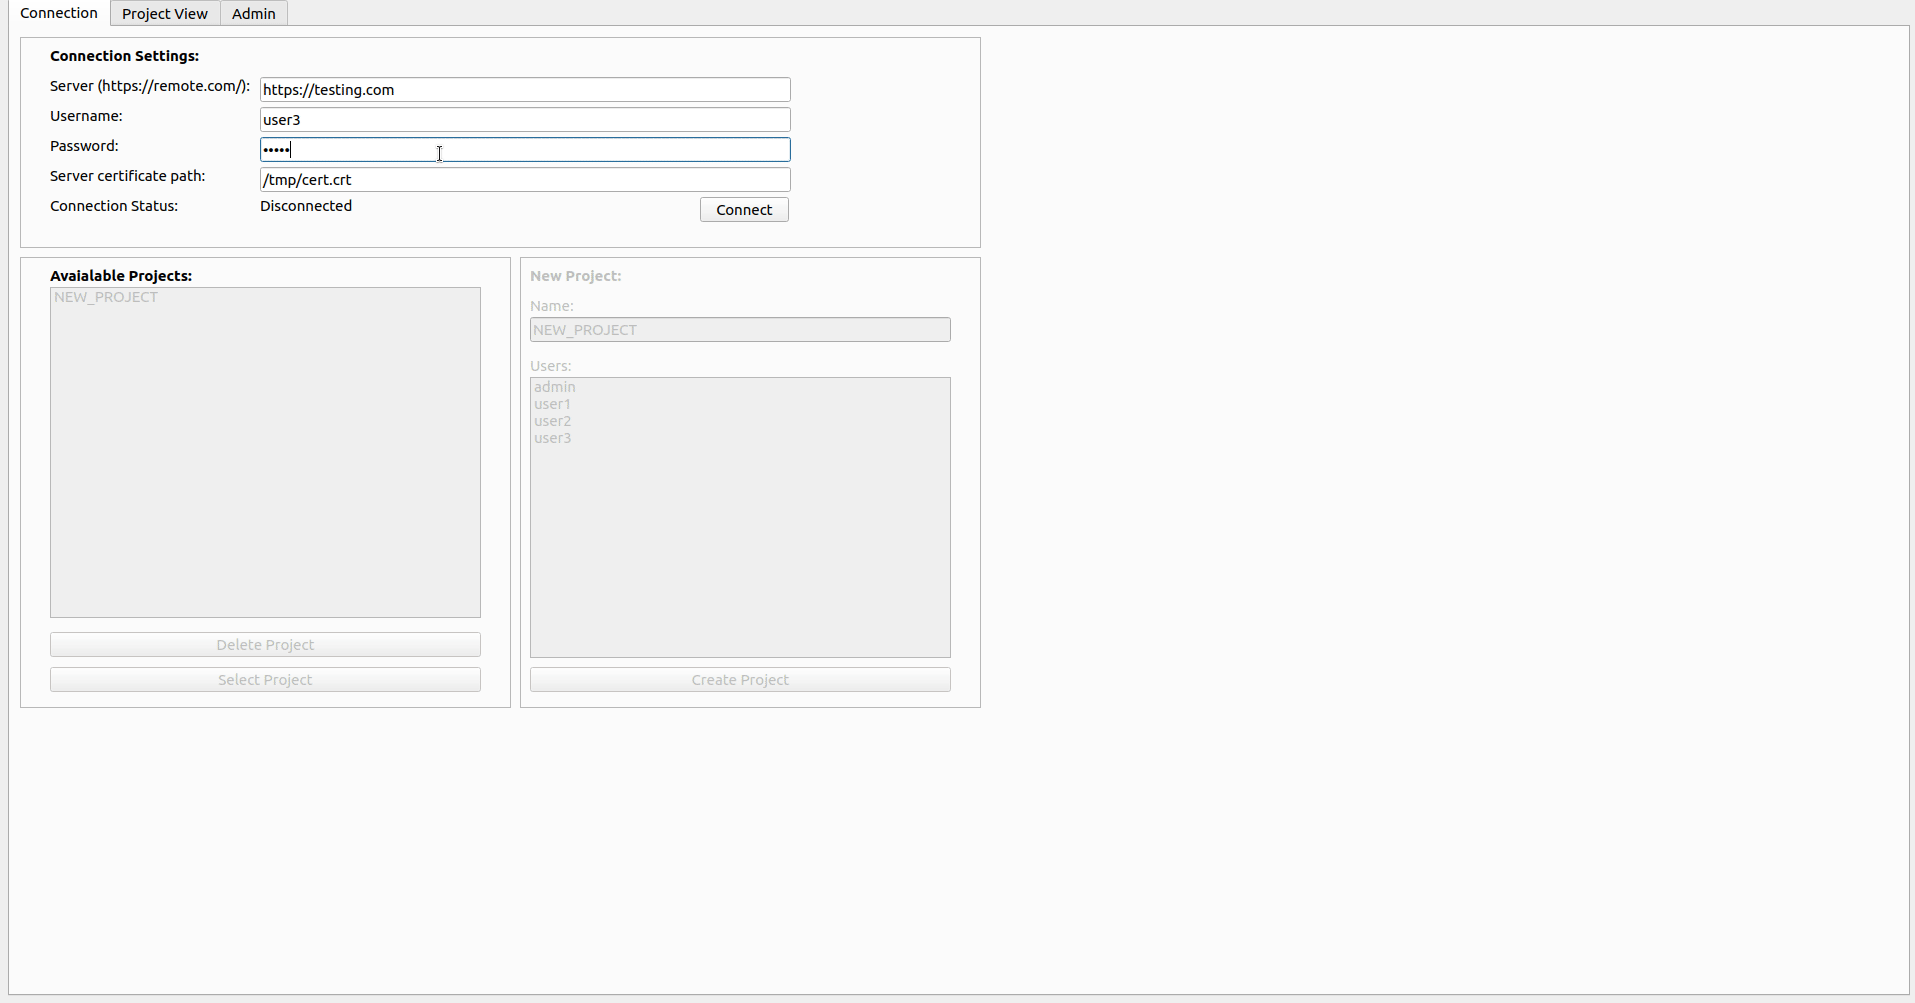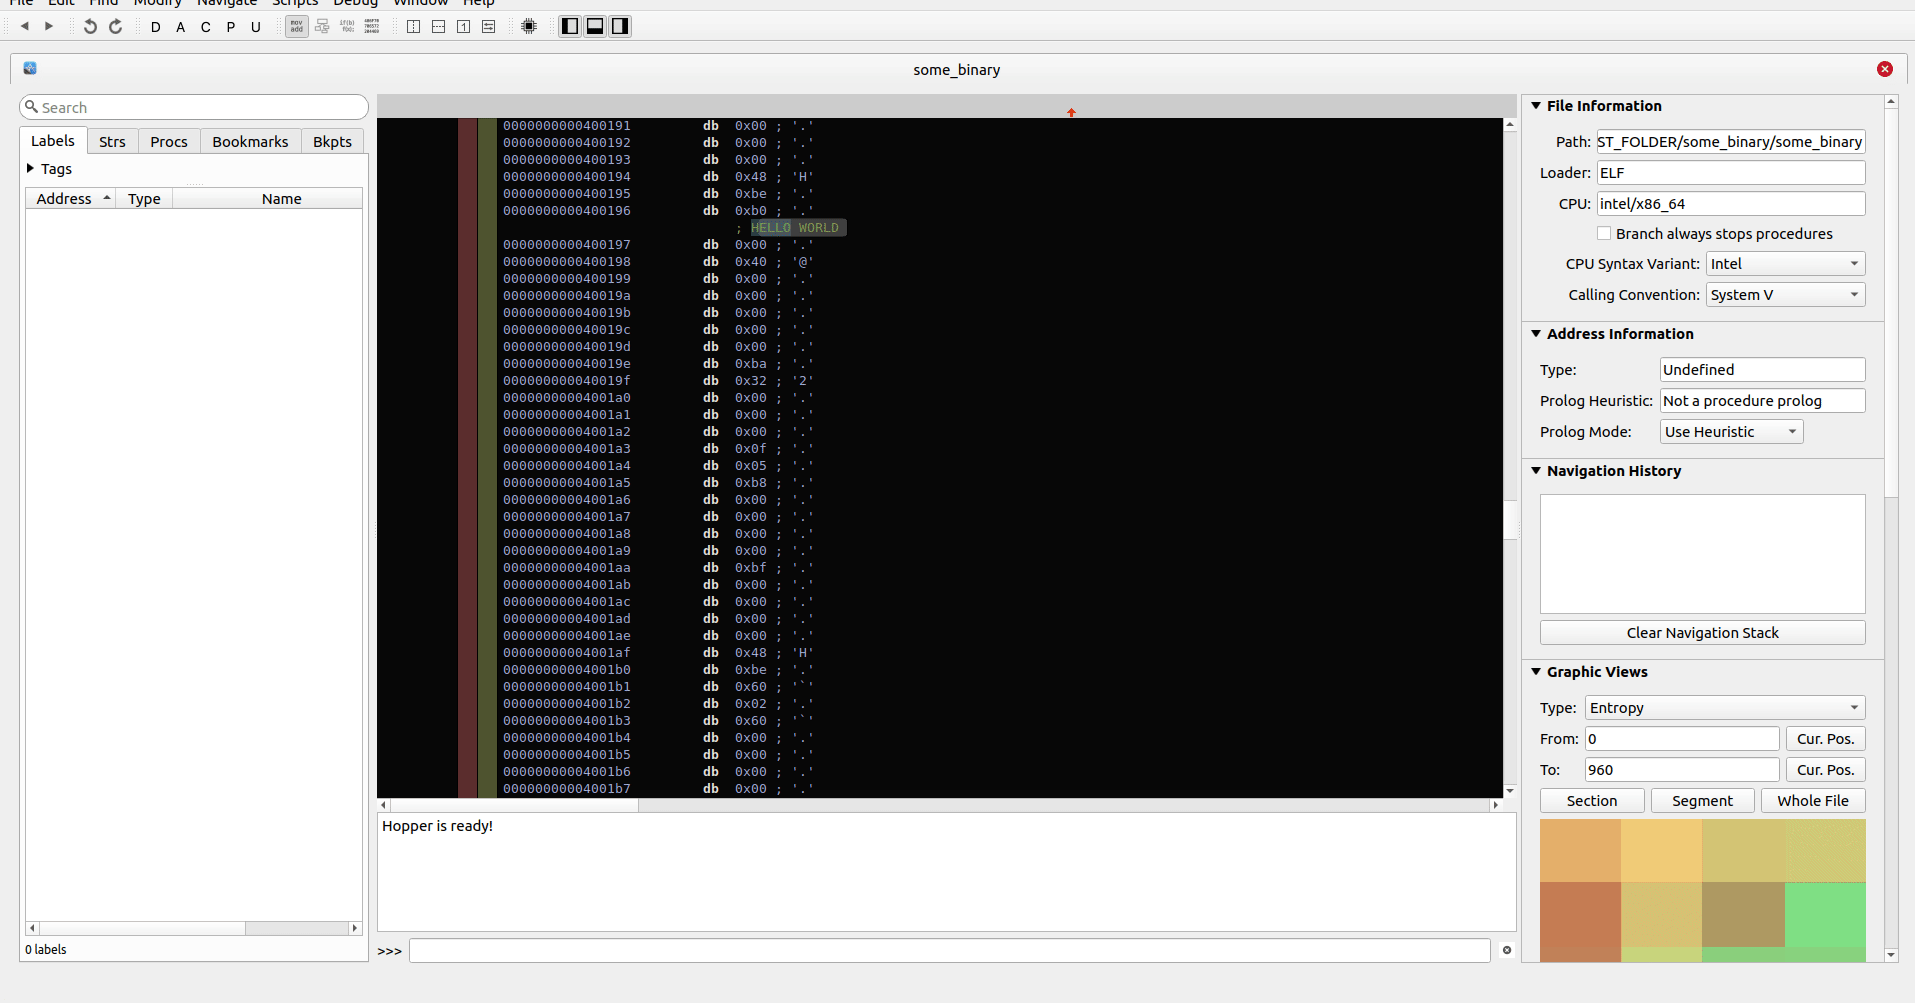 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 infobyte/cve-2023-21036
Detection and sanitization for Acropalypse Now - CVE-2023-21036
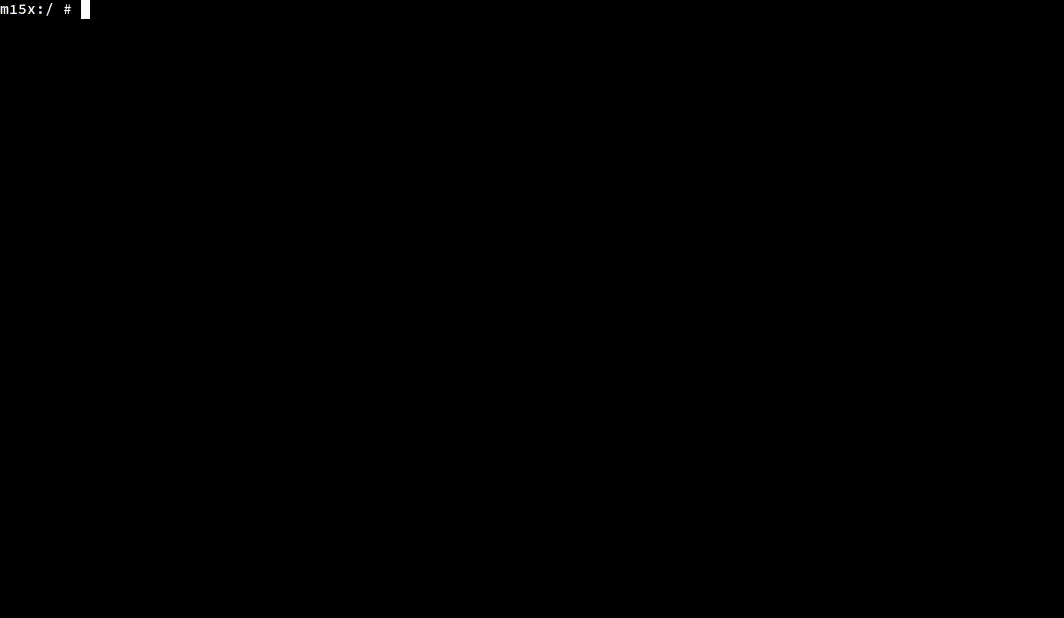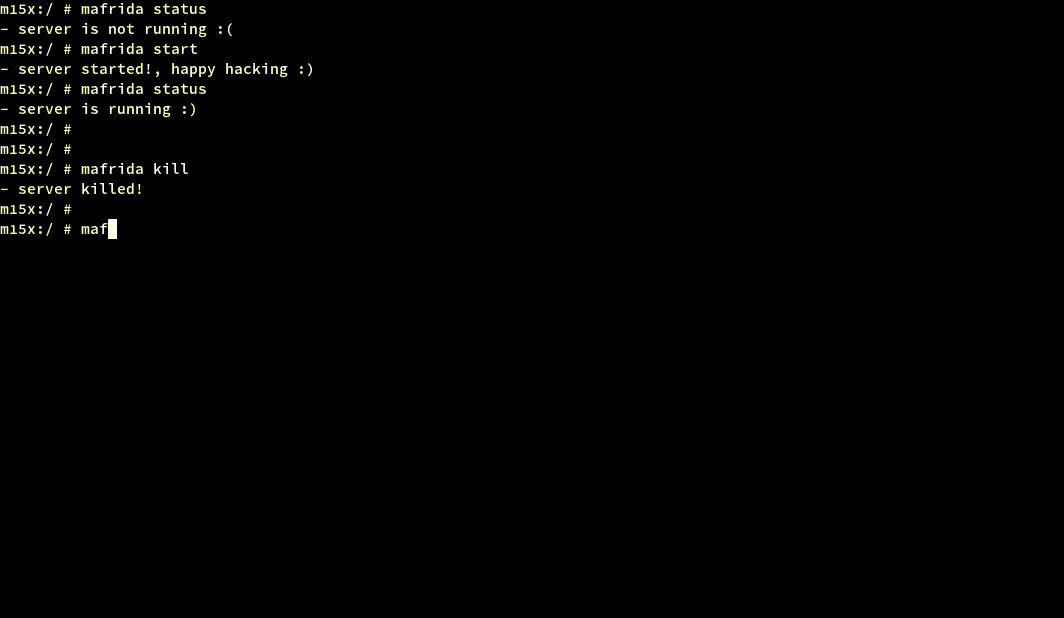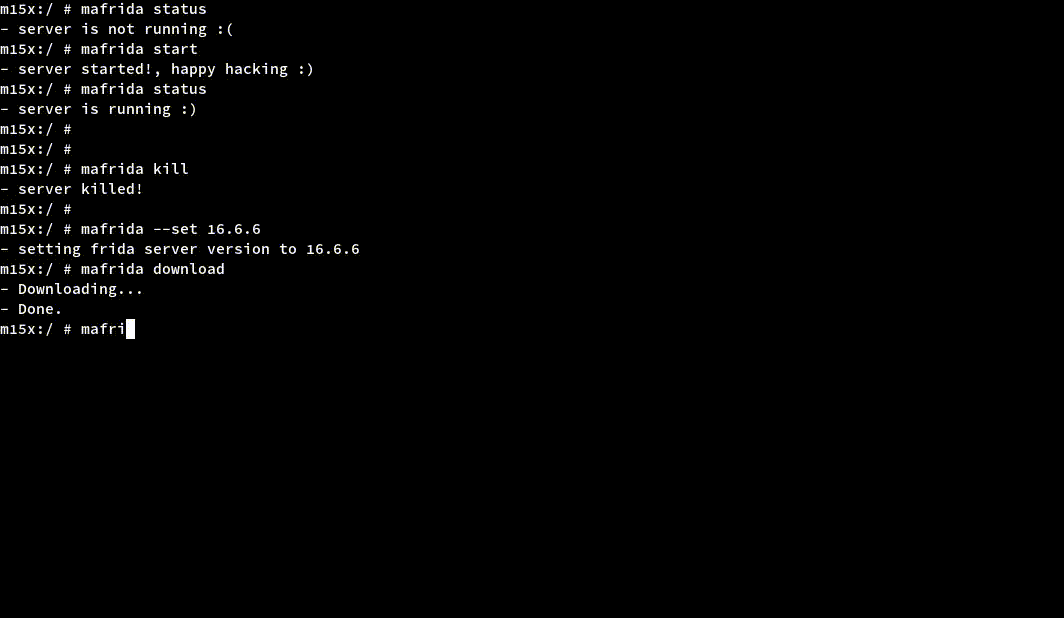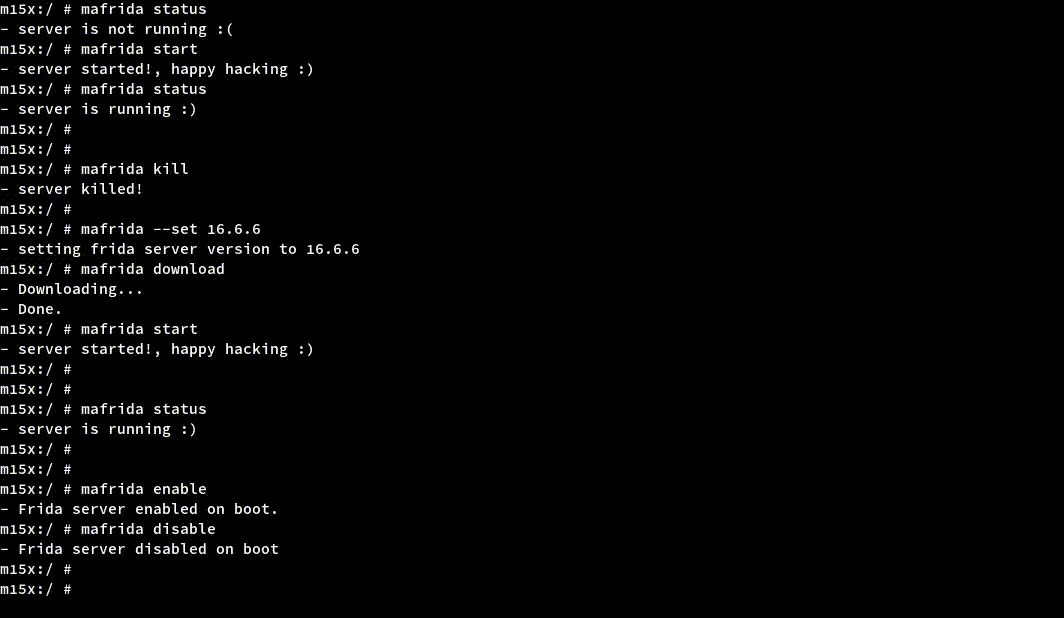 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…








