
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 seifheakal/blue-harness
Make your own app expensive to reverse. A build-time audit, harden and verify harness for native binaries and mobile apps, built to counter…
 virustotal/virustotal-mcp
MCP server exposing VirusTotal threat intelligence to AI agents: file, URL, domain and IP reports, analysis submission, and receipt recovery via VTAI.
 theauditortool/benchproctor
Open SAST benchmark corpus: 2,938,418 balanced cases, 11 languages, 21 framework targets, 242 emitted categories, and 231 distinct CWE IDs. Score…
 deathshotxd/sip2shell
One SIP text message to FreeSWITCH, and you are running commands. Exploit, scanner and a real vulnerable/patched Docker lab for CVE-2026-116779.
 tlsbollei/kittyloader
Evasive Windows loader in C/Assembly that decrypts an embedded payload in memory, unhooks PEB module lists, and applies anti-debug, sandbox and…
 dobin/supermega
Stealthily inject shellcode into an executable
 hunt3r-1/cybersec-intel
Single-file terminal threat-intelligence tool: live threat feeds, indicator lookups, passive site checks and CVE-to-exploit search, using free API…
 racoten/suture-pic
A Windows implant development framework for offensive engineering and C2 research.
 mein-0/fortiless
Proof-of-concept and analysis of a type-3 kernel out-of-bounds write in FortiClient's FortiShield_74.sys minifilter, including port protocol details…
 gmh5225/saadahla-docplz-with-slack
Document-harvesting implant that finds and hashes target files, kills locking processes, and exfiltrates them to a Slack channel via the Web API…
 ahmedboin/jailbreak
Domain-organized library of reverse engineering playbooks, guides, and research notes for analyzing software and recreating patches, with repeatable…
 mafarricos/badbox-tv-audit
Audits Android TV and Google TV devices over ADB for BadBox, XCPE and Vo1d malware, with a VPN traffic sentinel, IoC blocklists and reversible…
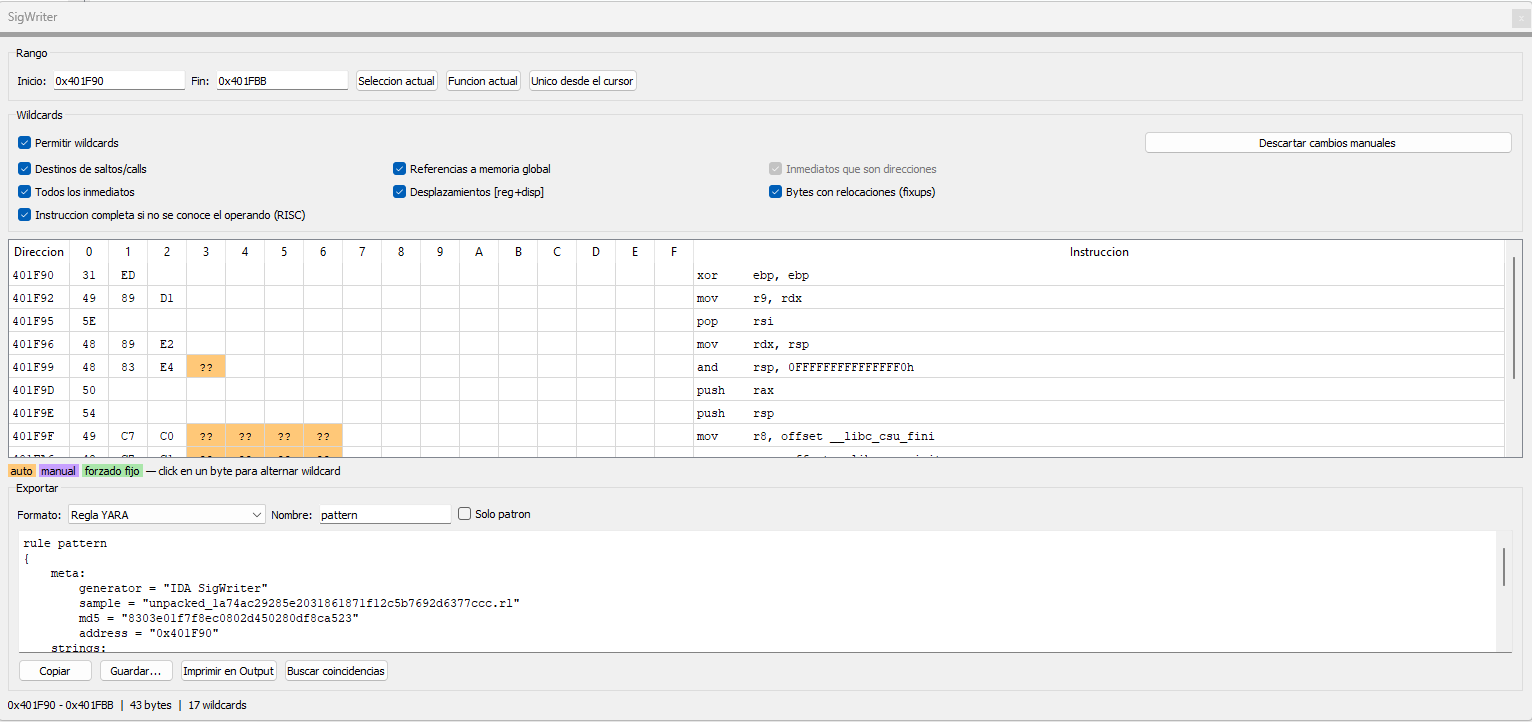 crackinglandia/idasignwriter
IDA Pro plugin that generates byte signatures from disassembly selections, with automatic and manual wildcards, match search, and export to YARA,…
 devtox/awesome-cybersecurity-blueteam
Curated blue-team resource list covering SOC operations, detection engineering, threat hunting, incident response, DFIR, malware analysis, and…
 ryftenius/resx
Specialized Windows Reverse Engineering & Binary Analysis Toolkit | API Deobfuscation, Call Graphs, Kernel Driver & IOCTL Analysis
 gleeda/memtriage
Allows you to quickly query a Windows machine for RAM artifacts
 unicornofhunt/s1l3nc3r
C tool that silences Microsoft Defender for Endpoint telemetry on Linux by writing syscall IDs into the exposed disabled_syscal eBPF map, suppressing…
 akari-sora/synology-nas-cli
Zero-dependency Python CLI and MCP server for Synology DSM 7 that audits NAS configuration against the C3RB3R/.L0CK3D ransomware campaign, plans…








